
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
1421 results
Spartacus preview
Archived

Spartacus

GitHubaccenture/spartacus

Spartacus DLL/COM Hijacking Toolkit

binary-analysiscode-analysisdefensive-tools+5
1.1k
2 years ago
Ghidrathon preview
Archived

Ghidrathon

GitHubmandiant/ghidrathon

The FLARE team's open-source extension to add Python 3 scripting to Ghidra.

binary-analysismalware-analysisreverse-engineering+1
7902 years ago
panopticon preview
Archived

panopticon

GitHubdas-labor/panopticon

A libre cross-platform disassembler.
binary-analysisdebuggersfirmware-analysis+2
1.4k7 years ago
path-auditor preview
Archived

path-auditor

GitHubgoogle/path-auditor

Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…

binary-analysisdynamic-code-analysisexploitation+3
2505 years ago
flare-ida preview
Archived

flare-ida

GitHubmandiant/flare-ida

IDA Pro utilities from FLARE team
binary-analysisdebuggersdynamic-analysis-sandboxing+3
2.4k1 year ago
flashmingo preview
Archived

flashmingo

GitHubmandiant/flashmingo

Automatic analysis of SWF files based on some heuristics. Extensible via plugins.
binary-analysisdynamic-analysis-sandboxingeducation+6
1207 years ago
BrokenType preview
Archived

BrokenType

GitHubgoogleprojectzero/brokentype

TrueType and OpenType font fuzzing toolset
binary-analysisexploitationfuzzing+1
4357 years ago
Mangle preview
Archived

Mangle

GitHuboptiv/mangle

Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
binary-analysisdefensive-toolsexploitation+6
1.2k3 years ago
GoDefender preview
Archived

GoDefender

GitHubkiexitdispatcher/godefender

Anti Virtulization, Anti Debugging, AntiVM, Anti Virtual Machine, Anti Debug, Anti Sandboxie, Anti Sandbox, VM Detect package. Windows ONLY.

anti-botbinary-analysisdefensive-tools+3
85610 months ago
LoGiC.NET preview
Archived

LoGiC.NET

GitHubanerruption/logic.net

A free and open-source .NET obfuscator using dnlib.

anti-botbinary-analysiscode-analysis+2
5153 years ago
DLLirant preview
Archived

DLLirant

GitHubsh0ckfr/dllirant

DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.

binary-analysisexploitationprivilege-escalation+2
3224 years ago
viper preview
Archived

viper

GitHubviper-framework/viper

Binary analysis and management framework
binary-analysisexploit-frameworksforensics+3
1.6k3 years ago
luadec-tplink preview

luadec-tplink

GitHubsuperkhung/luadec-tplink

Modified luadec version to decompile TP-Link Archer C7 LUA firmware.

binary-analysisembedded-systems-securityfirmware-analysis+4
336 years ago
cve-2014-2734 preview
Archived

cve-2014-2734

GitHubadrienthebo/cve-2014-2734

I think this CVE is full of lies and deceit and very confusing code.
binary-analysisexploitationvulnerability-analysis
112 years ago
seetong-ts81xxd3x-rce preview

seetong-ts81xxd3x-rce

GitHubheapframe/seetong-ts81xxd3x-rce

CVE-2026-100886 | Unauthenticated Remote Code Execution toolkit.
binary-analysisembedded-systems-securityexploitation+6
11 days ago
LetMeGG preview

LetMeGG

GitHubgmh5225/letmegg

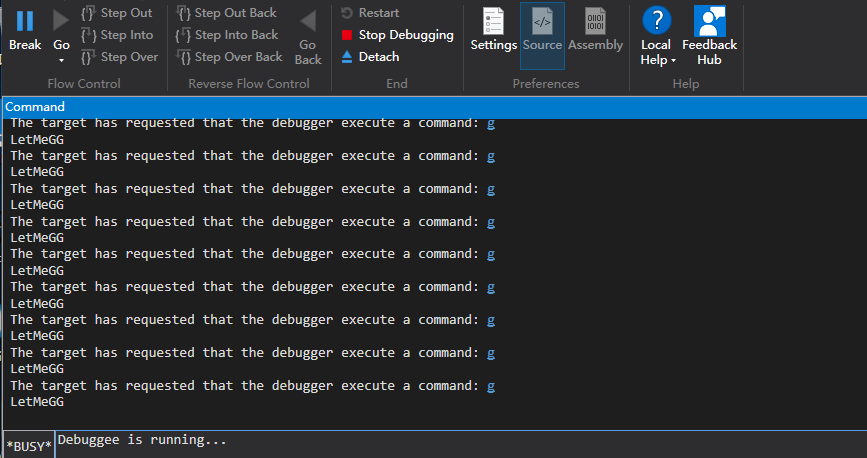
Windows kernel proof-of-concept demonstrating an anti-debugging technique that prevents WinDbg from breaking by manipulating the kernel exception…
anti-botbinary-analysisdebuggers+1
154 years ago
illusion-rs preview
Archived

illusion-rs

GitHubmemn0ps/illusion-rs

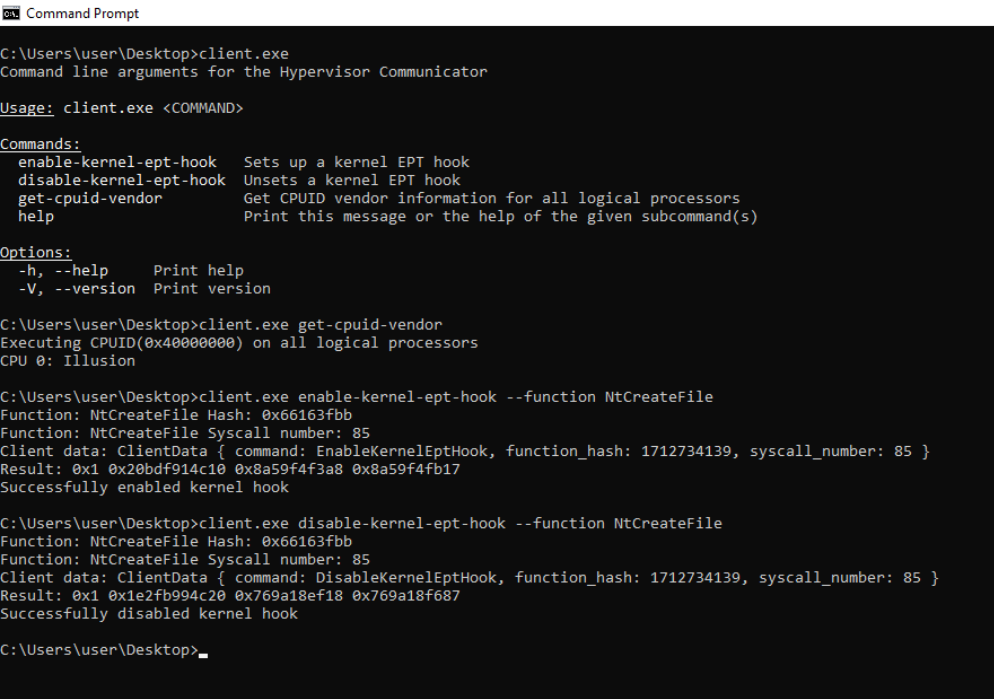
Rusty Hypervisor - Windows UEFI Blue Pill Type-1 Hypervisor in Rust (Codename: Illusion)

binary-analysisdefensive-toolshardware-security+7
4134 months ago
Previous1…7879Next