disrobe
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
android-securitybinary-analysisfirmware-analysis+4
113
1-3-7/disrobeRust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 newliver666/apk-reverse
Agent skill for Android APK reverse engineering: dex patching, unpacking, repacking, ad and paywall removal, native .so analysis, and runtime…
 ejfkdev/ddc
DEX → Java decompiler in Rust — fast, progressive analysis, bilingual CLI
 ejfkdev/avdroot
Root an Android Studio emulator by patching its ramdisk with Magisk — in pure Go.
 ejfkdev/dae
Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…
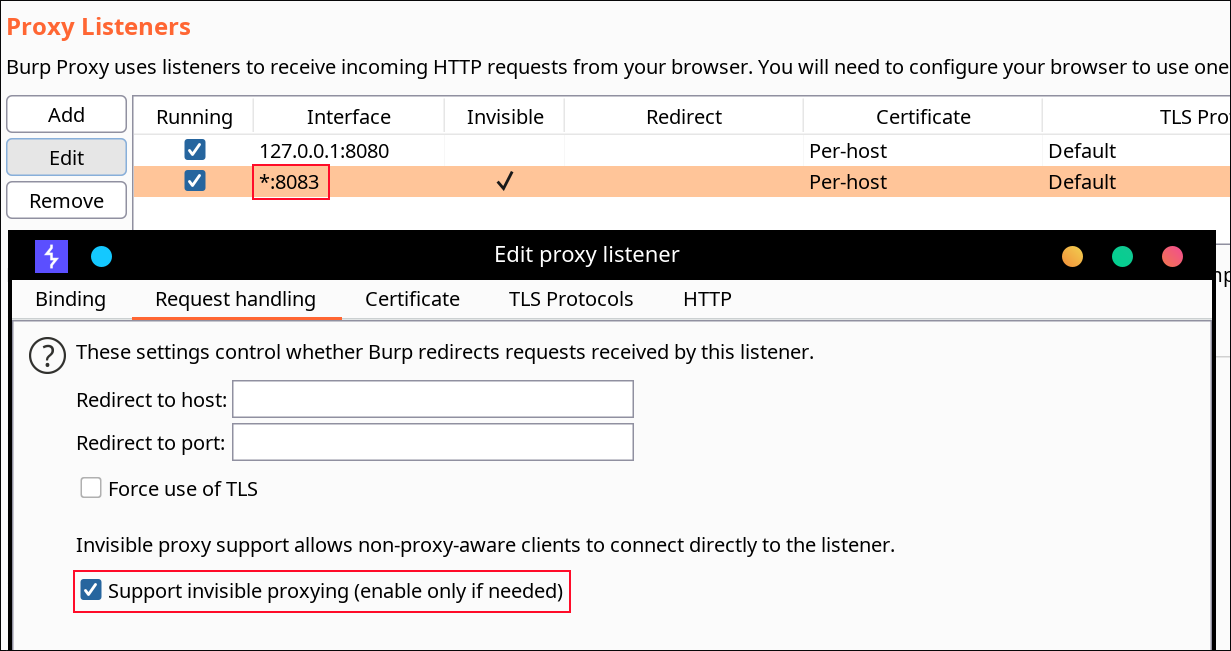 ptswarm/reflutter
Flutter Reverse Engineering Framework
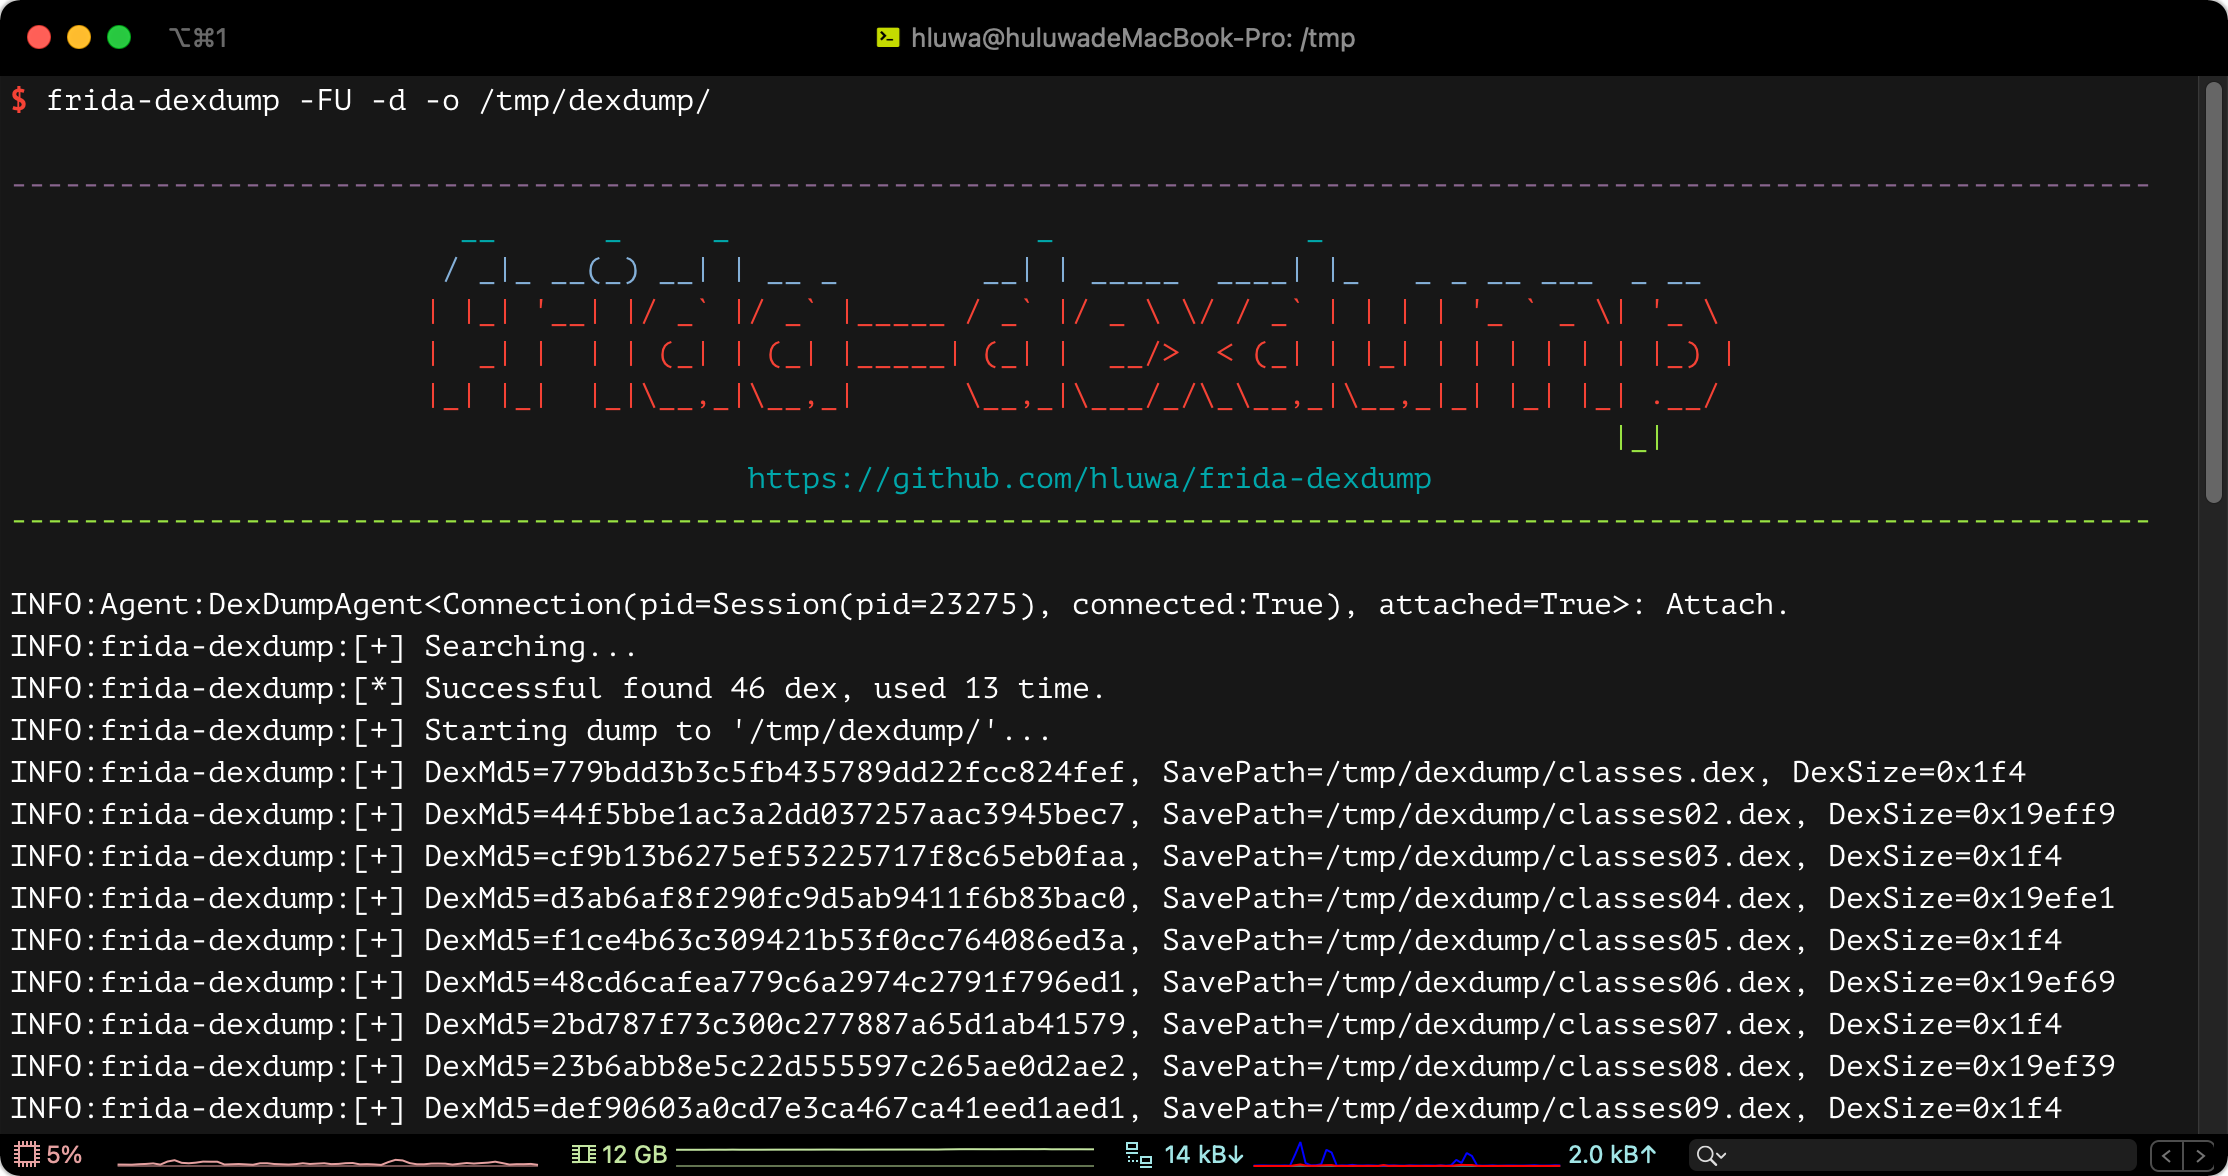 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
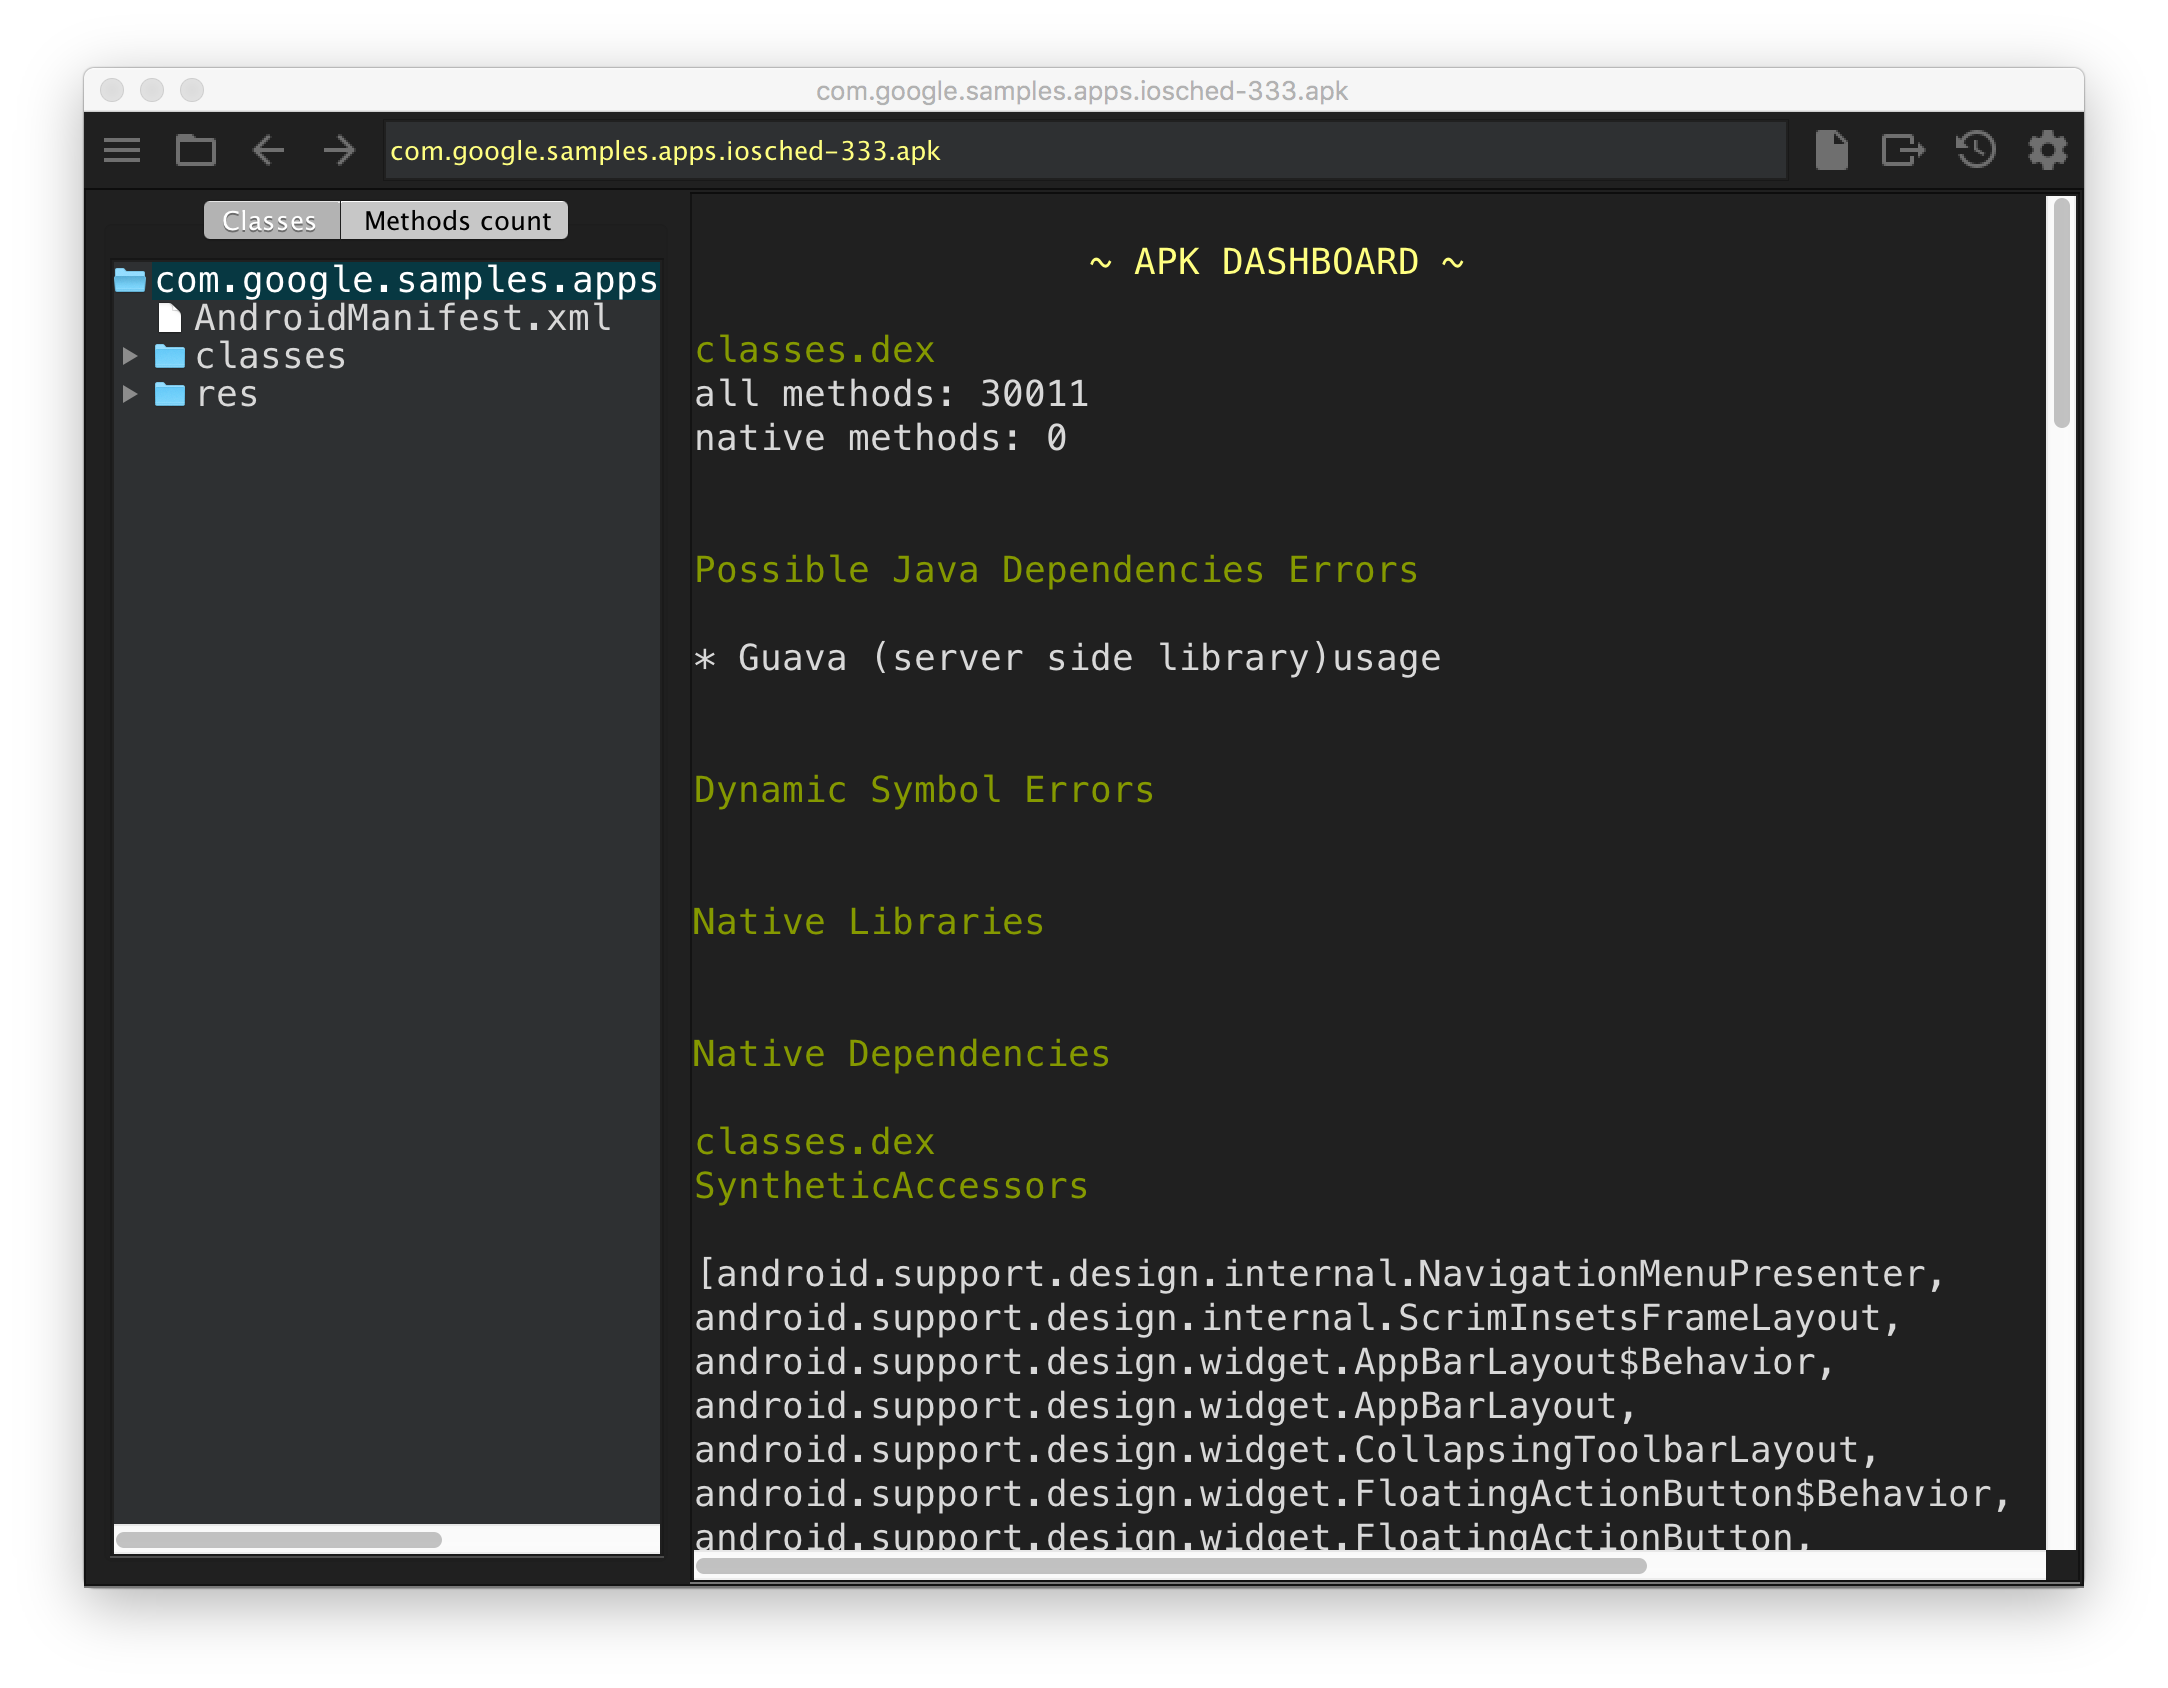 google/android-classyshark
Android and Java bytecode viewer
 google/enjarify
Translates Dalvik bytecode (DEX/APK) to equivalent Java bytecode, enabling Java analysis tools to process Android applications with high correctness…
 abhi-r3v0/adhrit
Android Security Suite for in-depth reconnaissance and static bytecode analysis based on Ghera benchmarks.
 sonyxperiadev/apkanalyser
Static analysis tool for Android APKs that inspects Dalvik bytecode, decodes XML resources, and detects potential issues. Supports binary…