
0xCr0ssCrush
 deathshotxd/0xcr0sscrush
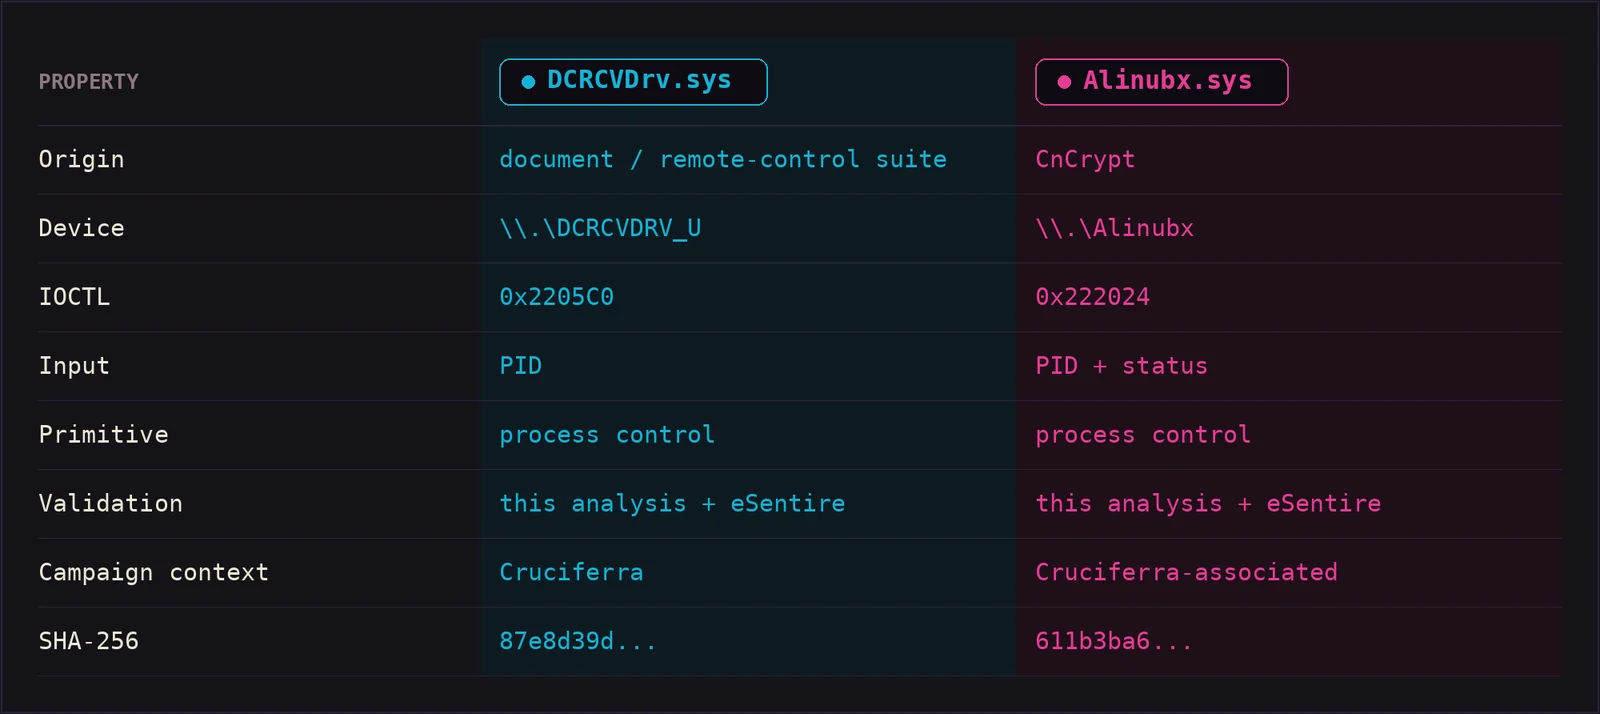
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.
binary-analysisdefensive-toolsexploitation+4
38
deathshotxd/0xcr0sscrushWindows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.
 cloudflare/filterforge
Tool for solving BPF filters and crafting packets based on these.
 elastic/die-python
Native Python3 bindings for @horsicq's Detect-It-Easy
 umpolungfish/byvalver
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
 dsnezhkov/elfpack
ELF binary section docking toolkit for stageless payload delivery, enabling in-field payload attachment, signature evasion, and static/dynamic…
 hasherezade/sig_finder
Signature finder (from PE-bear)
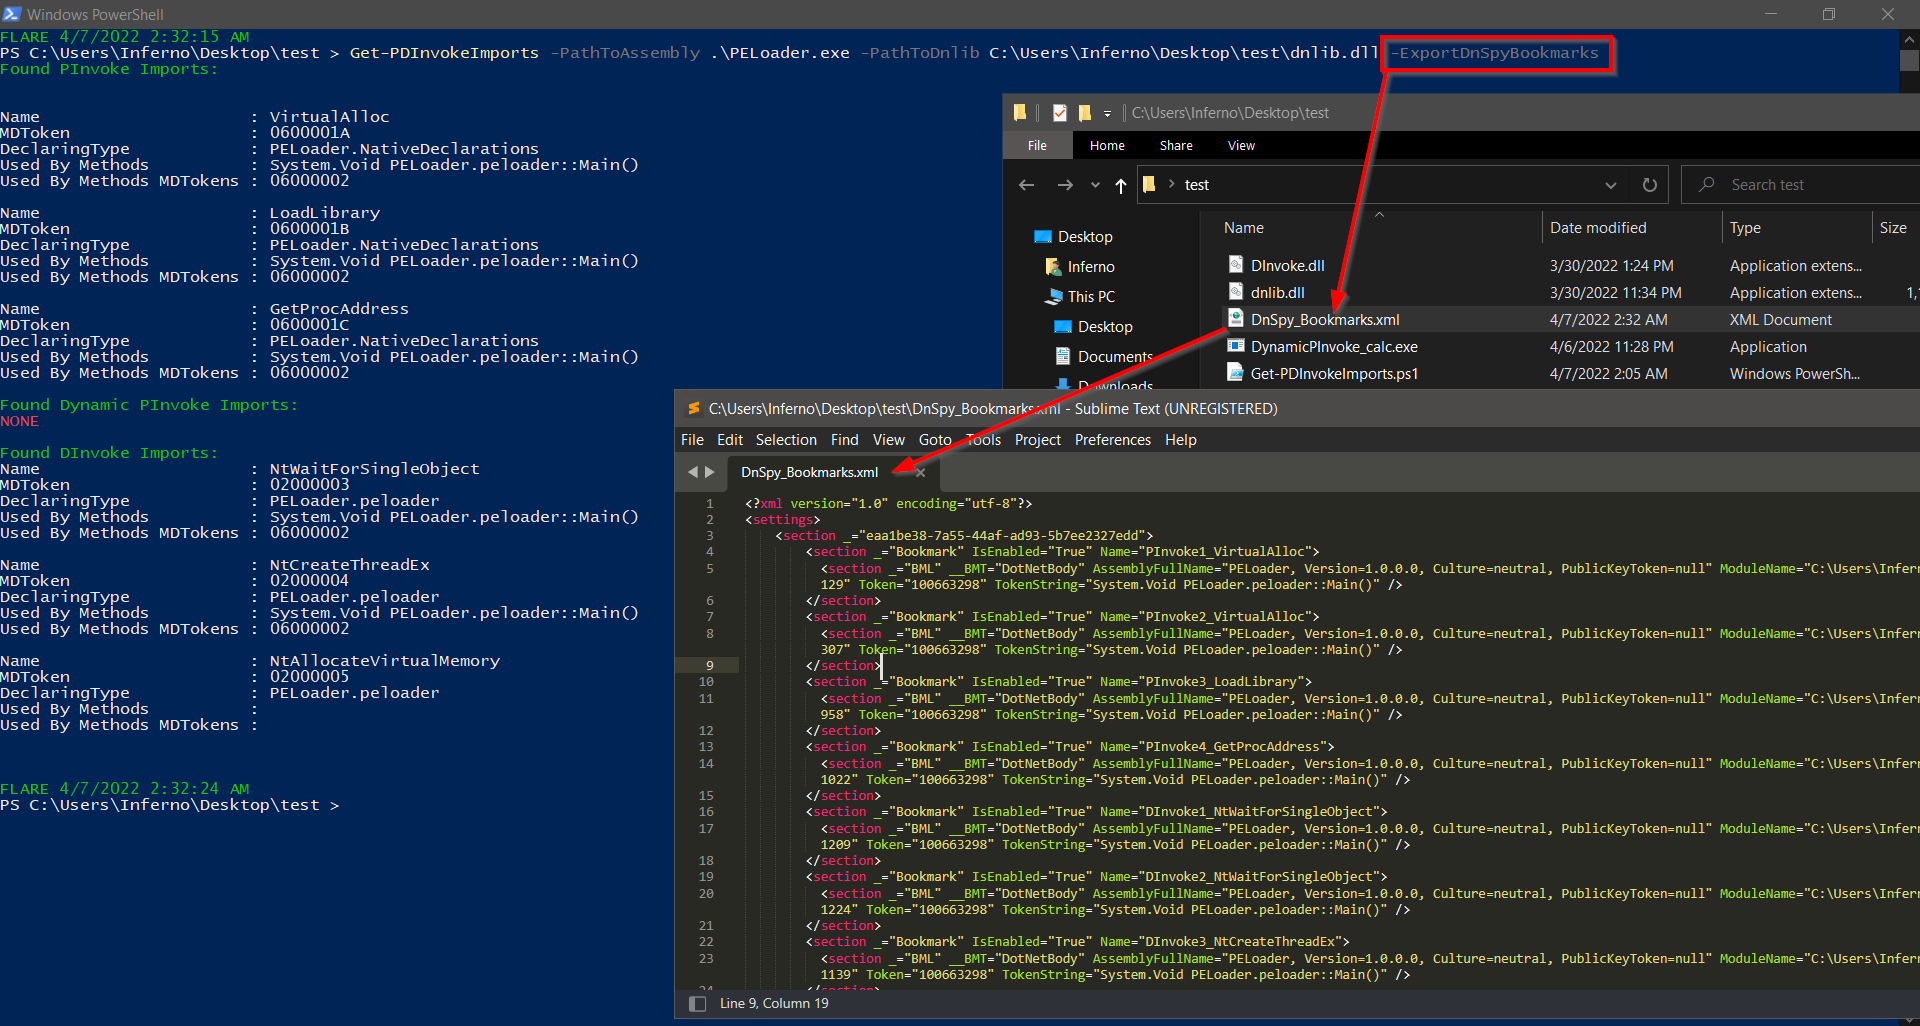 dump-guy/get-pdinvokeimports
PowerShell module for automatic detection of P/Invoke, Dynamic P/Invoke, and D/Invoke in .NET assemblies. Reveals unmanaged API calls, MDTokens, and…
 splintersfury/autopiff
Semantic analysis engine for detecting vulnerability fixes in Windows kernel driver patches — 58 YAML rules, Ghidra decompilation, reachability…
 eset/wslink-vm-analyzer
WslinkVMAnalyzer is a tool to facilitate analysis of code protected by a virtual machine featured in Wslink malware
 elevenpaths/pesto
Extracts and analyzes PE file security characteristics (ASLR, DEP, CFG, NO_SEH) from DLLs and EXEs across directories, storing results in a SQLite…
 withsecurelabs/radare2-scripts
Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…
 yaklang/javajive
Pure-Go Java Decompiler and Serialization Operator
 gmh5225/kli-ex
Extended kernel lazy importer for Windows drivers that resolves APIs at runtime with encrypted, cached import names to hide kernel function usage…
 nccgroup/pythia
A tool to extract RTTI information from Delphi executables, written in pure Python
 cyberclues/rtf_exploit_extractor
Script to extract malicious payload and decoy document from CVE-2015-1641 exploit documents
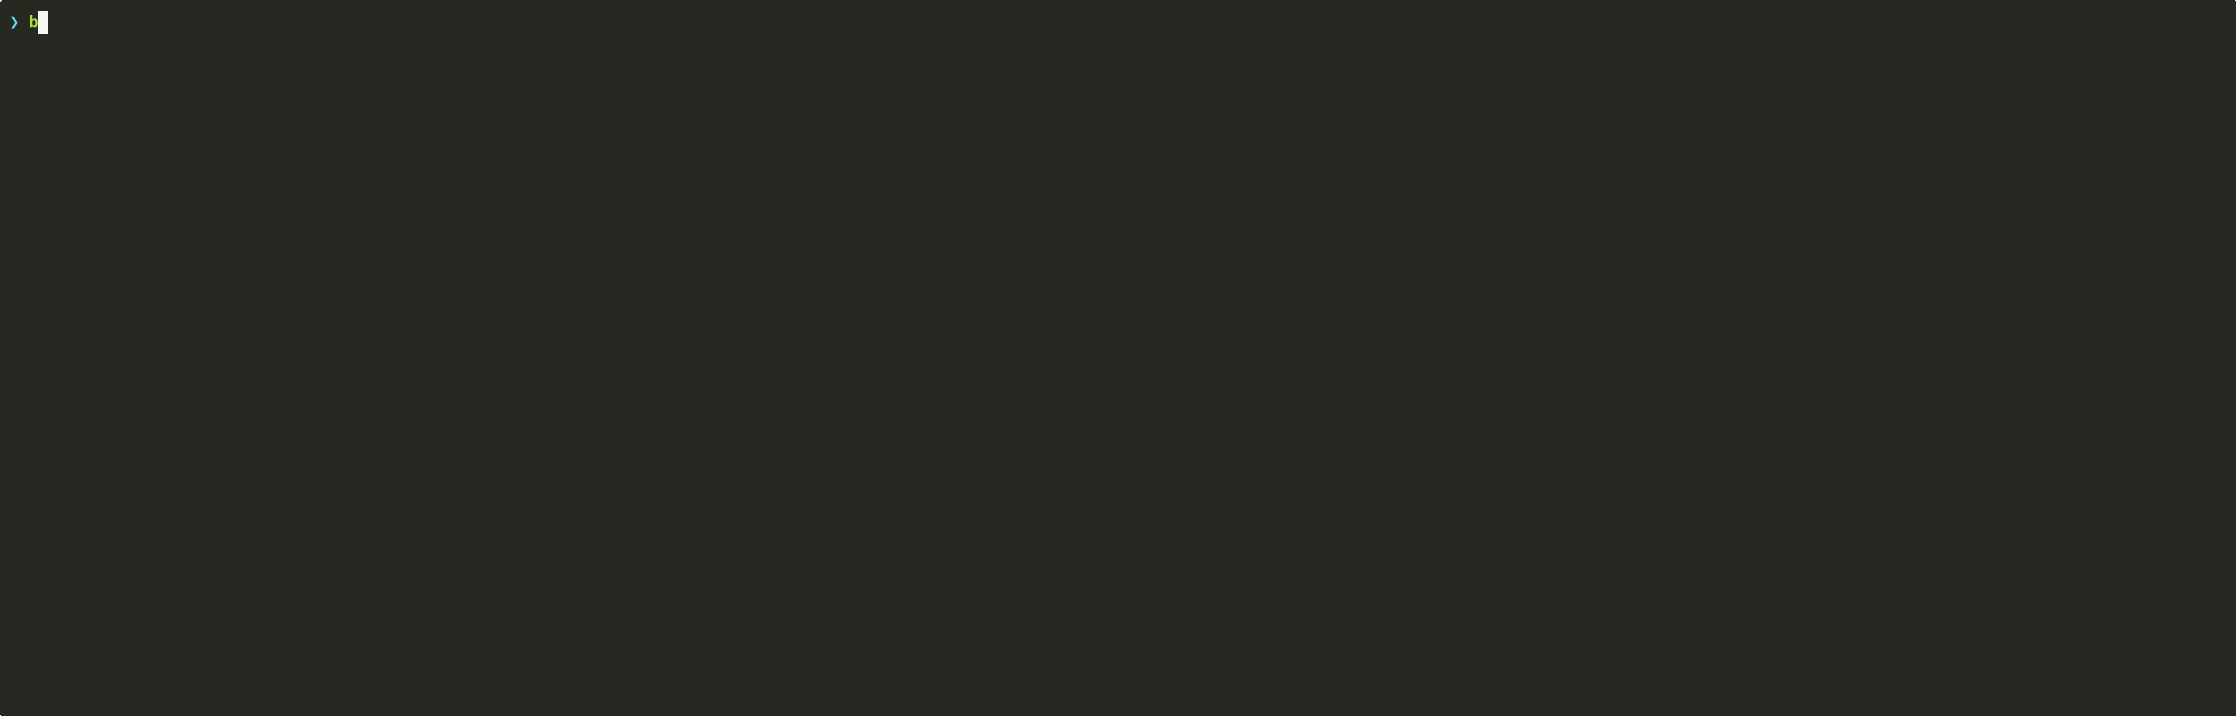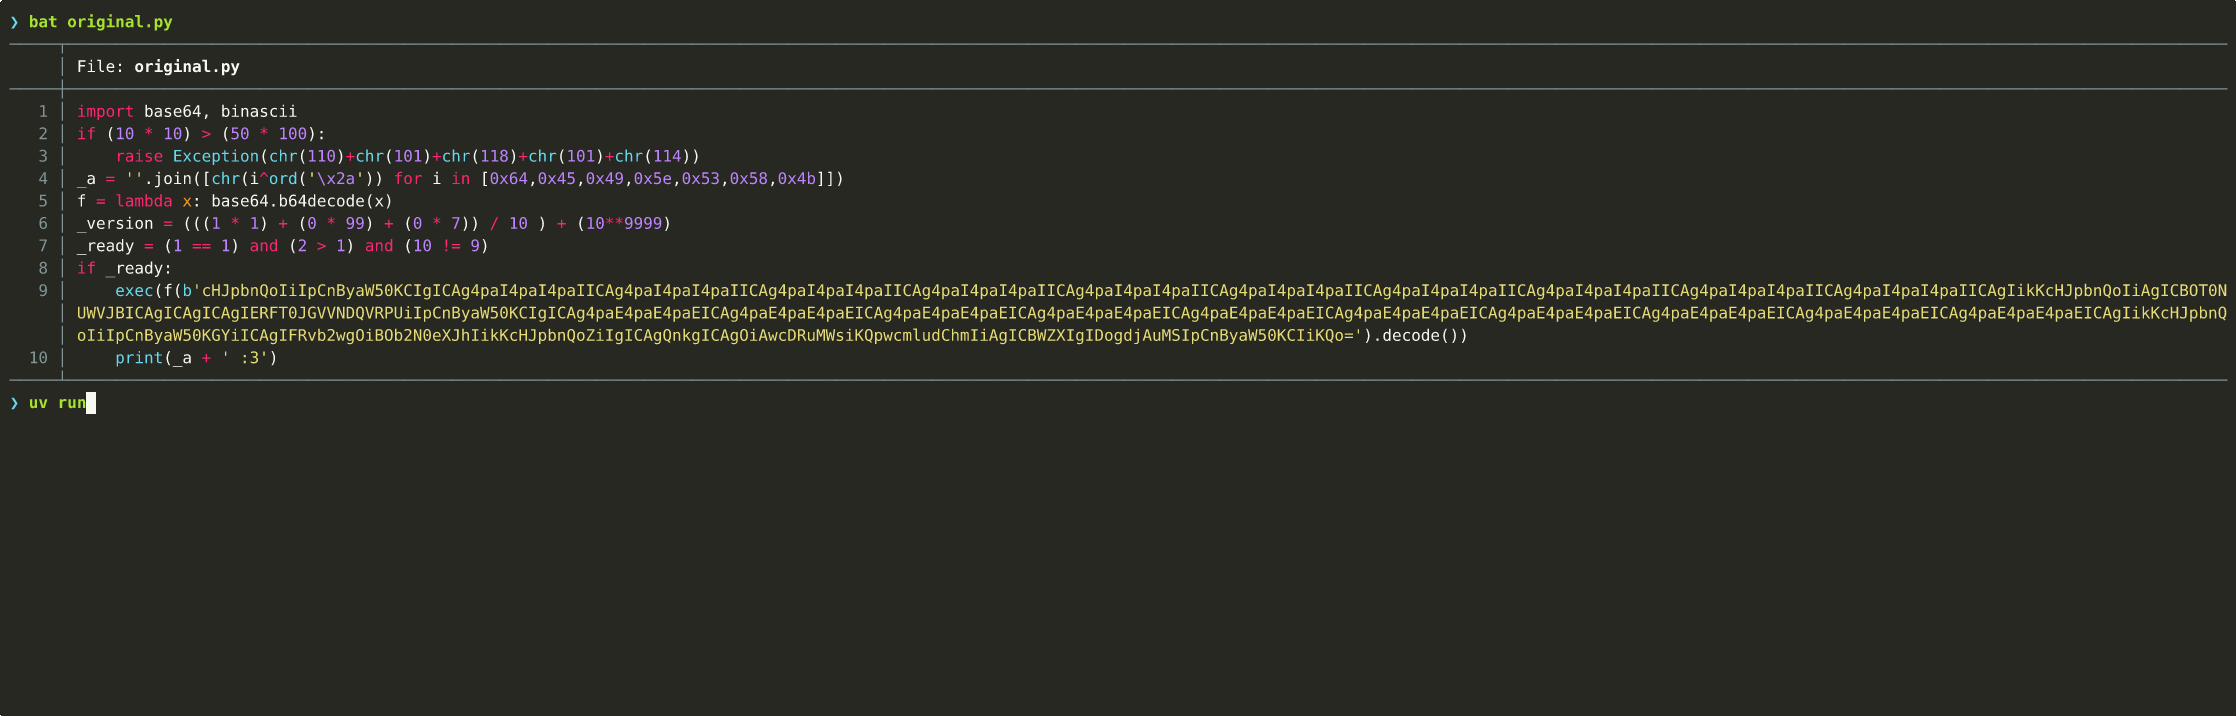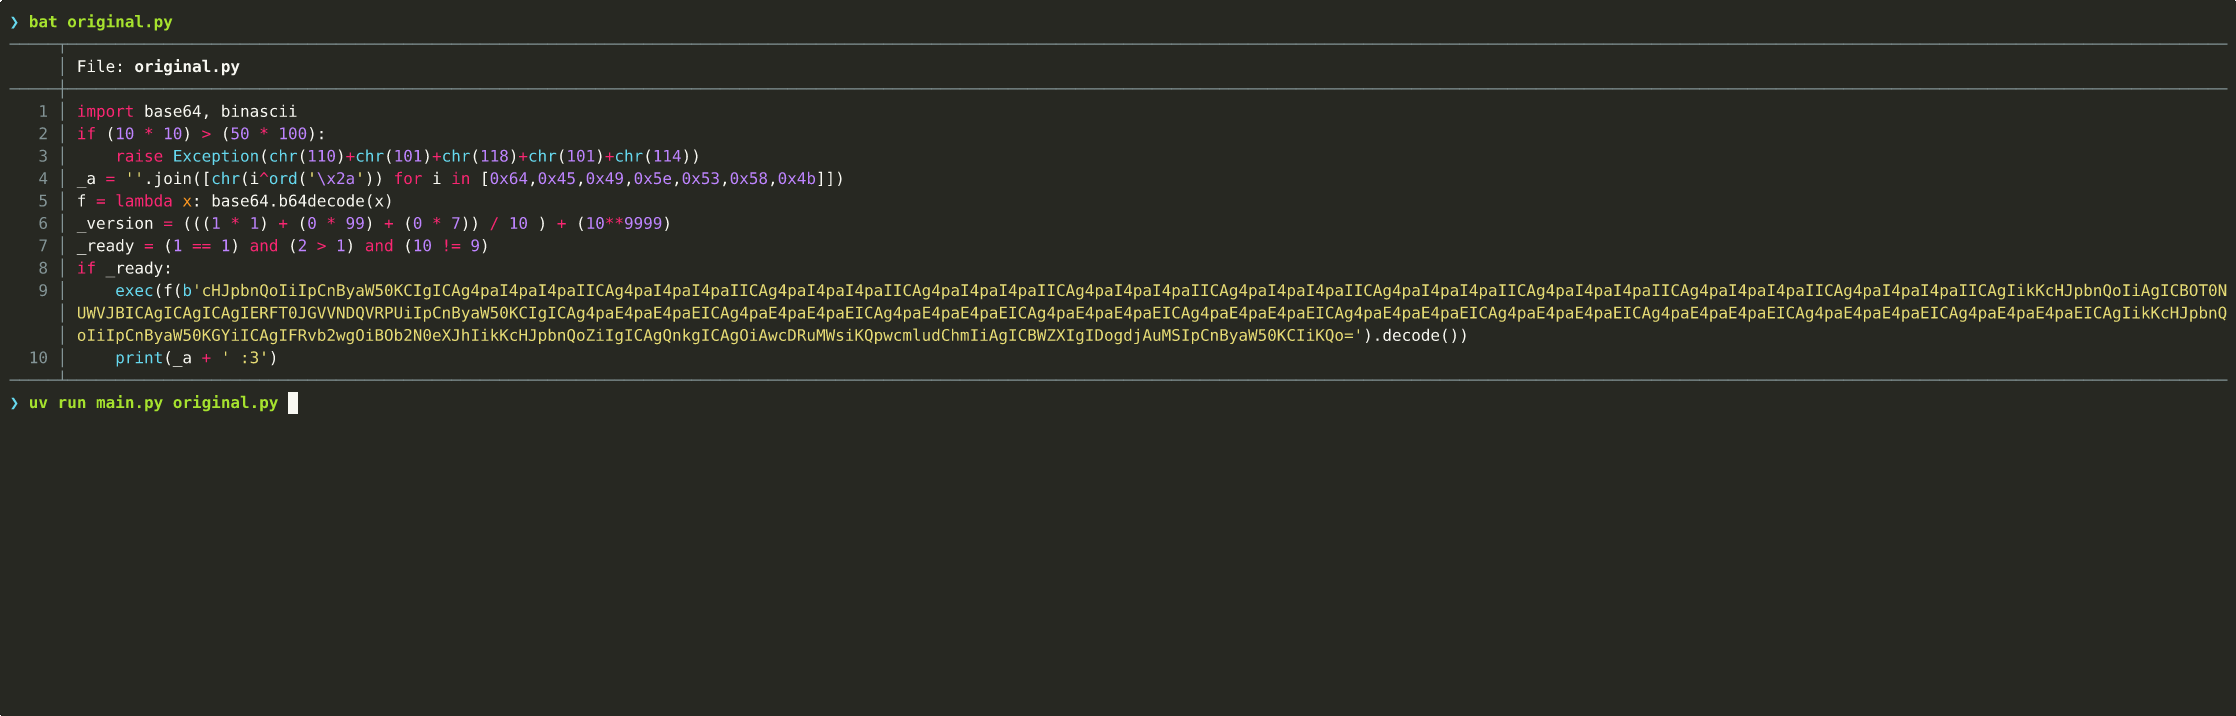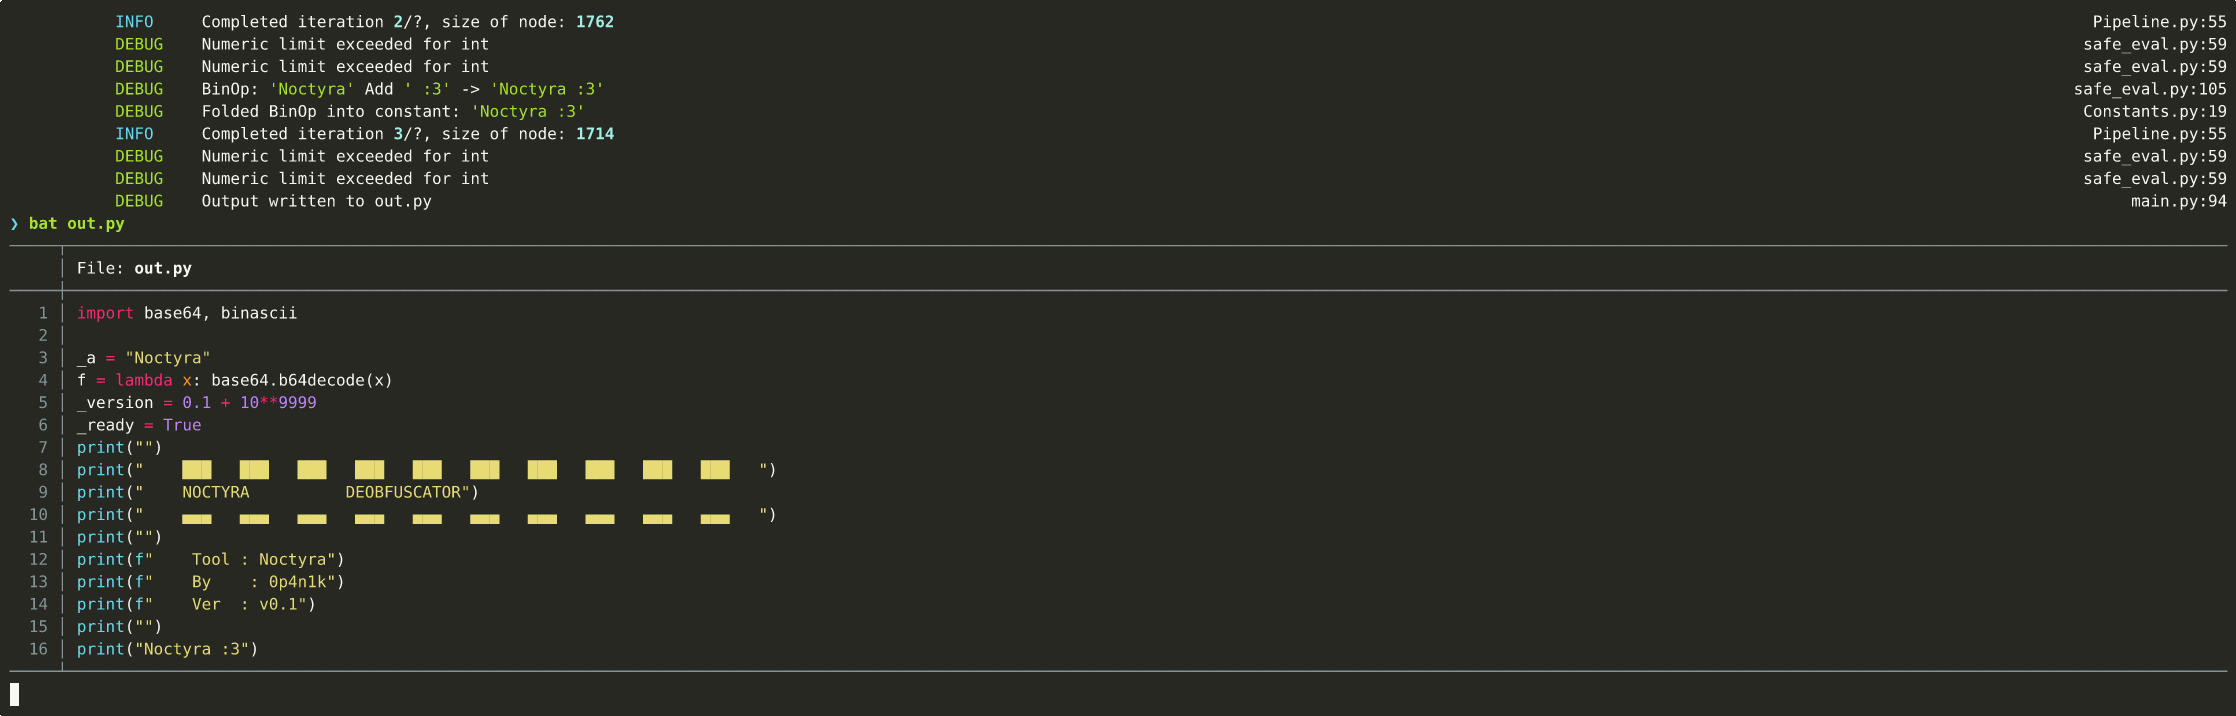 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
 ald3ns/copy-as-yara
This is a little plugin to copy disassembly in a way that is usable in YARA rules!