
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
125 results
DriverBuddy preview

DriverBuddy

GitHubnccgroup/driverbuddy

DriverBuddy is an IDA Python script to assist with the reverse engineering of Windows kernel drivers.
binary-analysisreverse-engineeringvulnerability-analysis
3837 years ago
SusanRTTI preview

SusanRTTI

GitHubnccgroup/susanrtti

Another RTTI Parsing IDA plugin
binary-analysisreverse-engineeringstatic-analysis+1
3123 years ago
ropr preview

ropr

GitHubben-lichtman/ropr

A blazing fast™ multithreaded ROP Gadget finder. ropper / ropgadget alternative (currently x86 only)
binary-analysisexploitationreverse-engineering+1
5556 months ago
REpsych preview

REpsych

GitHubbattelle/repsych

Psychological warfare in reverse engineering
binary-analysisreverse-engineeringsteganography
21010 years ago
lumina_server preview

lumina_server

GitHubsynacktiv/lumina_server

Local server for IDA Lumina feature
binary-analysisreverse-engineeringutilities-frameworks
1935 years ago
rhabdomancer preview

rhabdomancer

GitHub0xdea/rhabdomancer

Vulnerability research assistant that locates calls to potentially insecure API functions in a binary file.

binary-analysisreverse-engineeringstatic-analysis+1
13117h 38m ago
haruspex preview

haruspex

GitHub0xdea/haruspex

Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
binary-analysisreverse-engineeringstatic-code-analysis+1
1311 day ago
ghidra-evm preview

ghidra-evm

GitHubadelapie/ghidra-evm

Ghidra module for disassembling, decompiling, and analyzing Ethereum smart contract bytecode. Detects insecure instructions, extracts hidden methods,…
binary-analysisreverse-engineeringstatic-analysis+1
1495 years ago
IDBs preview

IDBs

GitHubrolfrolles/idbs

Analyses in IDA/Hex-Rays

binary-analysisreverse-engineeringstatic-analysis
873 years ago
pocs_slides preview

pocs_slides

GitHubcq674350529/pocs_slides

my advisory, poc, slides and scripts related to IoT/protocol security
binary-analysisexploitationiot-security+4
711 year ago
KasperMeow preview

KasperMeow

GitHubmein-0/kaspermeow

Proof-of-concept that exploits a Kaspersky driver vulnerability to leak kernel pointers and bypass KASLR on Windows, enabling kernel exploit chain…
binary-analysisexploitationreverse-engineering+1
151 month ago
xfg_analyzer preview

xfg_analyzer

GitHubea/xfg_analyzer

A Binary Ninja plugin that uses bruteforced XFG hashes to recover precise function prototypes
binary-analysisreverse-engineeringstatic-analysis
162 years ago
pdbdownload preview

pdbdownload

GitHubp0dalirius/pdbdownload

An utility to download PDB files associated with a Portable Executable (PE).
binary-analysisreverse-engineeringutilities-frameworks
191 year ago
Decompiler_Tools preview

Decompiler_Tools

GitHubjas502n/decompiler_tools

Tools

binary-analysisreverse-engineeringstatic-code-analysis
86 years ago
CVE-2026-0073-Research preview

CVE-2026-0073-Research

GitHubnovaek/cve-2026-0073-research

CVE-2026-0073 is an RCE with a CVSS severity score of 8.3, and here we will explain how it works.
binary-analysisexploitationreverse-engineering+2
56 months ago
CVE-2023-36900 preview

CVE-2023-36900

GitHubromanrybachek/cve-2023-36900

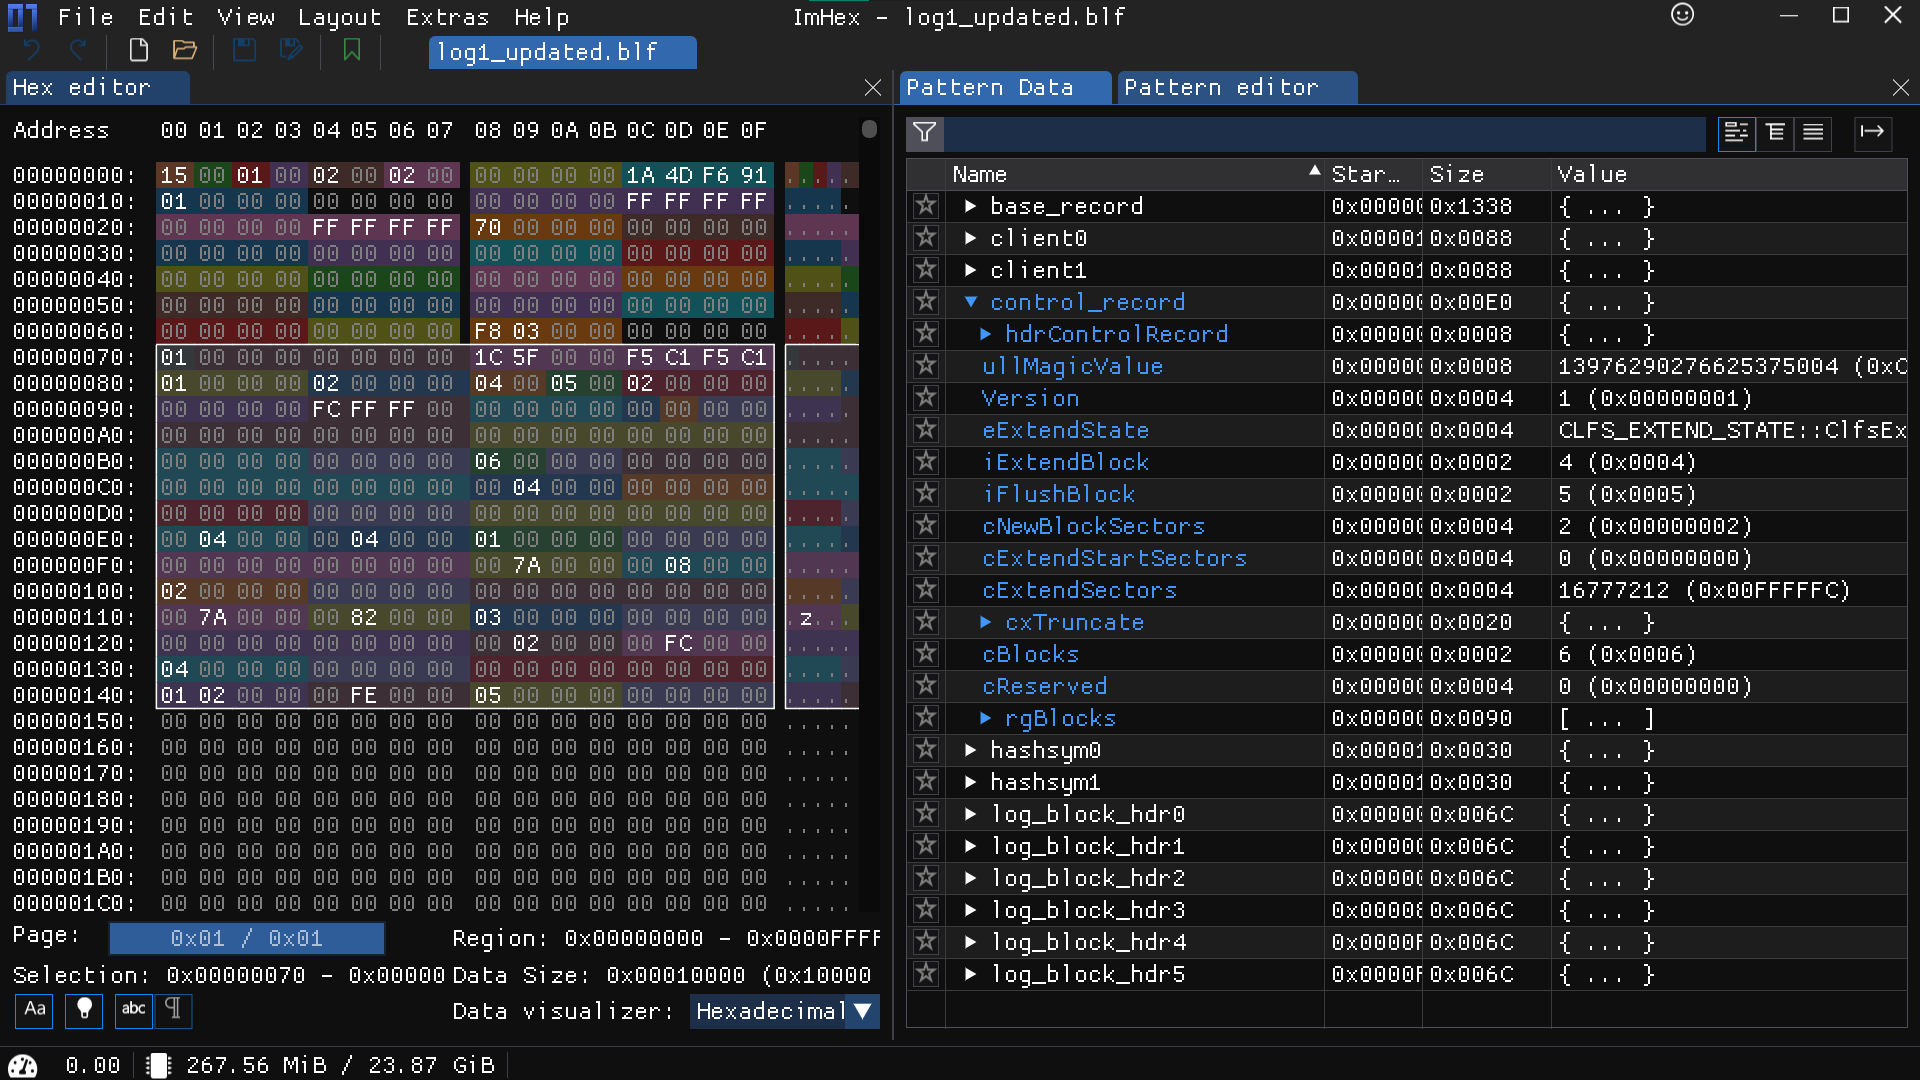
Denial-of-Service PoC | Writeup | Header with CLFS structures | Imhex pattern for .blf extension
binary-analysisexploitationreverse-engineering+1
42 years ago
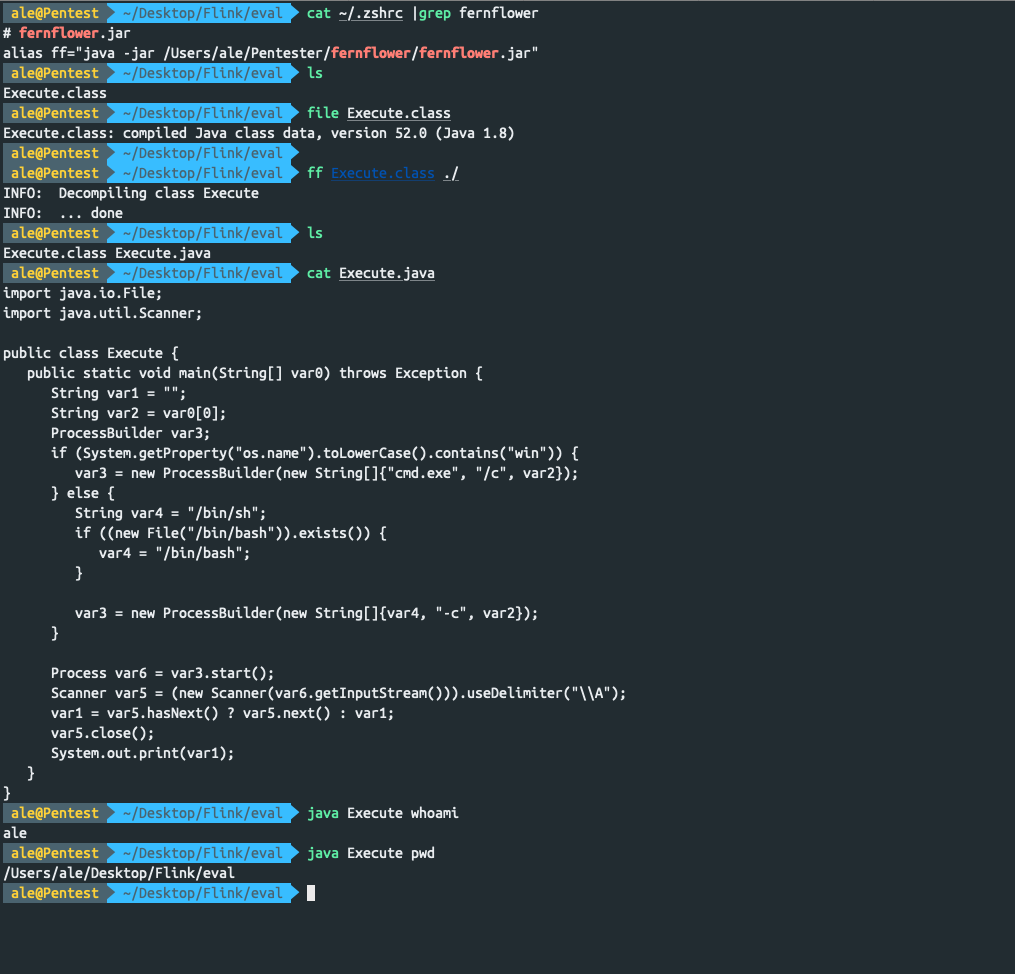
fernflower preview

fernflower

GitHubjas502n/fernflower

快速在终端反编译class文件

binary-analysisreverse-engineeringstatic-analysis
56 years ago
Previous1234567Next