autofs-cve-2026-84568
 jvidhan/autofs-cve-2026-84568
Reverse engineering notes and working PoC for CVE-2026-84568, a macOS automountd trust-boundary violation allowing mounts from localhost or the…
binary-analysiseducationexploitation+4
jvidhan/autofs-cve-2026-84568Reverse engineering notes and working PoC for CVE-2026-84568, a macOS automountd trust-boundary violation allowing mounts from localhost or the…
 das-labor/panopticon
A libre cross-platform disassembler.
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 boschresearch/gdbfuzz
Fuzzing Embedded Systems using Hardware Breakpoints
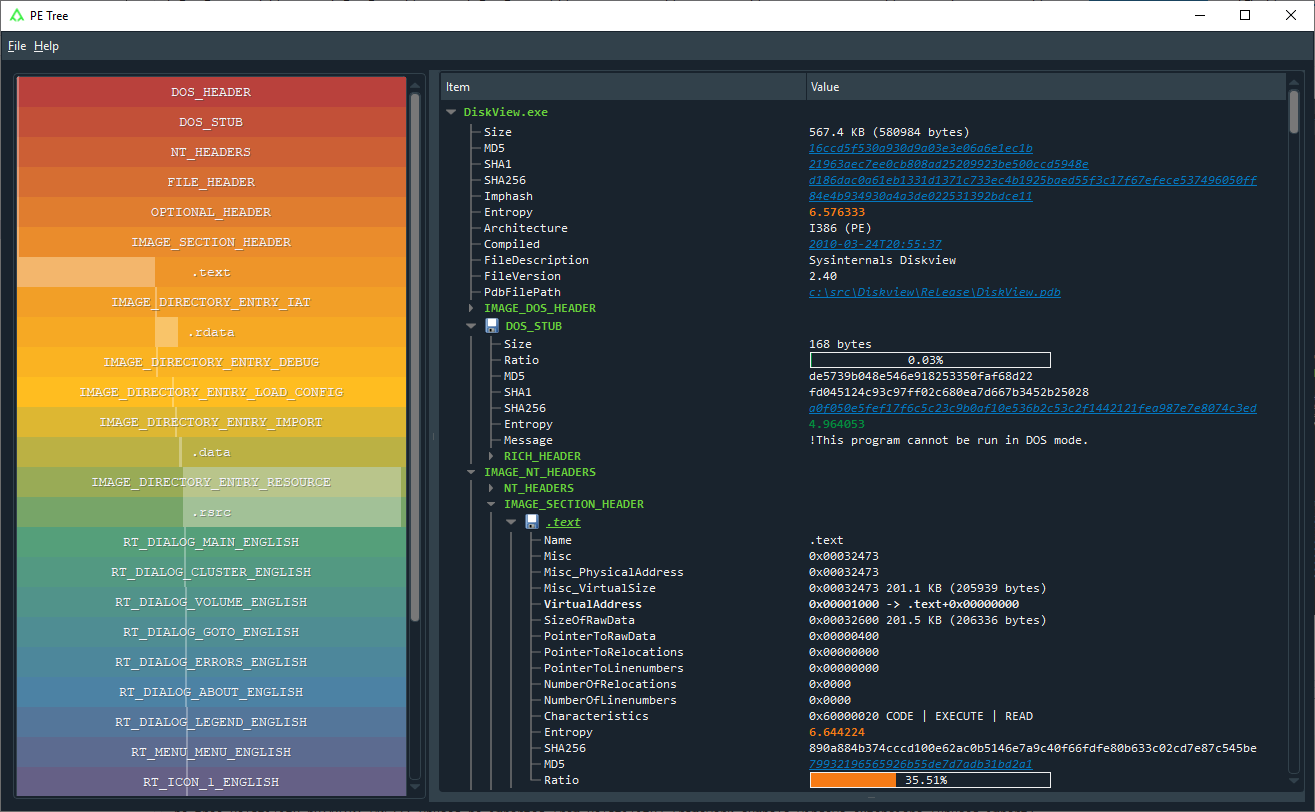 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 abhi-r3v0/adhrit
Android Security Suite for in-depth reconnaissance and static bytecode analysis based on Ghera benchmarks.
 egorrsp/cve-2020-15368-asrdrv103-research
Reverse engineering research of ASRock AsrDrv103.sys (CVE-2020-15368), covering its driver interface, encrypted request protocol, and privileged…
 whoami-012/cve-2026-96515
Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
 gmh5225/fracture-
🐈⬛ WIP Suite for reverse engineering JVM applications
 revng/revng-c
Core binary-lifting library that translates executable code to LLVM IR and reconstructs C-like source for reverse engineering and automated binary…
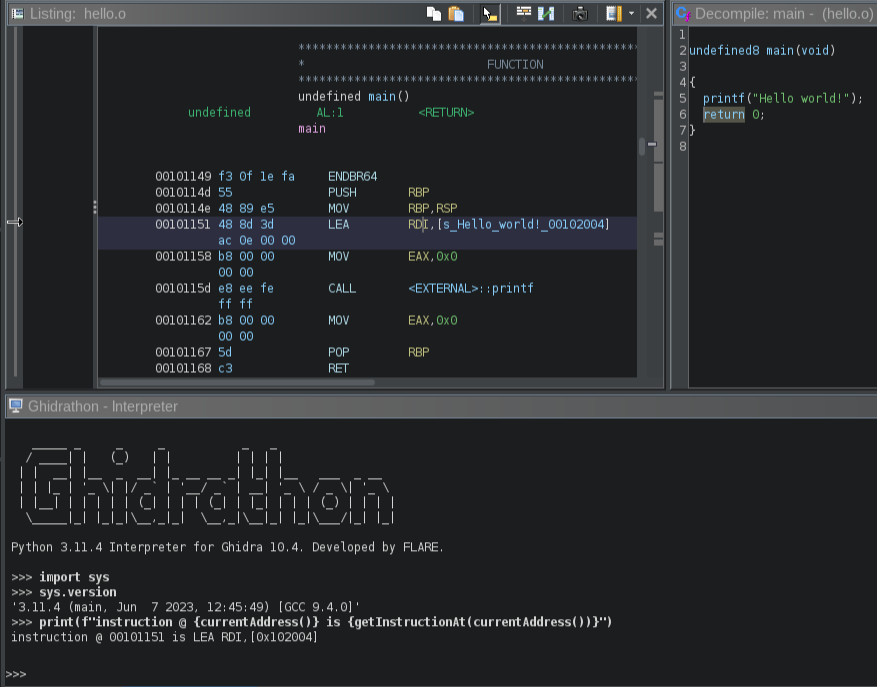 mandiant/ghidrathon
The FLARE team's open-source extension to add Python 3 scripting to Ghidra.
 mrakovic-org/nashavm
Nasha is a Virtual Machine for .NET files and its runtime was made in C++/CLI
 jvidhan/cve-2026-43687
Reverse engineering notes and a self-contained PoC for the macOS NFS client access-cache race (CVE-2026-43687), with kext disassembly diff and dtrace…
 googleprojectzero/brokentype
TrueType and OpenType font fuzzing toolset
 didi/kemon
An Open-Source Pre and Post Callback-Based Framework for macOS Kernel Monitoring.
 hugsy/recon_2024_windbg_workshop
Workshop materials for mastering WinDbg debugging in kernel and user mode, with KdNet setup, demos, and a Time Travel Debugging challenge for binary…
 sonyxperiadev/apkanalyser
Static analysis tool for Android APKs that inspects Dalvik bytecode, decodes XML resources, and detects potential issues. Supports binary…