

PyMemoryEditor
 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
binary-analysisdebuggerseducation+3
226
jeanextreme002/pymemoryeditorA pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
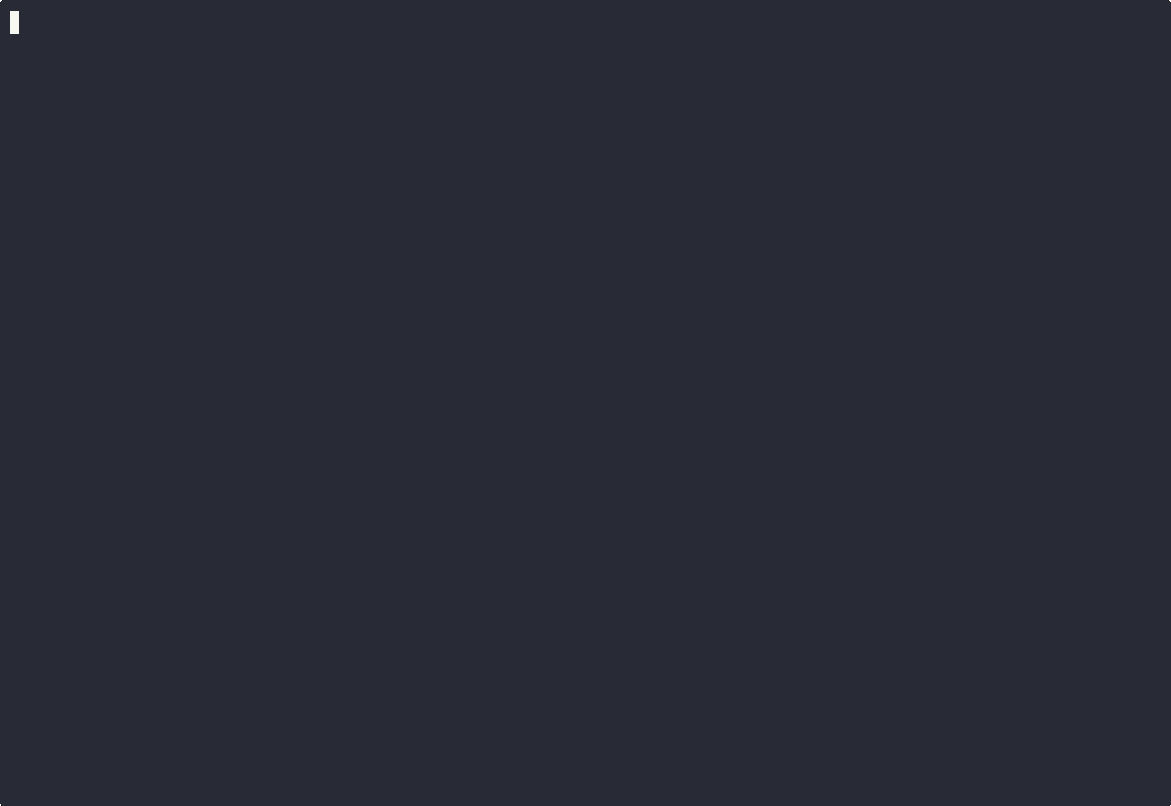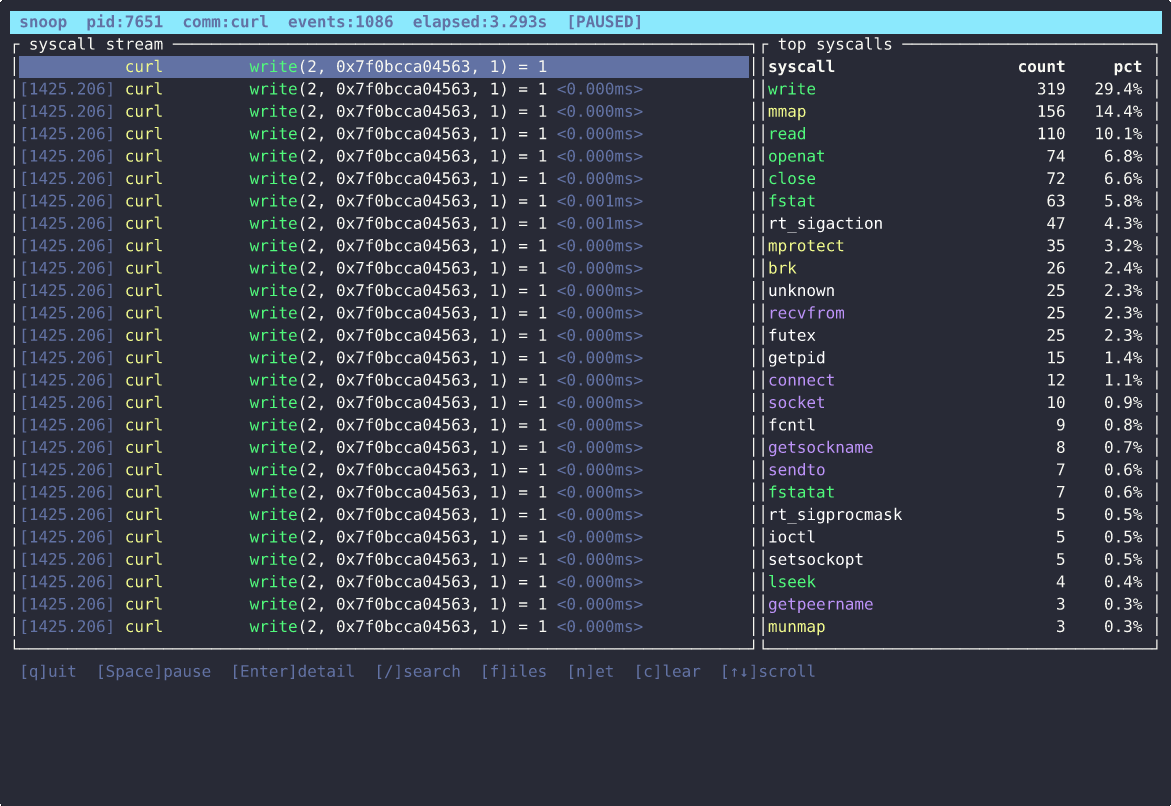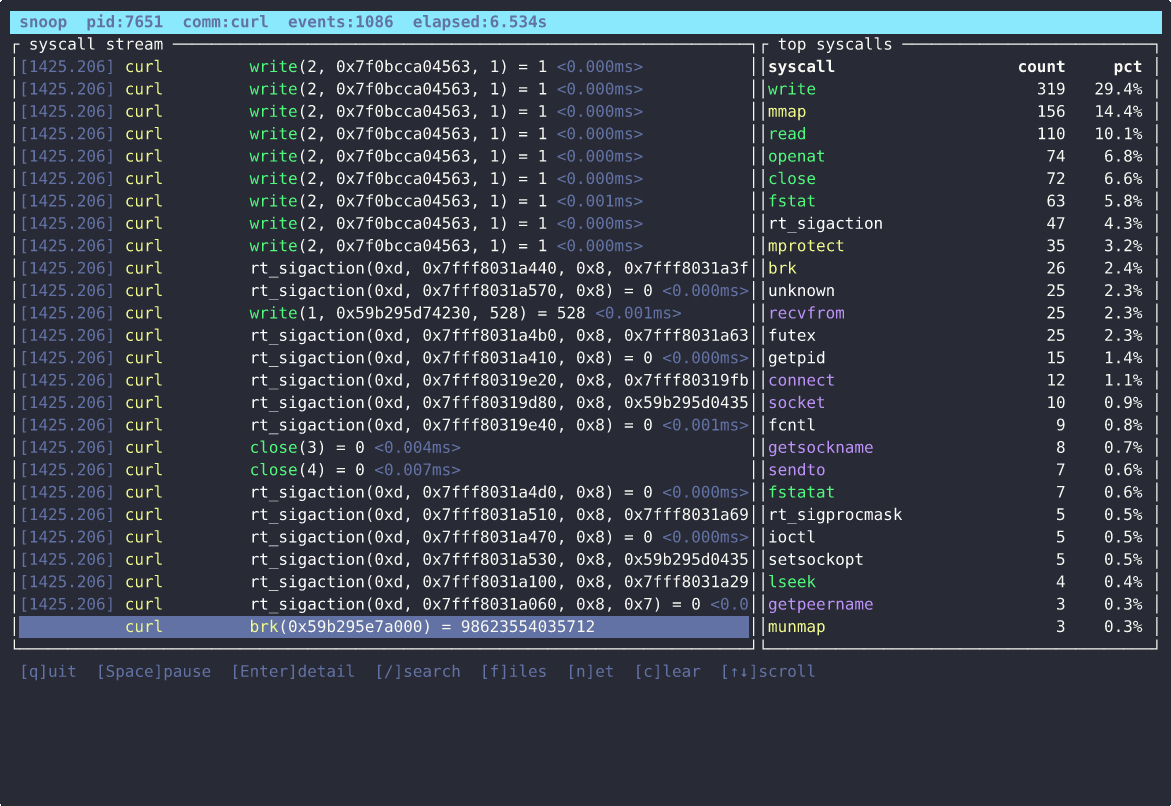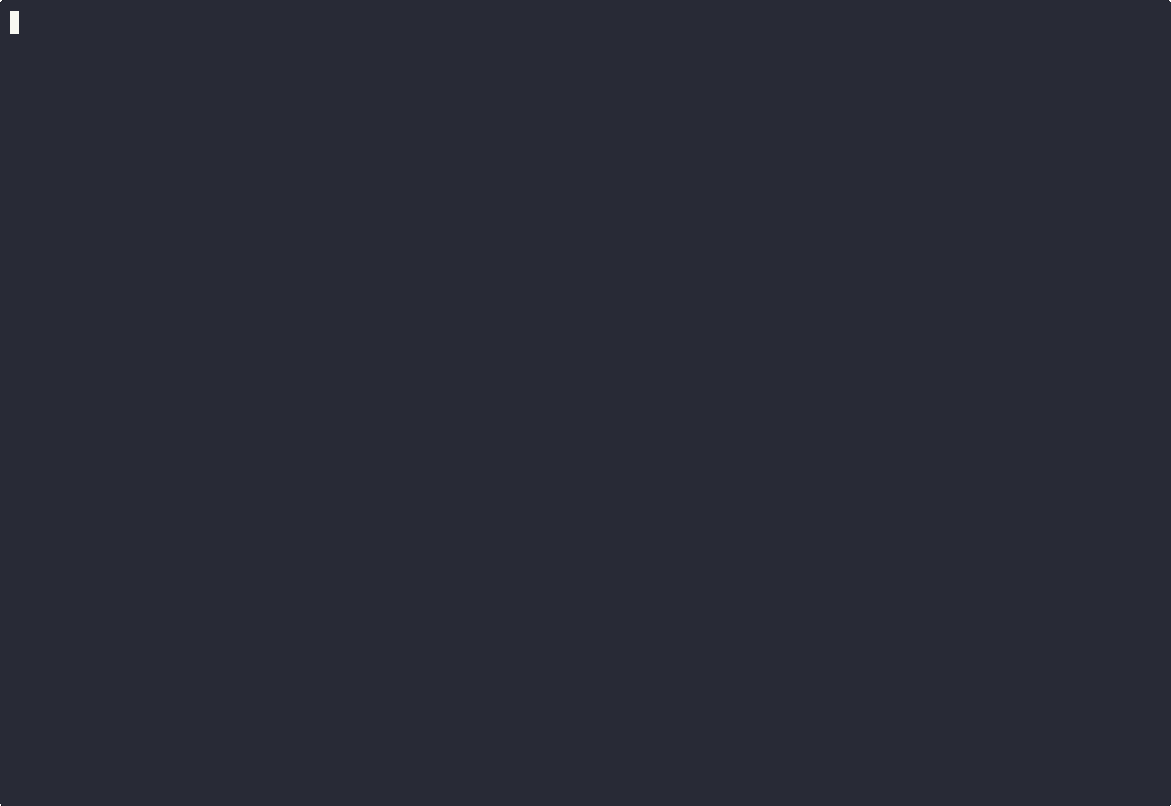 pandaadir05/snoop
A modern syscall tracer built on eBPF. Think strace, but with a real TUI, smart filters, TLS decryption, and output that's actually readable.
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework

 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
 nccgroup/triforceafl
AFL/QEMU fuzzing with full-system emulation.
 gjduck/e9patch
A powerful static binary rewriting tool
 volatilityfoundation/dwarf2json
convert ELF/DWARF symbol and type information into vol3's intermediate JSON
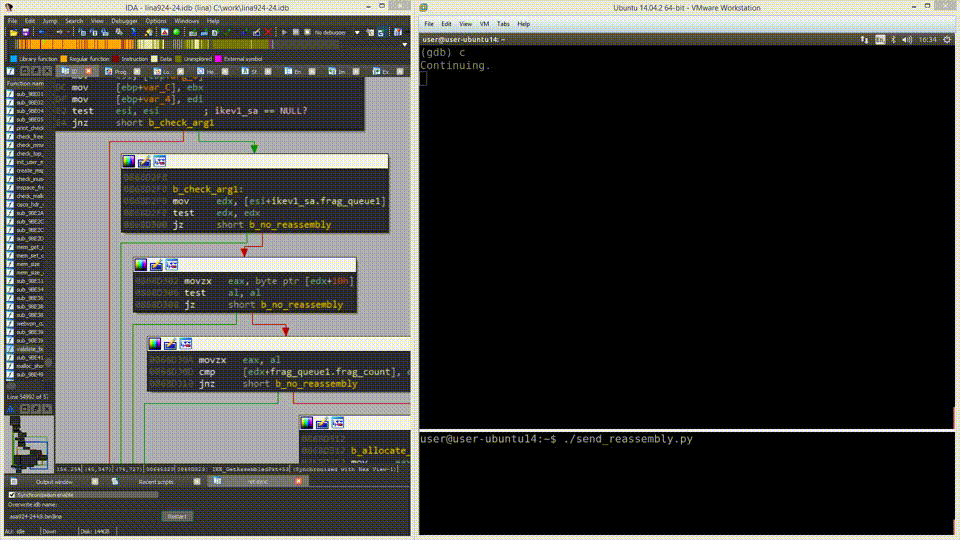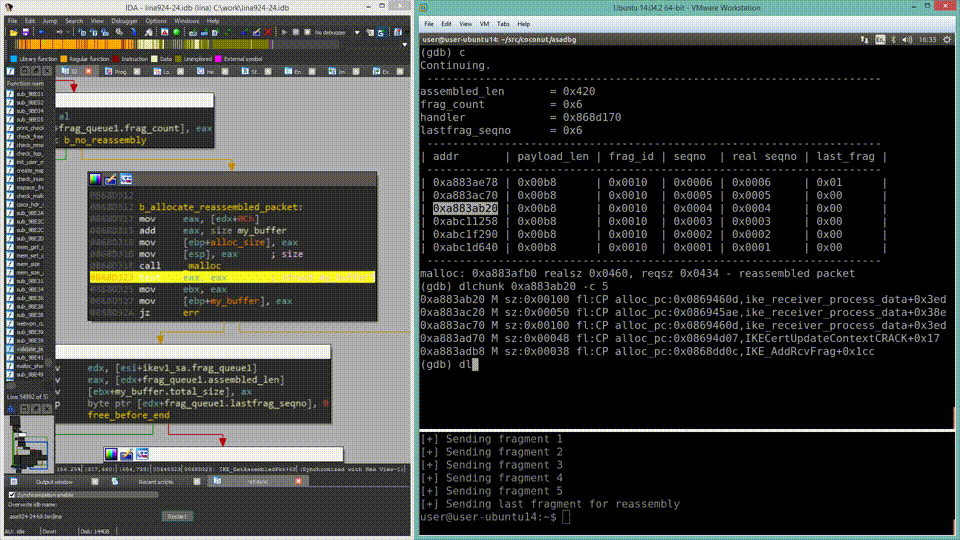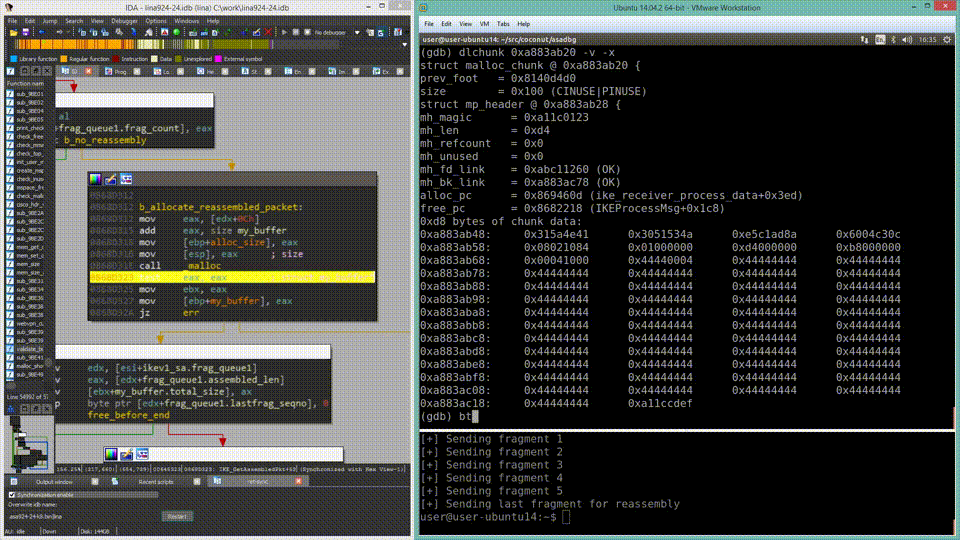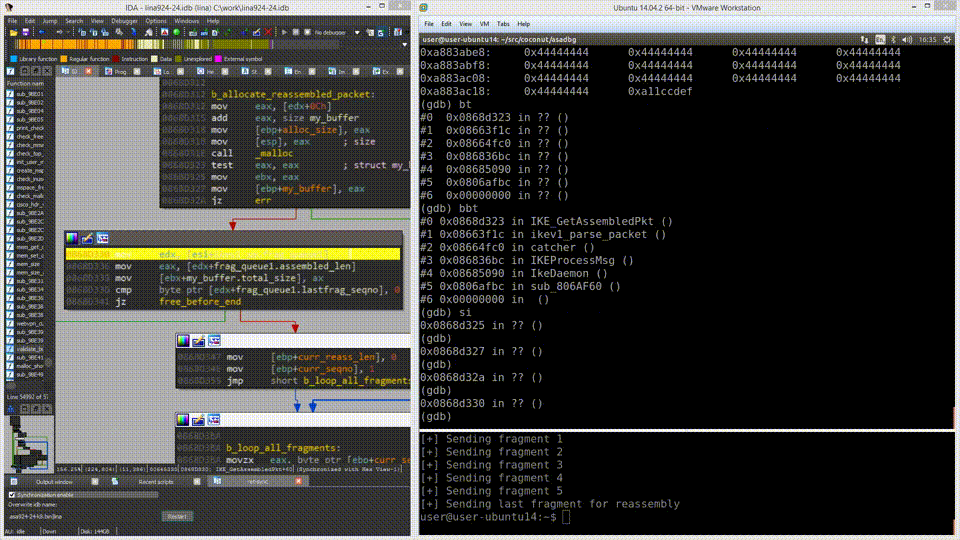 nccgroup/asadbg
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices
 cpkt9762/ida-cli
Headless IDA Pro MCP server for AI-assisted binary analysis, powered by idalib
 metrodango/pip3line
Swiss Army knife for raw bytes manipulation & interception
 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 vvirei333/abrake27
iOS 27 kernelcache RE: SEP dispatch map, AMFI diff, Ghidra workflow
 knight0x07/bibi-windows-wiper-analysis
Technical Analysis of Bibi-Windows Wiper Targeting Israeli Organizations
 tekkenbugattii/linusware-source-code-internal
Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…
 runtimeverification/kernel-c-to-rust-spike
Hardening kernel C parsers via Rust rewrite + differential fuzzing + formal verification. First target: UVC (CVE-2024-53104).