
python-decompile3
 rocky/python-decompile3
Python decompiler for 3.7-3.8 Stripped down from uncompyle6 so we can refactor and start to fix up some long-standing problems
binary-analysisdebuggerseducation+3
1.3k
rocky/python-decompile3Python decompiler for 3.7-3.8 Stripped down from uncompyle6 so we can refactor and start to fix up some long-standing problems
 hasherezade/tiny_tracer
Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
 sentinel-one/cobaltstrikeparser
Python parser for extracting CobaltStrike Beacon configurations from PE files, memory dumps, and C2 URLs using heuristic XOR decryption and…
 jackofmosttrades/gadgetinspector
A byte code analyzer for finding deserialization gadget chains in Java applications
 bats3c/darkloadlibrary
LoadLibrary for offensive operations
 grammatech/ddisasm
Datalog-based disassembler producing reassemblable assembly from ELF/PE binaries, with GTIRB intermediate representation for binary analysis and…
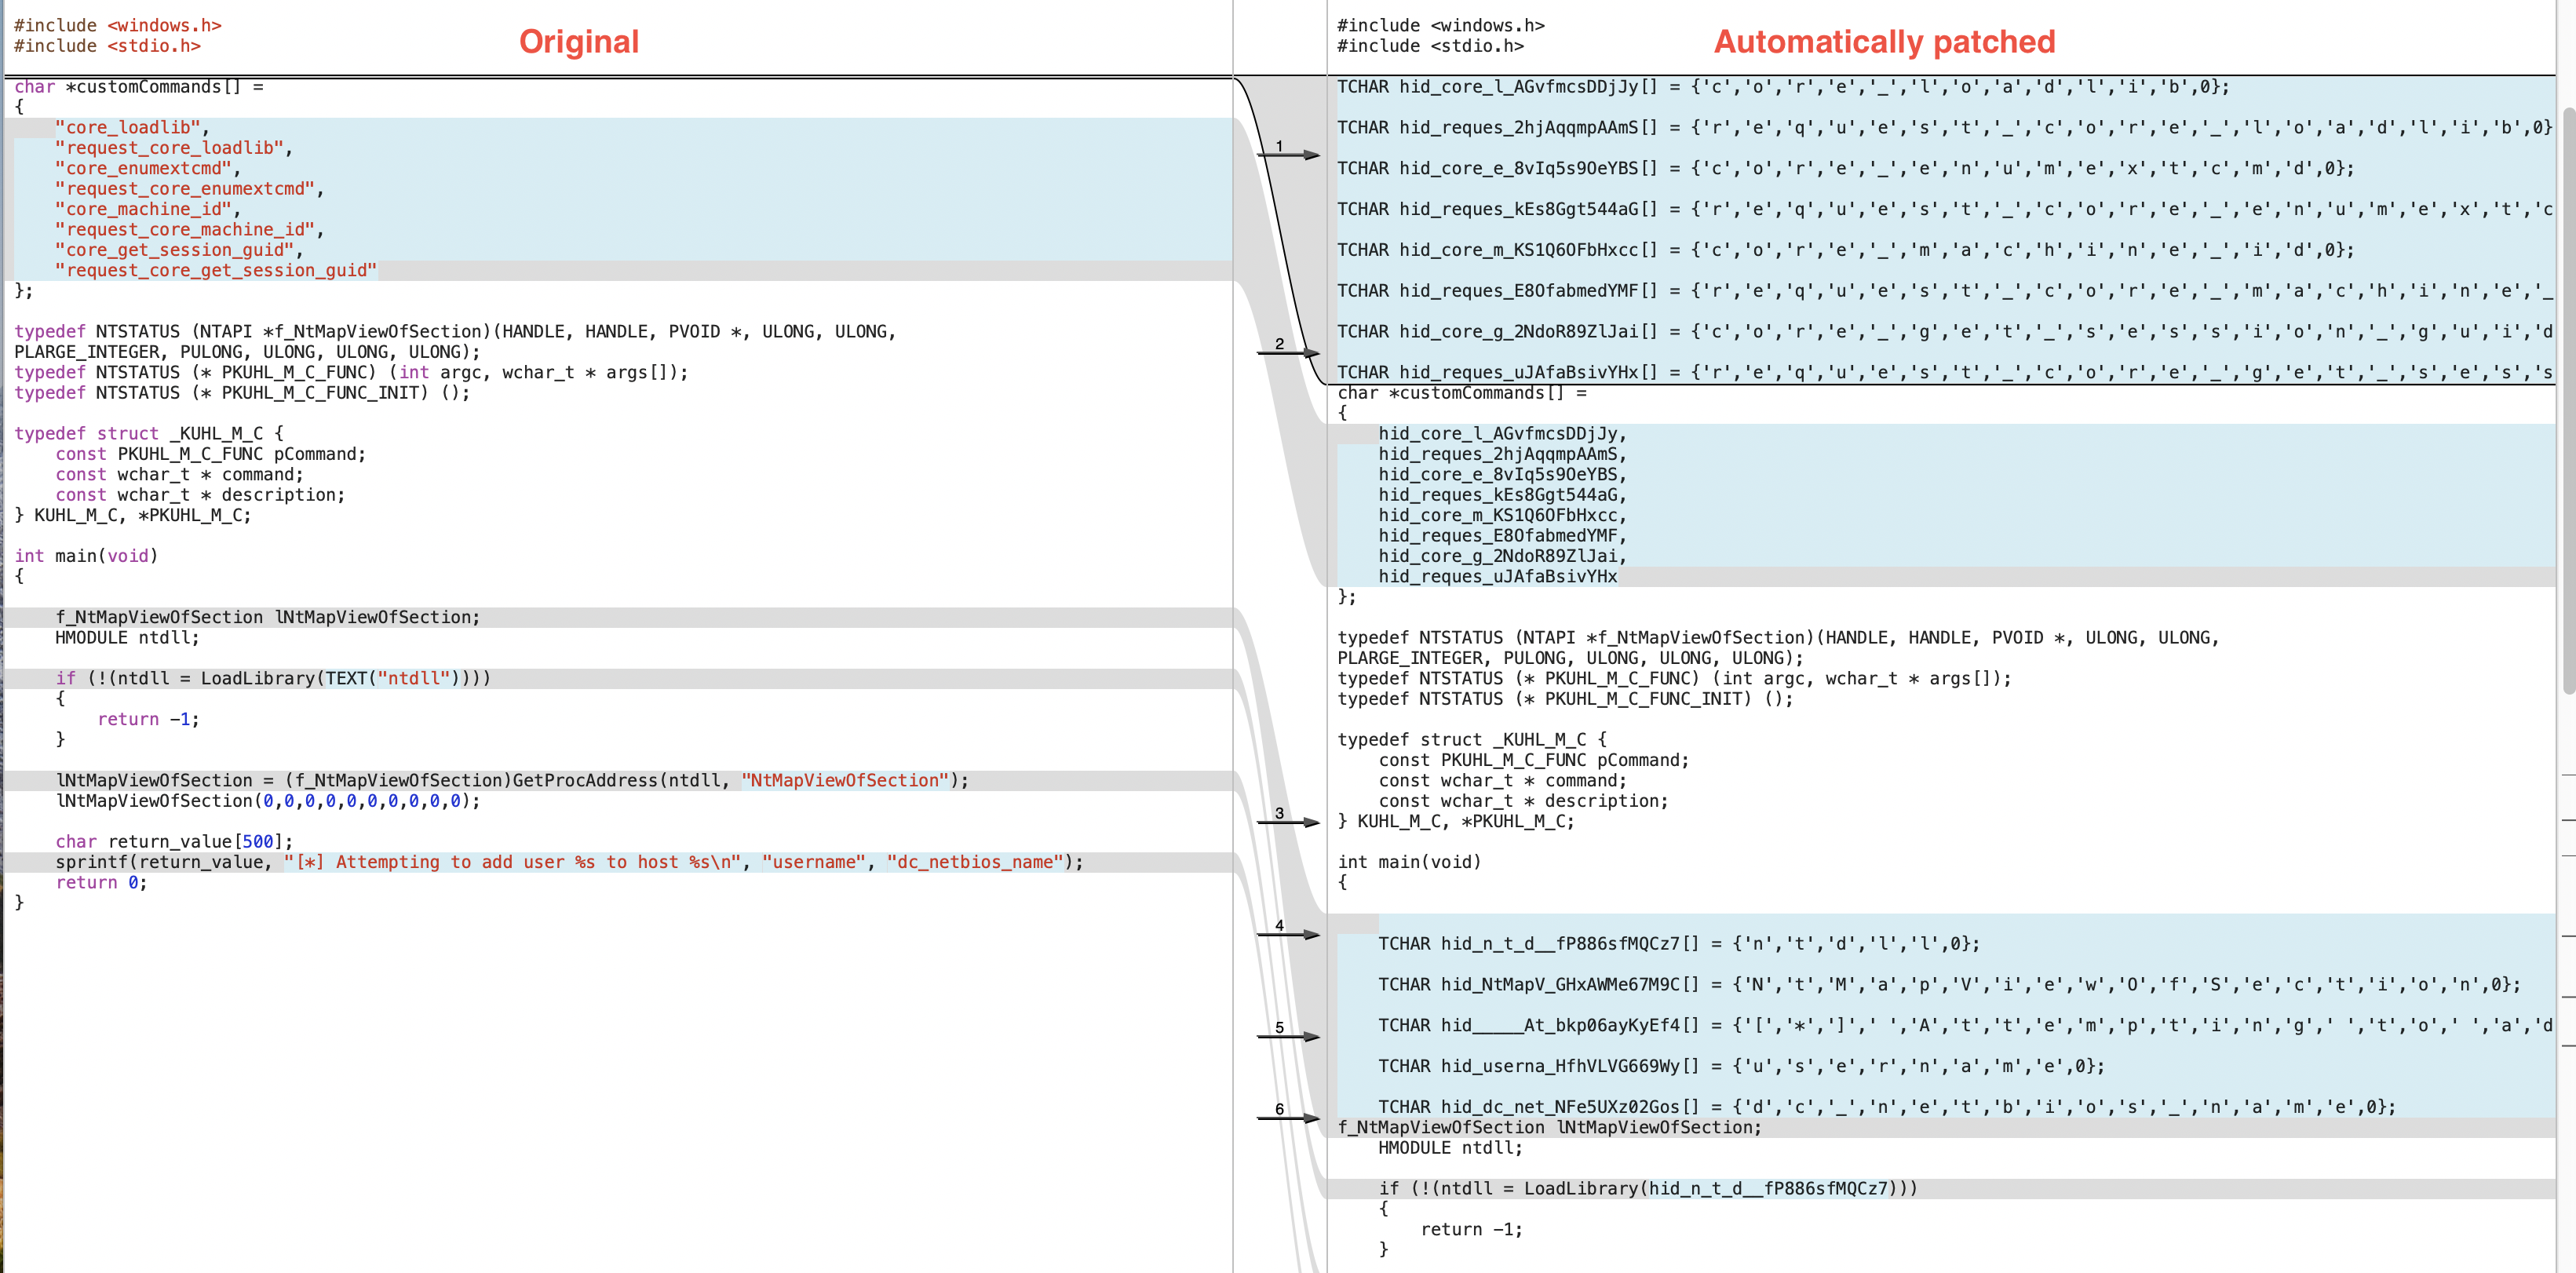 scrt/avcleaner
C/C++ source obfuscator for antivirus bypass
 ergrelet/unlicense
Dynamic unpacker and import fixer for Themida/WinLicense 2.x and 3.x.
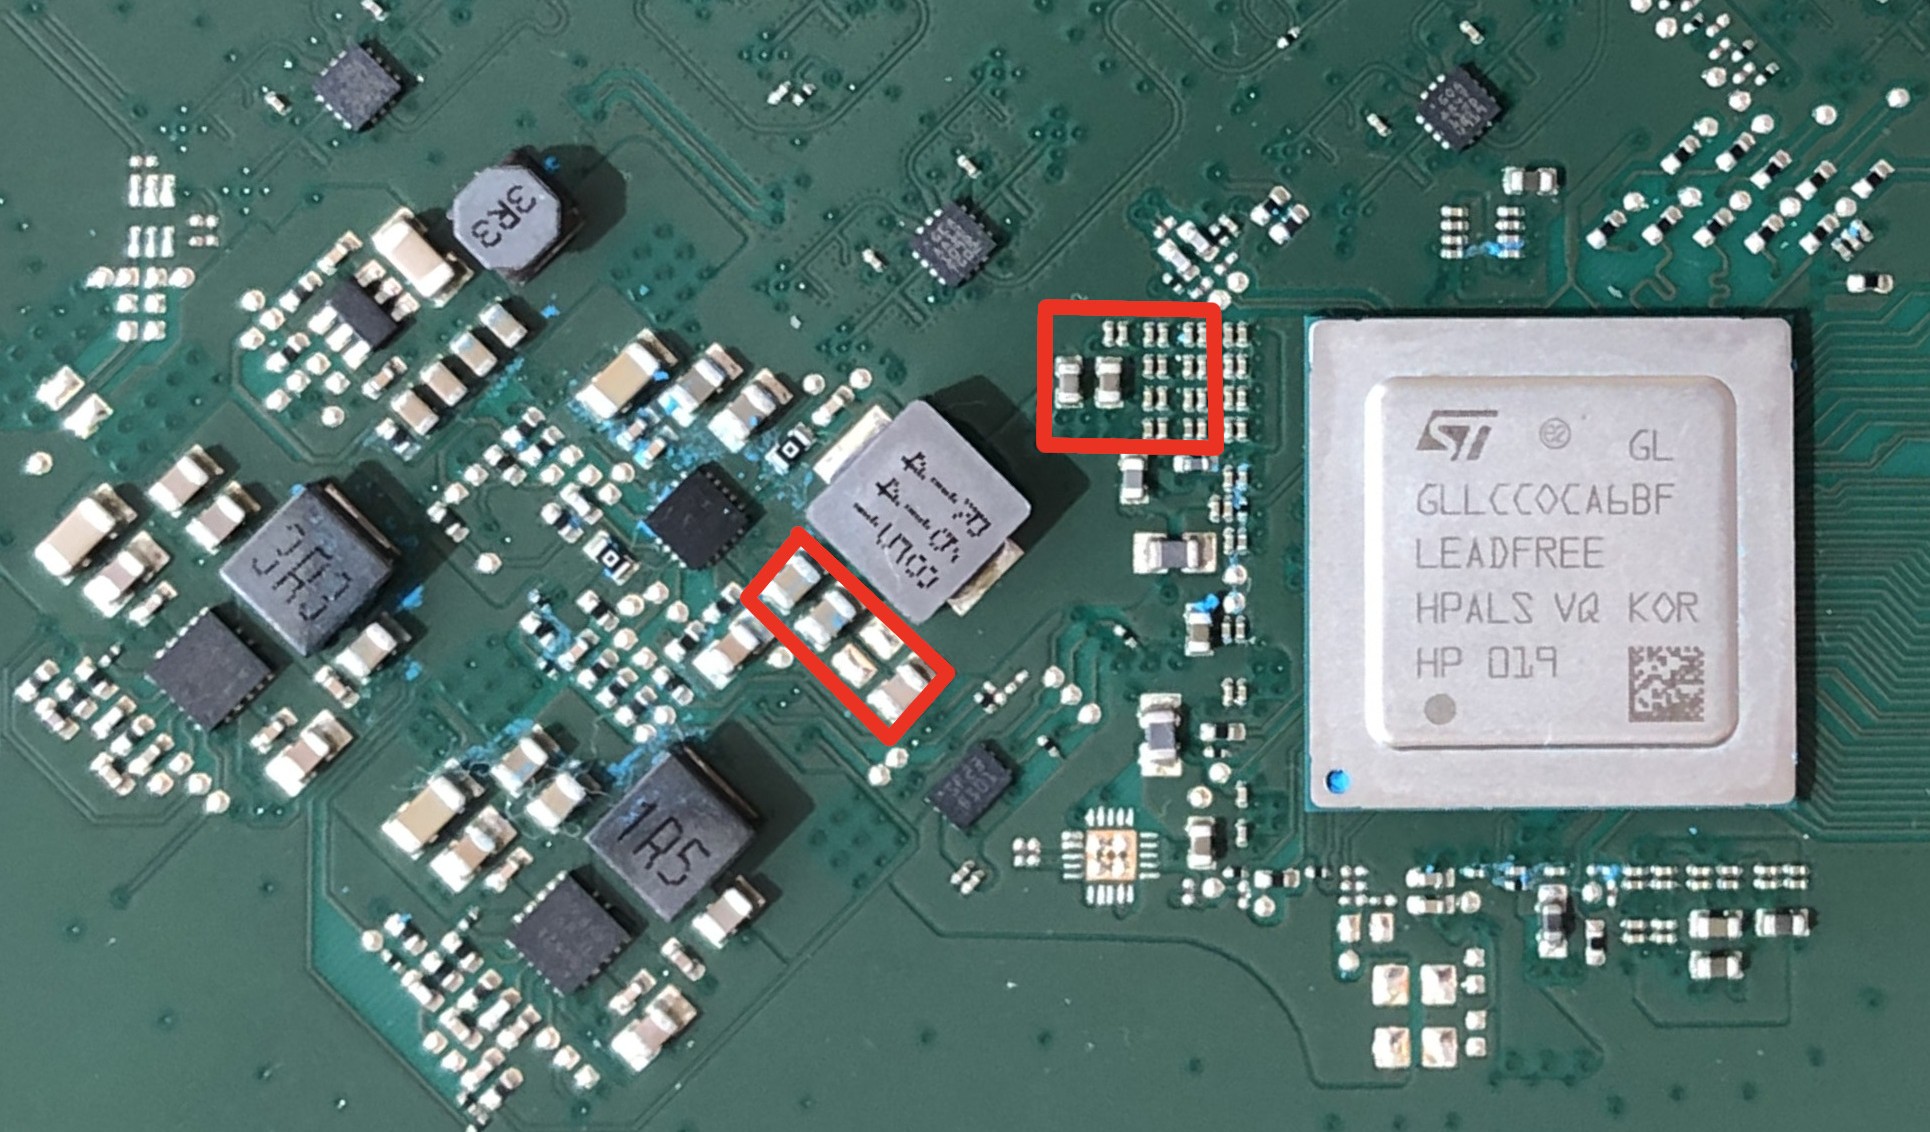 kuleuven-cosic/starlink-fi
Voltage fault-injection modchip for black-box security evaluation of Starlink terminals, bypassing bootloader signature verification to execute…
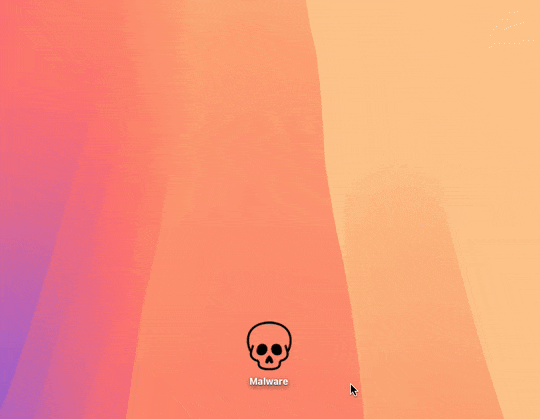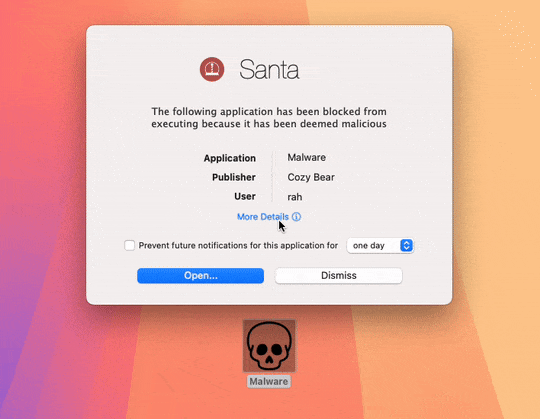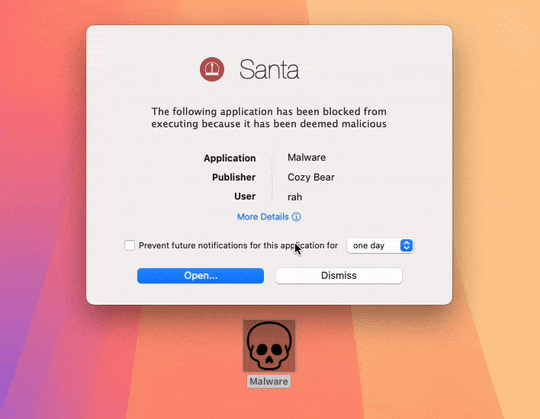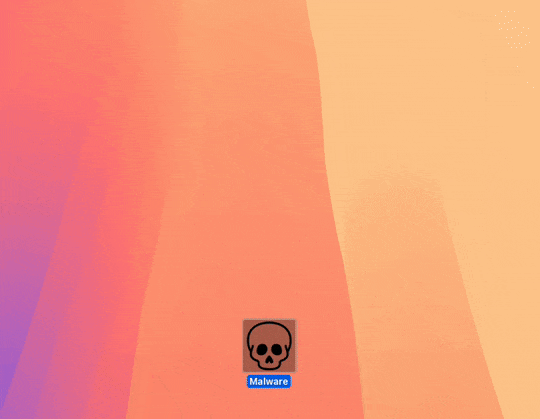 northpolesec/santa
A binary and file access authorization system for macOS.
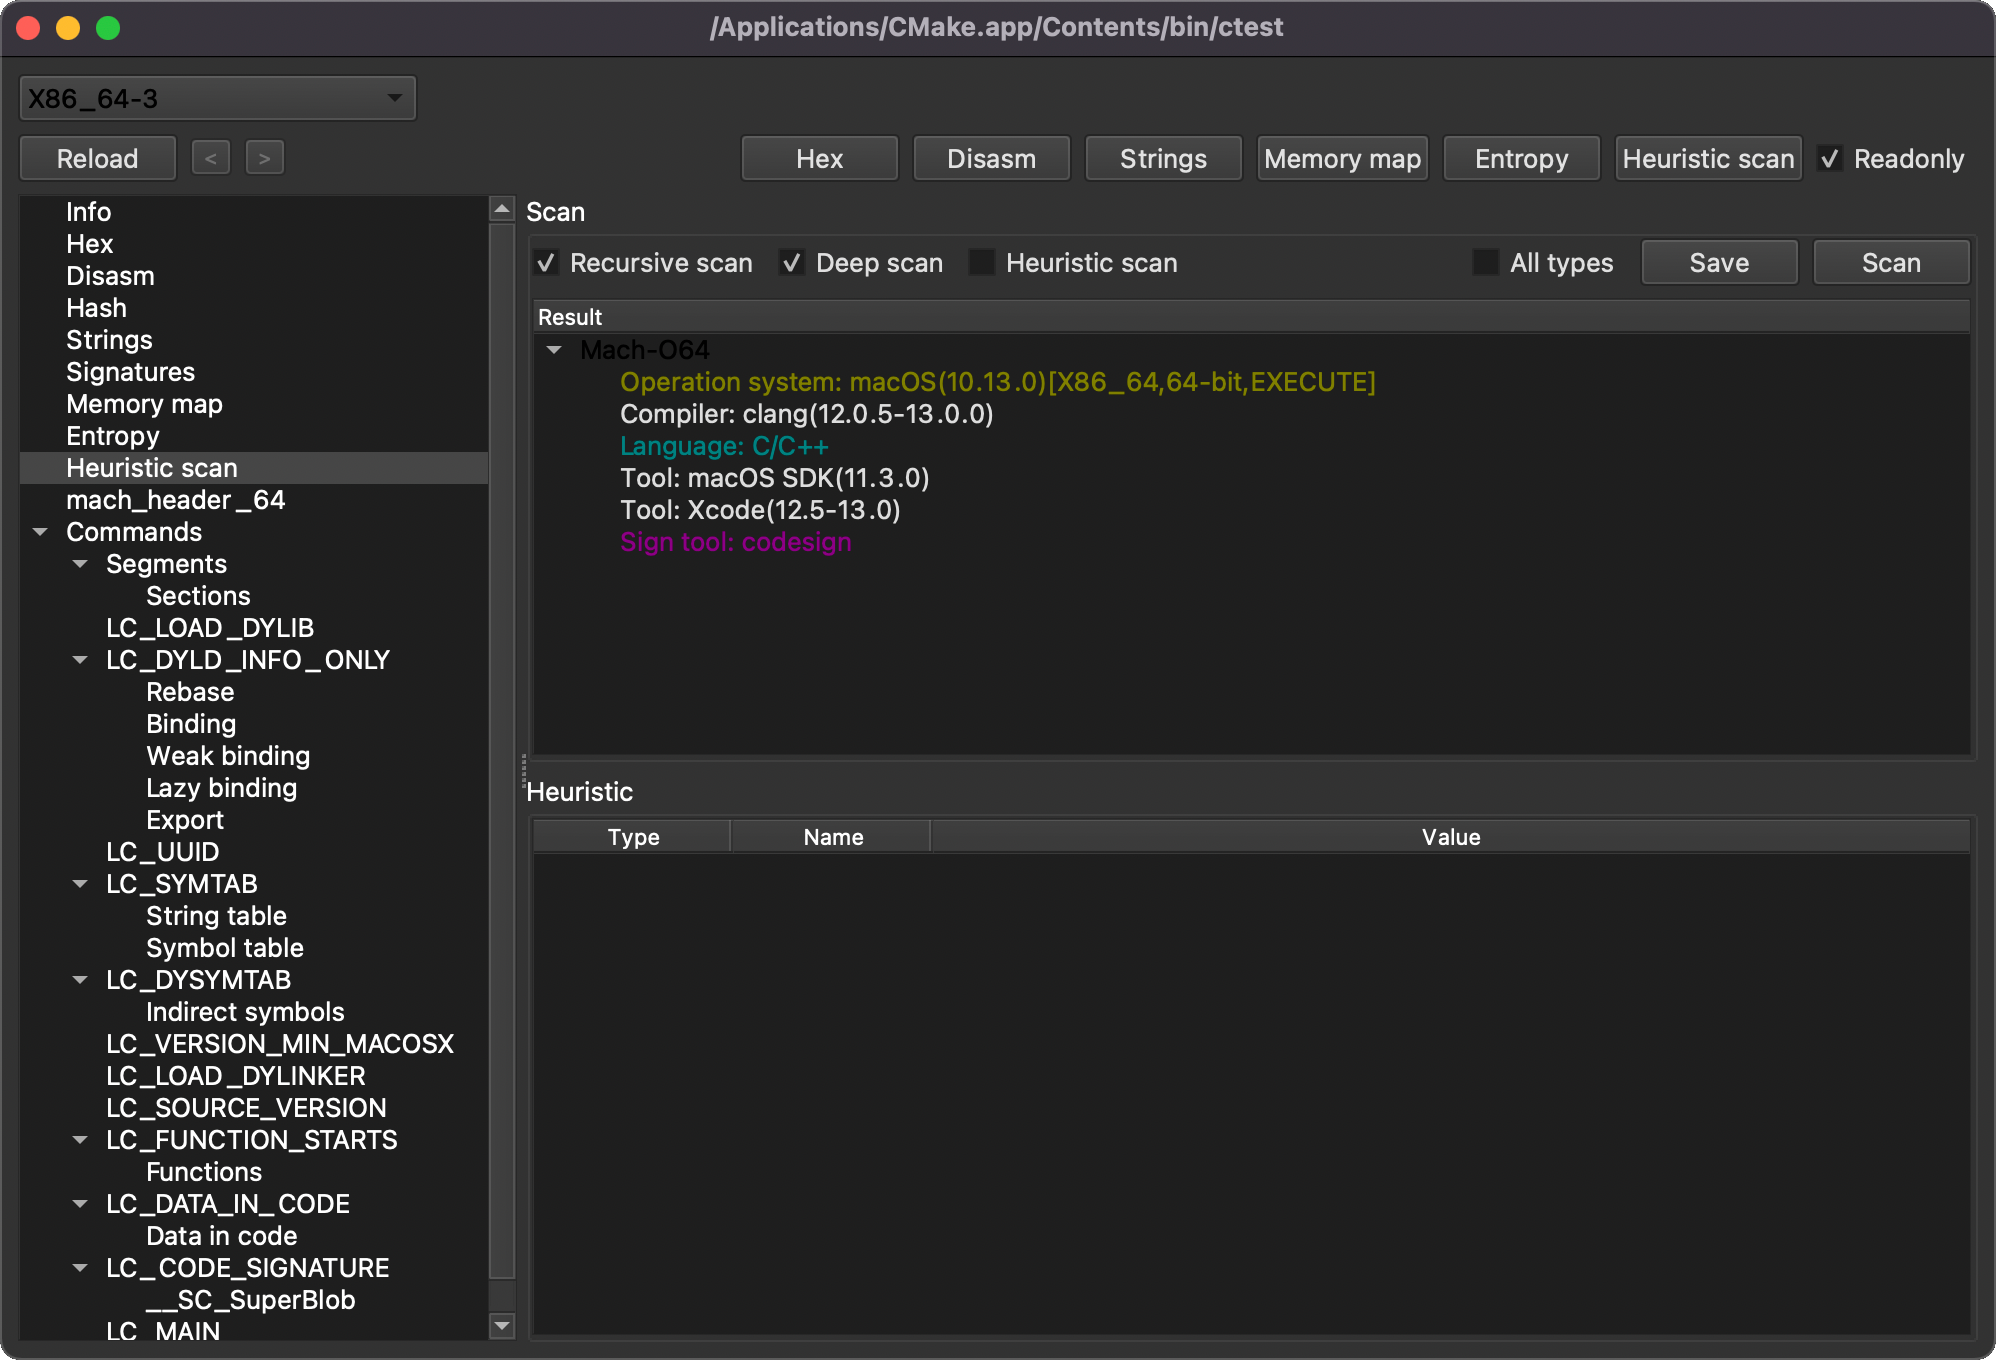 horsicq/xmachoviewer
XMachOViewer is a Mach-O viewer for Windows, Linux and MacOS
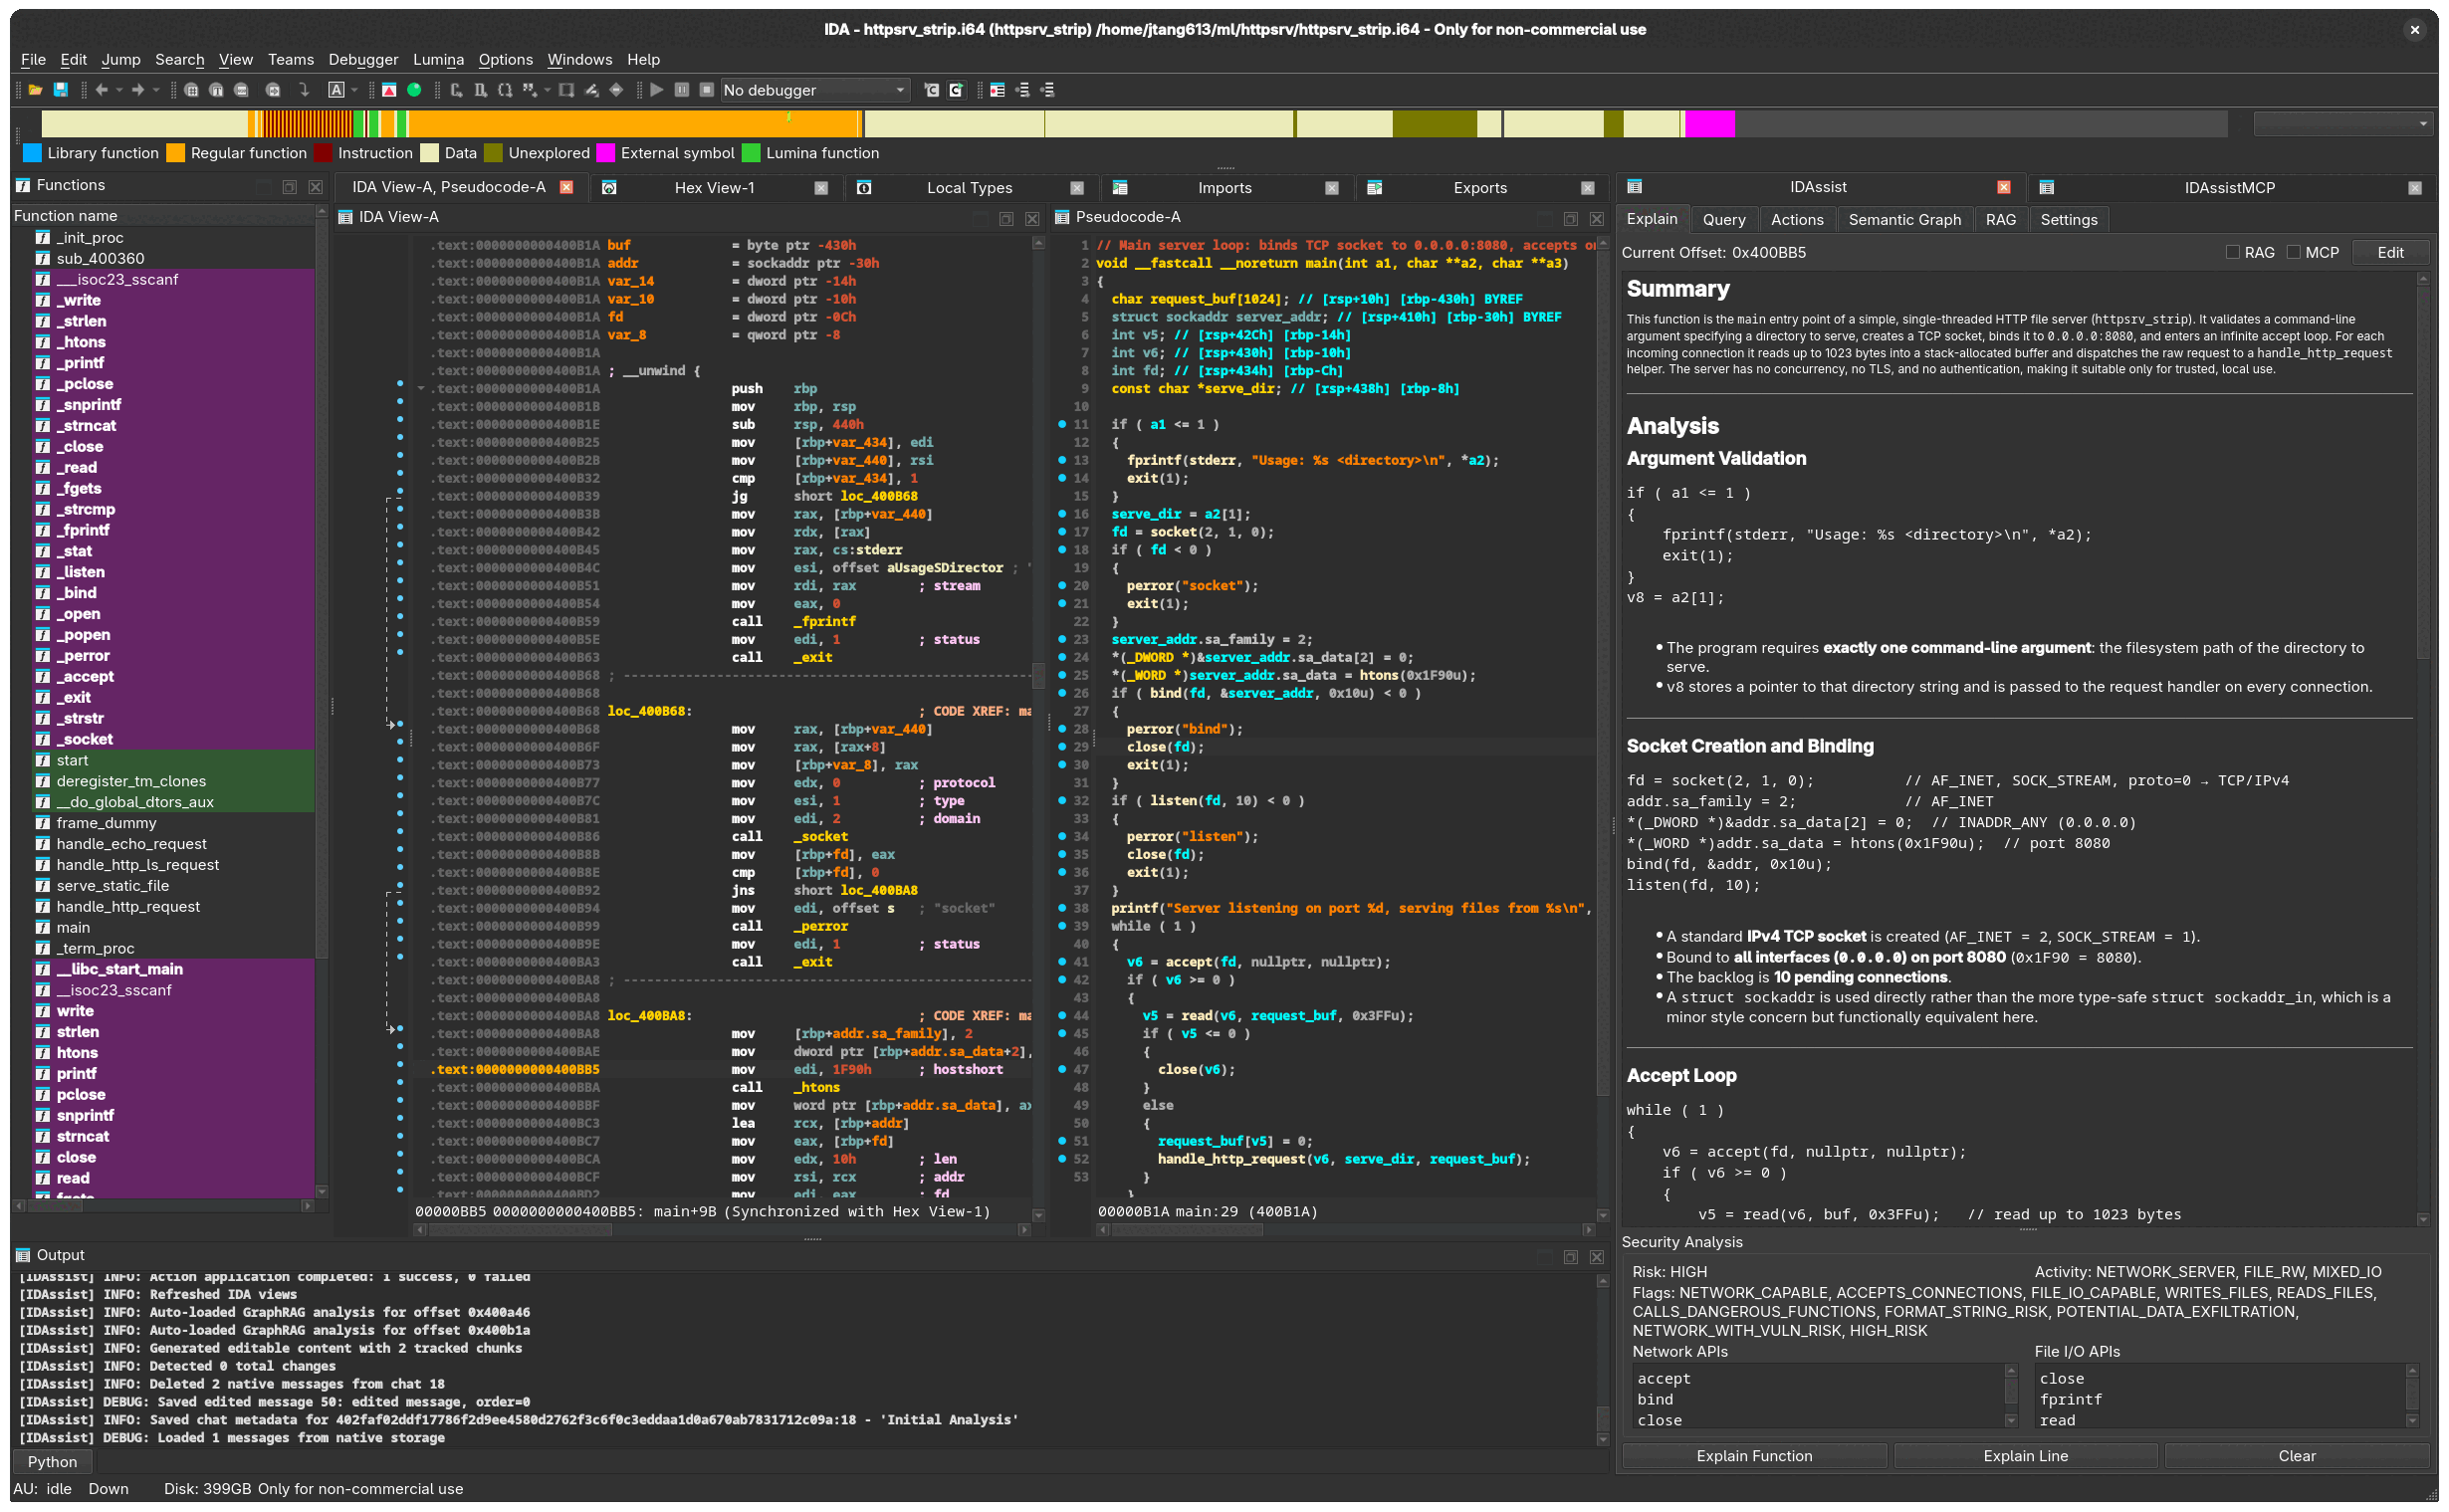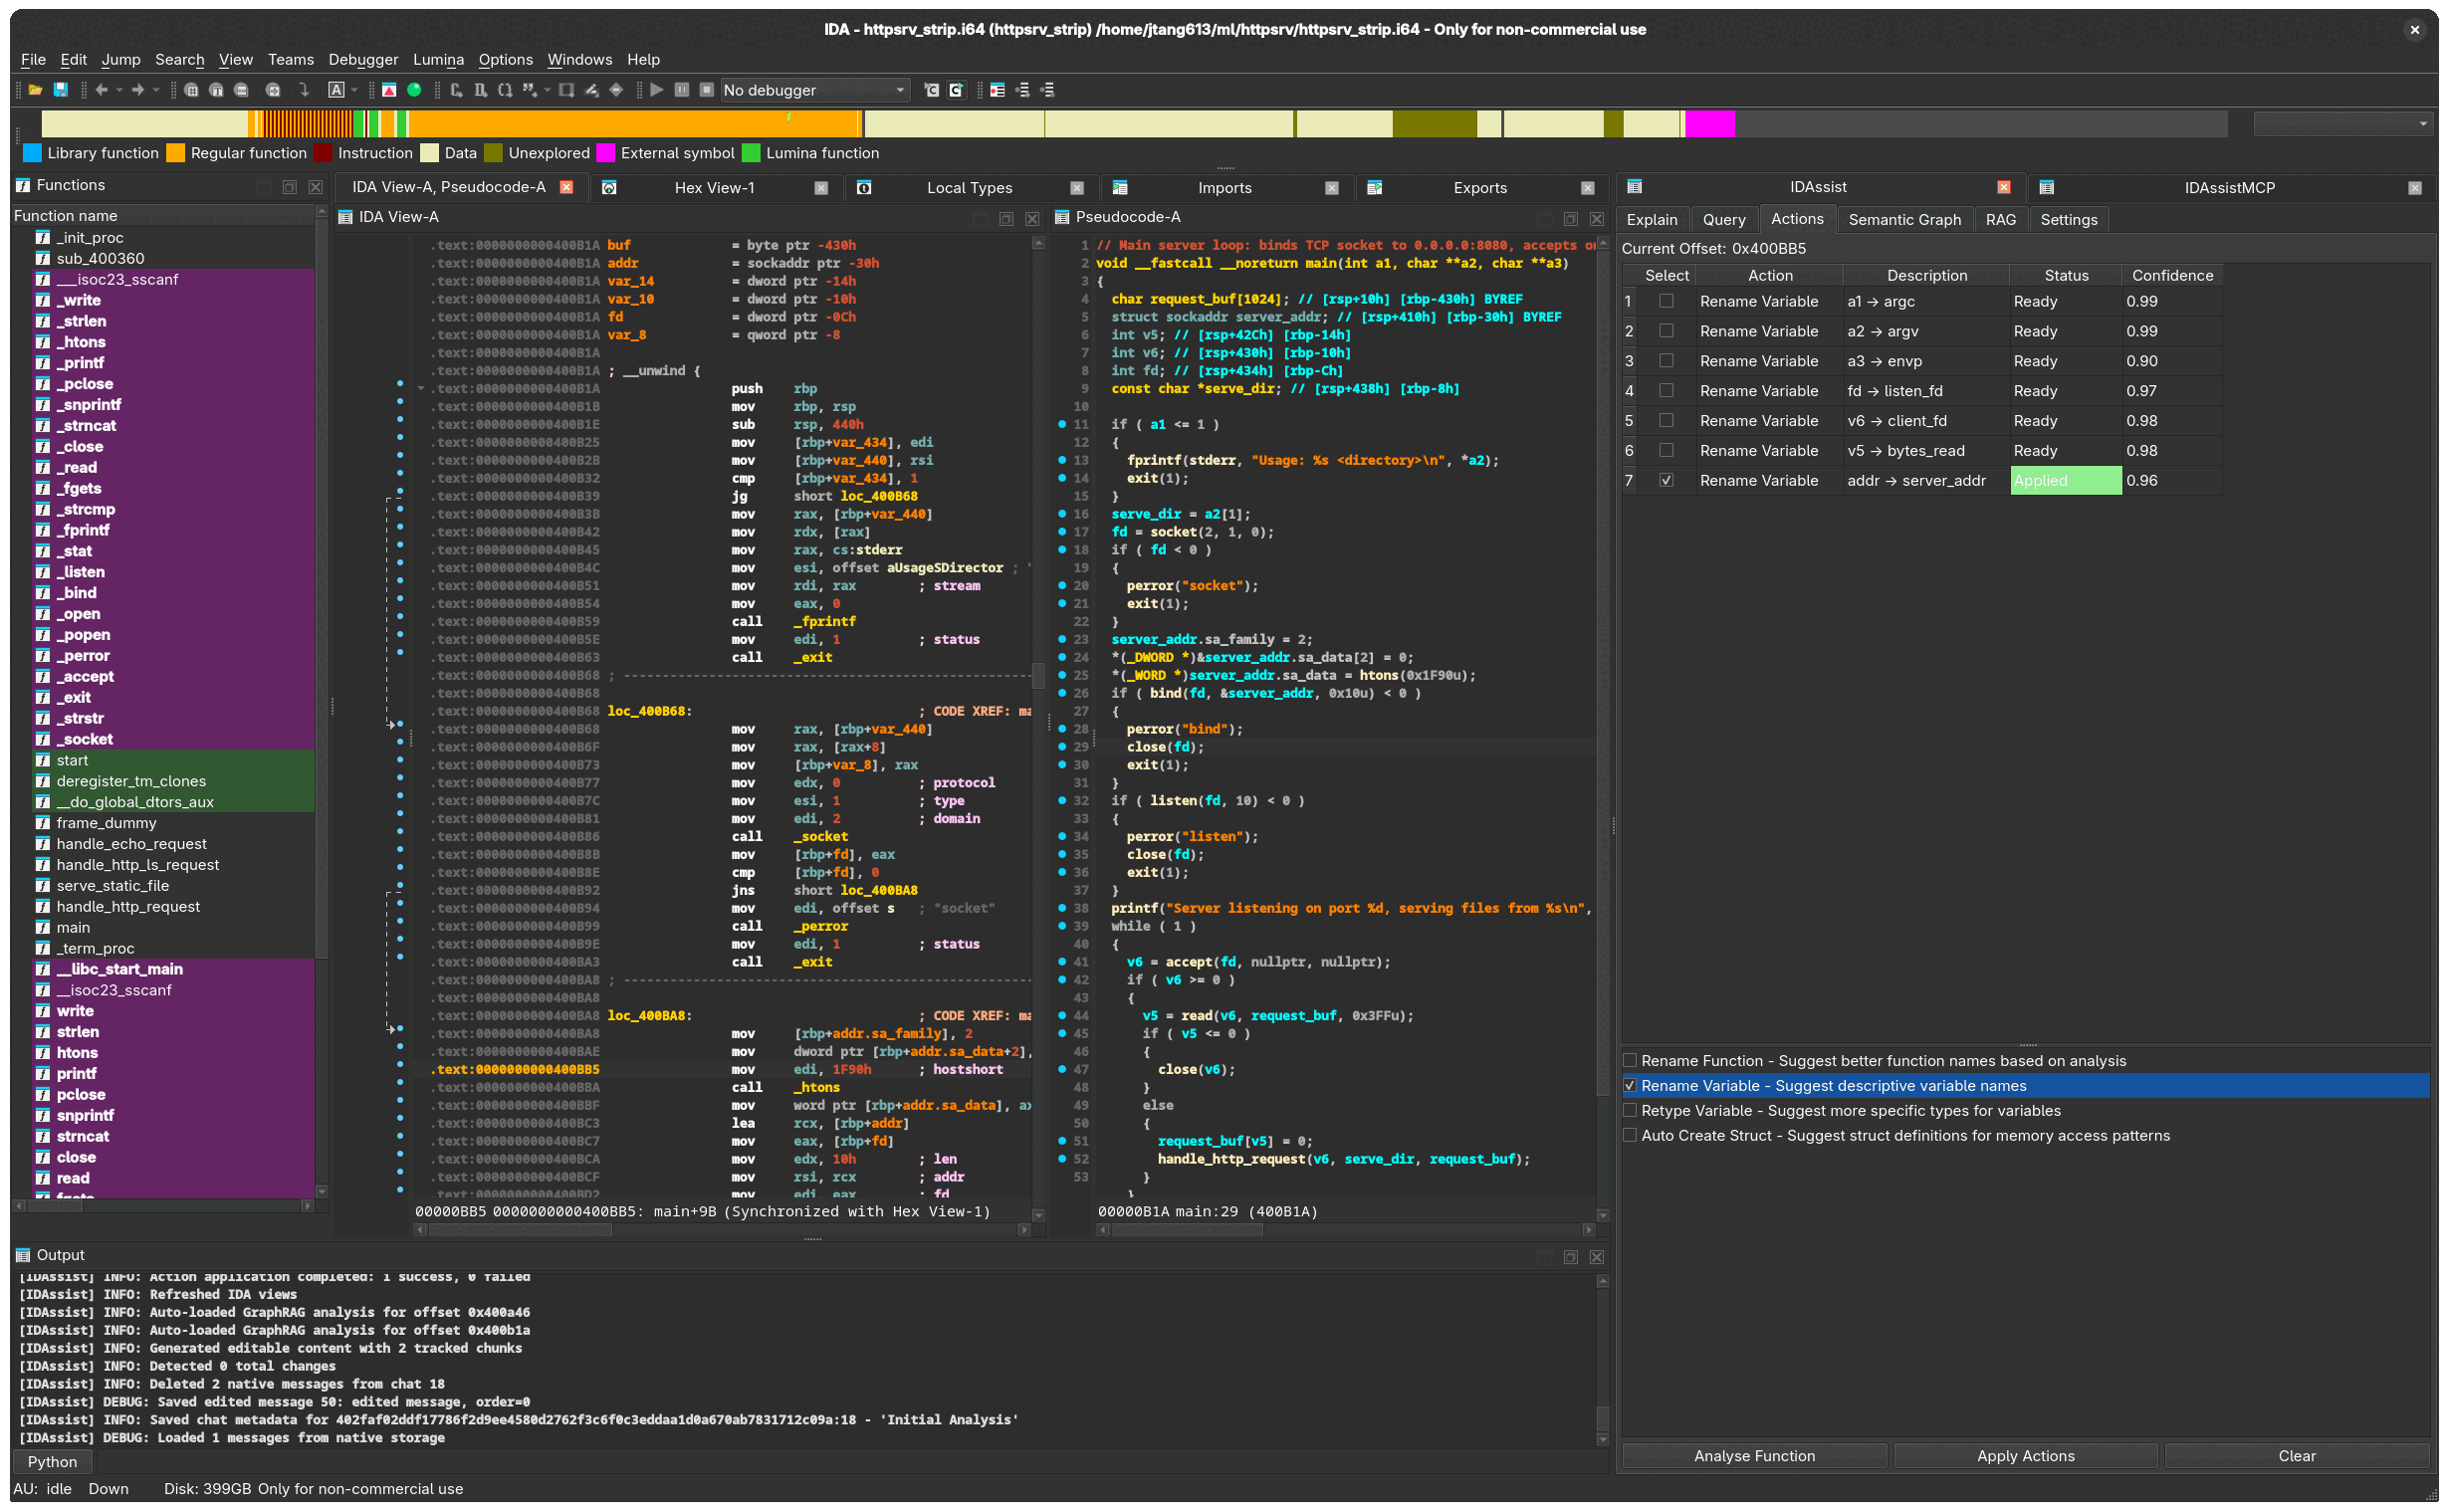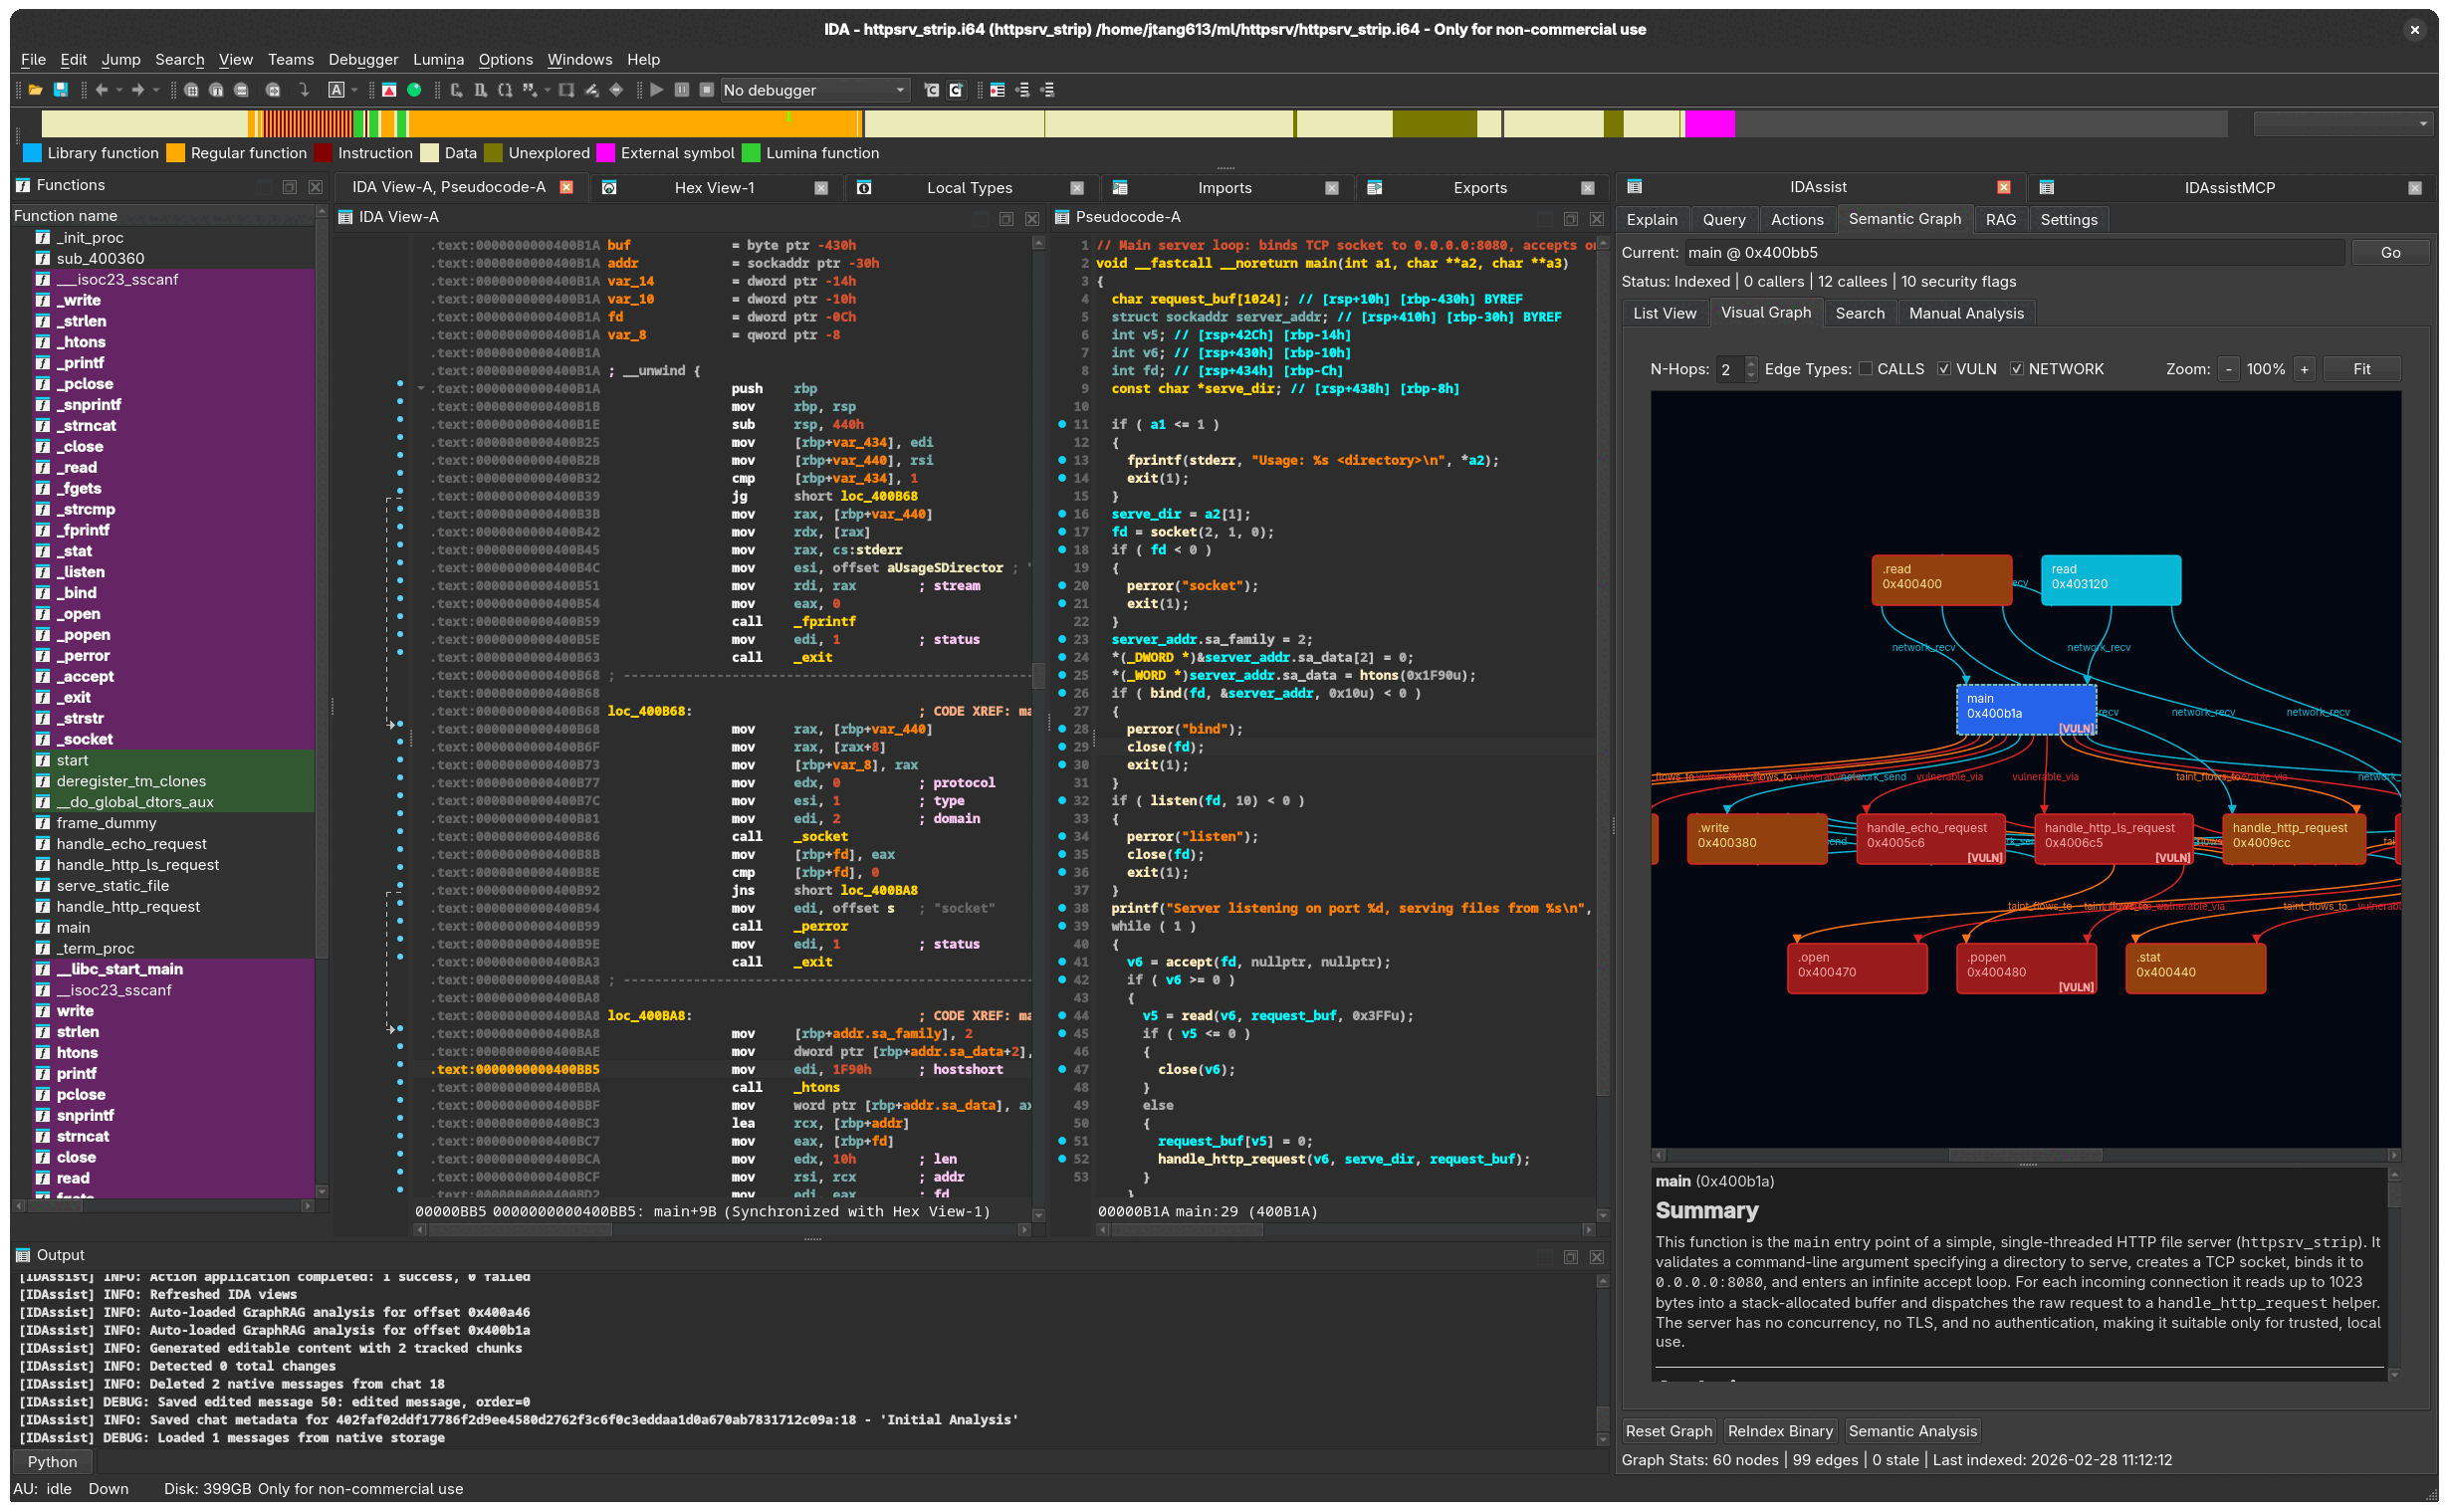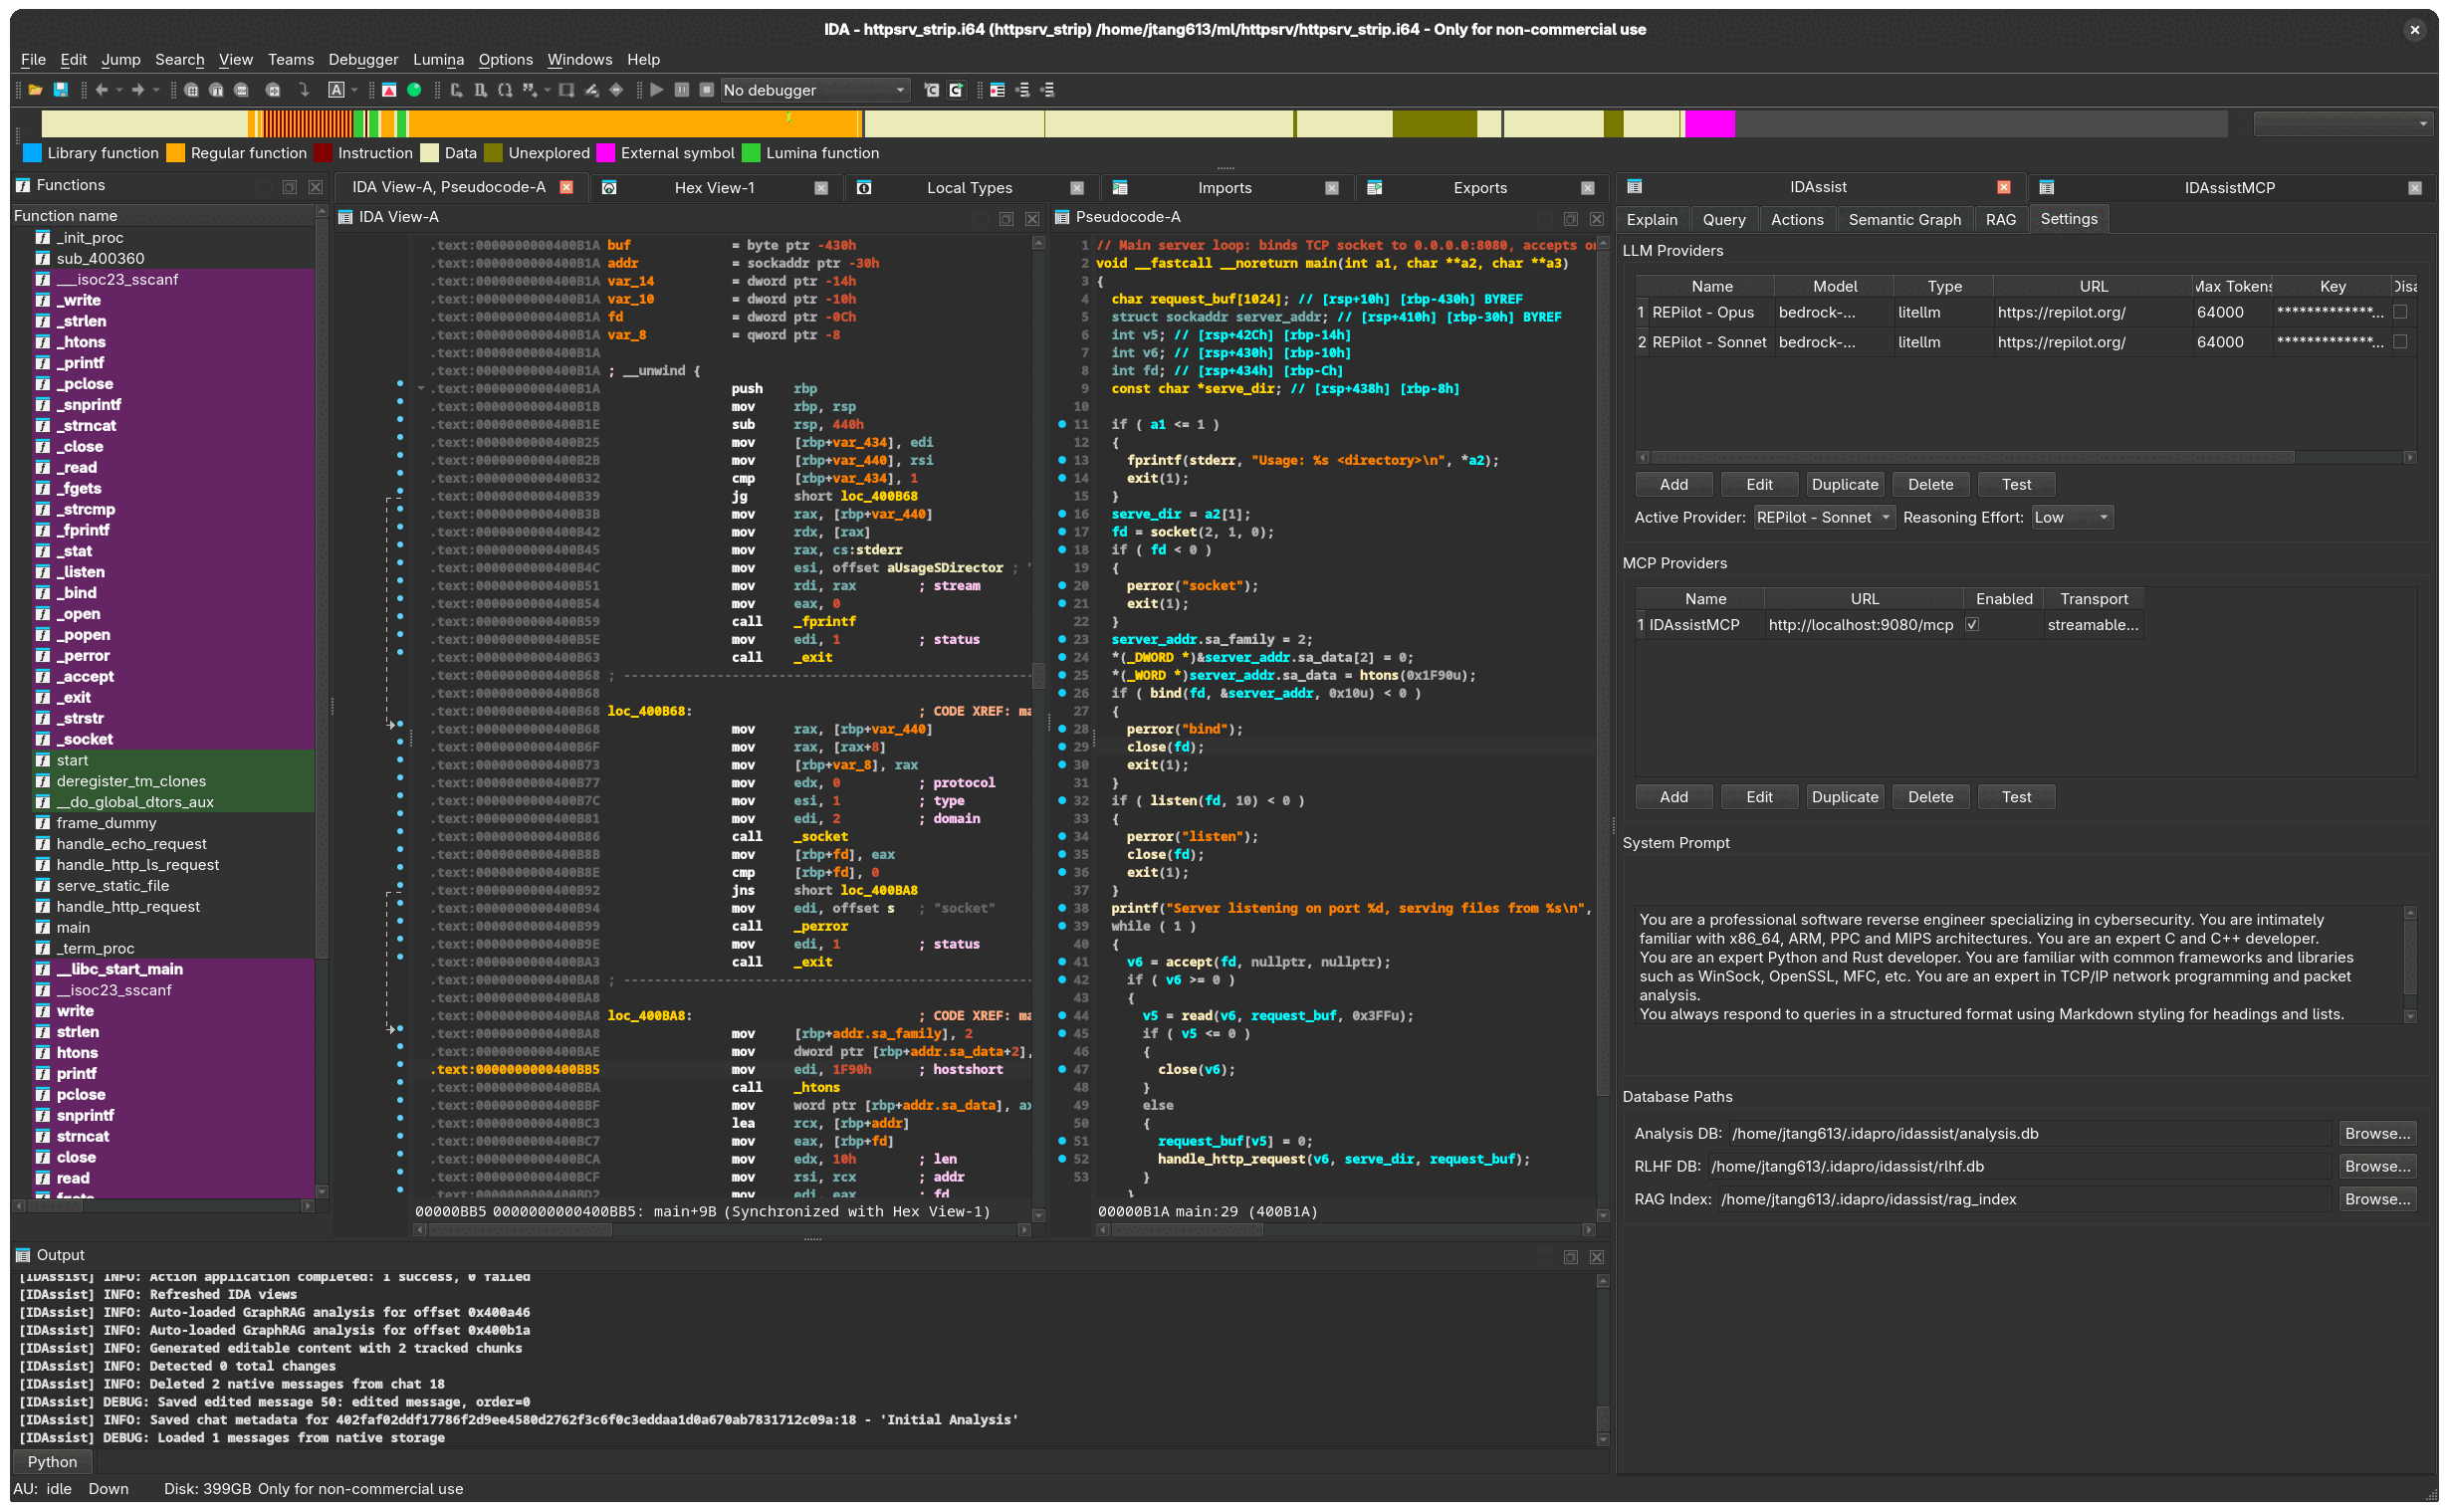 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
 symgraph/ghidrassist
An LLM extension for Ghidra to enable AI assistance in RE.
 gaasedelen/tenet
A Trace Explorer for Reverse Engineers
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
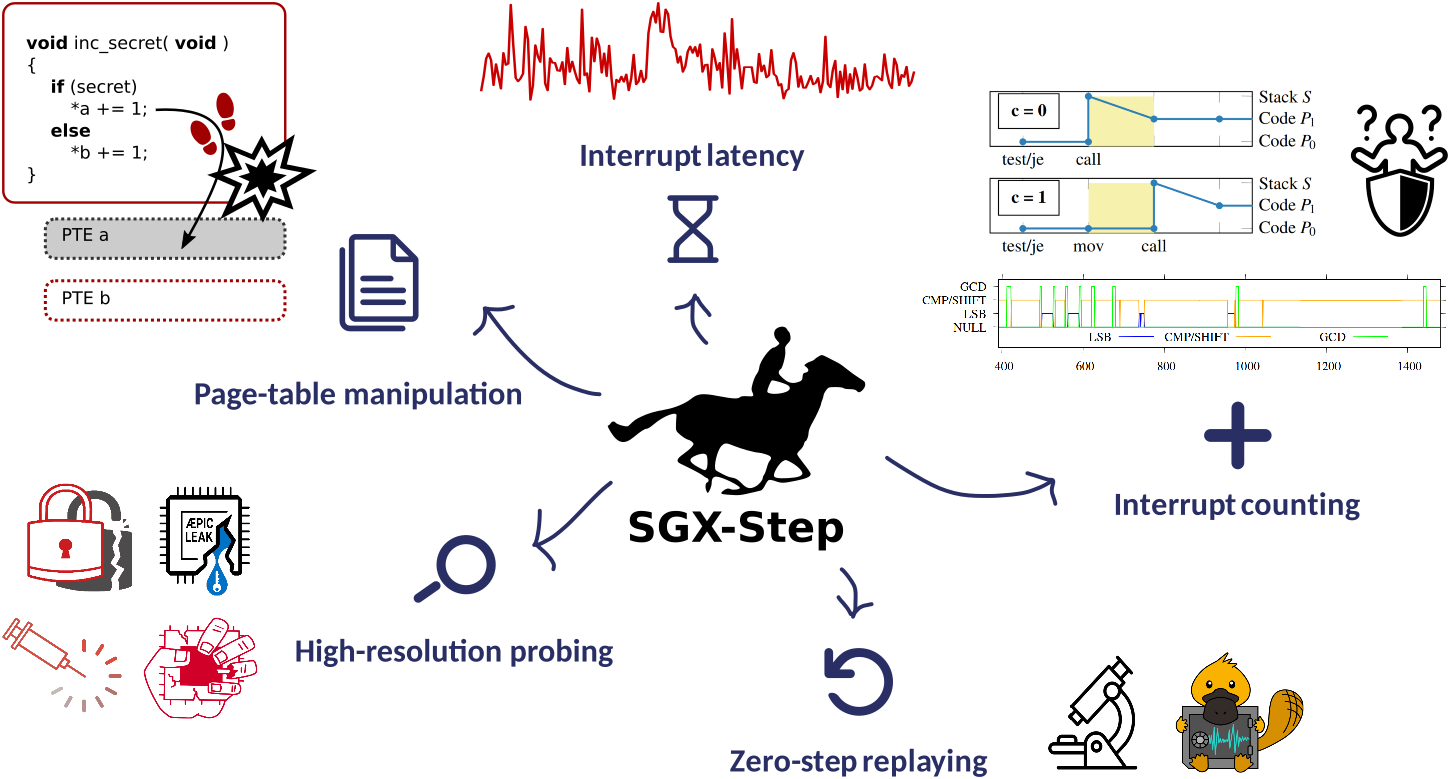 jovanbulck/sgx-step
A practical attack framework for precise enclave execution control
 bishopfox/bfinject
Dylib injection for iOS 11.0 - 11.1.2 with LiberiOS and Electra jailbreaks
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering