
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
256 results
ioctlance preview

ioctlance

GitHubzeze-zeze/ioctlance

A tool that is used to hunt vulnerabilities in x64 WDM drivers
binary-analysisdynamic-analysis-sandboxingexploit-frameworks+4
4733 months ago
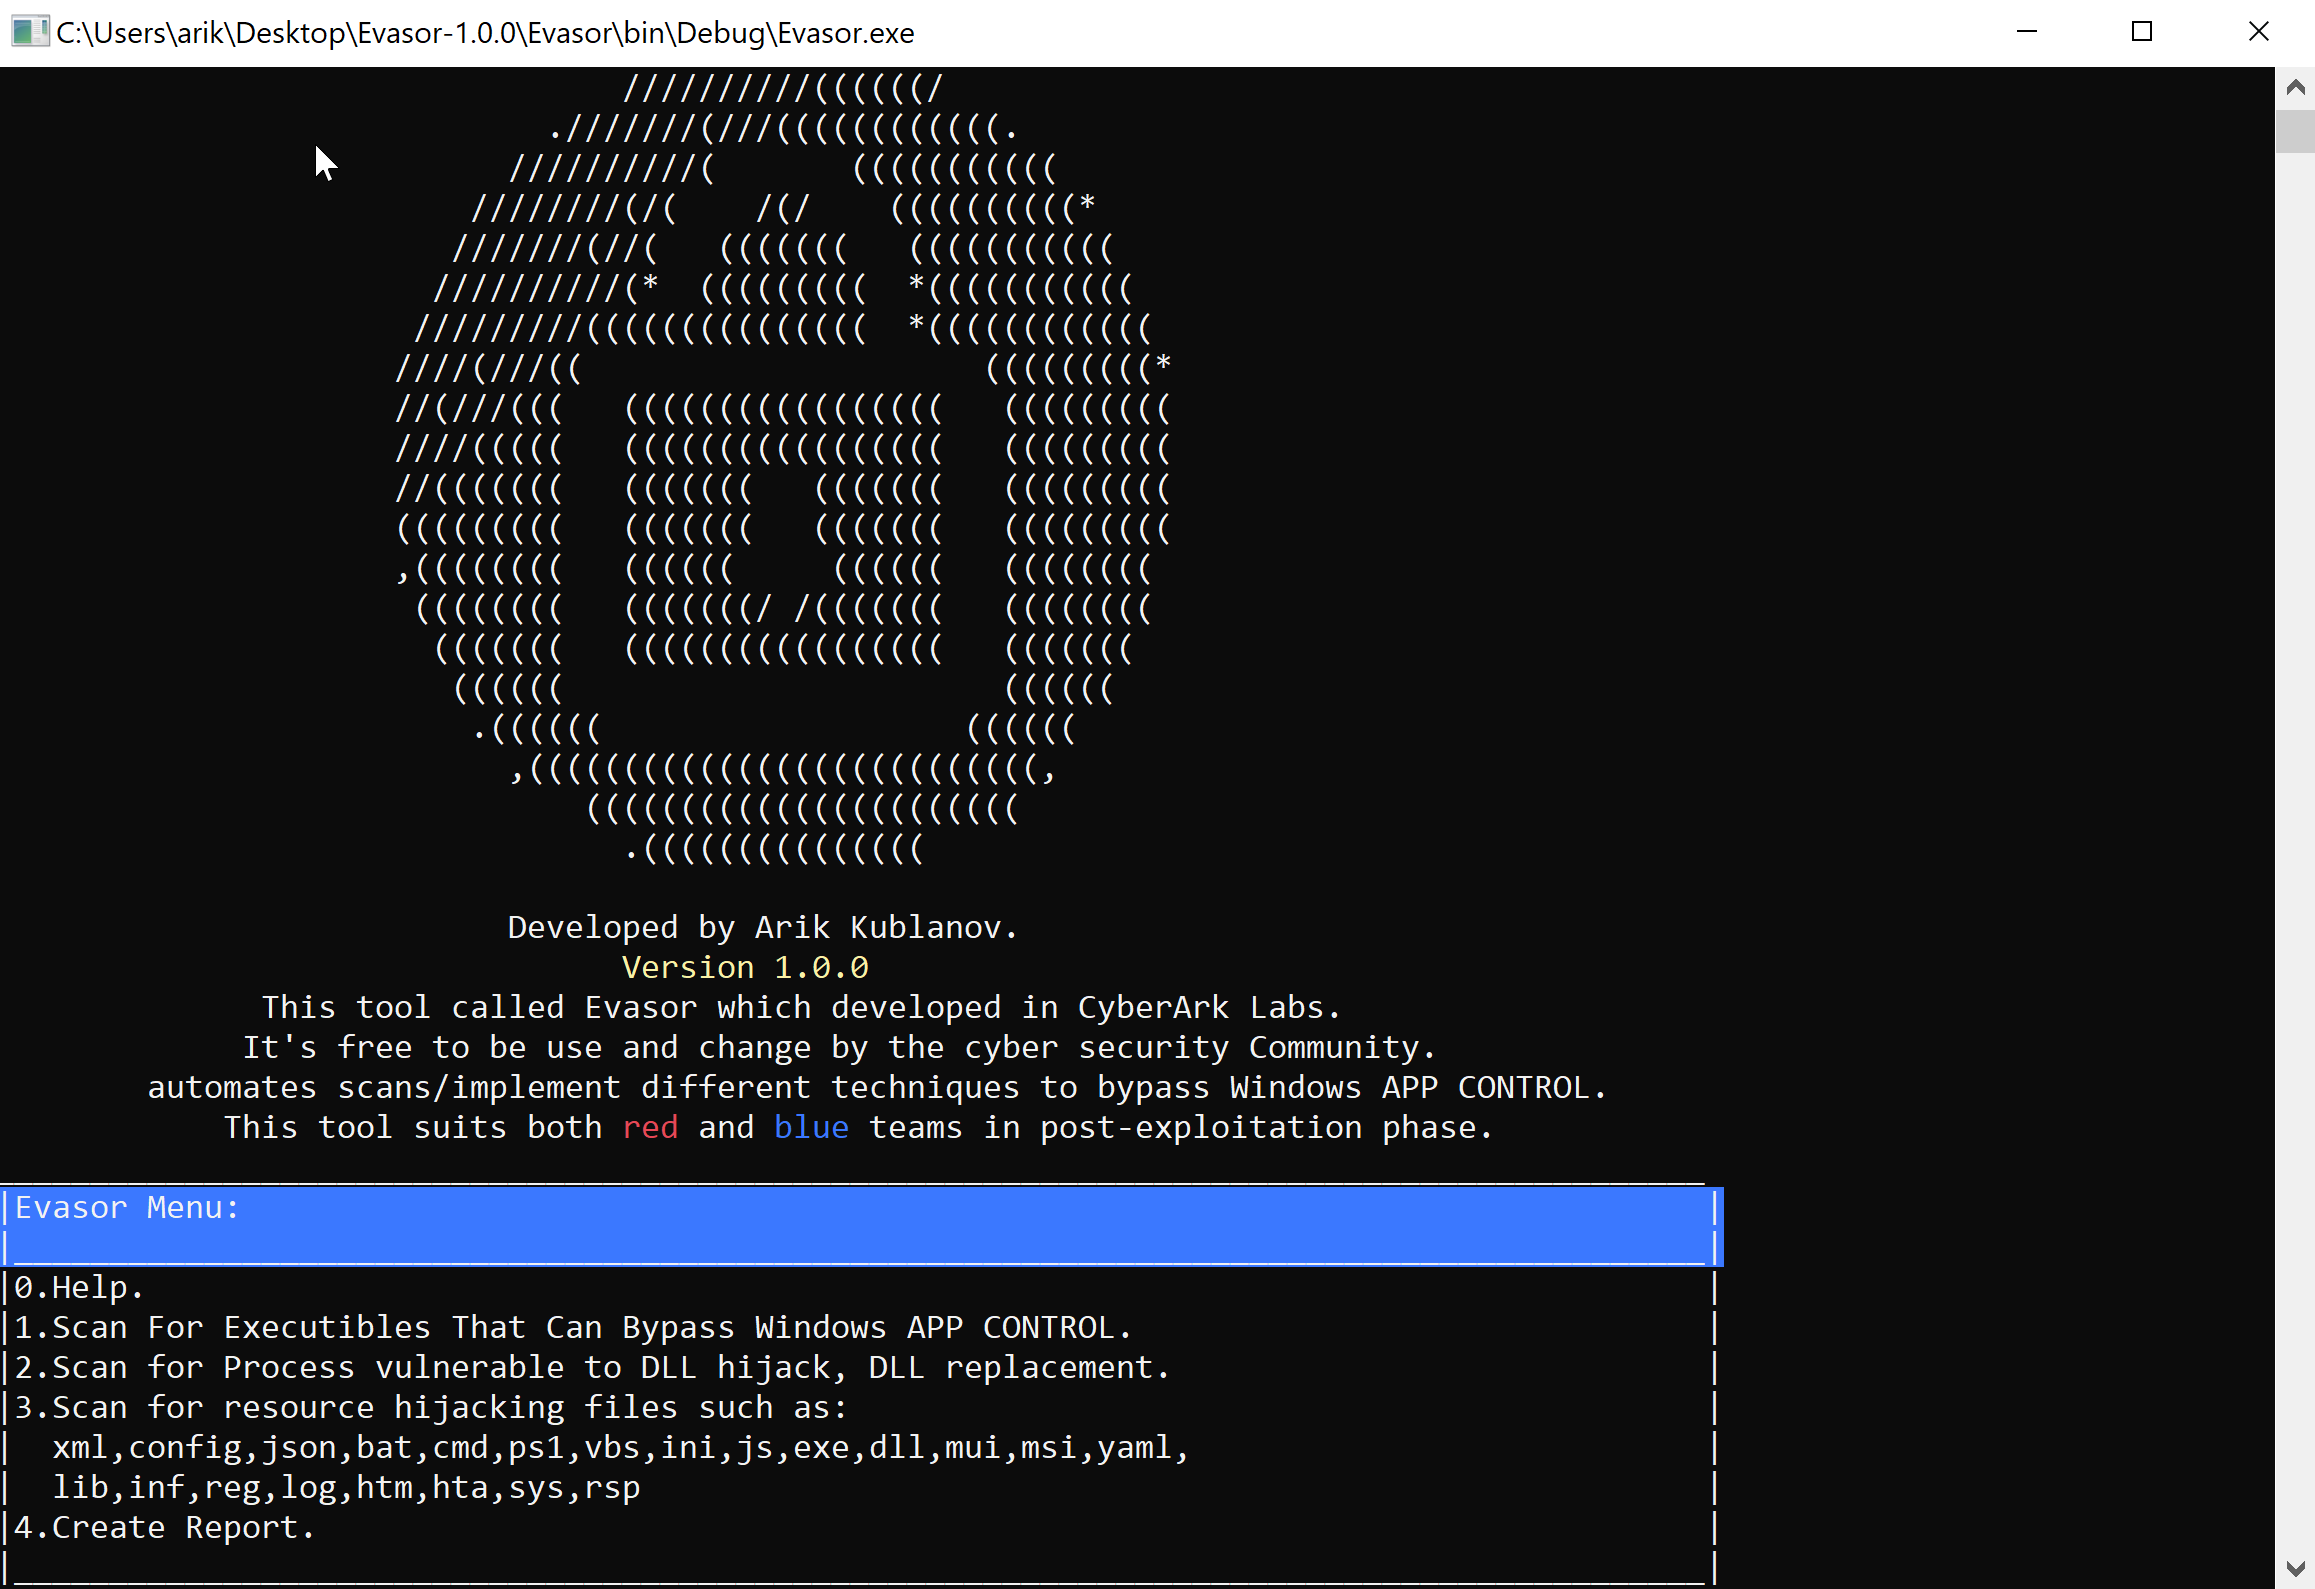
Evasor preview

Evasor

GitHubcyberark/evasor

A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies
binary-analysisdefensive-toolspenetration-testing+3
3266 years ago
polytracker preview

polytracker

GitHubtrailofbits/polytracker

An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
binary-analysisdynamic-code-analysiseducation+4
5993 months ago
binder-trace preview

binder-trace

GitHubfoundryzero/binder-trace

Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".
android-securitybinary-analysisdynamic-analysis-sandboxing+3
7701 year ago
DarunGrim preview

DarunGrim

GitHubohjeongwook/darungrim

A patch analysis tool

binary-analysisfuzzingreverse-engineering+2
3656 years ago
uniFuzzer preview

uniFuzzer

GitHubpagalaxylab/unifuzzer

A fuzzing tool for closed-source binaries based on Unicorn and LibFuzzer
binary-analysisembedded-systems-securityfuzzing+1
3477 years ago
apk-medit preview

apk-medit

GitHubsterrasec/apk-medit

memory search and patch tool on debuggable apk without root & ndk
android-securitybinary-analysismemory-forensics+2
4344 days ago
beebug preview

beebug

GitHubinvictus1306/beebug

A tool for checking exploitability

binary-analysisdebuggersexploitation+2
2117 years ago
inhale preview

inhale

GitHubnetspooky/inhale

A malware analysis and classification tool.
binary-analysisforensicshash-analysis+3
1915 years ago
elegant-bouncer preview

elegant-bouncer

GitHubmsuiche/elegant-bouncer

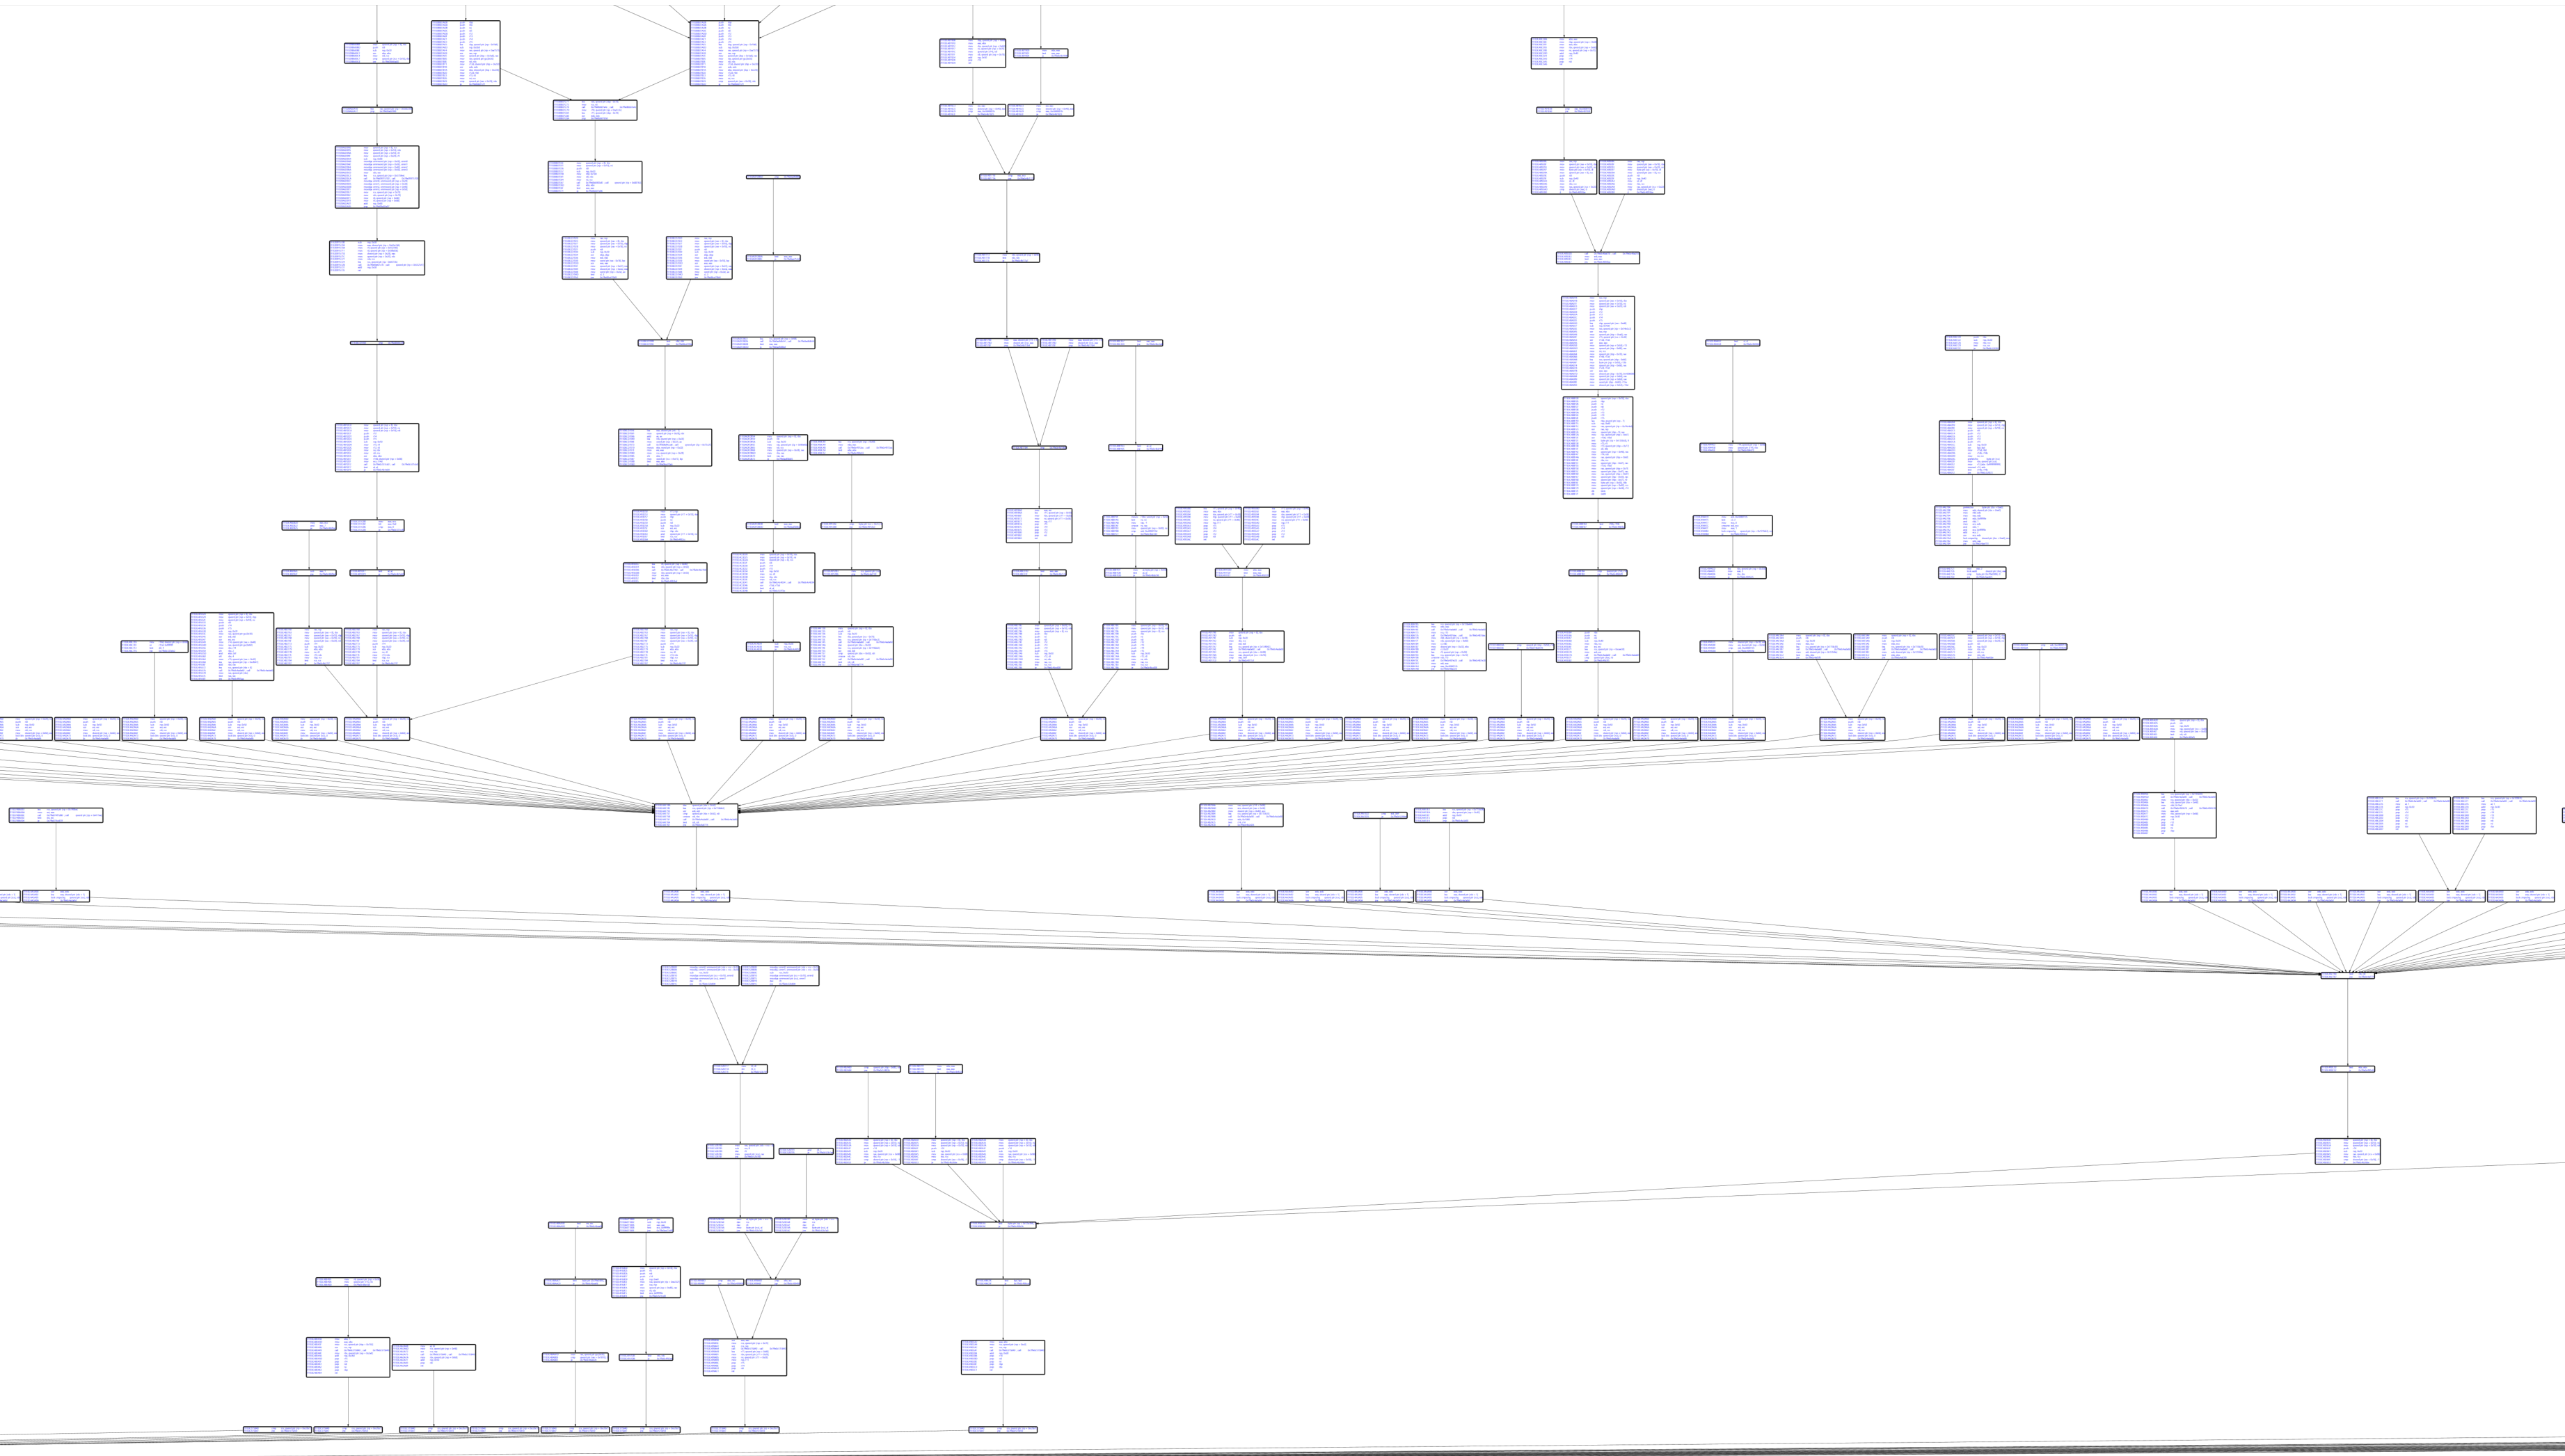
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.
binary-analysisdigital-forensicsios-security+4
1824 days ago
EhTrace preview

EhTrace

GitHubk2/ehtrace

ATrace is a tool for tracing execution of binaries on Windows.
binary-analysiscode-analysisdebuggers+4
24510 months ago
hacksguard preview

hacksguard

GitHubrhacknarok/hacksguard

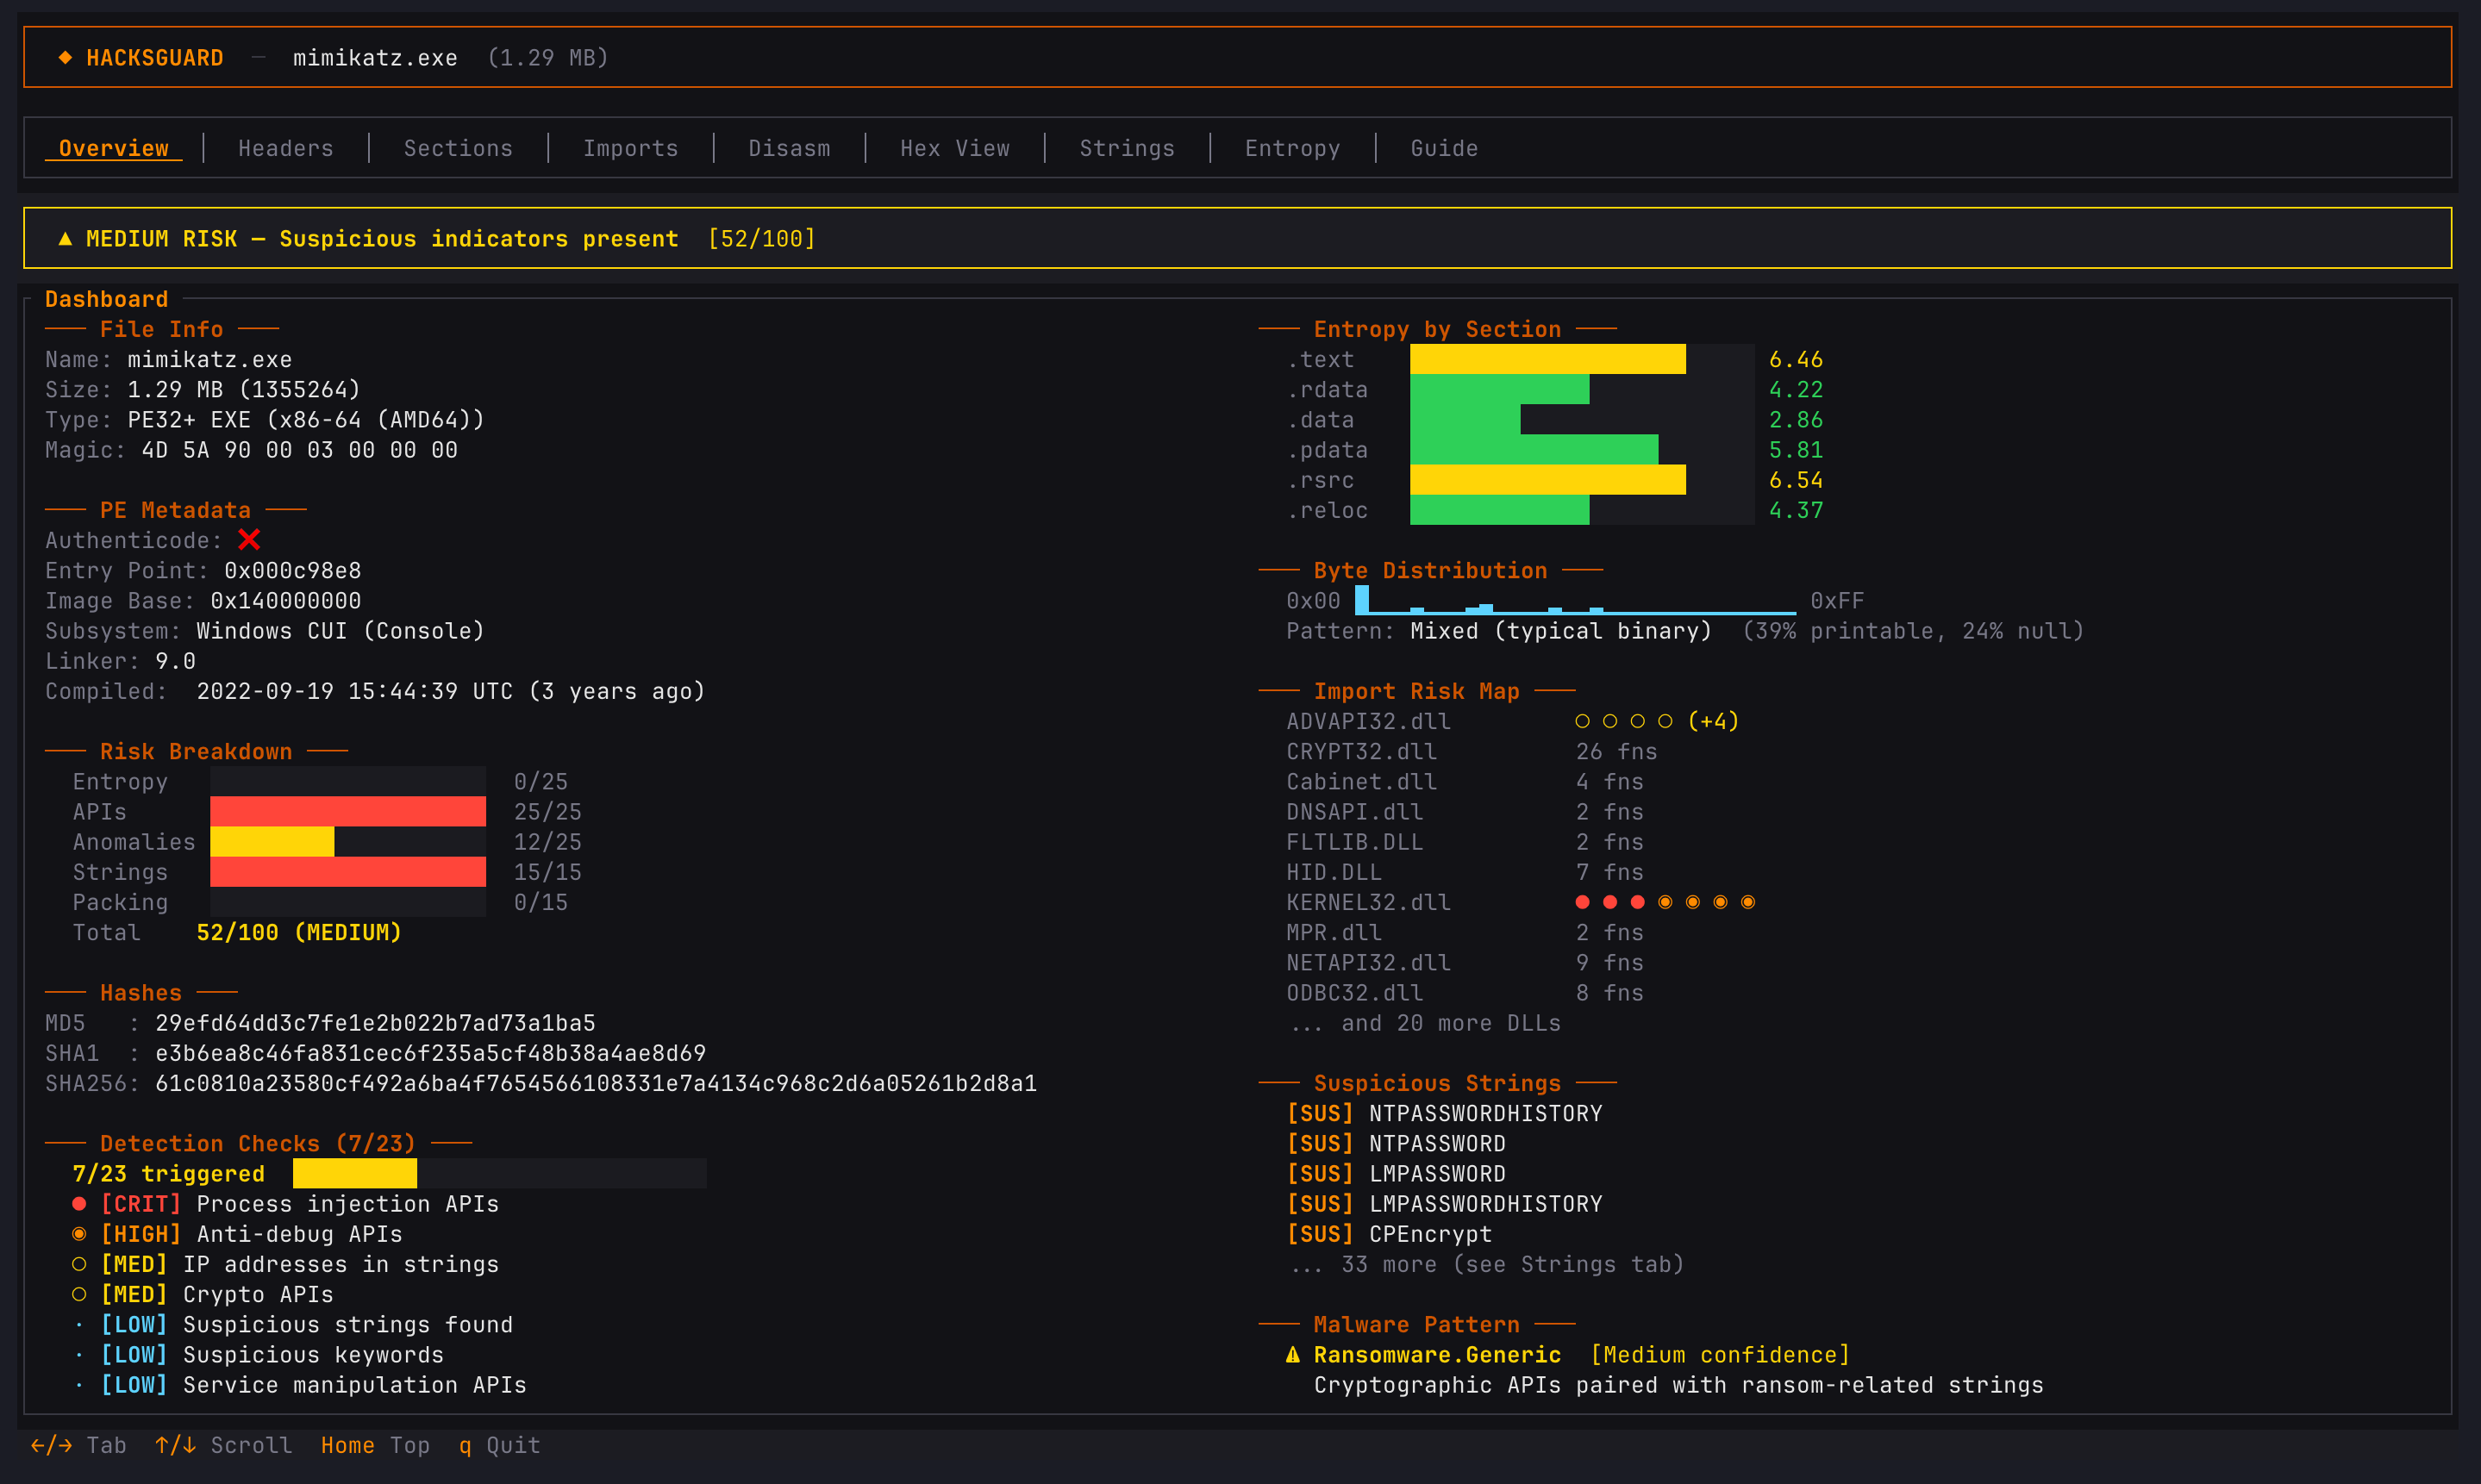
A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.
binary-analysisforensicsmalware-analysis+2
21315 days ago
DLLirant preview

DLLirant

GitHubredteamsocietegenerale/dllirant

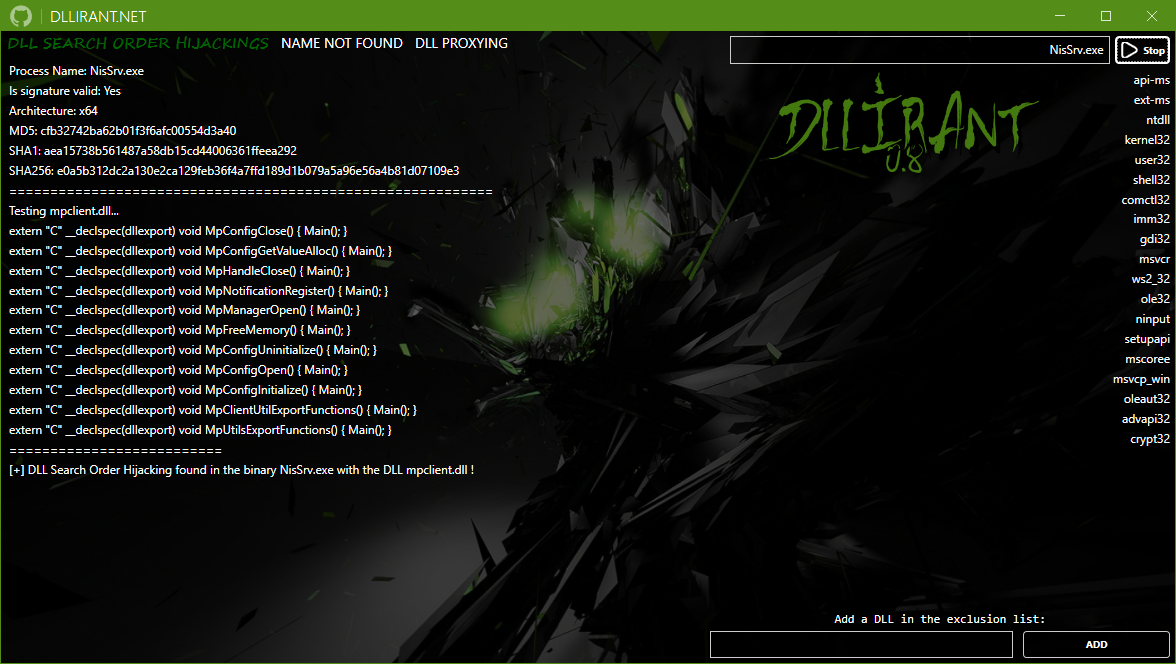
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.

binary-analysisdynamic-code-analysisexploitation+3
5023 years ago
asatools preview

asatools

GitHubnccgroup/asatools

Main repository to pull all NCC Group Cisco ASA-related tool projects.
binary-analysisdebuggersembedded-systems-security+3
2398 years ago
cdf preview

cdf

GitHubkudelskisecurity/cdf

Automated differential fuzzing tool for cryptographic software that detects implementation errors, compliance failures, and side-channel leaks…
binary-analysiscryptographyfuzzing+1
1715 years ago
nuitka-static-unpacker preview

nuitka-static-unpacker

GitHubdimareverse/nuitka-static-unpacker

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
binary-analysisdata-recoveryforensics+3
1321 month ago
RpcInvestigator preview

RpcInvestigator

GitHubtrailofbits/rpcinvestigator

Windows RPC interface discovery and analysis tool with visual endpoint enumeration, PE parsing, symbol resolution, real-time ETW sniffing, and…
binary-analysispenetration-testingreverse-engineering+1
3652 years ago
frida-extract preview

frida-extract

GitHuboalabs/frida-extract

Frida.re based RunPE (and MapViewOfSection) extraction tool

binary-analysisdynamic-analysis-sandboxingeducation+3
1159 years ago
Previous1…567…15Next