
draytek-arsenal
 infobyte/draytek-arsenal
Reverse Engineering and Observability toolkit for Draytek firewalls
binary-analysisembedded-systems-securityfirmware-analysis+5
54
infobyte/draytek-arsenalReverse Engineering and Observability toolkit for Draytek firewalls
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 gamozolabs/elfloader
An architecture-agnostic ELF file flattener for shellcode
 nccgroup/pythia
A tool to extract RTTI information from Delphi executables, written in pure Python

 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 parikhakshat/autoharness
A tool that automatically creates fuzzing harnesses based on a library
 dump-guy/get-pdinvokeimports
PowerShell module for automatic detection of P/Invoke, Dynamic P/Invoke, and D/Invoke in .NET assemblies. Reveals unmanaged API calls, MDTokens, and…
 shaikusaf/external_expact_aosp10_r33_cve-2022-25313
C library for stream-oriented XML parsing, providing handlers for parsing structures in documents. Includes xmlwf tool and supports UTF-16 encoding.
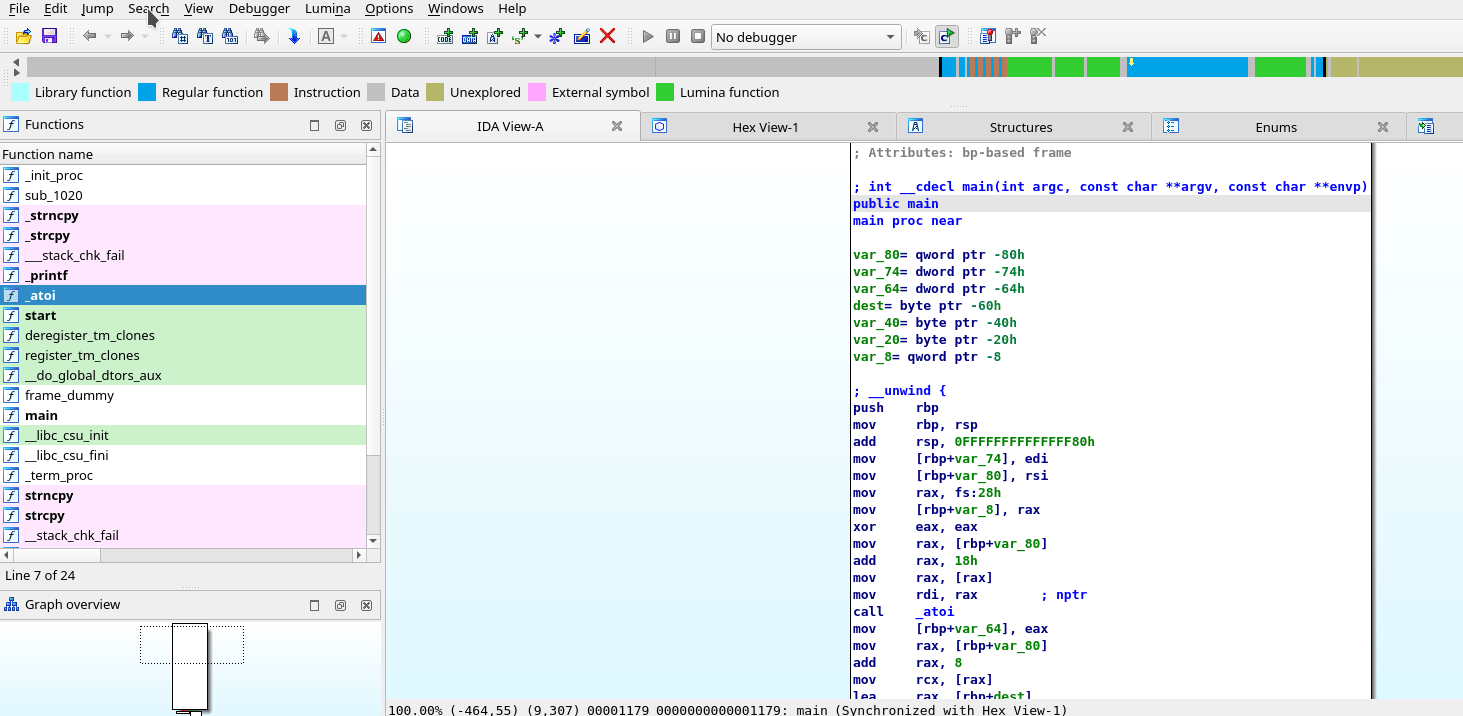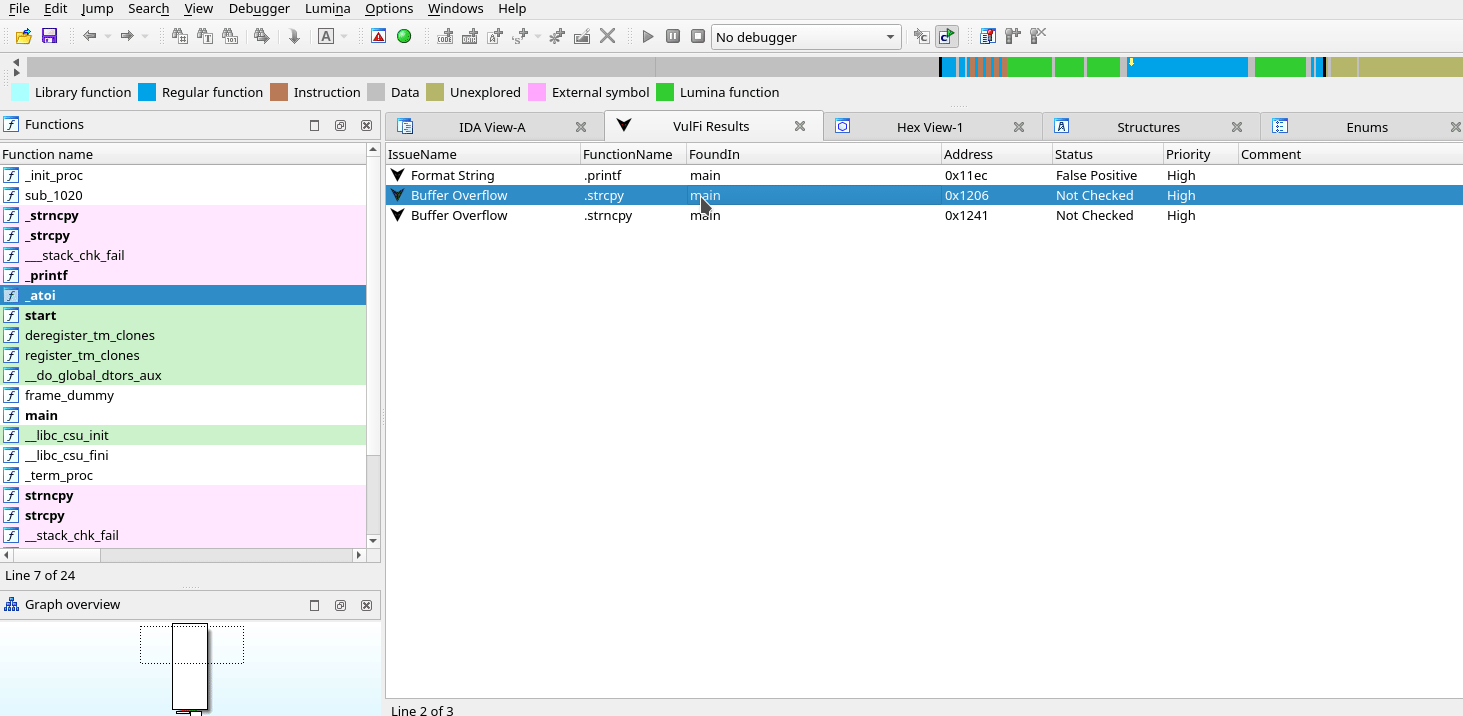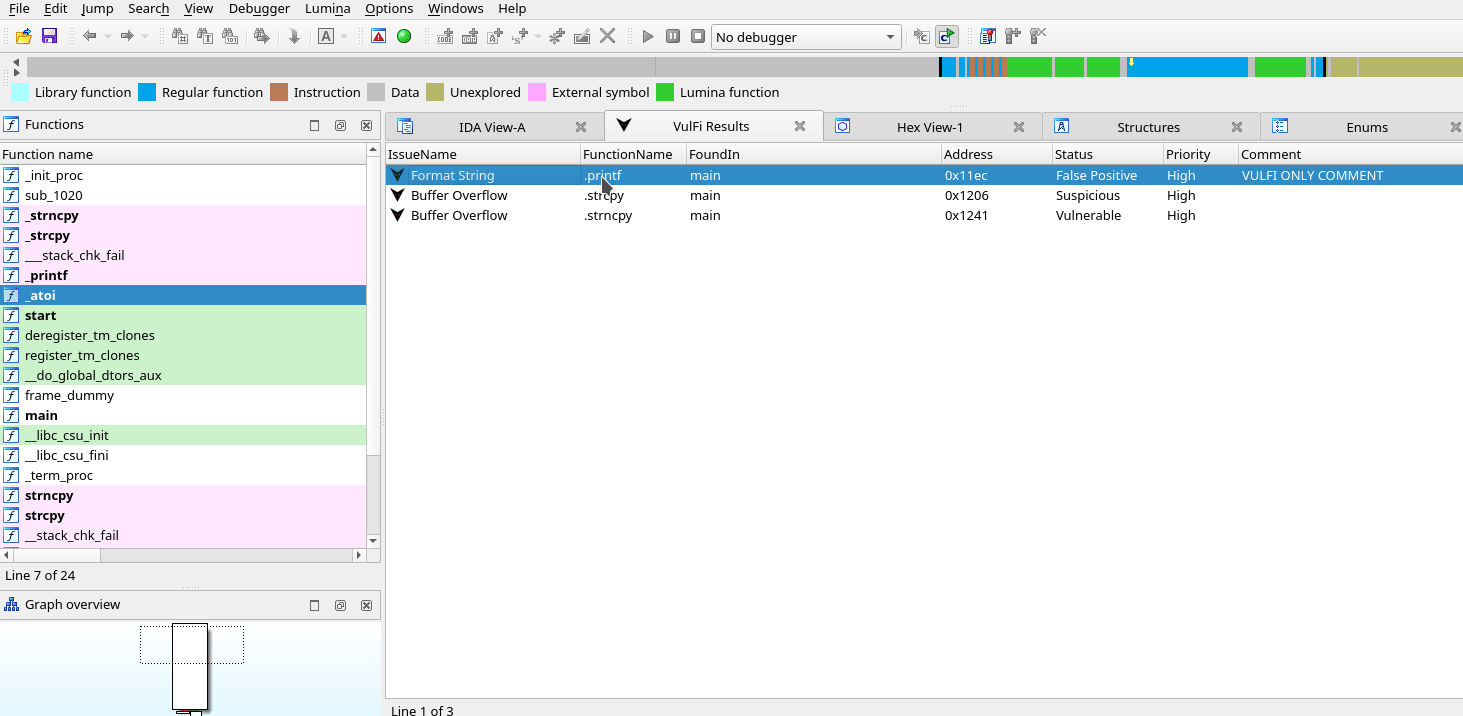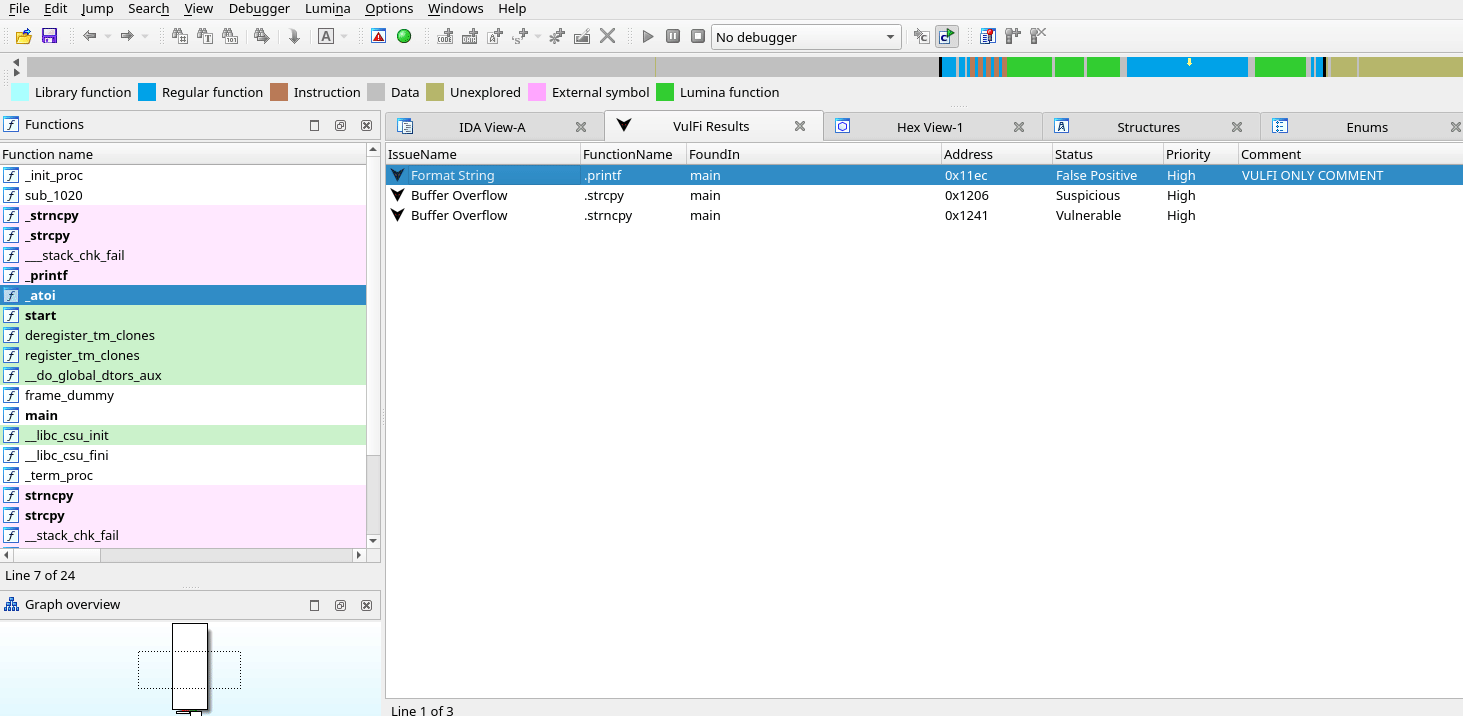 accenture/vulfi
IDA Pro plugin for query based searching within the binary useful mainly for vulnerability research.
 bmaia/binwally
Binary and Directory tree comparison tool using Fuzzy Hashing
 iilegacyyii/exportdumper
A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
 plum-umd/redexer
The Redexer binary instrumentation framework for Dalvik bytecode
 rasta-mouse/threatcheck
Identifies the bytes that Microsoft Defender / AMSI Consumer flags on.
 boratanrikulu/gobee
Write your BPF programs in Go, not C. gobee transpiles a Go subset to BPF C and generates typed cilium/ebpf bindings.
 mandiant/stringsifter
A machine learning tool that ranks strings based on their relevance for malware analysis.
 cyberark/evasor
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies