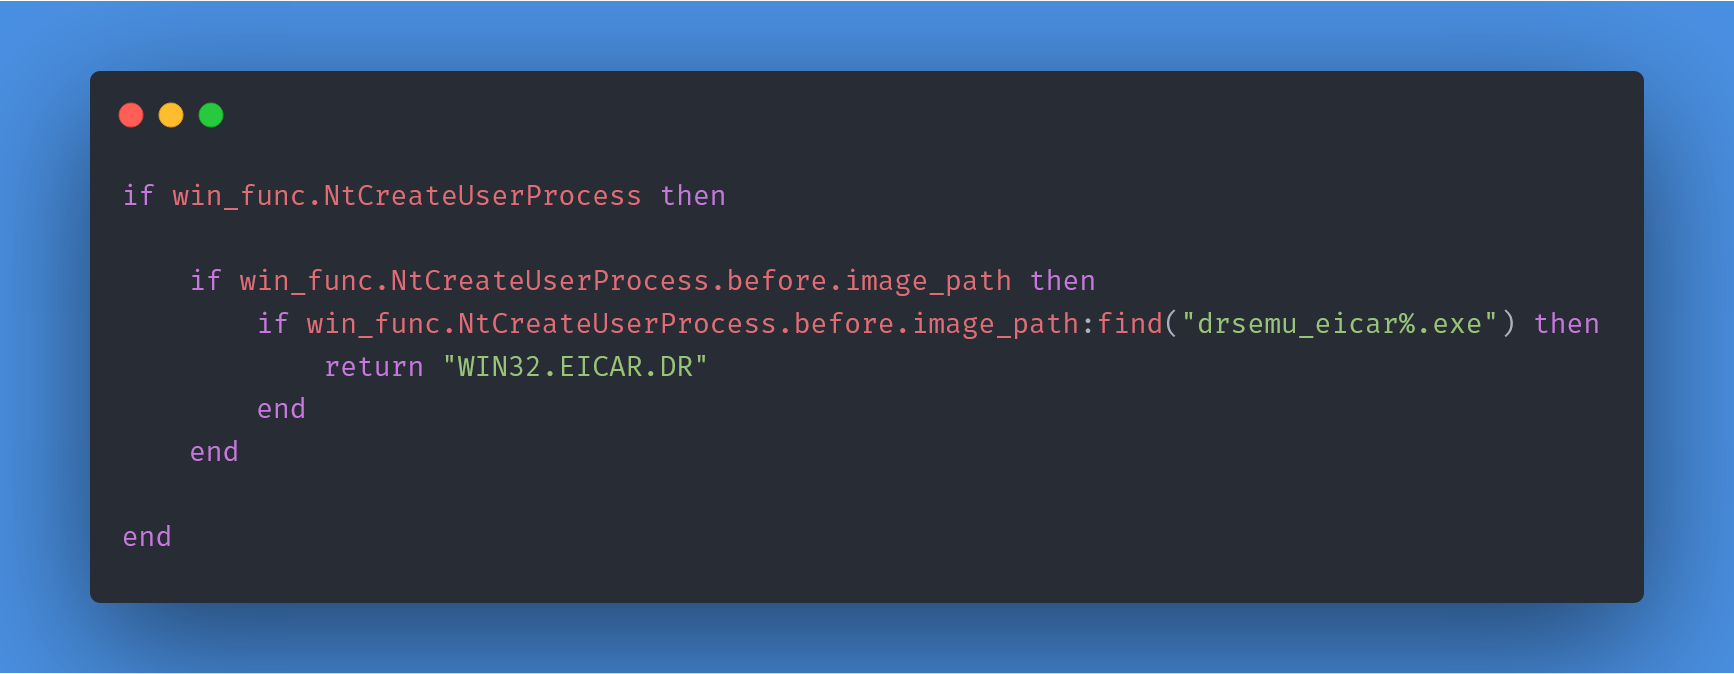
DrSemu
 secrary/drsemu
DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
2807 years ago
secrary/drsemuDrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
 owenpawl/cerberus-re-skill
cerberus-re is a local Apple-focused reverse-engineering workbench for building a repeatable three-headed static/dynamic/instrumentation loop around…
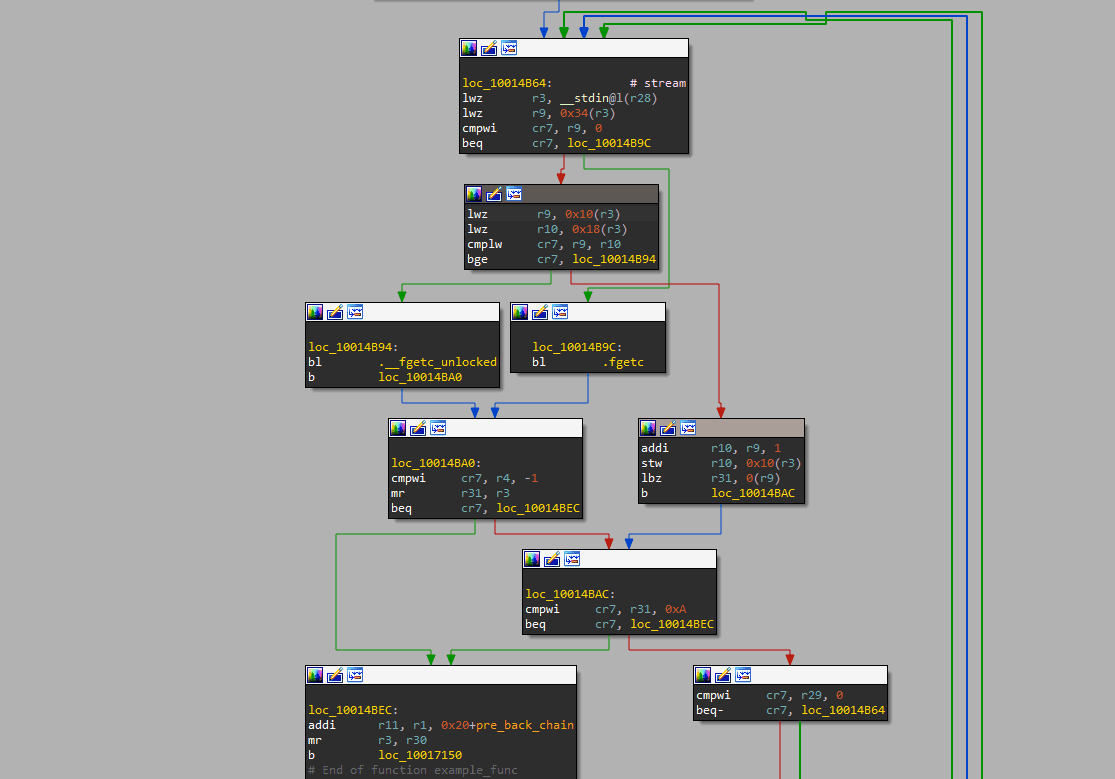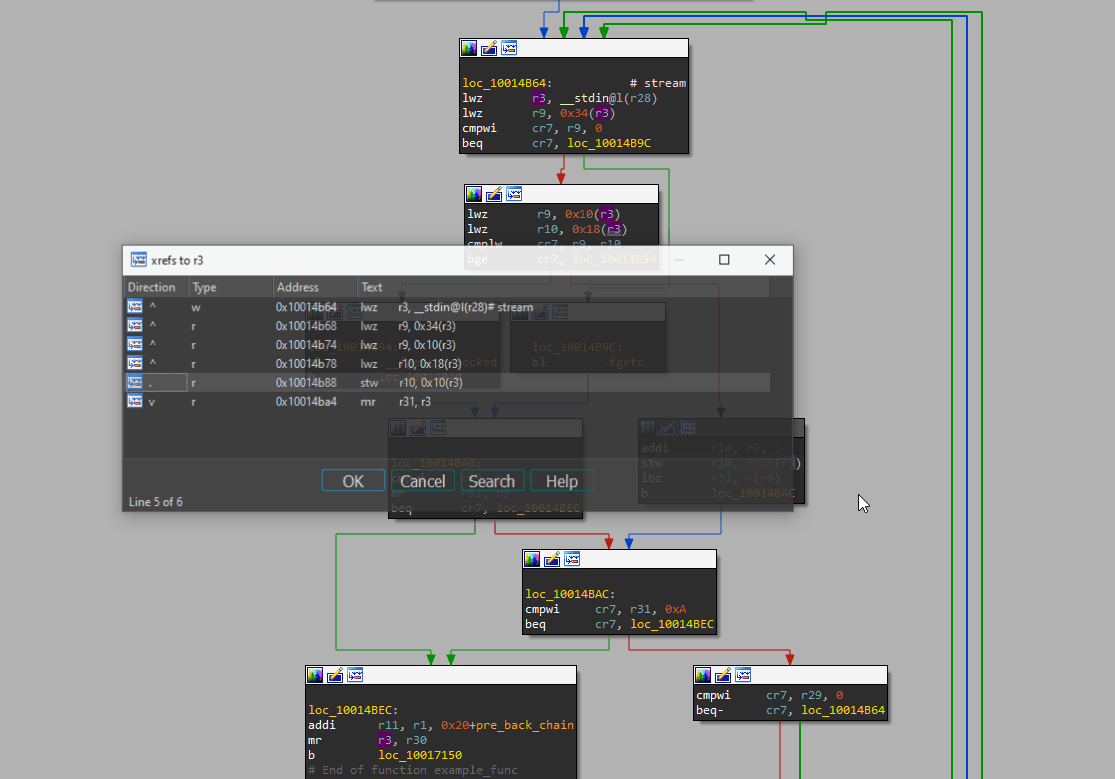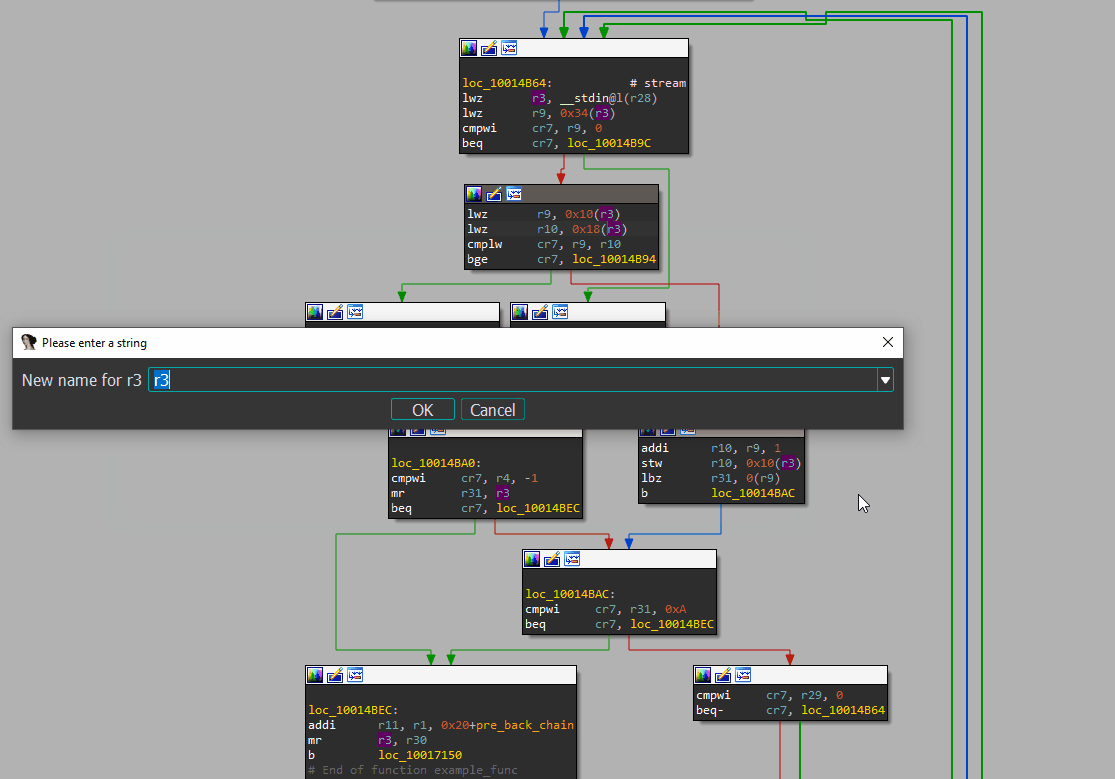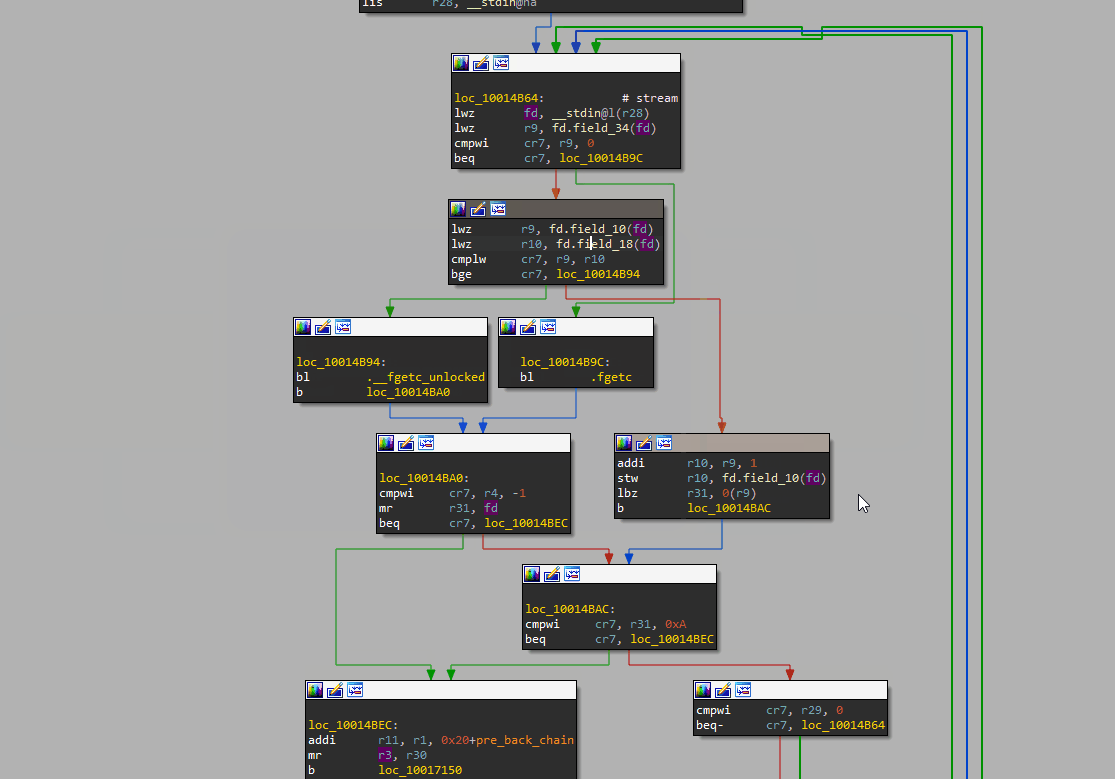 shemesh999/oregami
IDA plugins and scripts for analyzing register usage frame
 amossys/memitm
Tool to make in memory man in the middle
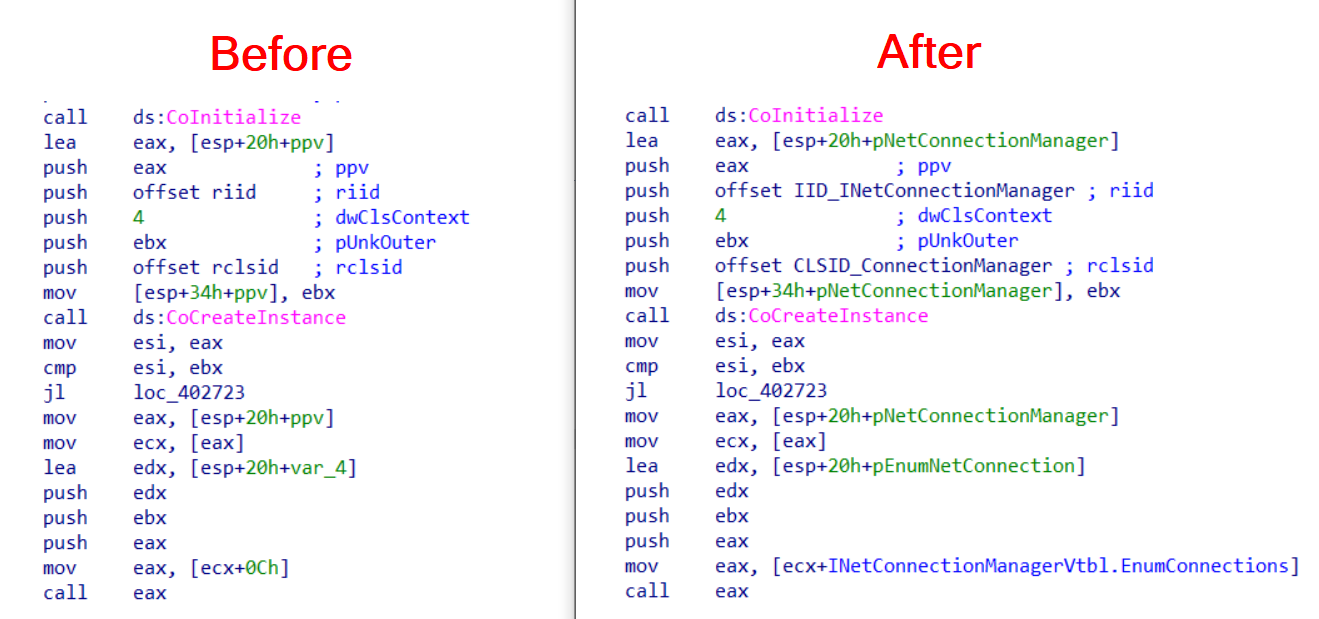 fboldewin/com-code-helper
Two IDAPython Scripts help you to reconstruct Microsoft COM (Component Object Model) Code
 robindavid/idasec
IDA plugin for reverse-engineering and dynamic interactions with the Binsec platform
 takahiroharuyama/ida_haru
scripts/plugins for IDA Pro
 sidenai/hyperion-disassembler
Native multi-arch disassembler & decompiler - PE/ELF/Mach-O, x86/x64/ARM64, Lua scripting, RTTI recovery
 struppigel/hedgehog-tools
Collection of scripts for malware analysis, deobfuscation, and configuration extraction. Supports static analysis, unpacking, shellcode conversion,…
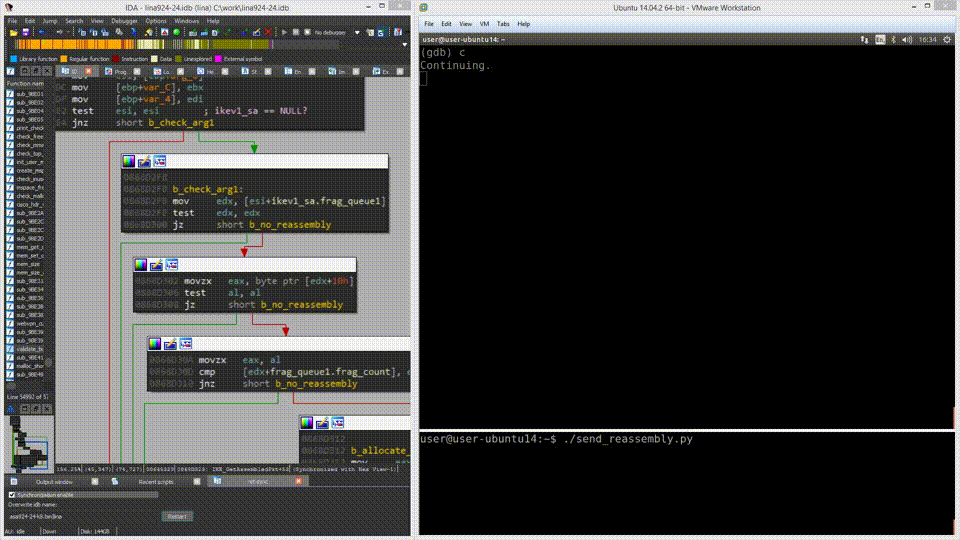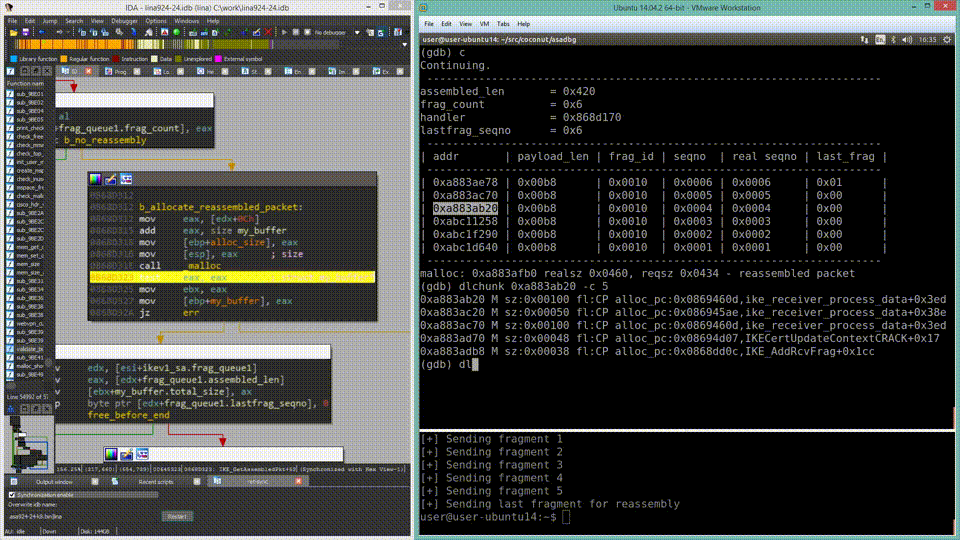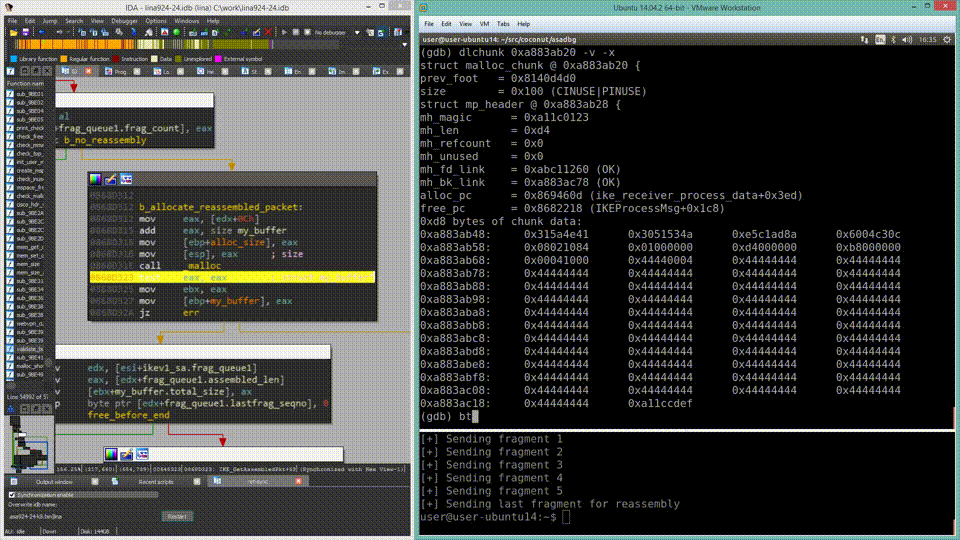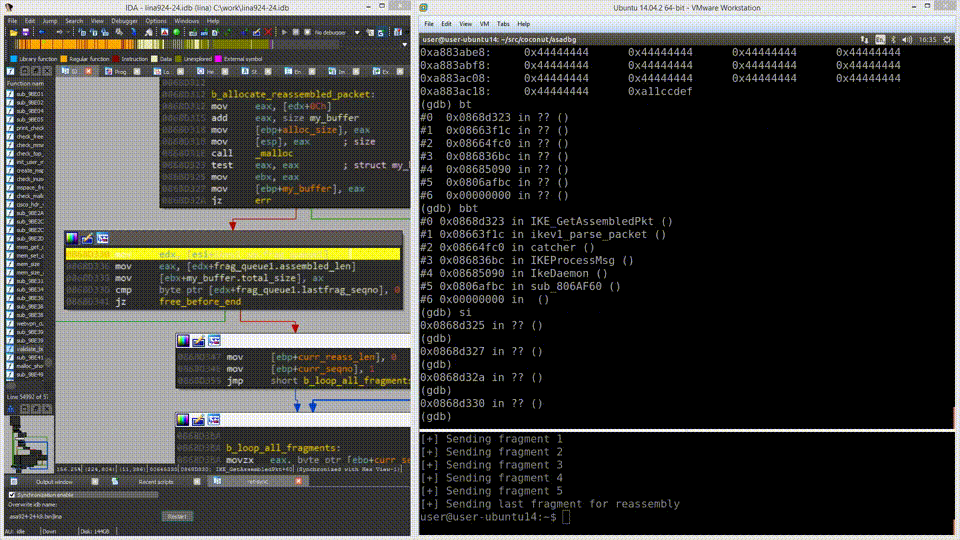 nccgroup/asadbg
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices
 immunityinc/libptrace
An event driven multi-core process debugging, tracing, and manipulation framework.
 buffer/pylibemu
A Libemu Cython wrapper
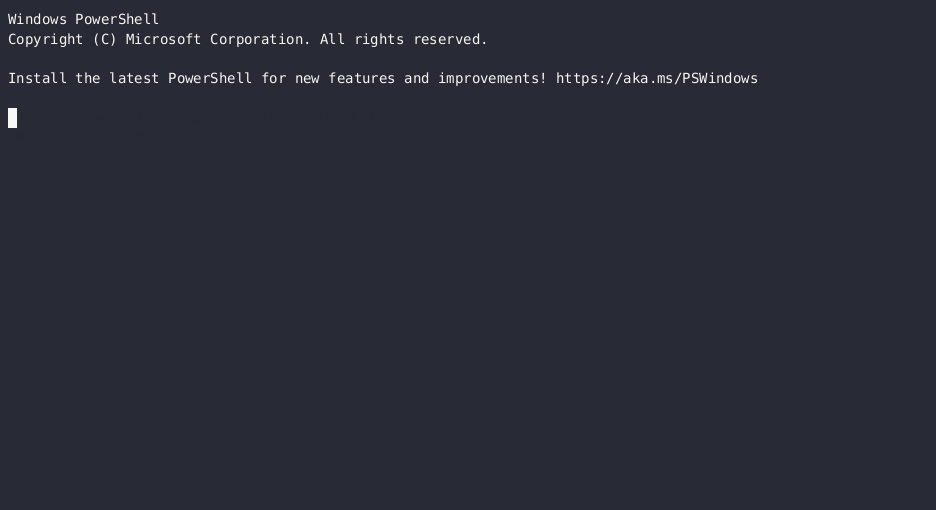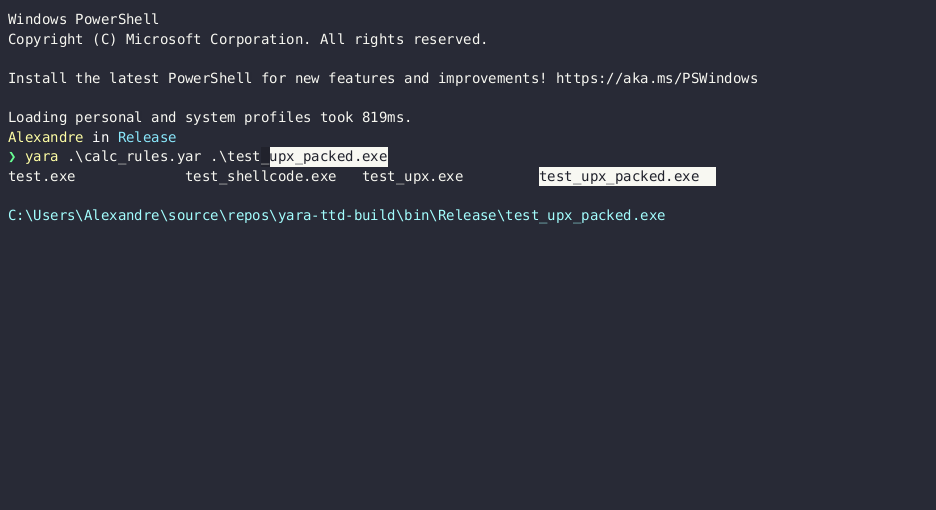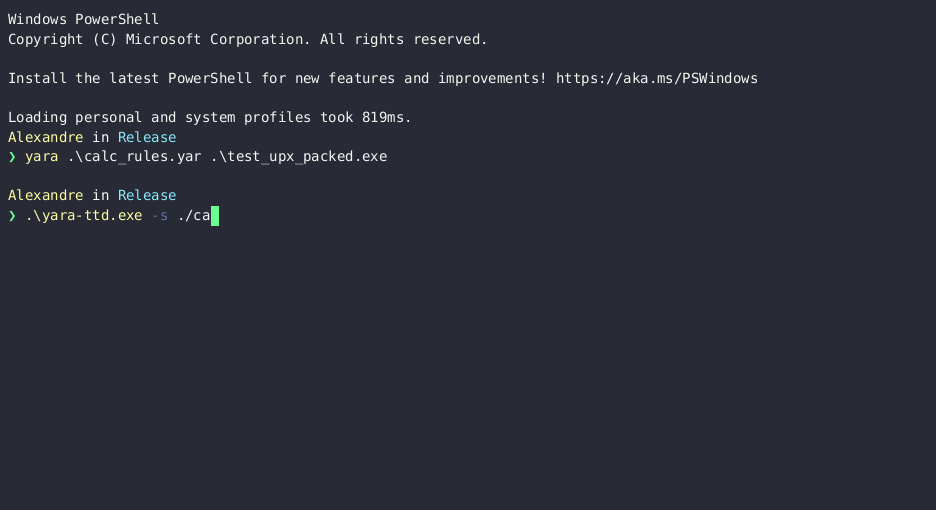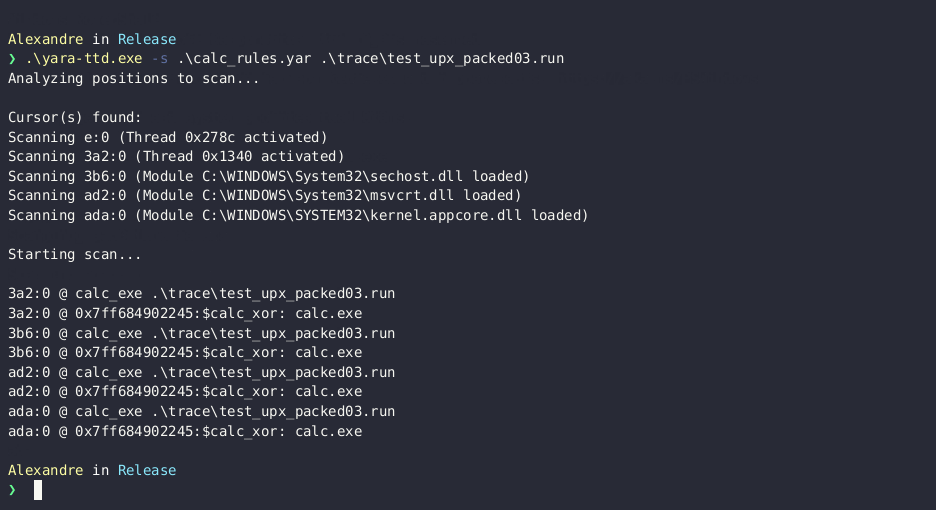 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces
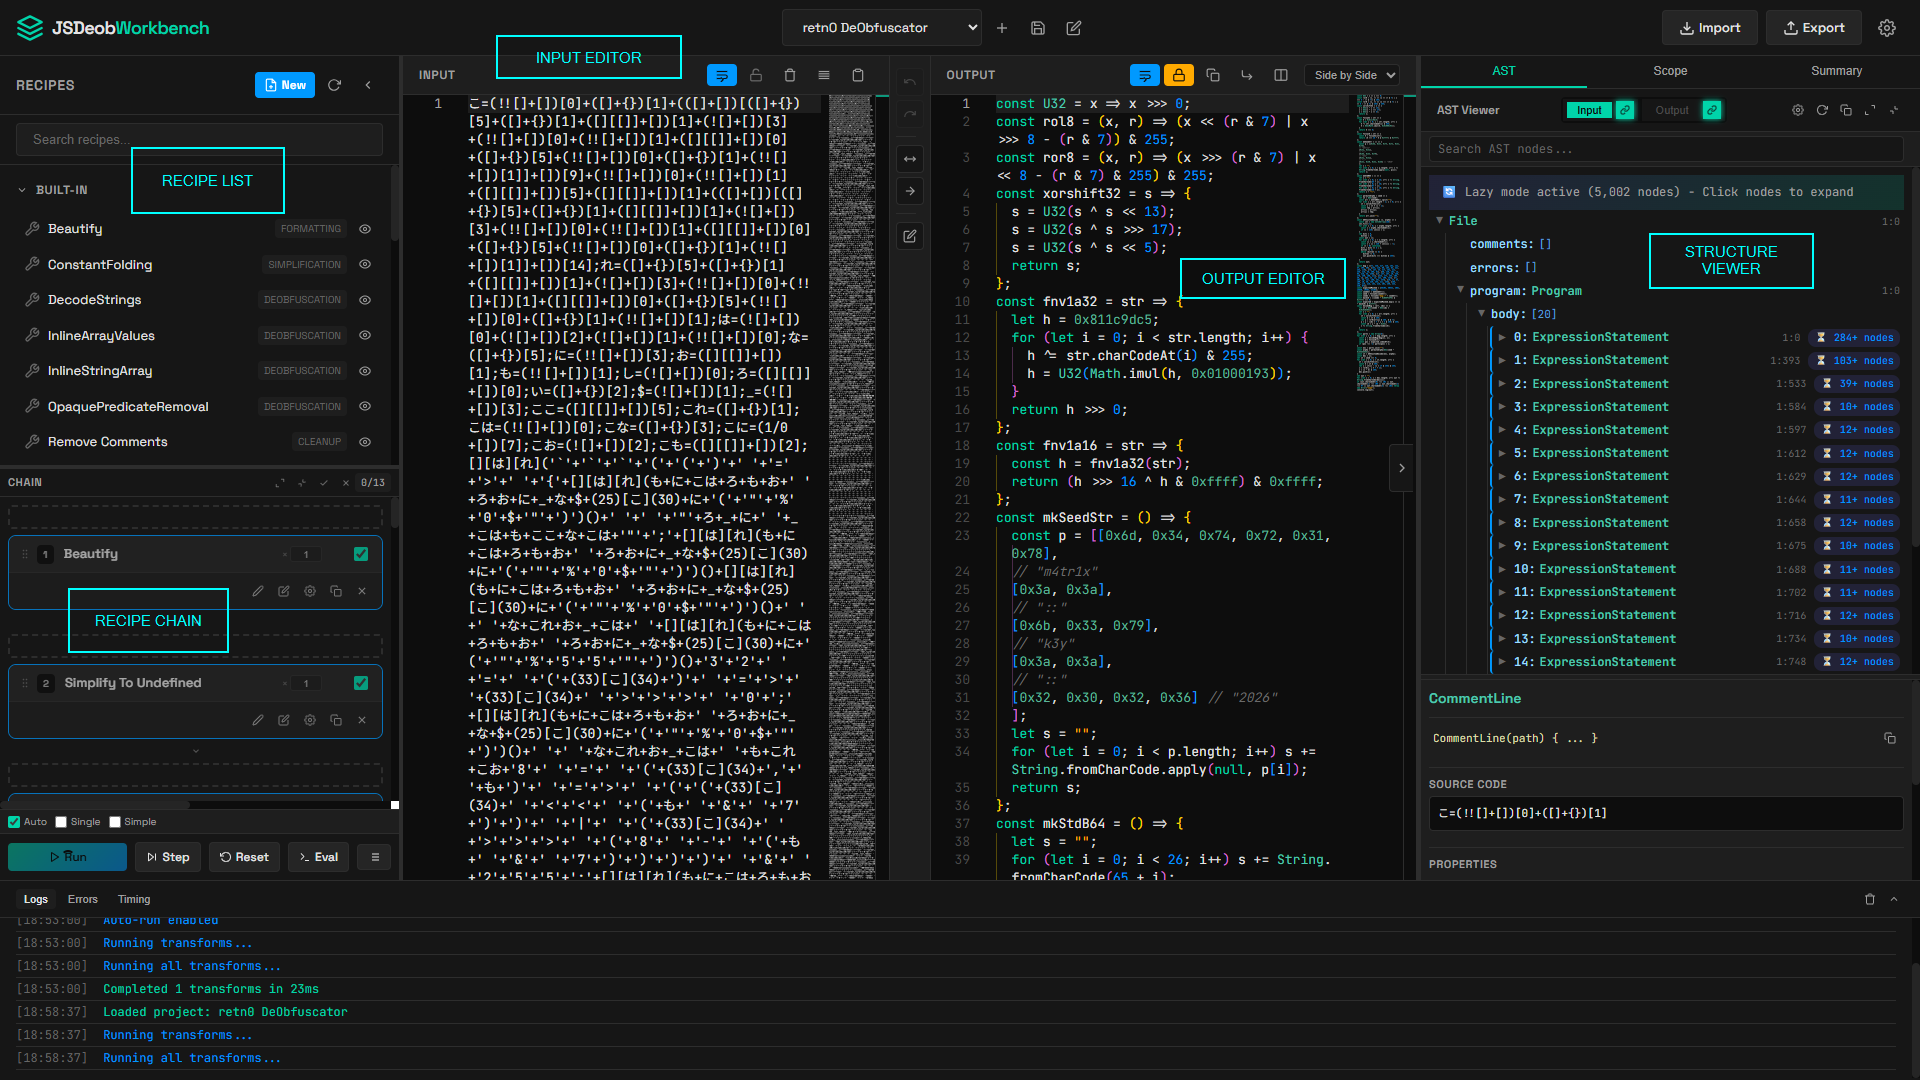 owl4444/jsdeob-workbench
Reverse engineer obfuscated JavaScript visually. Chain transforms, inspect AST changes, write reusable deobfuscation plugins.
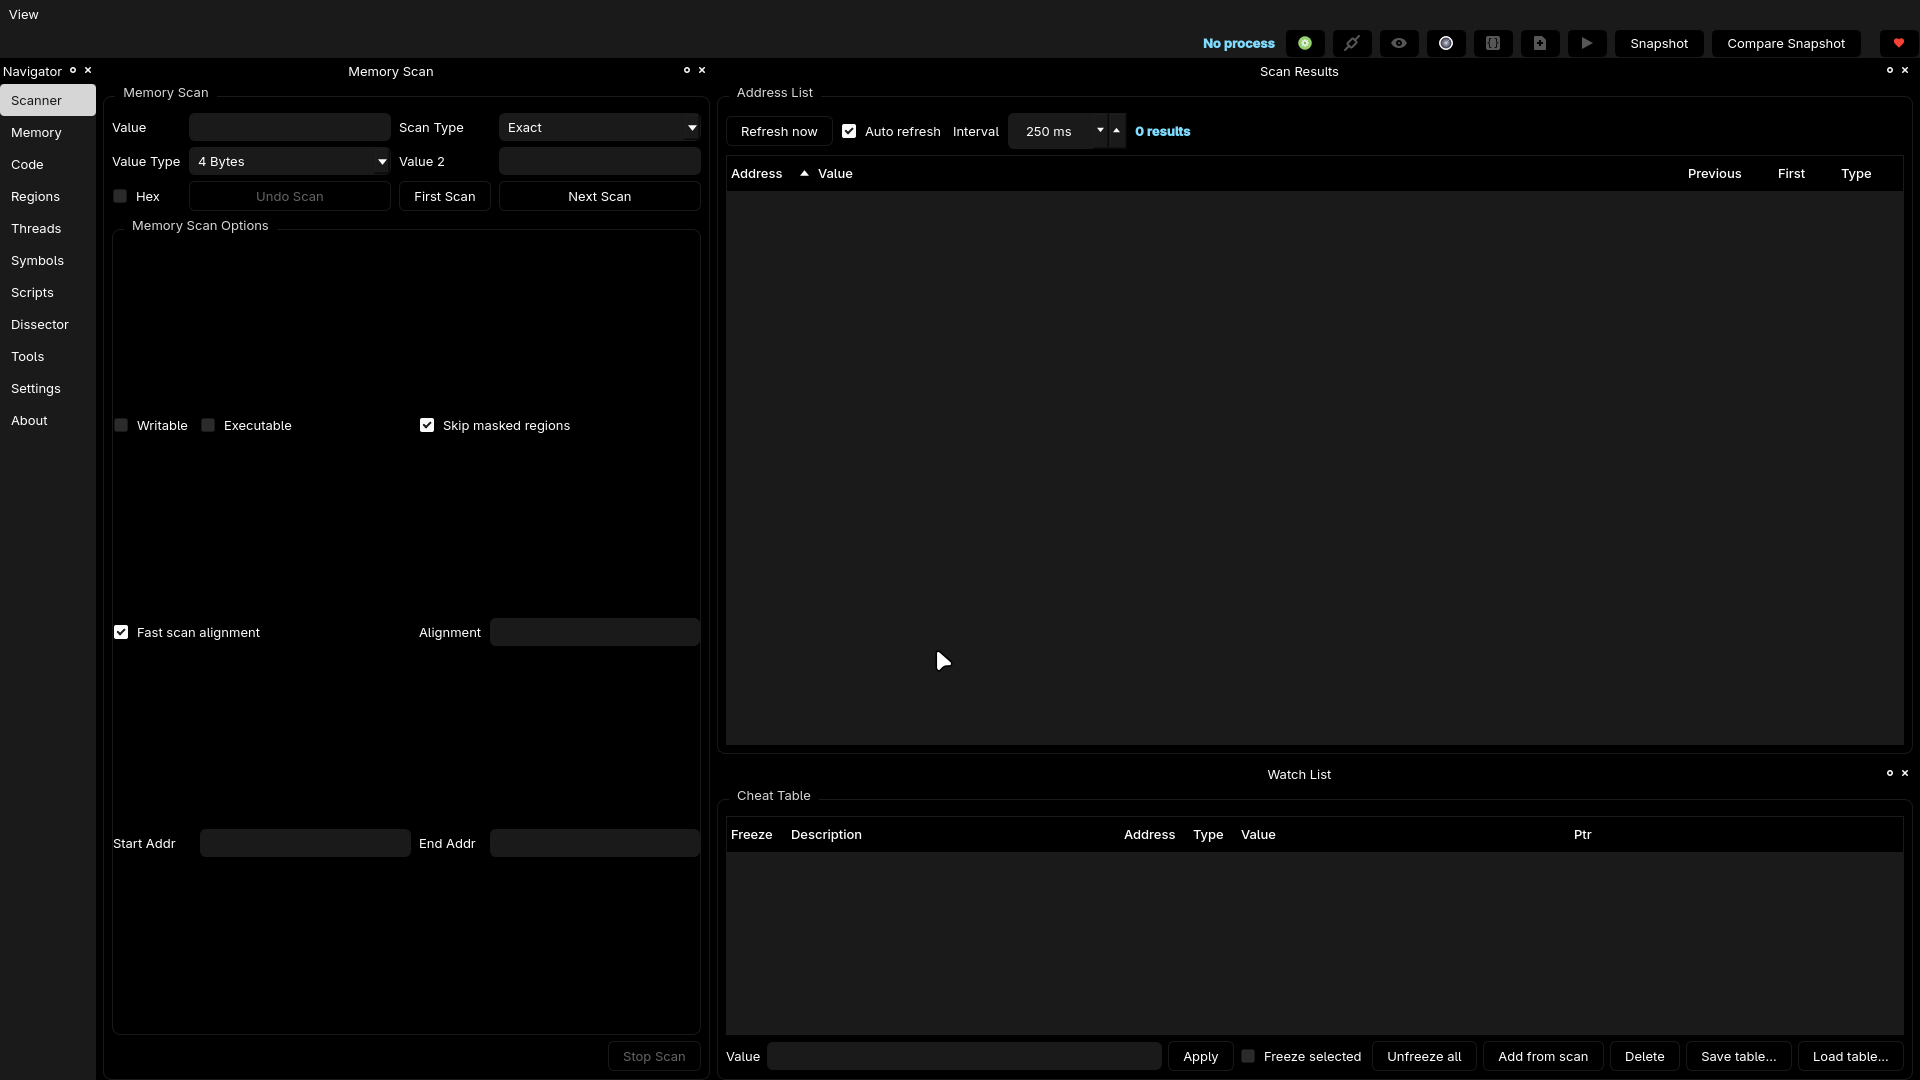 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect
 xteardx/diaphora-mcp
MCP server for automated binary diffing.