
CVE-2026-23907
 joakimbulow/cve-2026-23907
Proof-of-concept exploit for Apache PDFBox path traversal vulnerability (CVE-2026-23907), demonstrating arbitrary file write via malicious PDFs with…
binary-analysisexploitationmalware-analysis+3
joakimbulow/cve-2026-23907Proof-of-concept exploit for Apache PDFBox path traversal vulnerability (CVE-2026-23907), demonstrating arbitrary file write via malicious PDFs with…
 mohitsinghpapola/cve-2023-20052
Fixed Docker build for CVE-2023-20052 ClamAV XXE exploit. Resolves OpenSSL 3.0 compilation errors using Ubuntu 18.04 with OpenSSL 1.0 for…
 cyhe50/cve-2025-54874-poc
Proof-of-concept demonstrating a memory leak in OpenJPEG 2.5.1 via crafted JP2 files, triggering opj_read_header failure and heap leak, with valgrind…
 cdacesec/cve-2022-31901
Proof-of-concept exploit demonstrating a denial-of-service vulnerability in Notepad++ (x86) versions up to 8.4.9, triggered by opening specially…
 sandi-go/ps-2017-13---cve-2018-9950
Proof-of-concept for CVE-2018-9950, an out-of-bounds read vulnerability in Foxit Reader/PhantomPDF leading to information disclosure and potential…
 13m0n4de/pngcheck-vulns
A repository of proof-of-concept files demonstrating disclosed and patched vulnerabilities in pngcheck (2.4.0 - 3.0.1), including CVE-2020-27818,…
 tharindudh/tharindudh-log4j-vulnerability-in-ghidra-tool-cve-2021-44228
Ghidra-based tool for detecting and analyzing the Log4j vulnerability (CVE-2021-44228) in binary files, enabling reverse engineering of affected…
 sandi-go/cve-2018-15968
Technical disclosure of CVE-2018-15968: an out-of-bounds read vulnerability in Adobe Reader's PDF parsing, enabling information disclosure and…
 juul/xz-backdoor-scan
Scan for files containing the signature from the `xz` backdoor (CVE-2024-3094)
 mandiant/flashmingo
Automatic analysis of SWF files based on some heuristics. Extensible via plugins.
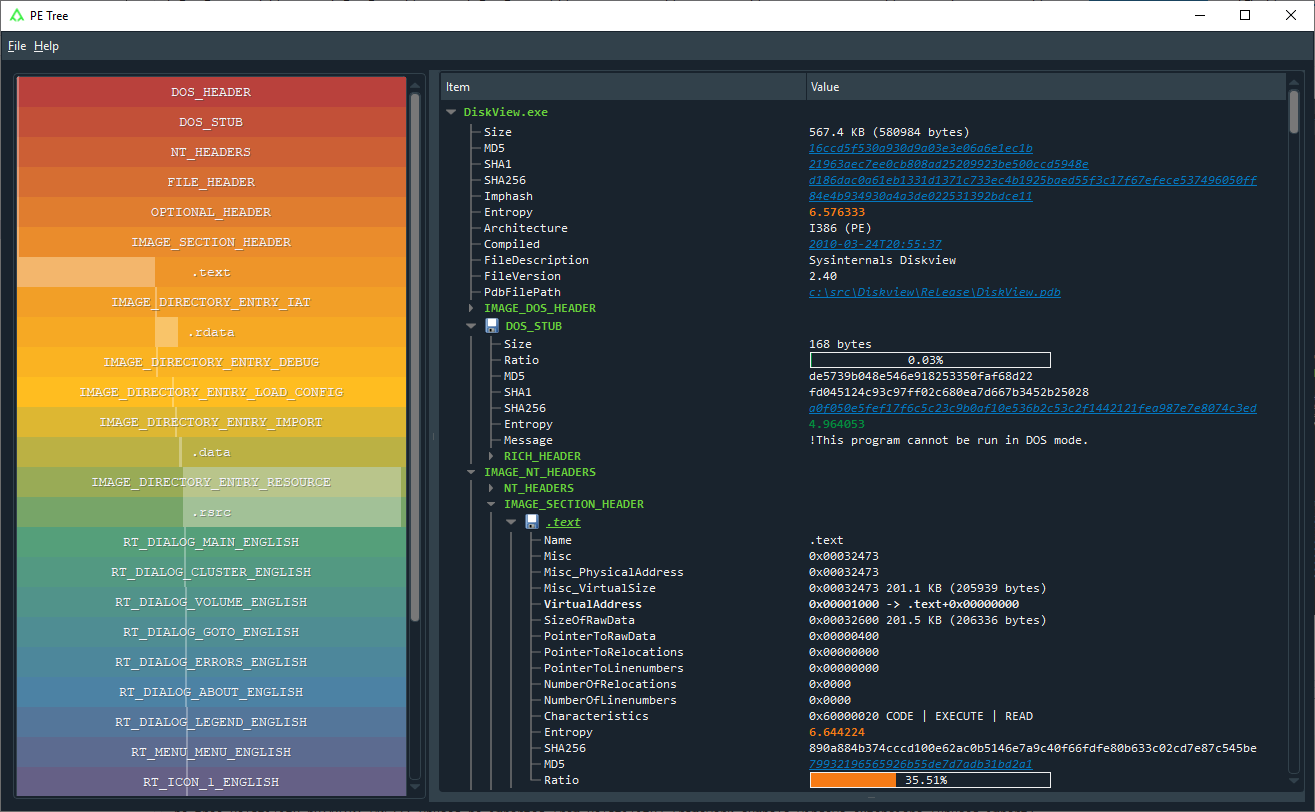 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 mrakovic-org/nashavm
Nasha is a Virtual Machine for .NET files and its runtime was made in C++/CLI
 lolbas-project/lolbas
Living Off The Land Binaries And Scripts - (LOLBins and LOLScripts)
 hasherezade/pe-bear
Portable Executable reversing tool with a friendly GUI
 google/bindiff
Quickly find differences and similarities in disassembled code
 justicerage/manalyze
Static analyzer for PE executables with plugin-based detection of packers, compilers, suspicious imports, cryptographic constants, and ClamAV…
 fabrimagic72/malware-samples
A collection of malware samples caught by several honeypots i manage
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…