
Archived
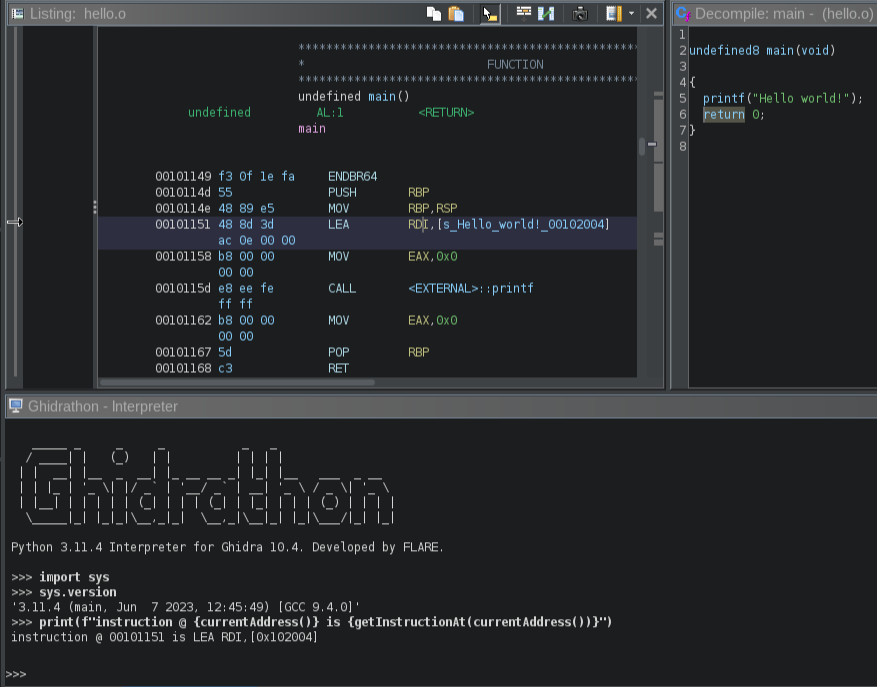
Ghidrathon
 mandiant/ghidrathon
The FLARE team's open-source extension to add Python 3 scripting to Ghidra.
binary-analysismalware-analysisreverse-engineering+1
789
mandiant/ghidrathonThe FLARE team's open-source extension to add Python 3 scripting to Ghidra.
 gallopsled/pwntools
CTF framework and exploit development library
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 mrexodia/ida-pro-mcp
AI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.
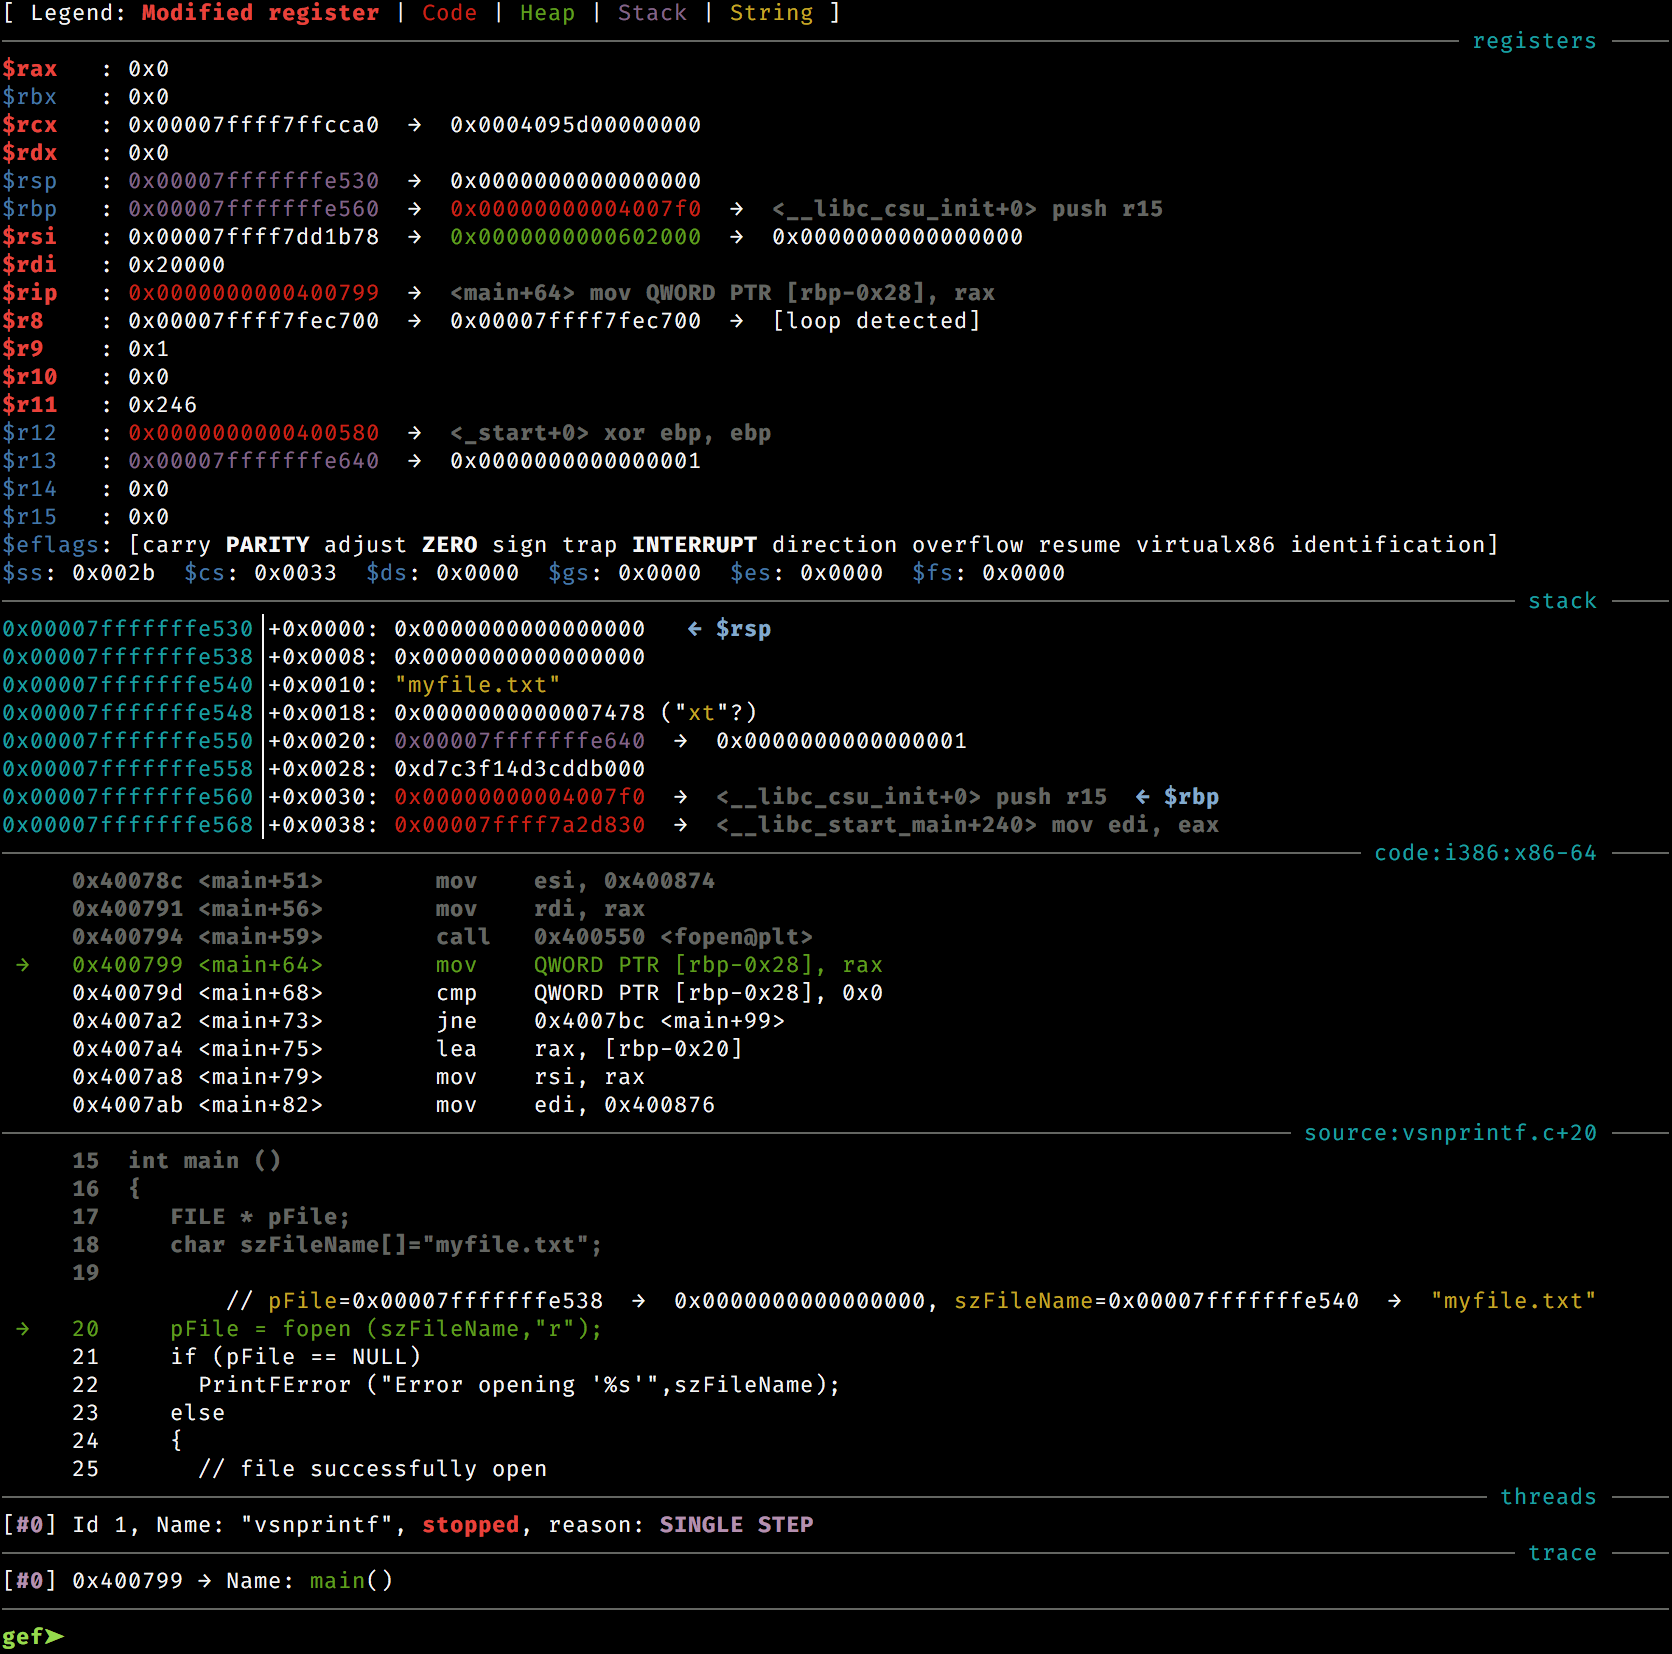 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 cs01/gdbgui
Browser-based frontend to gdb (gnu debugger). Add breakpoints, view the stack, visualize data structures, and more in C, C++, Go, Rust, and Fortran.…
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 onekey-sec/unblob
Extract files from any kind of container formats
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
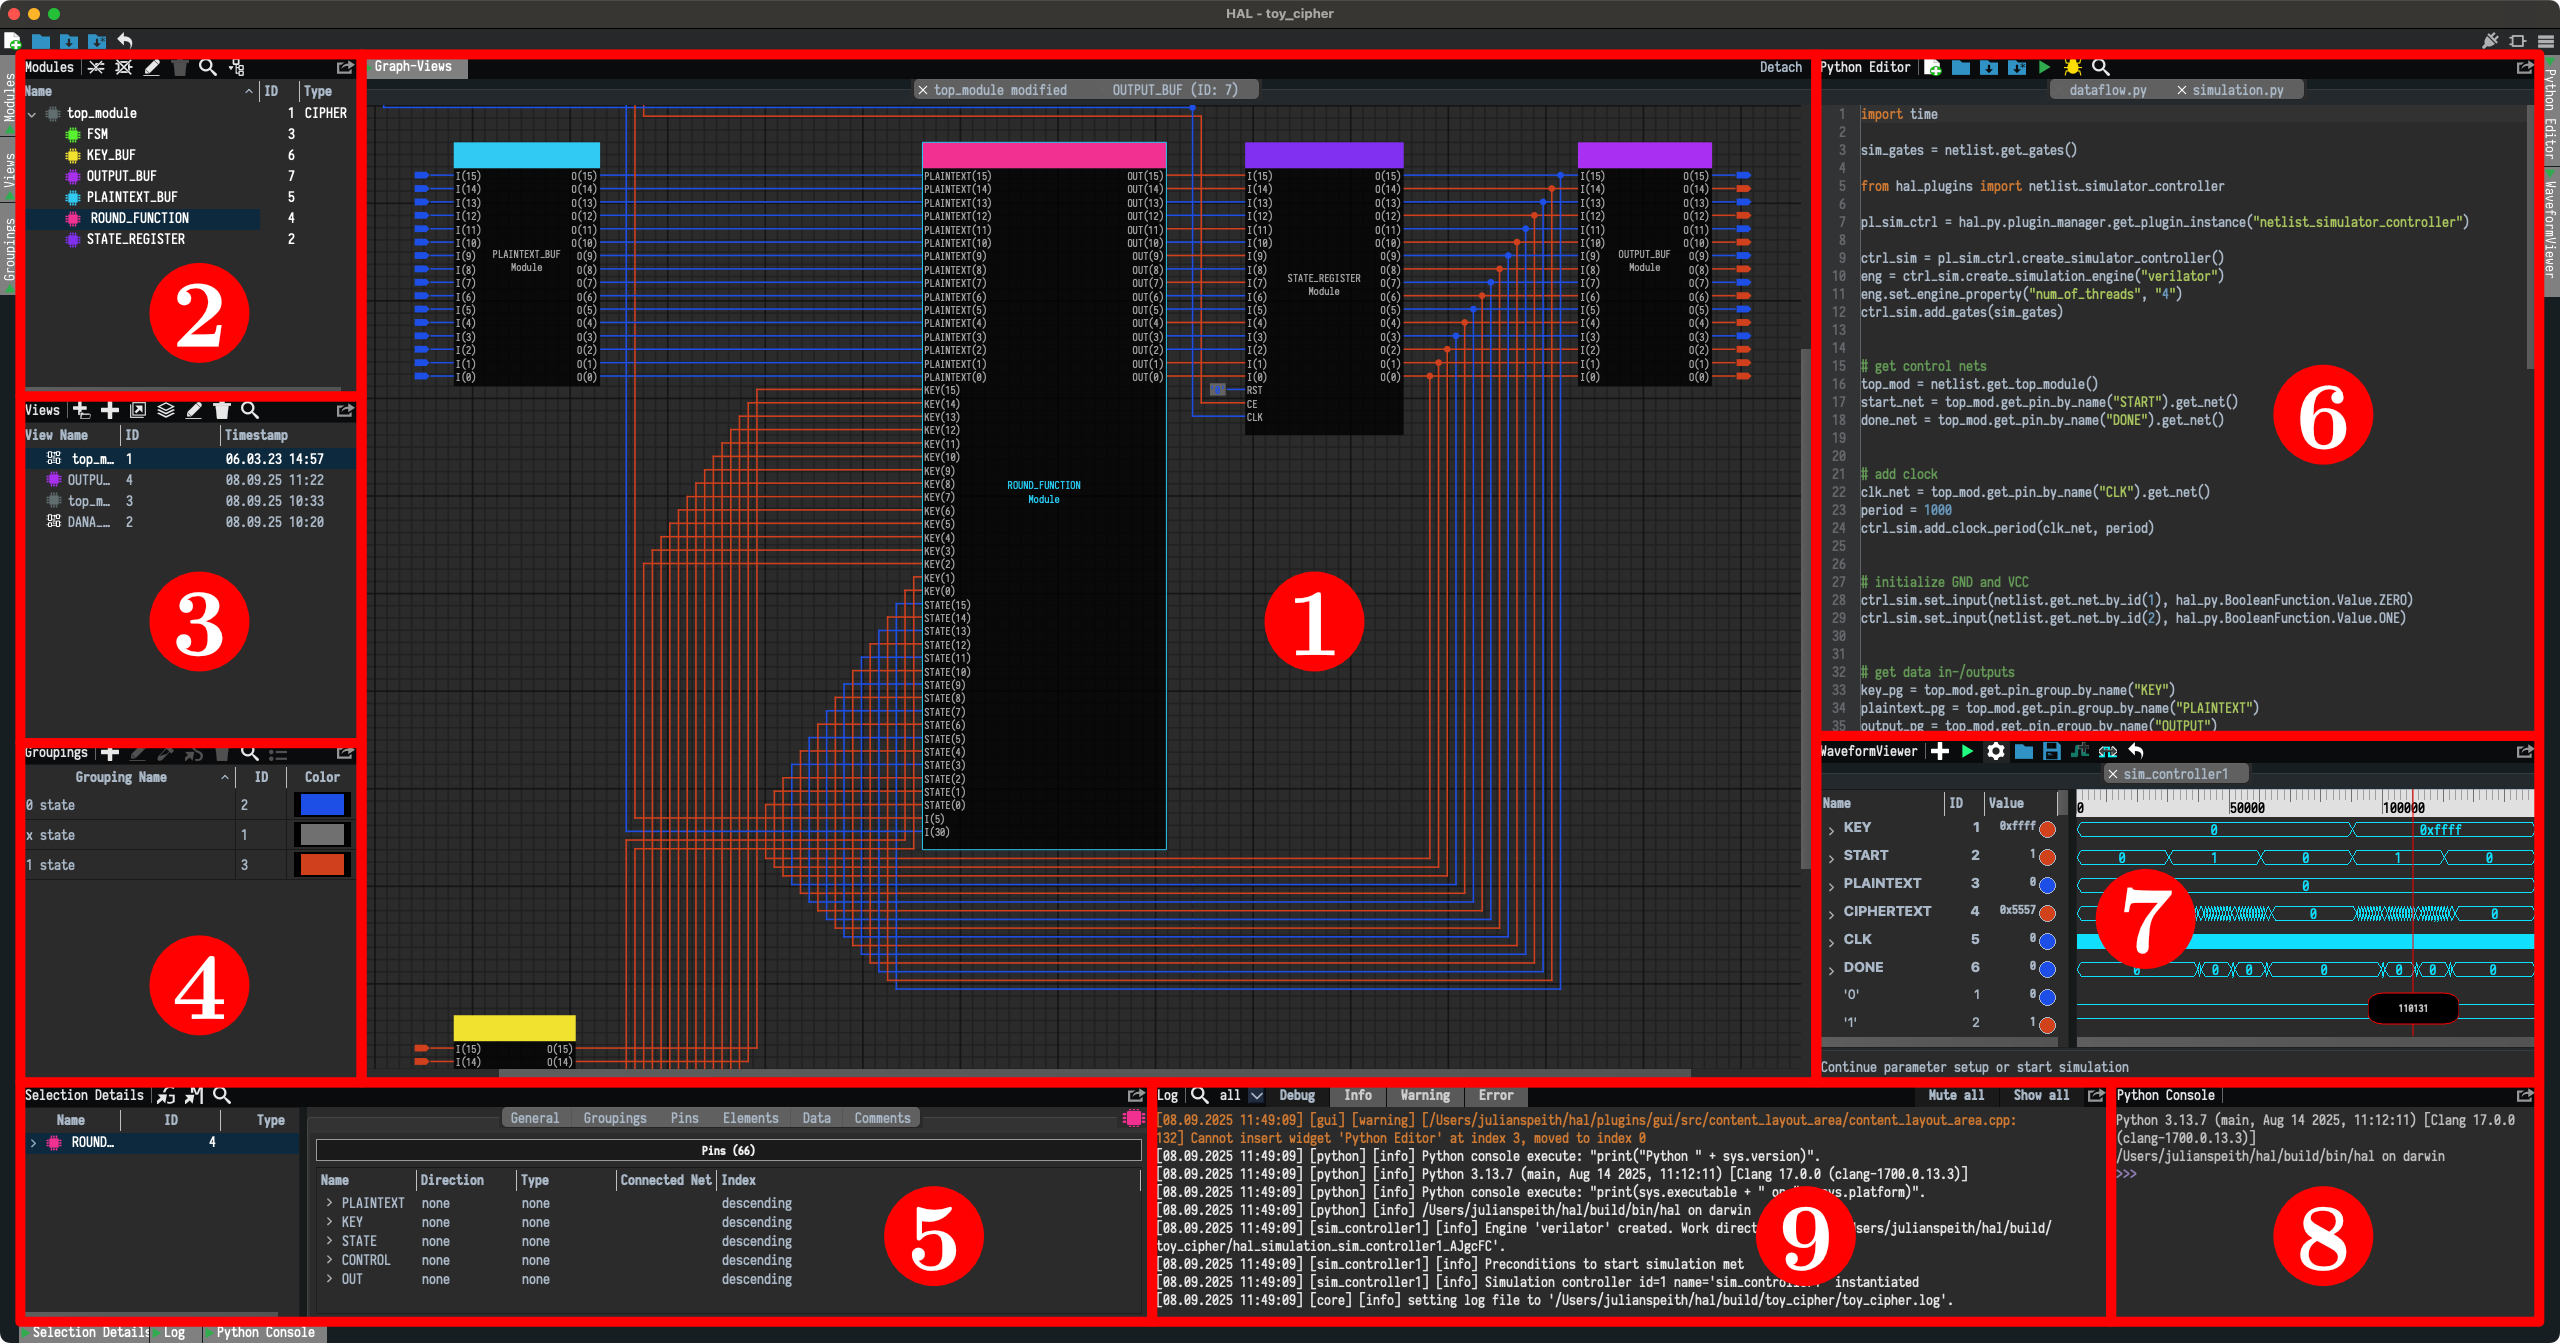
 airbus-seclab/bincat
Binary code static analyser, with IDA integration. Performs value and taint analysis, type reconstruction, use-after-free and double-free detection
 ergrelet/unlicense
Dynamic unpacker and import fixer for Themida/WinLicense 2.x and 3.x.
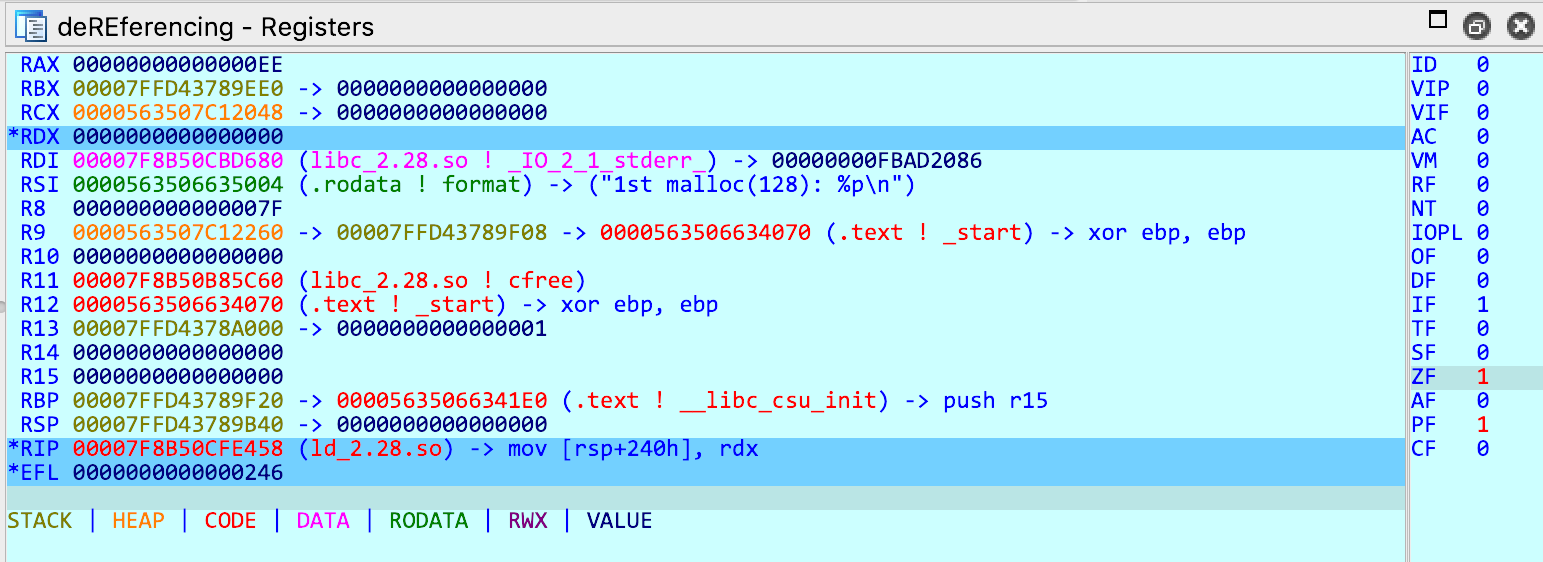 danigargu/dereferencing
IDA Pro plugin that implements more user-friendly register and stack views
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 danigargu/heap-viewer
IDA Pro plugin to examine the glibc heap, focused on exploit development
 netzob/netzob
Open-source toolkit for reverse engineering, modeling, and fuzzing communication protocols. Infers message formats and state machines from network…