
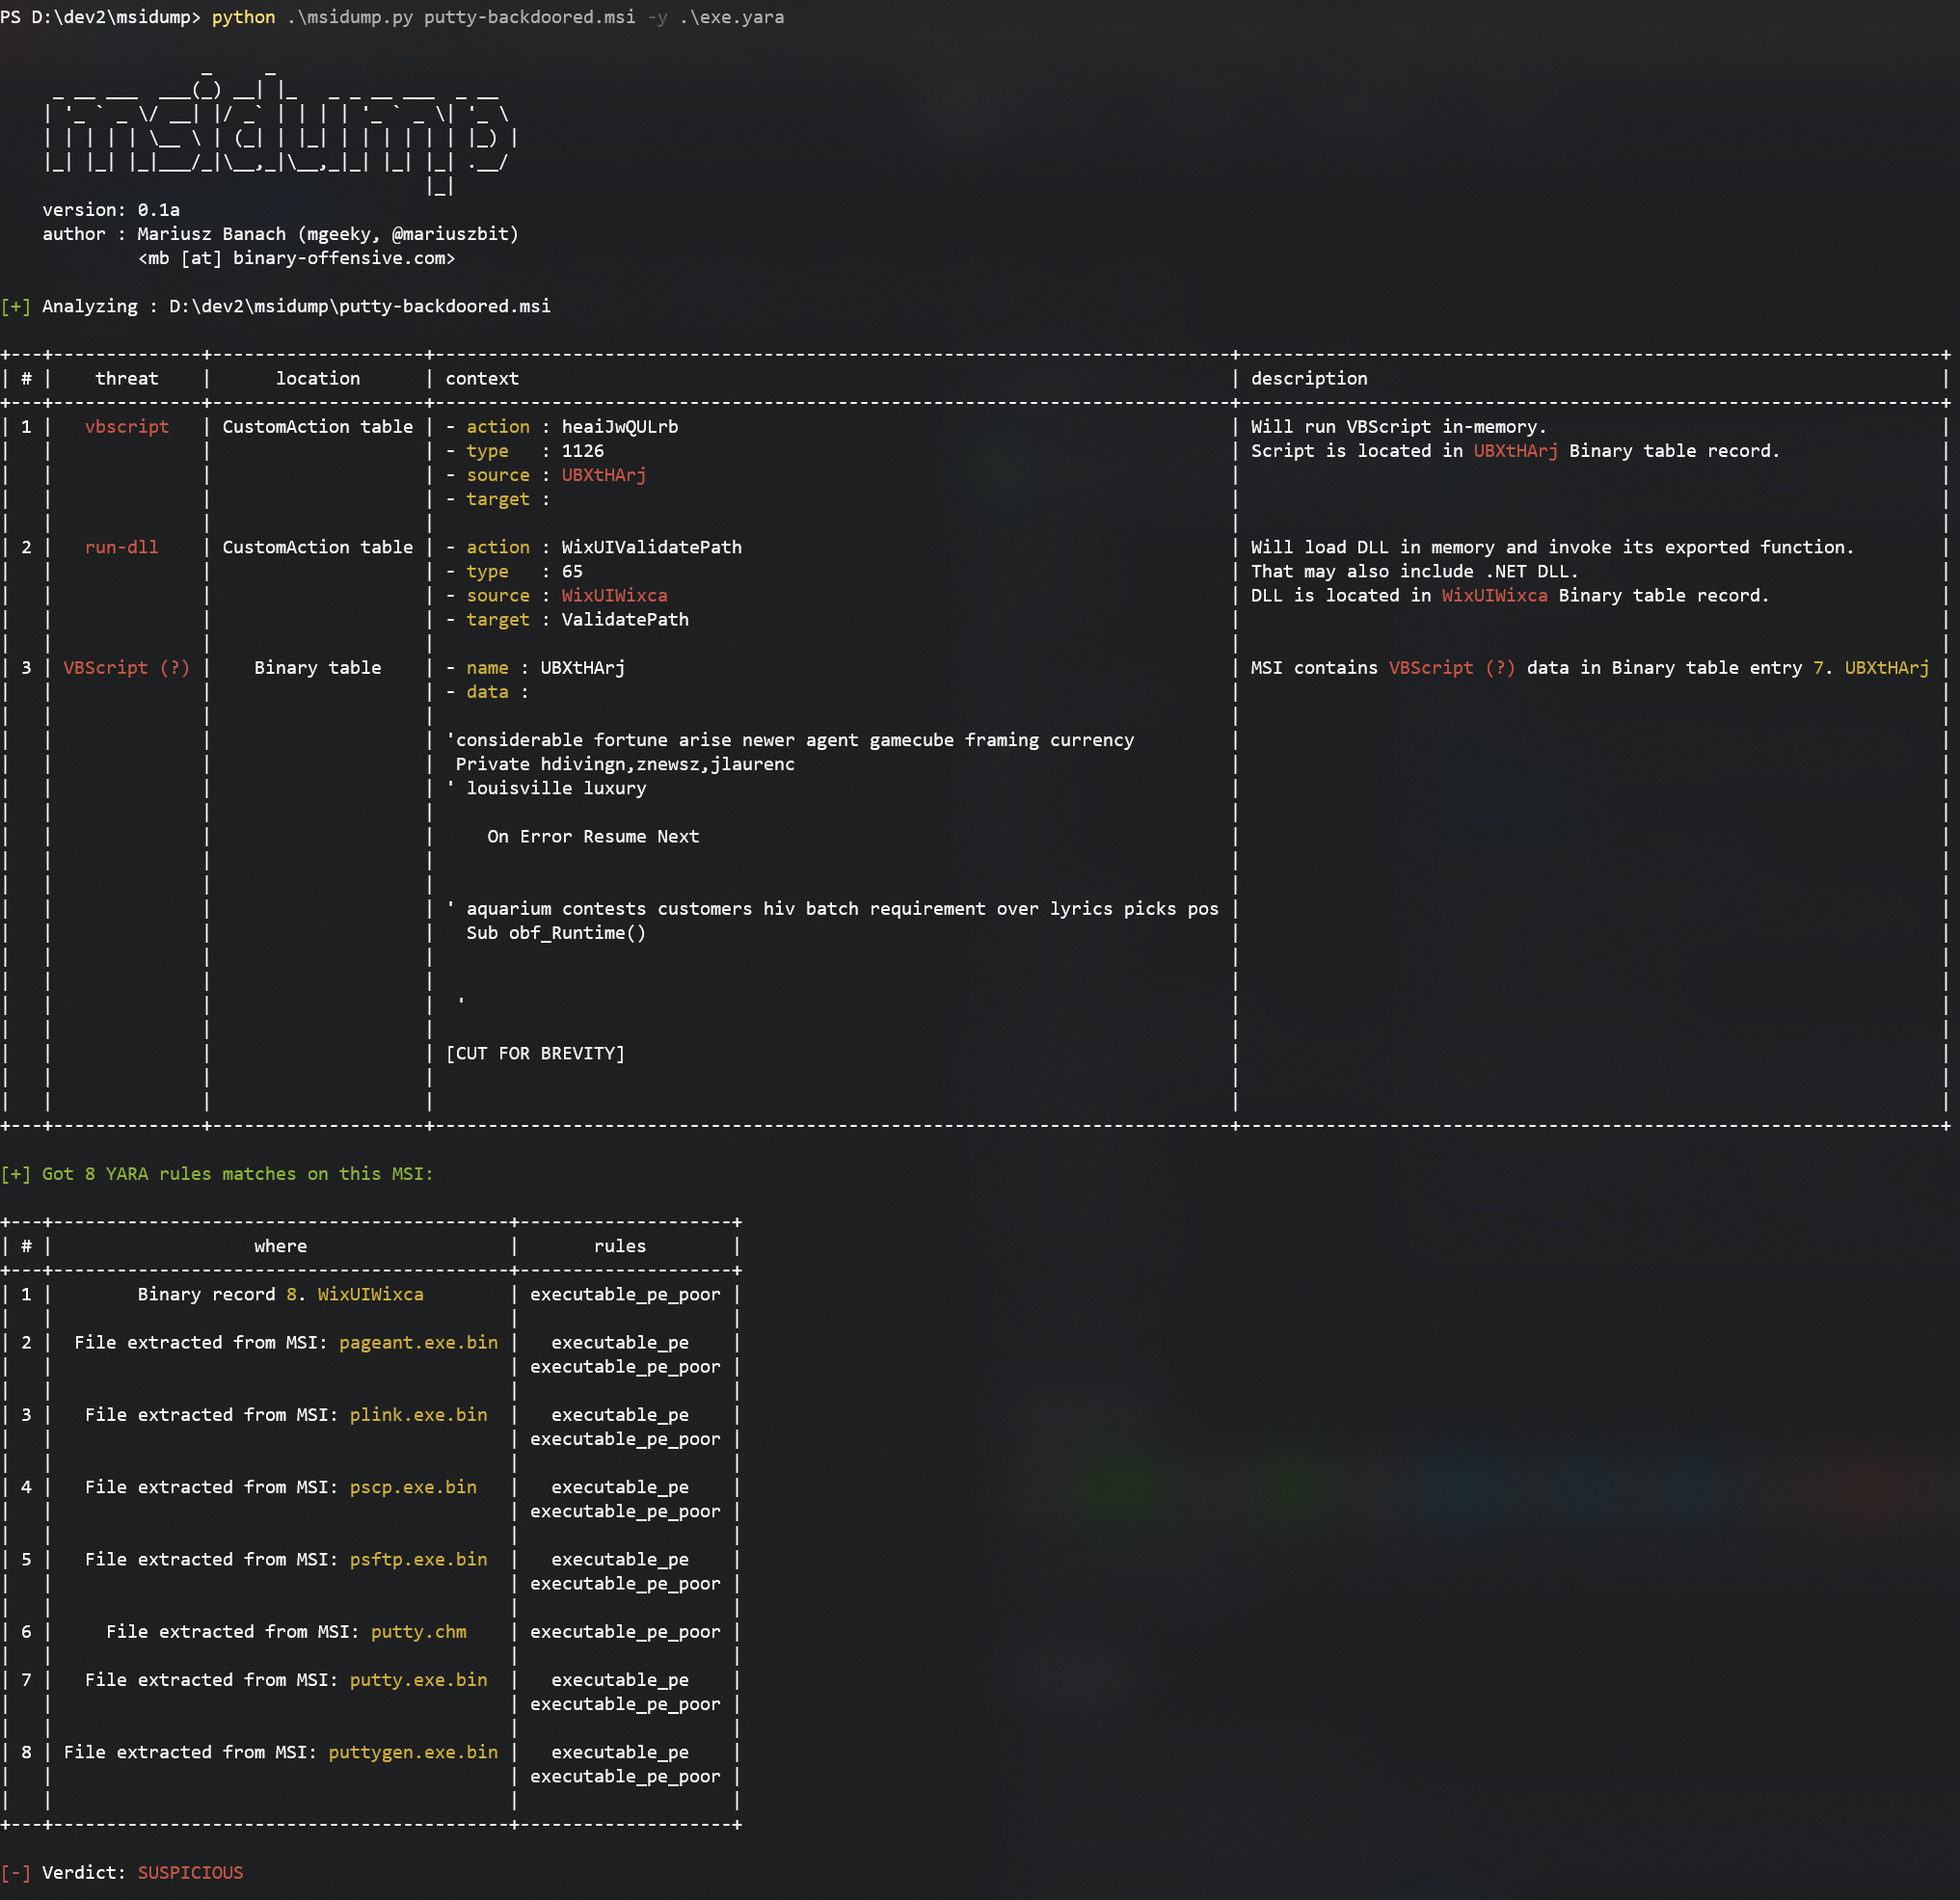
msidump
 mgeeky/msidump
MSI Dump - a tool that analyzes malicious MSI installation packages, extracts files, streams, binary data and incorporates YARA scanner.
binary-analysisforensicsmalware-analysis+1
232
mgeeky/msidumpMSI Dump - a tool that analyzes malicious MSI installation packages, extracts files, streams, binary data and incorporates YARA scanner.
 strivexjun/memorymodulepp
C++ library to load DLLs directly from memory without touching disk, with exception handling support, enabling stealthy code execution and evasion of…
 cristianzsh/freki
Open-source malware analysis platform with static PE analysis, YARA pattern matching, VirusTotal integration, REST API, and Docker deployment for…
 reb311ion/replica
Ghidra plugin that enhances reverse engineering by fixing missed disassembly, detecting functions, labeling crypto constants, and renaming functions…
 ubfx/bindiffhelper
Ghidra Extension to integrate BinDiff for function matching
 4w4k3/repy2exe
A Reverse Engineering Tool for py2exe applications.
 denuvosoftwaresolutions/gamba
Simplification of General Mixed Boolean-Arithmetic Expressions: GAMBA
 ergrelet/themida-unmutate
Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
 oalabs/findyara-ida
IDA python plugin to scan binary with Yara rules
 mandiant/dncil
The FLARE team's open-source library to disassemble Common Intermediate Language (CIL) instructions.
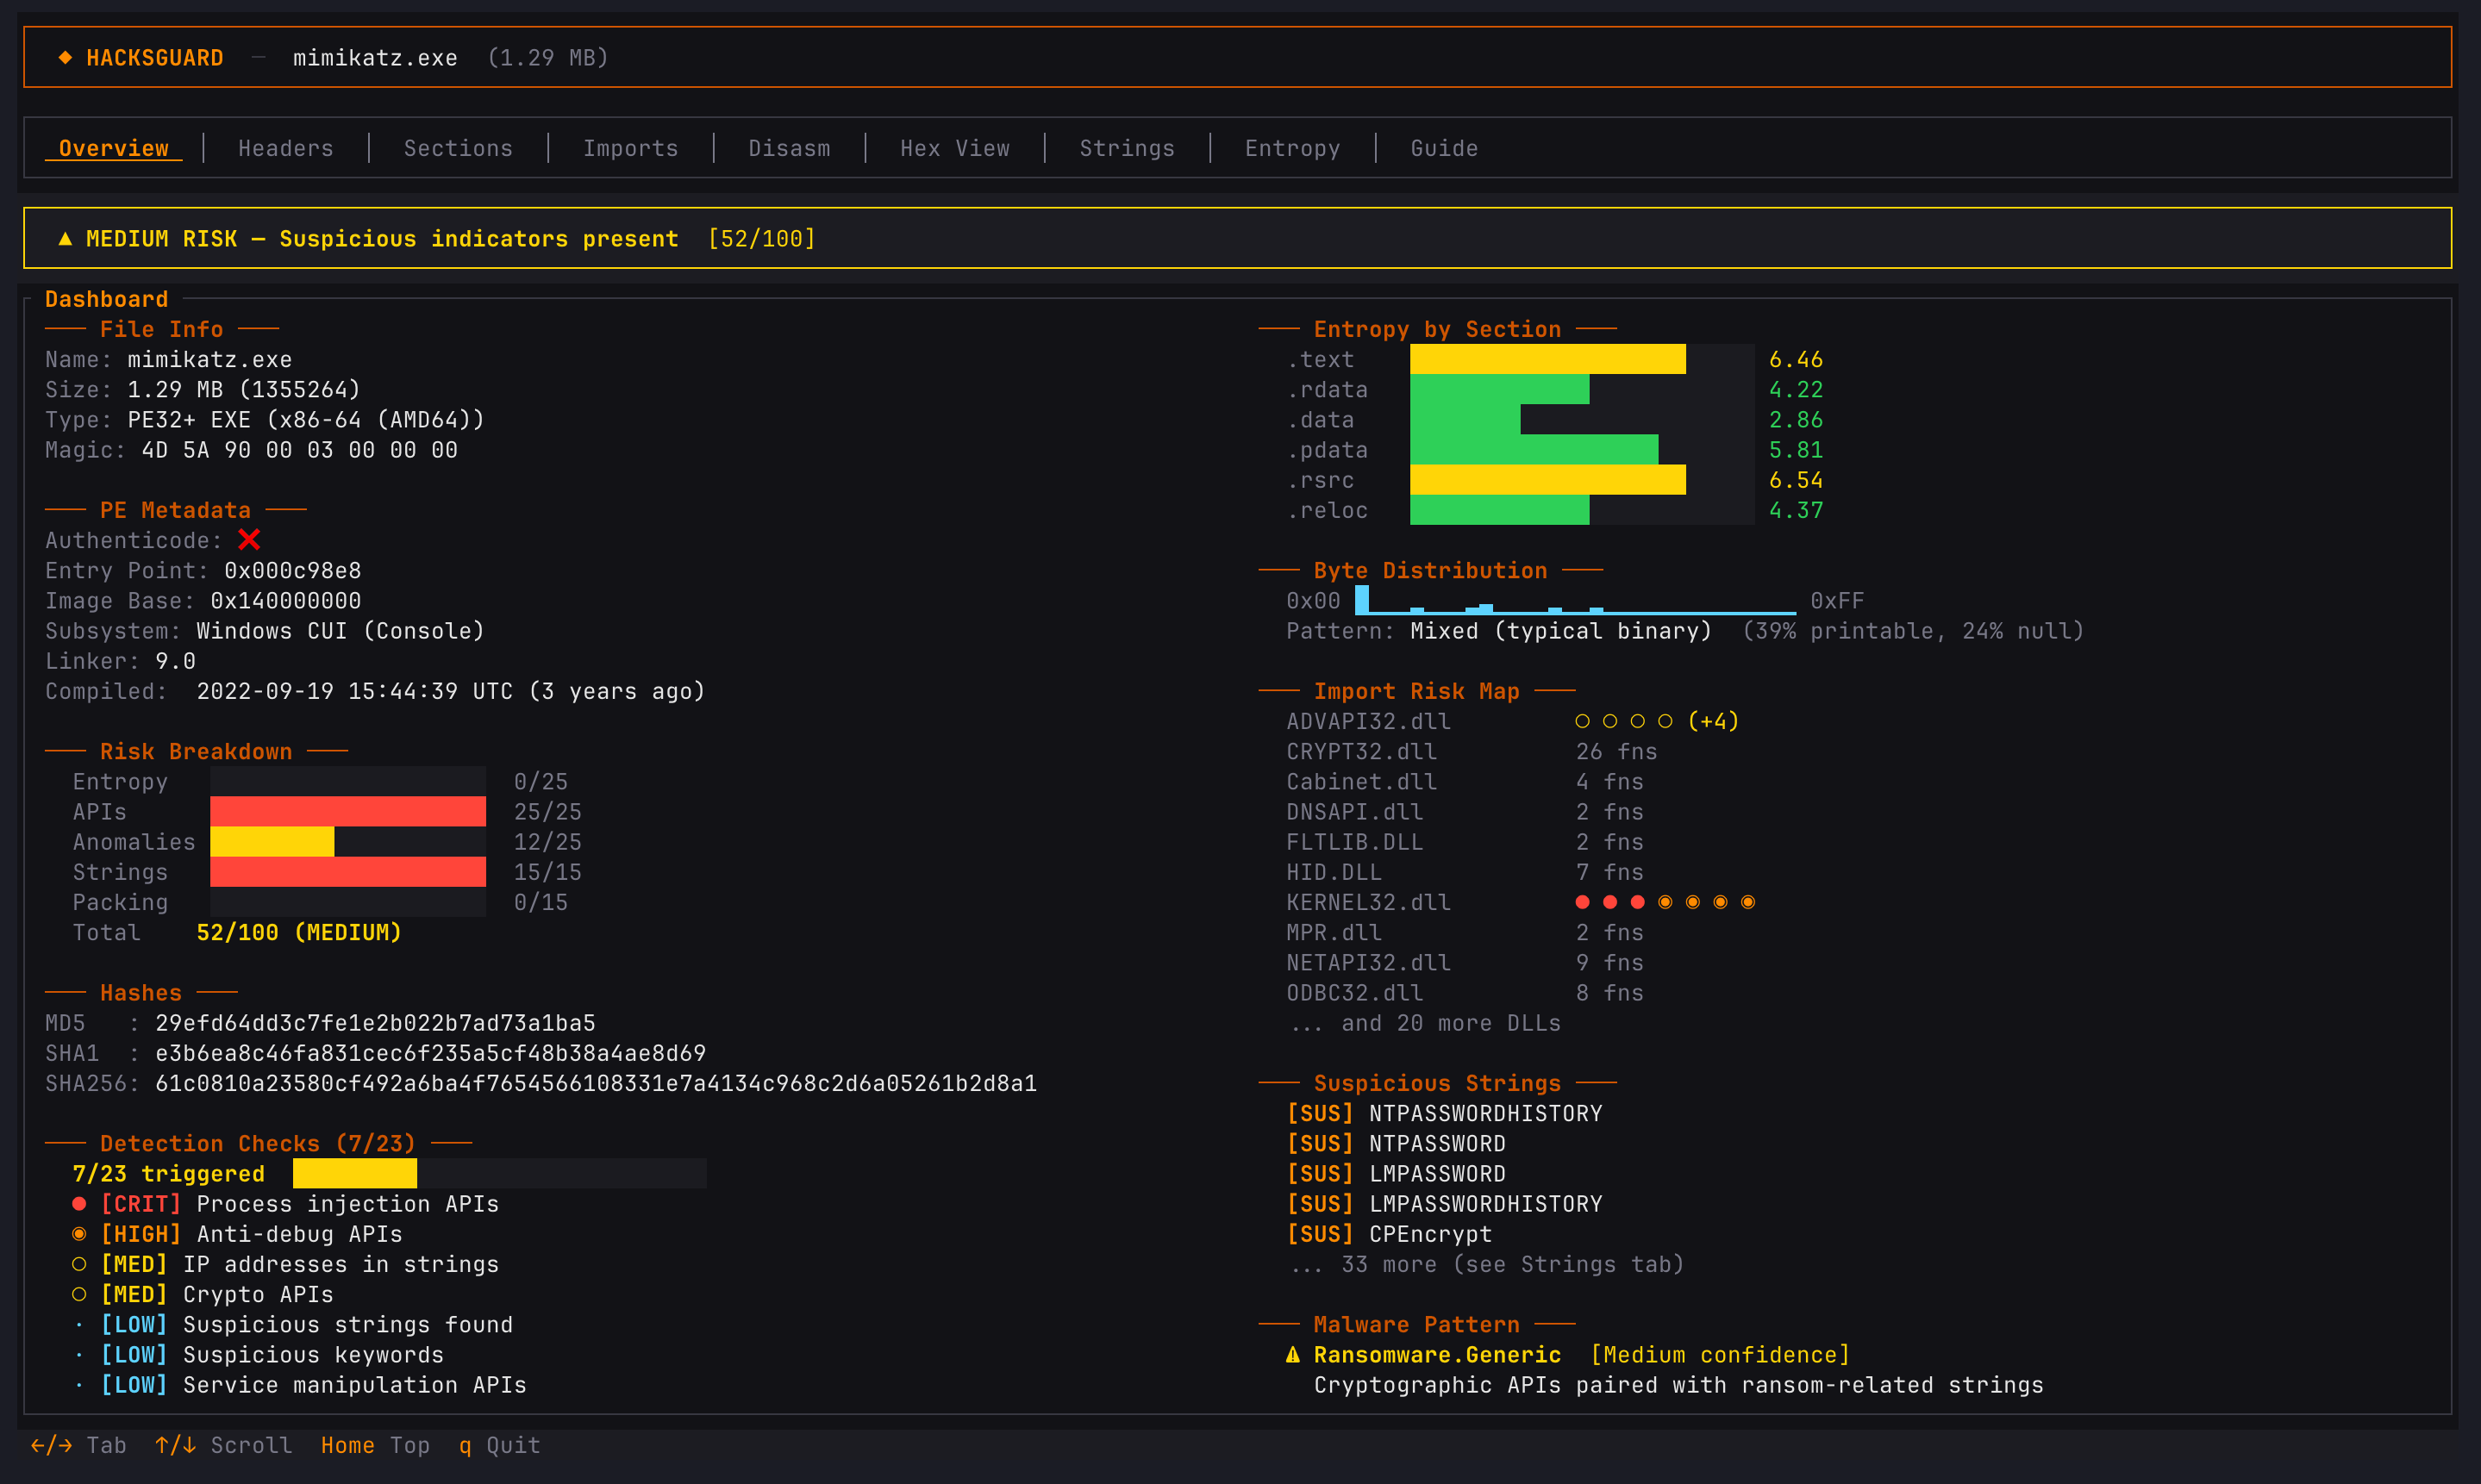 rhacknarok/hacksguard
A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.
 armadito/armadito-av
Armadito antivirus main repository
 mrphrazer/obfuscation_analysis
Binary Ninja plugin to analyze and simplify obfuscated code
 malwaretech/fakembr
TDL4 style rootkit to spoof read/write requests to master boot record
 nazywam/autoit-ripper
Extract AutoIt scripts embedded in PE binaries
 sandflysecurity/sandfly-entropyscan
Entropy scanner for Linux to detect packed or encrypted binaries related to malware. Finds malicious files and Linux processes and gives output with…
 dr4k0nia/niximports
A .NET malware loader, using API-Hashing to evade static analysis
 dimareverse/nuitka-static-unpacker
Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.