Archived
certfuzz
 certcc/certfuzz
This project contains the source code for the CERT Basic Fuzzing Framework (BFF) and the CERT Failure Observation Engine (FOE).
binary-analysisdynamic-analysis-sandboxingexploitation+3
 reverseclabs/needle
The iOS Security Testing Framework
 didi/kemon
An Open-Source Pre and Post Callback-Based Framework for macOS Kernel Monitoring.
 viper-framework/viper
Binary analysis and management framework
 angr/angr
A powerful and user-friendly binary analysis platform!
 lepotekil/msfmania
Python AV Evasion Tools
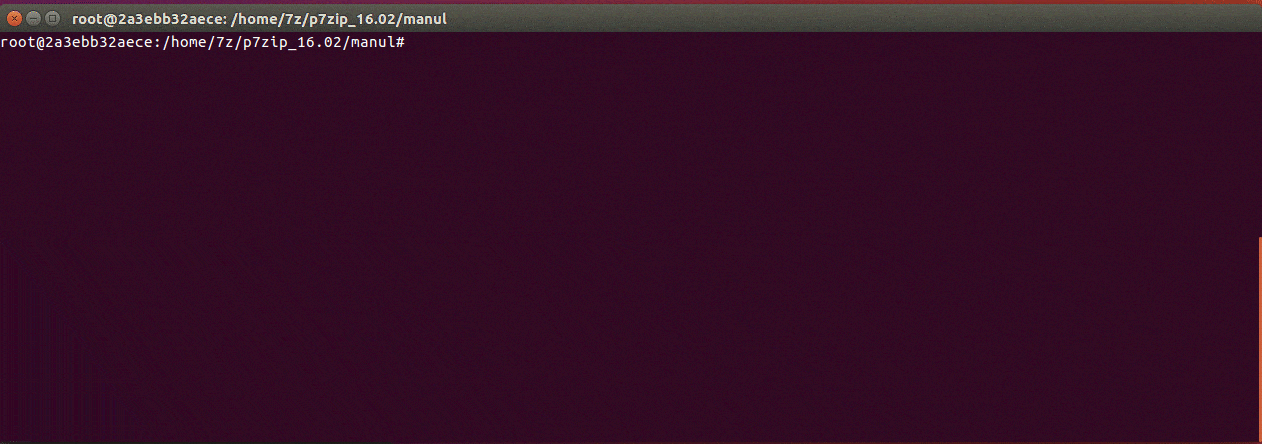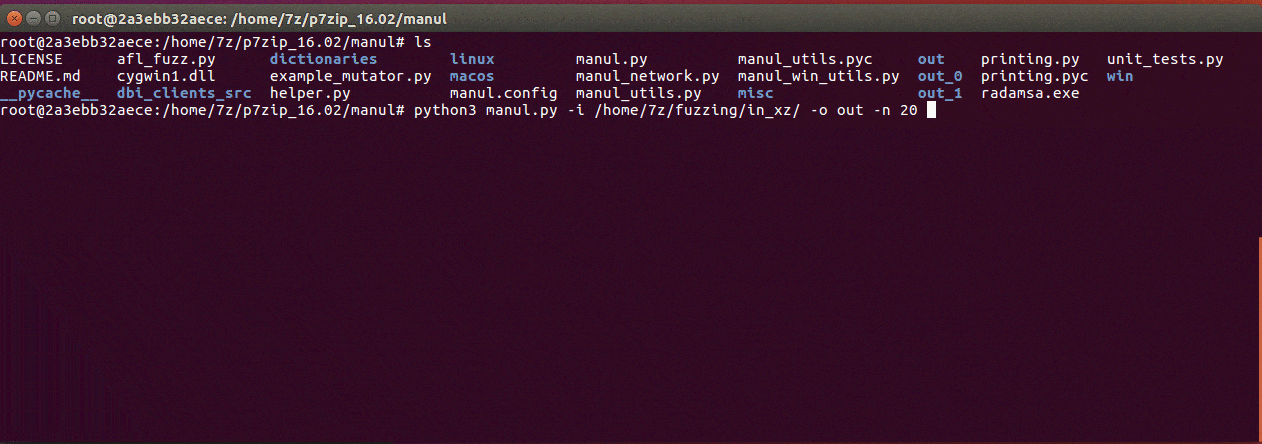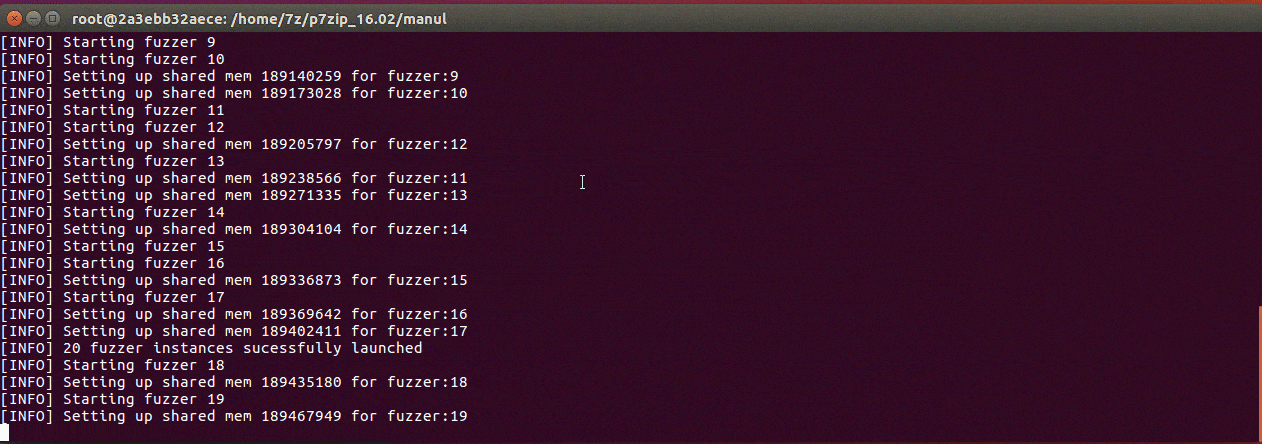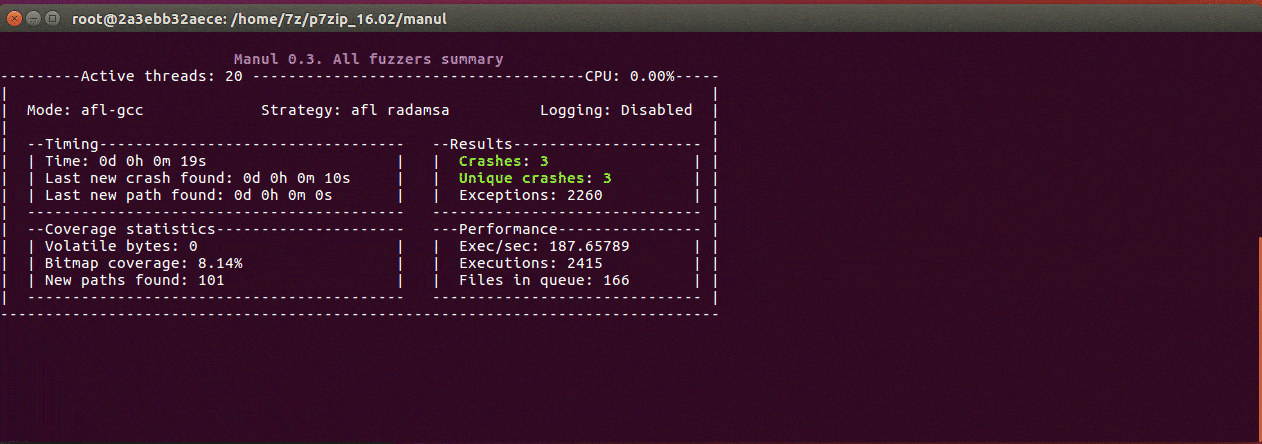 mxmssh/manul
Manul is a coverage-guided parallel fuzzer for open-source and blackbox binaries on Windows, Linux and MacOS
 splintersfury/autopiff
Semantic analysis engine for detecting vulnerability fixes in Windows kernel driver patches — 58 YAML rules, Ghidra decompilation, reachability…
 chris1sflaggin/lcsajdump
An ML powered Graph-Based Multi-Architecture Approach for ROP Gadget Detection
 vollragm/ghostdebug
Debugger utilizing stealth hooks to hide from debugger detection
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 boku7/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
 jackofmosttrades/gadgetinspector
A byte code analyzer for finding deserialization gadget chains in Java applications
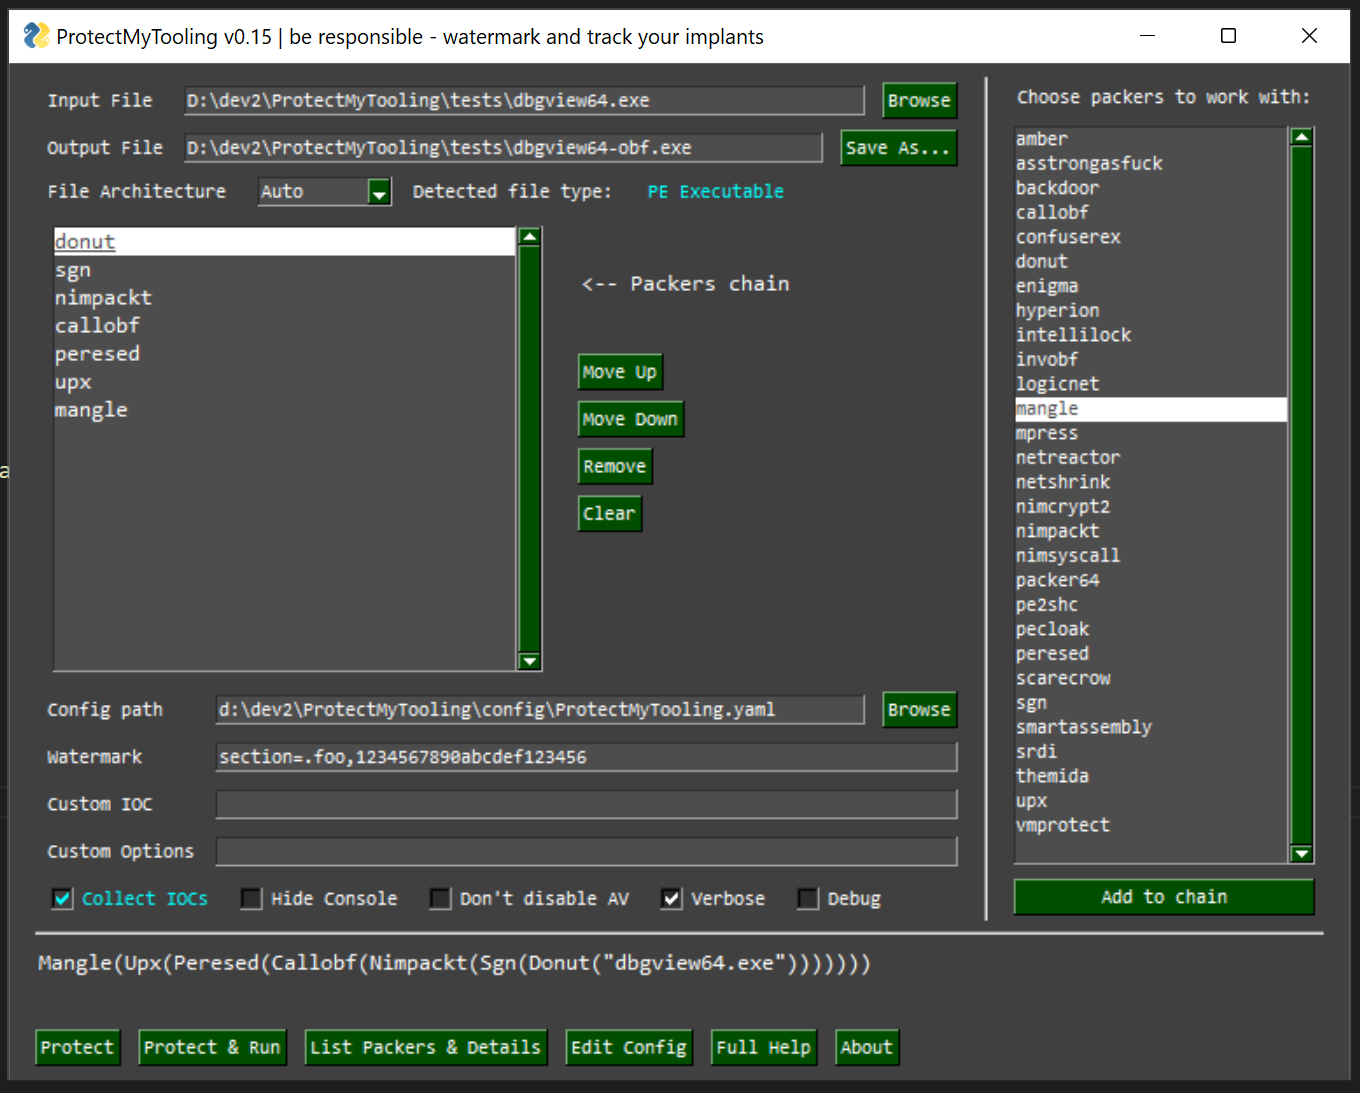 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
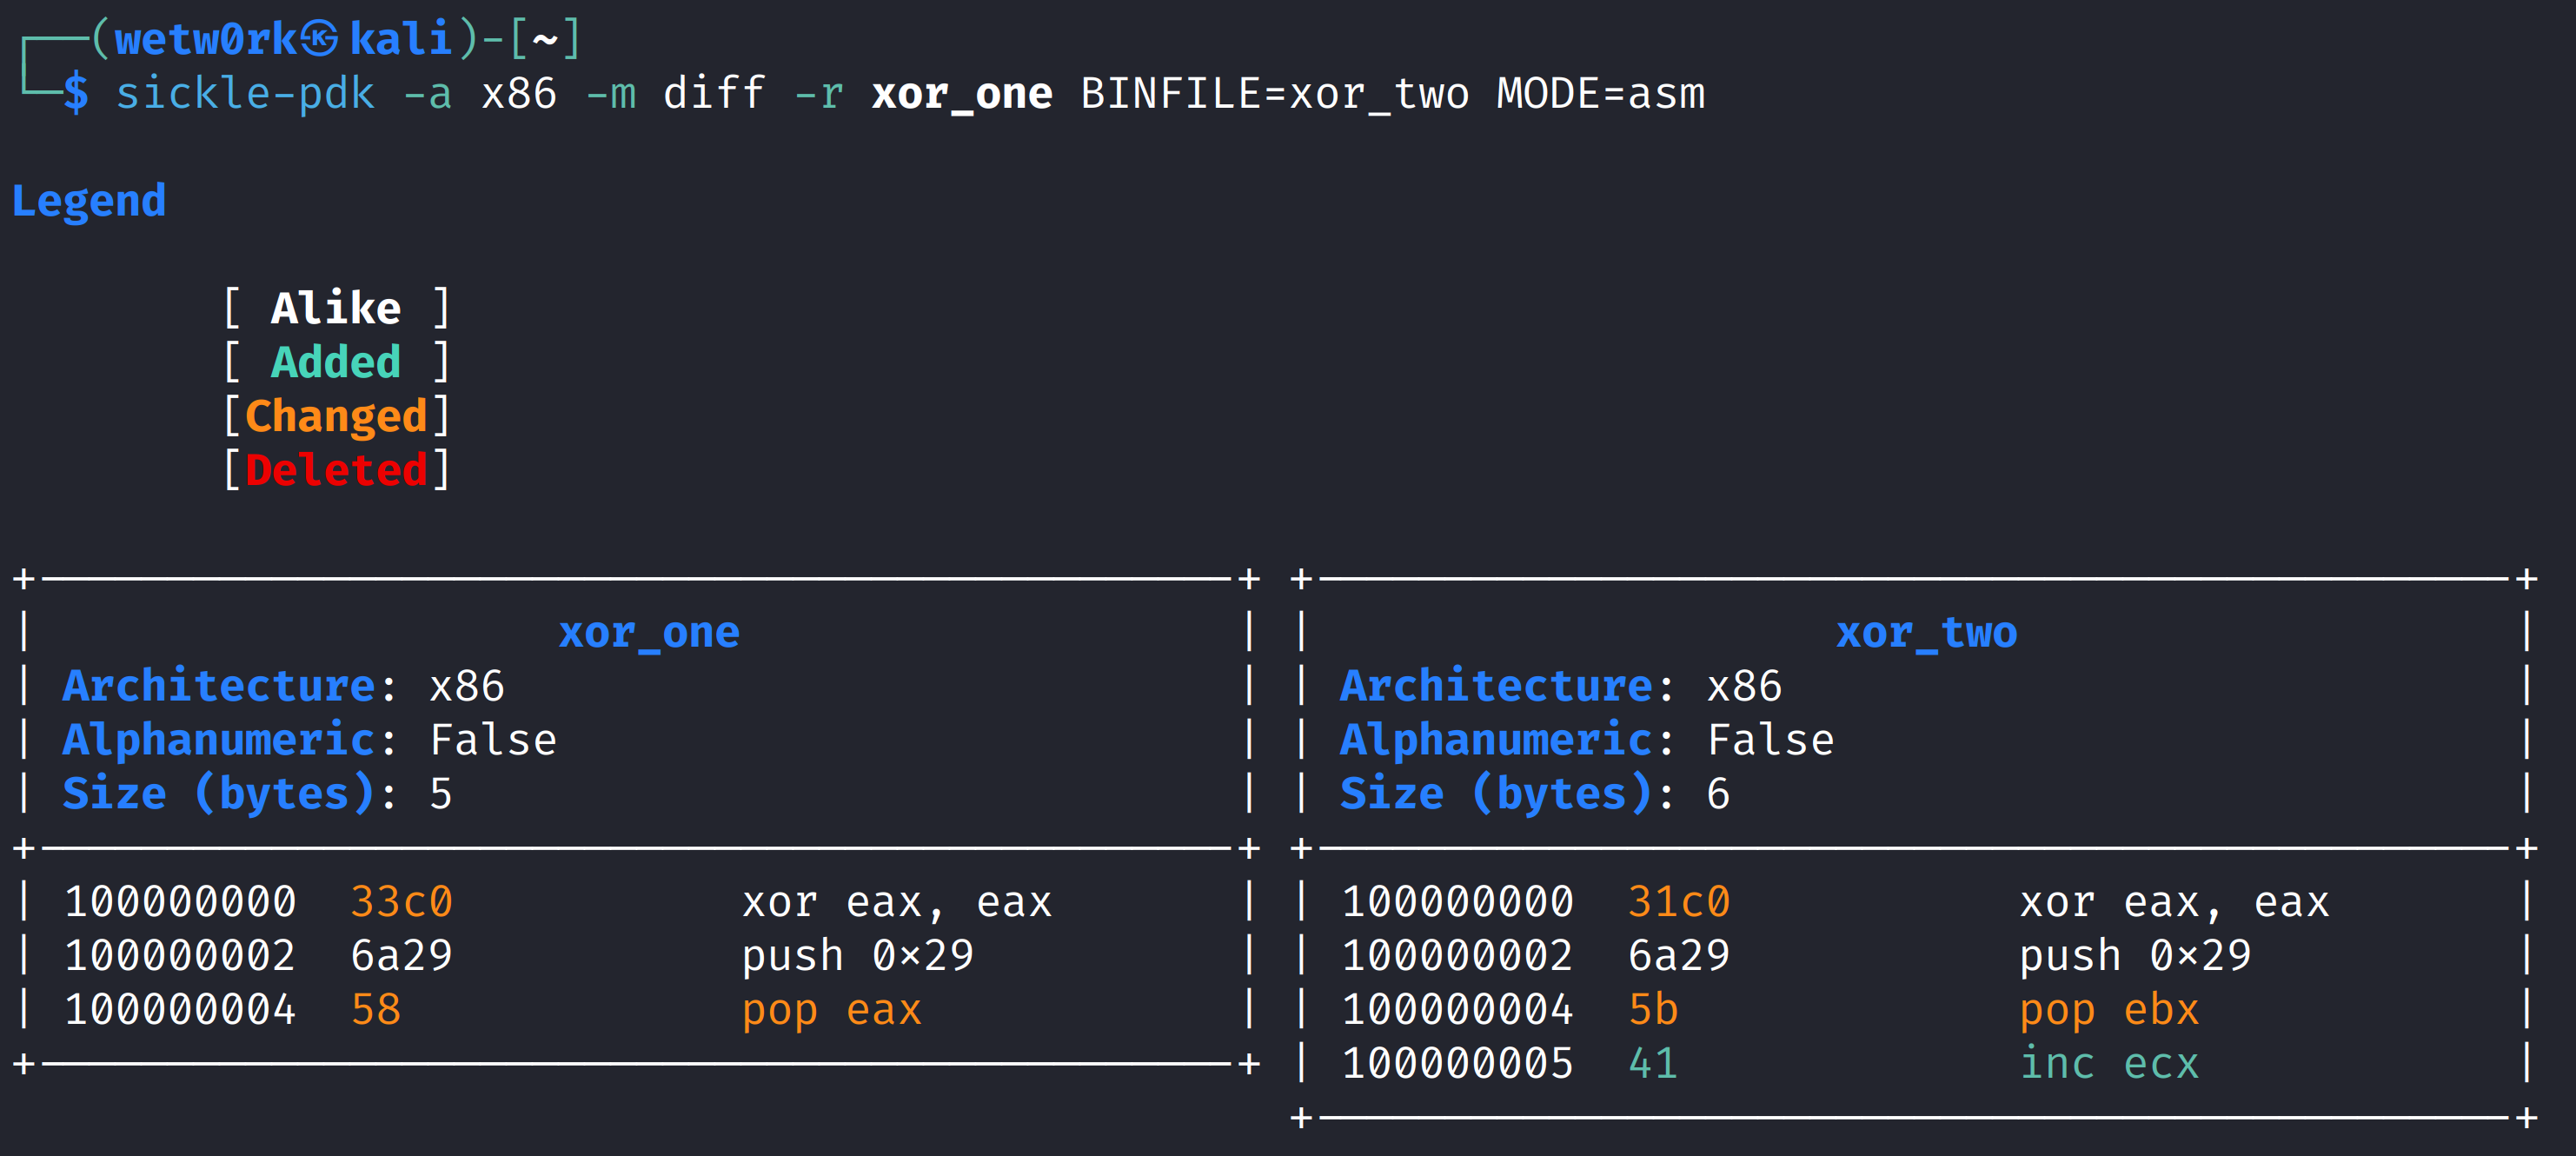 wetw0rk/sickle-pdk
Sickle - Payload Development Kit
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…