
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
390 results
SnipRecover-CLI preview

SnipRecover-CLI

GitHubm31r0n/sniprecover-cli

Detection and restoration of Windows Snipping Tool PNG captures vulnerable to CVE-2023-28303

binary-analysisdata-recoverydigital-forensics+3
2
1 year ago
KernelFlirt preview

KernelFlirt

GitHubakatorich/kernelflirt

Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
ai-assisted-reversingai-securityanti-bot+9
324 months ago
ioctlance preview

ioctlance

GitHubzeze-zeze/ioctlance

A tool that is used to hunt vulnerabilities in x64 WDM drivers

binary-analysisdynamic-analysis-sandboxingexploit-frameworks+4
4733 months ago
zeek-xor-exe-plugin preview

zeek-xor-exe-plugin

GitHubcorelight/zeek-xor-exe-plugin

Zeek plugin to detect and decrypt XOR-encrypted EXEs
anomaly-detectionbinary-analysisdynamic-analysis-sandboxing+5
52 years ago
columbo preview

columbo

GitHubvisma-prodsec/columbo

ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
anomaly-detectionbinary-analysisdigital-forensics+3
614 years ago
DriverBuddy preview

DriverBuddy

GitHubnccgroup/driverbuddy

DriverBuddy is an IDA Python script to assist with the reverse engineering of Windows kernel drivers.

binary-analysisreverse-engineeringvulnerability-analysis
3836 years ago
instrumentation_callbacks preview

instrumentation_callbacks

GitHubdeputation/instrumentation_callbacks

A proof of concept demonstrating instrumentation callbacks on Windows 10 21h1 with a TLS variable to ensure all syscalls are caught.
binary-analysisdebuggersdynamic-analysis-sandboxing+1
1664 years ago
CallObfuscator preview

CallObfuscator

GitHubd35ha/callobfuscator

Obfuscate specific windows apis with different apis
binary-analysisdefensive-toolsdynamic-analysis-sandboxing+4
1.0k5 years ago
Evasor preview

Evasor

GitHubcyberark/evasor

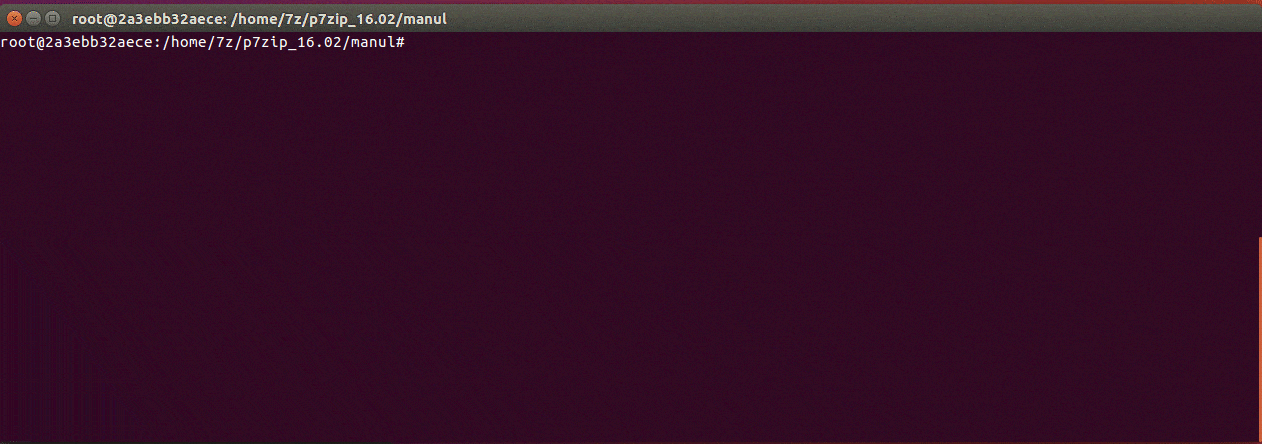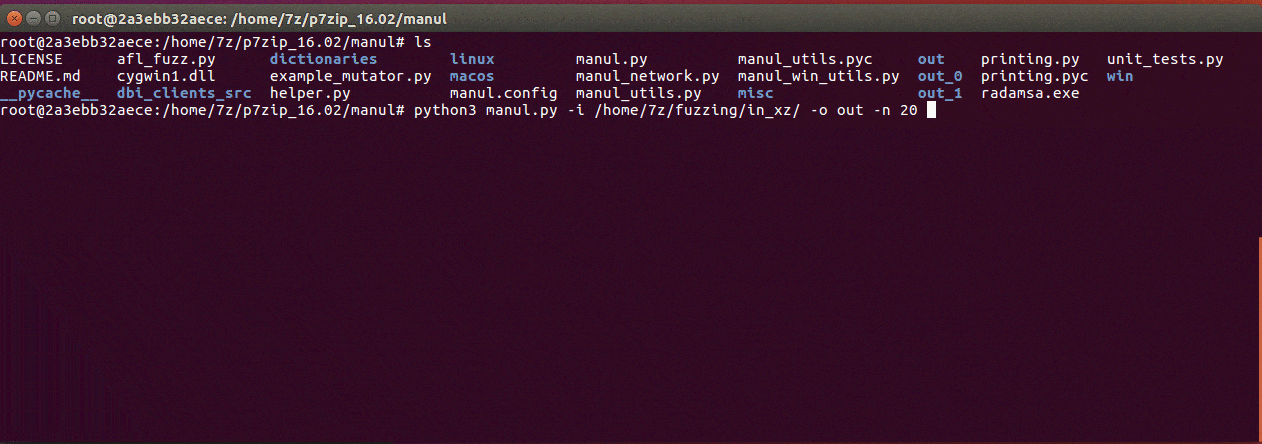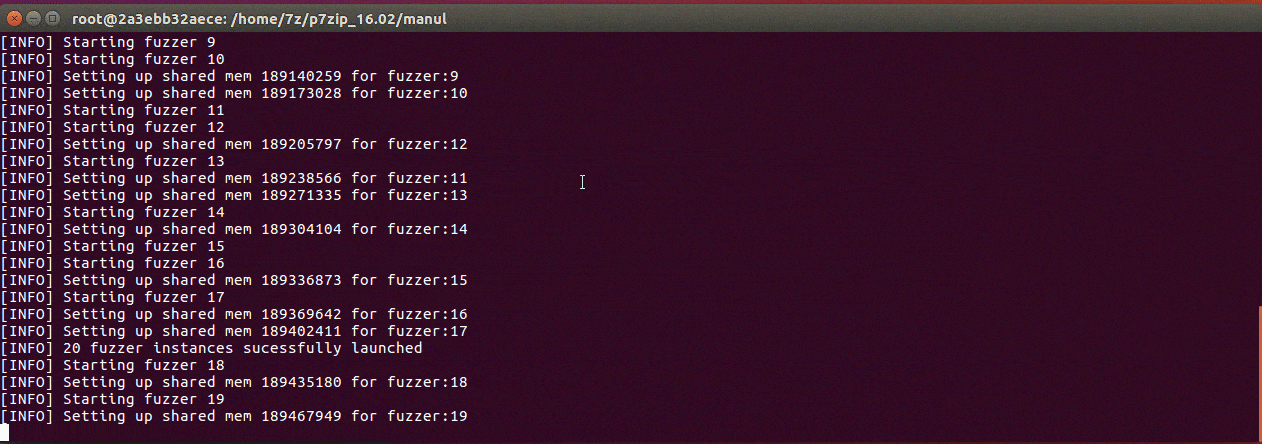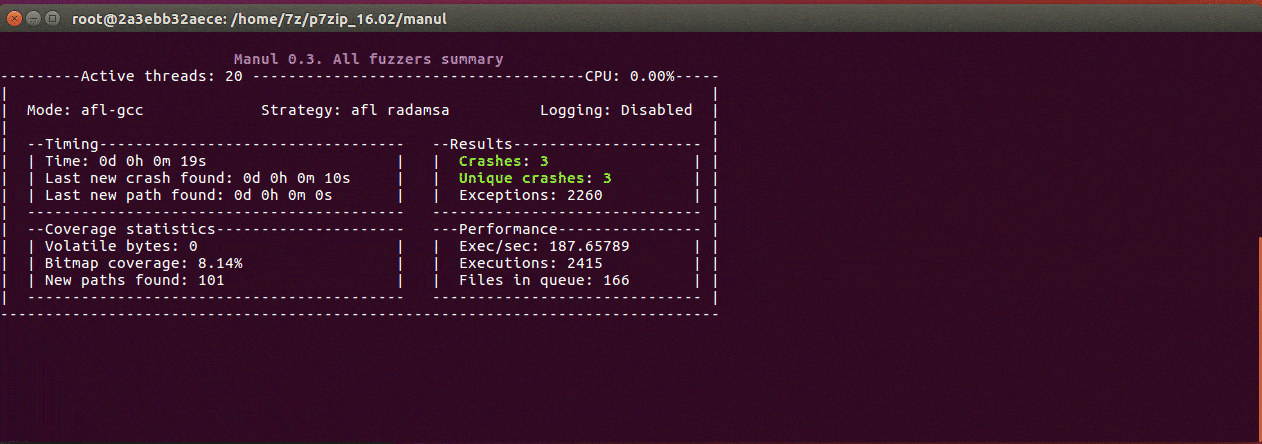
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies
binary-analysisdefensive-toolspenetration-testing+3
3256 years ago
manul preview

manul

GitHubmxmssh/manul

Manul is a coverage-guided parallel fuzzer for open-source and blackbox binaries on Windows, Linux and MacOS
binary-analysisdynamic-analysis-sandboxingfuzzing+1
3346 years ago
msf_shellcode_analysis preview

msf_shellcode_analysis

GitHubyo-yo-yo-jbo/msf_shellcode_analysis

Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…
binary-analysiseducationmalware-analysis+3
282 months ago
pip3line preview

pip3line

GitHubmetrodango/pip3line

Swiss Army knife for raw bytes manipulation & interception

binary-analysiscryptographypacket-sniffing-analysis+2
563 years ago
SigLens preview

SigLens

GitHubst0rn/siglens

Windows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…
binary-analysisdefensive-toolsdigital-forensics+7
34 days ago
ghostdebug preview

ghostdebug

GitHubvollragm/ghostdebug

Debugger utilizing stealth hooks to hide from debugger detection
binary-analysisdebuggersdefensive-tools+1
231 month ago
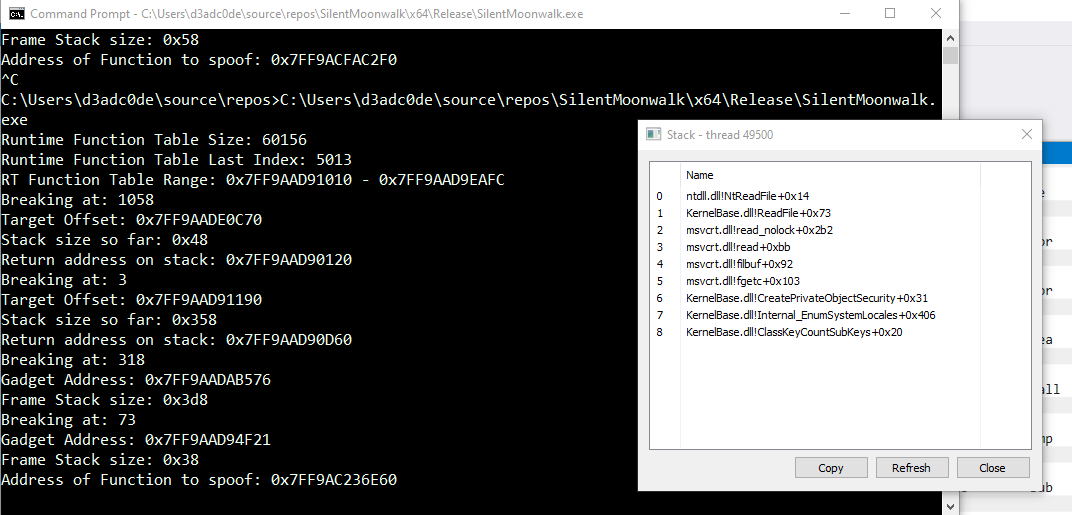
SilentMoonwalk preview

SilentMoonwalk

GitHubklezvirus/silentmoonwalk

PoC Implementation of a fully dynamic call stack spoofer
binary-analysisexploitationpayload-development+2
1.0k2 years ago
CVE-2020-15368-AsrDrv103-research preview

CVE-2020-15368-AsrDrv103-research

GitHubegorrsp/cve-2020-15368-asrdrv103-research

Reverse engineering research of ASRock AsrDrv103.sys (CVE-2020-15368), covering its driver interface, encrypted request protocol, and privileged…

binary-analysiseducationhardware-security+4
612 days ago
widevine-l3-decryptor preview
Archived

widevine-l3-decryptor

GitHubtomer8007/widevine-l3-decryptor

A Chrome extension that demonstrates bypassing Widevine L3 DRM
binary-analysiseducationencryption-decryption-tools+3
1.2k3 years ago
EhTrace preview

EhTrace

GitHubk2/ehtrace

ATrace is a tool for tracing execution of binaries on Windows.

binary-analysiscode-analysisdebuggers+4
24510 months ago
Previous1…345…22Next