VMProtect-devirtualization

Playing with the VMProtect software protection. Automatic deobfuscation of pure functions using symbolic execution and LLVM.

Playing with the VMProtect software protection. Automatic deobfuscation of pure functions using symbolic execution and LLVM.

A tool that helps you easy trace classes, functions, and modify the return values of methods on iOS platform

A tool that is used to hunt vulnerabilities in x64 WDM drivers

Dynamic unpacker based on PE-sieve

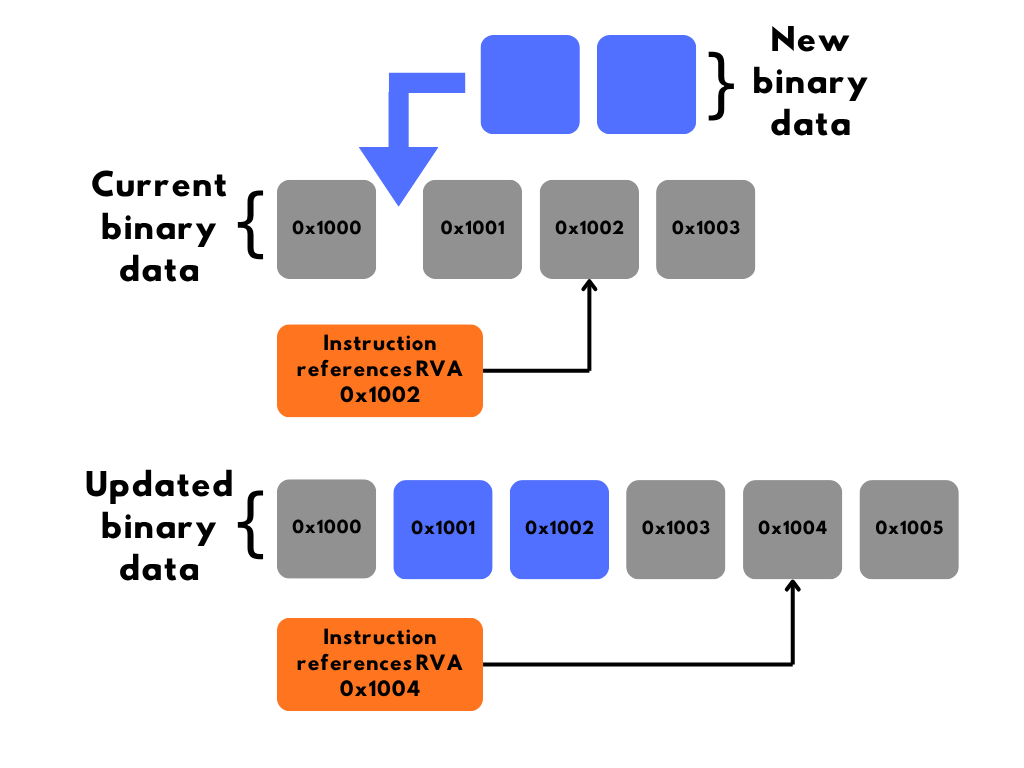
x64 PE bin2bin obfuscator which doesn't add a section to the binary

Frida-based dynamic analysis tool that automatically identifies DLL sideloading and COM hijacking vulnerabilities in Windows executables through…

AFL + DynamoRIO = fuzzing binaries with no source code on Linux

Frida.re based RunPE (and MapViewOfSection) extraction tool

Detect compiler-invented memory loads that turn secure C into TOCTOU vulnerabilities. Includes automated source audits, Unicorn-based binary…

Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment

Automated DLL hijacking vulnerability discovery tool that analyzes PE binaries at load-time and runtime via API hooking, enumerating missing DLLs and…

AArch64 fuzzer based on the Apple Silicon hypervisor

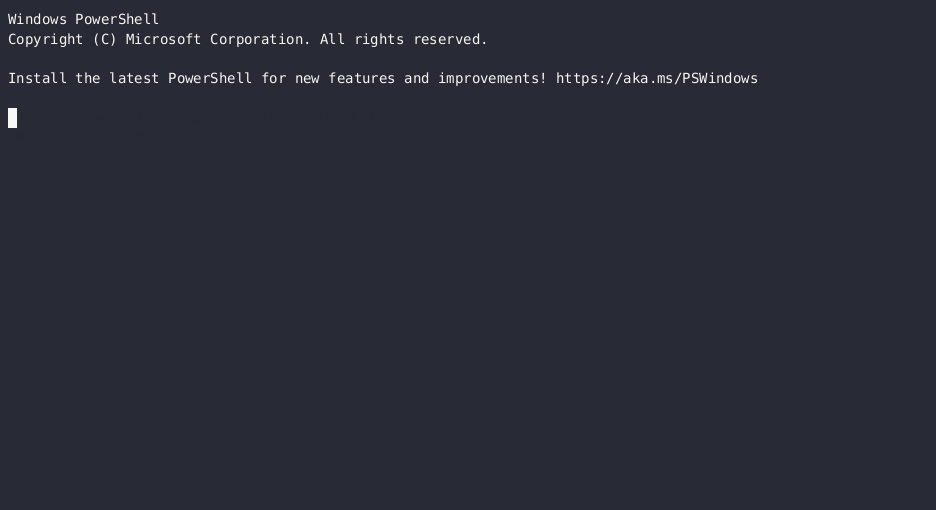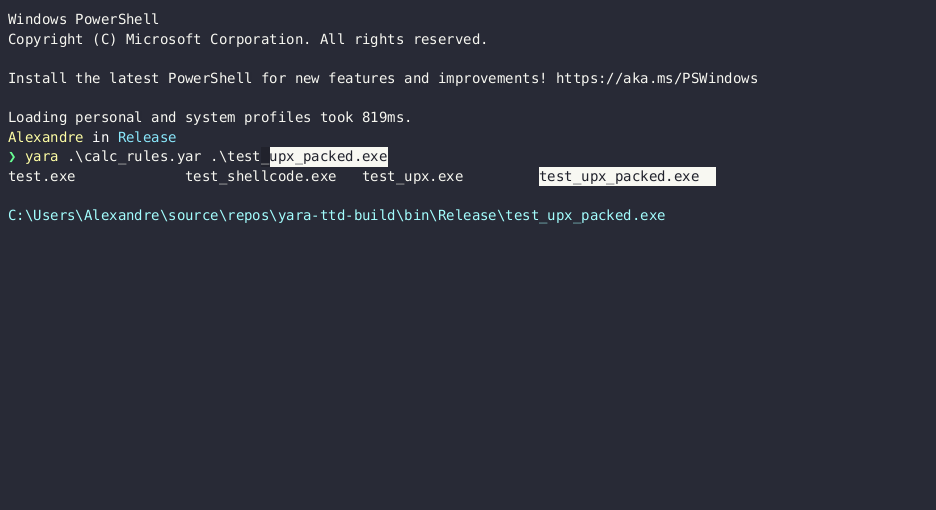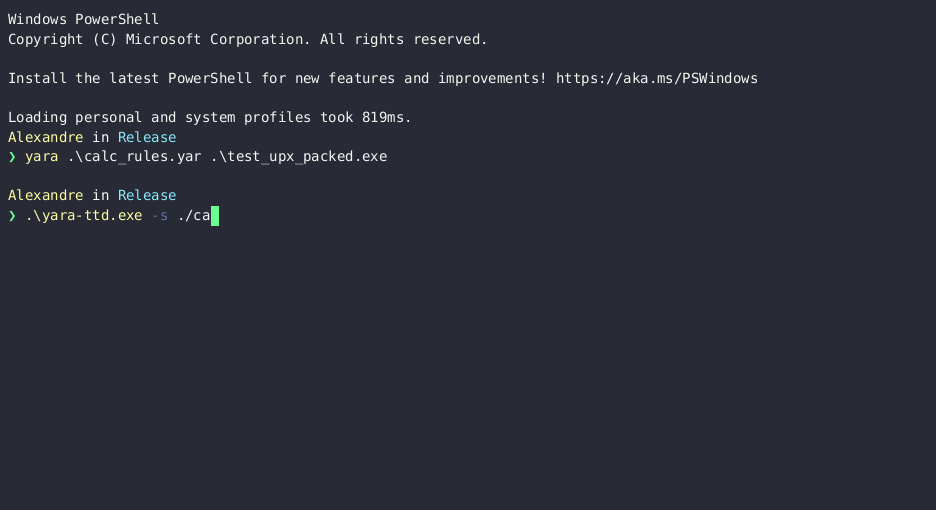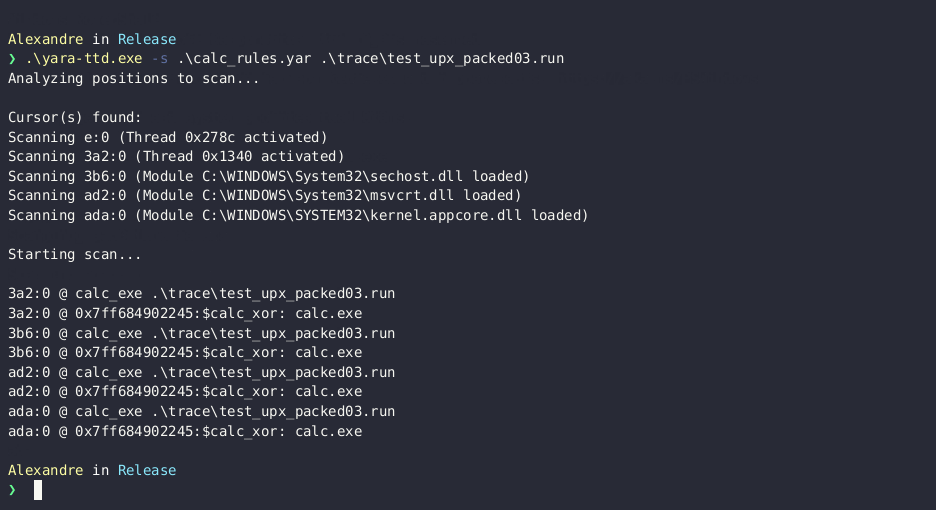
Use YARA rules on Time Travel Debugging traces

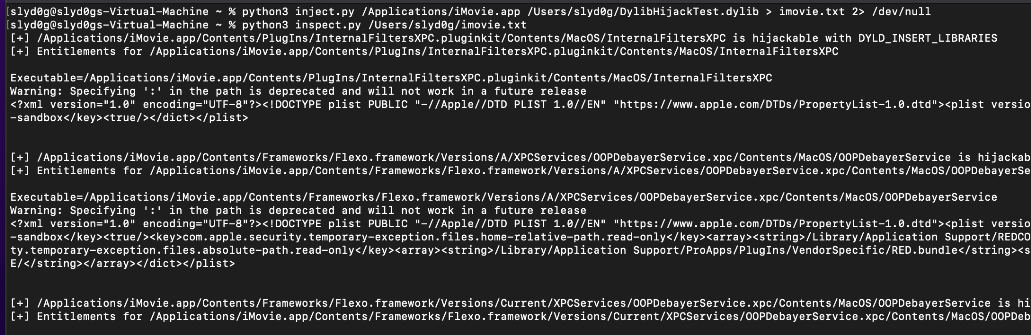
Discover DYLD_INSERT_LIBRARIES hijacks on macOS

Extracts nanocore sample from compile AutoIT script

Exhaustive differential validation of all 4.3B AArch64 instruction encodings.

Firmware reverse engineering of the Philips PM5139 / PM5138A / PM5136 function generators: 8051 emulators used as measuring instruments, 35 sections…

Triggering the famous libweb 0day vuln with libfuzzer