bip
 synacktiv/bip
Object-oriented Python API to simplify interaction with IDA for reverse engineering, enabling plugin development and automation of disassembly…
binary-analysiscode-analysisreverse-engineering+2
205
synacktiv/bipObject-oriented Python API to simplify interaction with IDA for reverse engineering, enabling plugin development and automation of disassembly…
 backengineering/themida-devirt
Themida Devirt Results
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
 watchfulip/tp-link-decrypt
Decrypt TP-Link Firmware
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
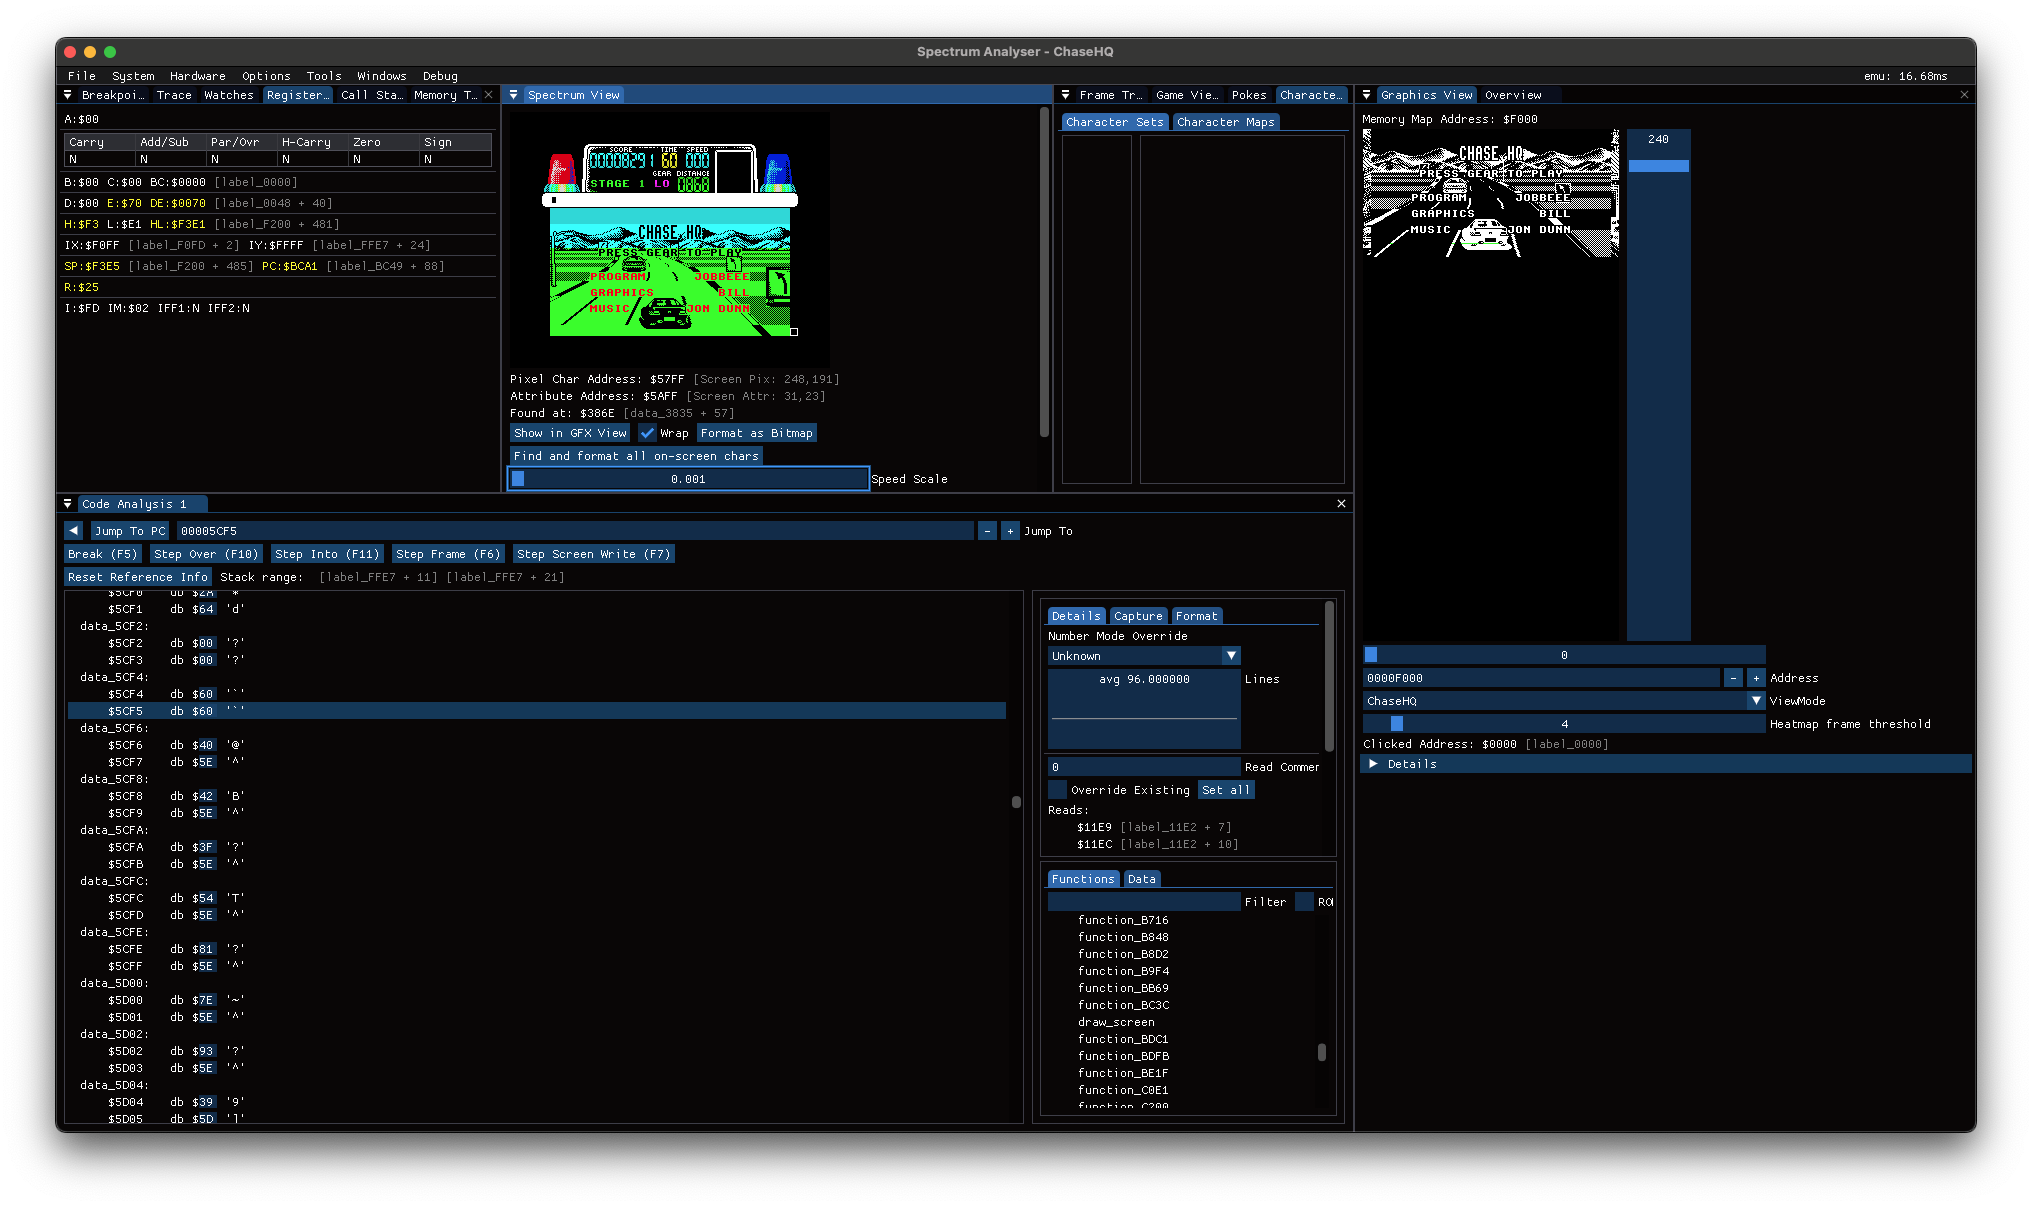 dpt/chasehq
Chase H.Q. for ZX Spectrum — reverse-engineered and reconstructed in portable C
 trailofbits/manticoreui
The Manticore User Interface with plugins for Binary Ninja and Ghidra
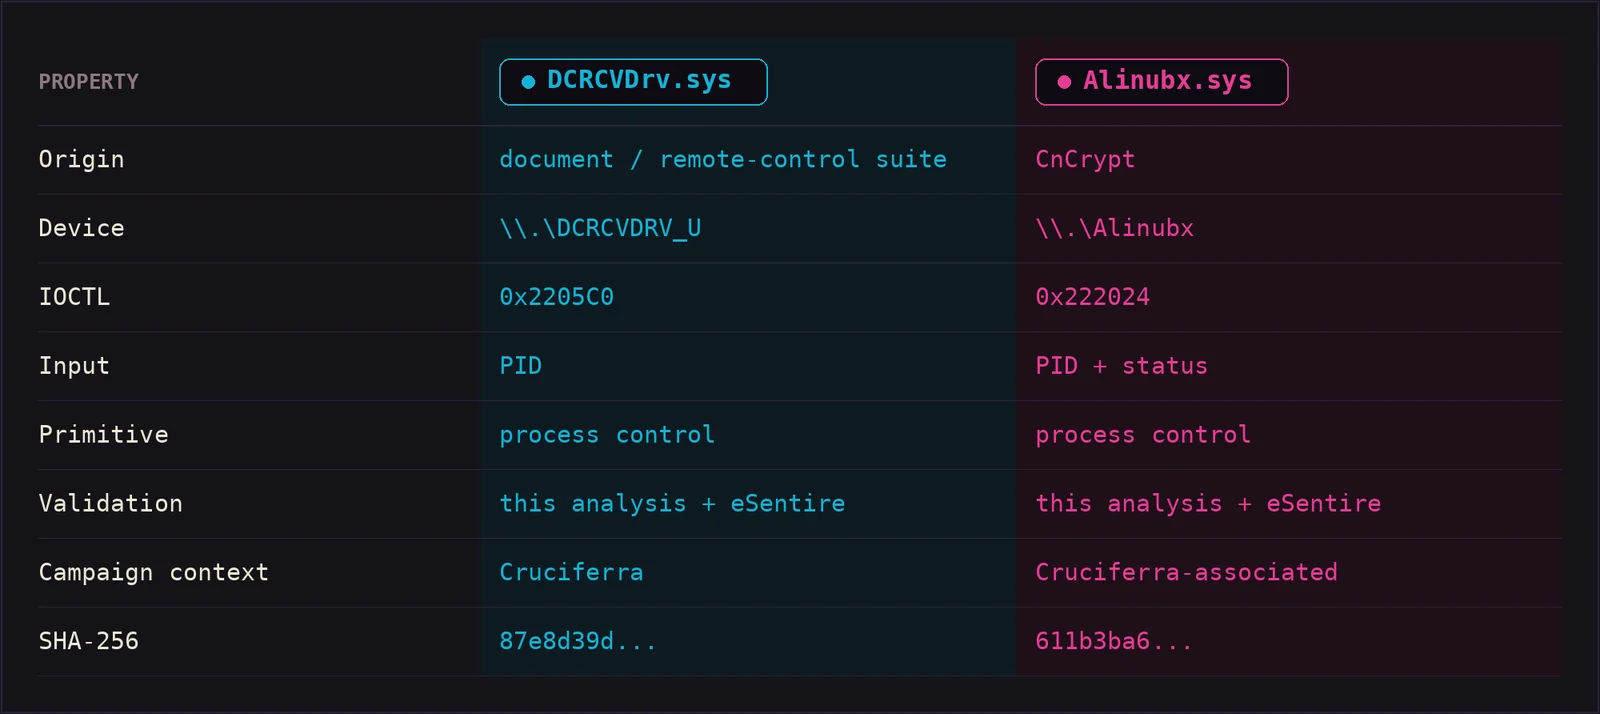 deathshotxd/0xcr0sscrush
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.
 yuvadm/quantumslop
Quantum solver for the Elliptic Curve Discrete Logarithm Problem using Shor's algorithm, implementing multiple oracle strategies to recover ECC…
 icicle-emu/icicle-python
Python bindings for the Icicle emulator, enabling grey-box firmware fuzzing, binary emulation, and reverse-engineering workflows across x64 and ARM64…
 iss4cf0ng/dotnetpeloader
A C# PE loader for x64 and x86 PE files.
 synacktiv/thats_no_pipe
Windows named pipe hooking toolkit
 hasherezade/pesieve-go
Golang bindings for PE-sieve
 geeoon/fault-injection-finder
Automatically find and execute fault injection attacks
 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 partywavesec/invesalius3_vulnerabilities
InVesalius discovered CVE. CVE-2024-42845, CVE-2024-44825
 yousif-iq/cve-2026-39259
CVE-2026-39259