
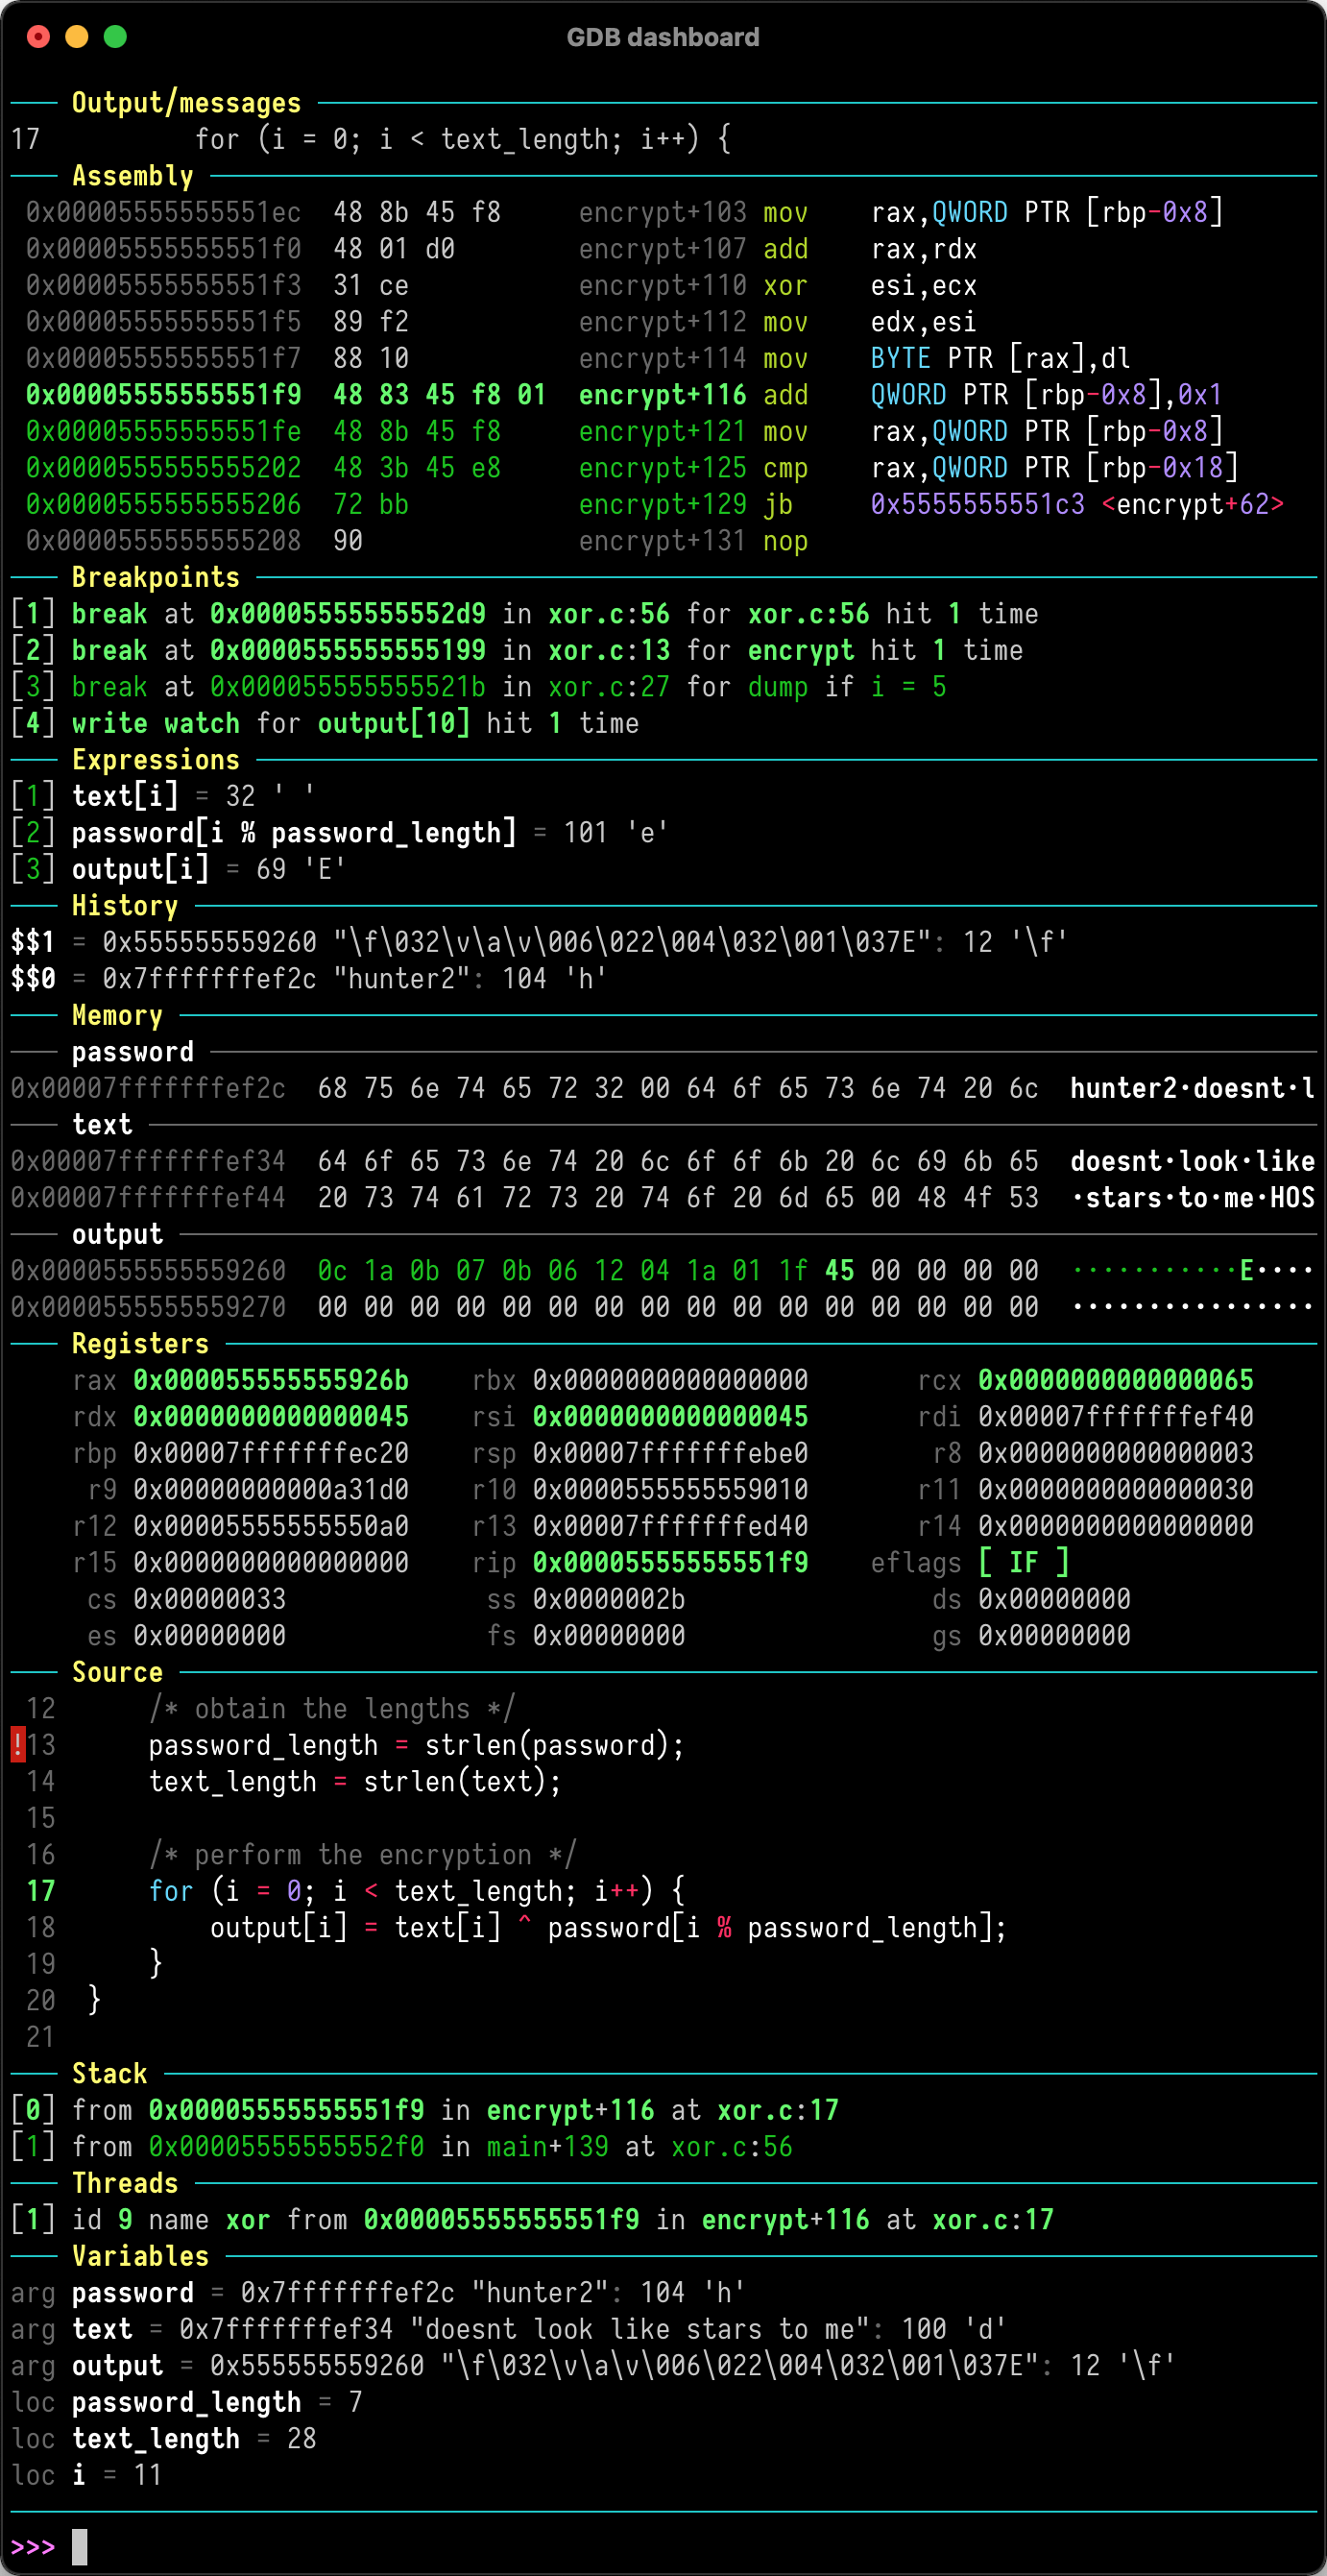
gdb-dashboard
 cyrus-and/gdb-dashboard
Modular GDB interface providing a visual dashboard with customizable panels for inspecting registers, source code, assembly, and program state during…
binary-analysisdebuggersreverse-engineering+1
12.3k
cyrus-and/gdb-dashboardModular GDB interface providing a visual dashboard with customizable panels for inspecting registers, source code, assembly, and program state during…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 joernio/joern
Open-source code analysis platform for C/C++/Java/Binary/Javascript/Python/Kotlin based on code property graphs. Discord https://discord.gg/vv4MH284Hc
 0xz0f/z0fcourse_reverseengineering
Structured reverse engineering course covering x64 Windows binaries, assembly, debugging, and malware analysis. Designed for beginners to…
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 dosx-dev/obfus.h
Macro-header for compile-time C polymorphic obfuscation (tcc, win x86/x64)
 snare/voltron
Extensible debugger UI toolkit providing customizable register, disassembly, stack, memory, breakpoint, and backtrace views for LLDB, GDB, VDB, and…
 dman95/sasm
SASM - simple crossplatform IDE for NASM, MASM, GAS and FASM assembly languages
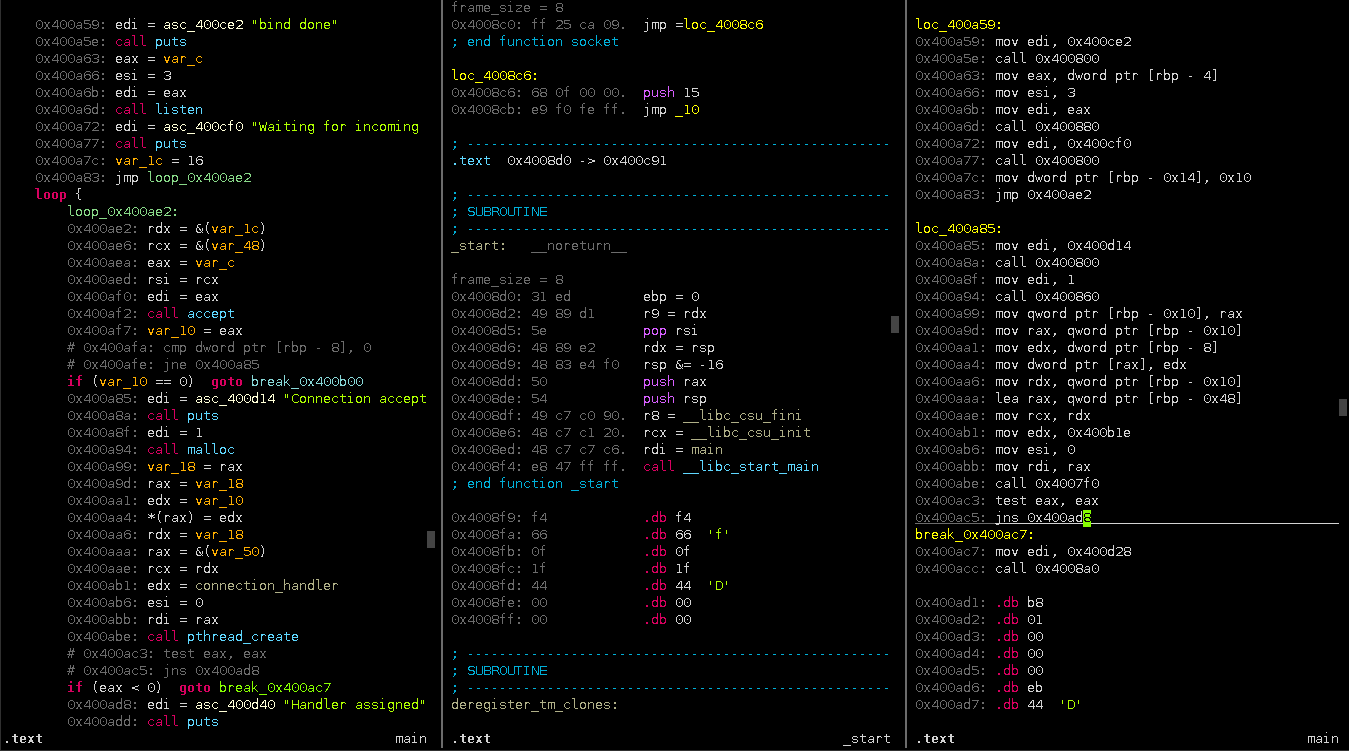 plasma-disassembler/plasma
Plasma is an interactive disassembler for x86/ARM/MIPS. It can generates indented pseudo-code with colored syntax.
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 mandiant/speakeasy
Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
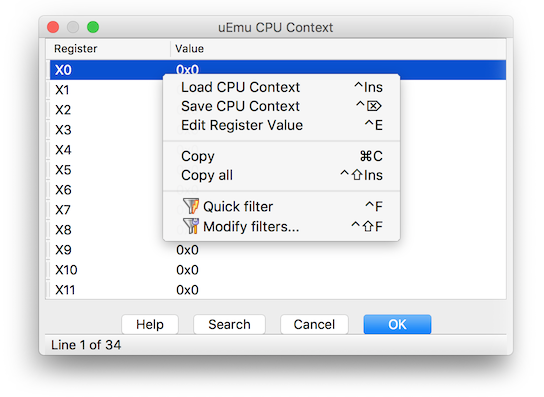 alexhude/uemu
Tiny cute emulator plugin for IDA based on unicorn.
 amlweems/xzbot
notes, honeypot, and exploit demo for the xz backdoor (CVE-2024-3094)
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 kjcracks/clutch
Jailbreak-only iOS utility that decrypts installed app executables and dumps them as .ipa or raw binary files for security research and…
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android