
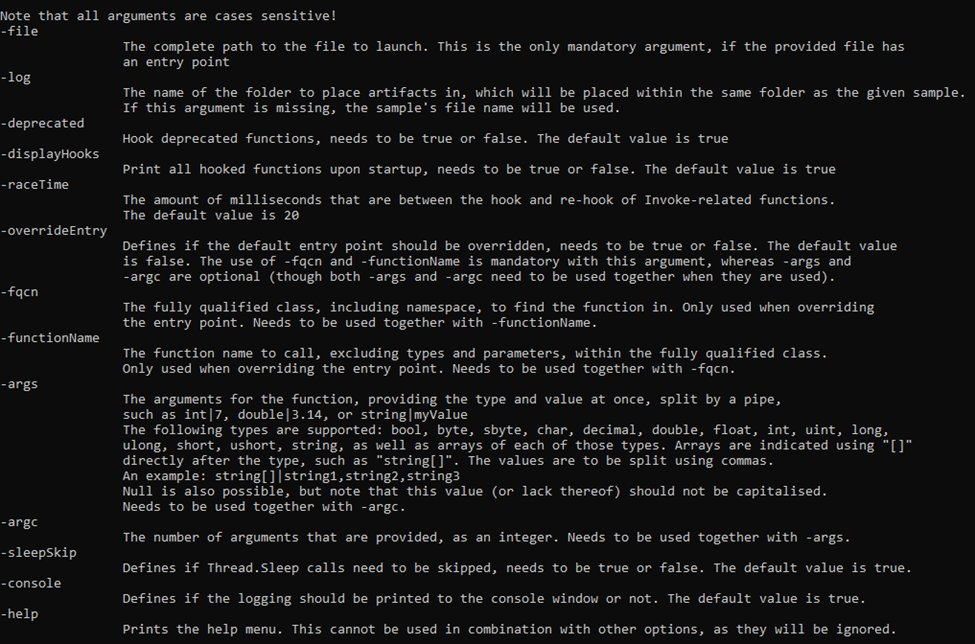
DotDumper
 advanced-threat-research/dotdumper
An automatic unpacker and logger for DotNet Framework targeting files
binary-analysisdebuggersdynamic-analysis-sandboxing+4
265
advanced-threat-research/dotdumperAn automatic unpacker and logger for DotNet Framework targeting files
 project-artist/artist
Open-source instrumentation framework for Android apps and Java middleware, modifying code during on-device compilation via the ART compiler.…
 trolldbois/python-haystack
Process heap analysis framework - Windows/Linux - record type inference and forensics
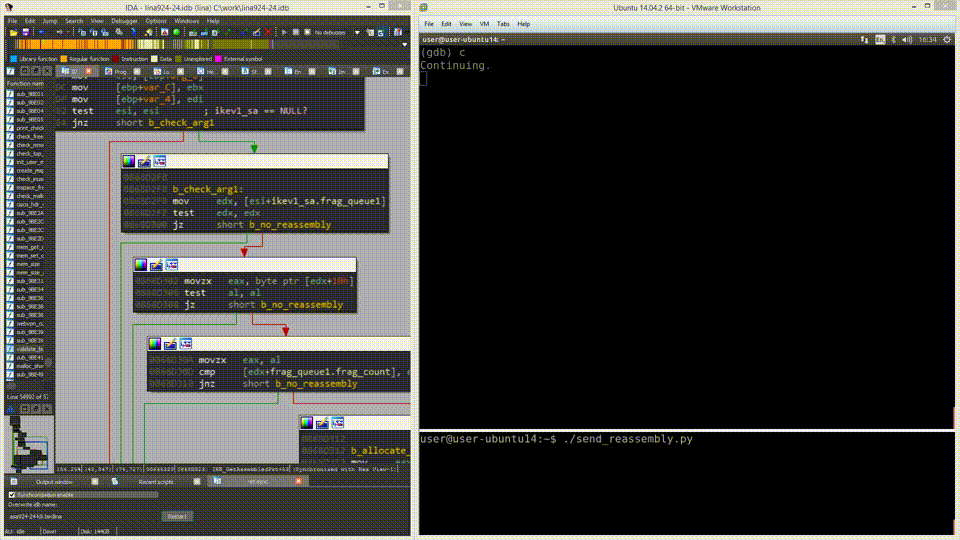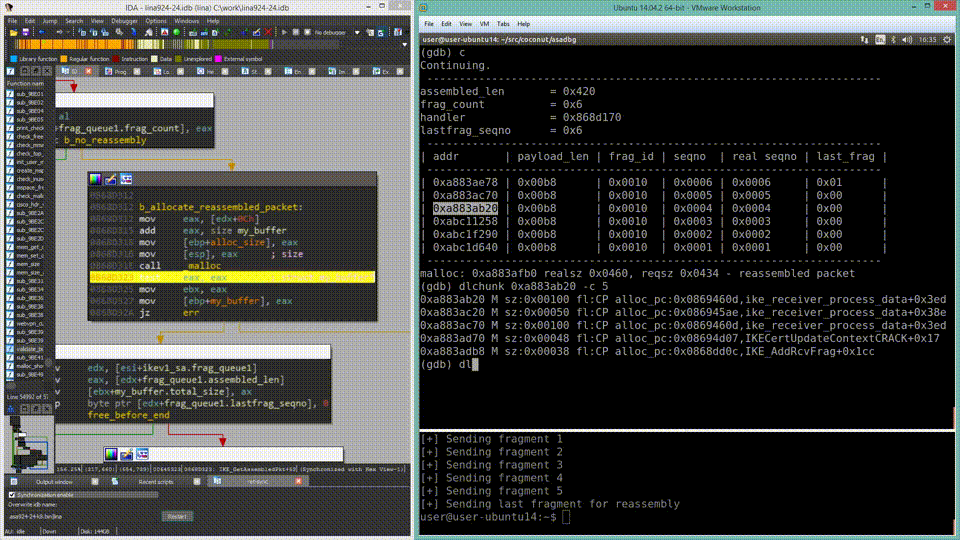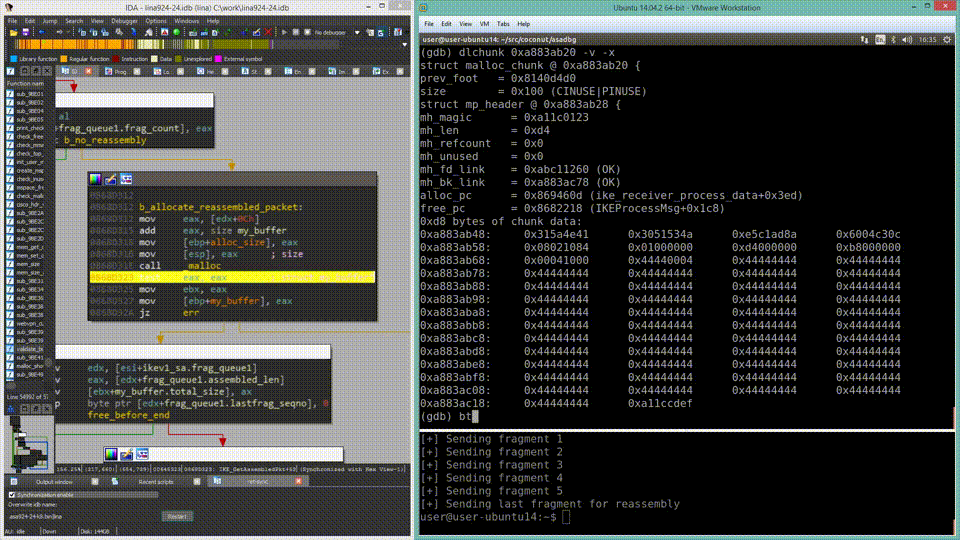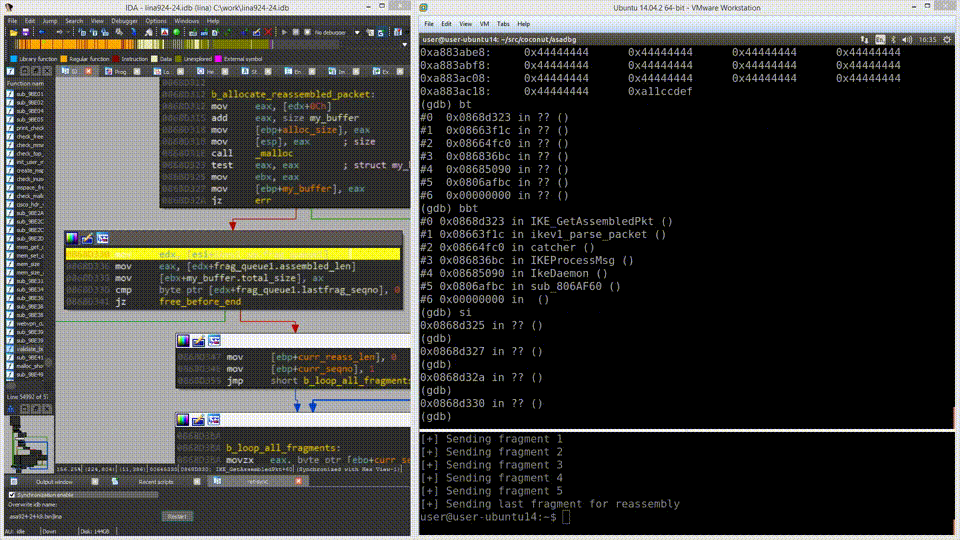 nccgroup/asadbg
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices
 immunityinc/libptrace
An event driven multi-core process debugging, tracing, and manipulation framework.
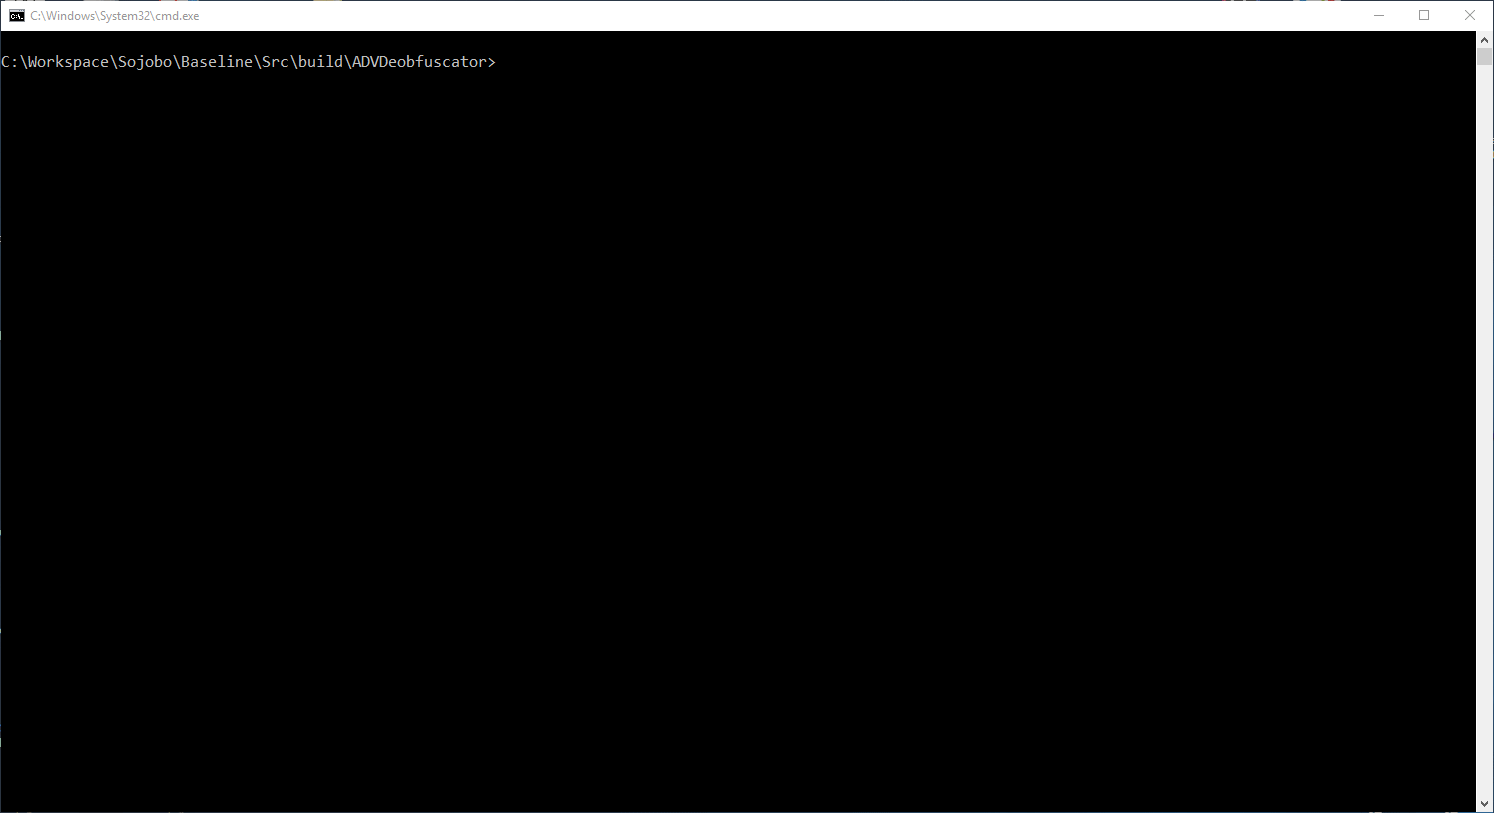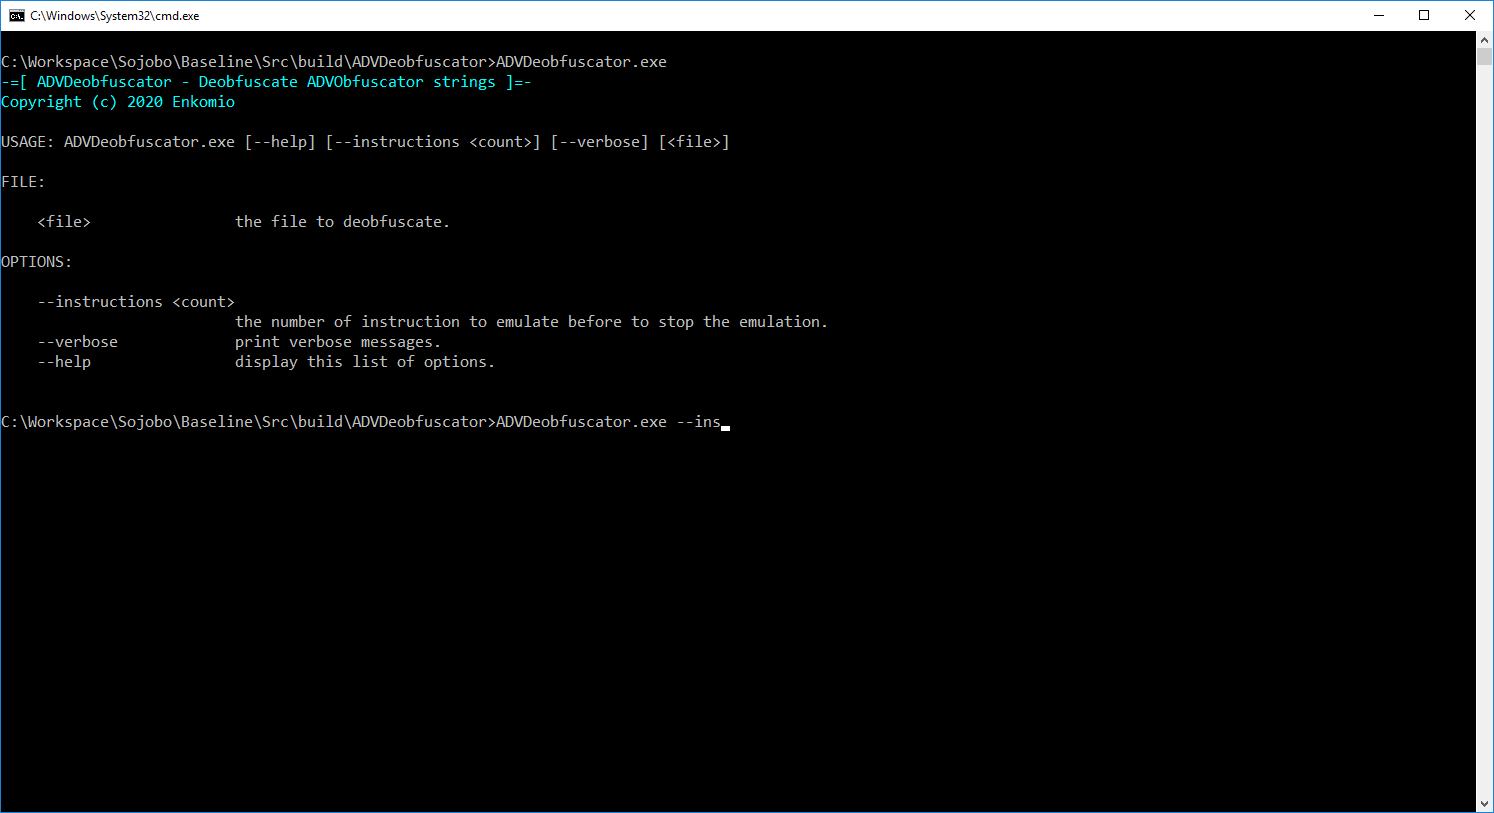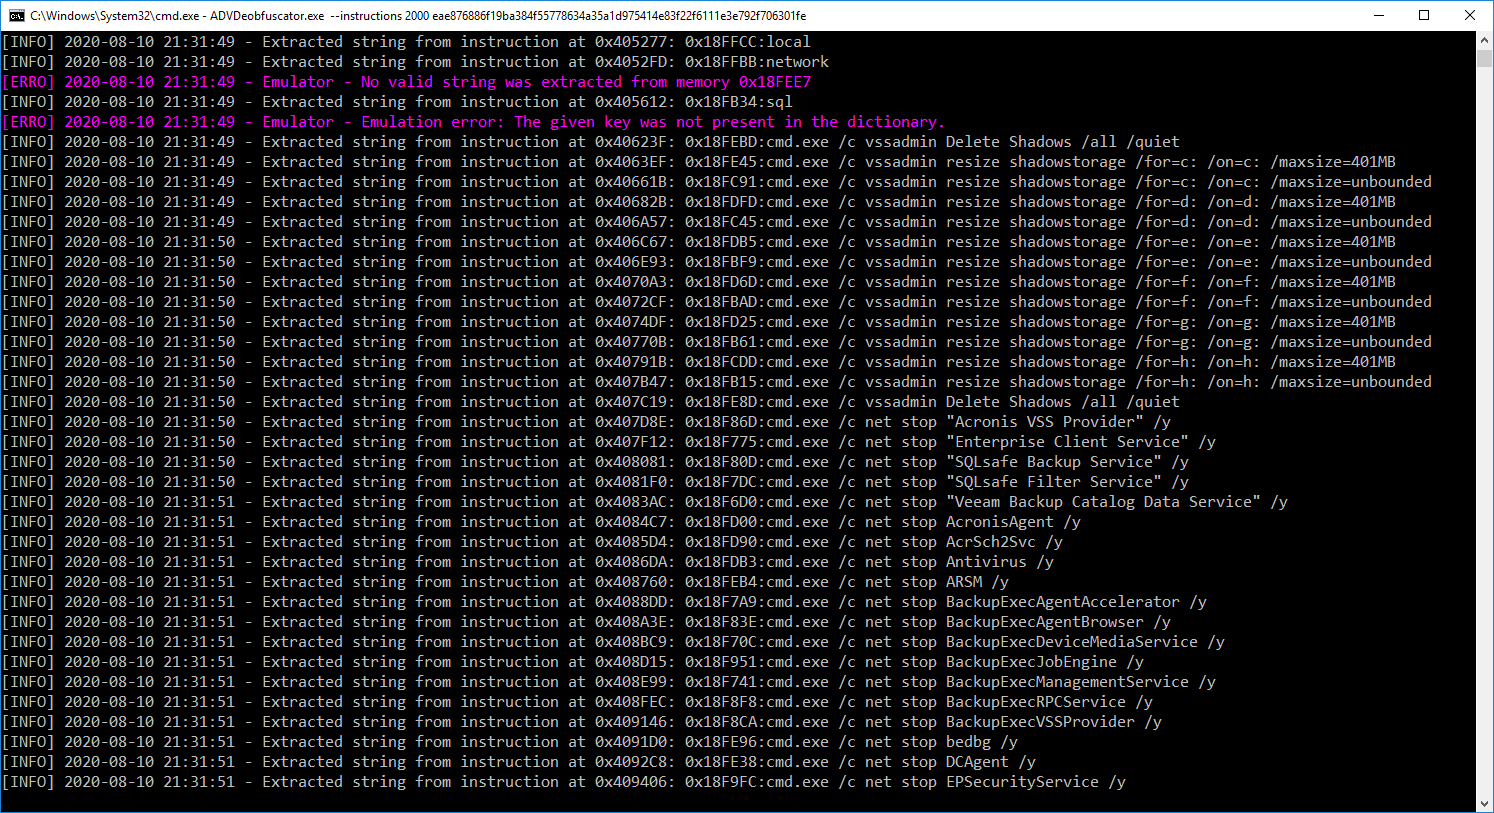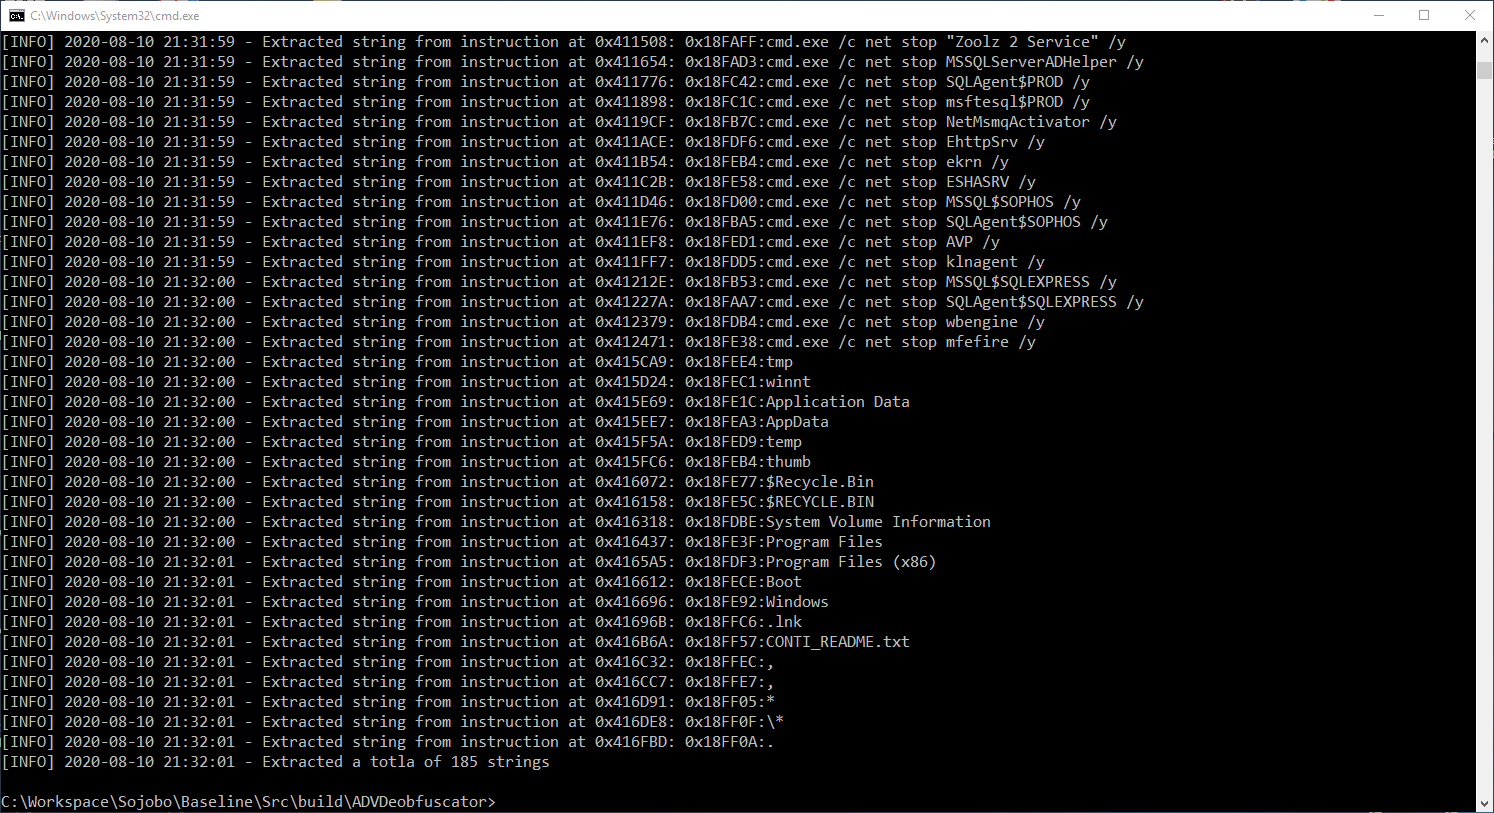 enkomio/sojobo
A binary analysis framework
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
 l33tdawg/aether
AI Smart Contract Security Analysis and PoC Generation Framework
 cispa/trevex
Automated Vulnerability Detection Framework for Transient Execution Vulnerabilities (IEEE S&P '26)
 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
 futureslab/binvariants
Register-level invariant-guided fuzzing framework for closed-source binaries, leveraging likely invariant violations to discover crashes and bugs in…
 darioi/droidcarve
Android Reverse Engineering Framework
 uthrasri/framework_base_cve-2023-21285_nopatch
Android framework vulnerability analysis and exploitation demonstration for CVE-2023-21285, providing a no-patch test case for security researchers.
 trinadh465/frameworks_av_aosp10_r33_cve-2021-0509
Android media framework vulnerability fix for CVE-2021-0509, addressing a use-after-free in audio flinger to prevent local privilege escalation.
 satheesh575555/frameworks_av_aosp10_r33_cve-2020-0245
Android frameworks_av module with modifications addressing CVE-2020-0245, a vulnerability in media framework. Provides patched source code for AOSP…
 trinadh465/frameworks_base_aosp10_r33_cve-2023-21246
Android framework patch for CVE-2023-21246, addressing a security vulnerability in the Android platform.