

CVE-2017-13672
 davidbuchanan314/cve-2017-13672
POCs for CVE-2017-13672 (OOB read in VGA Cirrus QEMU driver, causing DoS)
binary-analysisembedded-systems-securityexploitation+3
3
davidbuchanan314/cve-2017-13672POCs for CVE-2017-13672 (OOB read in VGA Cirrus QEMU driver, causing DoS)
 aliask/dinkleberry
Patch your D-Link device affected by CVE-2024-3272
 gimminse/firmware-analysis
Rediscovered CVE-2020-25279, a critical vulnerability in the Shannon baseband used in Samsung Exynos chipsets
 whoami-012/cve-2026-96515
Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
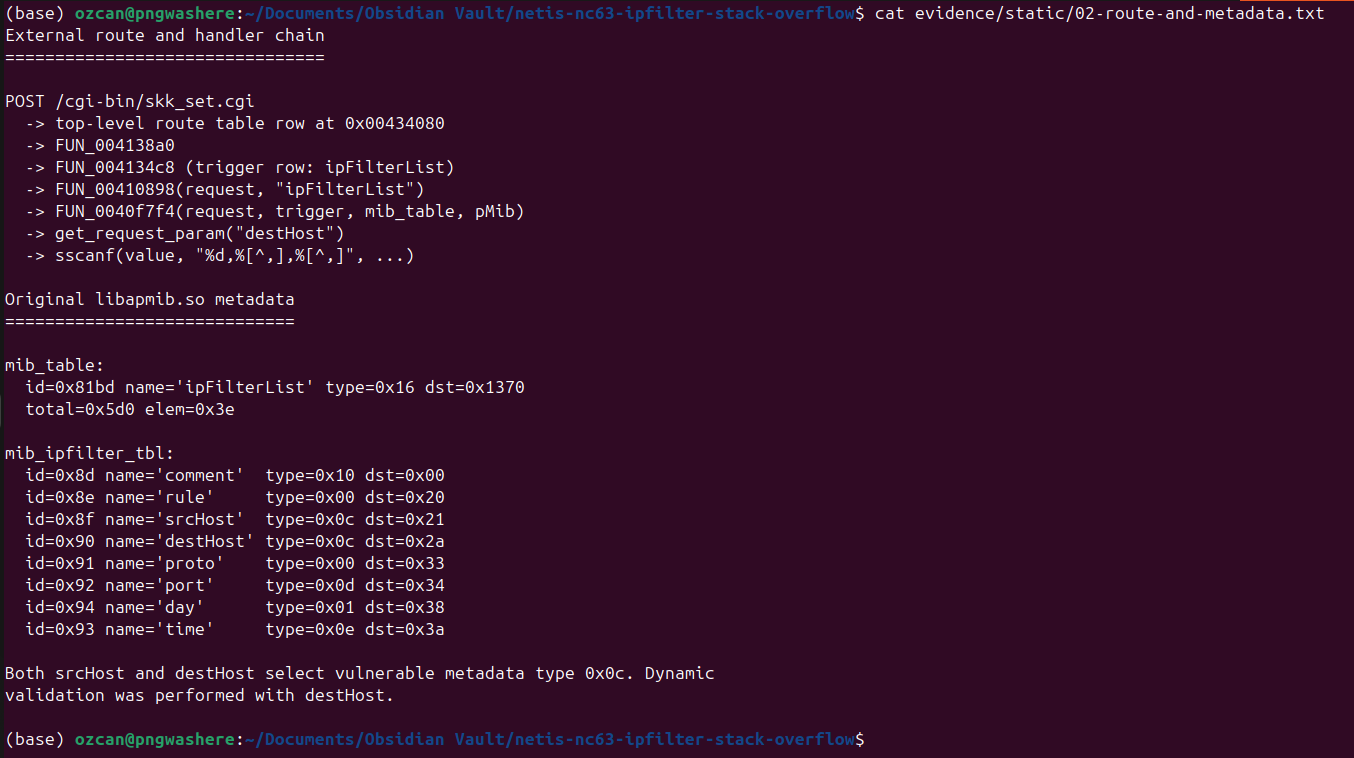 ozcanpng/cve-2026-76071
Original research and PoC for a pre-auth stack buffer overflow via unbounded sscanf scanset in the Netis NC63 ipFilterList handler
 yeahhbean/cve-2026-45729
ThorVG NULL pointer dereference via malformed SVG — AFL++ fuzzing writeup
 isukasanuj/cve-2026-85769
Proof-of-concept exploit for CVE-2026-85769, a heap out-of-bounds read in libtpms TPM 2.0 state deserialization, demonstrating denial of service via…
 abrarkhan/external_sonivox_cve-2024-23709
Proof-of-concept for CVE-2024-23709, an out-of-bounds write vulnerability in Android's Sonivox audio synthesis library, demonstrating exploitation on…
 adikso/cve-2024-5633
PoC for CVE-2024-5633
 3dluvr/new-lib3mf.dll-for-meshmixer
Precompiled lib3mf.dll for MeshMixer which includes a backported patch for CVE-2021-21772 and zlib 1.3.1
 spiralbl0ck/bios-stuff-related-programming
Final OBJECTIVE:BIOS ROOTKIT AND RSHELL USING BIOS NETWORKING STACK
 beardypig/ghidra-emotionengine
Ghidra Processor for the Play Station 2's Emotion Engine MIPS based CPU
 checkpointsw/karta
IDA Python plugin for fast, location-driven matching of open-source library symbols in binaries, enabling efficient reverse engineering and…
 kraxel/virt-firmware
Toolkit for decoding, inspecting, and modifying UEFI firmware volumes and variable stores. Supports secure boot certificate enrollment, PE binary…
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
 nmatt0/moria
IoT firmware identification and extraction
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.