

pe-bear
 hasherezade/pe-bear
Portable Executable reversing tool with a friendly GUI
binary-analysisforensicsmalware-analysis+3
3.8k
hasherezade/pe-bearPortable Executable reversing tool with a friendly GUI
 justicerage/manalyze
Static analyzer for PE executables with plugin-based detection of packers, compilers, suspicious imports, cryptographic constants, and ClamAV…
 hasherezade/tiny_tracer
Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
 gjduck/e9patch
A powerful static binary rewriting tool
 helixo32/crimsonedr
Simulate the behavior of AV/EDR for malware development training.
 madmin3r/unconfuserex
Deobfuscator for ConfuserEx 2.
 lcbower33/stegoscan
Automated steganography detection tool that scans websites, web servers, and local directories using AI-driven object/text recognition and deep file…
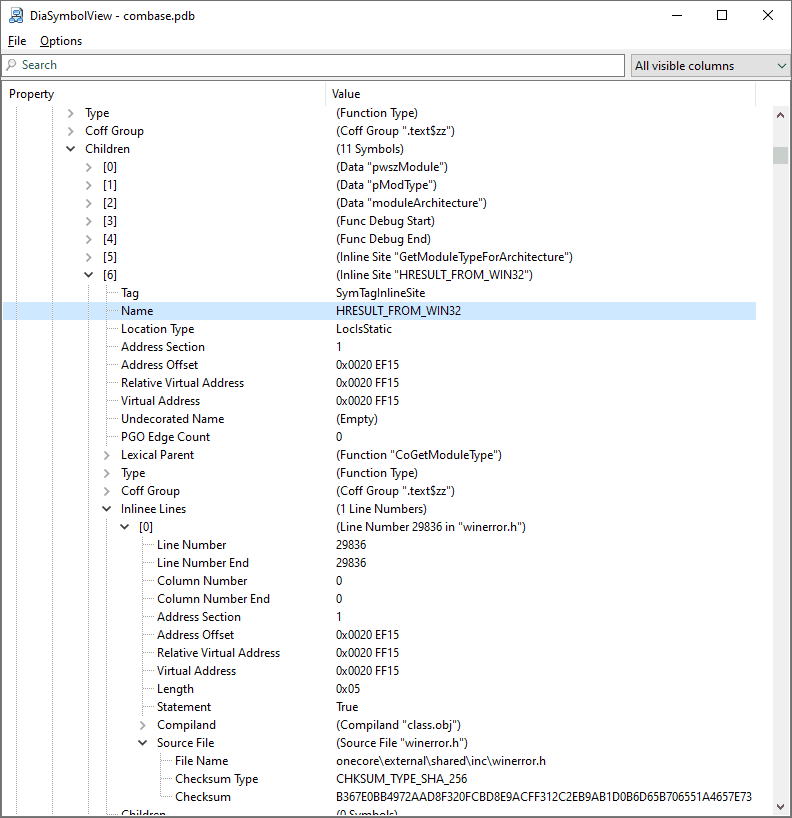 diversenok/diasymbolview
PDB file inspection tool
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
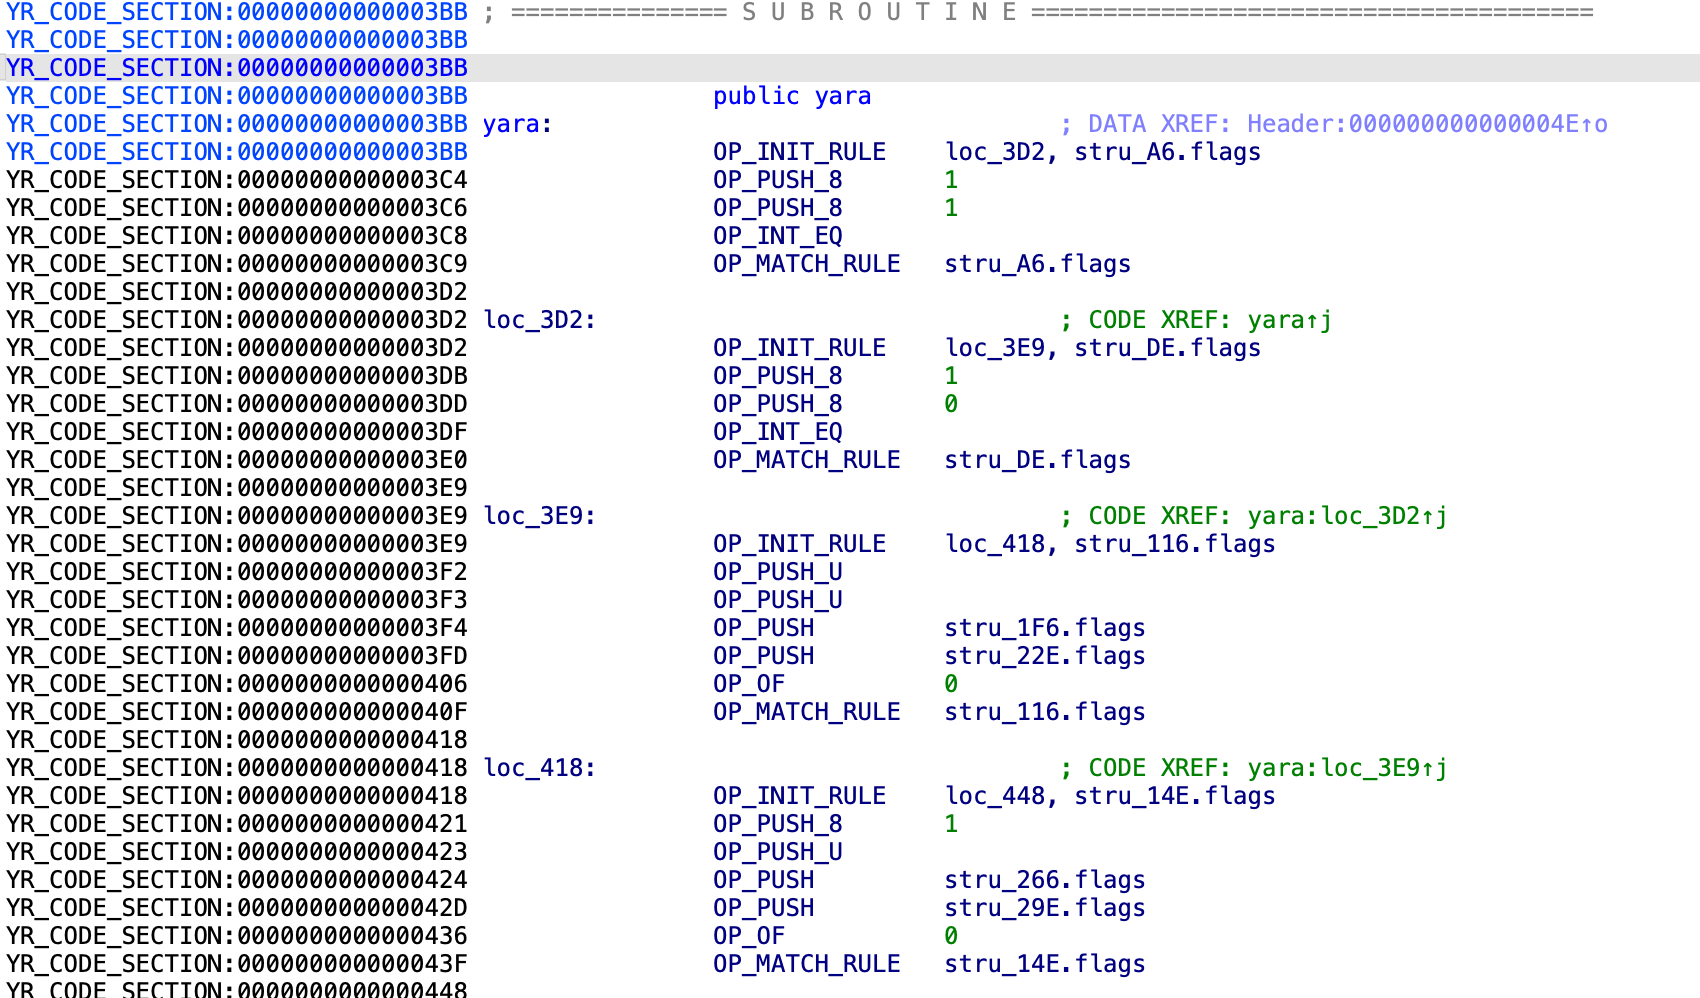 milankovo/yaravm
This repository contains an IDA processor for loading and disassembling compiled yara rules.
 deepquantum/dconstruct
A disassembler & experimental decompiler for TLOU2 DC Scripts.
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
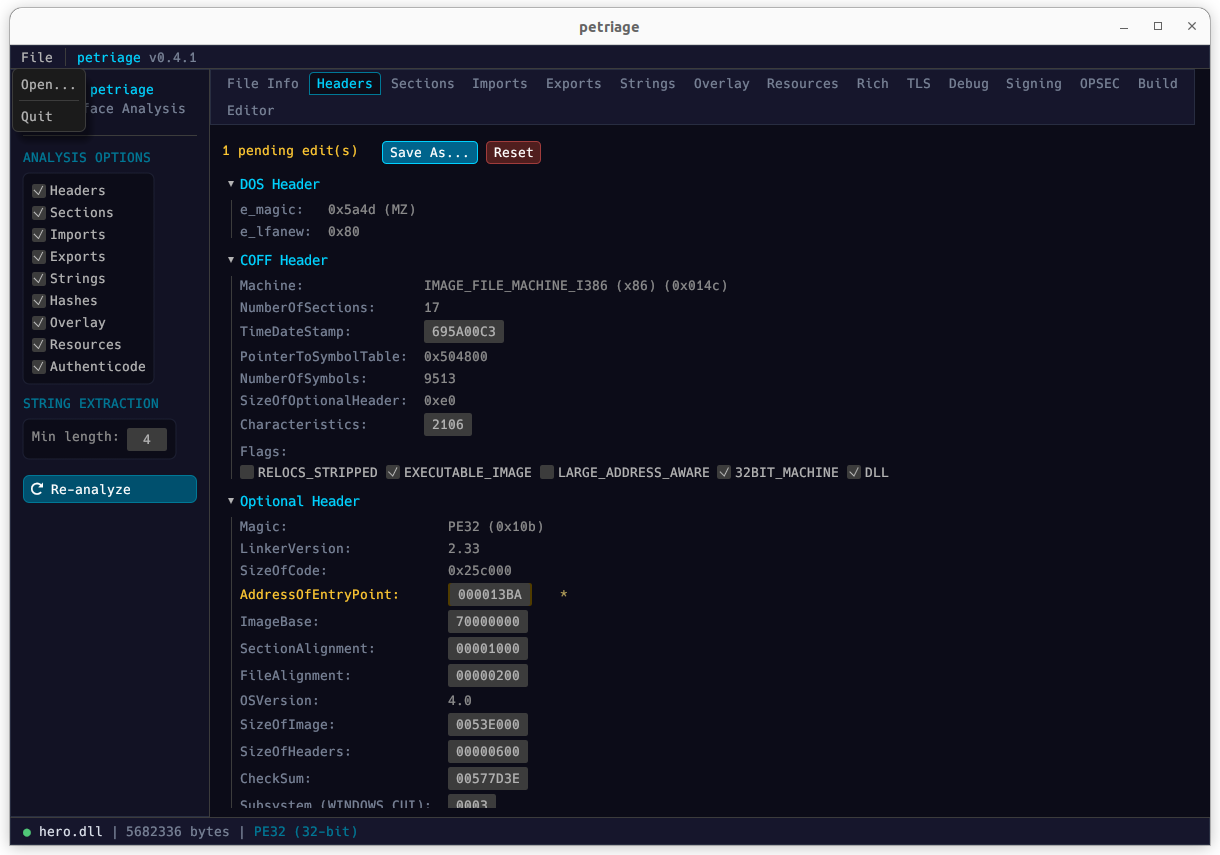 uky007/petriage
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.
 forentfraps/pe-signgen
Universal signature generation for any system function from all Windows Builds using Winbindex
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
 cmu-sei/pharos
Automated static analysis tools for binary programs
 yadyvazifeh1oz92/ecdsa-private-key-recovery
Perform ECDSA and DSA nonce reuse private key recovery attacks to analyze signature vulnerabilities and recover private keys from blockchain…
 hasherezade/pe-bear-old
PE-bear (builds only)