
fuzzilli
 googleprojectzero/fuzzilli
A JavaScript Engine Fuzzer
binary-analysiseducationfuzzing+2
2.3k6 days ago
googleprojectzero/fuzzilliA JavaScript Engine Fuzzer
 fuzzysecurity/powershell-suite
My musings with PowerShell
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
 snare/voltron
Extensible debugger UI toolkit providing customizable register, disassembly, stack, memory, breakpoint, and backtrace views for LLDB, GDB, VDB, and…
 dryxio/auto-re-agent
Reconstruct and validate C/C++ code from compiled programs with AI.
 dman95/sasm
SASM - simple crossplatform IDE for NASM, MASM, GAS and FASM assembly languages
 mandiant/speakeasy
Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…

 plasma-disassembler/plasma
Plasma is an interactive disassembler for x86/ARM/MIPS. It can generates indented pseudo-code with colored syntax.
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 onekey-sec/unblob
Extract files from any kind of container formats
 vmoranv/jshookmcp
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
 iddoeldor/frida-snippets
Hand-crafted Frida examples
 amlweems/xzbot
notes, honeypot, and exploit demo for the xz backdoor (CVE-2024-3094)
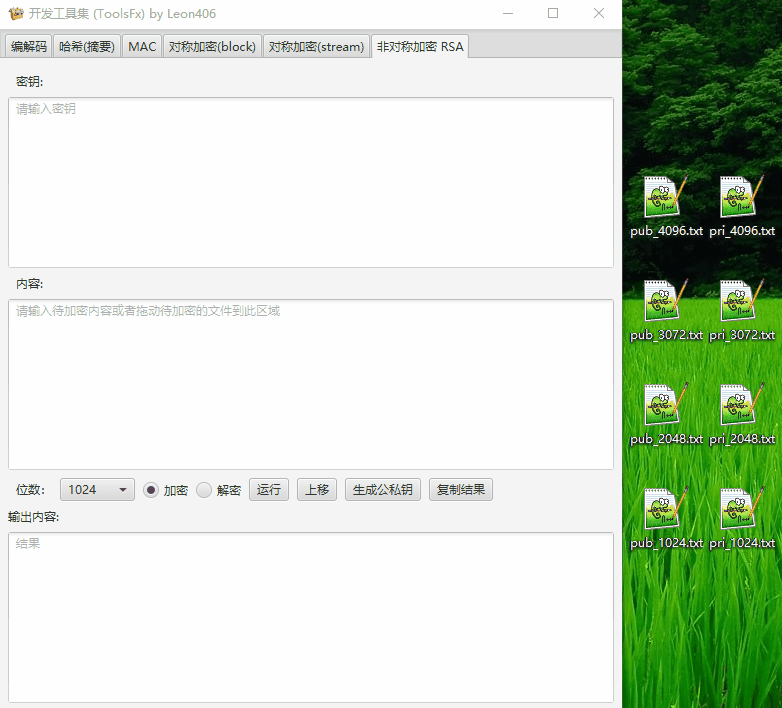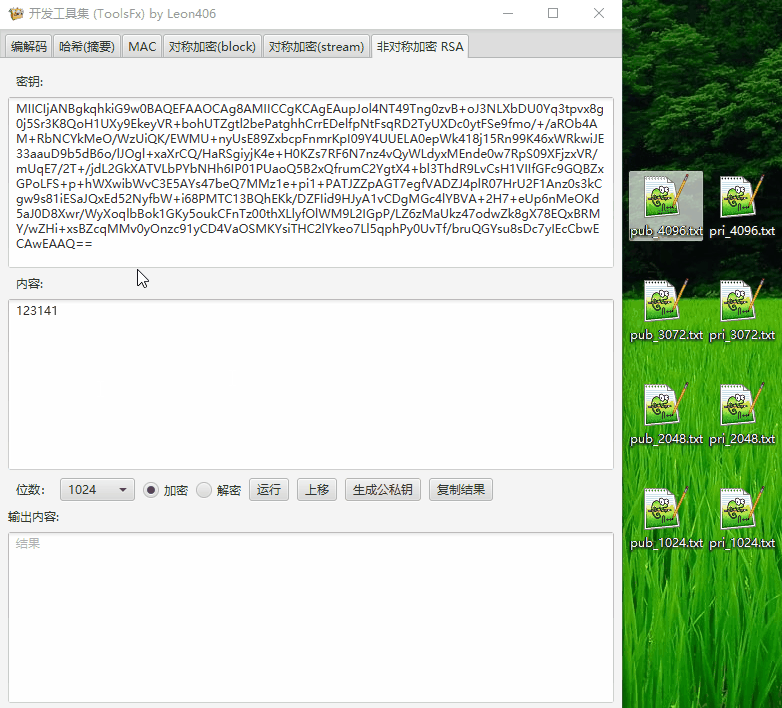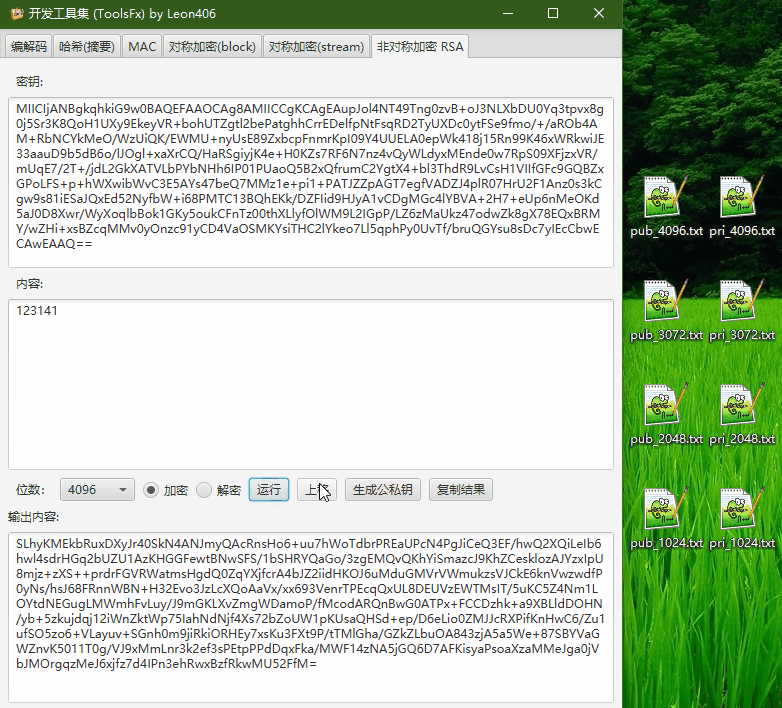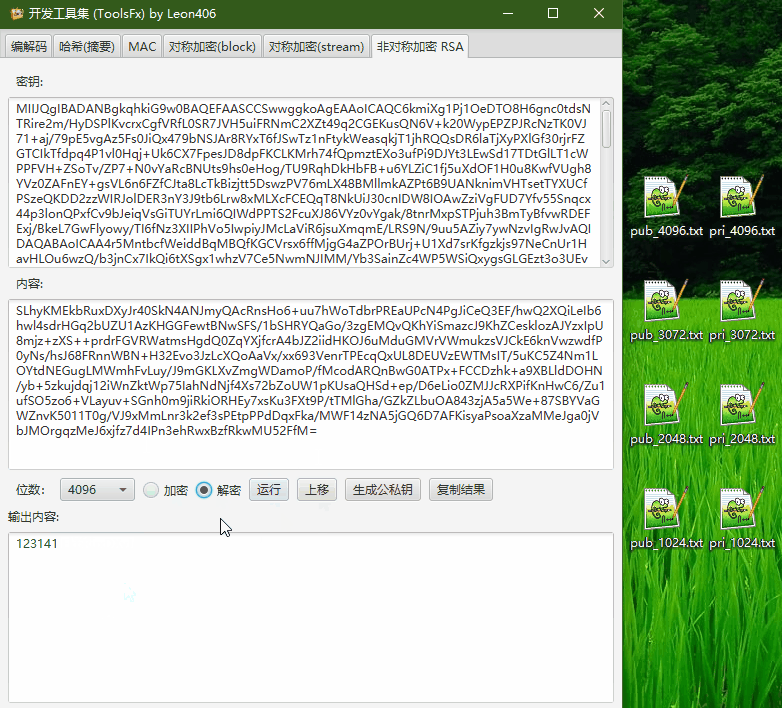 leon406/toolsfx
跨平台密码学工具箱。包含编解码,编码转换,加解密, 哈希,MAC,签名,大数运算,压缩,二维码功能,CTF等功能。
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
 lifting-bits/remill
Library for lifting machine code to LLVM bitcode