
krie
 gui774ume/krie
Linux Kernel Runtime Integrity with eBPF
binary-analysisdefensive-toolsintrusion-detection
gui774ume/krieLinux Kernel Runtime Integrity with eBPF
 elfmaster/maya
Highly advanced Linux anti-exploitation and anti-tamper binary protector for ELF.
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 himitsushell/himitsushell
shell script protector (obfuscation, embedded interpreter, DRM) - invisible to kernel tracing
 shcesama/cve-2023-4863-analysis
Educational analysis of CVE-2023-4863 (libwebp heap buffer overflow) with Blue Team detection tools, static WebP scanner, defensive Java validator,…
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
 gamozolabs/applepie
A hypervisor for fuzzing built with WHVP and Bochs
 tarunyadav/fix-cve-2013-2094
Generates portable SystemTap kernel modules to mitigate CVE-2013-2094 on Enterprise Linux systems, with automated build and deployment scripts for…
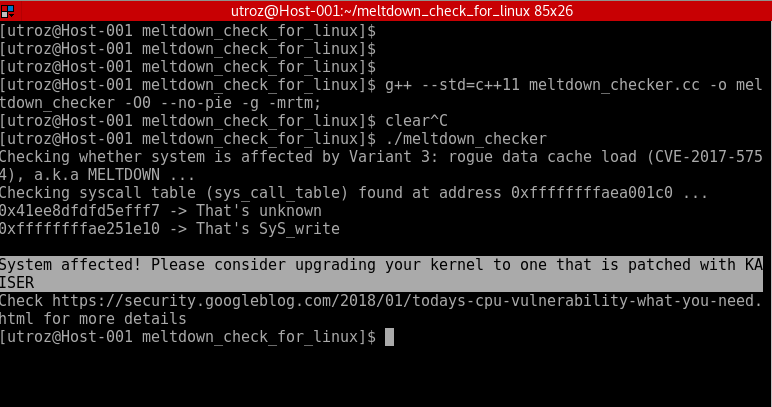 raphaelsc/am-i-affected-by-meltdown
Meltdown Exploit / Proof-of-concept / checks whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a MELTDOWN.
 google/silifuzz
Fuzzes CPU implementations by generating test inputs from software proxies, then executes them on real hardware to detect microarchitecture defects…
 xj2268-ta/kvm-januscape
CVE-2026-53359漏洞补丁

 uni-due-syssec/efcf-framework
EF/CF - Extremely Fast smart Contract Fuzzing
 zhaoxuya520/reverse-skill
AI-powered skill router pack for reverse engineering, penetration testing, and security research. Routes AI agents to correct methodologies and…
 mr-un1k0d3r/edrs
Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
 nanopathi/linux-4.19.72_cve-2020-29370
Linux kernel version 4.19.72 with a specific patch for CVE-2020-29370, intended for vulnerability analysis and exploitation research.
 trinadh465/linux-4.19.72_cve-2023-35828
Linux kernel source tree modified to demonstrate CVE-2023-35828, providing a reference for vulnerability analysis and exploitation research.