Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
67 results
PS-2017-13---CVE-2018-9950 preview

PS-2017-13---CVE-2018-9950

GitHubsandi-go/ps-2017-13---cve-2018-9950

Proof-of-concept for CVE-2018-9950, an out-of-bounds read vulnerability in Foxit Reader/PhantomPDF leading to information disclosure and potential…

binary-analysisexploitationinformation-gathering+2
6 years ago
PowerShell-Suite preview

PowerShell-Suite

GitHubfuzzysecurity/powershell-suite

My musings with PowerShell

binary-analysisdebuggersforensics+5
2.7k4 years ago
OffensiveCSharp preview

OffensiveCSharp

GitHubmatterpreter/offensivecsharp

Collection of Offensive C# Tooling

binary-analysiscode-analysisexploitation+7
1.5k3 years ago
Squalr preview

Squalr

GitHubsqualr/squalr

A generic game/software hacking tool written from the ground up in Rust.

binary-analysisdebuggersdynamic-analysis-sandboxing+5
1863 months ago
magic-extractor preview

magic-extractor

GitHubxchwarze/magic-extractor

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.

binary-analysisdata-recoverydigital-forensics+8
421 month ago
memgrep preview

memgrep

GitHubnccgroup/memgrep

Memory searching utilities

binary-analysisdigital-forensicsforensics+3
4412 years ago
cve-2022-44268-detector preview

cve-2022-44268-detector

GitHubjnschaeffer/cve-2022-44268-detector

Detect images that likely exploit CVE-2022-44268

binary-analysisdata-exfiltrationforensics+3
52 years ago
ElectronVulnerableVersion preview

ElectronVulnerableVersion

GitHubgtgalaxi/electronvulnerableversion

Find Electron Apps Vulnerable to CVE-2023-4863 / CVE-2023-5129

binary-analysisinformation-gatheringreconnaissance+3
63 years ago
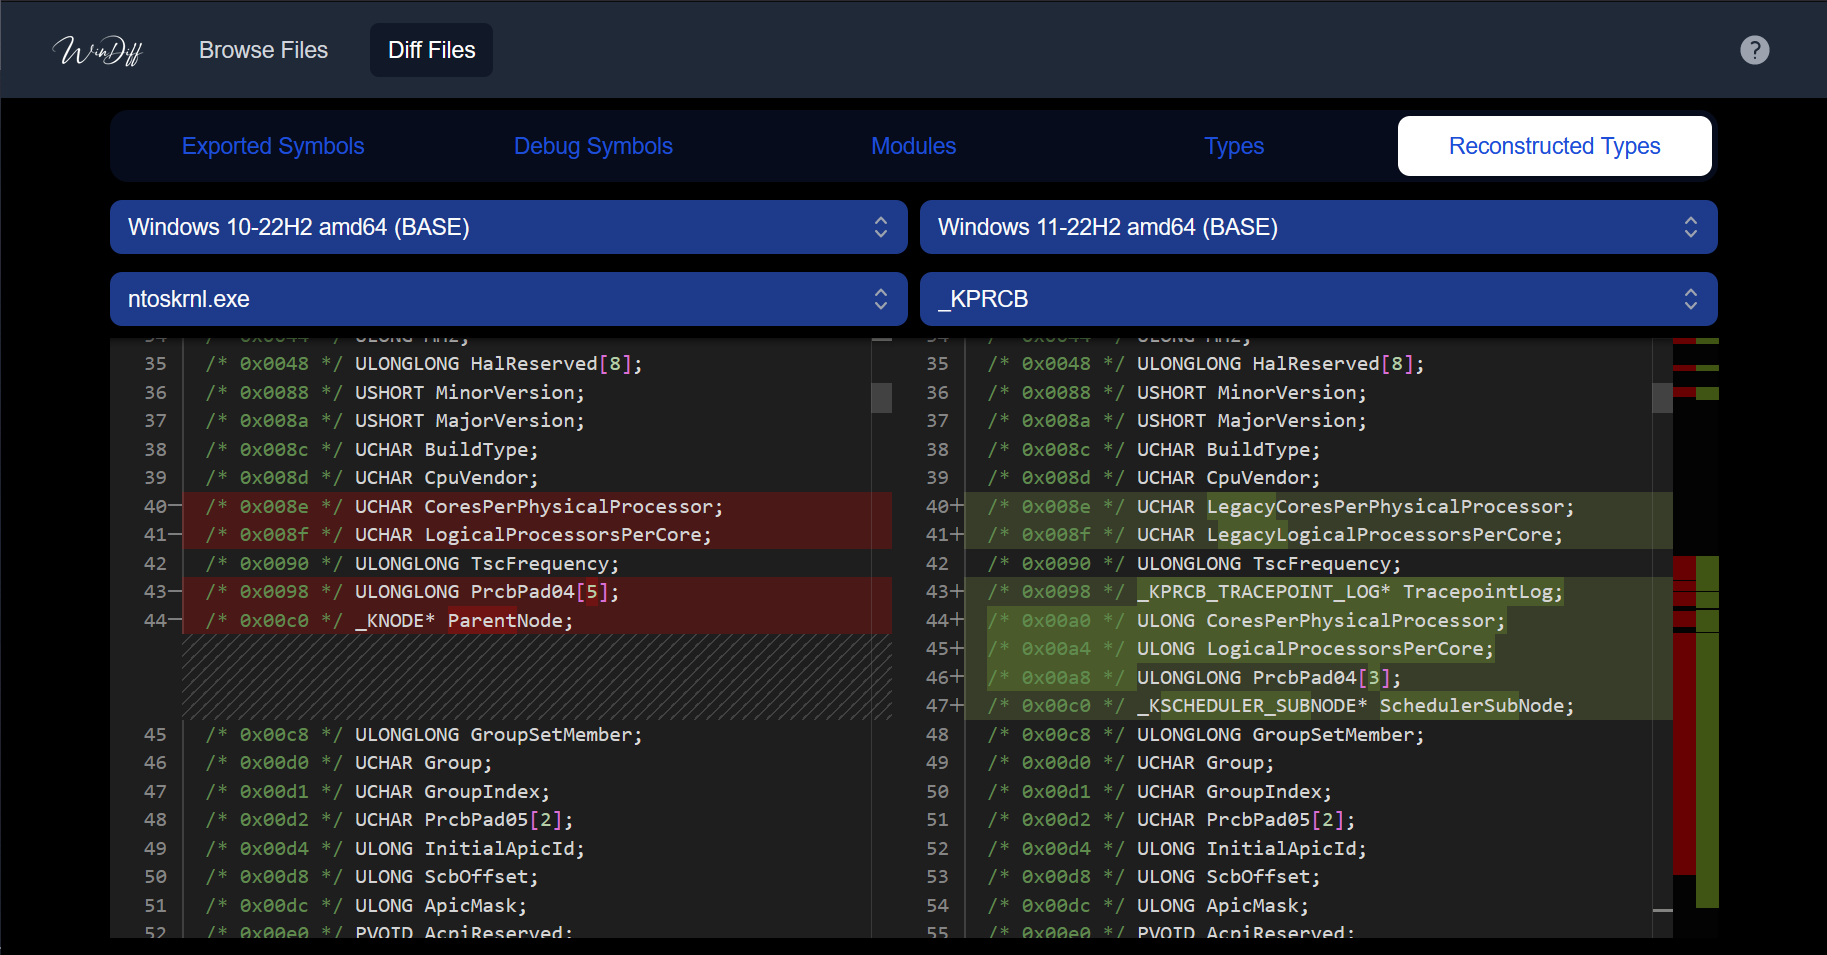
windiff preview

windiff

GitHubergrelet/windiff

Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…

binary-analysisinformation-gatheringreverse-engineering+1
3901 day ago
inhale preview

inhale

GitHubnetspooky/inhale

A malware analysis and classification tool.

binary-analysisforensicshash-analysis+3
1915 years ago
Thick-Client-Pentest-Checklist preview

Thick-Client-Pentest-Checklist

GitHubhari-prasaanth/thick-client-pentest-checklist

A OWASP Based Checklist With 80+ Test Cases

binary-analysiscurated-resourceseducation+5
2053 years ago
DIRT preview

DIRT

GitHubjthuraisamy/dirt

Driver Initial Reconnaissance Tool

binary-analysisreconnaissancevulnerability-analysis
1266 years ago
frida-android-libbinder preview

frida-android-libbinder

GitHubhamz-a/frida-android-libbinder

PoC Frida script to view Android libbinder traffic

android-securitybinary-analysisdynamic-analysis-sandboxing+3
1432 years ago
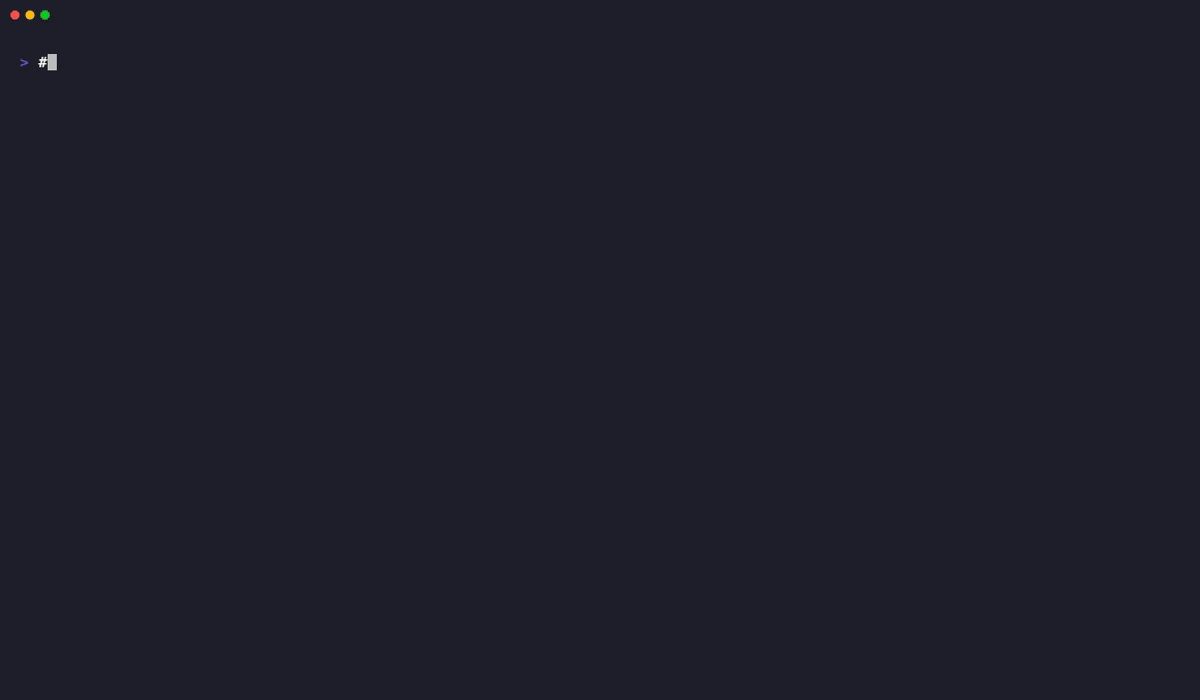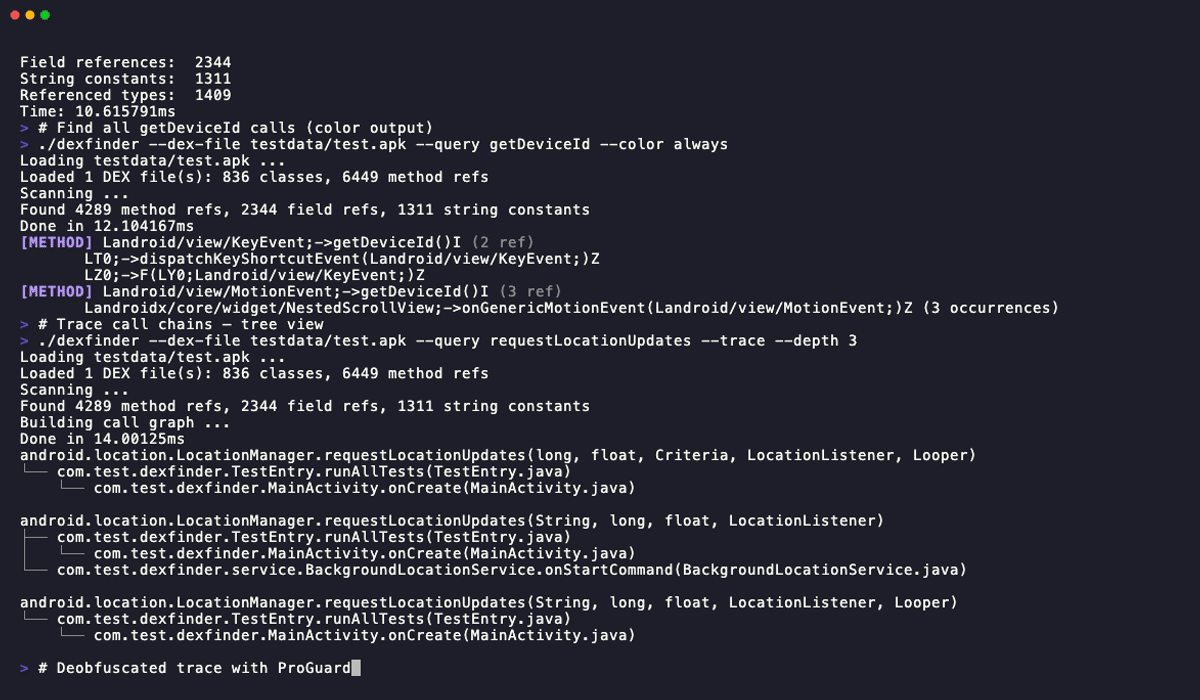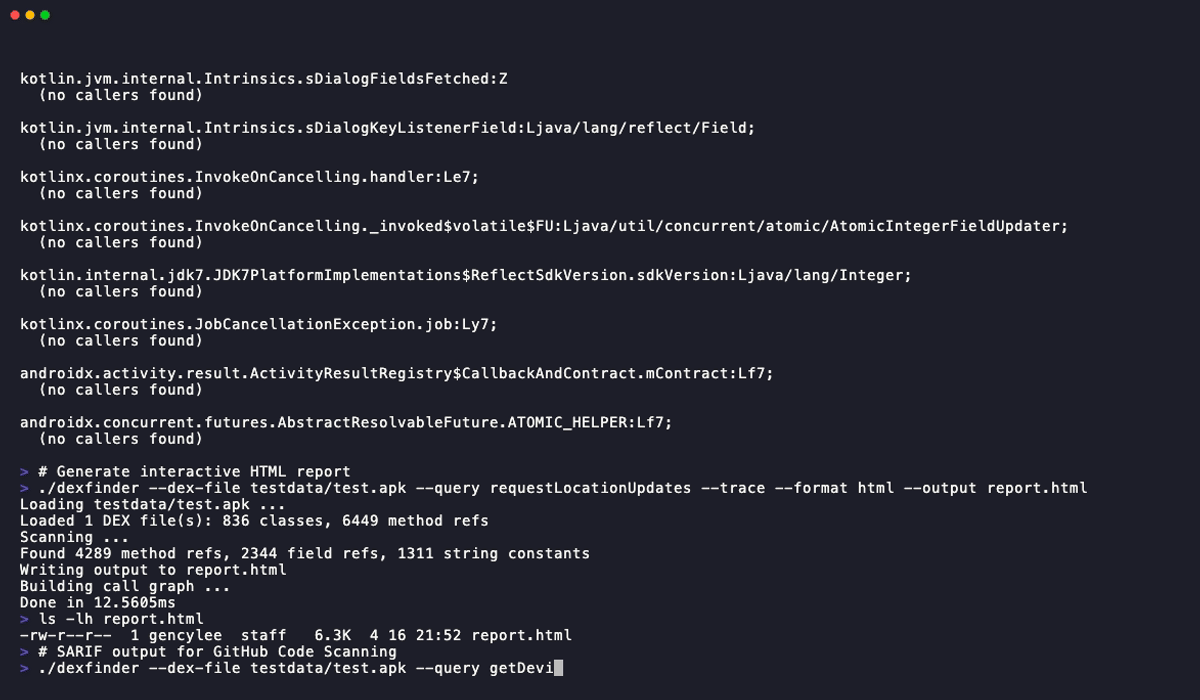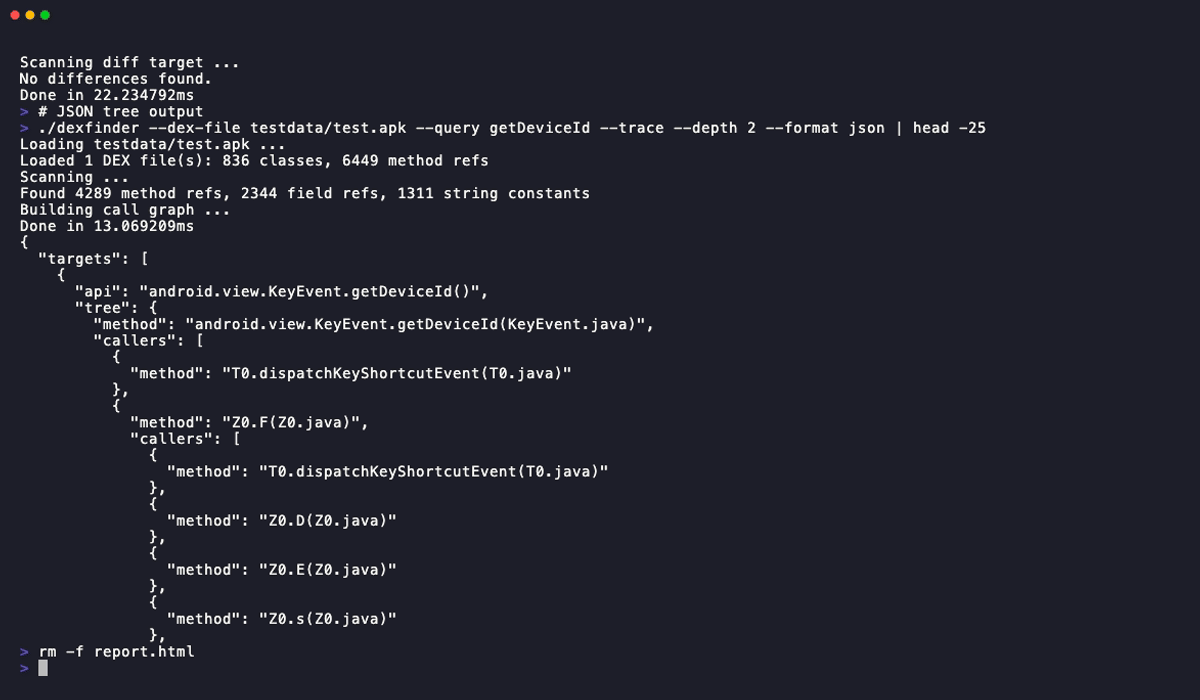
dexfinder preview

dexfinder

GitHubjunelegency/dexfinder

Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection

android-securitybinary-analysiscode-analysis+6
1085 months ago
lifer preview

lifer

GitHubpaul-tew/lifer

Windows link file (shortcuts) examiner

binary-analysisdigital-forensicsforensics+1
682 years ago
jadx-magic-strings preview

jadx-magic-strings

GitHub0rshemesh/jadx-magic-strings

JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.

android-securitybinary-analysiscode-analysis+5
461 month ago
CVE-2019-8540 preview

CVE-2019-8540

GitHubmaldiohead/cve-2019-8540

Kernel Stack info leak at exportObjectToClient function

binary-analysisexploitationinformation-gathering+2
407 years ago
RPC-Triage preview

RPC-Triage

GitHubtalha-nazeef-ahmed/rpc-triage

A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.

binary-analysisreconnaissancered-teaming+3
141 month ago
Previous1234Next