
Evasor
 cyberark/evasor
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies
binary-analysisdefensive-toolspenetration-testing+3
3266 years ago
cyberark/evasorA tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies
 mertdas/privkit
PrivKit is a simple beacon object file that detects privilege escalation vulnerabilities caused by misconfigurations on Windows OS.
 shack2/javaserializetools
Java反序列化漏洞利用工具V1.0 Java反序列化相关漏洞的检查工具,采用JDK 1.8+NetBeans8.2开发,软件运行必须安装JDK 1.8或者以上版本。 支持:weblogic xml反序列化漏洞…
 trailofbits/rpcinvestigator
Windows RPC interface discovery and analysis tool with visual endpoint enumeration, PE parsing, symbol resolution, real-time ETW sniffing, and…
 lab52io/leakedhandlesfinder
Leaked Windows processes handles identification tool
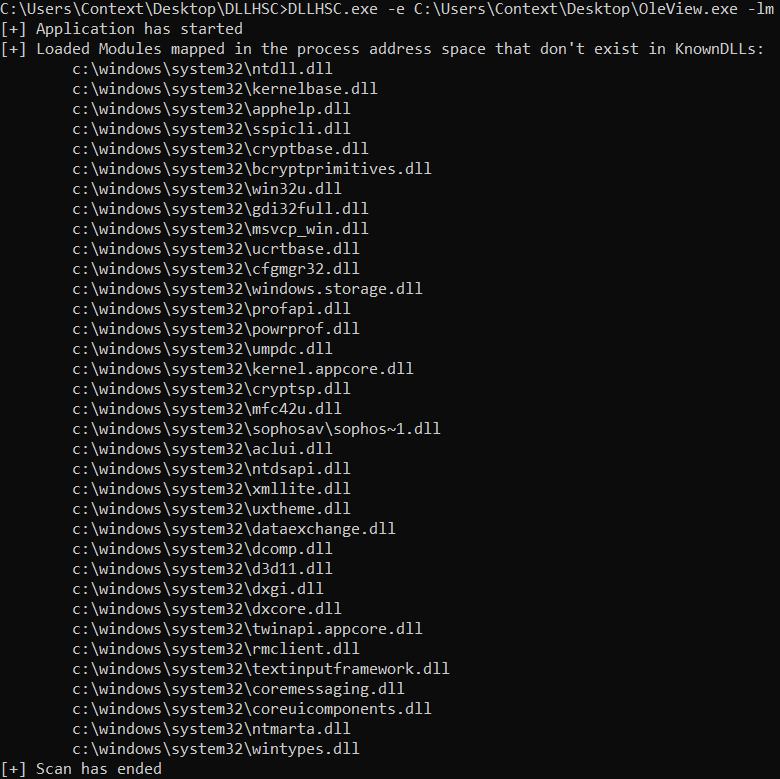 ctxis/dllhsc
Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…
 blacksnufkin/holygrail
BYOVD hunter to help prioritize windows drivers worth manual analysis
 siemens/fluffi
FLUFFI (Fully Localized Utility For Fuzzing Instantaneously) - A distributed evolutionary binary fuzzer for pentesters
 own2pwn/r0ak
r0ak ("roak") is the Ring 0 Army Knife -- A Command Line Utility To Read/Write/Execute Ring Zero on for Windows 10 Systems
 moiz-2x/cve-2025-21420_poc
Proof of Concept CVE-2025-21420 (Windows Disk Cleanup Tool EoP)
 sec-tools/litefuzz
A multi-platform fuzzer for poking at userland binaries, network clients and servers
 iss4cf0ng/dotnetpeloader
A C# PE loader for x64 and x86 PE files.
 xyl2k/black-eye-rsa-attacking-toolkit-v0.1f-compiled
The great RSA Attacking Toolkit compiled for Windows
 tarpeg007/cve-2026-19490
NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC
 ctn-qvo/auto_extract_offsets
Automated offset calculator for CVE-2026-43499, enabling precise memory offset computation for vulnerability exploitation and binary analysis.
 jbaines-r7/theway
A tool for extracting, modifying, and crafting ASDM binary packages (CVE-2022-20829)
 nam3lum/msi-central_privesc
CVE-2022-38532 - Local Privilege Escalation vulnerability in MSI Center Application