
Bitmancer
 zimawhit3/bitmancer
Nim Library for Offensive Security Development
binary-analysisids-ips-evasionpayload-development+4
200
zimawhit3/bitmancerNim Library for Offensive Security Development
 allthingsida/allthingsida
Repository for the code snippets from the AllThingsIDA video channel
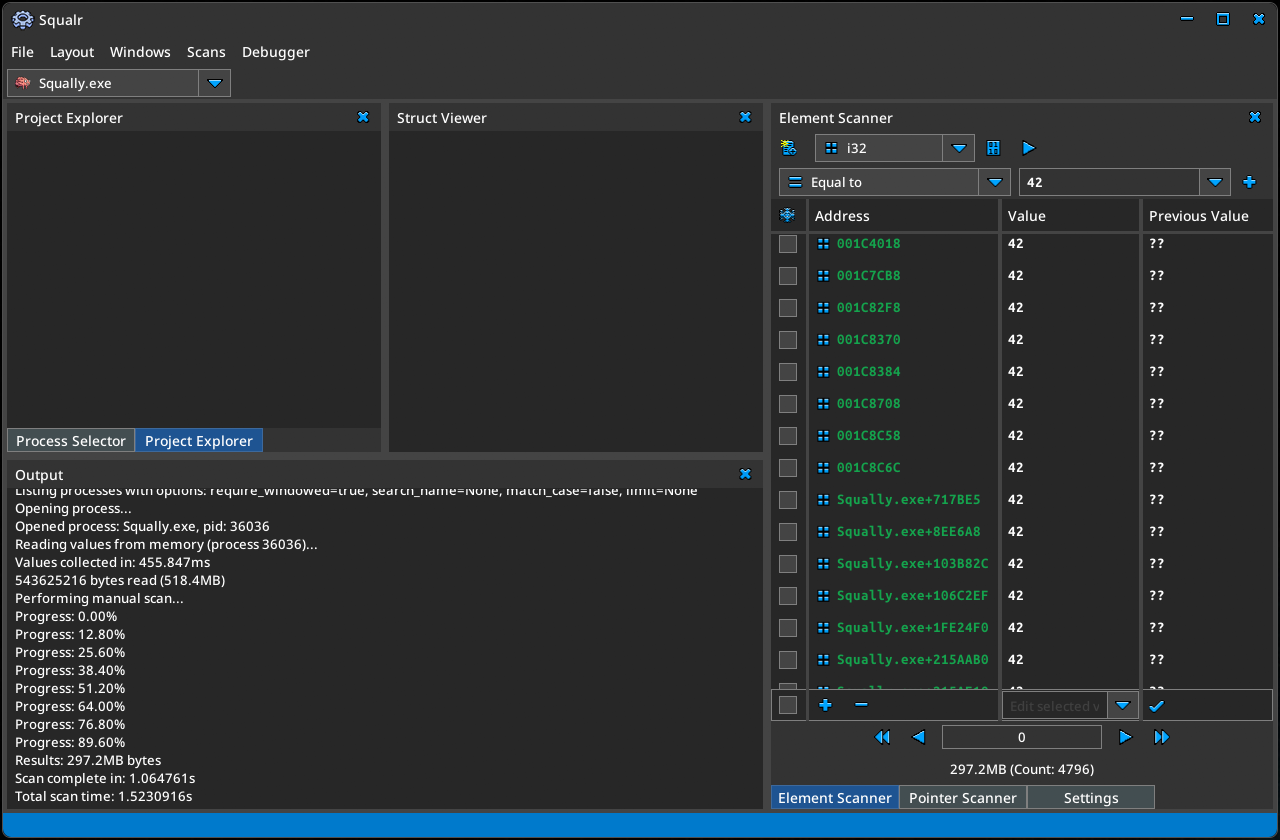 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 jthuraisamy/dirt
Driver Initial Reconnaissance Tool
 lcbower33/stegoscan
Automated steganography detection tool that scans websites, web servers, and local directories using AI-driven object/text recognition and deep file…
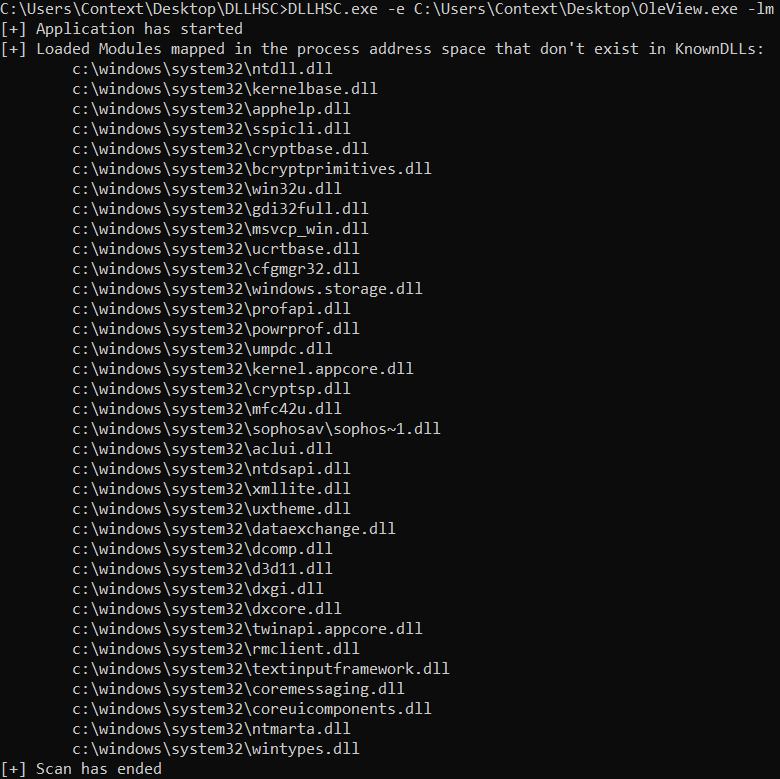 ctxis/dllhsc
Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…
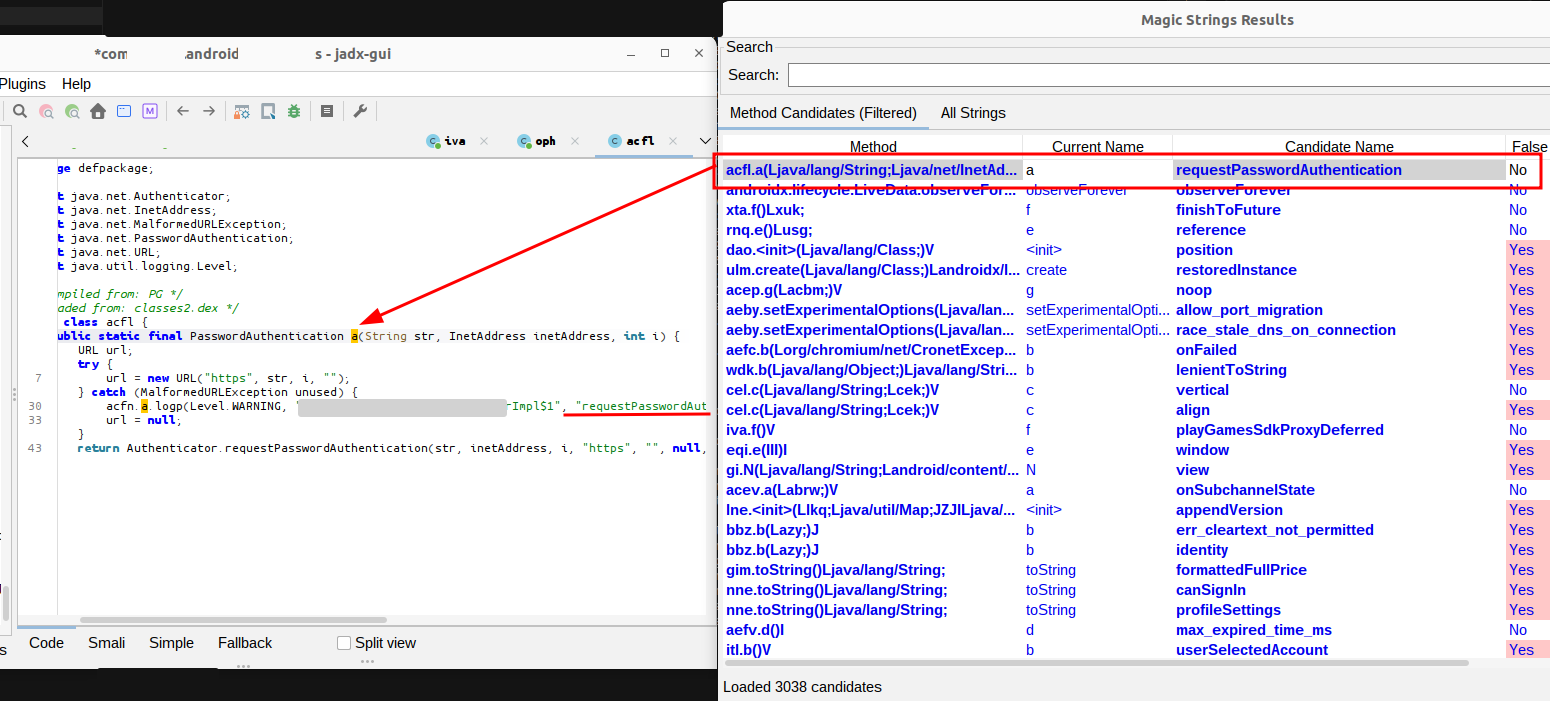 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
 karollooool/cve-2026-50416-writeup-and-poc
CVE-2026-50416: Windows 11 KASLR bypass
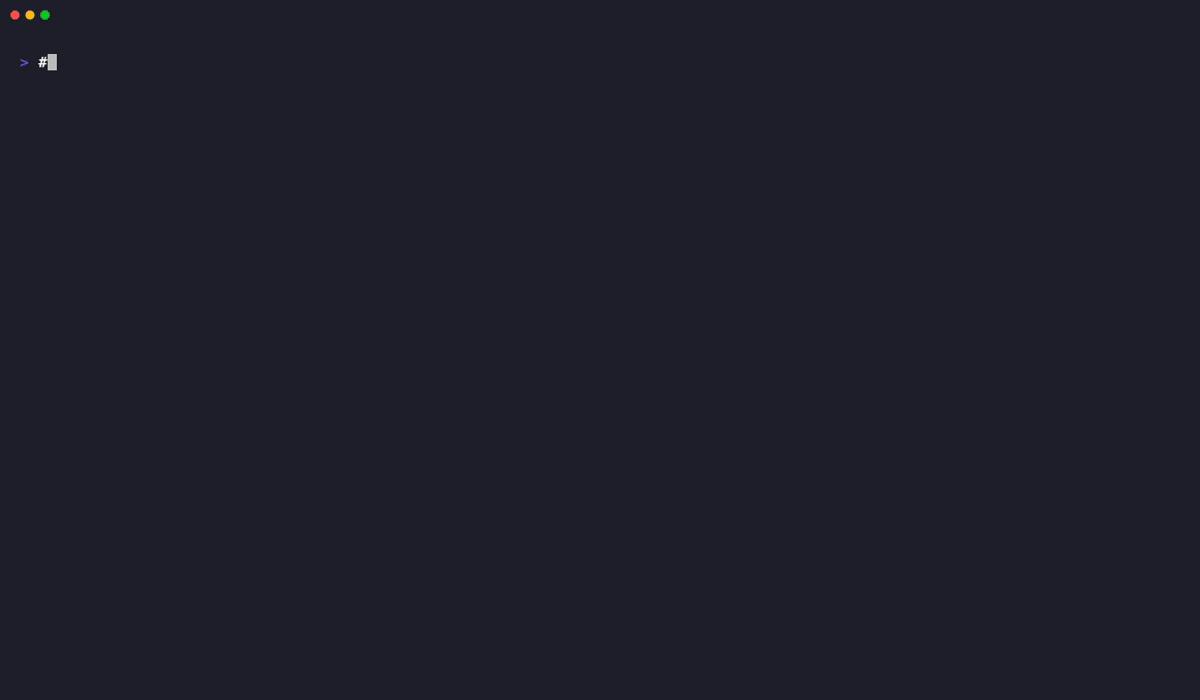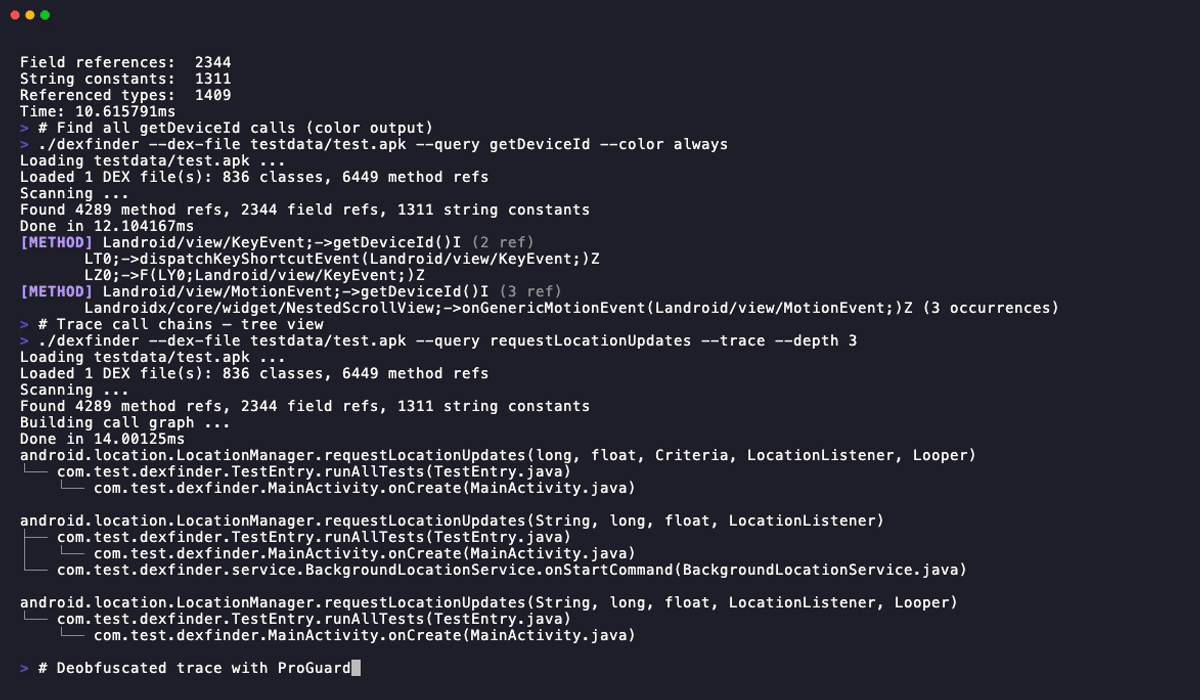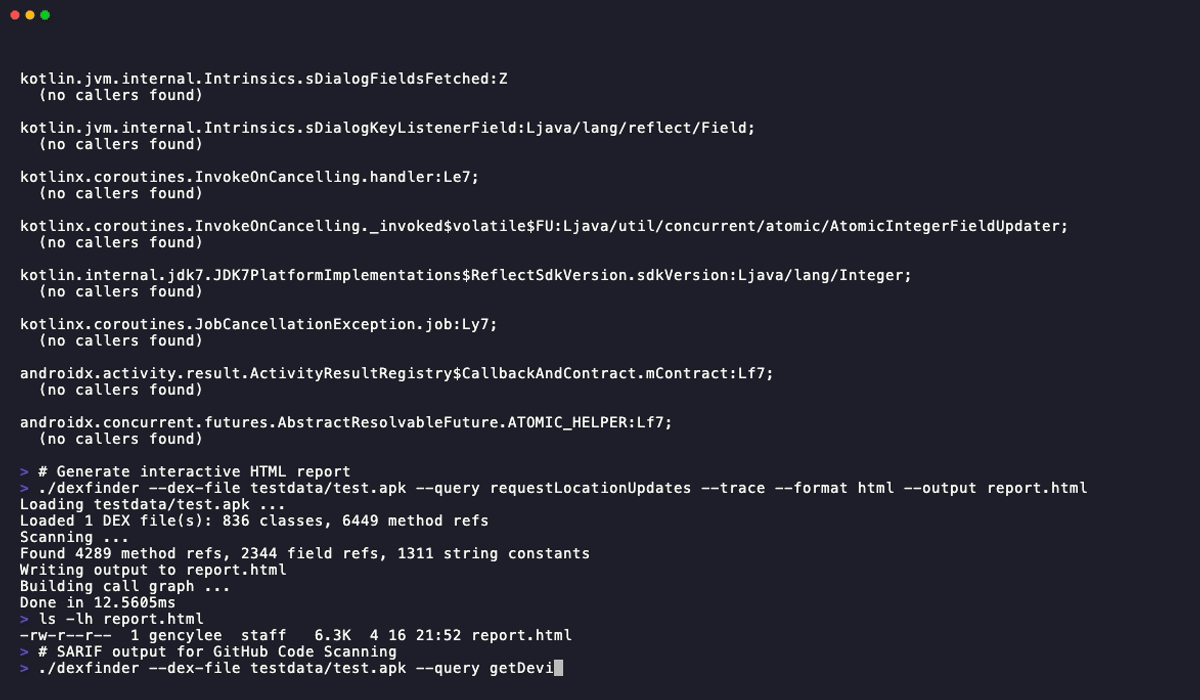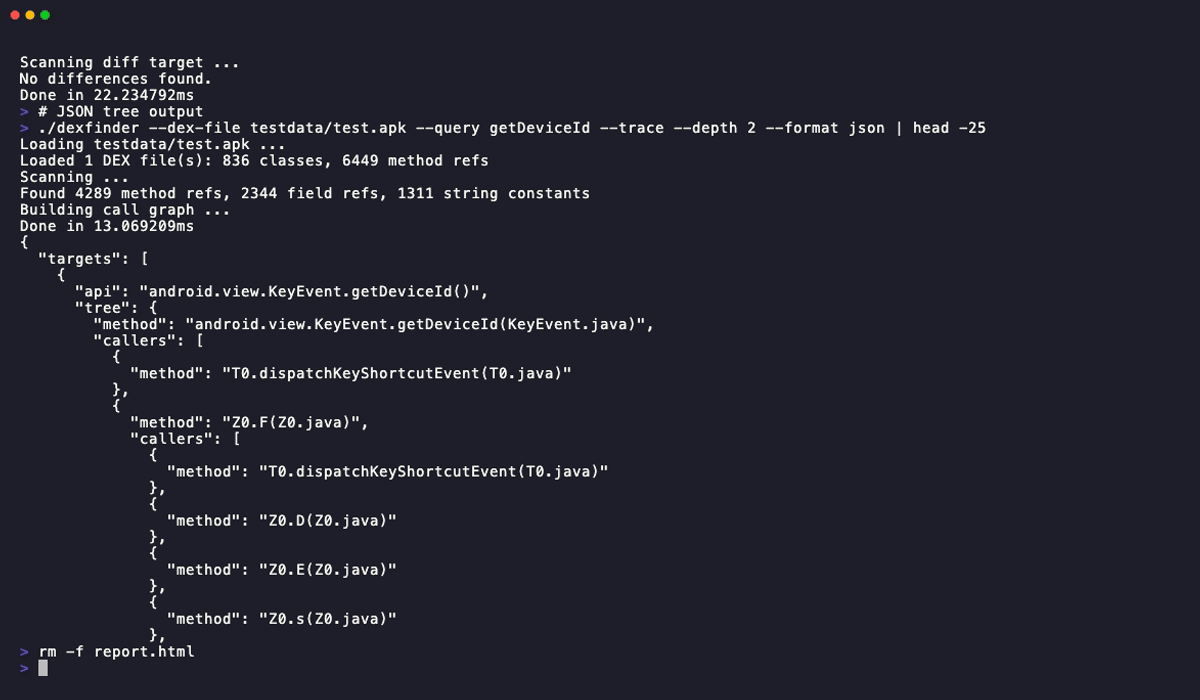 junelegency/dexfinder
Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection
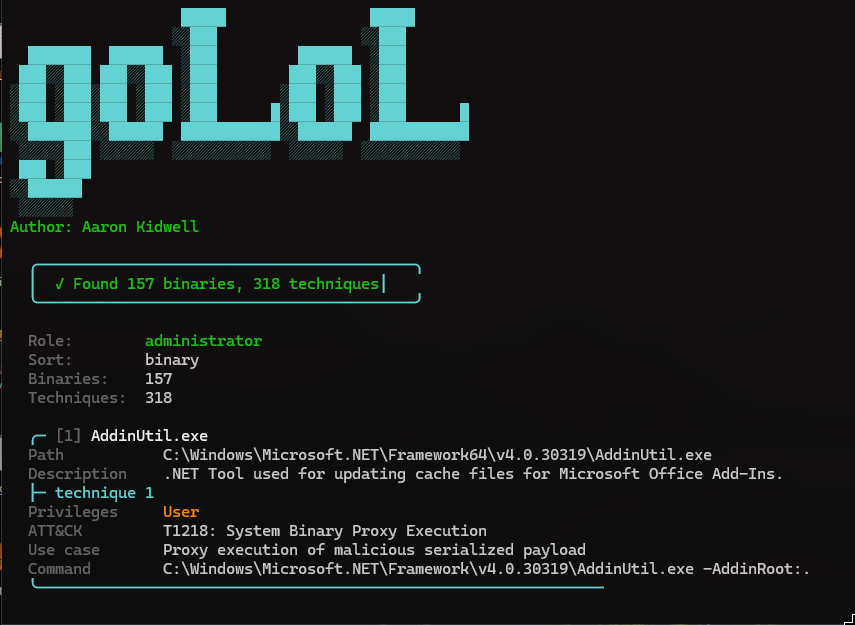 aaron-kidwell/golol
goLoL is a Windows host scanner with dual support for LOLBAS binaries and LOLDrivers. It lists LOLBAS techniques runnable at your current privilege…
 paul-tew/lifer
Windows link file (shortcuts) examiner
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 cxiao/rust-reversing-workshop-recon-2024
Slides and files for the Reversing Rust Binaries: One step beyond strings workshop at REcon 2024, presented on June 28, 2024.
 kartoffelpflanze/odis-project-explorer
Python dumper/explorer for MCD Runtime Projects used by ODIS
 maldiohead/cve-2019-8540
Kernel Stack info leak at exportObjectToClient function

 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect