

raptor
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
ai-assisted-reversingbinary-analysisdynamic-analysis-sandboxing+7
3.6k
gadievron/raptorAutonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
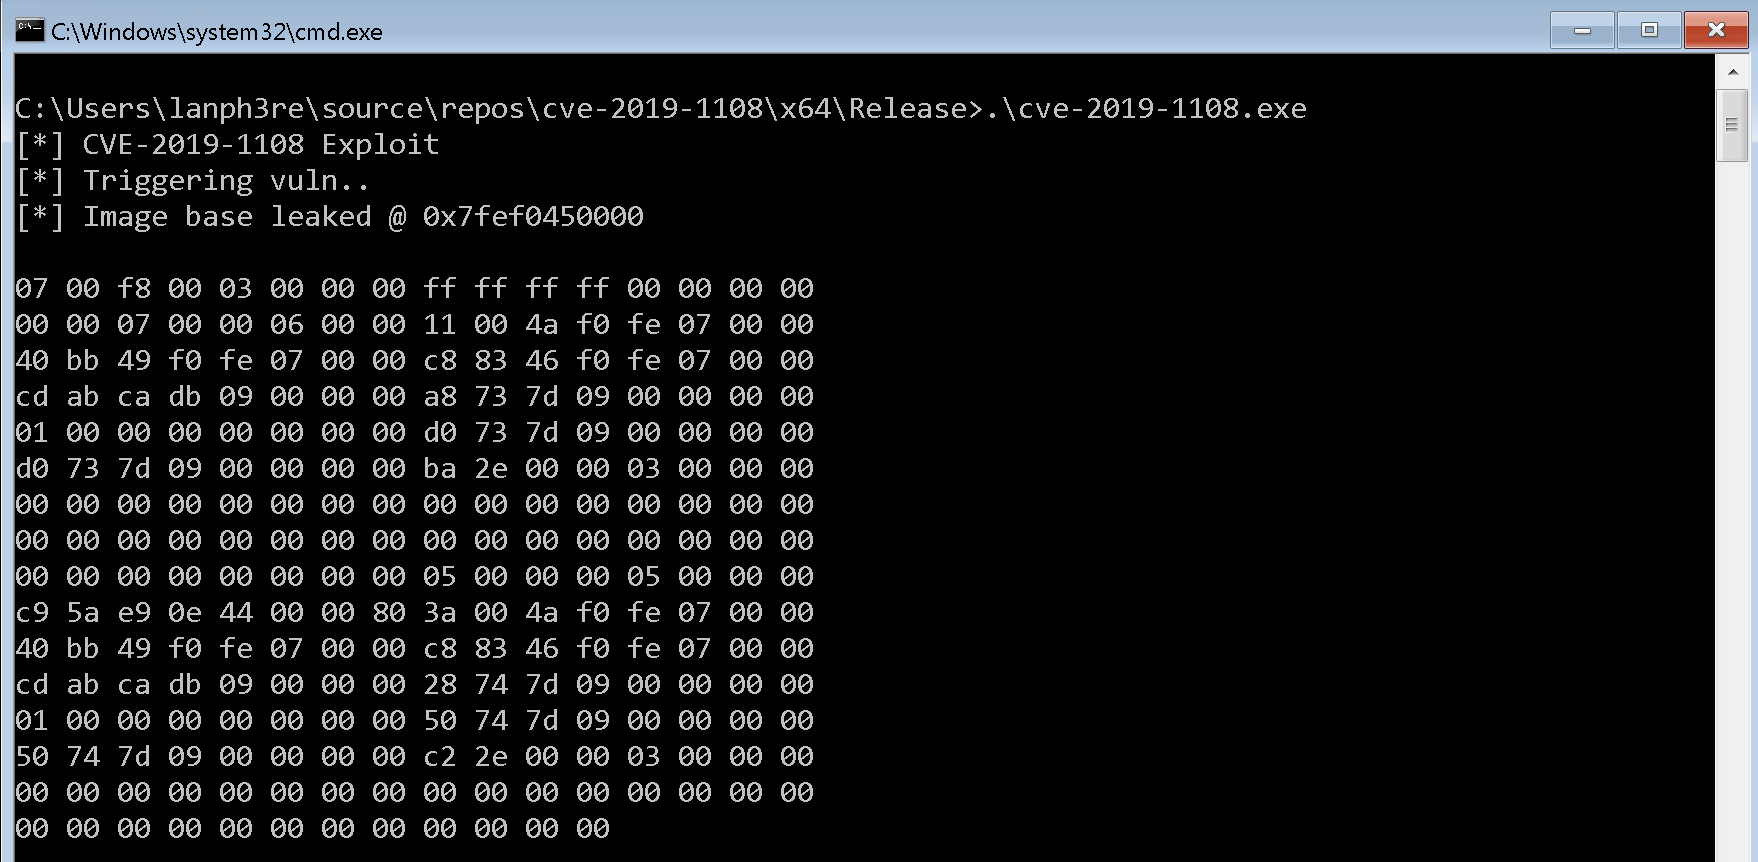 lanph3re/cve-2019-1108
Proof-of-concept exploit for CVE-2019-1108, an RDP client information disclosure vulnerability that leaks memory contents via specially crafted…
 nidhihcl/external_expat_2.1.0_cve-2022-43680
C library for stream-oriented XML parsing with a focus on vulnerability analysis and exploitation of CVE-2022-43680, enabling fuzzing and…
 galoisinc/mate
Interactive program analysis suite using Code Property Graphs to hunt for bugs in C and C++ code, unifying application-specific and low-level…
 jnschaeffer/cve-2022-44268-detector
Detect images that likely exploit CVE-2022-44268
 checkpointsw/karta
IDA Python plugin for fast, location-driven matching of open-source library symbols in binaries, enabling efficient reverse engineering and…
 pazhanivelmani/webp_android10_r33_cve-2023-1999
Proof-of-concept exploit for CVE-2023-1999 targeting the WebP codec library on Android 10 (r33). Demonstrates a heap buffer overflow vulnerability in…
 trinadh465/external_aac_aosp10_r33_cve-2023-21282
Analyzes and patches a specific Android vulnerability (CVE-2023-21282) in the AAC audio codec, providing a patched AOSP10 source tree for security…
 saurabh2088/expat_2_1_0_cve-2024-28757
C library for stream-oriented XML parsing, with a focus on analyzing and reproducing CVE-2024-28757 vulnerability in Expat 2.1.0.
 nccgroup/tpmgenie
TPM Genie is an I2C bus interposer for discrete Trusted Platform Modules
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect
 vivianuba/grandstream-cve-2026-2329-analysis
Defensive vulnerability-research project comparing vulnerable and patched Grandstream GXP1600 firmware for CVE-2026-2329, using SquashFS extraction,…
 idanshechter/cve-2017-13208-scanner
Python script using r2pipe to detect CVE-2017-13208 in Android libnetutils.so by checking for missing dhcp_size validation via static binary analysis.
 ga1ois/blackhat-europe-2022
Select Bugs From Binary Where Pattern Like CVE-1337-Days
 gtgalaxi/electronvulnerableversion
Find Electron Apps Vulnerable to CVE-2023-4863 / CVE-2023-5129
 cao-wuhui/cve-2025-69720
Advisory for CVE-2025-69720: stack-based buffer overflow in GNU ncurses infocmp (CWE-121)
 20urc3/sekiryu
Comprehensive toolkit for Ghidra headless.
 vulhunt-re/vulhunt
Vulnerability detection framework by Binarly's REsearch team