
filterforge
 cloudflare/filterforge
Tool for solving BPF filters and crafting packets based on these.
binary-analysisforensicsfuzzing+5
cloudflare/filterforgeTool for solving BPF filters and crafting packets based on these.
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
 gmh5225/frida-stalker-ntstrace
frida-stalker based system call tracer on windows(x64).
 0xxon/cve-2020-0601-utils
C++ based utility to check if certificates are trying to exploit CVE-2020-0601
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
 coldzer0/cmulator
Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…
 beardypig/ghidra-emotionengine
Ghidra Processor for the Play Station 2's Emotion Engine MIPS based CPU
 mandiant/flashmingo
Automatic analysis of SWF files based on some heuristics. Extensible via plugins.
 cs01/gdbgui
Browser-based frontend to gdb (gnu debugger). Add breakpoints, view the stack, visualize data structures, and more in C, C++, Go, Rust, and Fortran.…
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
 indalok/rzweb
A complete browser-based reverse engineering platform built on Rizin, running entirely client-side via WebAssembly.
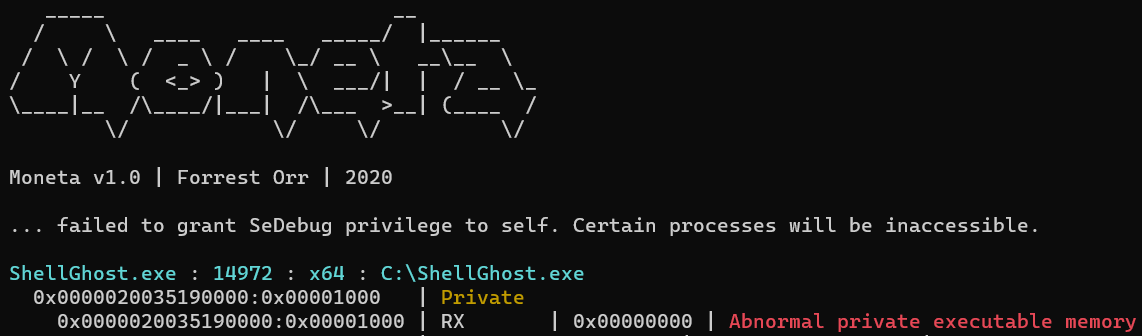 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
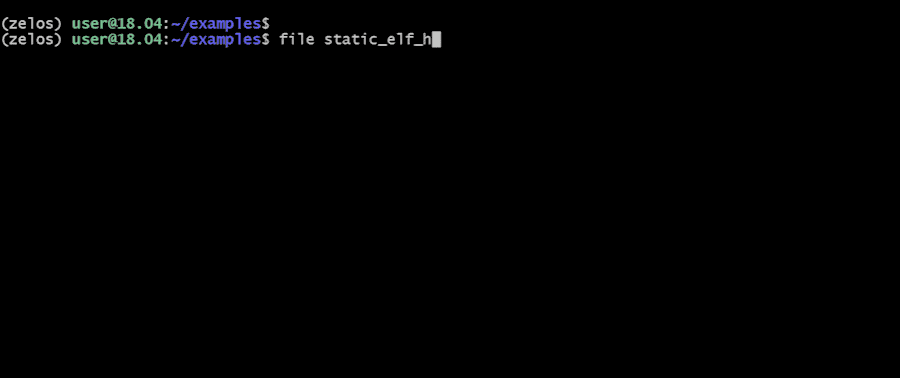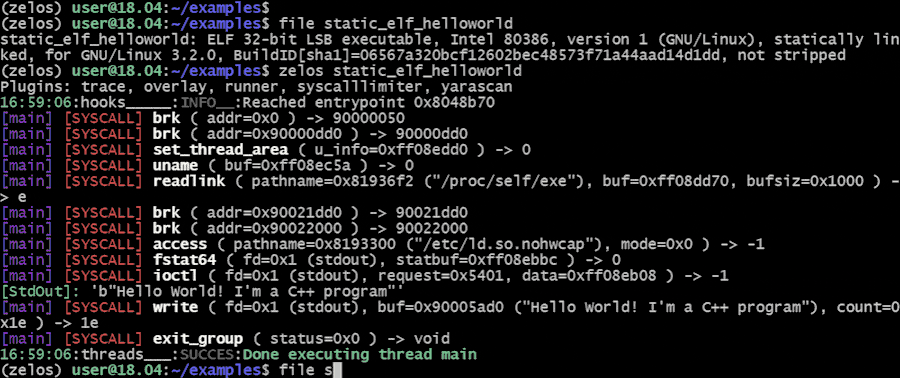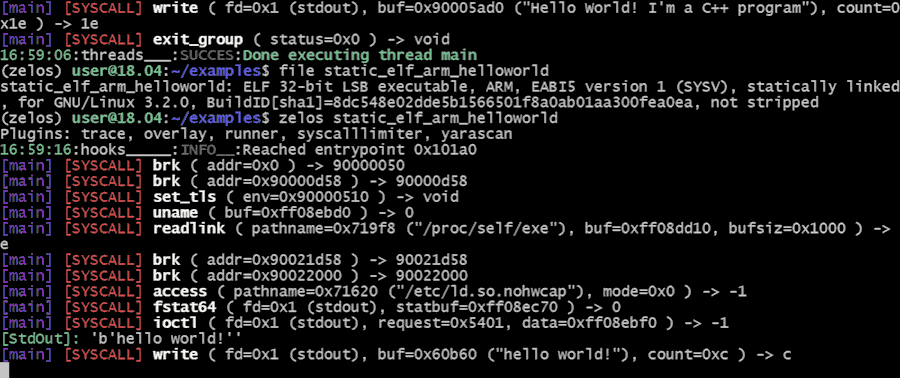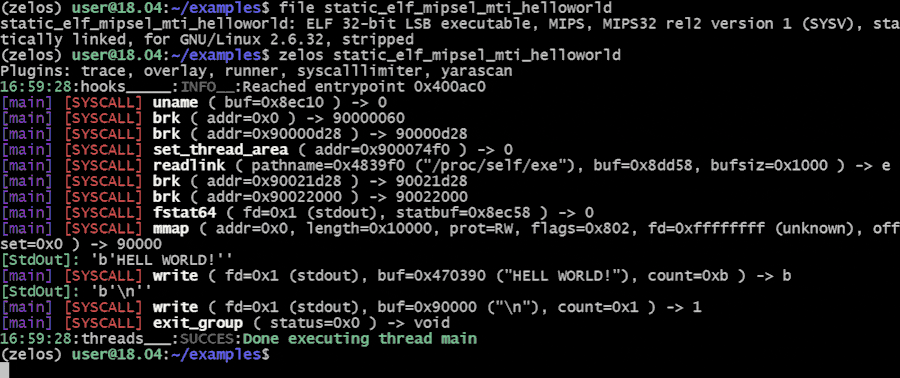 zeropointdynamics/zelos
A comprehensive binary emulation and instrumentation platform.