cerberus-re-skill
cerberus-re is a local Apple-focused reverse-engineering workbench for building a repeatable three-headed static/dynamic/instrumentation loop around…

cerberus-re is a local Apple-focused reverse-engineering workbench for building a repeatable three-headed static/dynamic/instrumentation loop around…

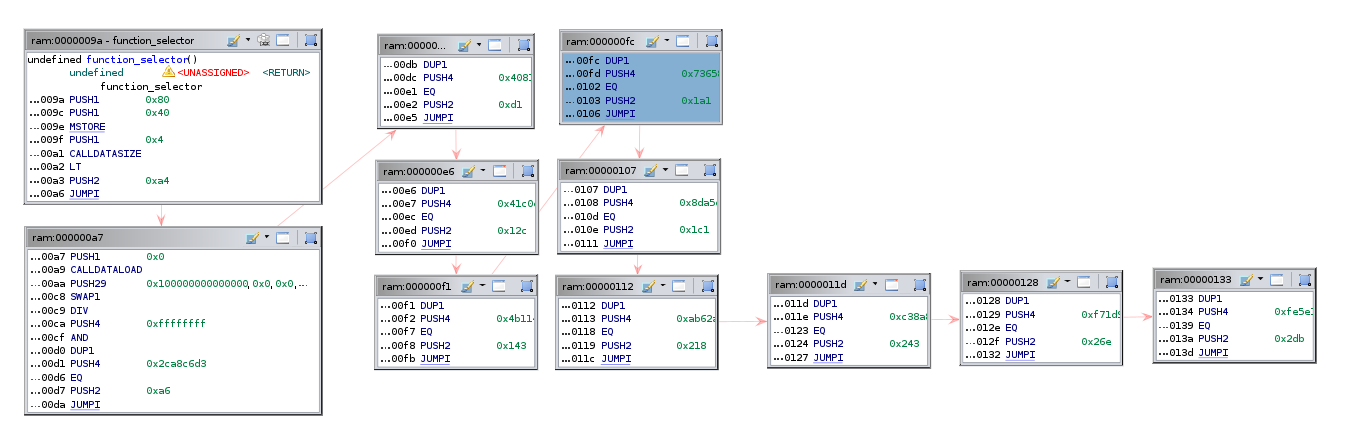
Ghidra module for disassembling, decompiling, and analyzing Ethereum smart contract bytecode. Detects insecure instructions, extracts hidden methods,…

Intel 64/Windows low-level experiments

A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…

A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…

Repository for the code snippets from the AllThingsIDA video channel

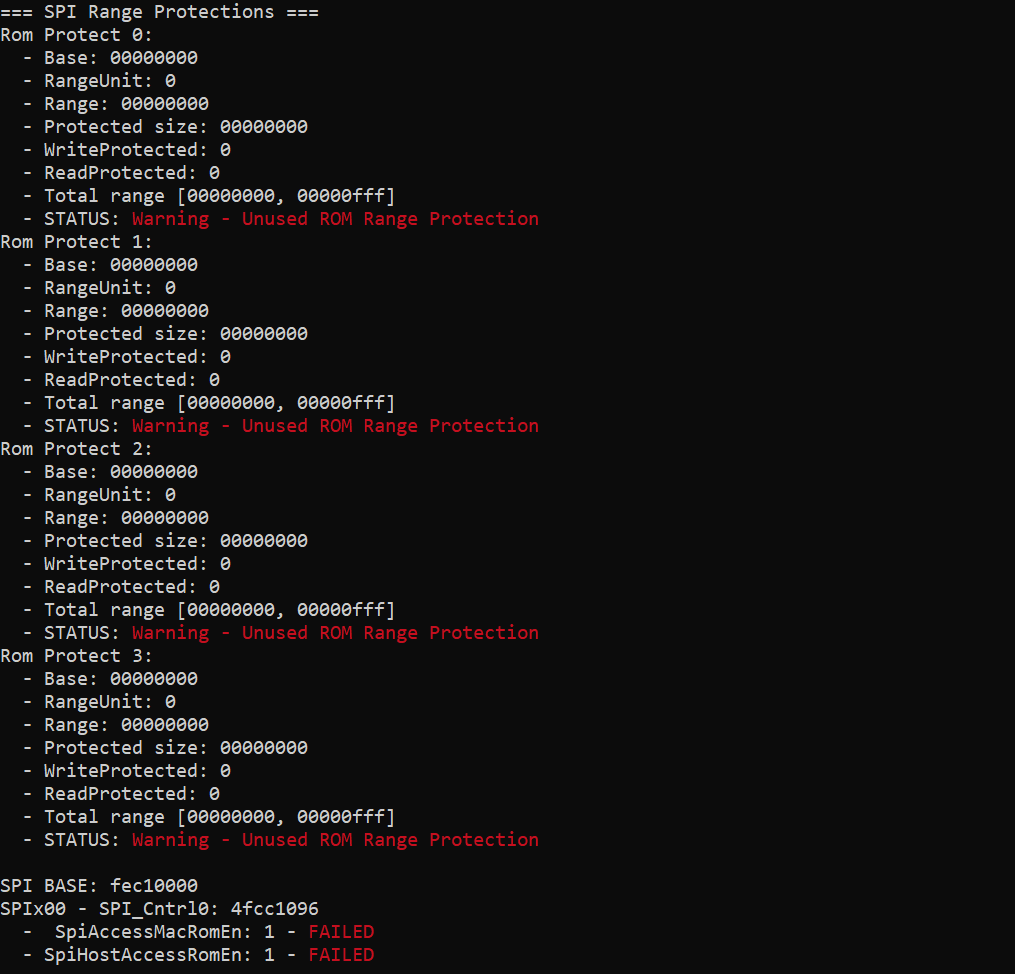
Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…

A generic game/software hacking tool written from the ground up in Rust.

Fuzzy comparison tool for deobfuscating Android APKs by identifying renamed functions across versions, generating mapping files and interactive HTML…

Adaptix C2 agent using Crystal Palace PIC linker and PICO module system

Platform independent peCloak fork based on Capstone

An event driven multi-core process debugging, tracing, and manipulation framework.

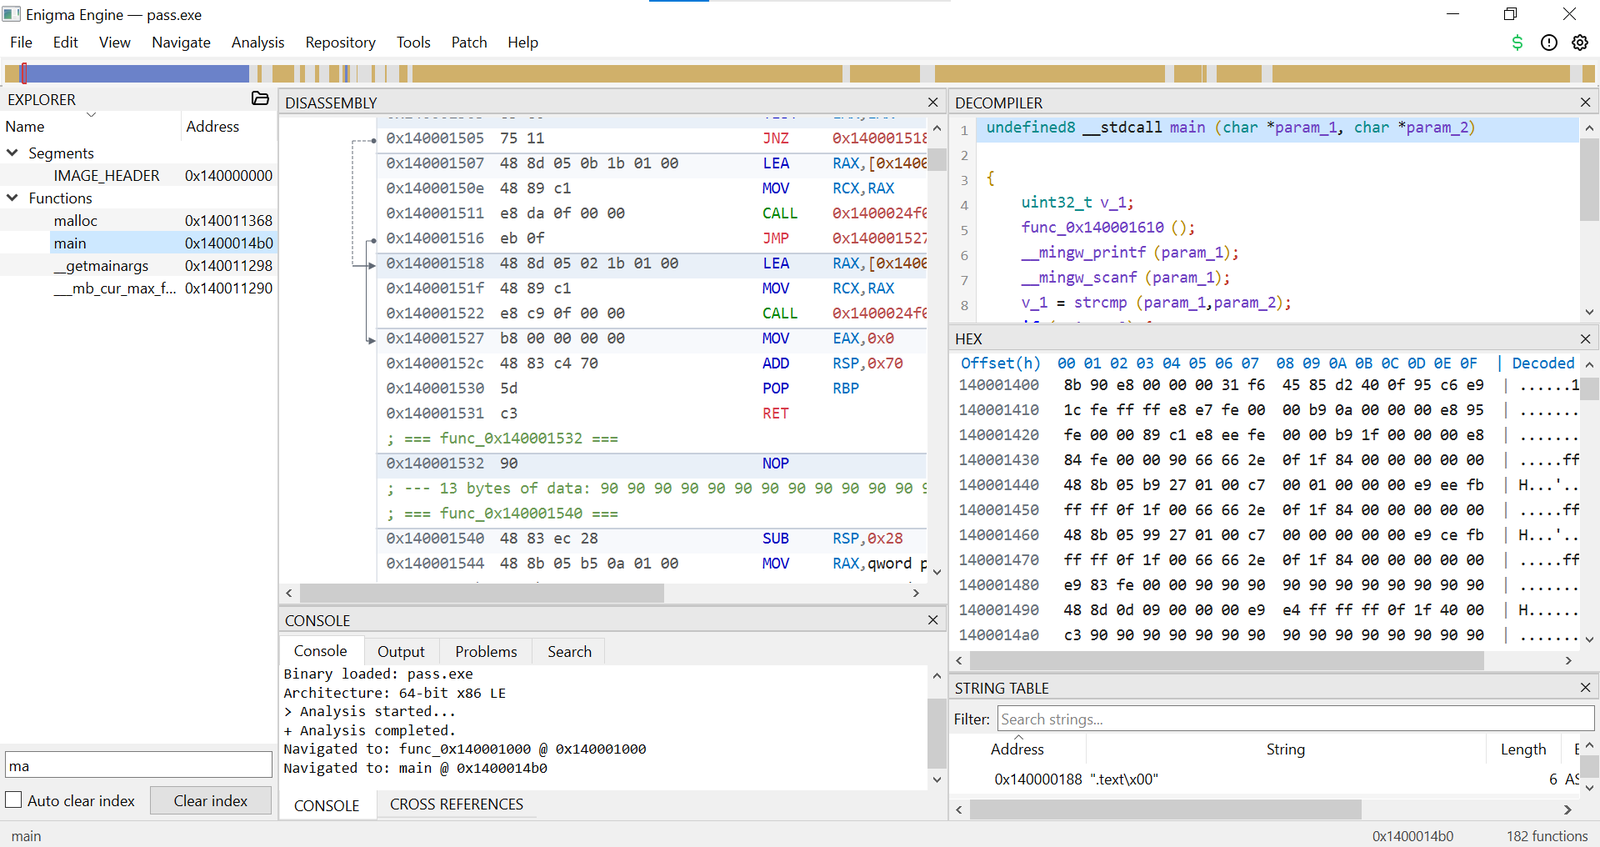
Native C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and…

Determine which CPU architecture is used in a binary file.

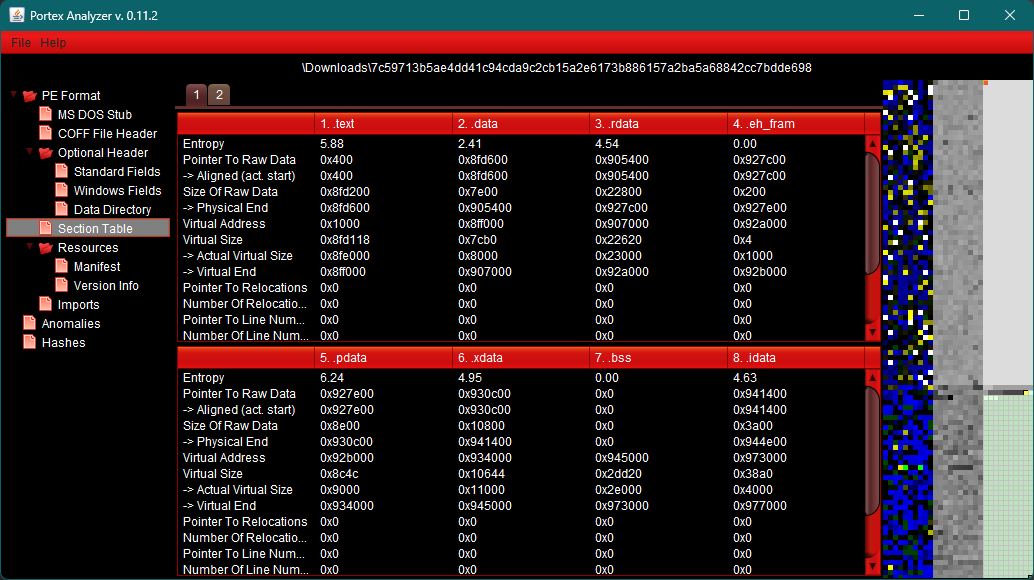
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library

Static deobfuscation toolkit for compiled V8 JavaScript bytecode, focusing on JSCeal payloads. Provides pattern-driven filters, control-flow…

:detective: Analyse binaries for missing security features, information disclosure and more...

GarbageMan is a set of tools for analyzing .NET binaries through heap analysis.