
litefuzz
 sec-tools/litefuzz
A multi-platform fuzzer for poking at userland binaries, network clients and servers
binary-analysisexploitationfuzzing+2
sec-tools/litefuzzA multi-platform fuzzer for poking at userland binaries, network clients and servers
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
 vivianuba/grandstream-cve-2026-2329-analysis
Defensive vulnerability-research project comparing vulnerable and patched Grandstream GXP1600 firmware for CVE-2026-2329, using SquashFS extraction,…
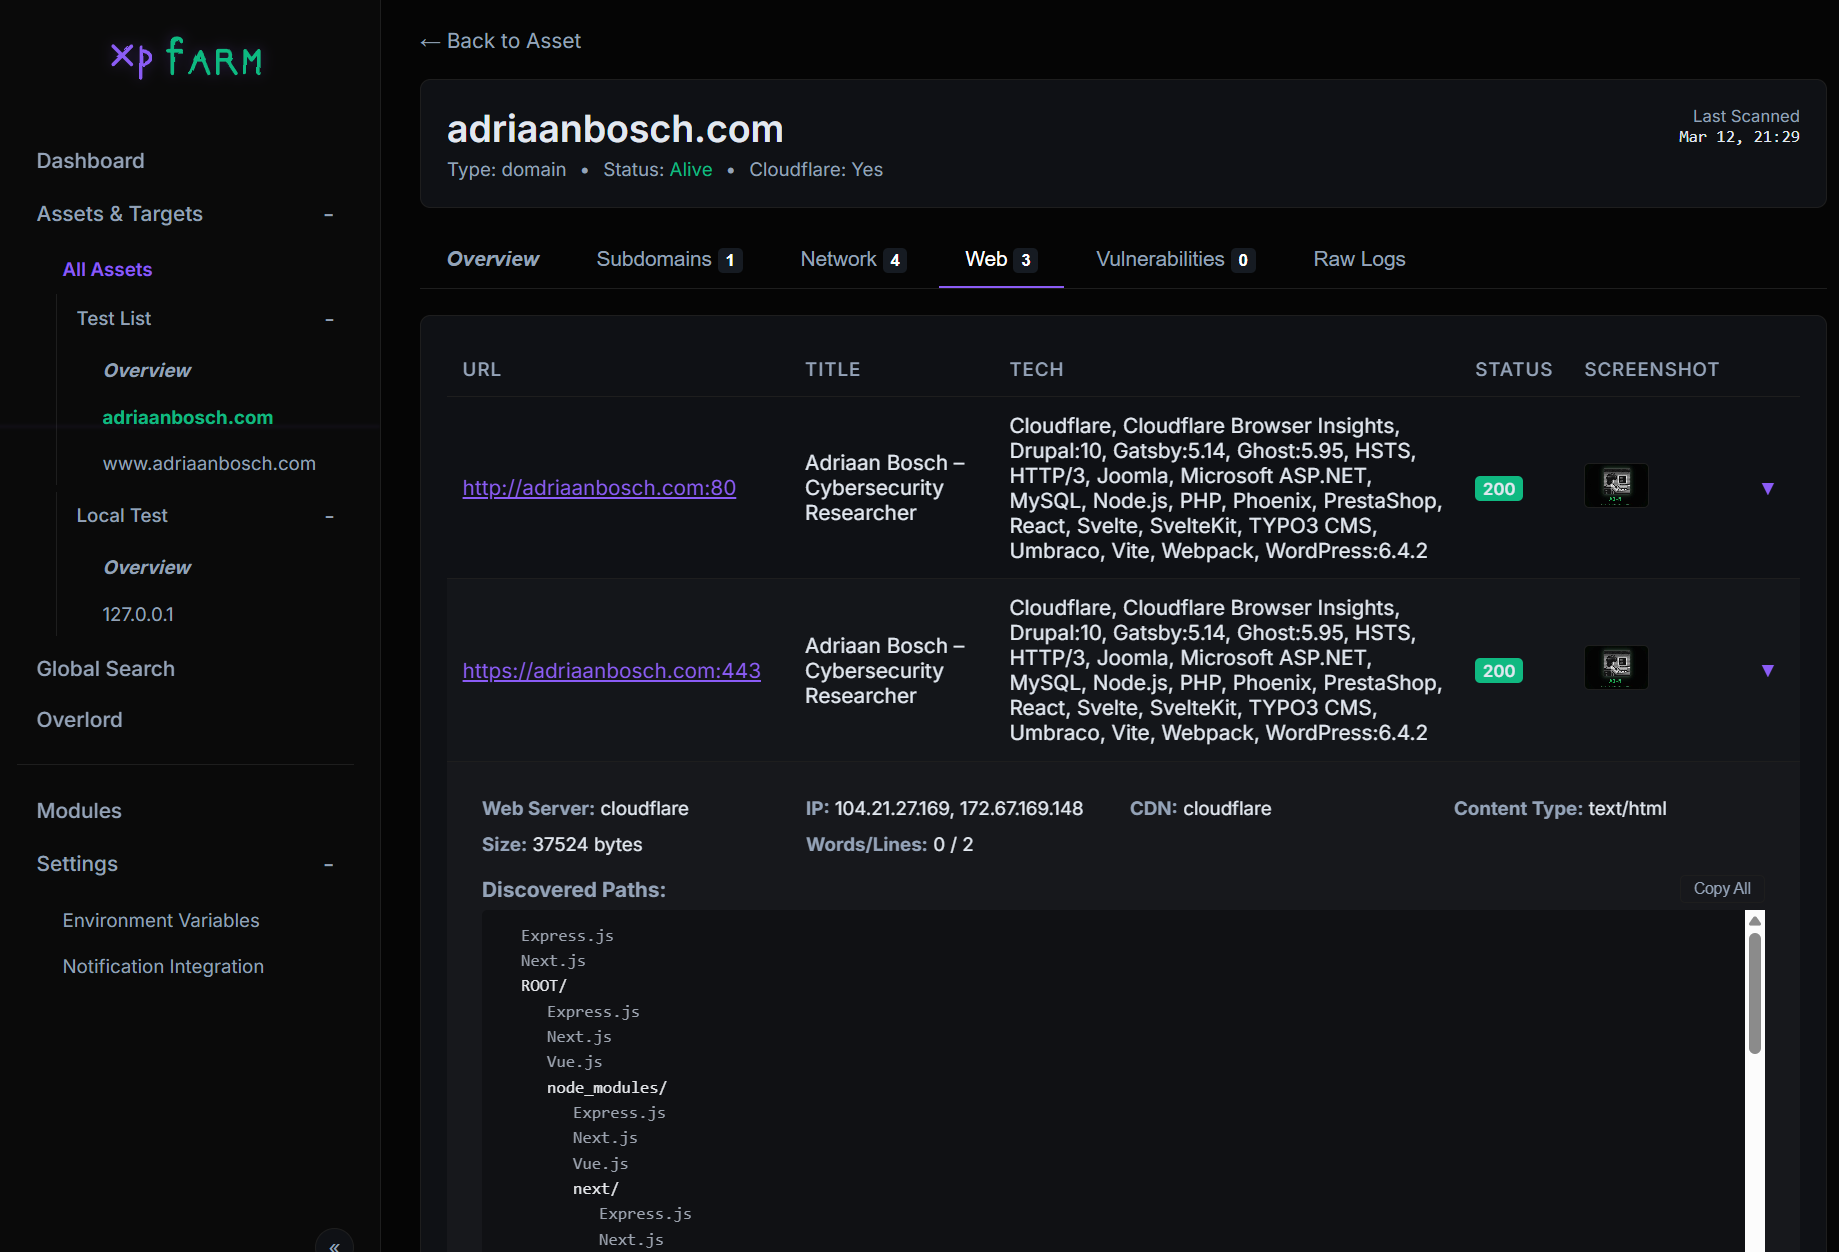 a3-n/xpfarm
Free XP on bug bounty, vulnerability scanning by wrapping well maintained tools, to perform automated tests. Alongside AI agents for binary analysis,…
 libriscv/libloong
The fastest LoongArch sandbox
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 redballoonsecurity/ofrak
Binary analysis and modification platform for unpacking, analyzing, modifying, and repacking firmware and executable formats via GUI and Python API.
 baiduxlab/sgxray
Automated reasoning tool based on the SMACK verifier that detects SGX enclave bugs from trusted boundary violations, including invalid pointer…
 0x0oz/cve-2026-7482-poc
Proof-of-concept exploit for CVE-2026-7482, an unauthenticated heap out-of-bounds read in Ollama's GGUF loader, demonstrating memory exfiltration via…
 kaleth4/cve-2026-55200
Technical analysis and proof-of-concept for CVE-2026-55200, a critical heap-based buffer overflow in libssh2 allowing pre-authentication RCE.…
 johanneslks/cve-2026-32945
PJSIP DNS Compression Pointer Heap OOB Read (Remote DoS)
 spiralbl0ck/learning-history-of-cff-bug-in-iphone
Dive into CFF font and coincidently learn about a bof in cff parsing from some jailbreak. just for fun
 pazhanivelmani/external_libcap-android10_r33_cve-2023-2603
POSIX.1e capability library for Android 10, addressing CVE-2023-2603 with tools for setting and getting process capabilities to manage privilege…
 trailofbits/manticore
Symbolic execution tool
 emproof-com/workshop_firmware_reverse_engineering
Workshop on firmware reverse engineering
 whatthefuzz/openssl-fuzz
Finding CVE-2022-3786 (openssl) with Mayhem
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…