
WDExtract
 hfiref0x/wdextract
Extract Windows Defender database from vdm files and unpack it
binary-analysisencryption-decryption-toolsforensics+2
hfiref0x/wdextractExtract Windows Defender database from vdm files and unpack it
 hackerschoice/bincrypter
Pack/Encrypt/Obfuscate ELF + SHELL scripts
 cerbersec/ares
Project Ares is a Proof of Concept (PoC) loader written in C/C++ based on the Transacted Hollowing technique
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
 x86byte/sbox
Compile-time AES string obfuscation for C++
 weedhashpeddler/rc4decryption
Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
 nccgroup/pip3line
The Swiss army knife of byte manipulation
 mhelwig/adwind-decryptor
Simple decrypter for Java AdWind, jRAT, jBifrost trojan
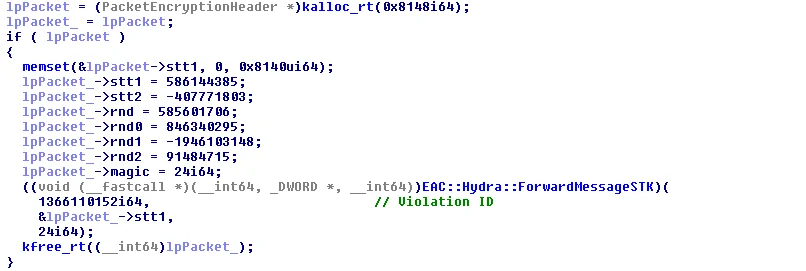 gmh5225/eac-kernel-packet-fucker
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…
 kvesel/zipbrk
Zip file format fuzzer and multi-tool.

 dump-guy/powershell-tools
Collection of some easy of use tools - in powershell.
 malwaretech/phasedump
Python tool for decrypting W32/Phase modules
 dodo-sec/kpot-string-decrypter
IDA python scripts to decrypt strings from KPOT and set those as comments
 claesmnyberg/sdc
Self Decrypting Binary Generator
 trinadh465/openssl-1_0_1g_cve-2015-3195
OpenSSL toolkit implementing SSL/TLS protocols and a general-purpose cryptography library with ciphers, digests, public key algorithms, and X.509…