
bread
 theldus/bread
Injectable real-mode x86 debugger for BIOS reverse engineering and arbitrary real-mode code debugging via serial cable, with GDB integration and…
binary-analysisdebuggersfirmware-analysis+2
326
theldus/breadInjectable real-mode x86 debugger for BIOS reverse engineering and arbitrary real-mode code debugging via serial cable, with GDB integration and…
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
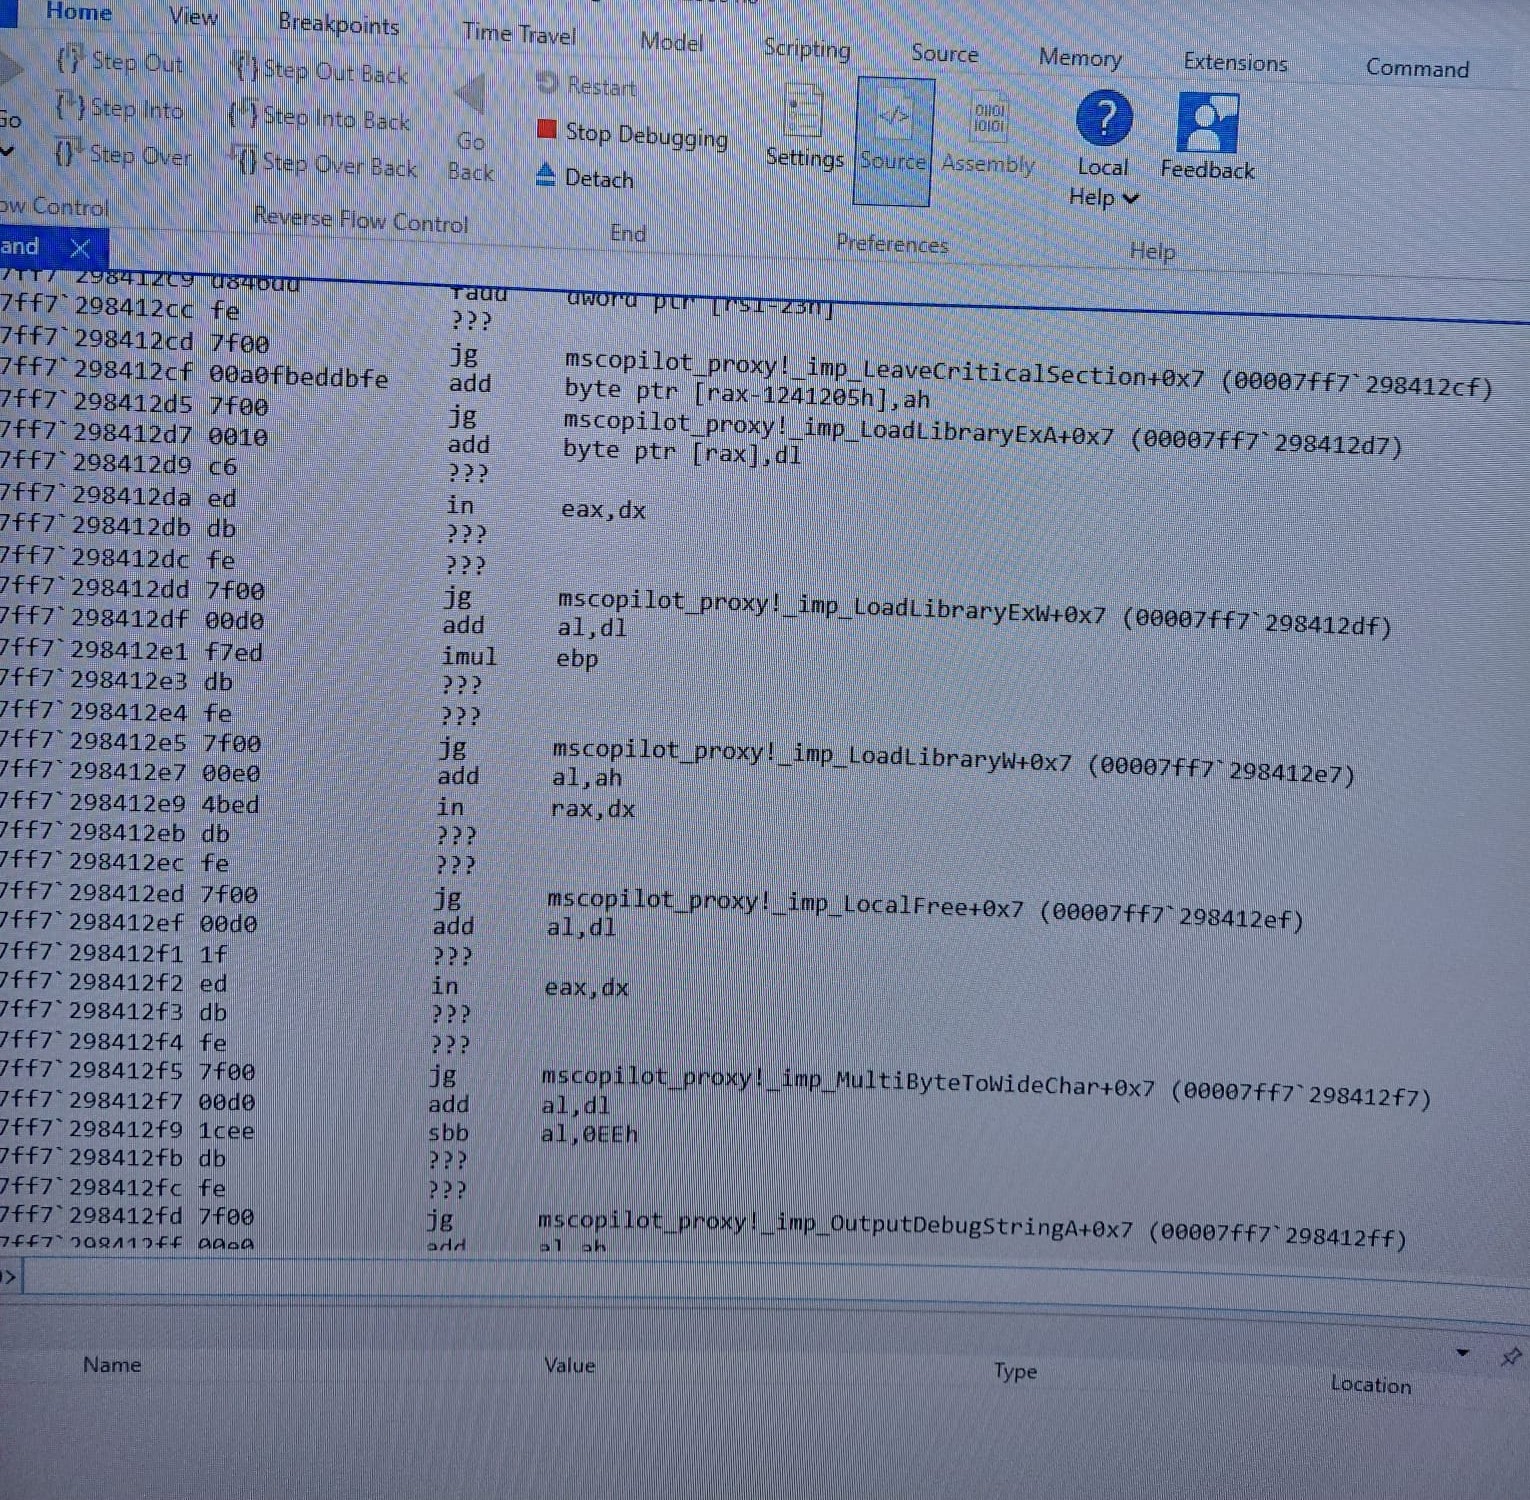 kaandemir993/vidar-stealer-reverse-engineering
"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…