
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
131 results
CobaltStrikeParser preview

CobaltStrikeParser

GitHubsentinel-one/cobaltstrikeparser

Python parser for extracting CobaltStrike Beacon configurations from PE files, memory dumps, and C2 URLs using heuristic XOR decryption and…
binary-analysiscommand-and-controlmalware-analysis+1
1.1k
3 years ago
Process-Dump preview

Process-Dump

GitHubglmcdona/process-dump

Windows tool for dumping malware PE files from memory back to disk for analysis.

binary-analysisforensicsmalware-analysis+2
1.9k3 years ago
Shoggoth preview

Shoggoth

GitHubfrkngksl/shoggoth

Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…

binary-analysisexploit-frameworkspayload-generation+2
8105 months ago
uefi-firmware-parser preview

uefi-firmware-parser

GitHubtheopolis/uefi-firmware-parser

Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
binary-analysisembedded-systems-securityfirmware-analysis+2
9253 months ago
netzob preview

netzob

GitHubnetzob/netzob

Open-source toolkit for reverse engineering, modeling, and fuzzing communication protocols. Infers message formats and state machines from network…
binary-analysisfuzzingnetwork-security+1
8363 years ago
Android-Disassembler preview

Android-Disassembler

GitHubyhs0602/android-disassembler

Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
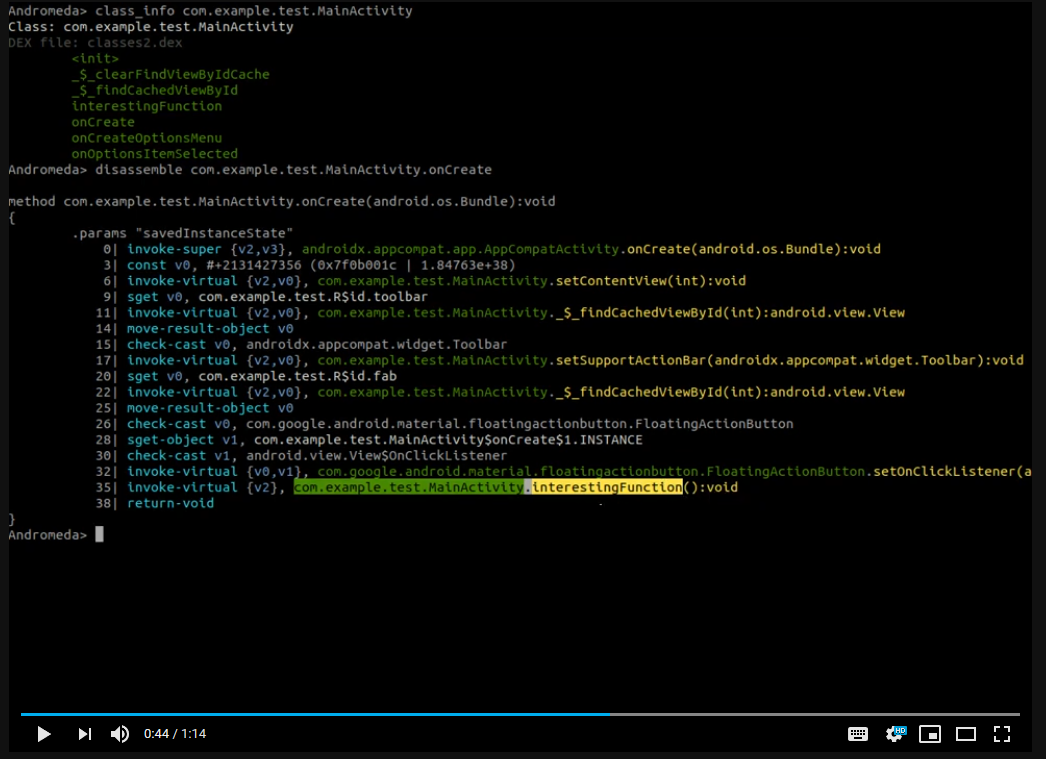
android-securitybinary-analysisdebuggers+4
7146 months ago
Andromeda preview

Andromeda

GitHubsecrary/andromeda

C/C++ interactive reverse engineering tool for Android applications, enabling fast static analysis and binary inspection of APK files.
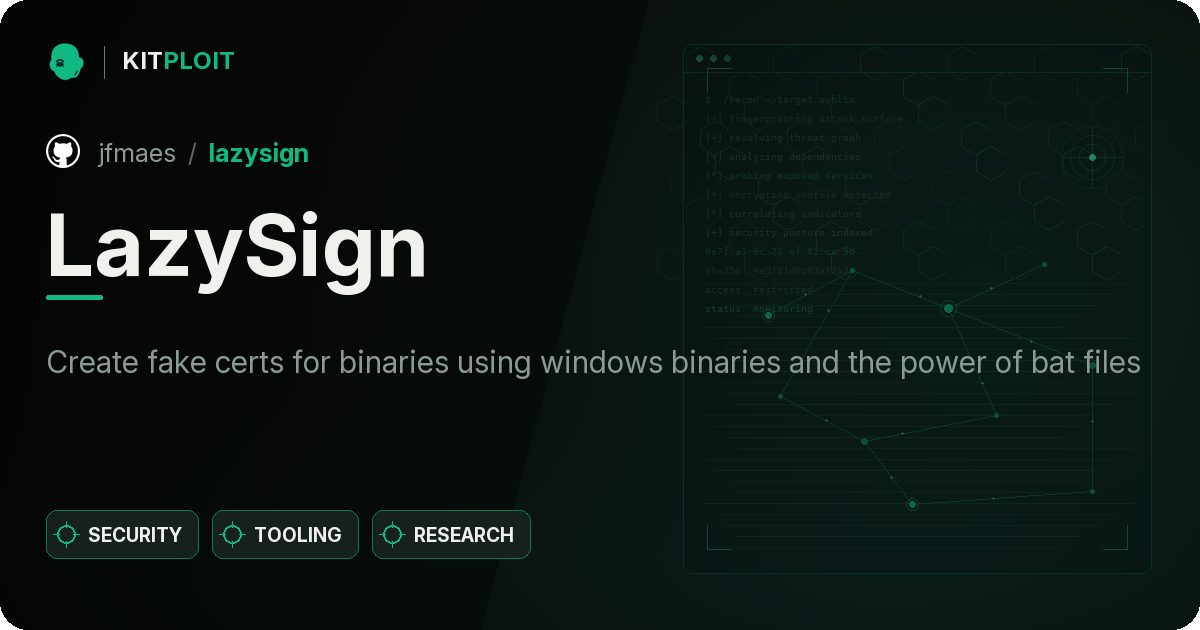
android-securitybinary-analysisreverse-engineering+1
7136 years ago
LazySign preview

LazySign

GitHubjfmaes/lazysign

Create fake certs for binaries using windows binaries and the power of bat files
binary-analysisdefensive-toolsimpersonation-tools+6
5692 years ago
PortEx preview

PortEx

GitHubstruppigel/portex

Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
anomaly-detectionbinary-analysisforensics+3
5385 months ago
View8 preview

View8

GitHubsuleram/view8

Decompiles serialized V8 bytecode (JSC files) into high-level readable JavaScript-like code, with support for multiple V8 versions, tree output, and…
binary-analysismalware-analysisreverse-engineering+2
3761 month ago
WDExtract preview

WDExtract

GitHubhfiref0x/wdextract

Extract Windows Defender database from vdm files and unpack it

binary-analysisencryption-decryption-toolsforensics+2
4945 months ago
Windows-PE-Packer preview

Windows-PE-Packer

GitHubczs108/windows-pe-packer

🗜️ A packer for Windows x86 executable files written in C and Intel x86 Assembly. The new file after packing can obstruct reverse…
binary-analysisexploitationpayload-generation+1
3671 year ago
msidump preview

msidump

GitHubmgeeky/msidump

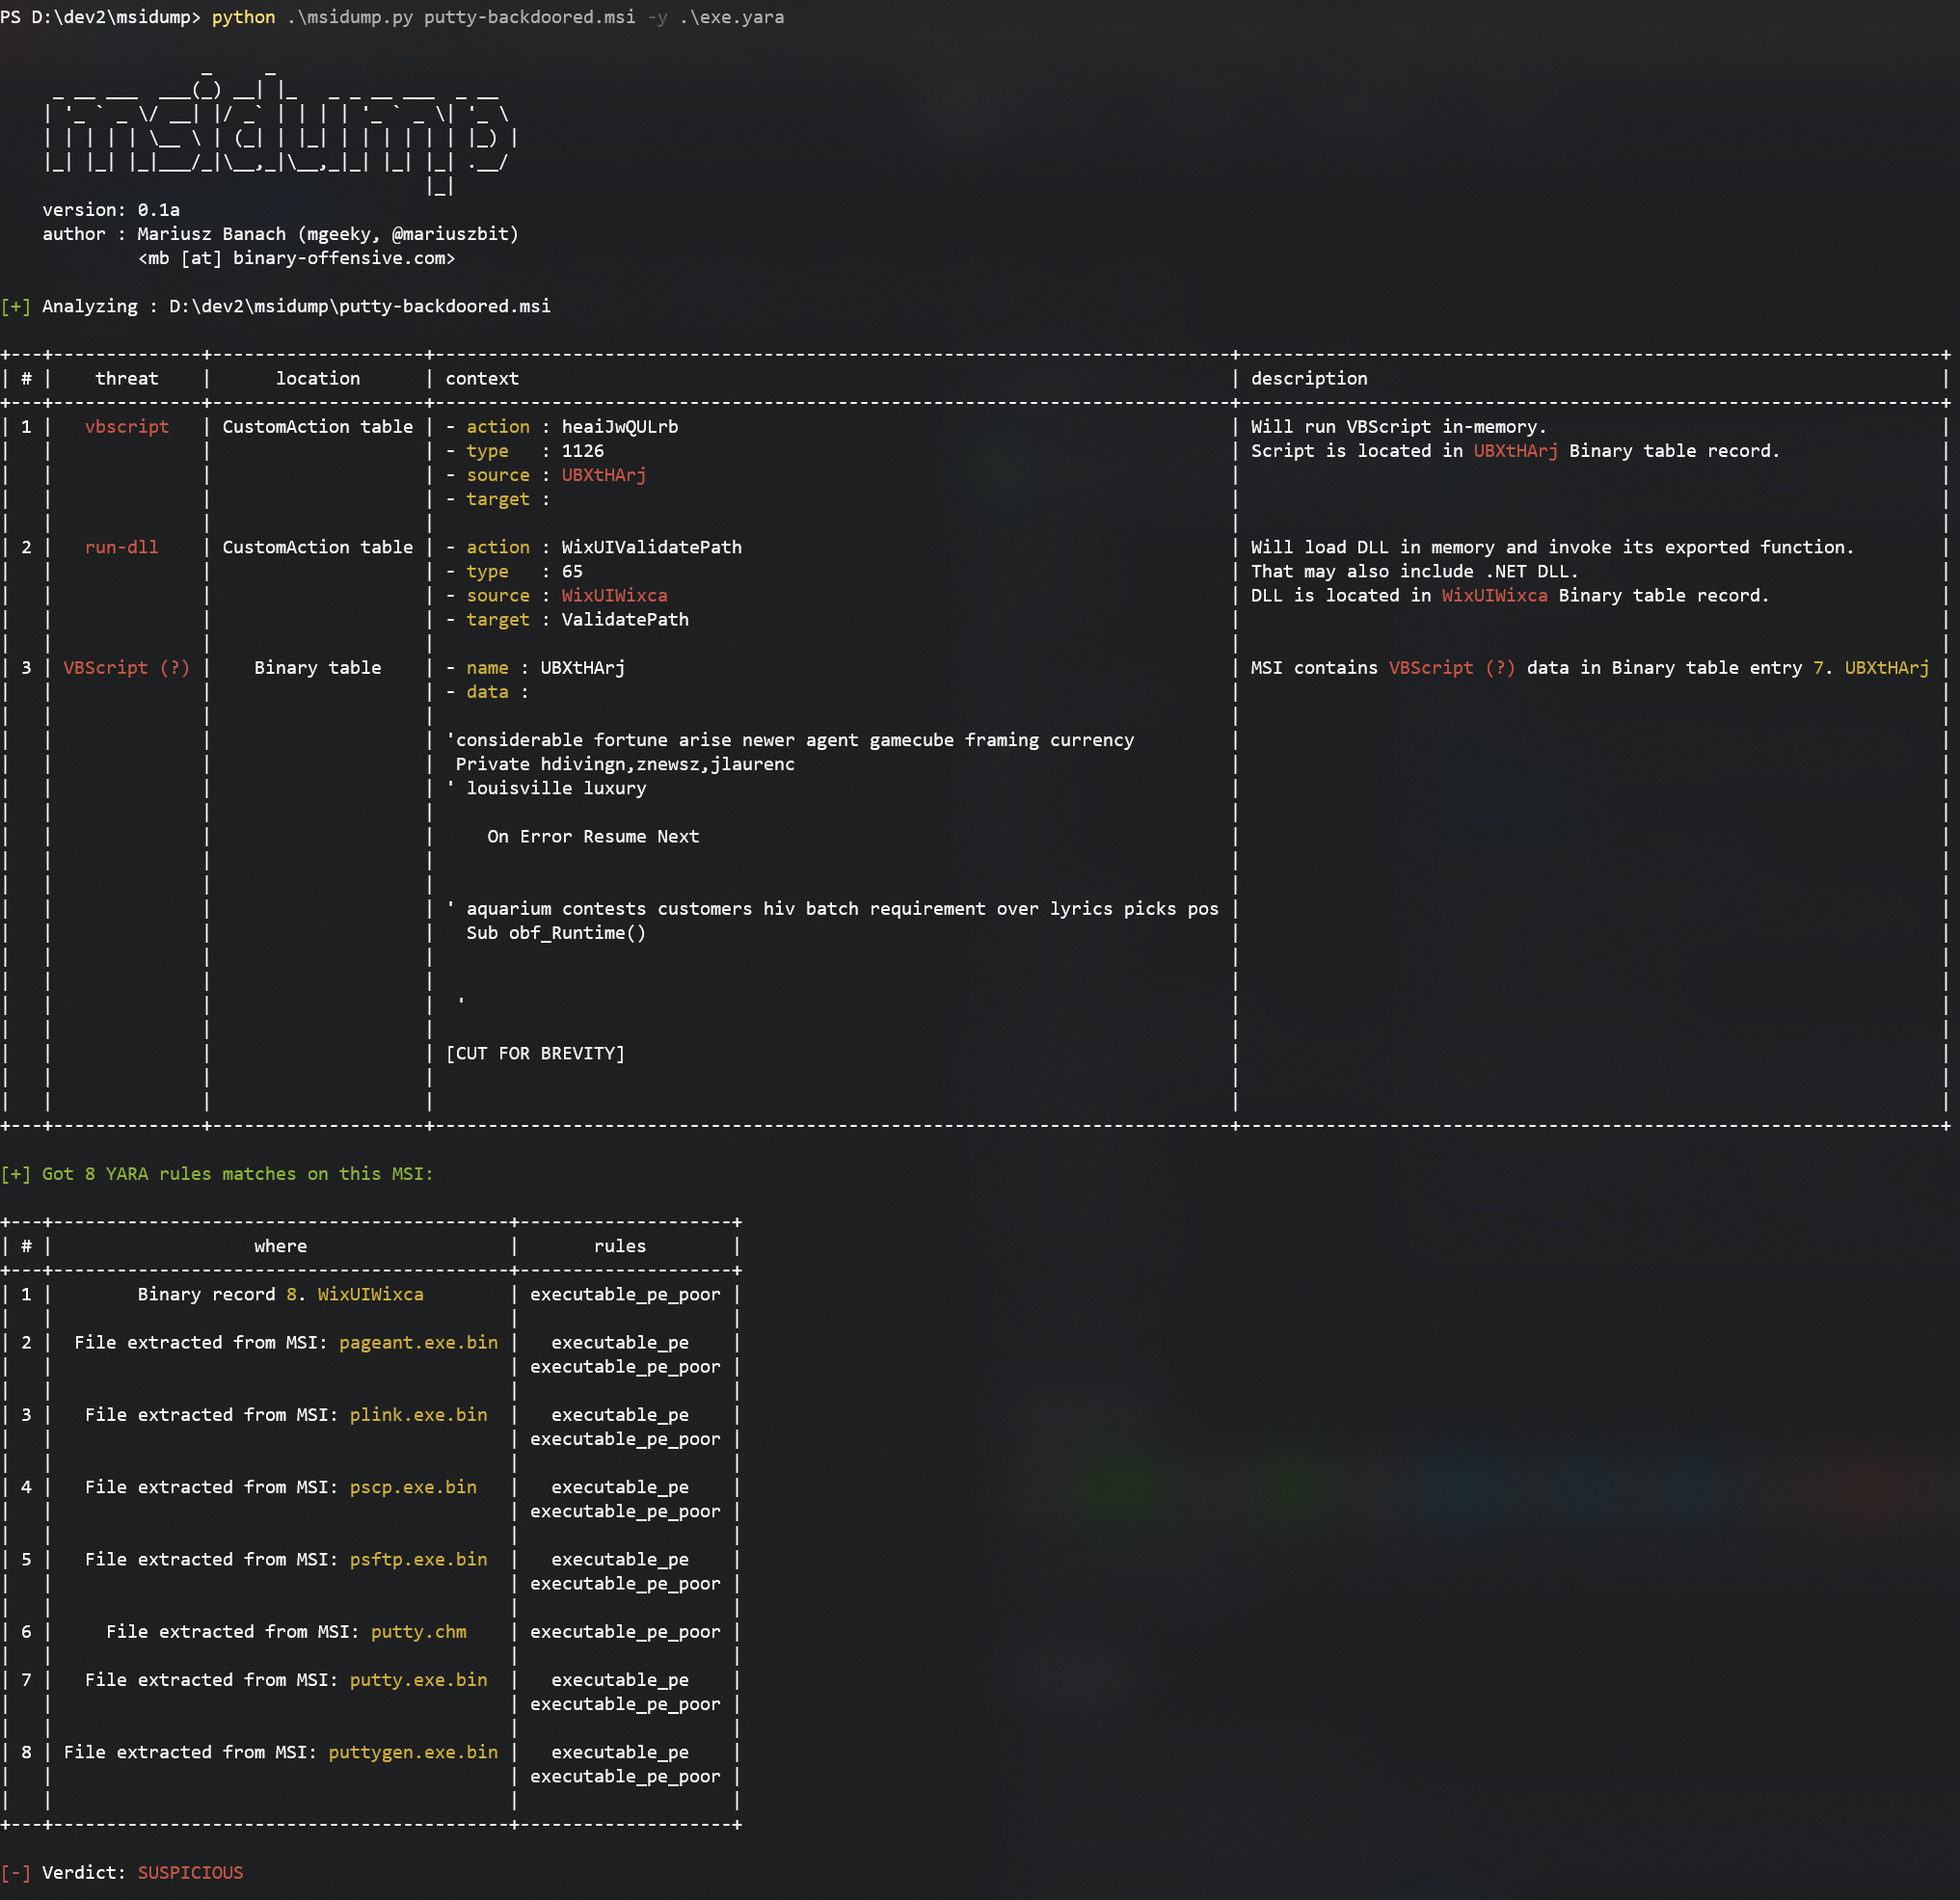
MSI Dump - a tool that analyzes malicious MSI installation packages, extracts files, streams, binary data and incorporates YARA scanner.
binary-analysisforensicsmalware-analysis+1
2323 years ago
nuitka-static-unpacker preview

nuitka-static-unpacker

GitHubdimareverse/nuitka-static-unpacker

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
binary-analysisdata-recoveryforensics+3
1321 month ago
pyxamstore preview

pyxamstore

GitHubjakev/pyxamstore

Python utility for parsing Xamarin AssemblyStore blob files

android-securitybinary-analysismobile-security+1
2023 years ago
hermes-decomp preview

hermes-decomp

GitHubsymbioticsec/hermes-decomp

A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…

ai-assisted-reversingandroid-securitybinary-analysis+8
17612 days ago
sandfly-entropyscan preview

sandfly-entropyscan

GitHubsandflysecurity/sandfly-entropyscan

Entropy scanner for Linux to detect packed or encrypted binaries related to malware. Finds malicious files and Linux processes and gives output with…
binary-analysisforensicsincident-response+1
1702 years ago
DotDumper preview

DotDumper

GitHubadvanced-threat-research/dotdumper

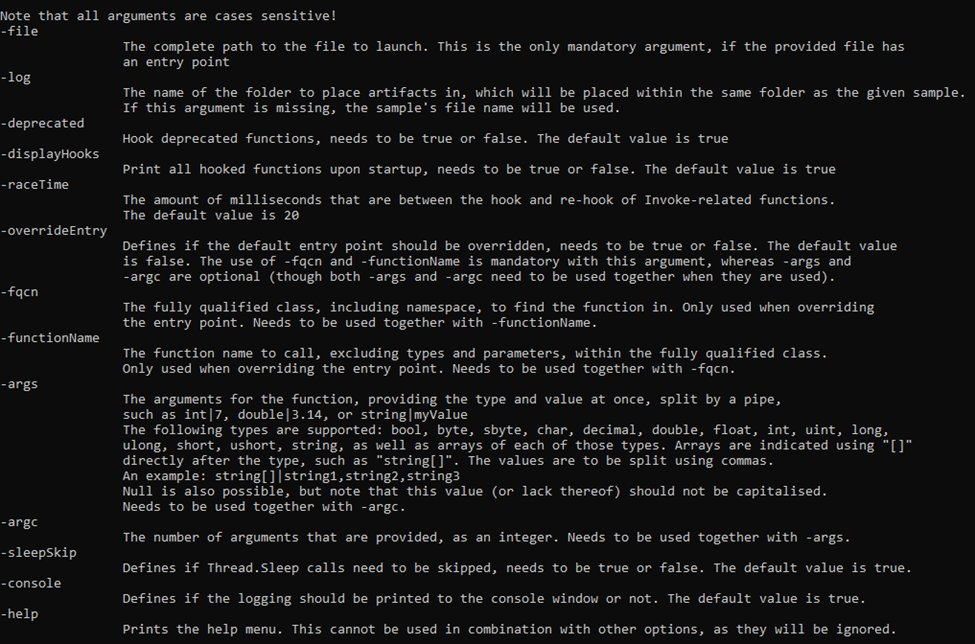
An automatic unpacker and logger for DotNet Framework targeting files

binary-analysisdebuggersdynamic-analysis-sandboxing+4
2643 years ago
Previous123…8Next