
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
65 results
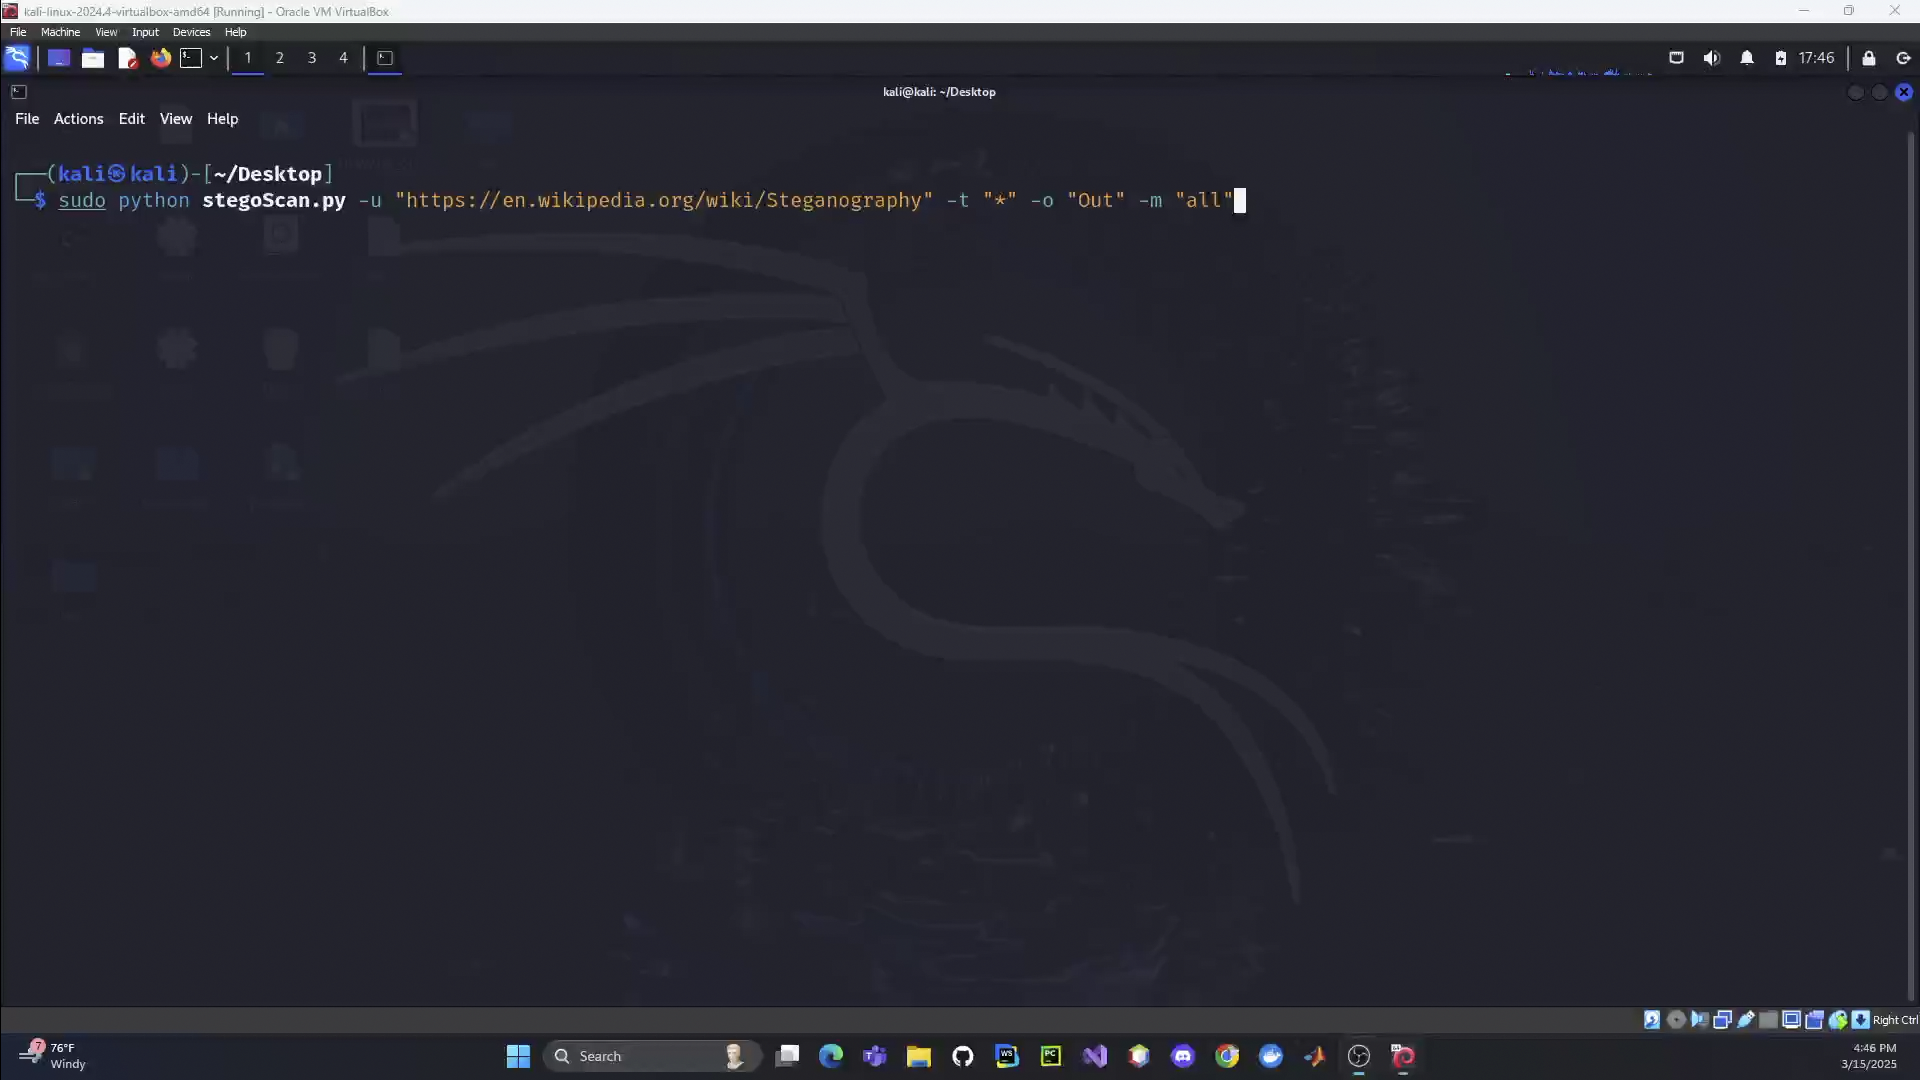
StegoScan preview

StegoScan

GitHublcbower33/stegoscan

Automated steganography detection tool that scans websites, web servers, and local directories using AI-driven object/text recognition and deep file…
ai-securitybinary-analysiscrawler+7
109
1 year ago
Freeloader preview

Freeloader

GitHubauthrequest/freeloader

Plex Unlocker

binary-analysiscontainer-securitydebuggers+8
983 months ago
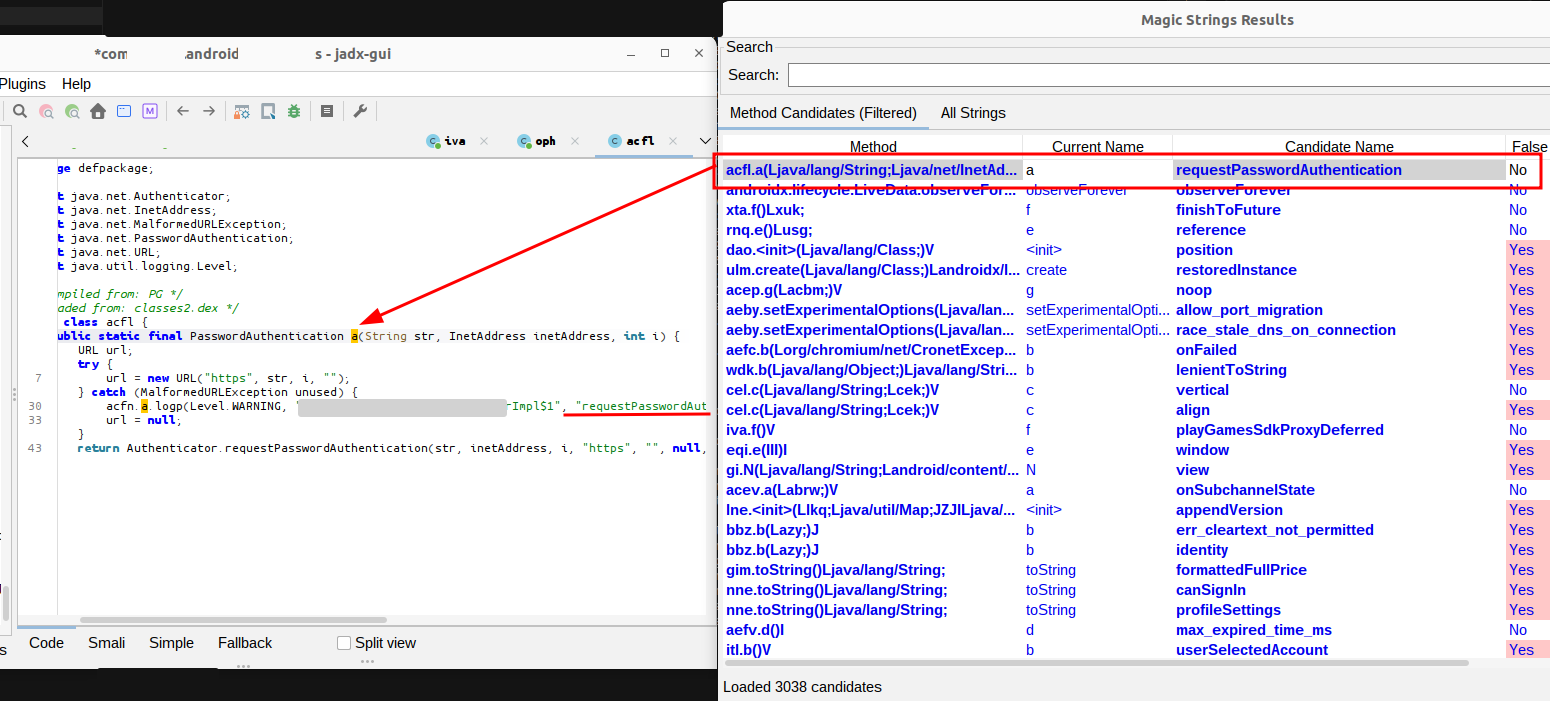
jadx-magic-strings preview

jadx-magic-strings

GitHub0rshemesh/jadx-magic-strings

JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
android-securitybinary-analysiscode-analysis+5
4522 days ago
dexfinder preview

dexfinder

GitHubjunelegency/dexfinder

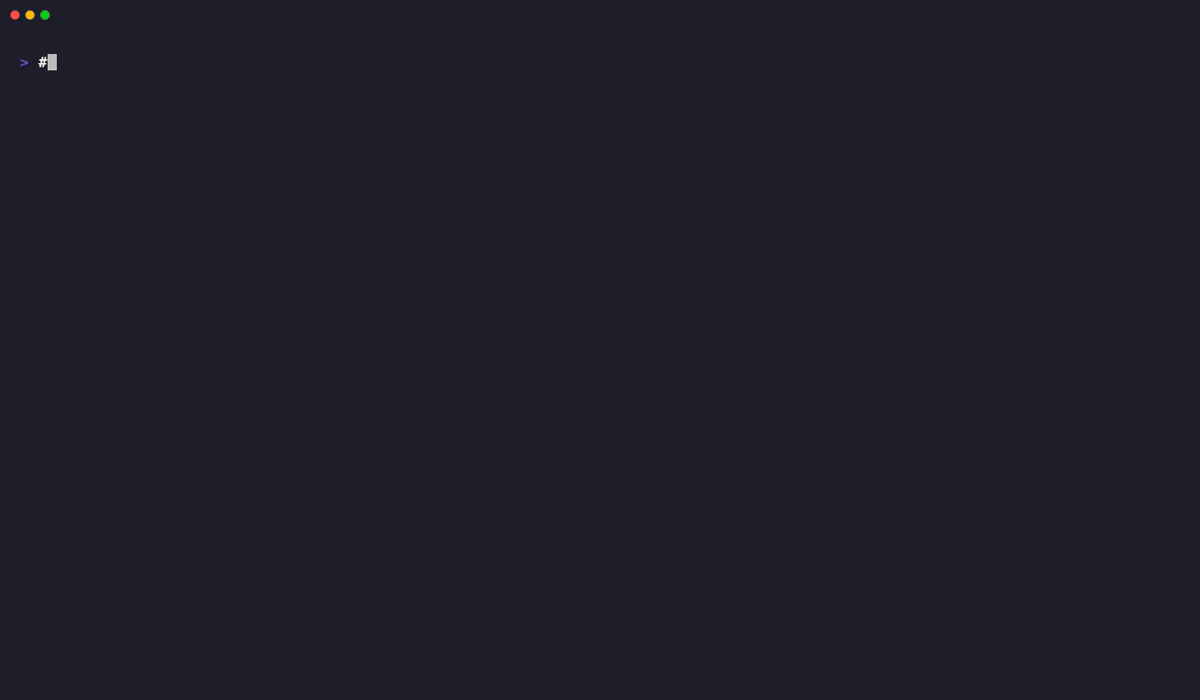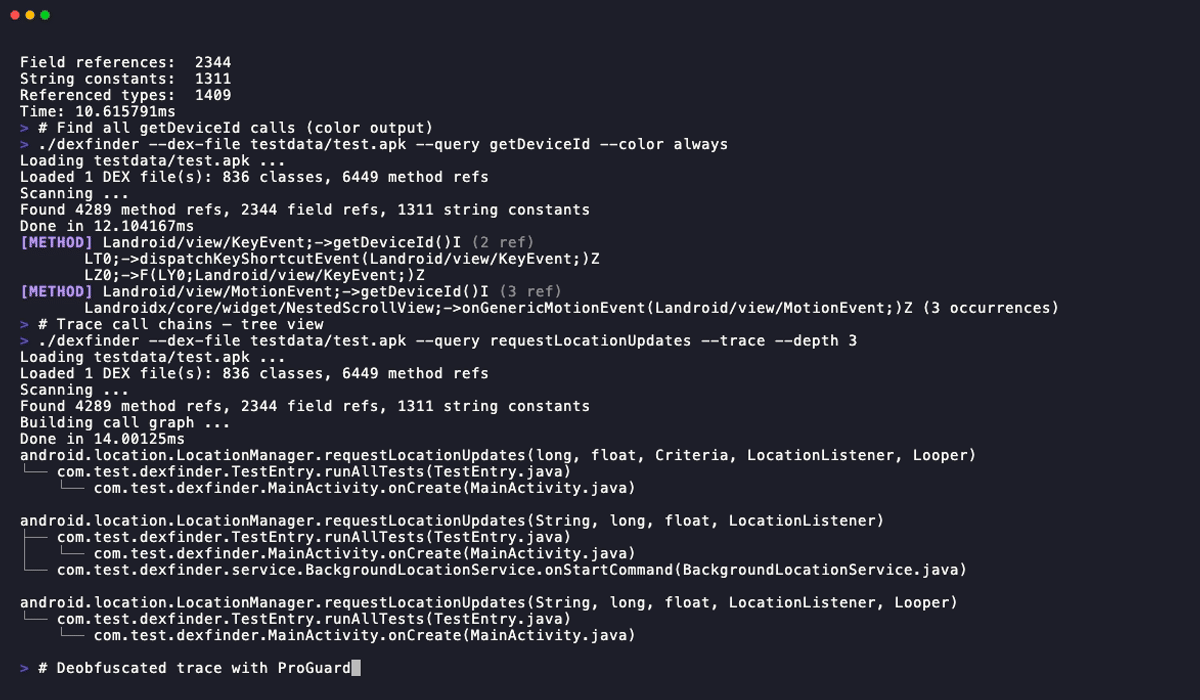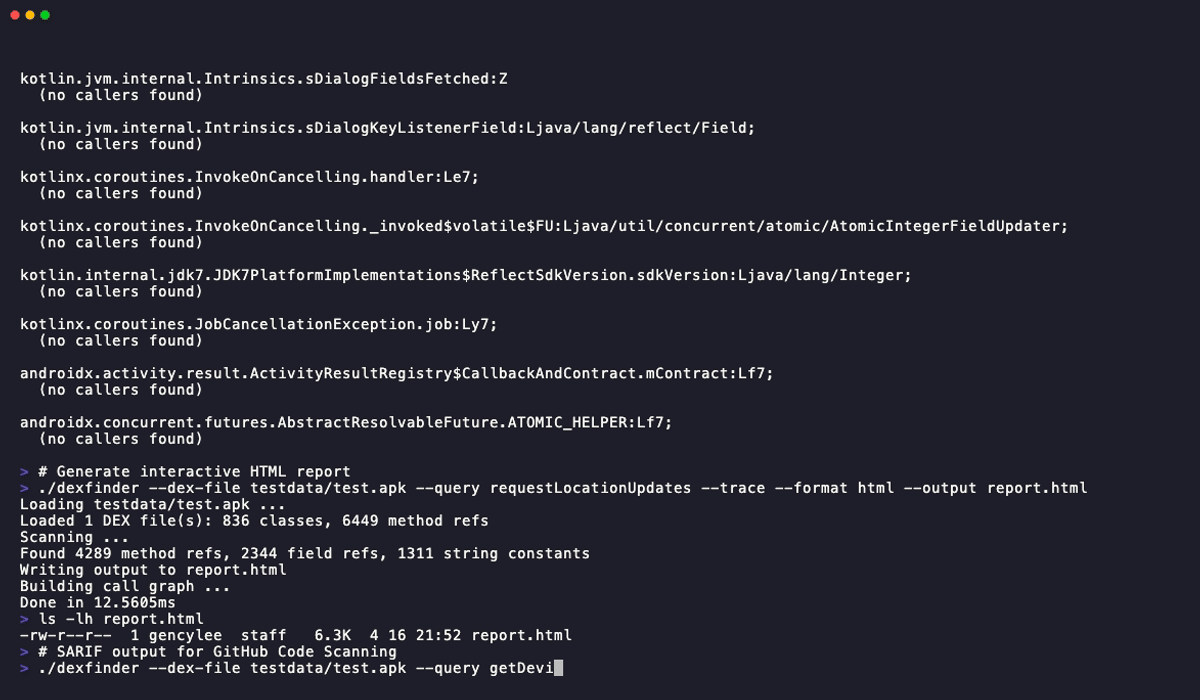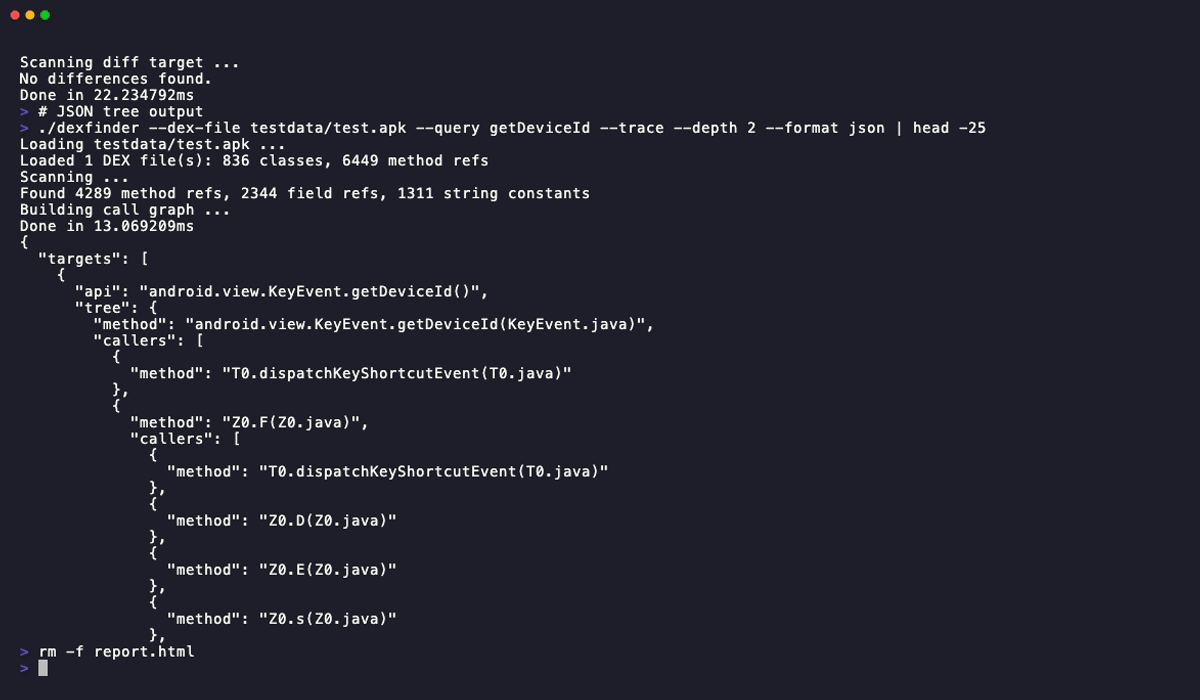
Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection
android-securitybinary-analysiscode-analysis+6
1065 months ago
goLoL preview

goLoL

GitHubaaron-kidwell/golol

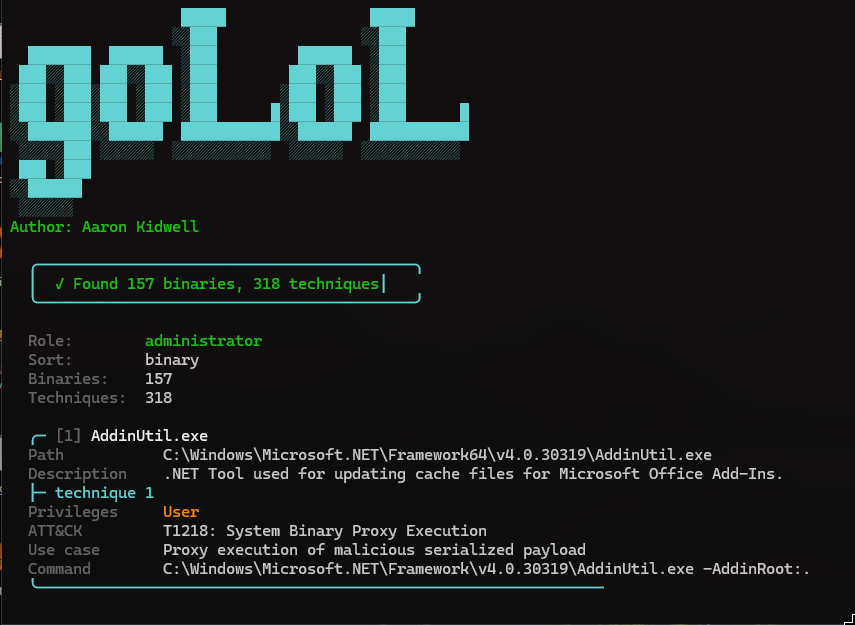
goLoL is a Windows host scanner with dual support for LOLBAS binaries and LOLDrivers. It lists LOLBAS techniques runnable at your current privilege…

binary-analysiseducationinformation-gathering+6
703 months ago
dezlock-dump preview

dezlock-dump

GitHubdougwithseismic/dezlock-dump

Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
binary-analysisdebuggersdynamic-code-analysis+6
946 months ago
lifer preview

lifer

GitHubpaul-tew/lifer

Windows link file (shortcuts) examiner
binary-analysisdigital-forensicsforensics+1
682 years ago
CVE-2026-50416-writeup-and-poc preview

CVE-2026-50416-writeup-and-poc

GitHubkarollooool/cve-2026-50416-writeup-and-poc

CVE-2026-50416: Windows 11 KASLR bypass
binary-analysisctfeducation+7
471 month ago
xpfarm preview

xpfarm

GitHuba3-n/xpfarm

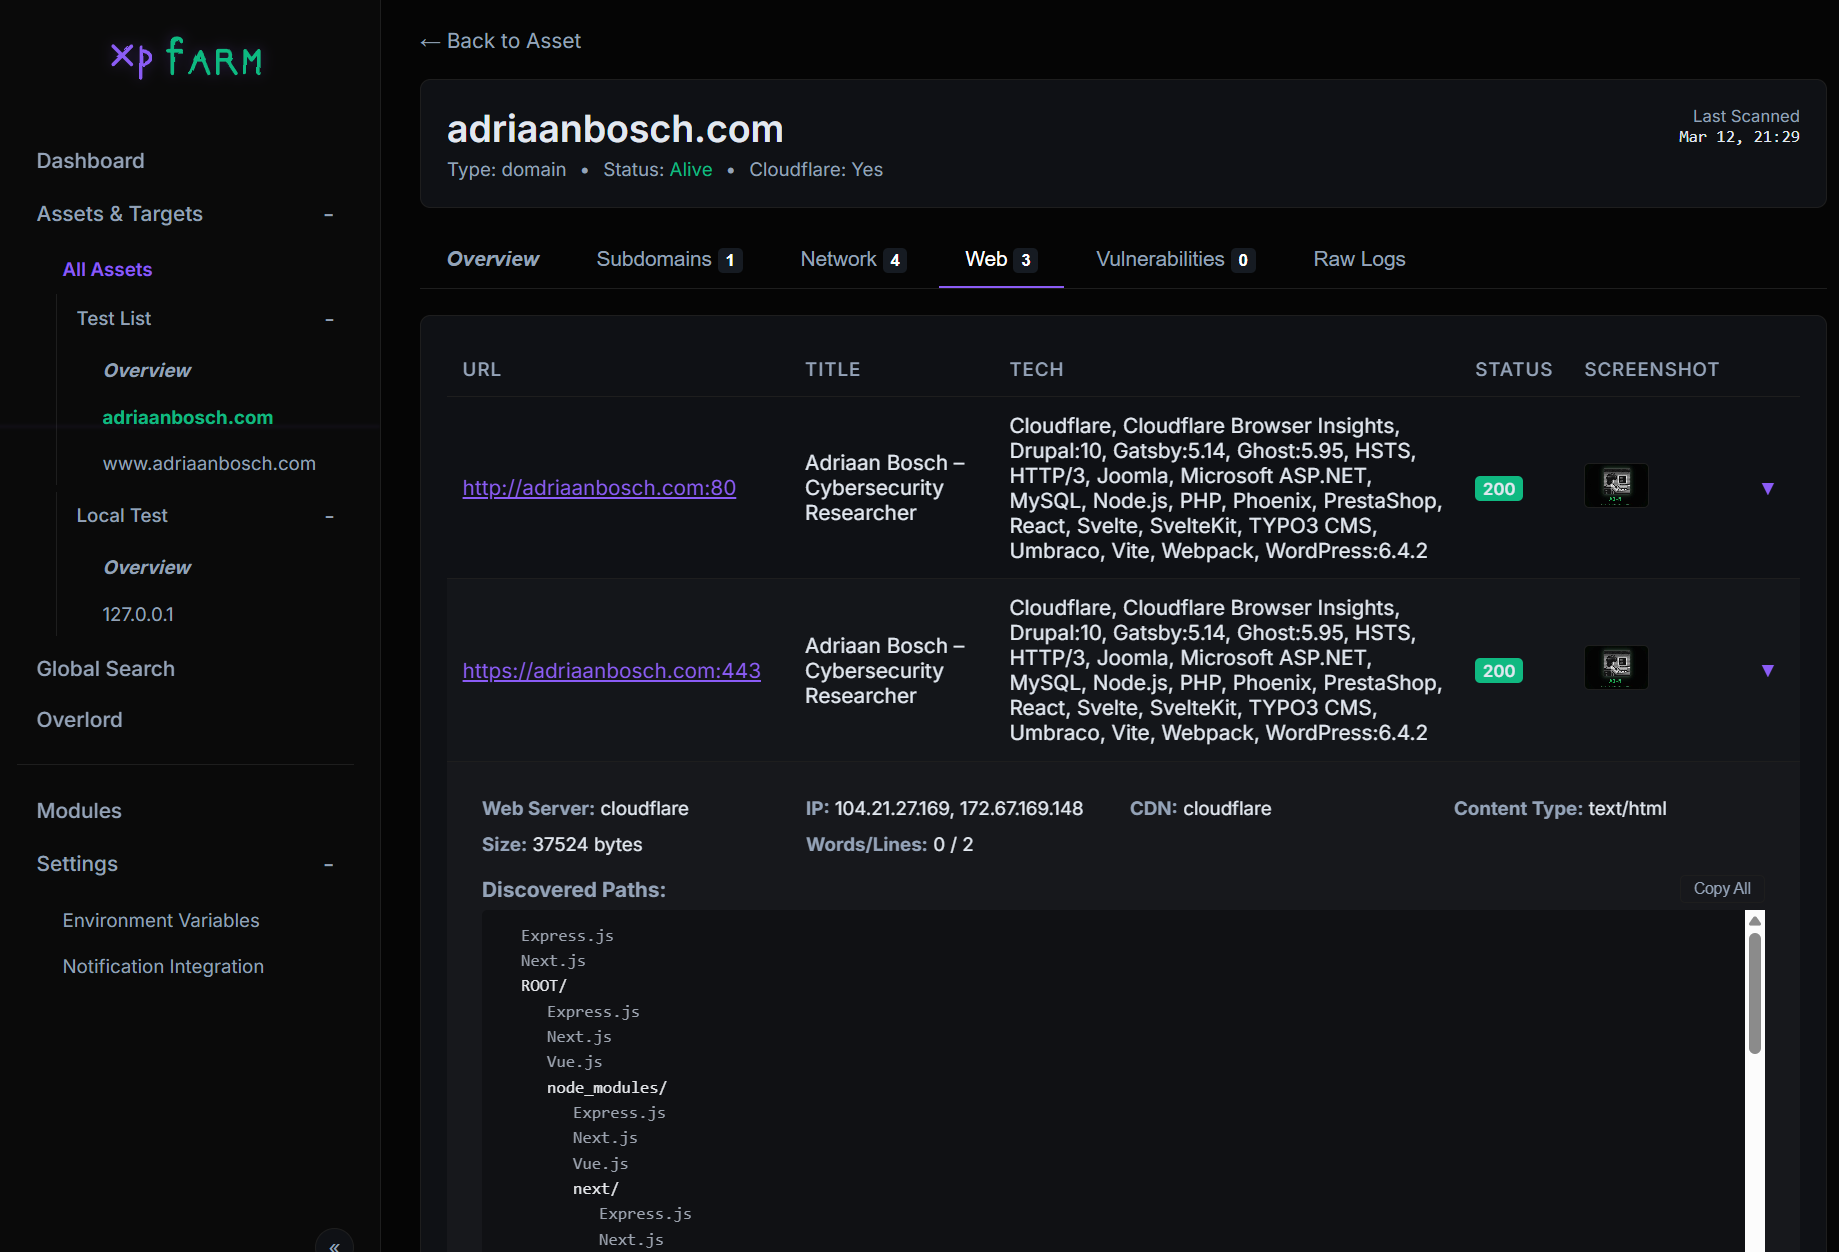
Free XP on bug bounty, vulnerability scanning by wrapping well maintained tools, to perform automated tests. Alongside AI agents for binary analysis,…

ai-securitybinary-analysiseducation+6
445 months ago
ODIS-project-explorer preview

ODIS-project-explorer

GitHubkartoffelpflanze/odis-project-explorer

Python dumper/explorer for MCD Runtime Projects used by ODIS

binary-analysisdebuggersembedded-systems-security+4
401 year ago
CVE-2019-8540 preview

CVE-2019-8540

GitHubmaldiohead/cve-2019-8540

Kernel Stack info leak at exportObjectToClient function

binary-analysisexploitationinformation-gathering+2
407 years ago
magic-extractor preview

magic-extractor

GitHubxchwarze/magic-extractor

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.


binary-analysisdata-recoverydigital-forensics+8
431 month ago
memgrep preview

memgrep

GitHubnccgroup/memgrep

Memory searching utilities

binary-analysisdigital-forensicsforensics+3
4412 years ago
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis preview

PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

GitHubkaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
binary-analysiscommand-and-controldefensive-tools+6
1610 days ago
Anvil preview

Anvil

GitHubshellkraft/anvil

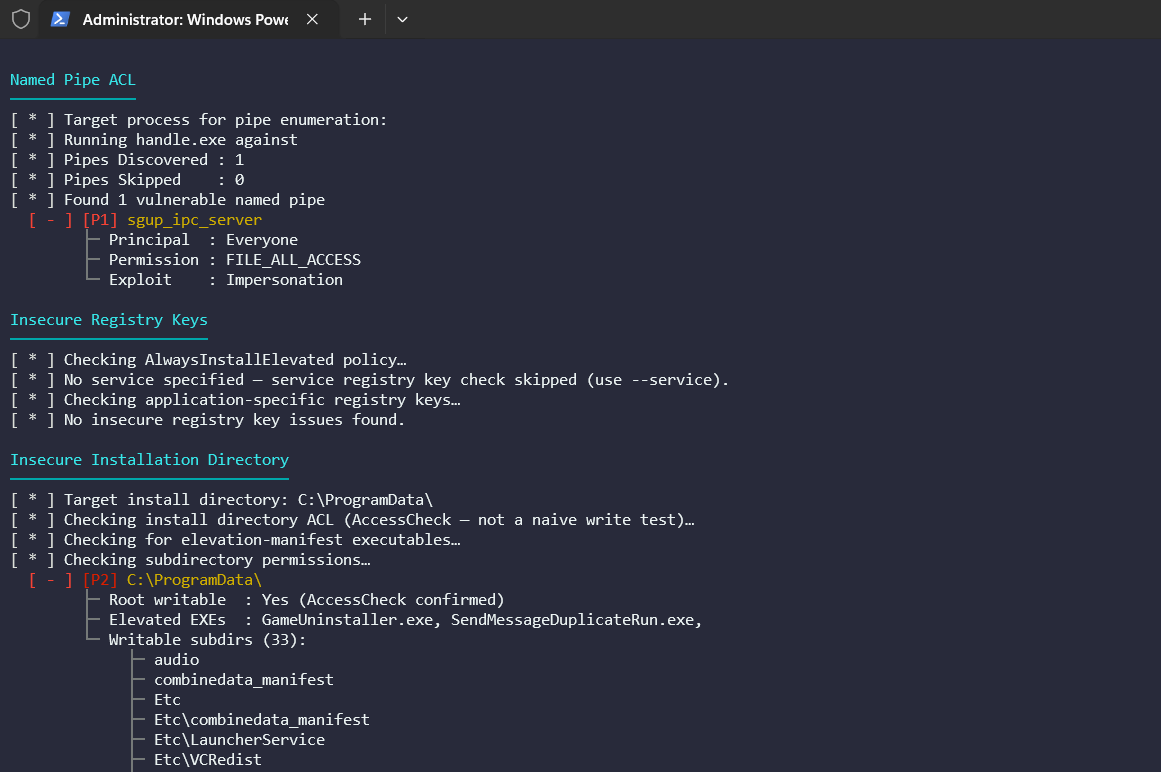
Anvil is a runtime-first attack surface assessment tool for Windows thick client applications, built for penetration testers and security researchers…
binary-analysisexploitationpenetration-testing+5
386 months ago
CVE-2021-1656 preview

CVE-2021-1656

GitHubwaleedassar/cve-2021-1656

Proof-of-concept exploit for CVE-2021-1656, an information disclosure vulnerability in the Windows TPM driver (tpm.sys). Demonstrates kernel memory…
binary-analysisexploitationinformation-gathering+1
225 years ago
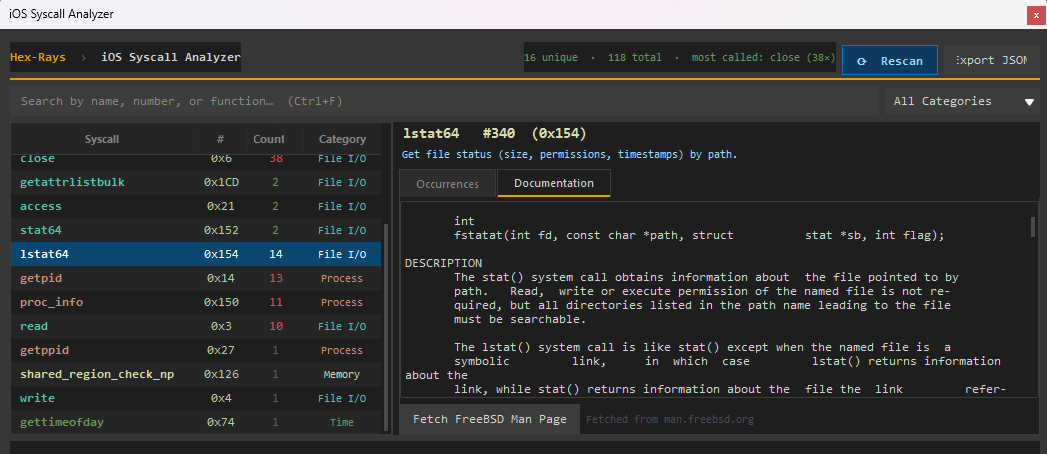
sylvia preview

sylvia

GitHubstolevchristian/sylvia

iOS Syscall Explorer for IDA 9.X
binary-analysisdebuggersinformation-gathering+5
154 months ago
intel-me-research preview

intel-me-research

GitHubjatinkapilaq1/intel-me-research

Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…

binary-analysisembedded-systems-securityfirmware-analysis+4
152 months ago
Previous1234Next