
intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…

Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…

Program for determining types of files for Windows, Linux and MacOS.

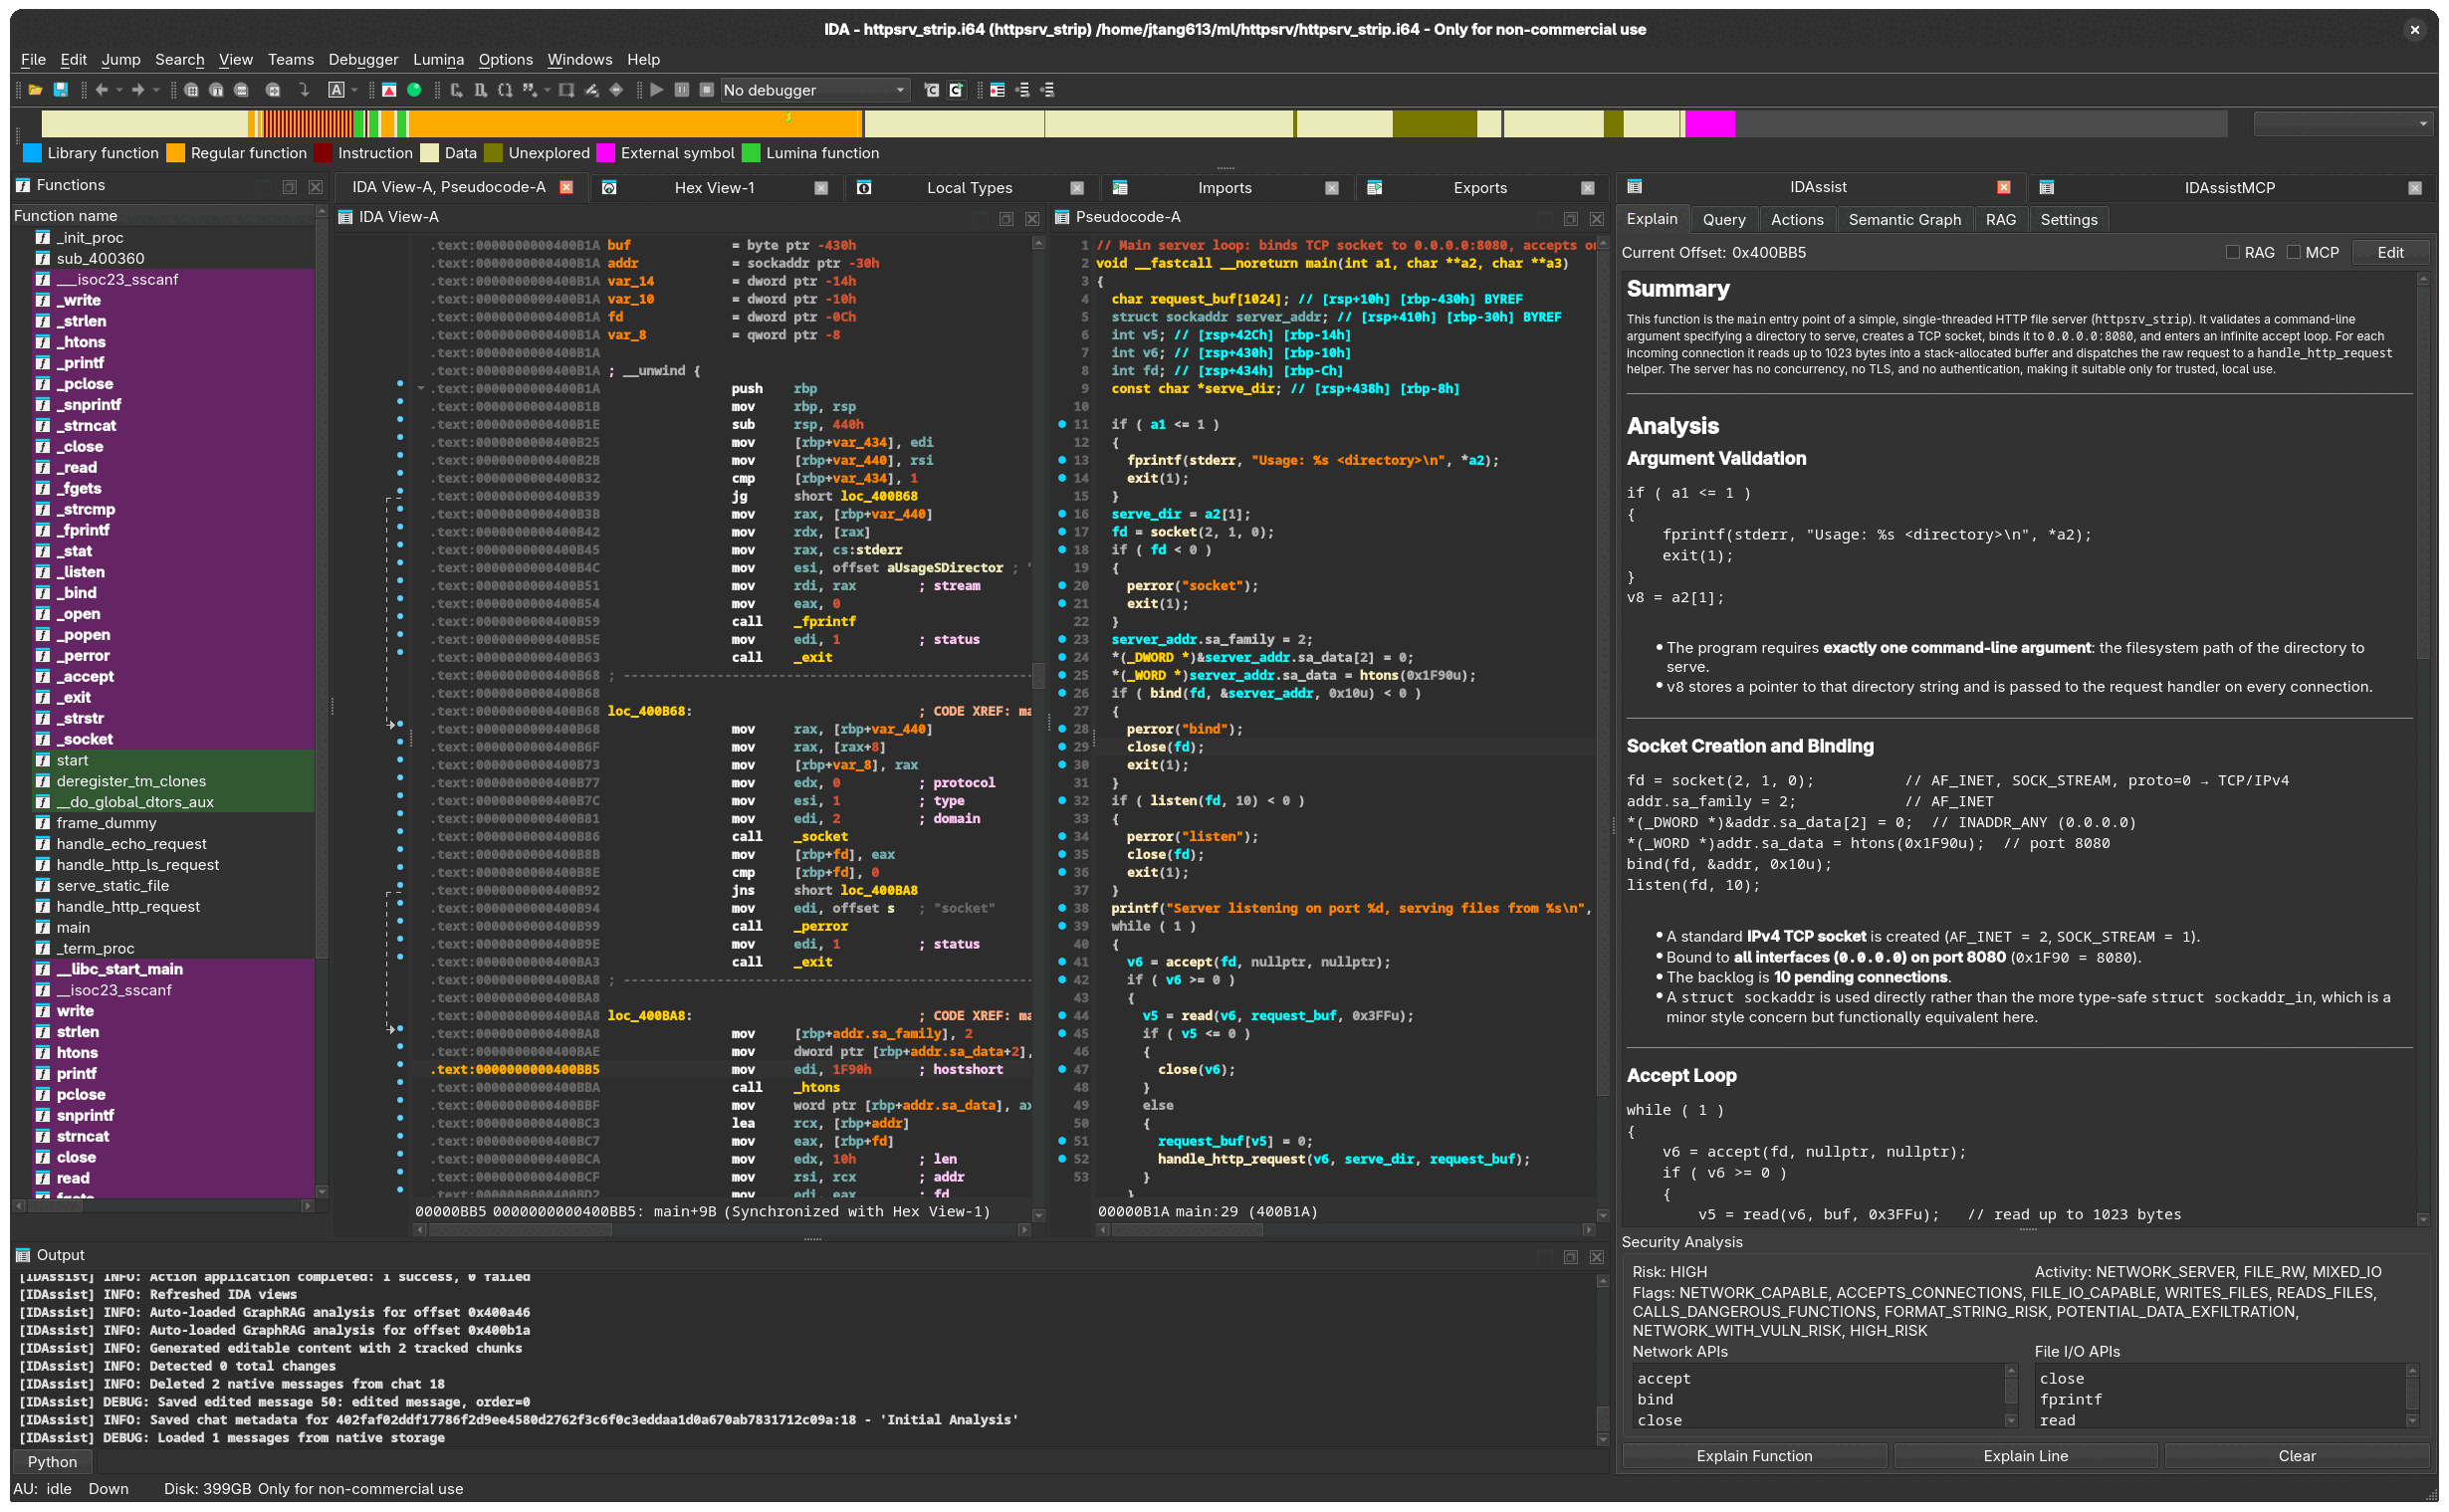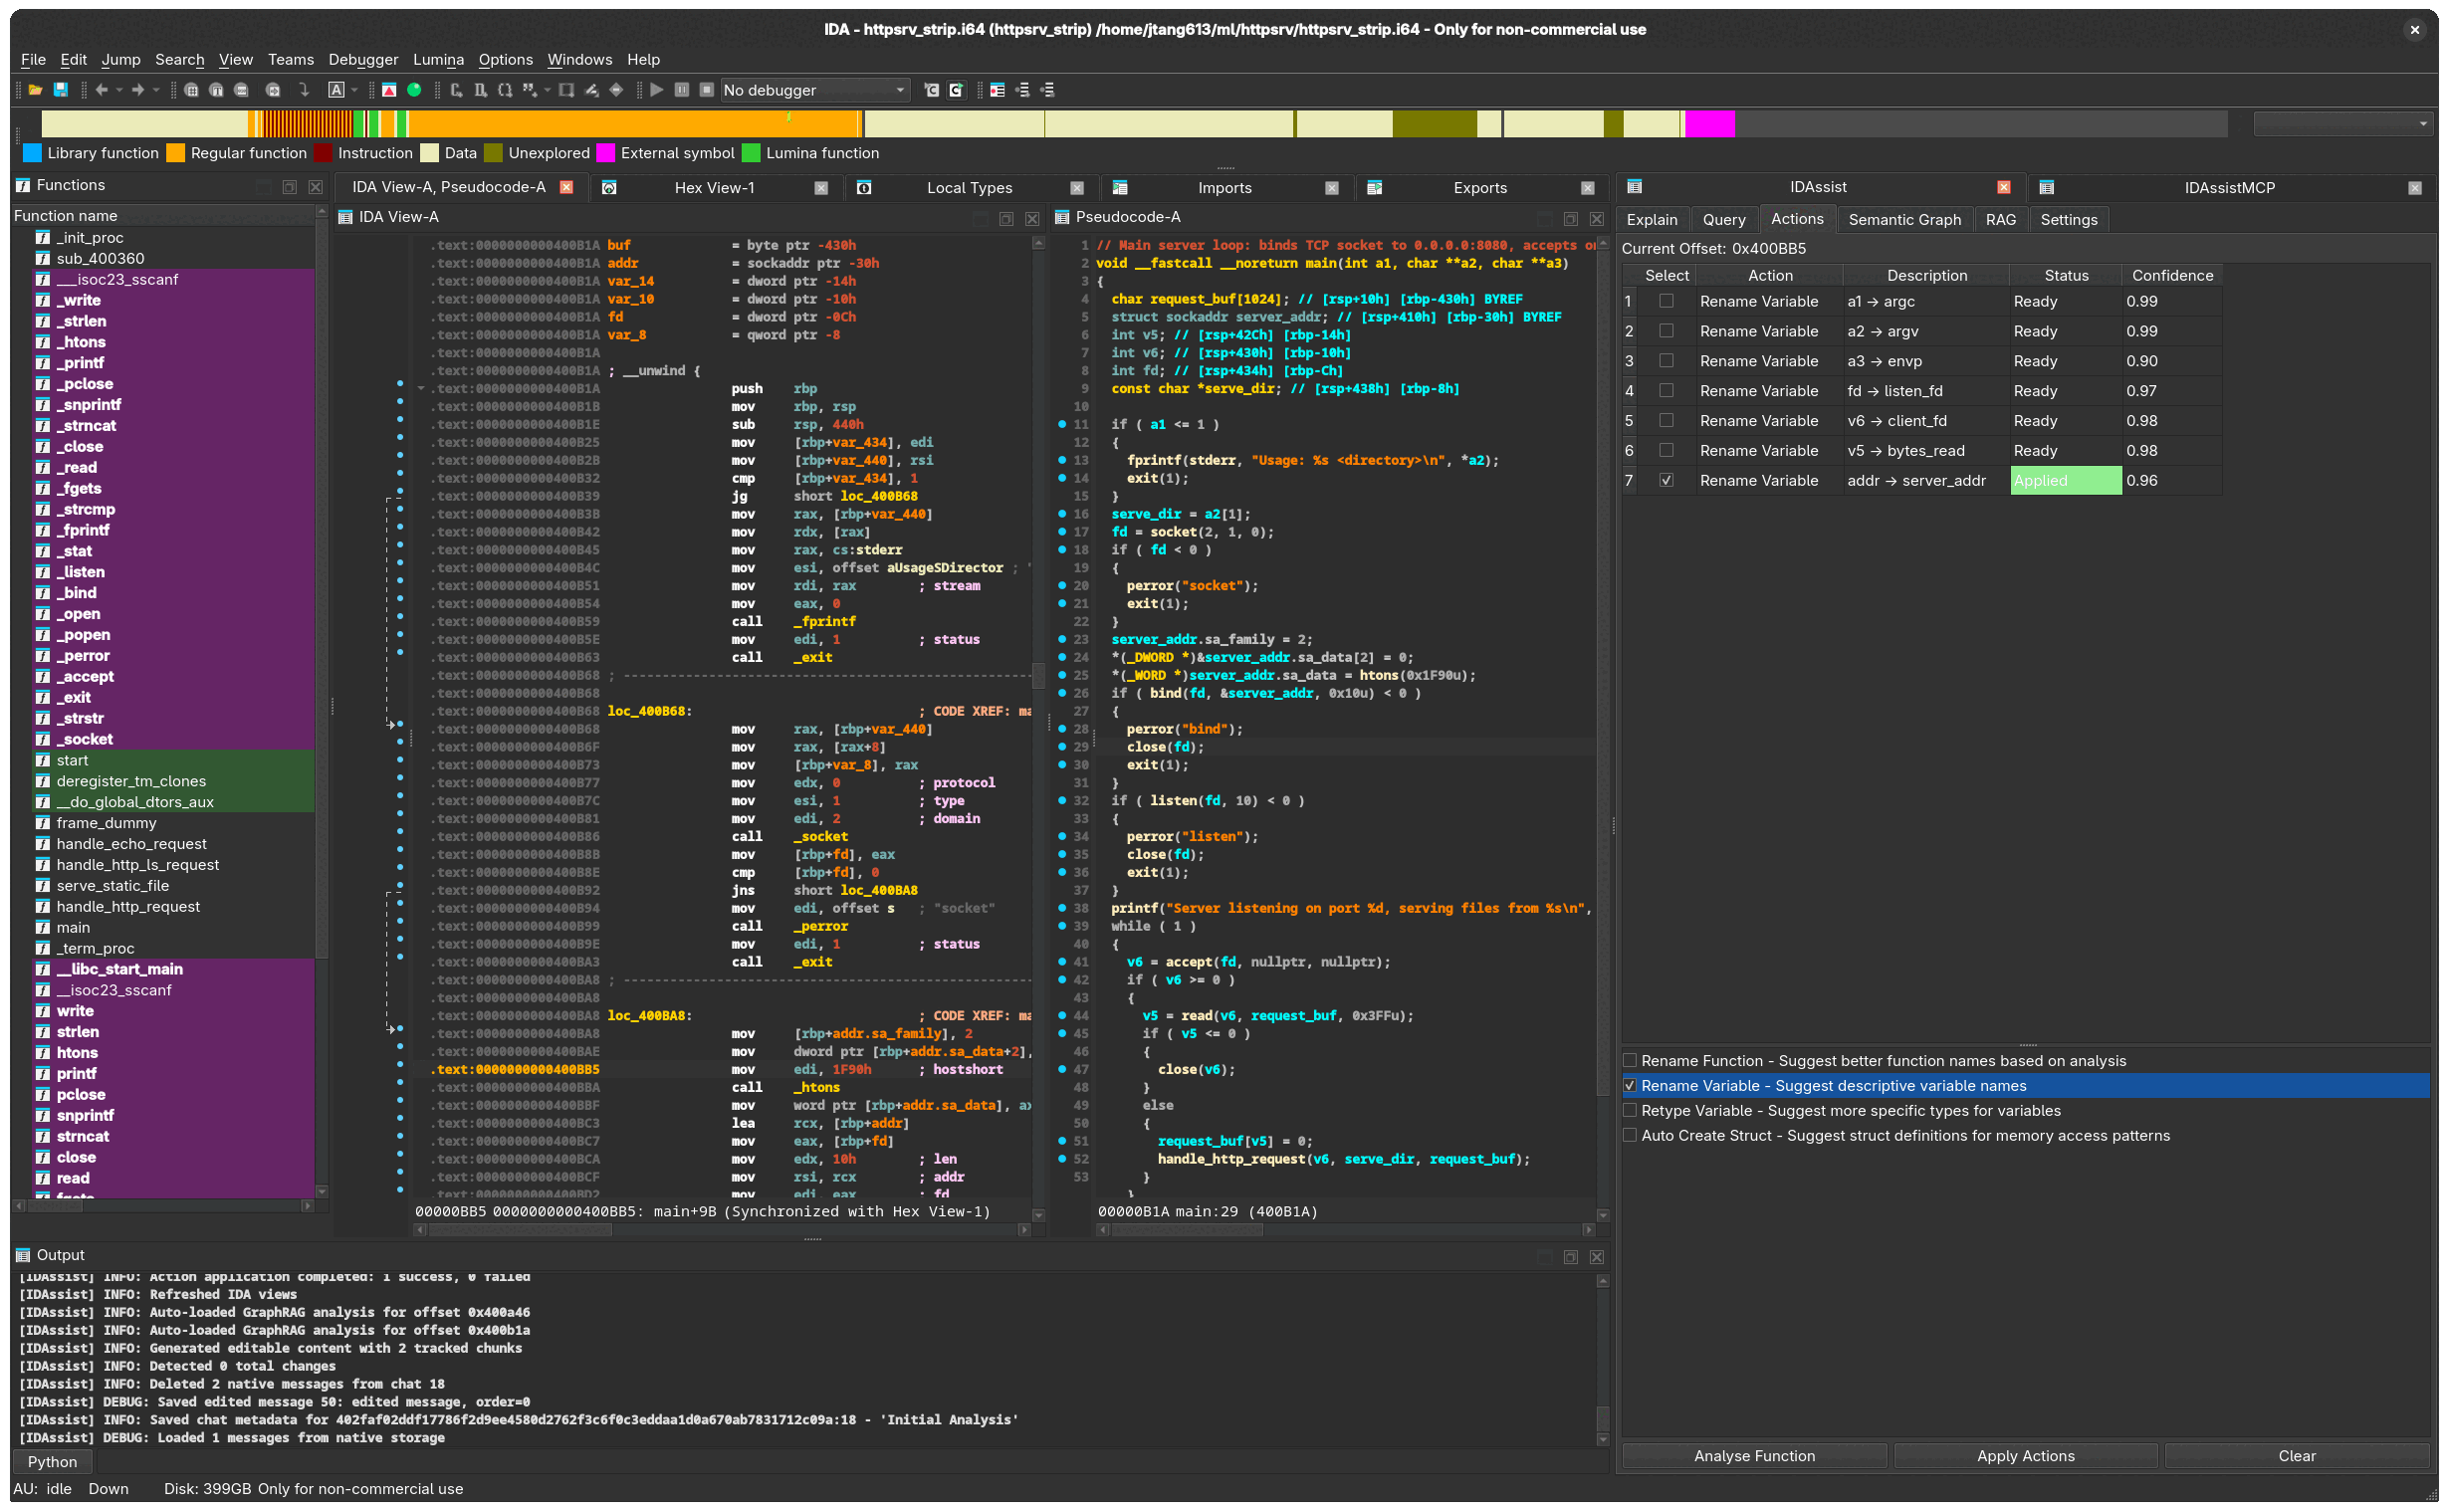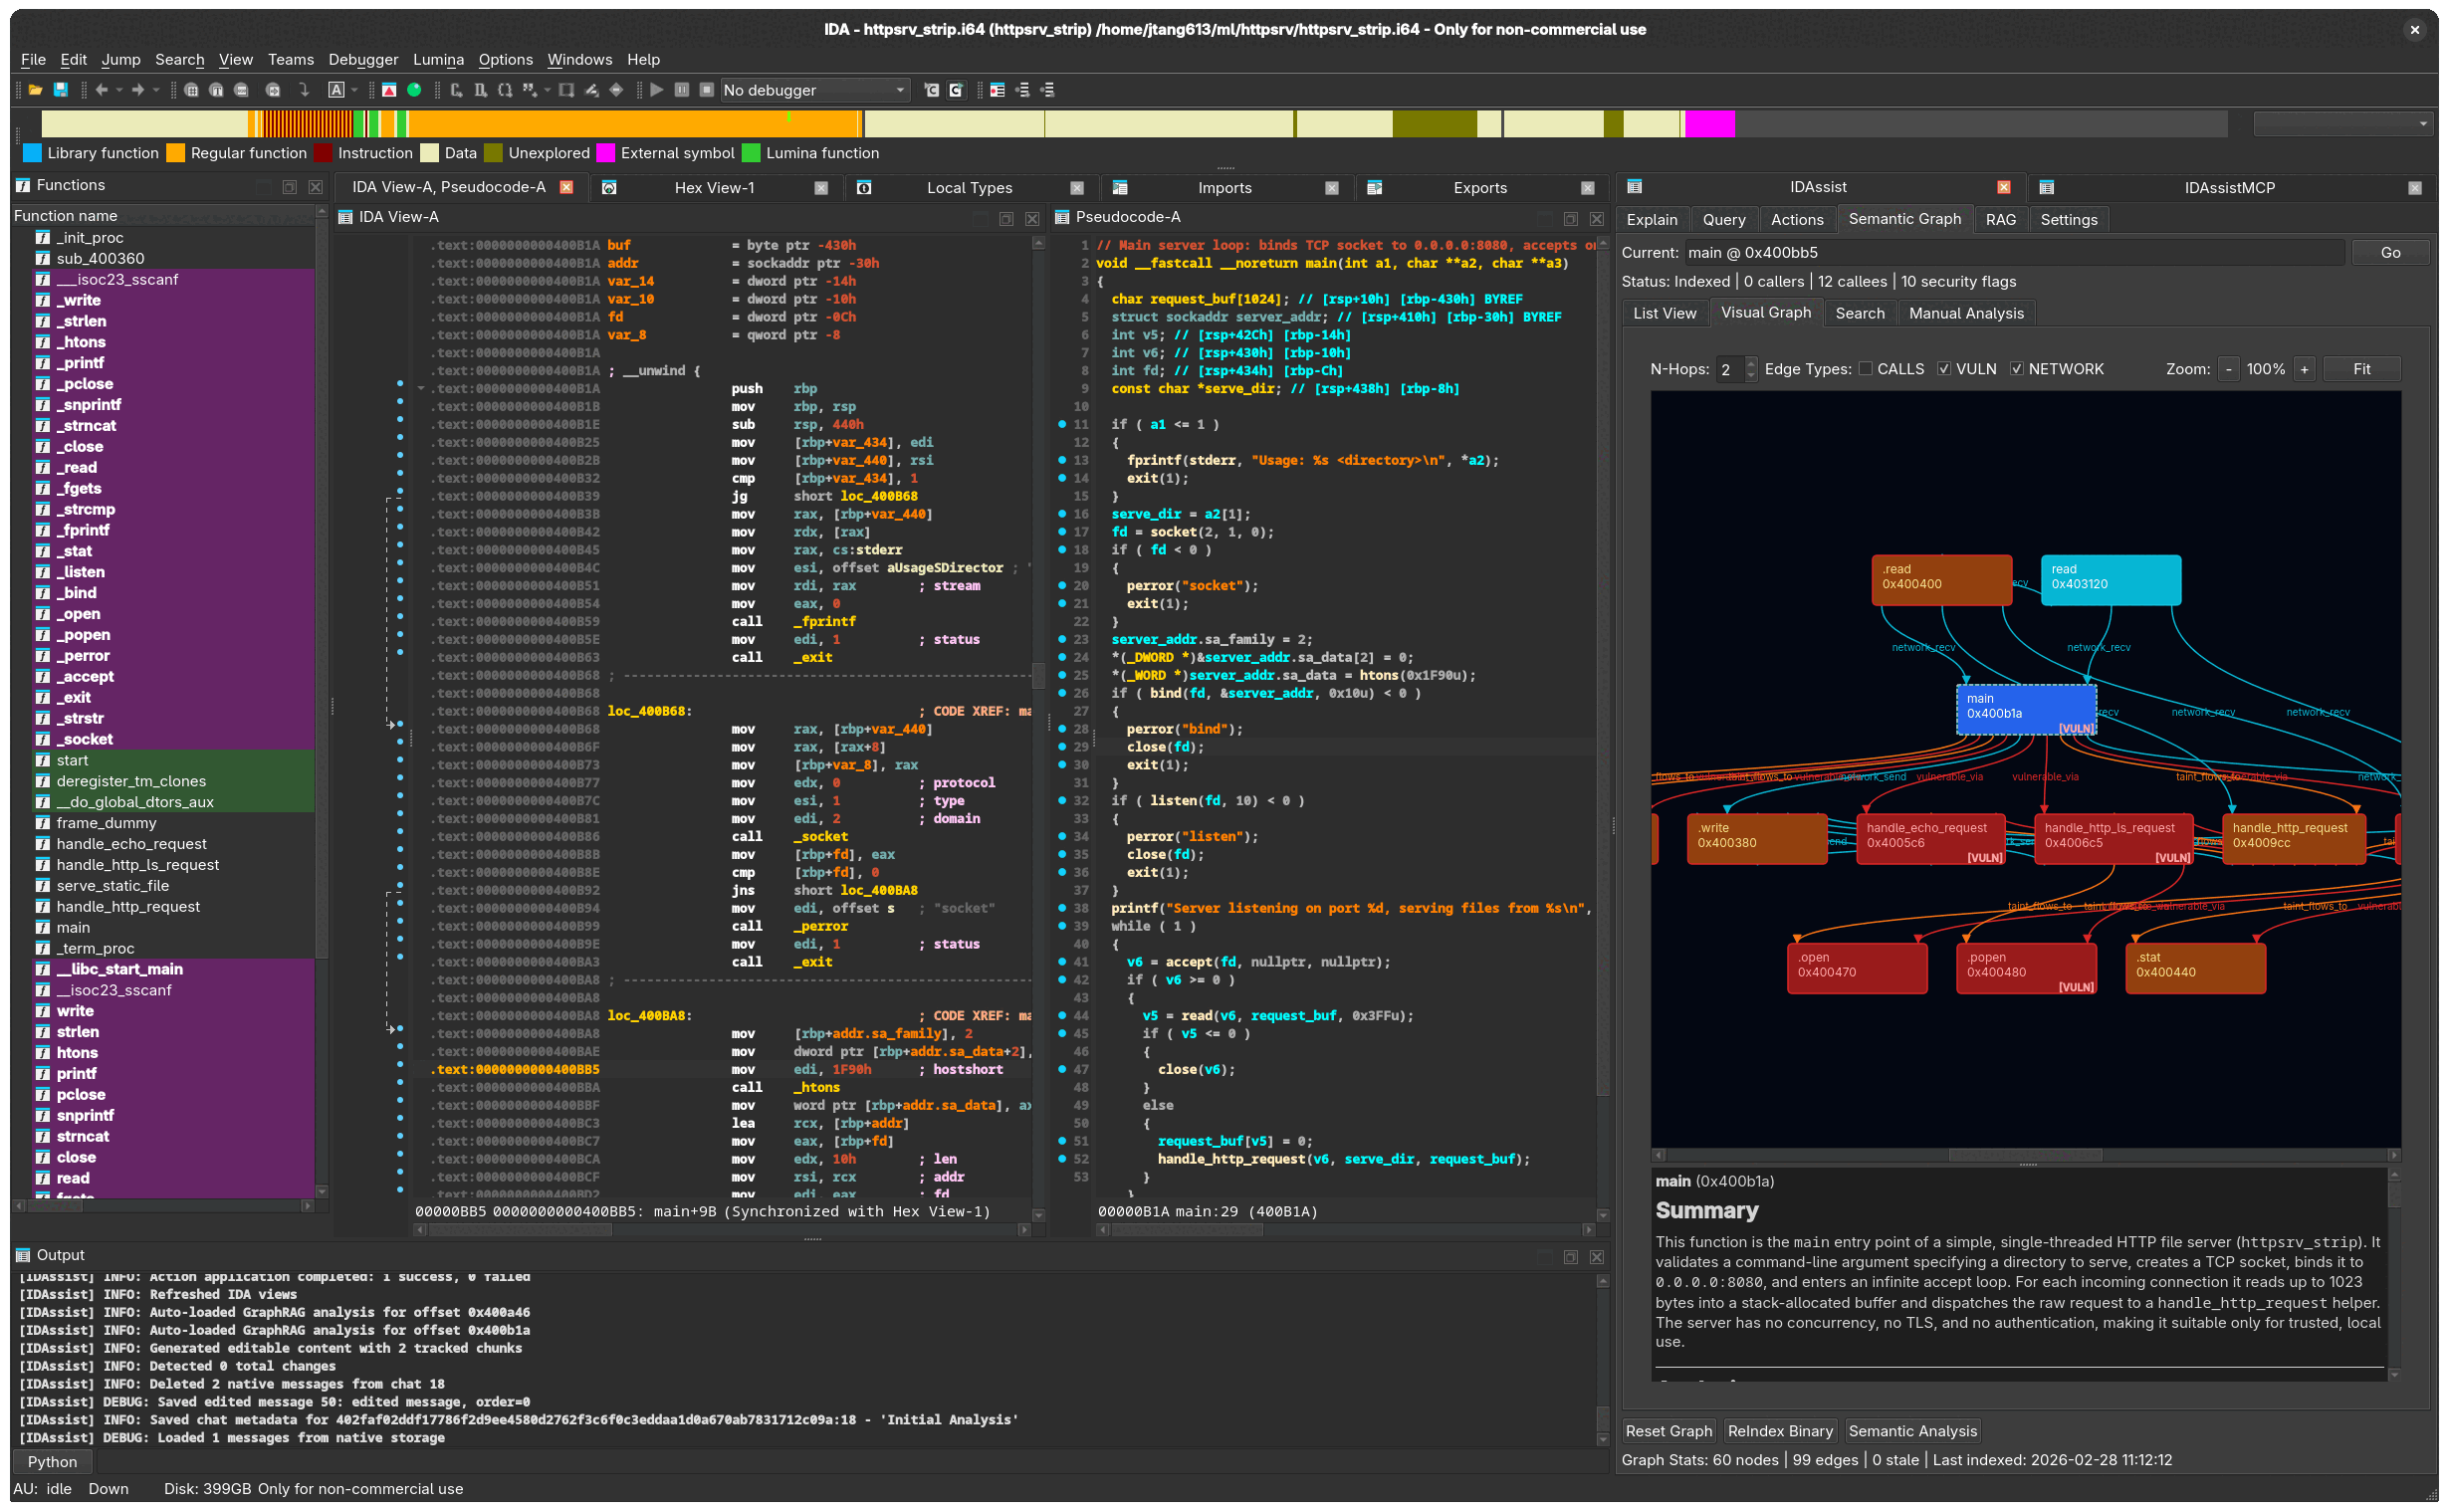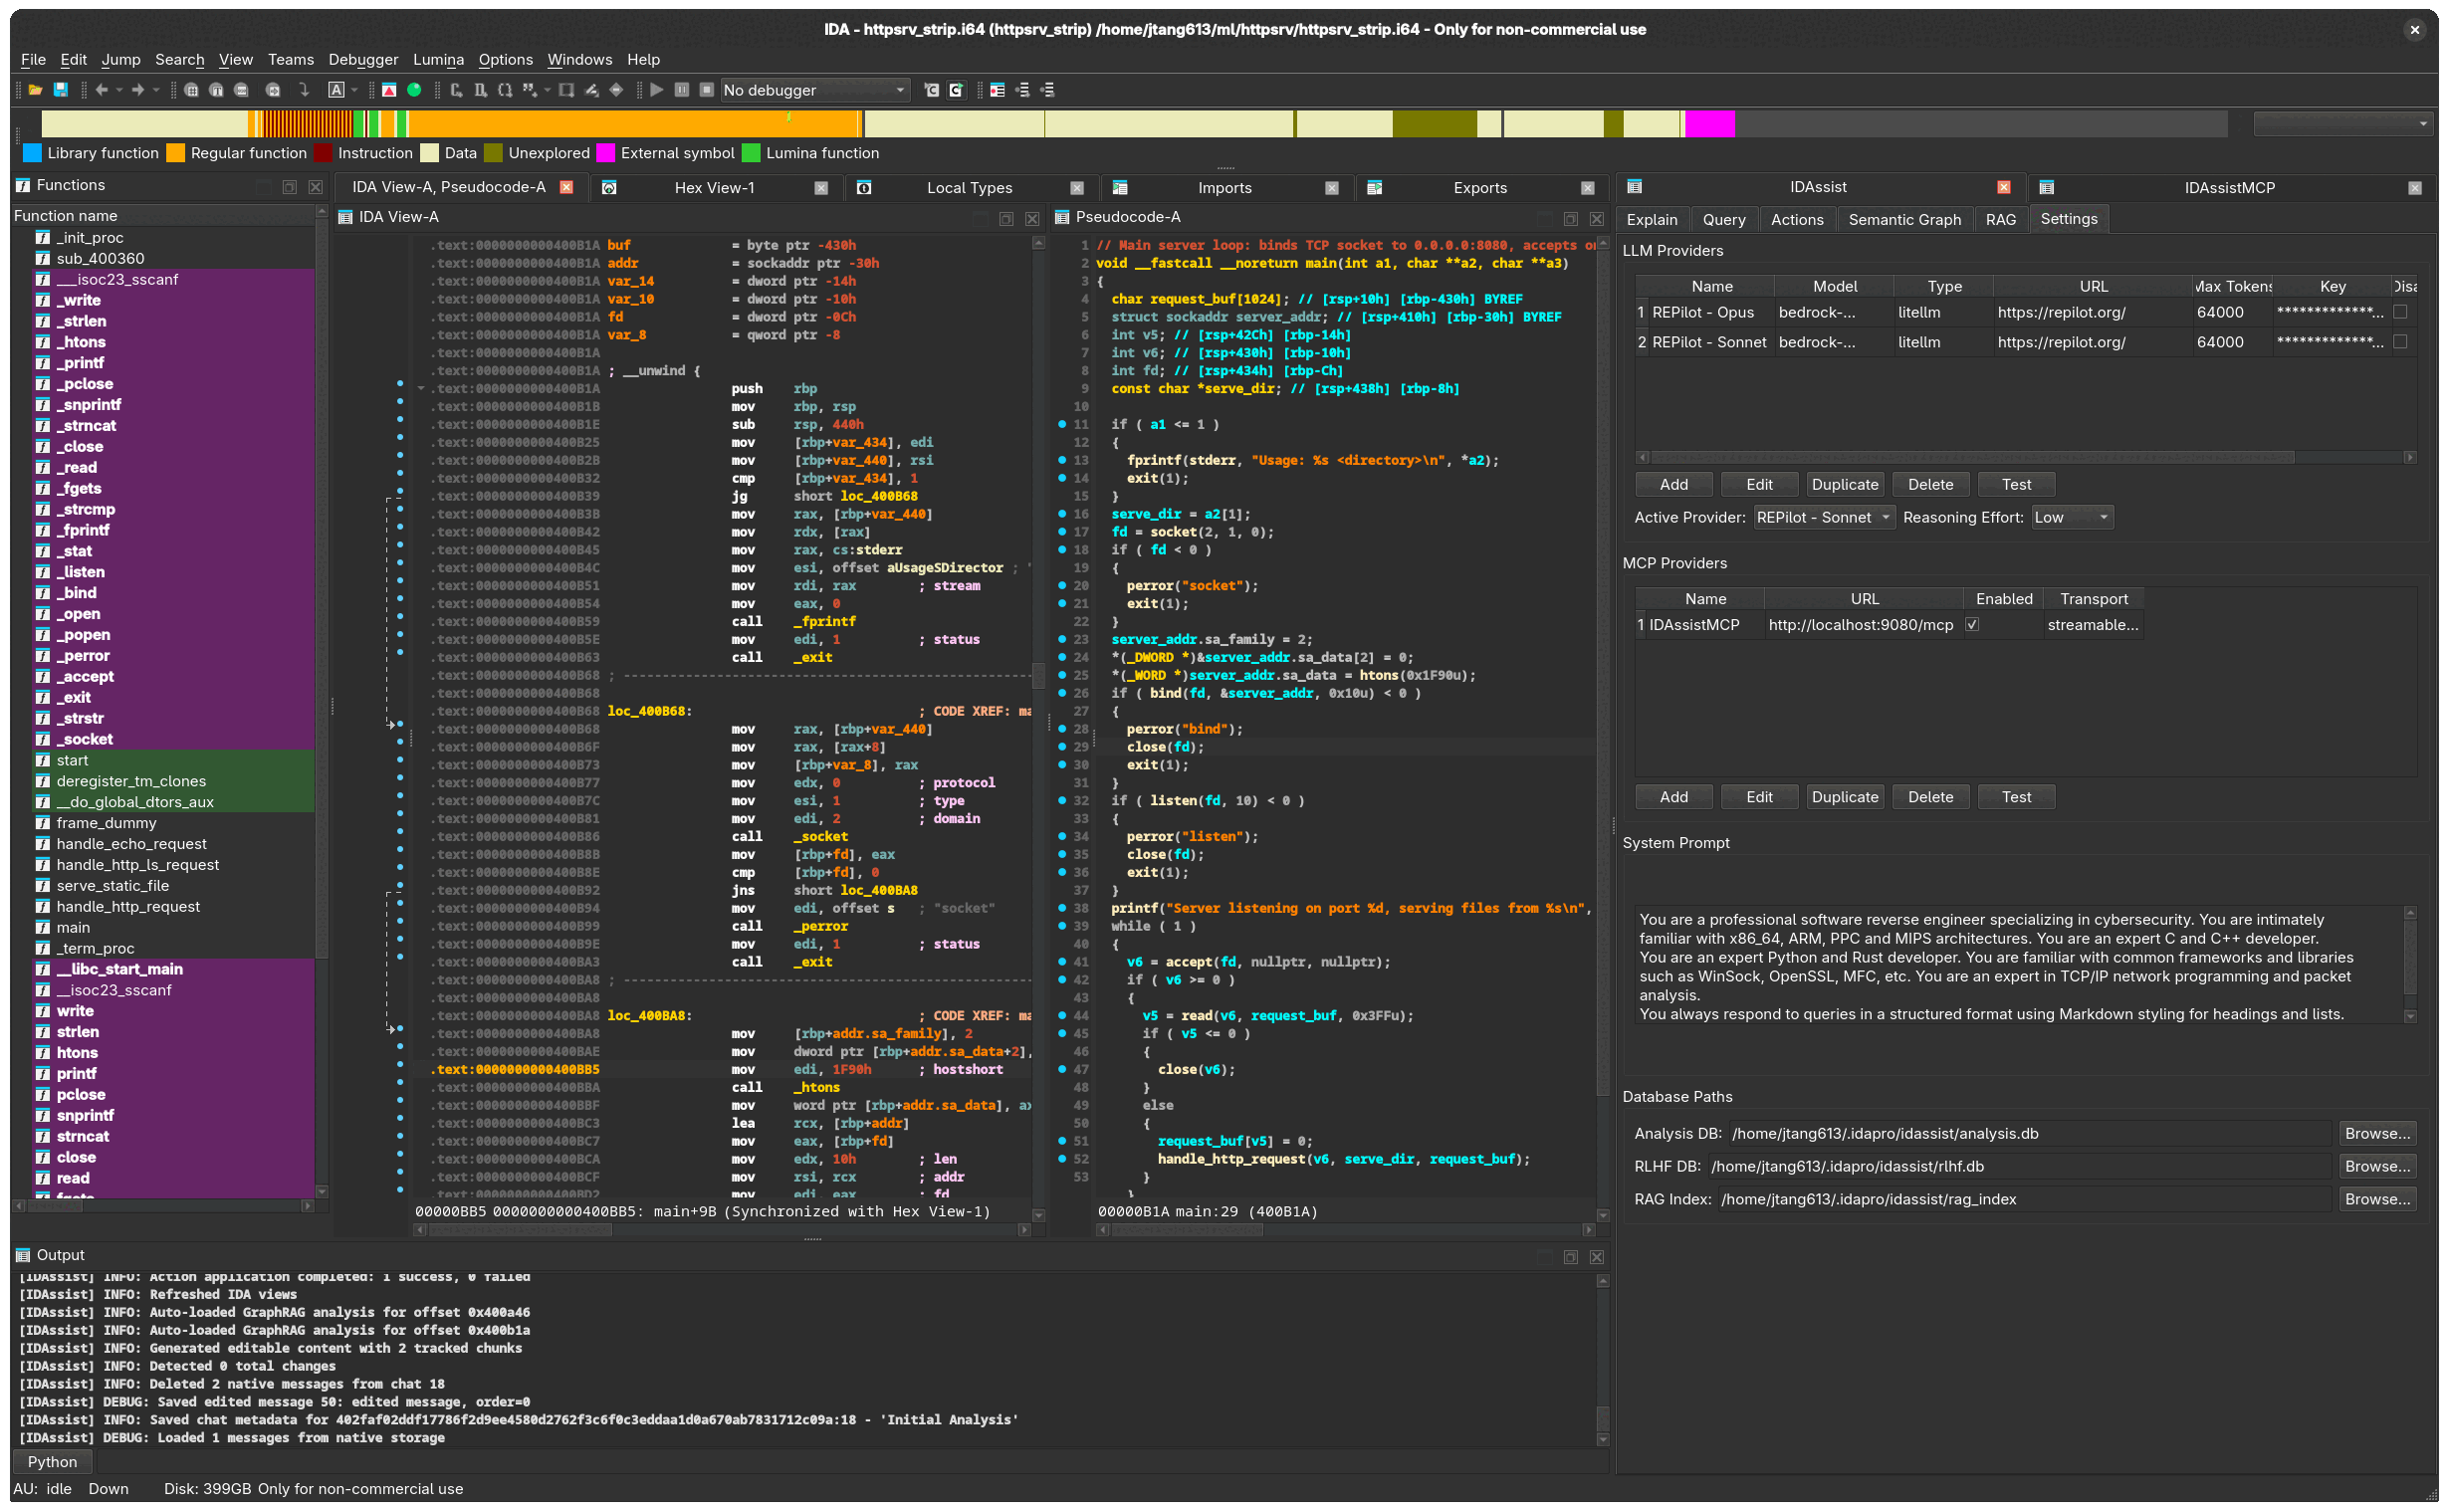
AI-Powered Reverse Engineering Plugin for IDA Pro

Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.

Python dumper/explorer for MCD Runtime Projects used by ODIS

Proof-of-concept exploit for CVE-2021-1656, an information disclosure vulnerability in the Windows TPM driver (tpm.sys). Demonstrates kernel memory…

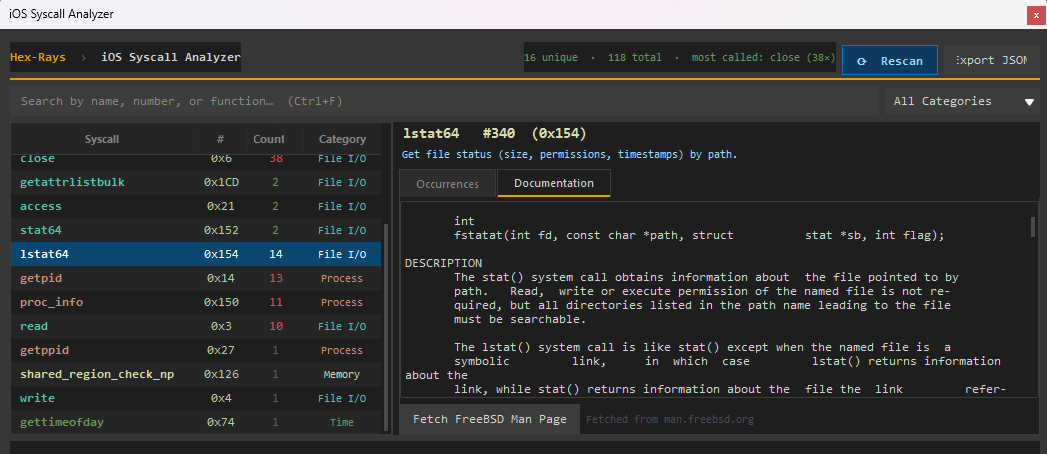
iOS Syscall Explorer for IDA 9.X

POC for CVE-2021-1699

POC For CVE-2022-24483

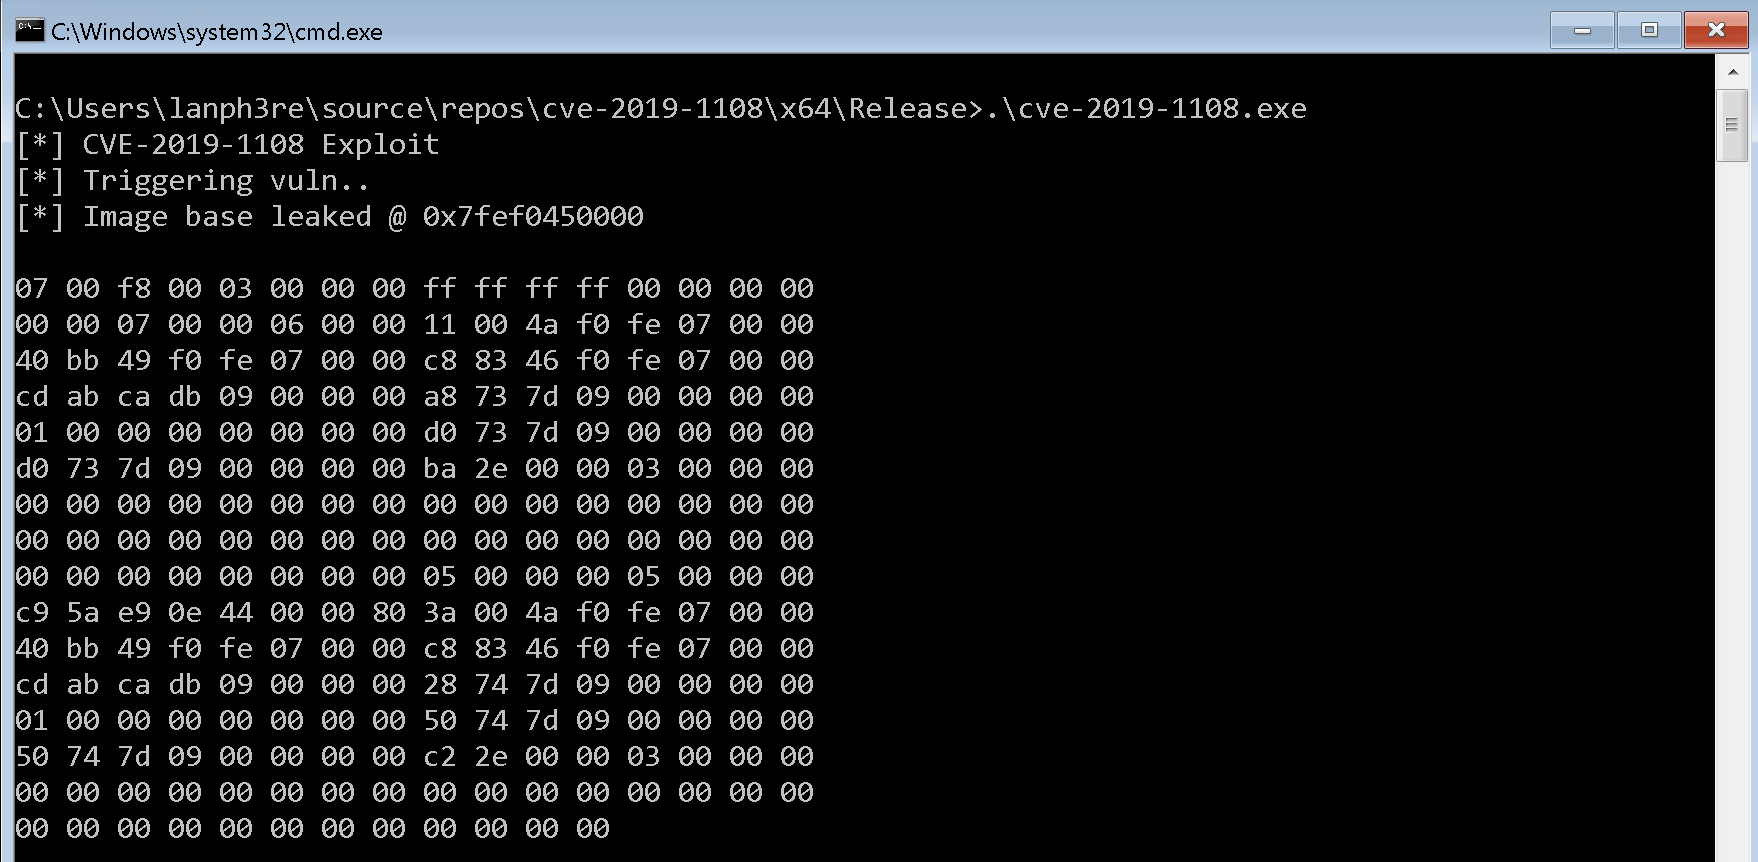
Proof-of-concept exploit for CVE-2019-1108, an RDP client information disclosure vulnerability that leaks memory contents via specially crafted…

Proof-of-concept exploit for CVE-2022-36163, a format string vulnerability in pdftoroff hovacui 1.1.0 PDF reader, demonstrating local…

Exploit code for CVE-2017-8481, a Windows privilege escalation vulnerability.

Crash File ( Poc for CVE-2024-24684)

Proof-of-concept and vulnerability analysis for CVE-2017-0541, demonstrating exploitation techniques and binary-level impact assessment.

Proof-of-concept for CVE-2018-9950, an out-of-bounds read vulnerability in Foxit Reader/PhantomPDF leading to information disclosure and potential…

My musings with PowerShell

Collection of Offensive C# Tooling

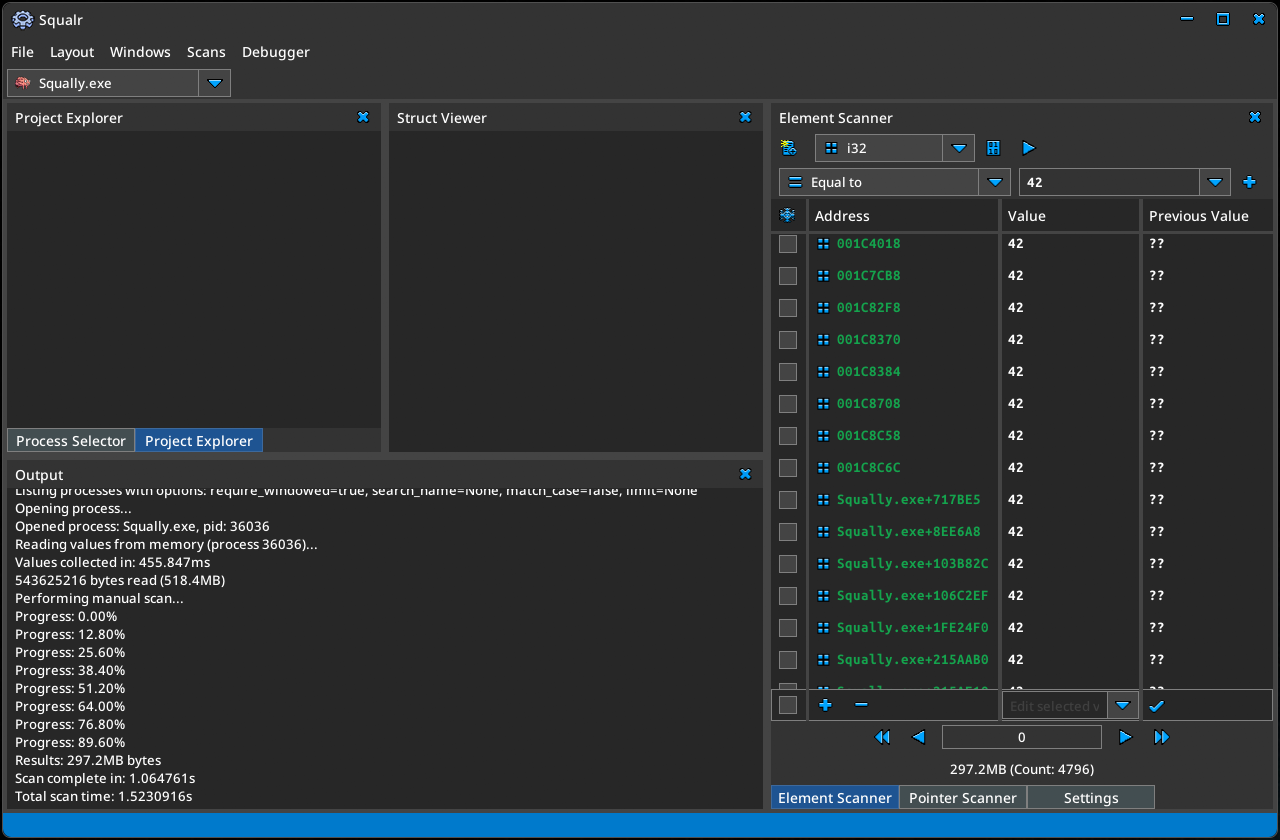
A generic game/software hacking tool written from the ground up in Rust.