
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
1512 results
patriot preview

patriot

GitHubjoe-desimone/patriot

In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
anomaly-detectionbinary-analysisdefensive-tools+3
164
4 years ago
mwcfg preview

mwcfg

GitHubc3rb3ru5d3d53c/mwcfg

A Feature Rich Modular Malware Configuration Extraction Utility for MalDuck
binary-analysisdefensive-toolsmalware-analysis+3
1342 years ago
draytek-arsenal preview

draytek-arsenal

GitHubinfobyte/draytek-arsenal

Reverse Engineering and Observability toolkit for Draytek firewalls
binary-analysisembedded-systems-securityfirmware-analysis+5
541 year ago
IDArling preview
Archived

IDArling

GitHubidarlingteam/idarling

Collaborative Reverse Engineering plugin for IDA Pro & Hex-Rays

binary-analysisdebuggerseducation+2
6705 years ago
LIEF preview

LIEF

GitHublief-project/lief

Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
ai-assisted-reversingandroid-securitybinary-analysis+12
5.6k17 days ago
MCPDebugger preview

MCPDebugger

GitHubfatmike-gh/mcpdebugger

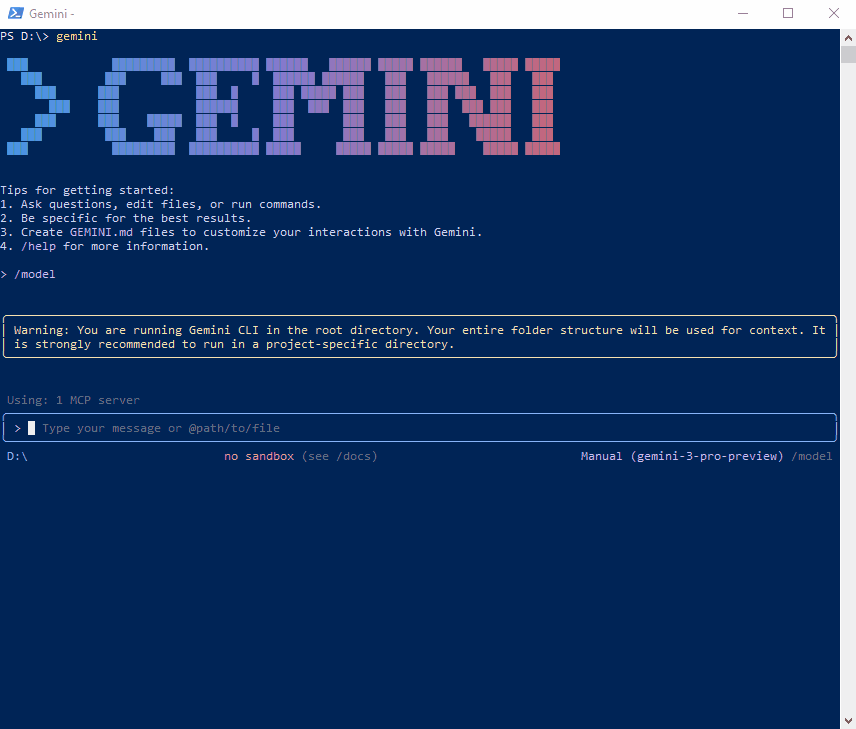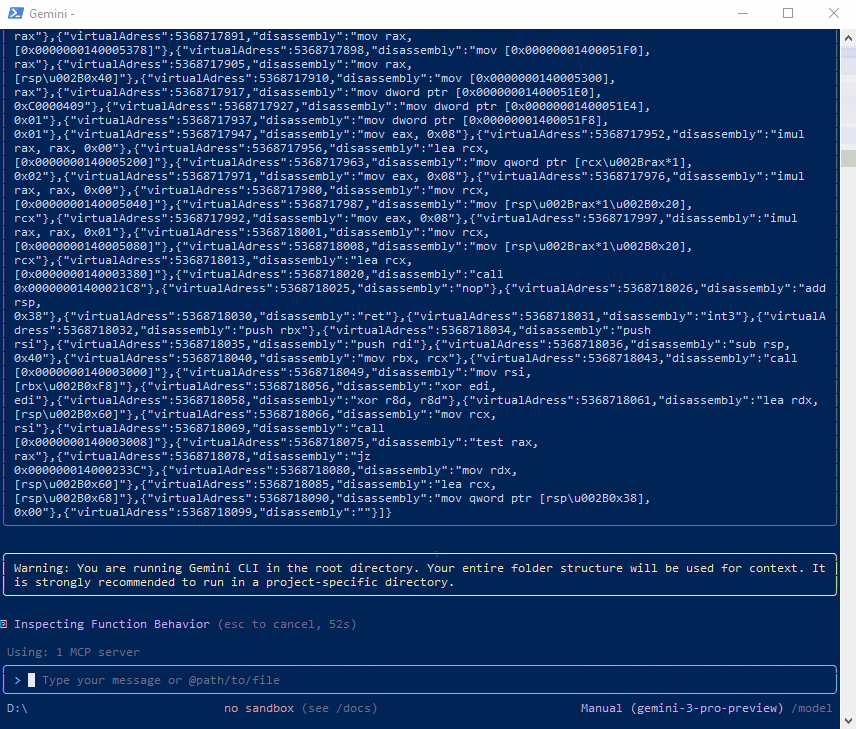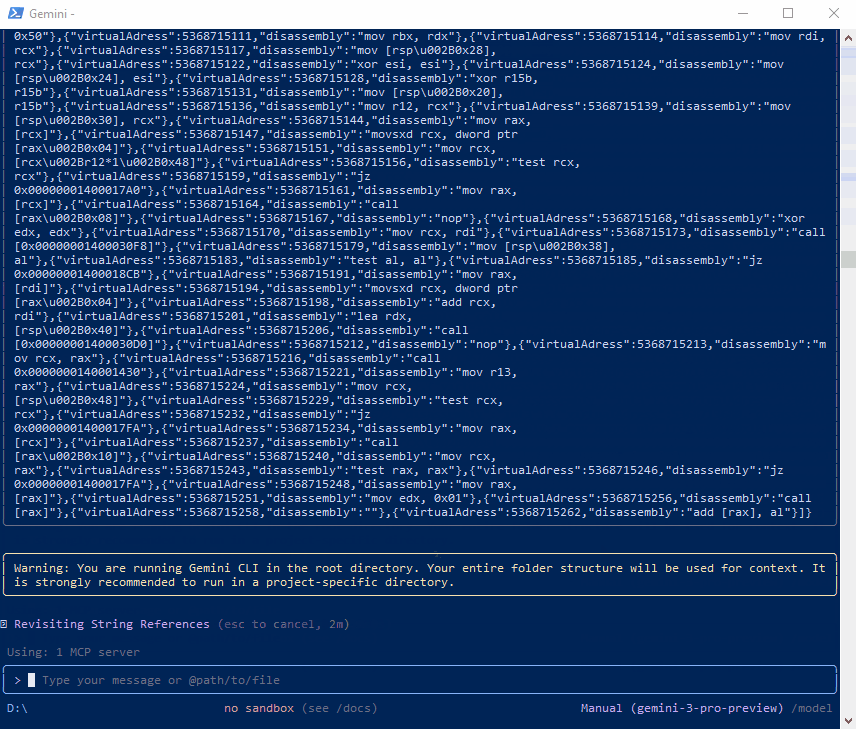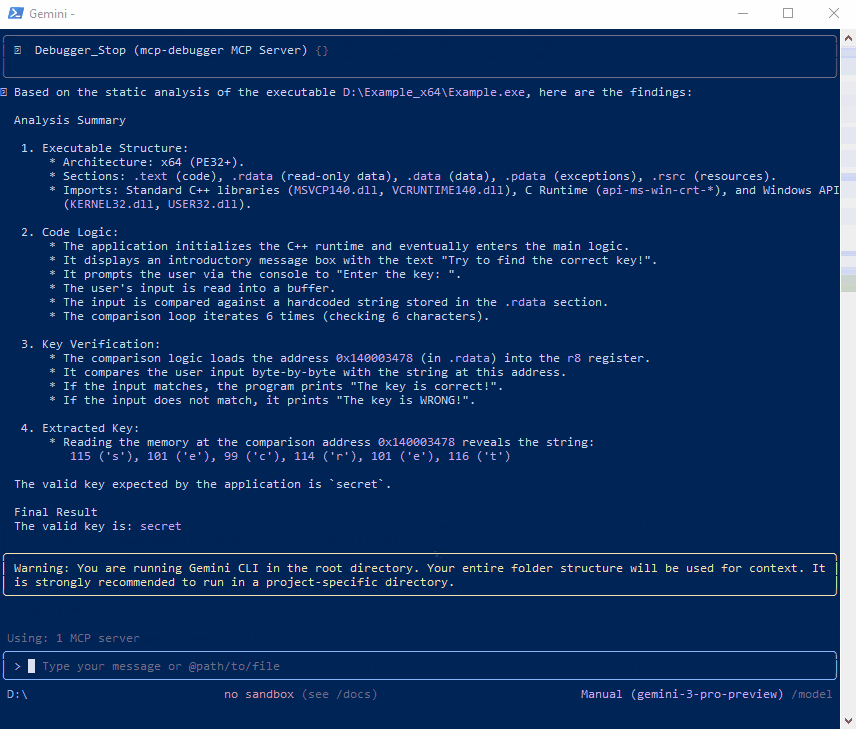
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
ai-assisted-reversingbinary-analysisdebuggers+4
135 months ago
certfuzz preview
Archived

certfuzz

GitHubcertcc/certfuzz

This project contains the source code for the CERT Basic Fuzzing Framework (BFF) and the CERT Failure Observation Engine (FOE).
binary-analysisdynamic-analysis-sandboxingexploitation+3
2741 year ago
binbloom preview

binbloom

GitHubquarkslab/binbloom

Raw binary firmware analysis software

binary-analysisembedded-systems-securityfirmware-analysis+1
5863 years ago
CVE-2021-42574 preview
Archived

CVE-2021-42574

GitHubshiomiyan/cve-2021-42574

Minimal Rust project demonstrating CVE-2021-42574 with compile-time behavior differences between patched and vulnerable rustc versions for…
binary-analysiscode-analysisexploitation+2
14 years ago
AtomicSyscall preview

AtomicSyscall

GitHubdaem0nc0re/atomicsyscall

Tools and PoCs for Windows syscall investigation.
adversarial-attackbinary-analysiseducation+3
3649 months ago
bip preview

bip

GitHubsynacktiv/bip

Object-oriented Python API to simplify interaction with IDA for reverse engineering, enabling plugin development and automation of disassembly…
binary-analysiscode-analysisreverse-engineering+2
2054 years ago
LibPNG_OSS-Fuzz preview

LibPNG_OSS-Fuzz

GitHubenessar/libpng_oss-fuzz

Security research project on fuzzing libpng with OSS-Fuzz. Includes seed corpus analysis, custom read/write fuzzers, and a proof-of-concept exploit…

binary-analysiscode-analysiseducation+3
111 months ago
IDARustDemangler preview

IDARustDemangler

GitHubtimetravelthree/idarustdemangler

Rust Demangler & Normalizer plugin for IDA
binary-analysiscode-analysisreverse-engineering
3563 years ago
OWN-Defender preview

OWN-Defender

GitHubnirvanaon/own-defender

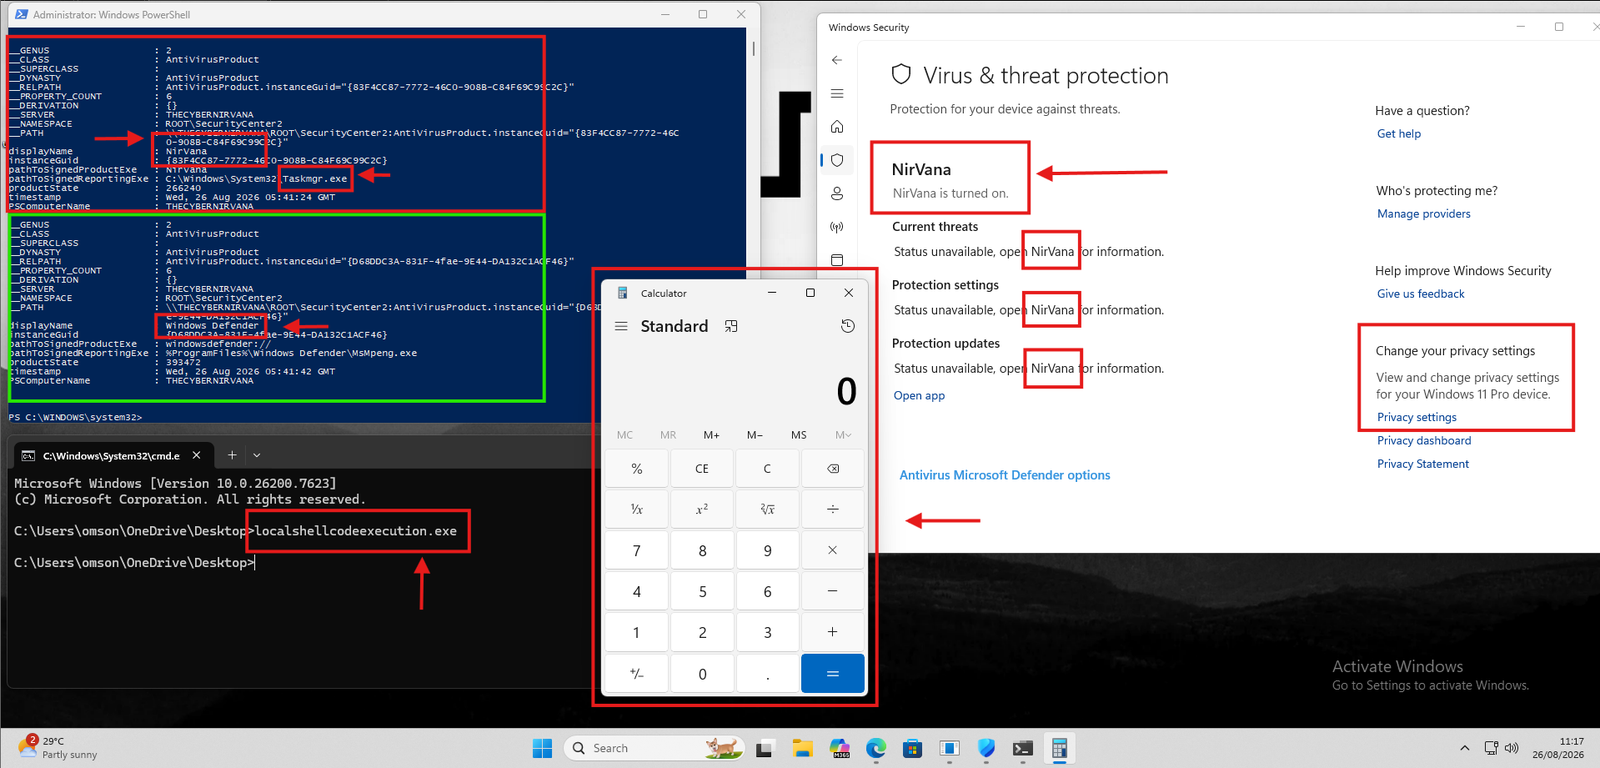
Research project reverse-engineering Windows Security Center COM interfaces to trace AV registration through ATL, vtable, WSCAPI, and RPC, with…

binary-analysisdefensive-toolseducation+2
3627 days ago
smoke_conf_extract preview

smoke_conf_extract

GitHubmyrtus0x0/smoke_conf_extract

Static config extractor for SmokeLoader samples that deobfuscates, unpacks, and emulates protected routines to recover final-stage C2 settings.

binary-analysisdynamic-analysis-sandboxingmalware-analysis+2
133 years ago
uofw preview

uofw

GitHubuofw/uofw

The unofficial Official FirmWare, a complete latest PSP firmware reverse engineering project
binary-analysiseducationembedded-systems-security+3
4407 months ago
idenLib preview

idenLib

GitHubsecrary/idenlib

idenLib - Library Function Identification [This project is not maintained anymore]
binary-analysisdebuggersmalware-analysis+2
3957 years ago
HyperDeceit preview

HyperDeceit

GitHubxyrem/hyperdeceit

HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…

adversarial-attackbinary-analysisids-ips-evasion+3
3823 years ago
Previous123…84Next