
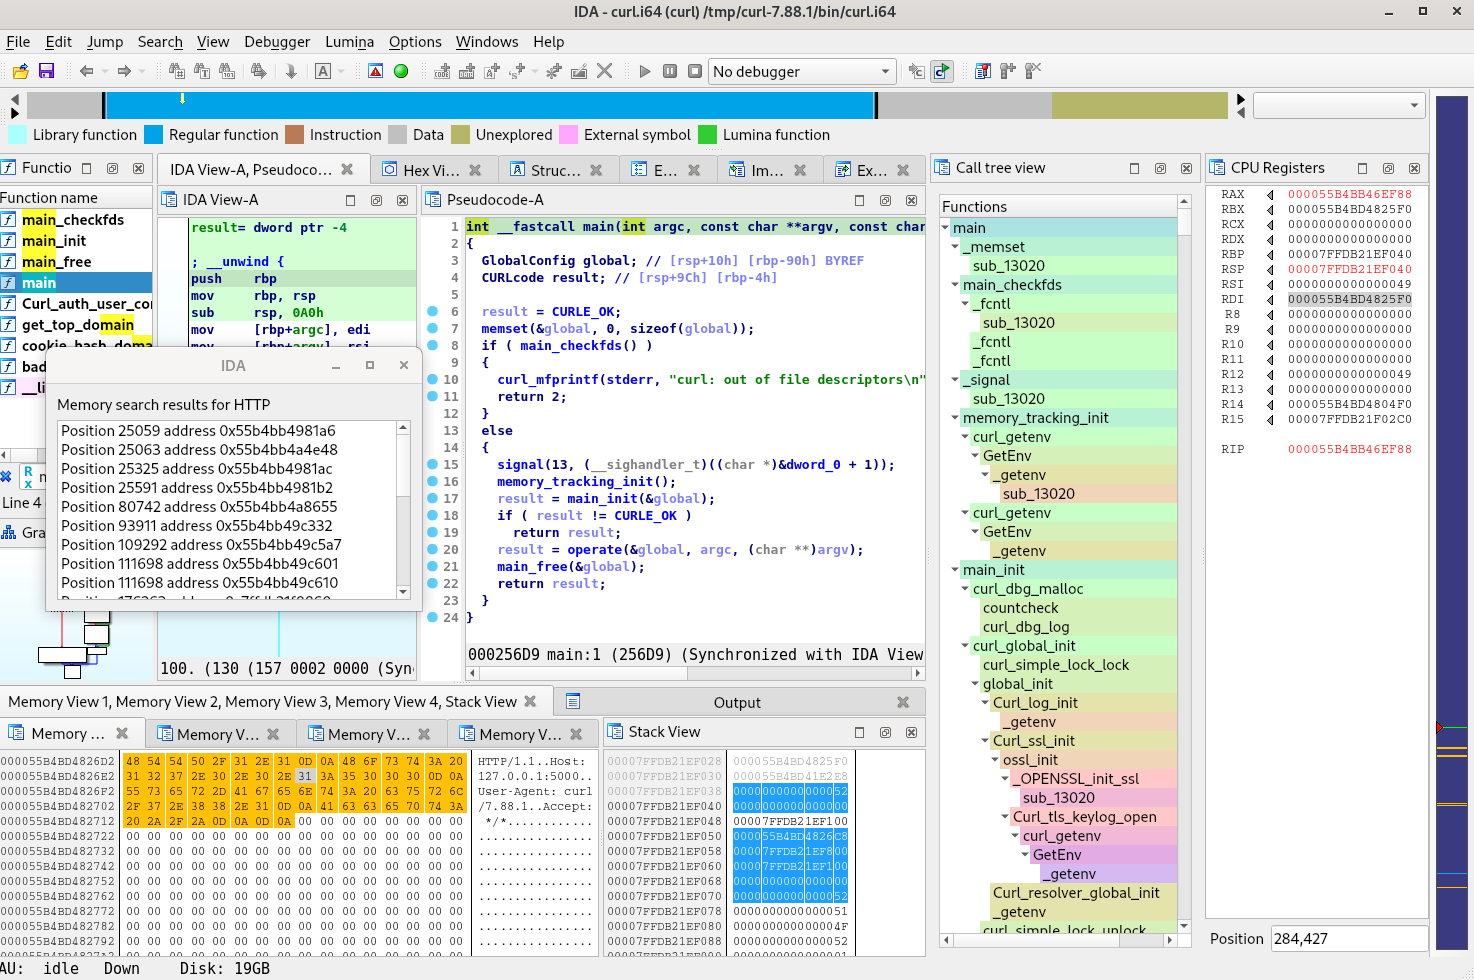
frinet
 synacktiv/frinet
Frida-based tracer for easier reverse-engineering on Android, iOS, Linux, Windows and most related architectures.
binary-analysisdebuggersdynamic-analysis-sandboxing+3
637
synacktiv/frinetFrida-based tracer for easier reverse-engineering on Android, iOS, Linux, Windows and most related architectures.
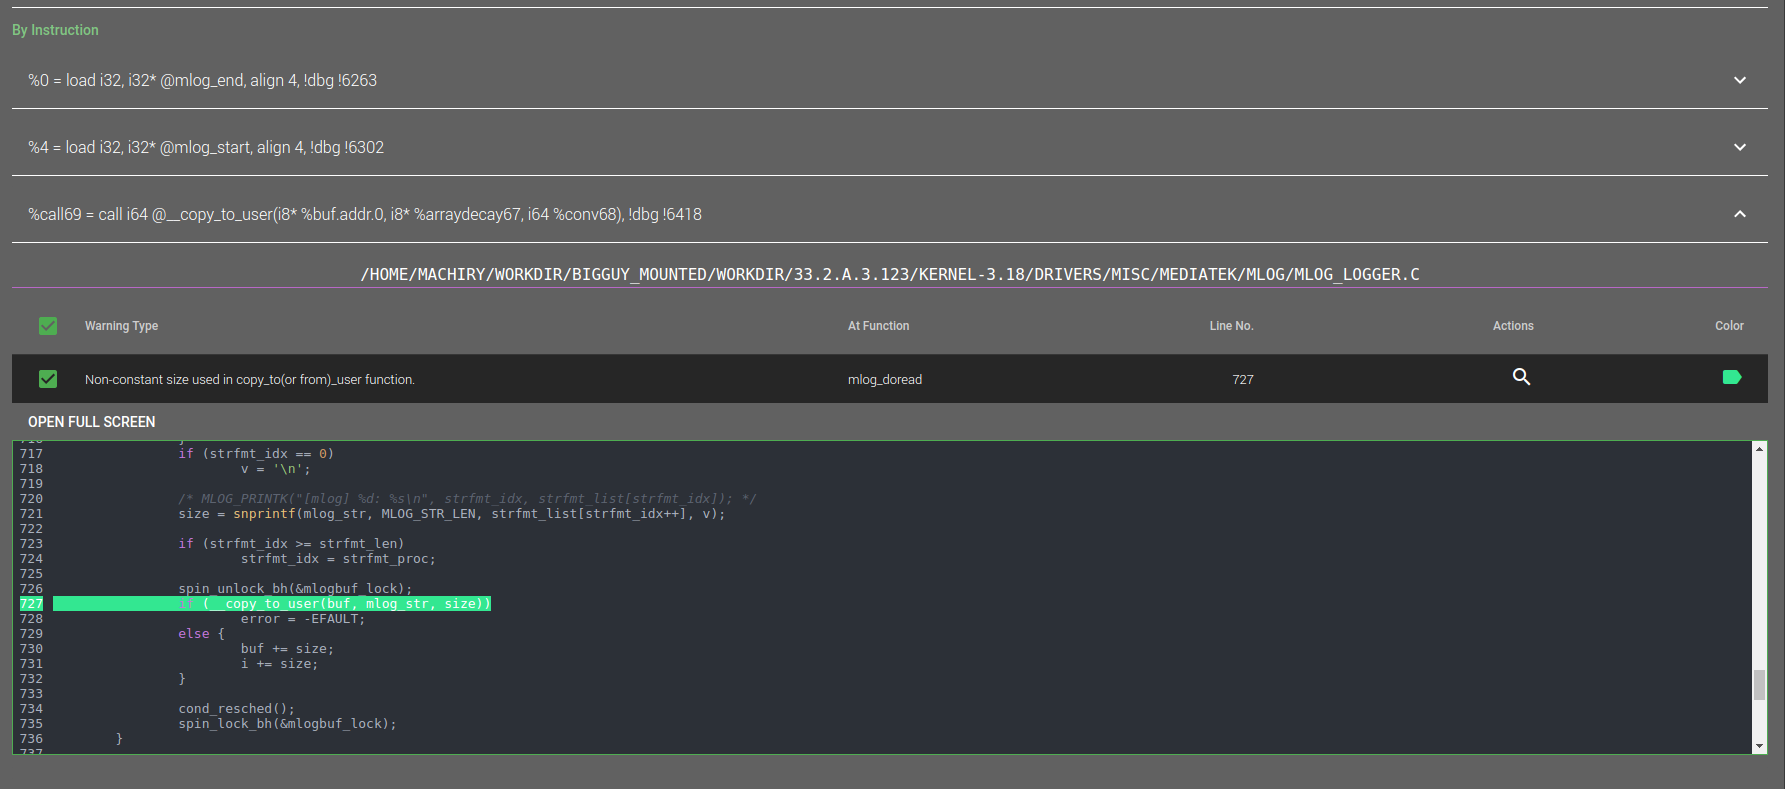 ucsb-seclab/dr_checker
DR.CHECKER : A Soundy Vulnerability Detection Tool for Linux Kernel Drivers
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
 eiln/ane
Reverse engineered Linux kernel driver and userspace library for the Apple Neural Engine (ANE), enabling hardware access and analysis on Linux…
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 mxmssh/drafl
AFL + DynamoRIO = fuzzing binaries with no source code on Linux
 ngwg/ceasta
disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
 gui774ume/krie
Linux Kernel Runtime Integrity with eBPF
 ricccrd/dd
JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
 packtpublishing/learning-linux-binary-analysis
Learning Linux Binary Analysis, published by Packt
 elfmaster/maya
Highly advanced Linux anti-exploitation and anti-tamper binary protector for ELF.
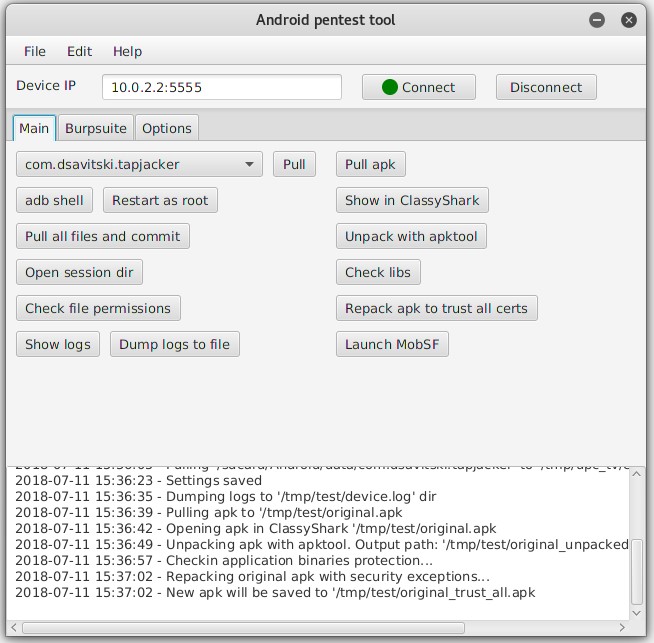 dzmitry-savitski/android-pentest-tool
Android penetration testing tool for Kali linux
 federicodotta/ghidra2frida
Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…
 helviojunior/shellcodetester
An application to test windows and linux shellcodes
 merces/awesome-hex-editors
A curated and enriched list of awesome hexadecimal editors for Windows, macOS, and Linux.
 inokinoki/attesor
AI-powered reverse-engineering of Rosetta (2 for Linux). Disclaimer: due to the user agreement, I will not touch the code. All is done by AI, so…