
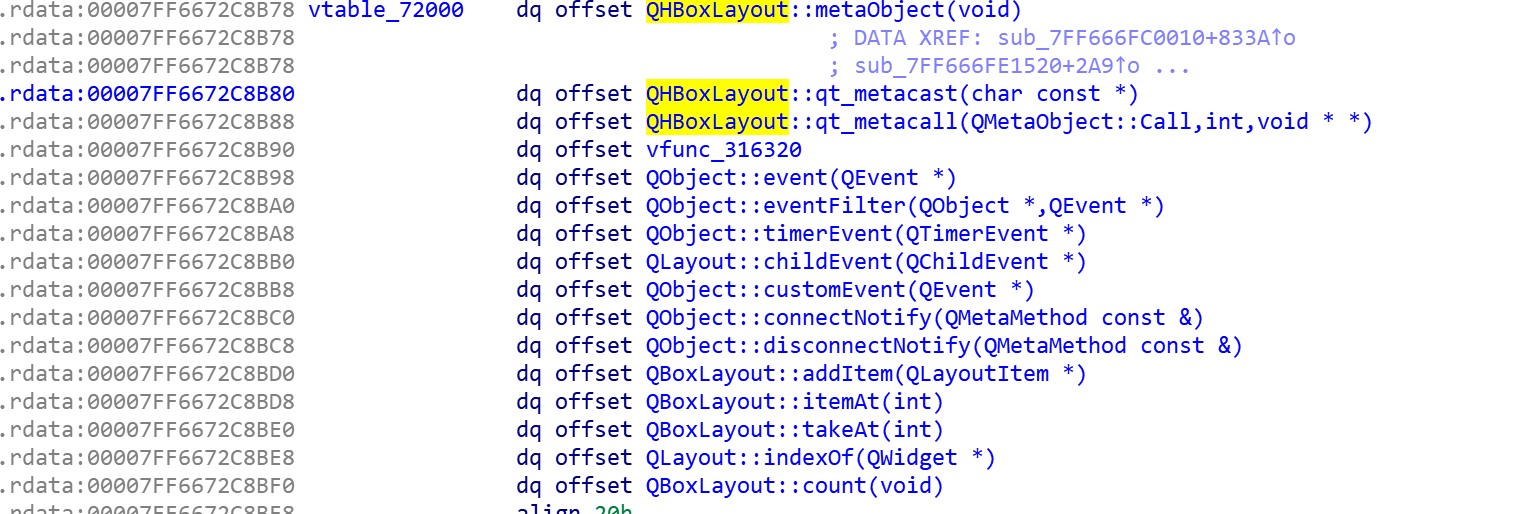
Virtuailor
 0xgalz/virtuailor
IDAPython tool for creating automatic C++ virtual tables in IDA Pro
binary-analysisdebuggersdynamic-analysis-sandboxing+2
1.4k
0xgalz/virtuailorIDAPython tool for creating automatic C++ virtual tables in IDA Pro
 airbus-seclab/bincat
Binary code static analyser, with IDA integration. Performs value and taint analysis, type reconstruction, use-after-free and double-free detection
 llnl/oghidra
OGhidra bridges Large Language Models (LLMs) via Ollama with the Ghidra reverse engineering platform, enabling AI-driven binary analysis through…
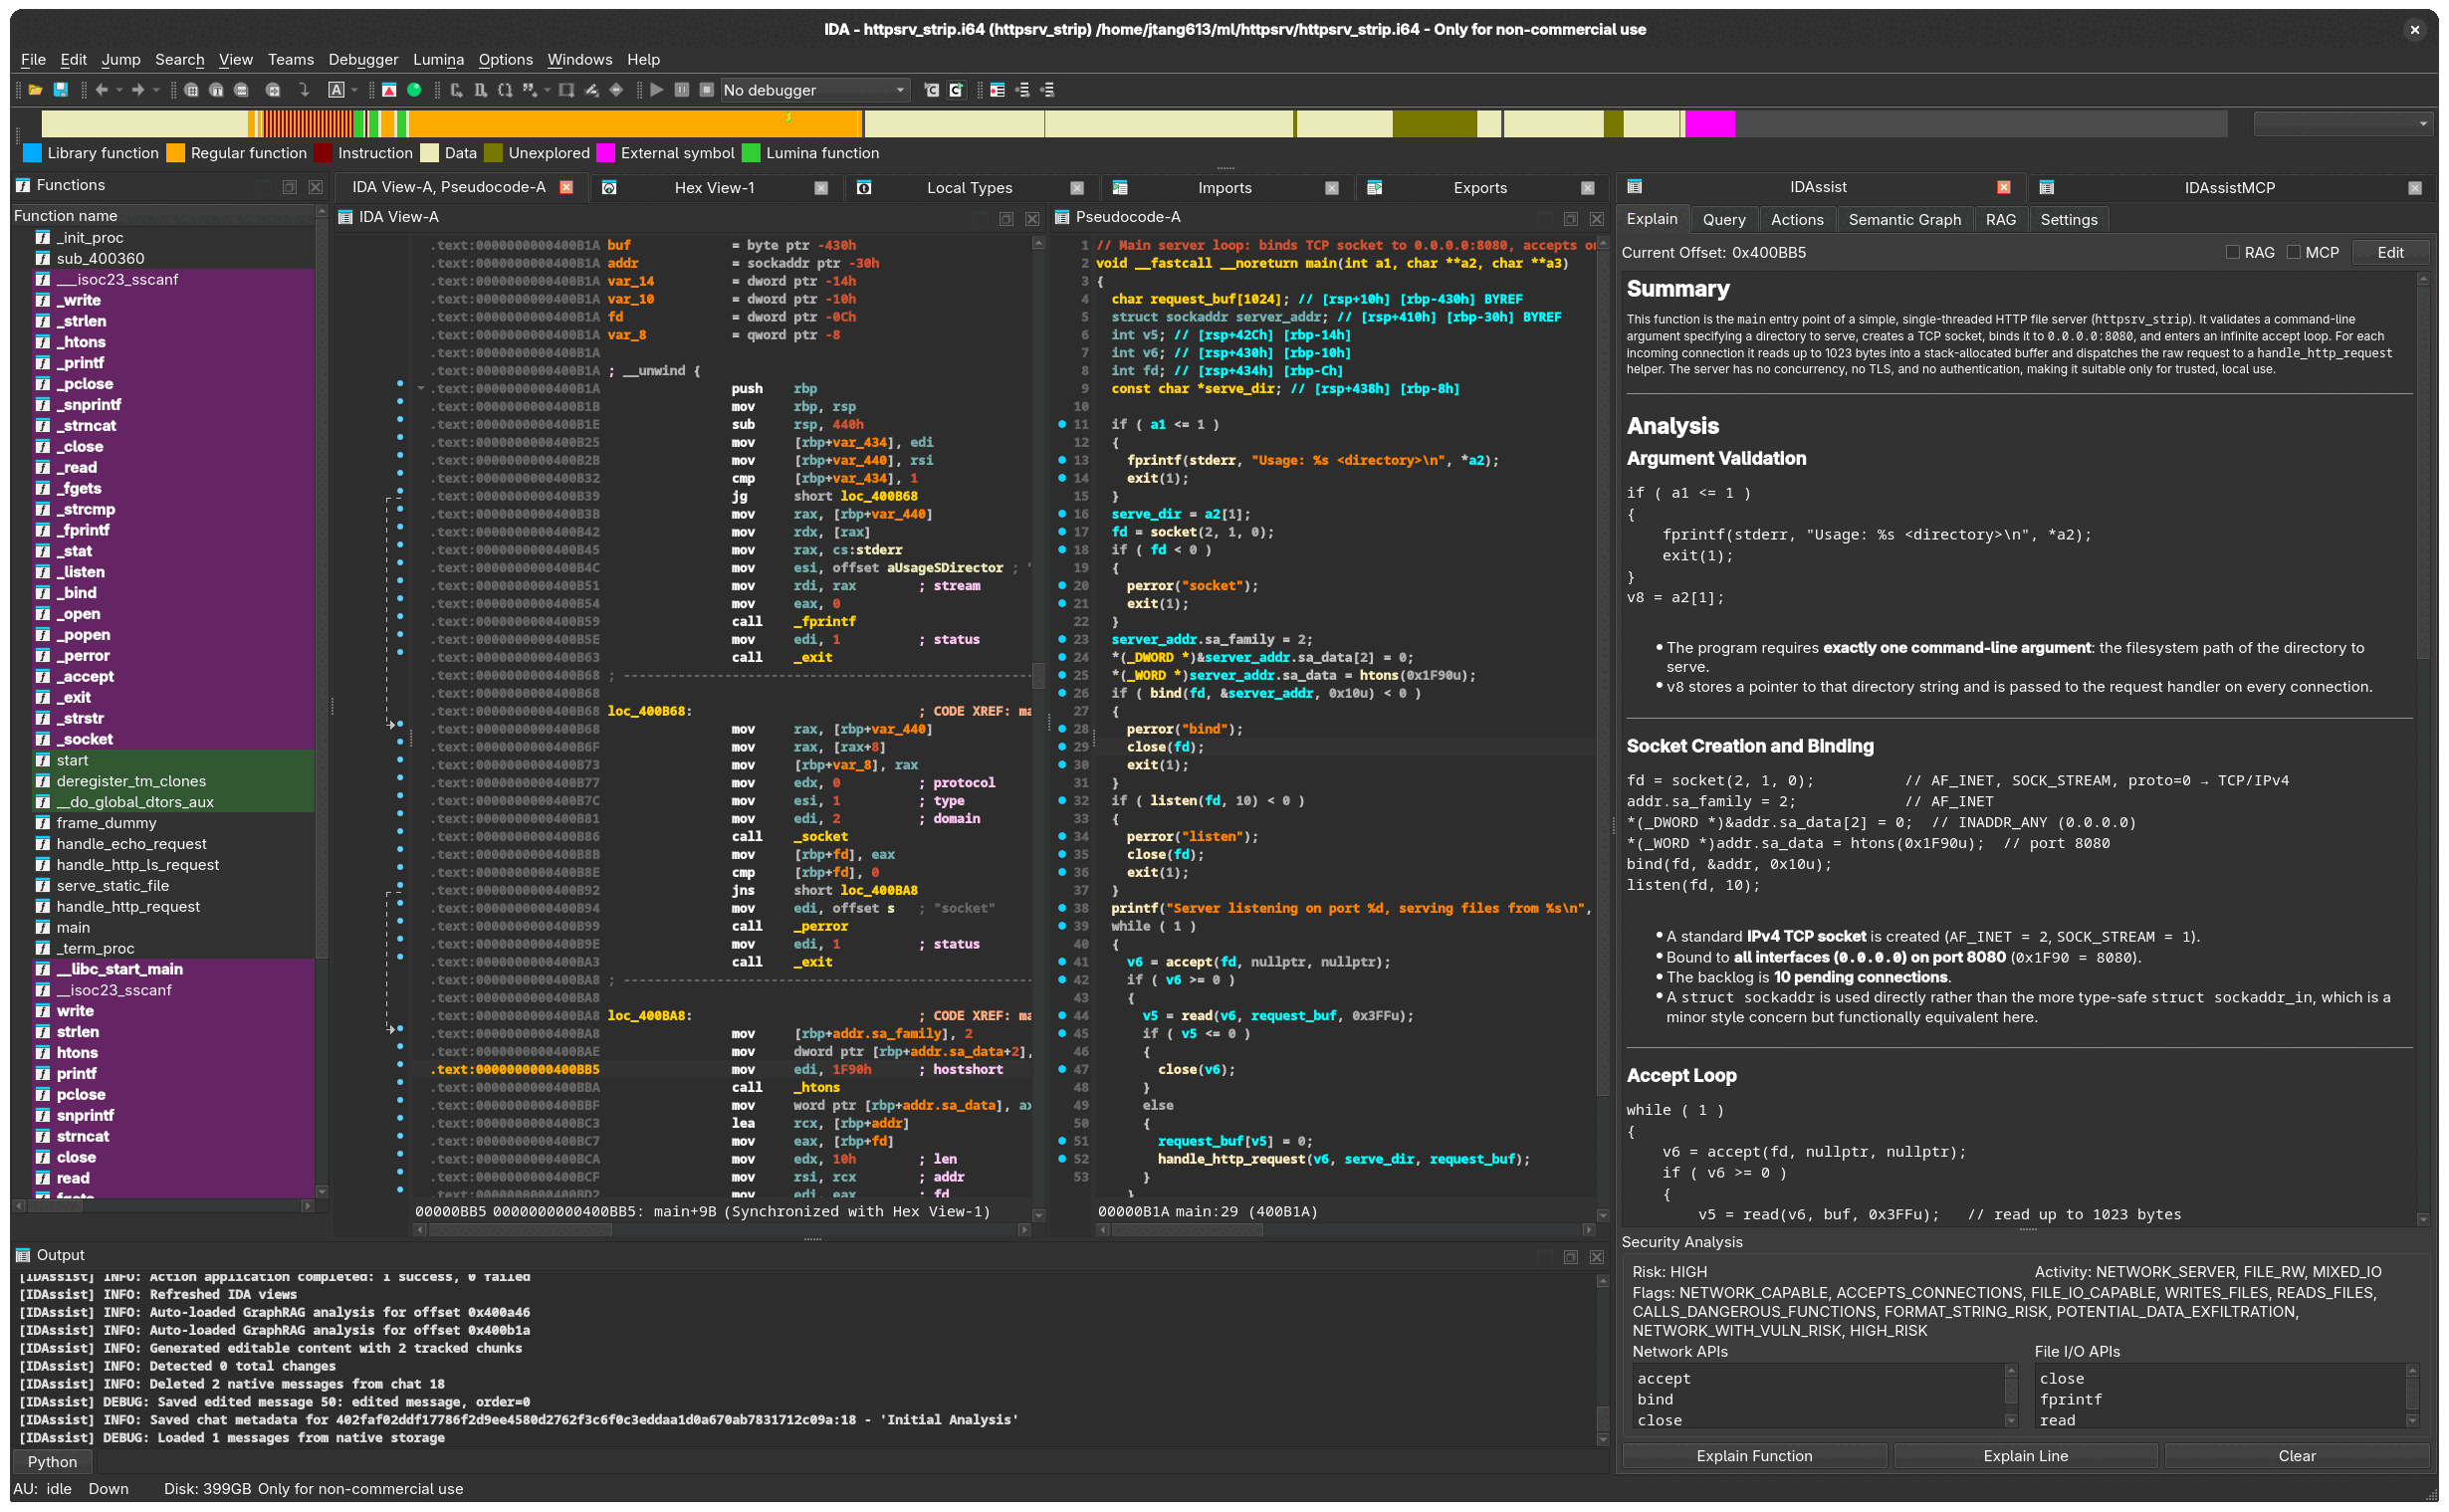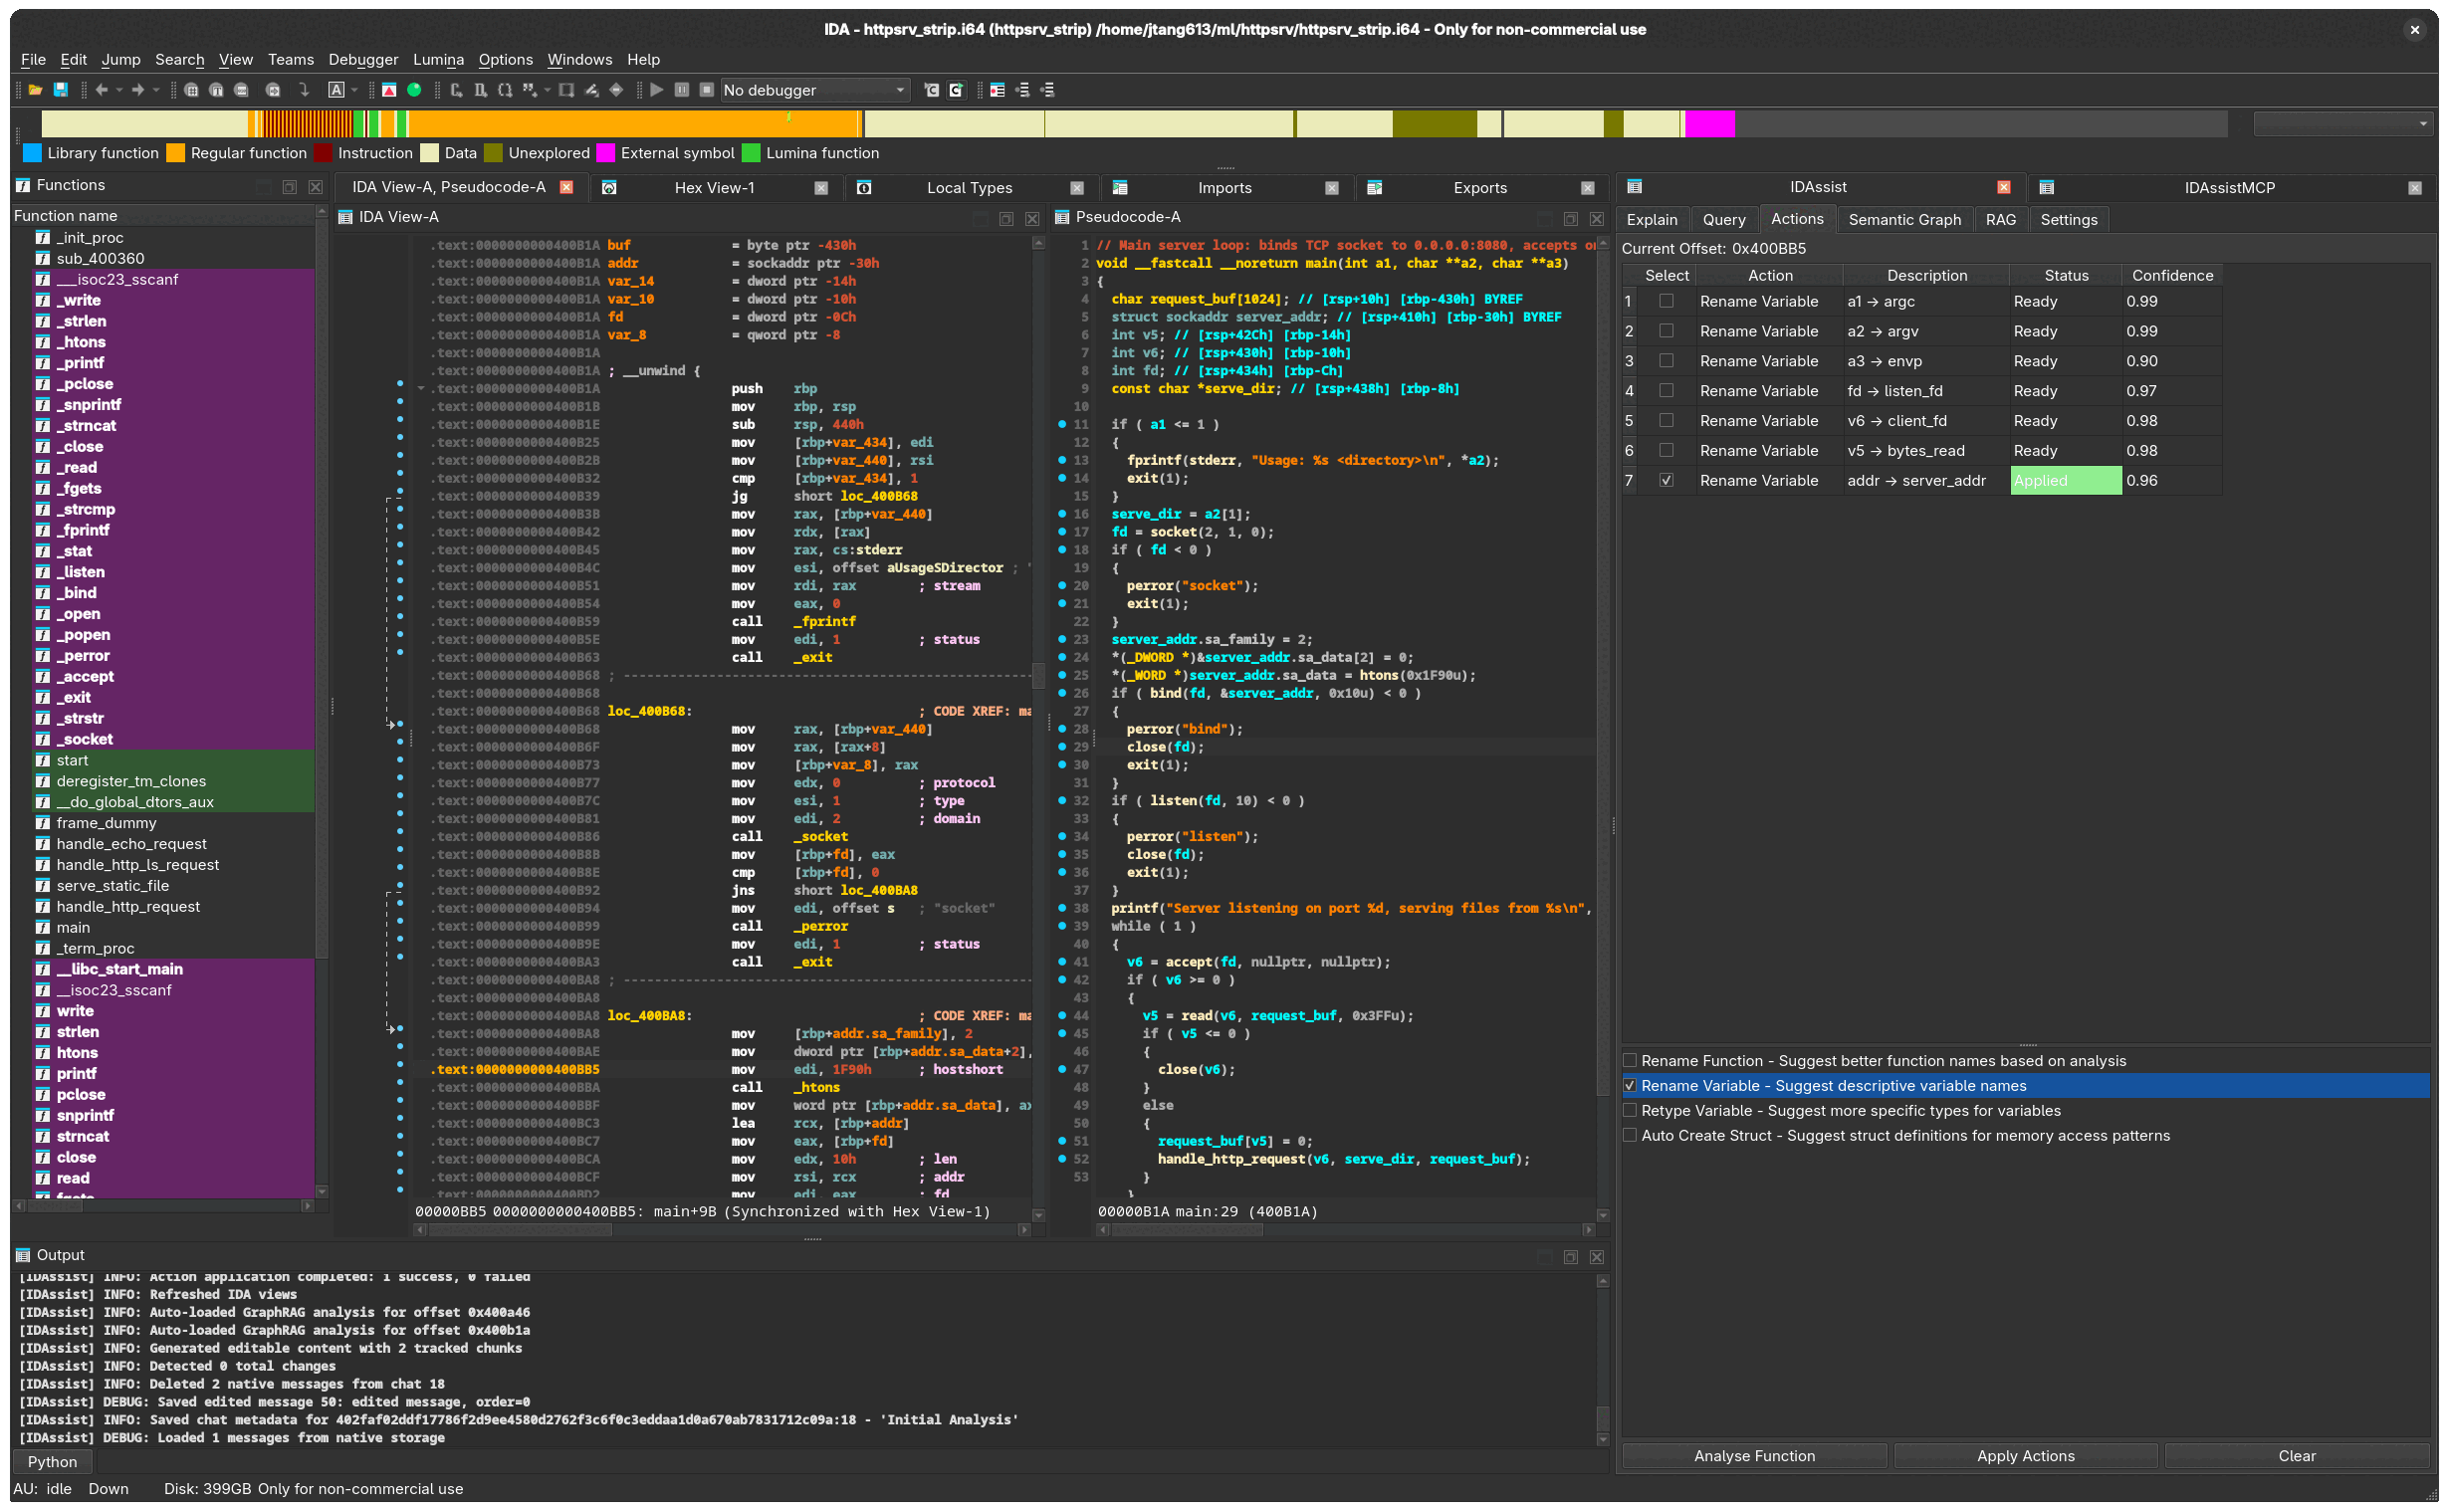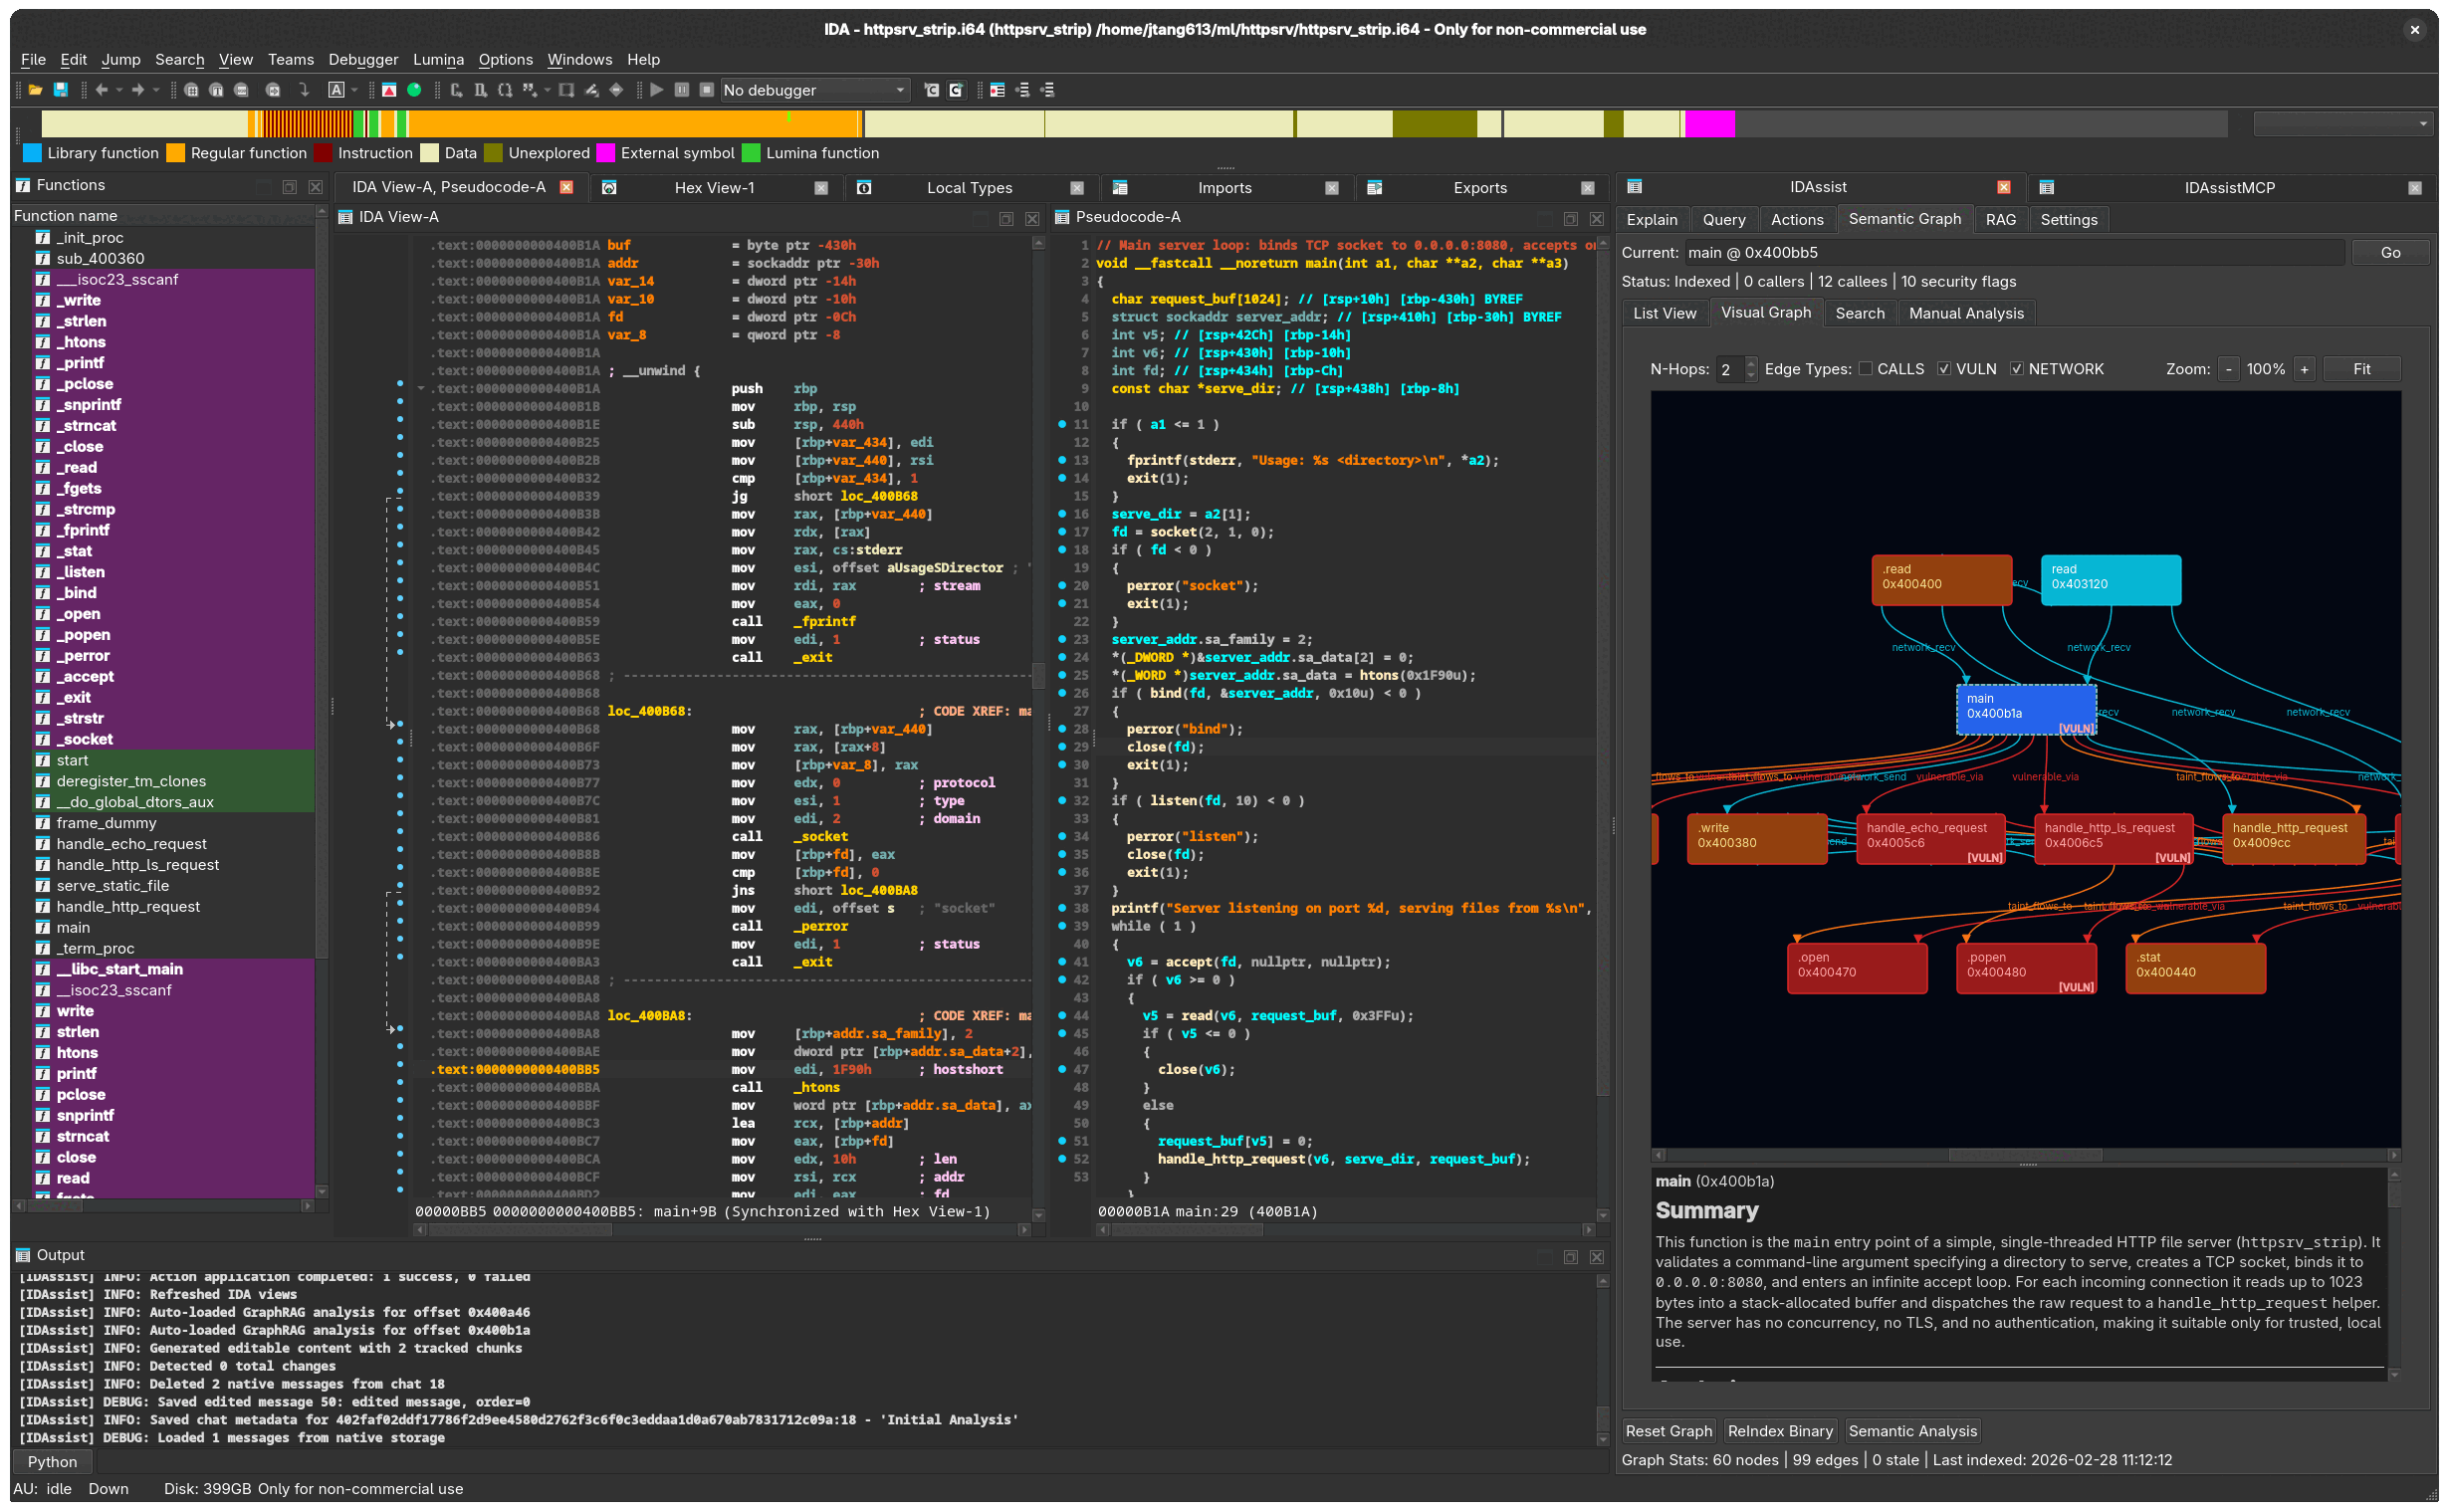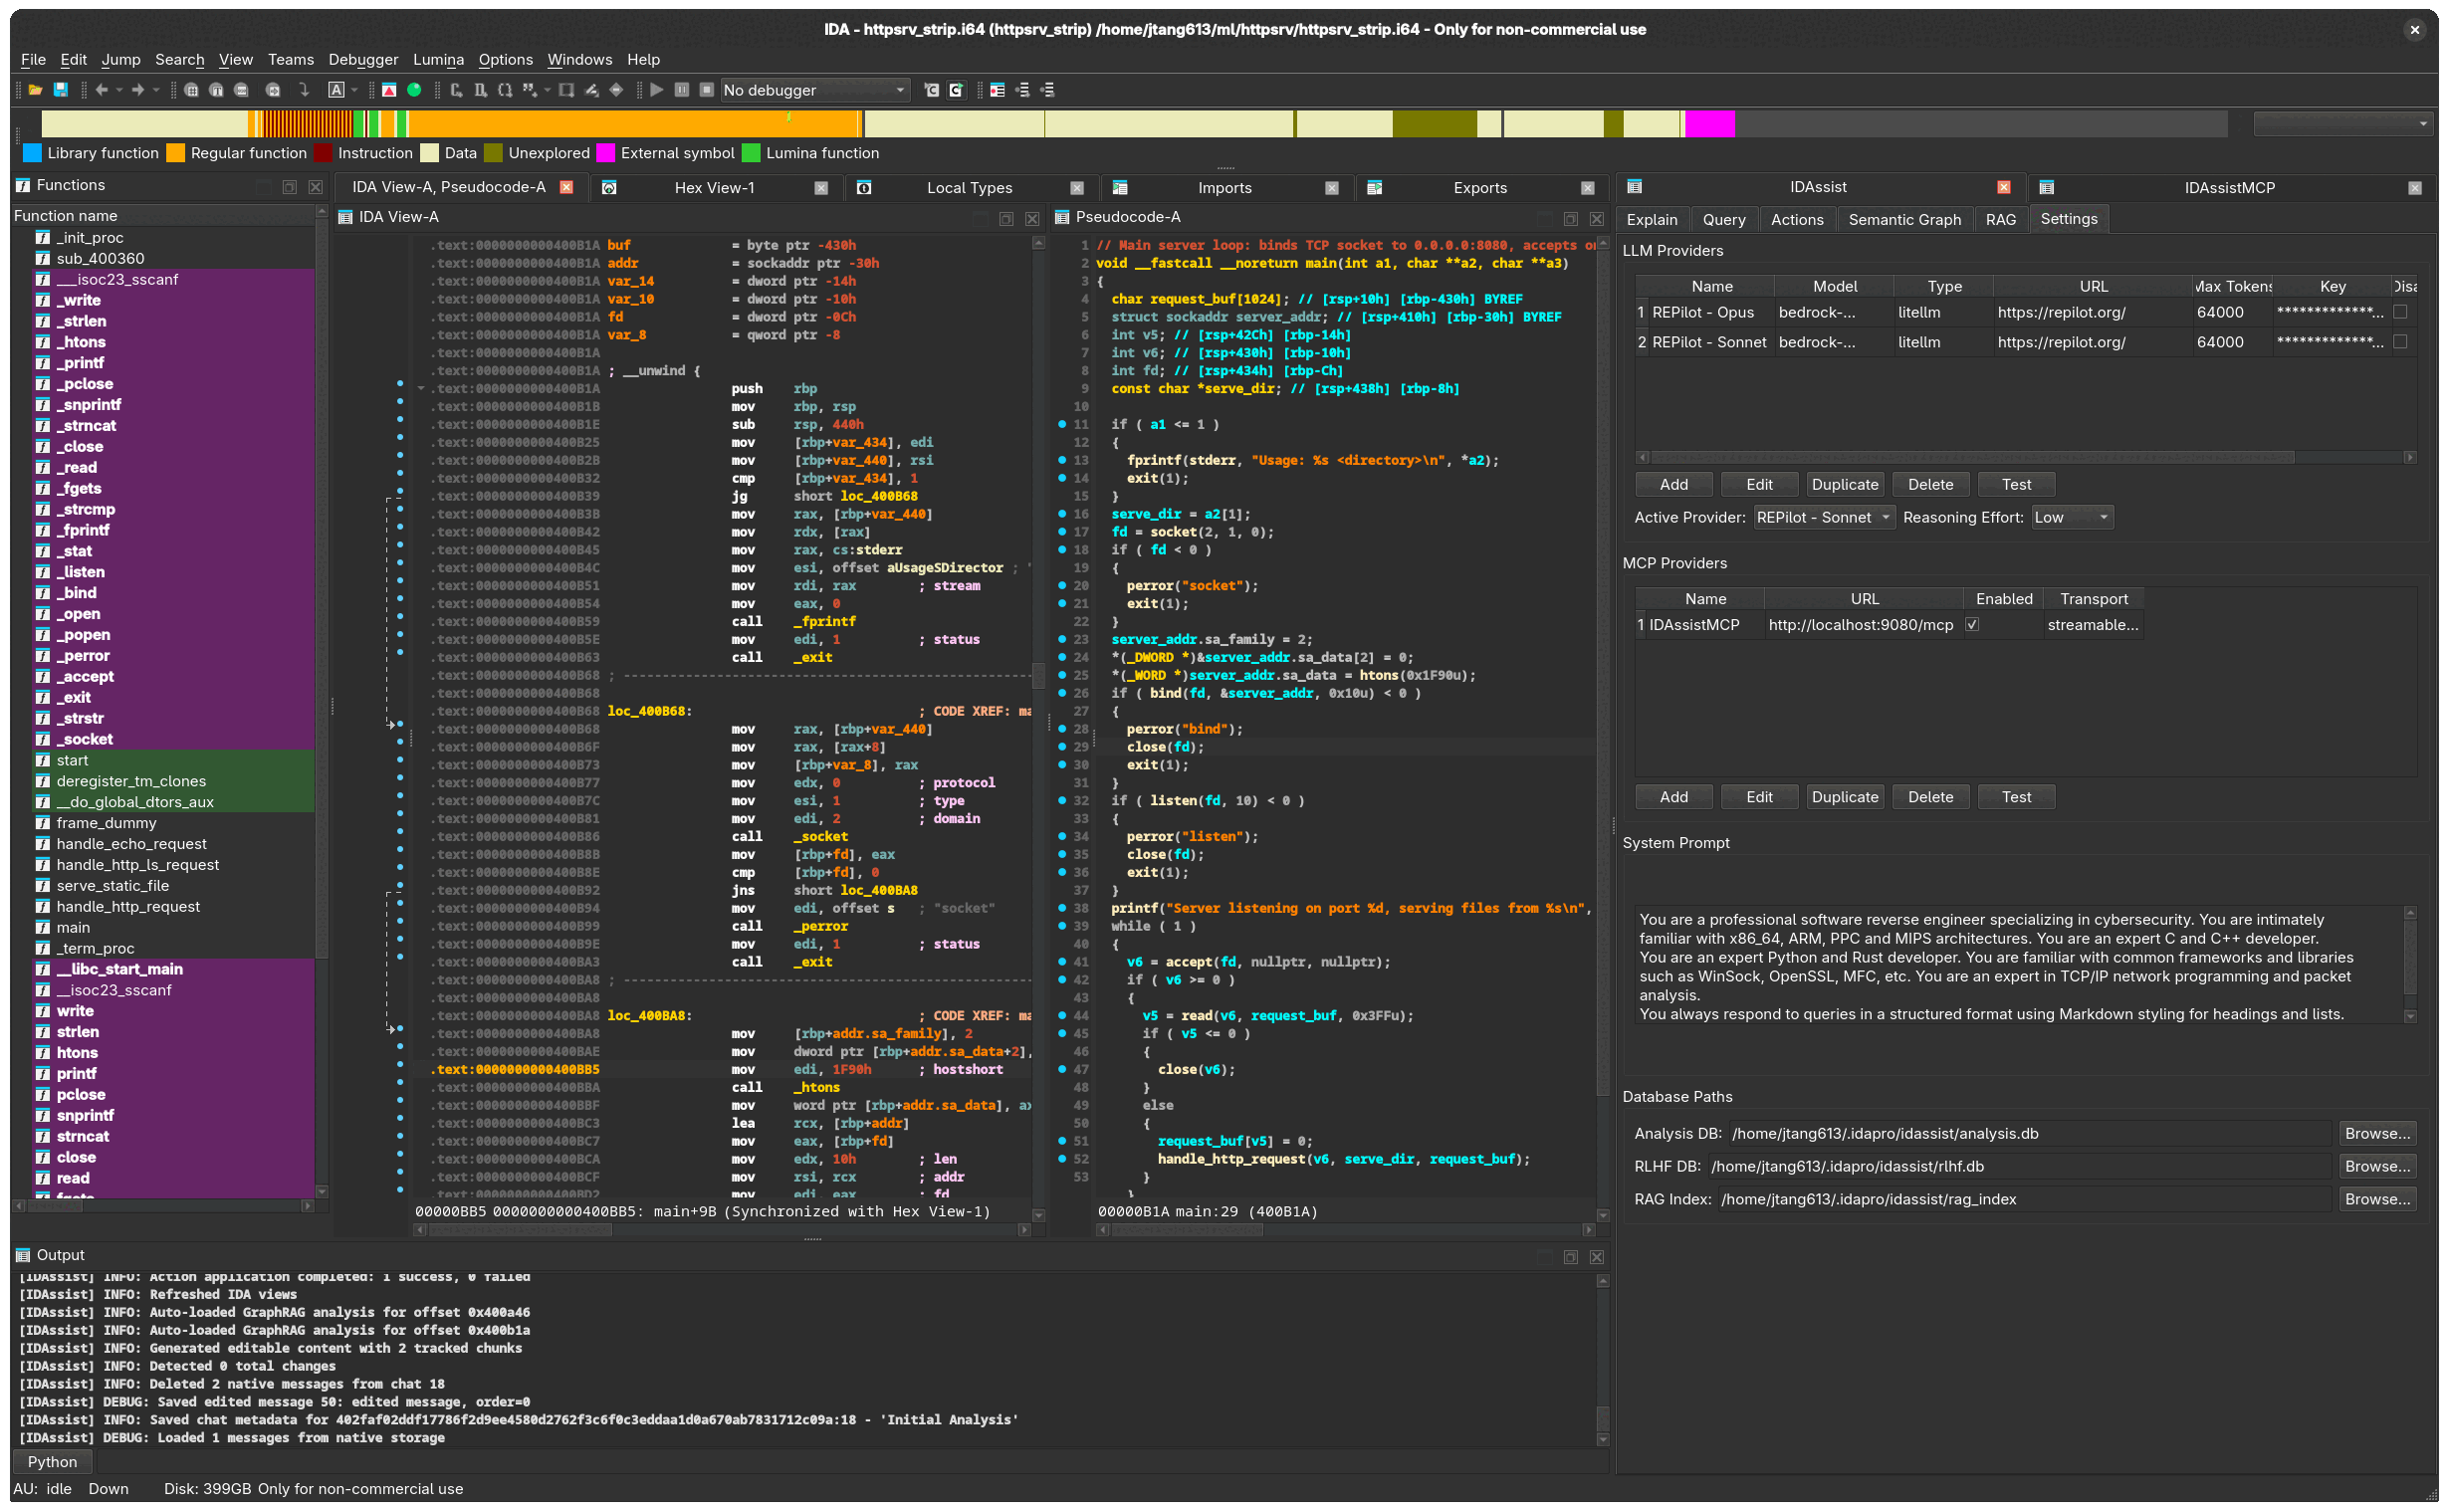 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro

 isecpartners/introspy-ios
Security profiling for blackbox iOS

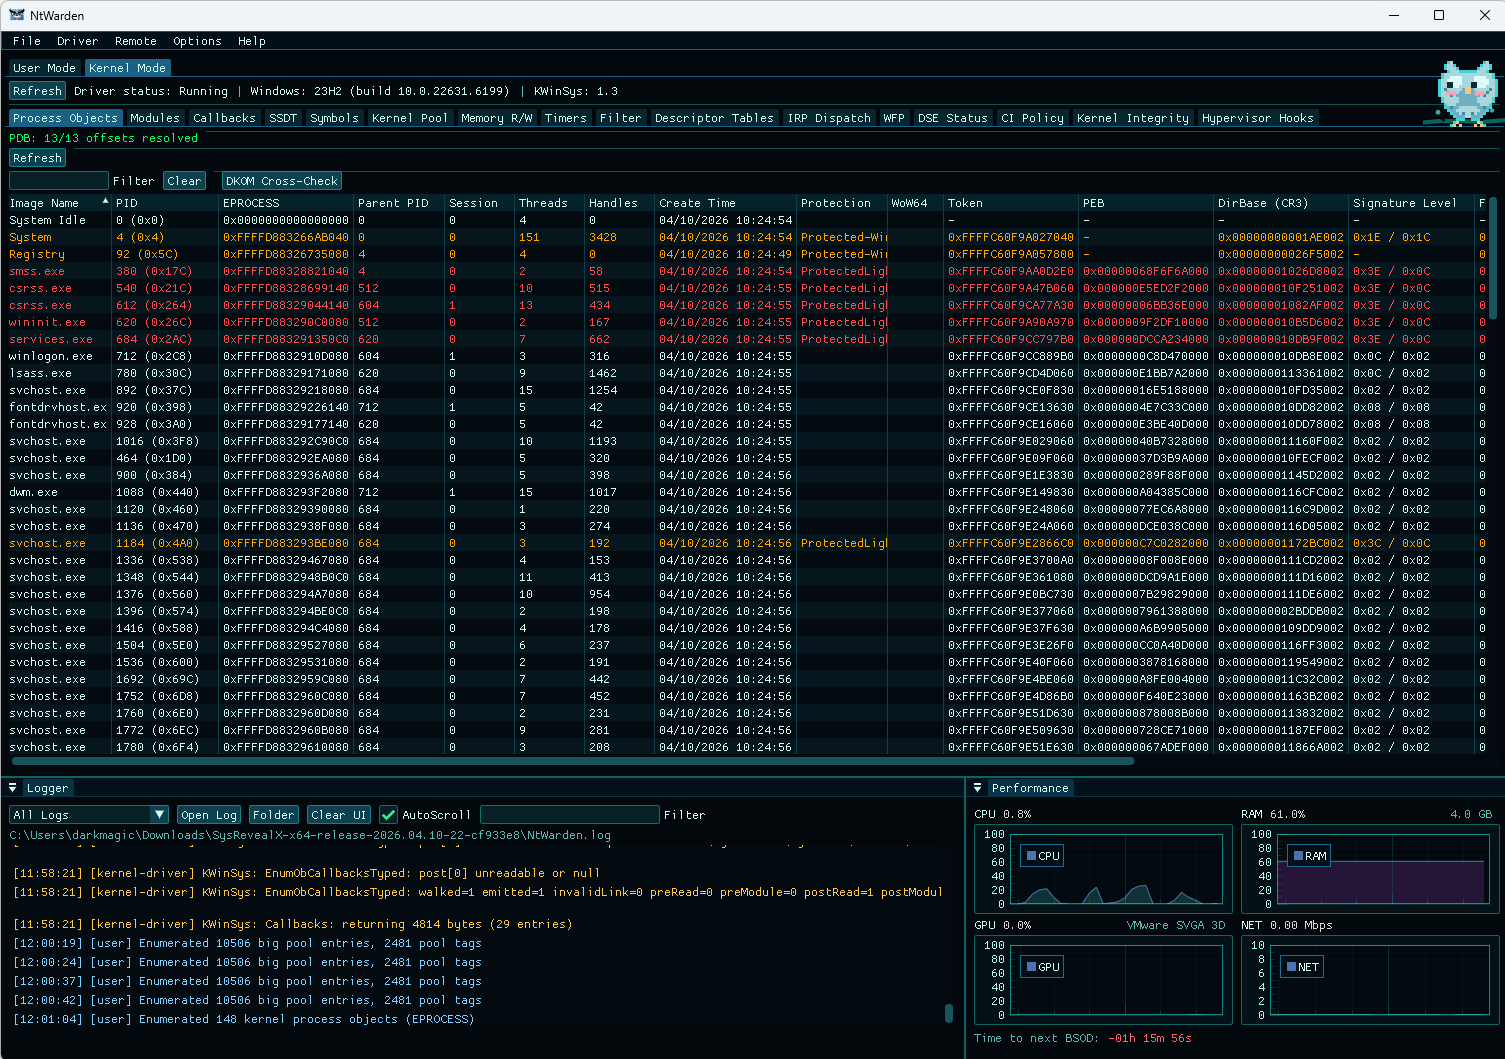 mrt4ntr4/ntwarden
Windows Analysis and Research Toolkit
 tothi/pwn-hisilicon-dvr
Proof-of-concept exploit and vulnerability disclosure for HiSilicon hi3520d DVR/NVR devices. Demonstrates RCE via web interface, backdoor…
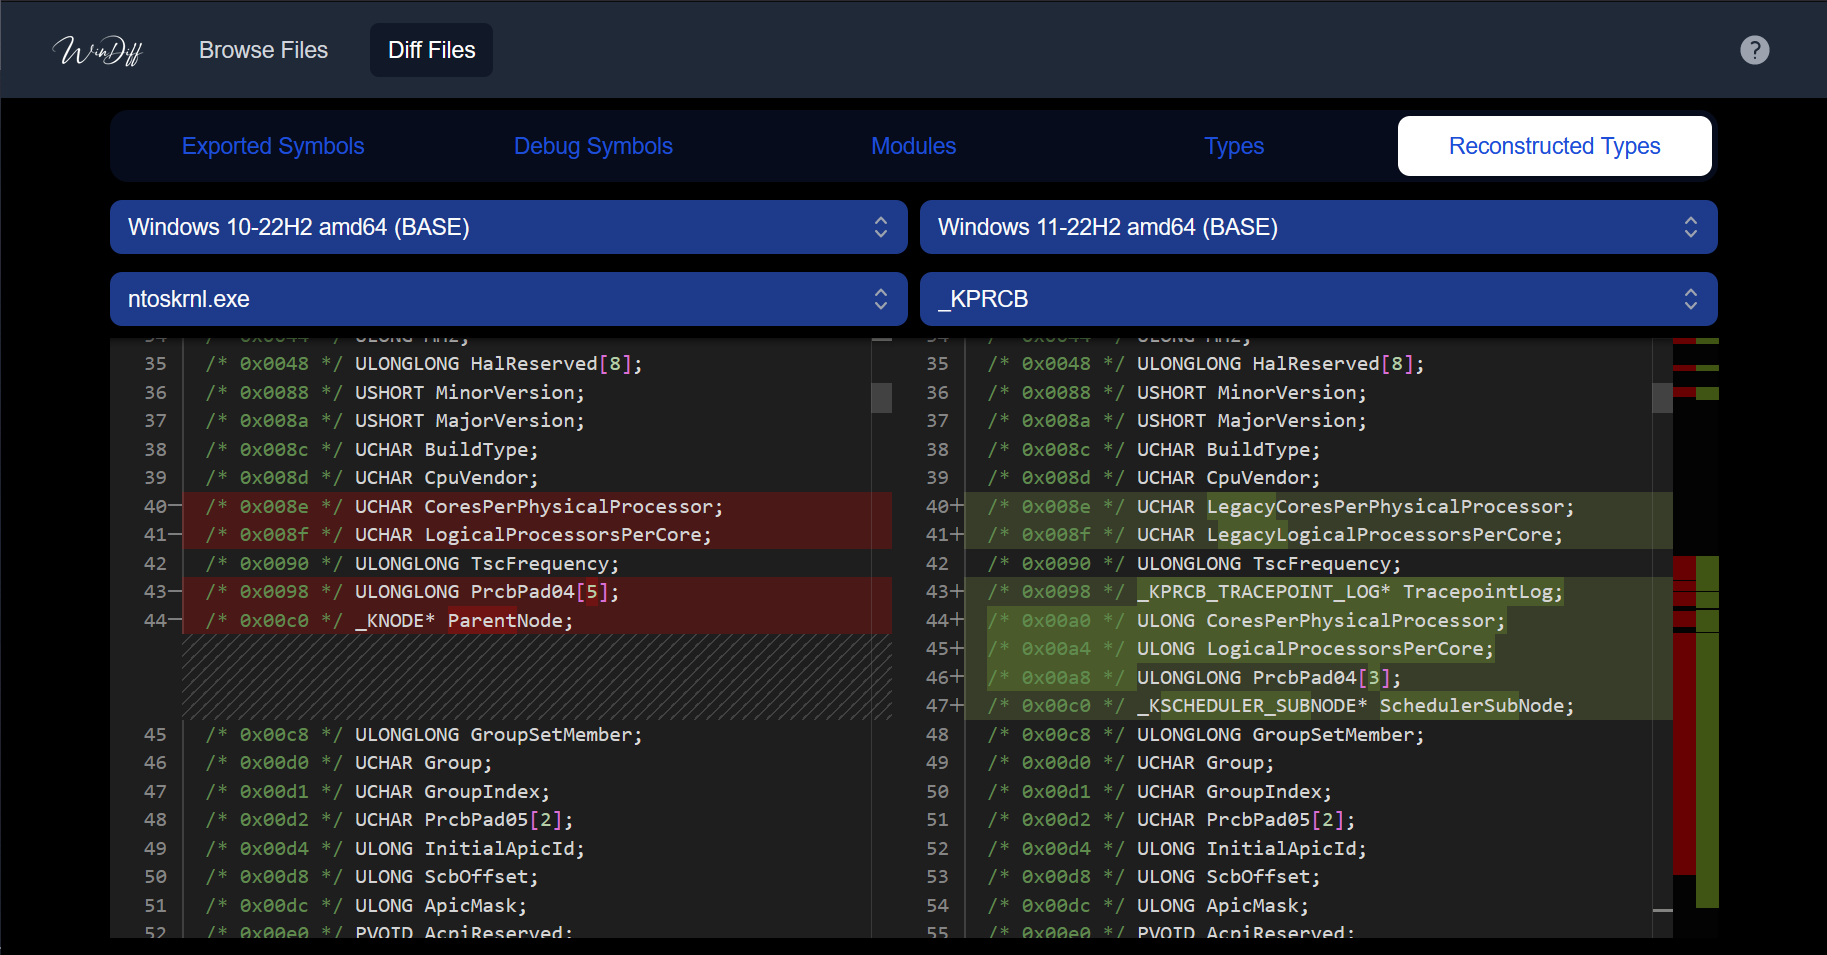 ergrelet/windiff
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.
 netspooky/inhale
A malware analysis and classification tool.
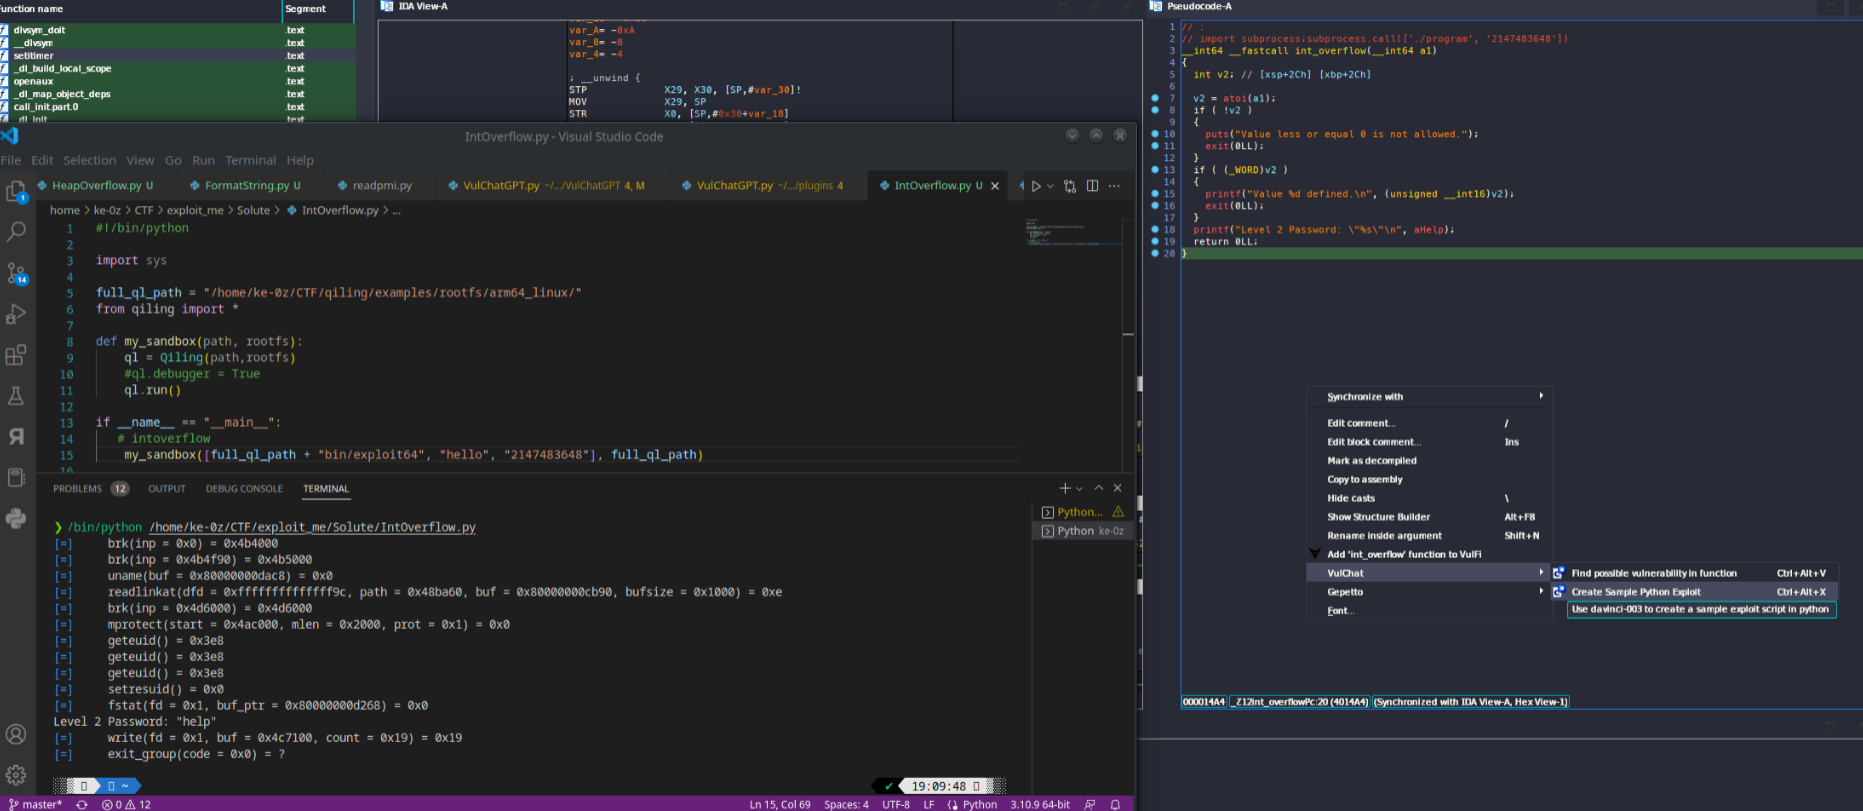 ke0z/binaivulhunter
Use IDA PRO HexRays decompiler with OpenAI(ChatGPT) to find possible vulnerabilities in binaries
 trailofbits/rpcinvestigator
Windows RPC interface discovery and analysis tool with visual endpoint enumeration, PE parsing, symbol resolution, real-time ETW sniffing, and…
 trailofbits/mquire
Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
 hari-prasaanth/thick-client-pentest-checklist
A OWASP Based Checklist With 80+ Test Cases
 hamz-a/frida-android-libbinder
PoC Frida script to view Android libbinder traffic