
Fault-Injection-Finder
 geeoon/fault-injection-finder
Automatically find and execute fault injection attacks
binary-analysisembedded-systems-securityexploitation+5
14
geeoon/fault-injection-finderAutomatically find and execute fault injection attacks
 aquasecurity/binfinder
Find binary files not installed through package manager
 gtgalaxi/electronvulnerableversion
Find Electron Apps Vulnerable to CVE-2023-4863 / CVE-2023-5129
 cdacesec/cve-2022-31902
Proof-of-concept for CVE-2022-31902, a denial-of-service vulnerability in Notepad++ (x86) triggered by the Find All feature on crafted text files,…
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 httpvoid/cve-reverse
Curated list of CVEs that have been reverse-engineered and analyzed, serving as a resource for vulnerability research, exploitation understanding,…

 fboldewin/com-code-helper
Two IDAPython Scripts help you to reconstruct Microsoft COM (Component Object Model) Code
 project-artist/artist
Open-source instrumentation framework for Android apps and Java middleware, modifying code during on-device compilation via the ART compiler.…
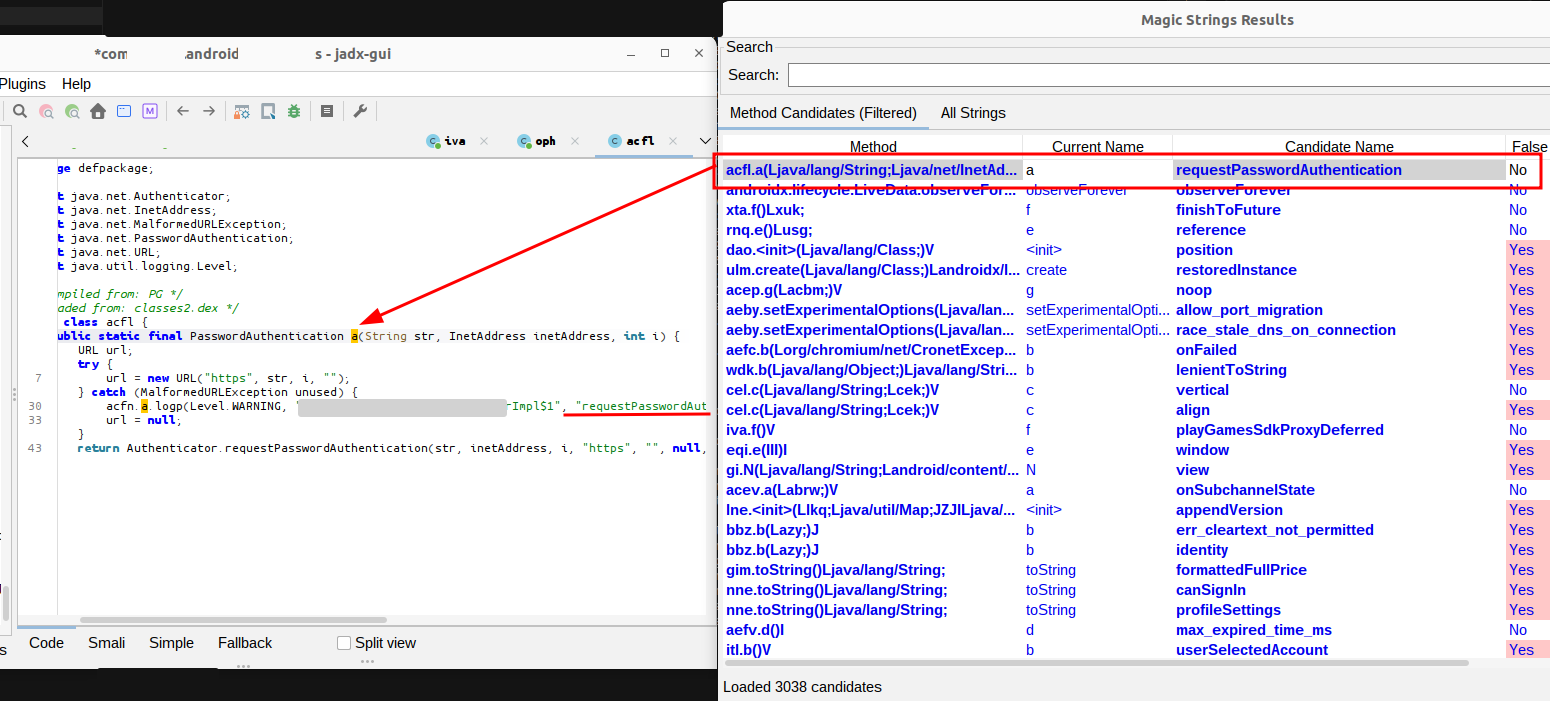 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
 hasherezade/sig_finder
Signature finder (from PE-bear)
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
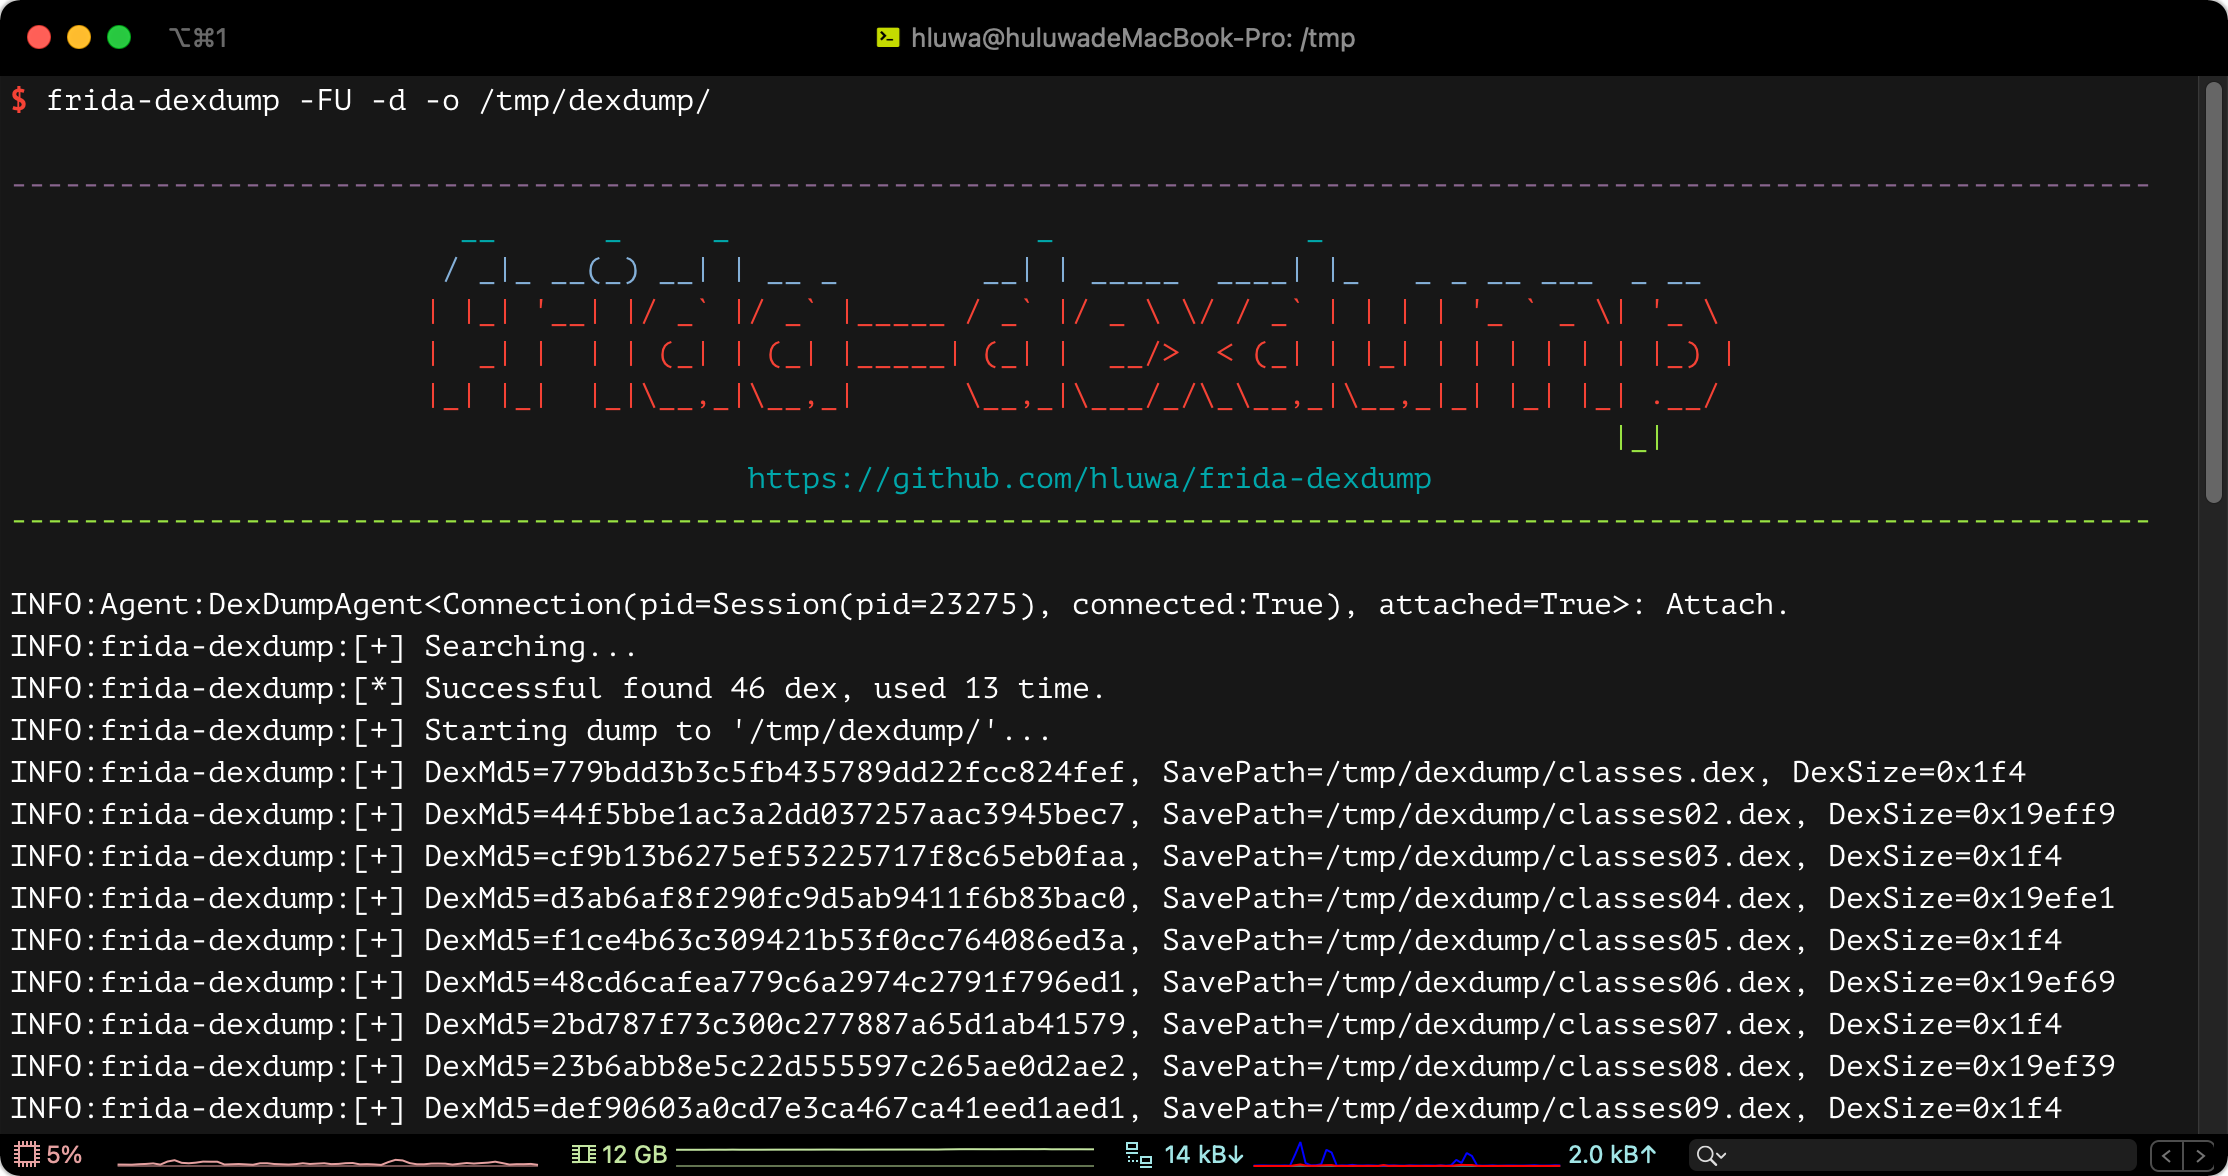 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…