awesome-game-security

Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…

Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…

Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…

Flutter Mobile Application Reverse Engineering Tool

Android APK unpacker that dumps DEX files from running or installed apps on Android 5.0–12 without root, Xposed, or Frida, supporting deep unpacking…

Android Reverse-Engineering Workbench for VS Code

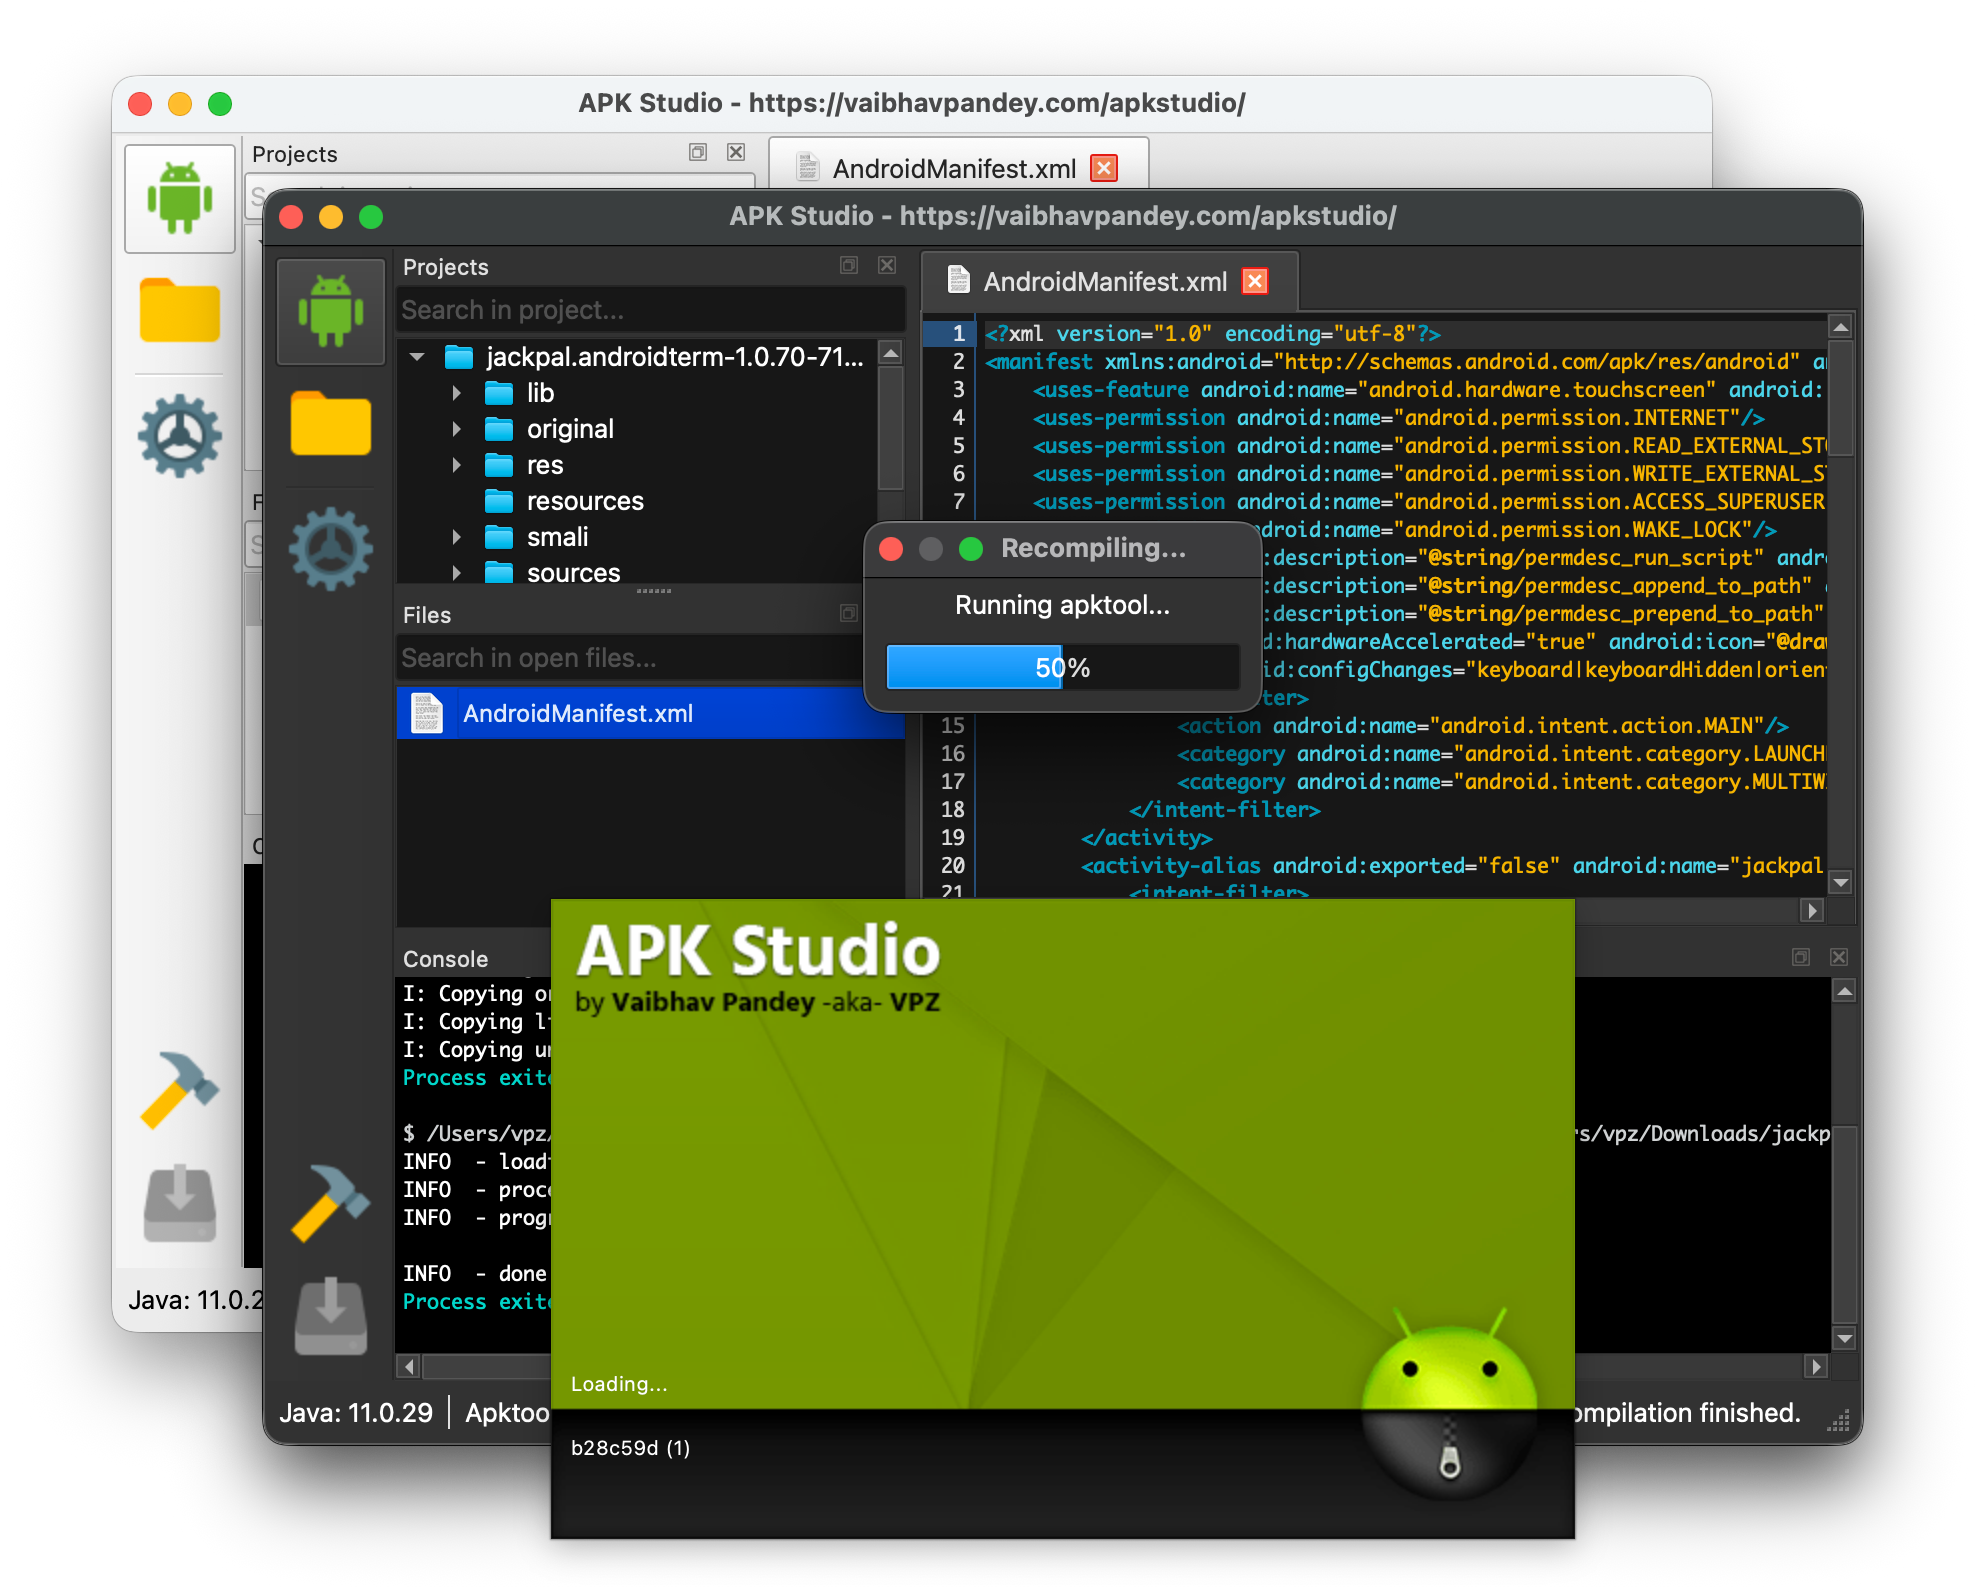
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…

Android virtual machine and deobfuscator

Patching and hooking the Linux kernel with only a stripped Linux kernel image.

GhostLock One-Tap Execution App (CVE-2026-43499)

Radare2 and Frida better together.

Makes reverse engineering Android apps easier, automating repetitive tasks like pulling, decoding, rebuilding and patching an APK.

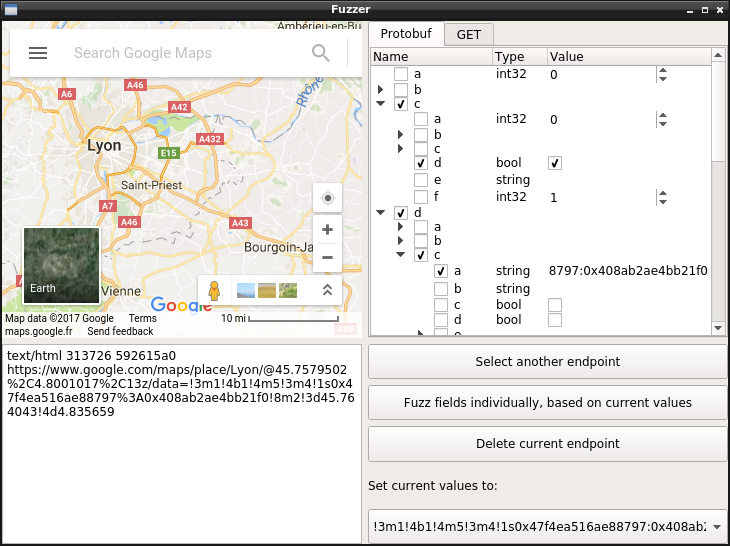
A toolset for reverse engineering and fuzzing Protobuf-based apps

The repo contains a series of challenges for learning Frida for Android Exploitation.

The new bridge between Burp Suite and Frida!

APKinspector is a powerful GUI tool for analysts to analyze the Android applications.

A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices

A Flutter/Dart reverse engineering tool

MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…