
CVE-2026-52885
 v3s9er/cve-2026-52885
Technical analysis of CVE-2026-52885: a TOCTOU race condition in Notepad++ v8.9.6.2 allowing arbitrary command execution via HMAC integrity bypass.…
binary-analysiscode-analysiseducation+3
v3s9er/cve-2026-52885Technical analysis of CVE-2026-52885: a TOCTOU race condition in Notepad++ v8.9.6.2 allowing arbitrary command execution via HMAC integrity bypass.…
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 gmh5225/enigma-
C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…
 trustedsec/ts_llmlib
Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…
 sumitshah00/cve-2025-66628
Technical analysis of CVE-2025-66628, an integer overflow in ImageMagick's TIM parser leading to out-of-bounds reads, with root cause, exploitation…
 enessar/libpng_oss-fuzz
Security research project on fuzzing libpng with OSS-Fuzz. Includes seed corpus analysis, custom read/write fuzzers, and a proof-of-concept exploit…
 nidhihcl/external_expat_2.1.0_cve-2022-43680
C library for stream-oriented XML parsing with a focus on vulnerability analysis and exploitation of CVE-2022-43680, enabling fuzzing and…
 sabecomoeh/cve-2013-3900
Proof-of-concept exploit for CVE-2013-3900, a WinVerifyTrust signature validation vulnerability enabling arbitrary code execution via crafted…
 trinadh465/external_aac_aosp10_r33_cve-2023-21282
Analyzes and patches a specific Android vulnerability (CVE-2023-21282) in the AAC audio codec, providing a patched AOSP10 source tree for security…
 trinadh465/platform_external_libvpx_v1.4.0_cve-2023-5217
C library for VP8/VP9 video encoding and decoding, with a focus on security patching for CVE-2023-5217.
 dshankle/vlc_cve-2021-25804_analysis
In-depth technical analysis of CVE-2021-25804, a VLC AVI parser vulnerability. Includes root cause, patch diff, and exploitation primitives for…
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 mistymntncop/cve-2023-4863
Proof-of-concept for CVE-2023-4863, a heap buffer overflow in WebP image decoding. Demonstrates the code_lengths trigger mechanism discovered by…
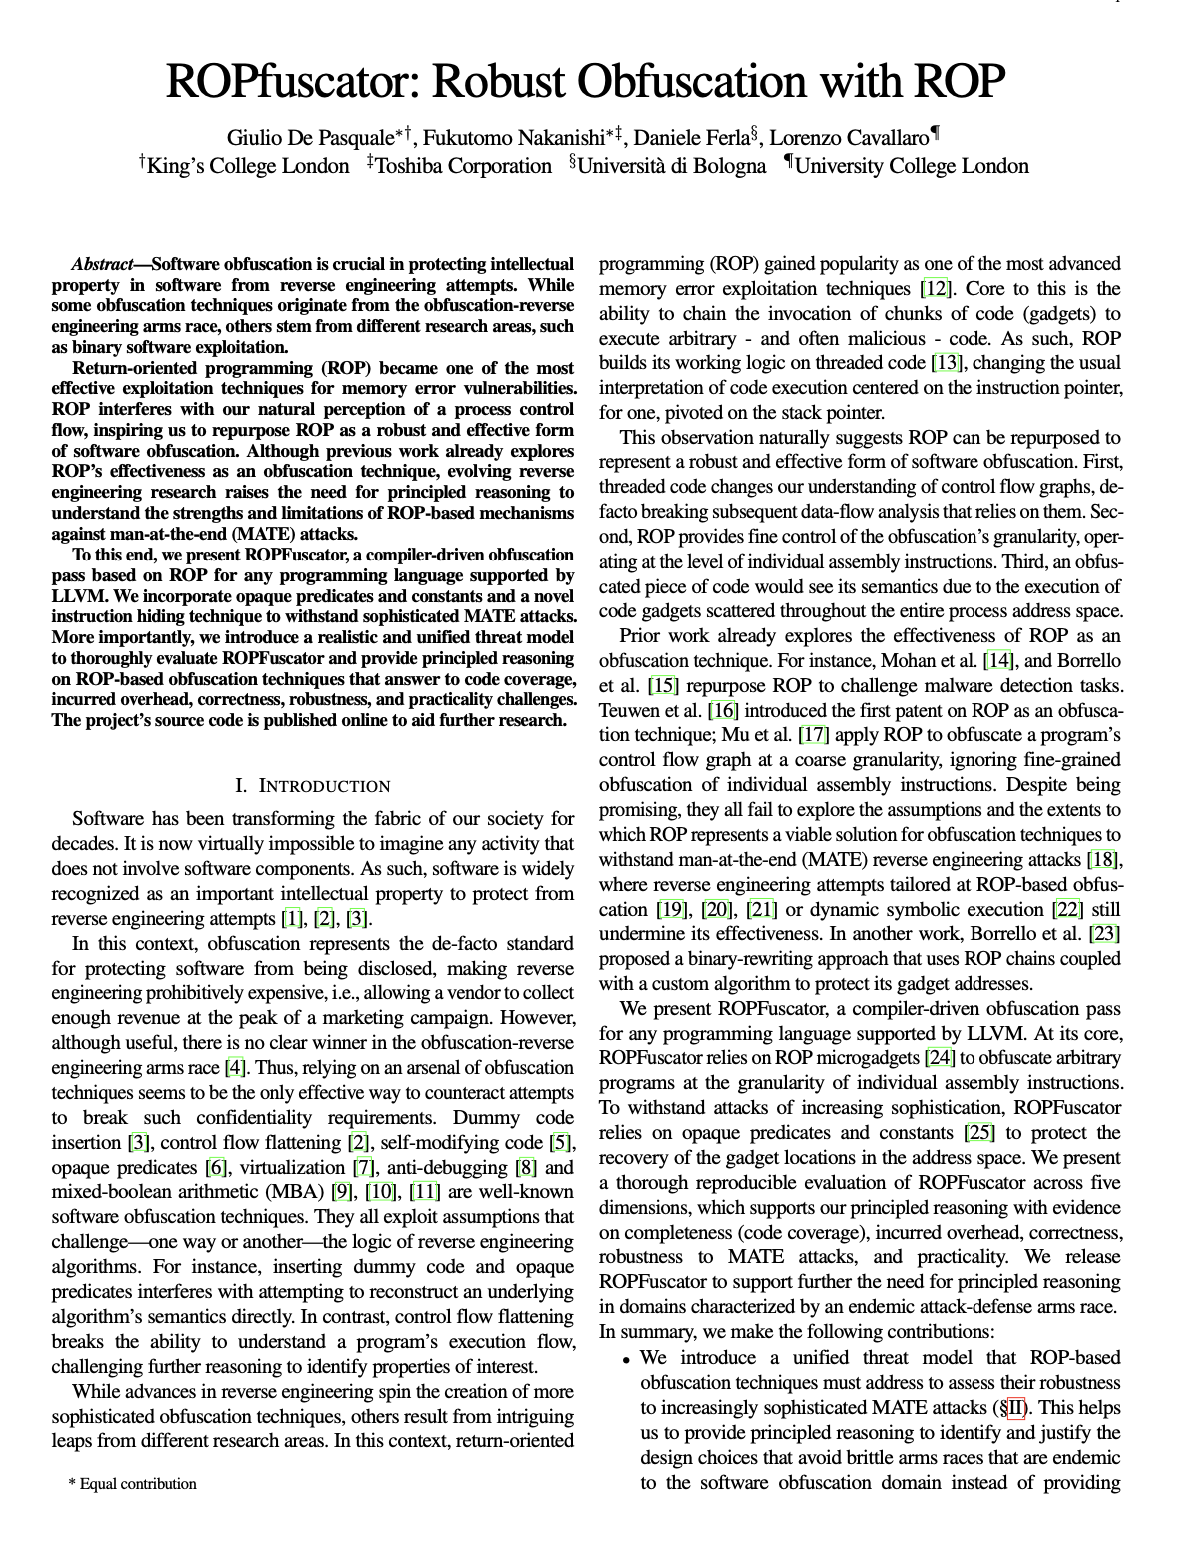 ropfuscator/ropfuscator
ROPfuscator is a fine-grained code obfuscation framework for C/C++ programs using ROP (return-oriented programming).
 thebabush/llvm-jutsu
Anti-LLM obfuscation via finger counting
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 peterhackz/zyrox
Zyrox: LLVM based, compile-time obfuscator plugin.