

replica
 reb311ion/replica
Ghidra plugin that enhances reverse engineering by fixing missed disassembly, detecting functions, labeling crypto constants, and renaming functions…
binary-analysiscryptographymalware-analysis+2
315
reb311ion/replicaGhidra plugin that enhances reverse engineering by fixing missed disassembly, detecting functions, labeling crypto constants, and renaming functions…
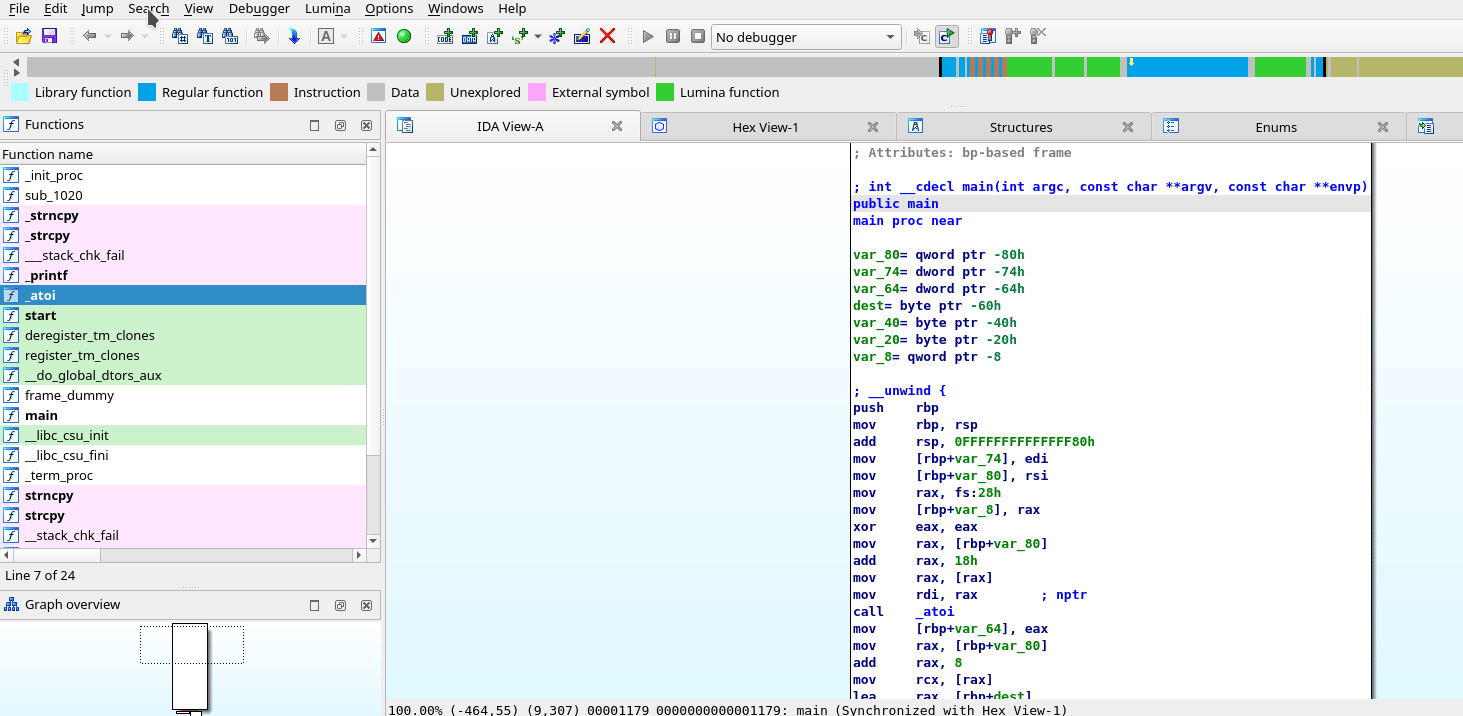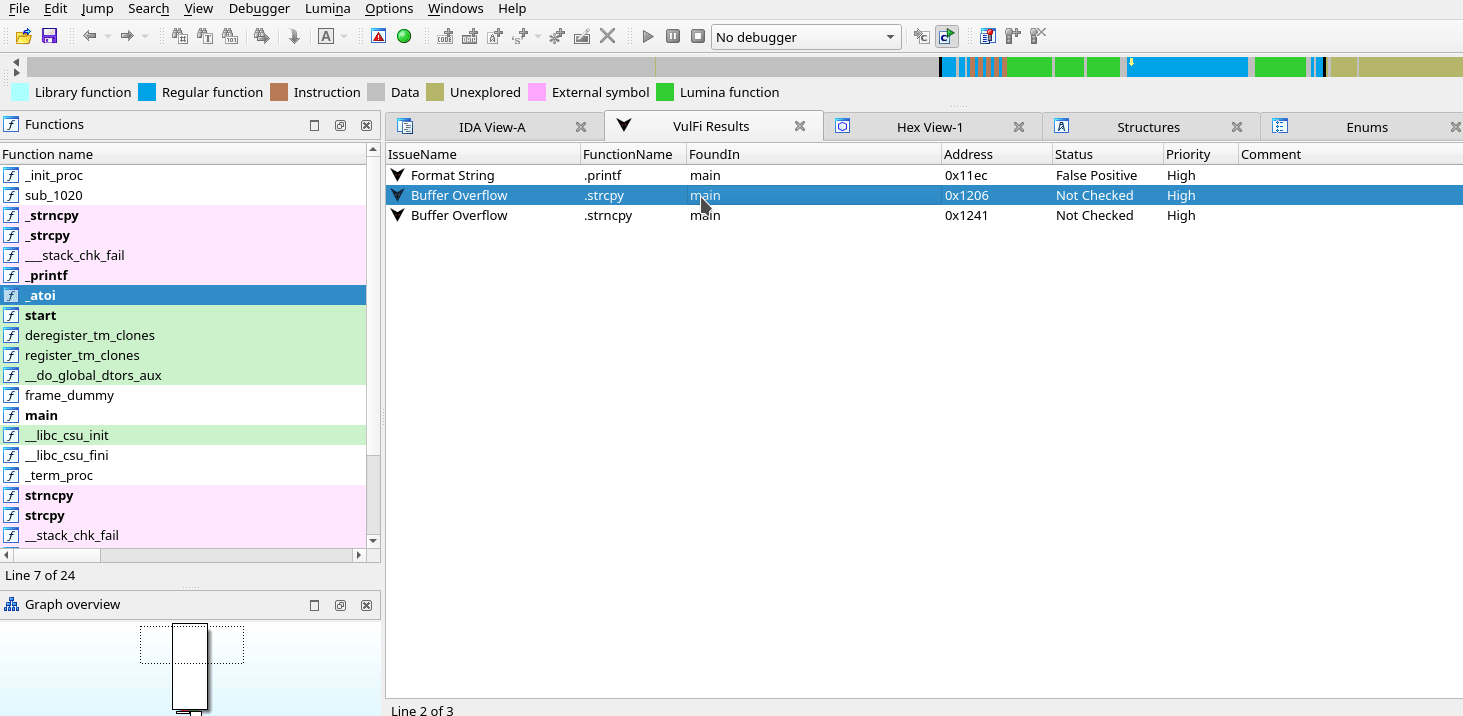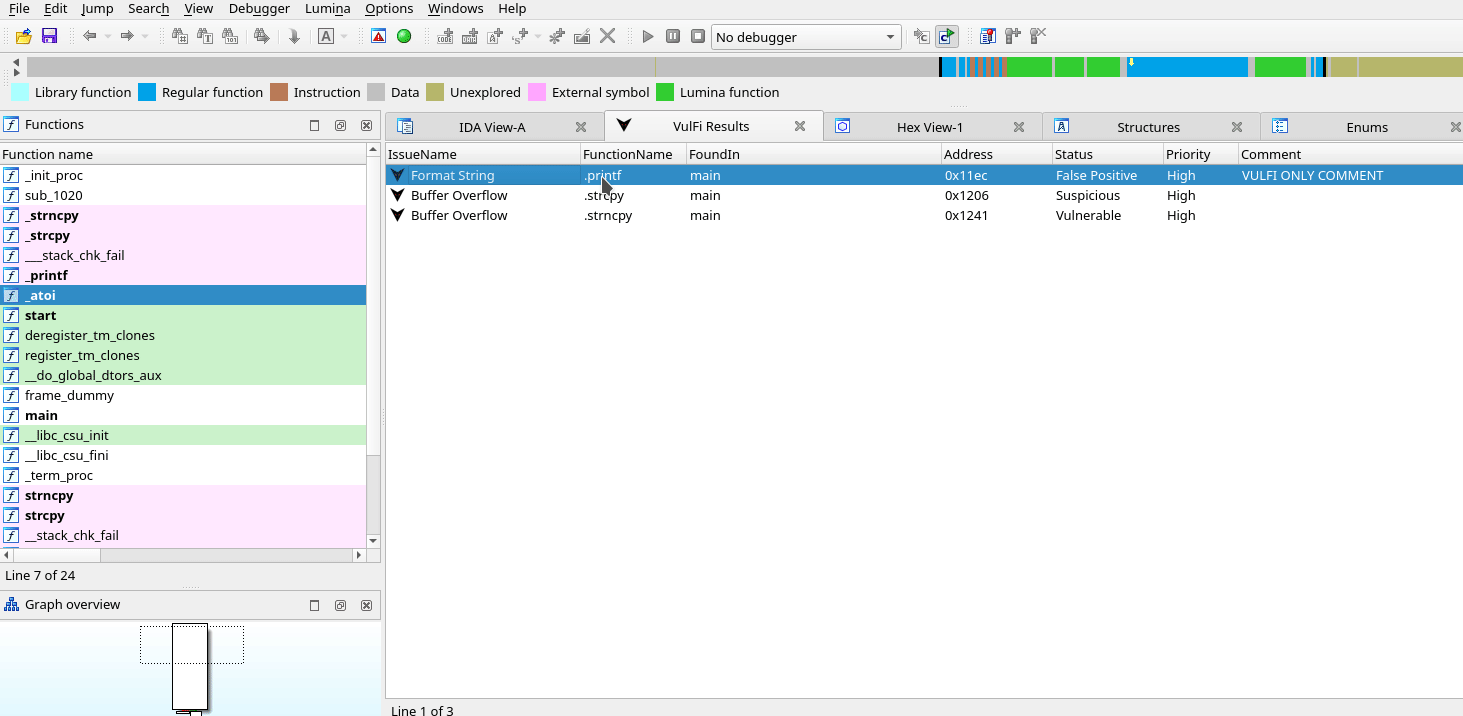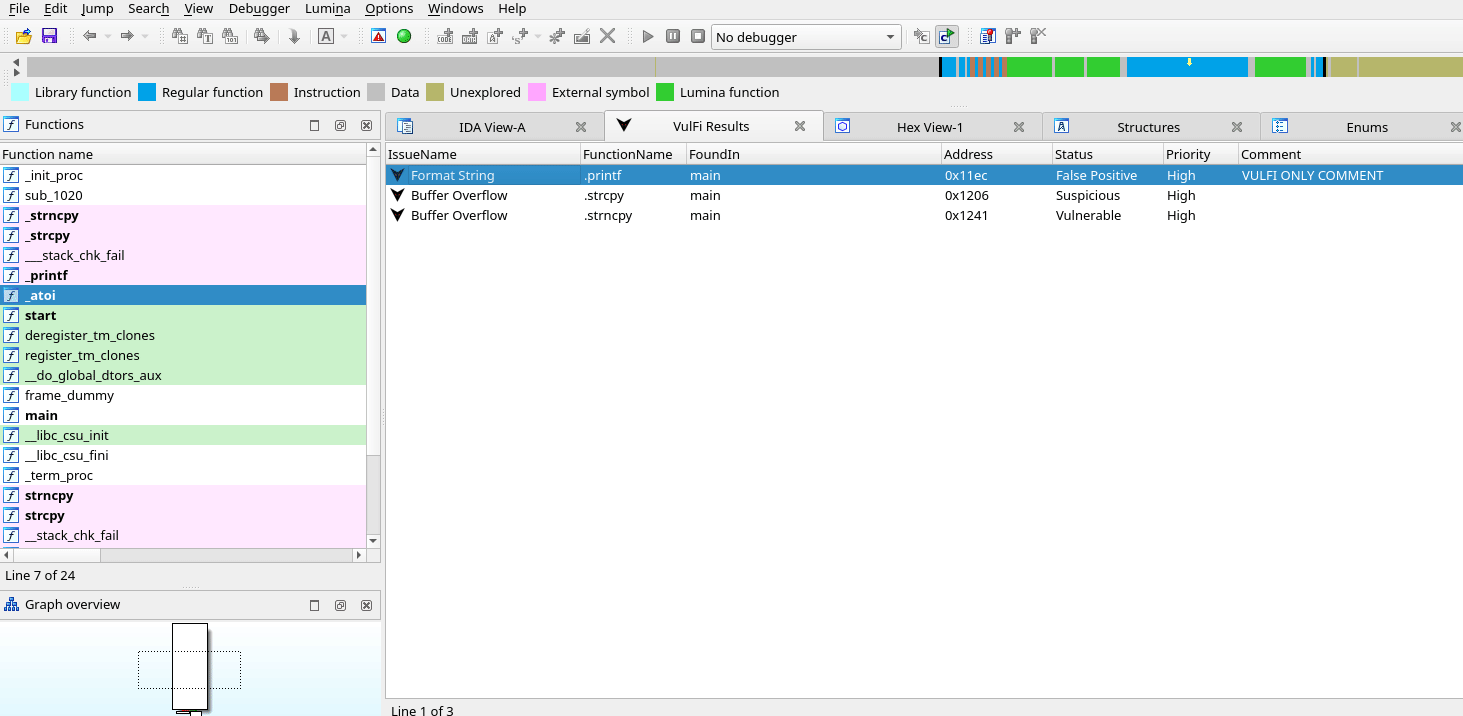 accenture/vulfi
IDA Pro plugin for query based searching within the binary useful mainly for vulnerability research.
 colton1skees/dna
LLVM based static binary analysis framework
 pagalaxylab/unifuzzer
A fuzzing tool for closed-source binaries based on Unicorn and LibFuzzer
 cerbersec/ares
Project Ares is a Proof of Concept (PoC) loader written in C/C++ based on the Transacted Hollowing technique
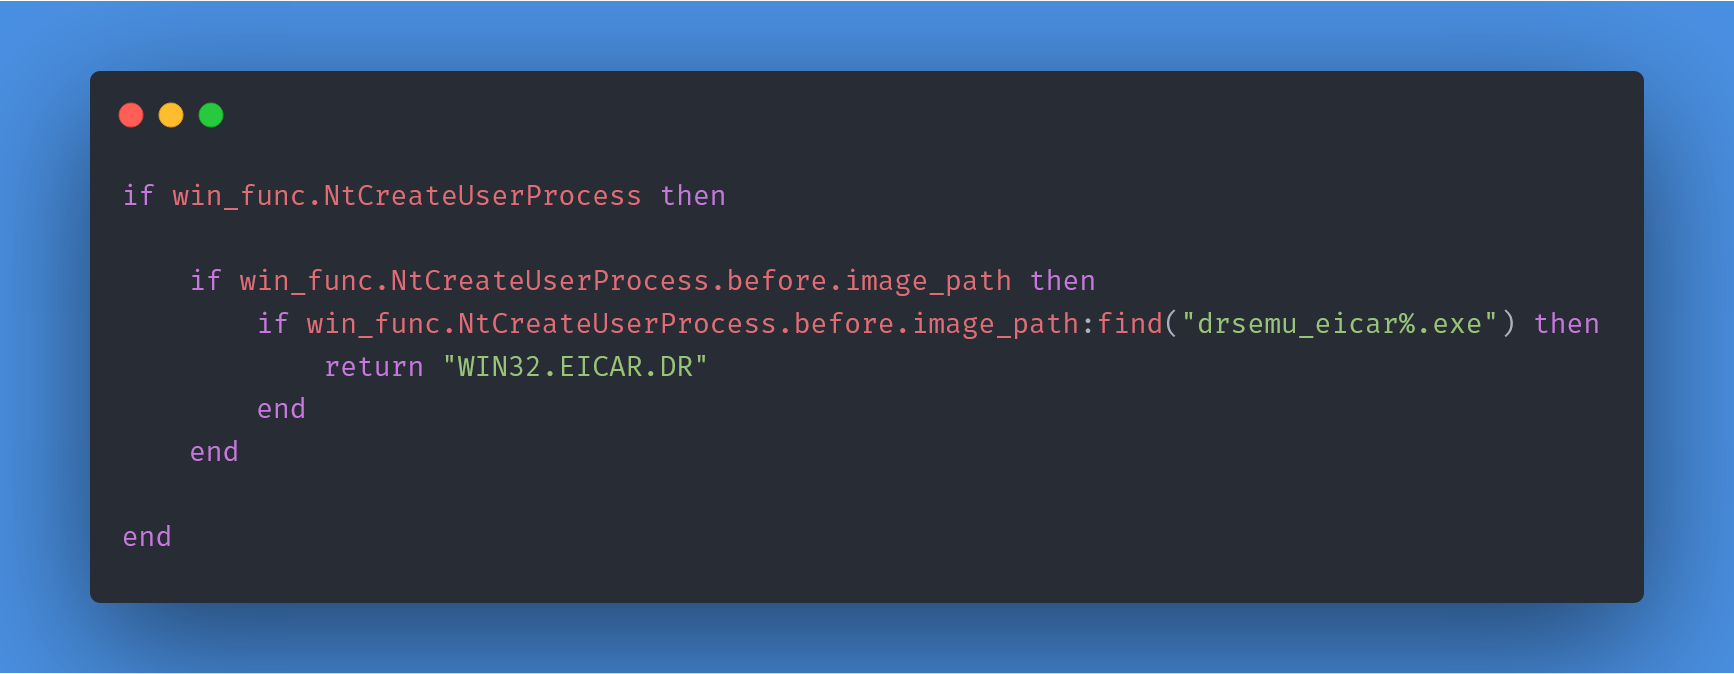 secrary/drsemu
DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
 nteseyes/pylane
An python vm injector with debug tools, based on gdb.
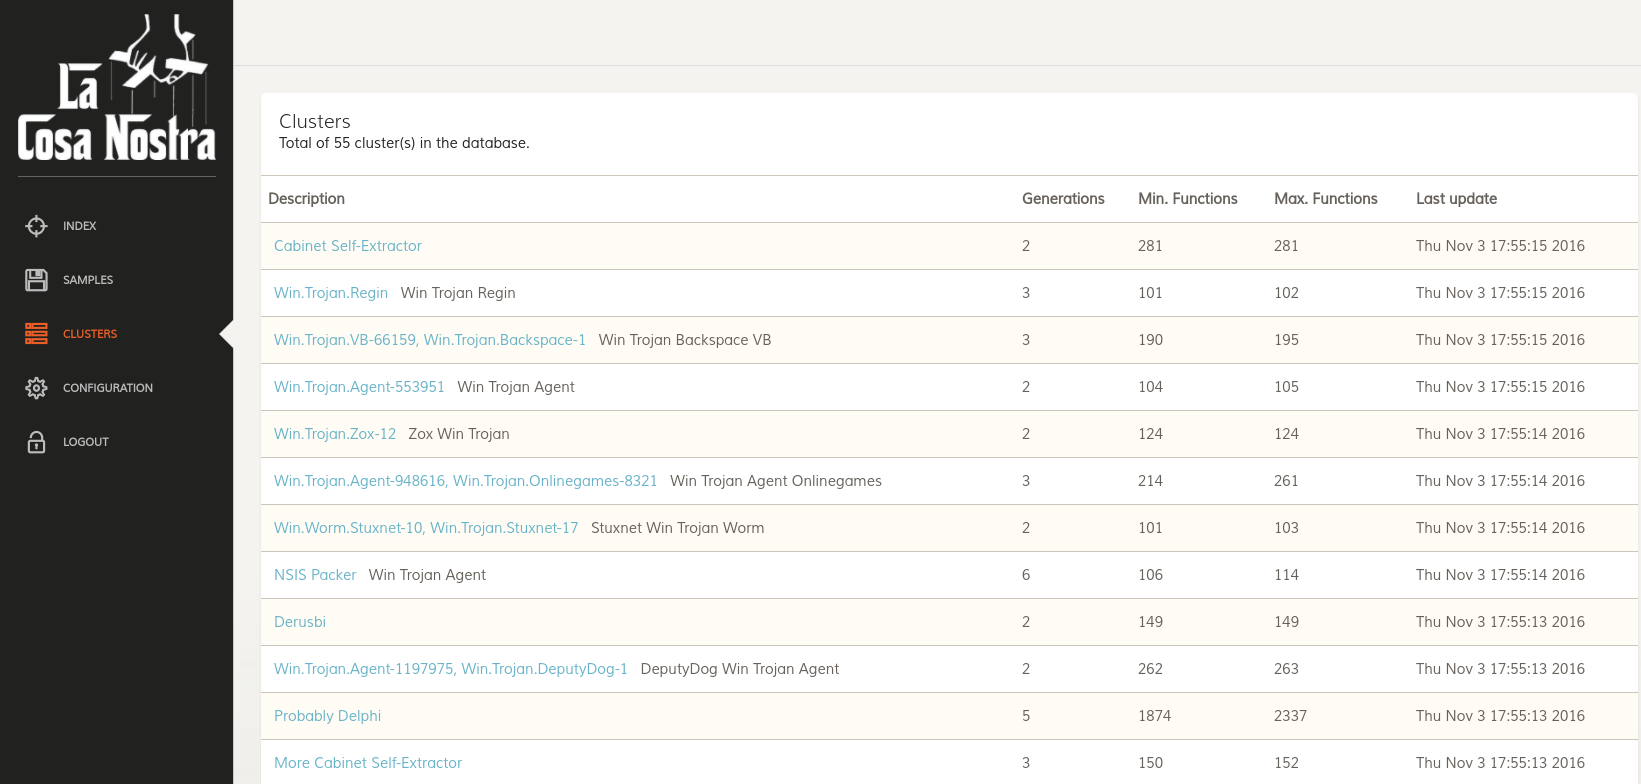 joxeankoret/cosa-nostra
Cosa Nostra, a FOSS graph based malware clusterization toolkit.
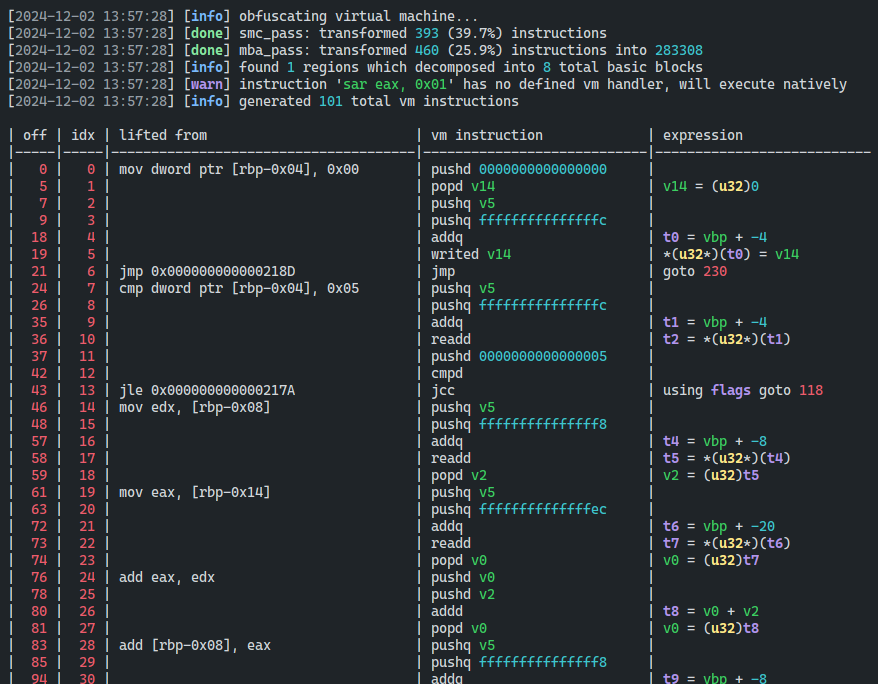 dmaivel/covirt
An x86-64 code virtualizer for VM based obfuscation
 oalabs/frida-extract
Frida.re based RunPE (and MapViewOfSection) extraction tool
 hari-prasaanth/thick-client-pentest-checklist
A OWASP Based Checklist With 80+ Test Cases
 airbus-seclab/gustave
GUSTAVE is a fuzzing platform for embedded OS kernels. It is based on QEMU and AFL (and all of its forkserver siblings). It allows to fuzz OS kernels…
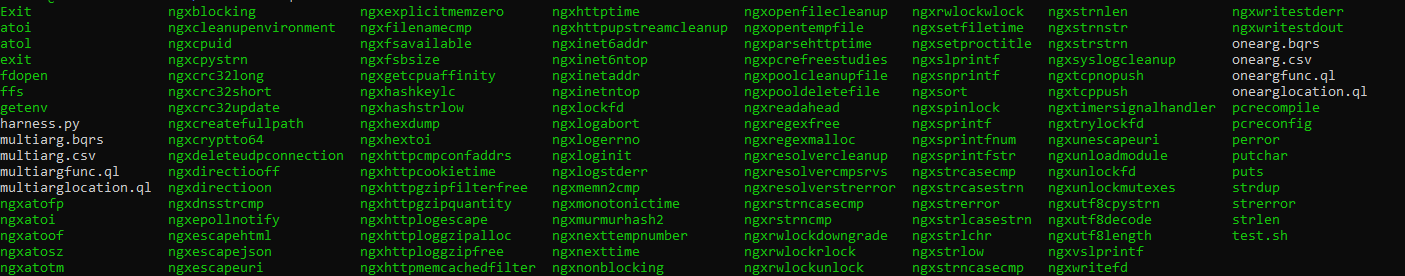 parikhakshat/autoharness
A tool that automatically creates fuzzing harnesses based on a library
 v-p-b/pecloakcapstone
Platform independent peCloak fork based on Capstone
 impalabs/hyperpom
AArch64 fuzzer based on the Apple Silicon hypervisor
 peterhackz/zyrox
Zyrox: LLVM based, compile-time obfuscator plugin.
 baiduxlab/sgxray
Automated reasoning tool based on the SMACK verifier that detects SGX enclave bugs from trusted boundary violations, including invalid pointer…