
binja_arch_ref
 nccgroup/binja_arch_ref
A simple Binary Ninja plugin to display a cheat sheet with information about the current architecture
binary-analysisembedded-systems-securityreverse-engineering
nccgroup/binja_arch_refA simple Binary Ninja plugin to display a cheat sheet with information about the current architecture
 llgsjsm/cve-2026-3008
Technical analysis and proof-of-concept for CVE-2026-3008, a format string injection in Notepad++ 8.9.3 via nativeLang.xml, enabling denial of…

 waleedassar/cve-2021-1699
POC for CVE-2021-1699
 waleedassar/cve-2022-24483
POC For CVE-2022-24483
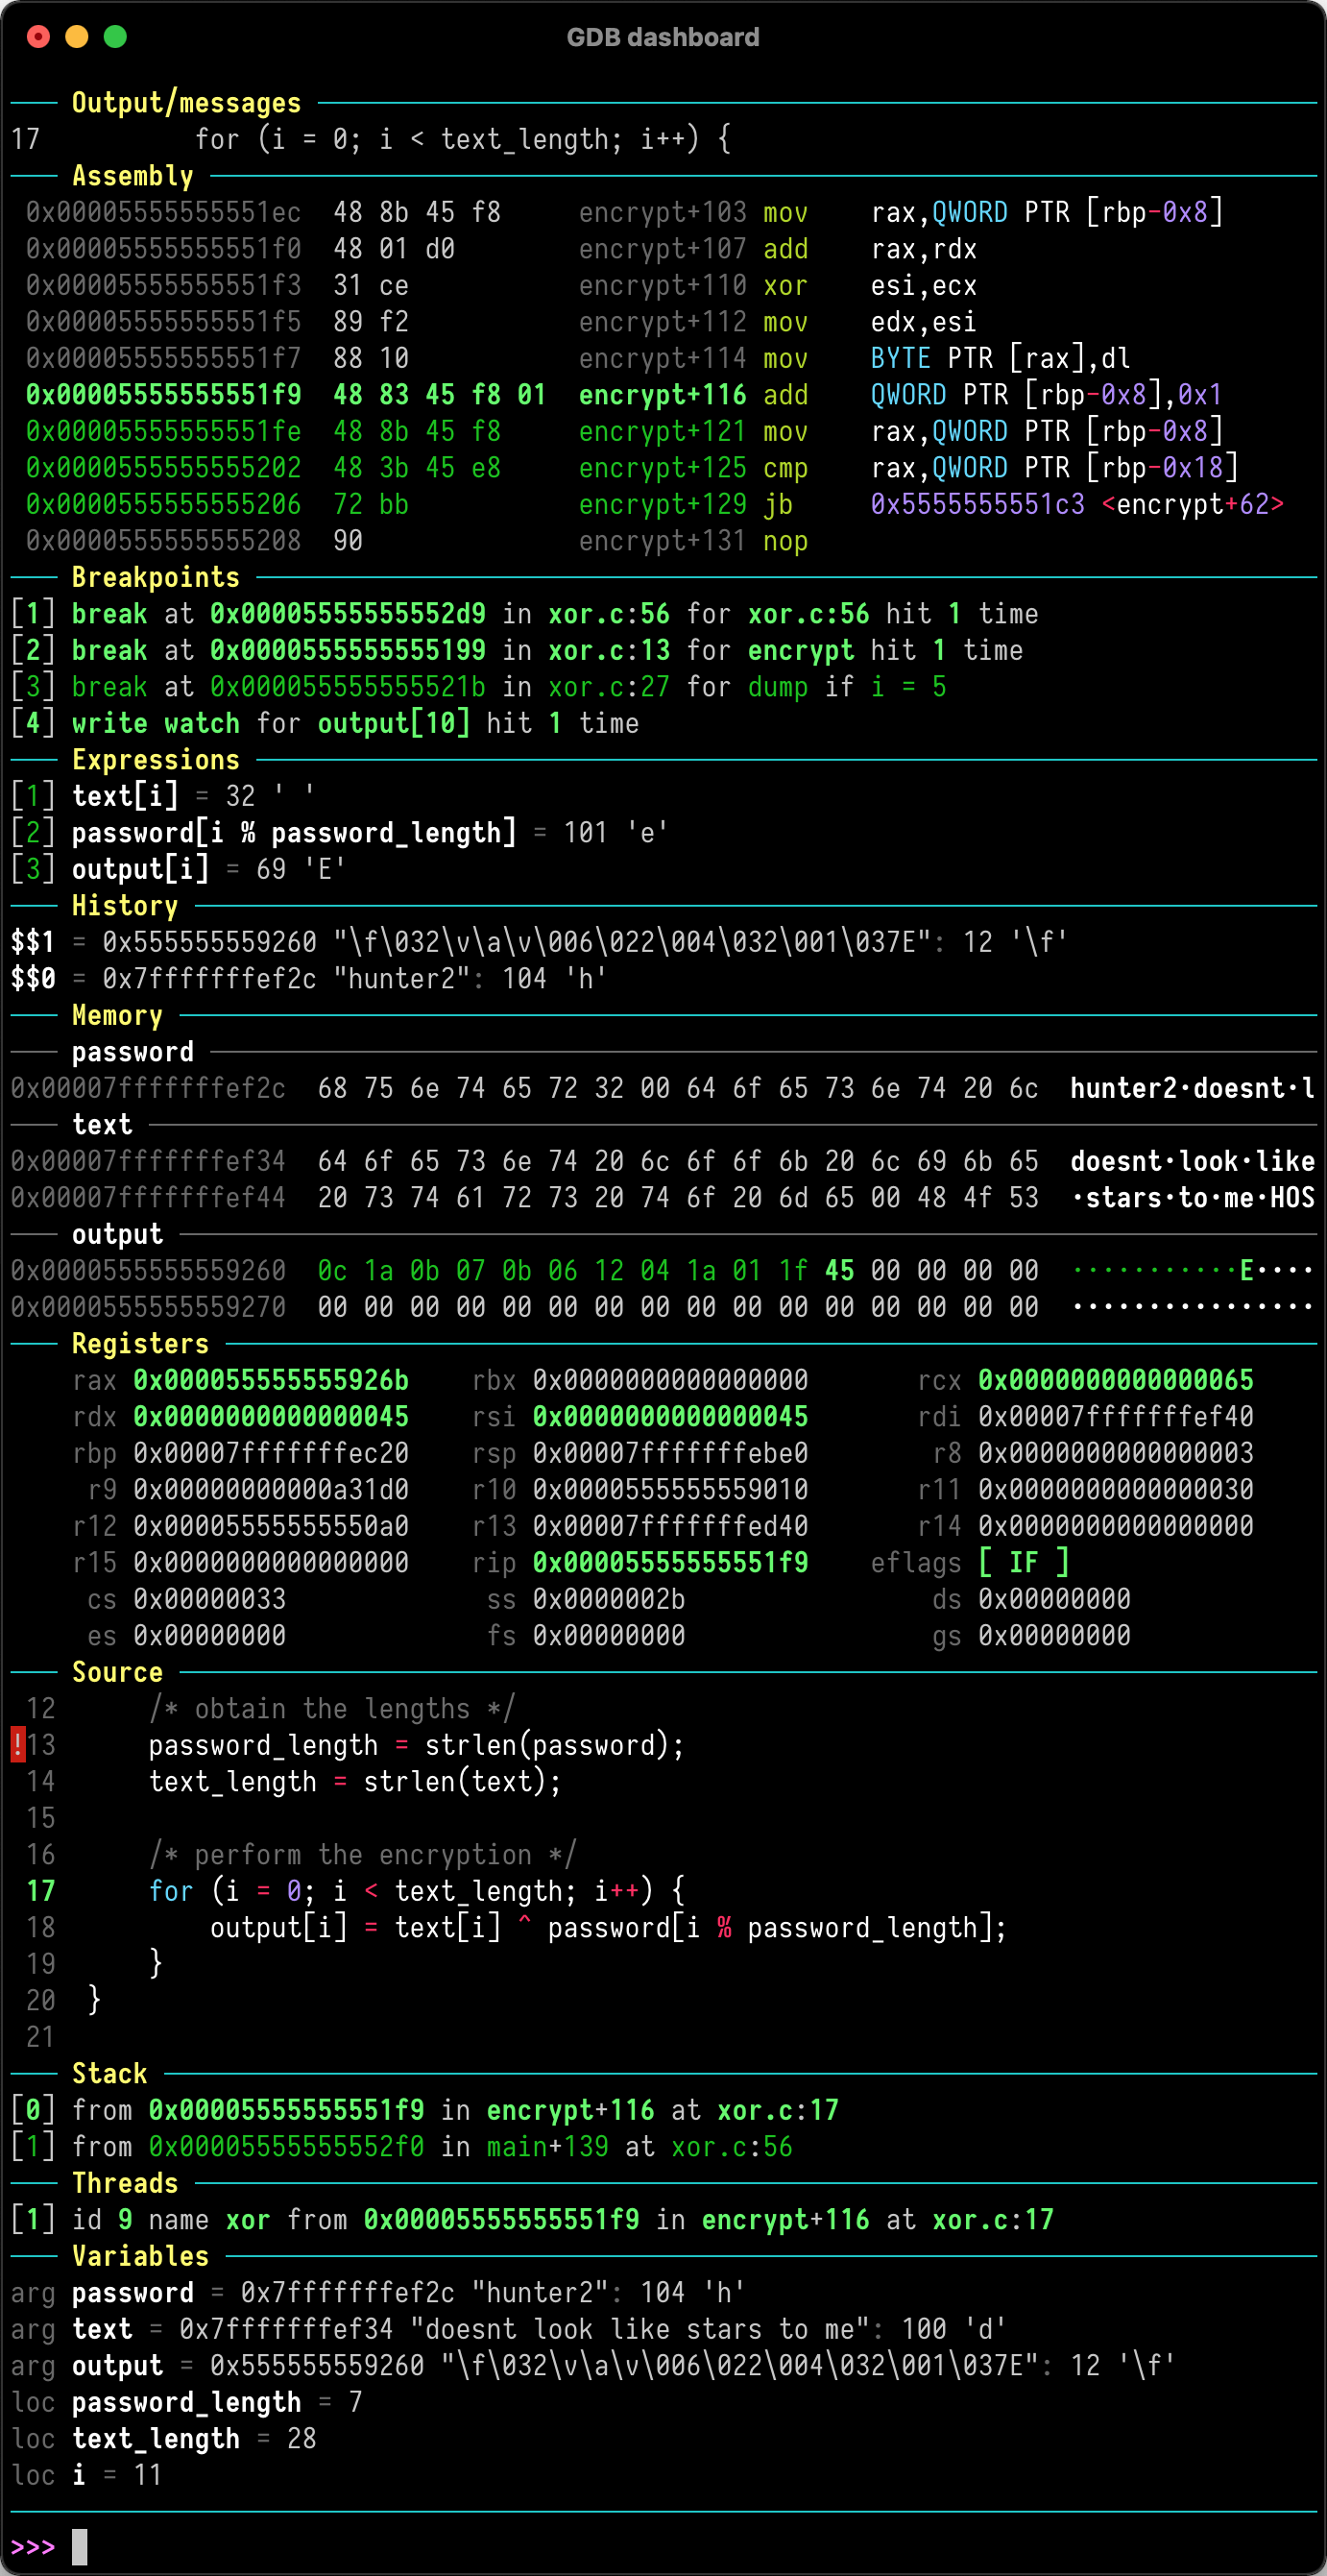 cyrus-and/gdb-dashboard
Modular GDB interface providing a visual dashboard with customizable panels for inspecting registers, source code, assembly, and program state during…
 mr-un1k0d3r/edrs
Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
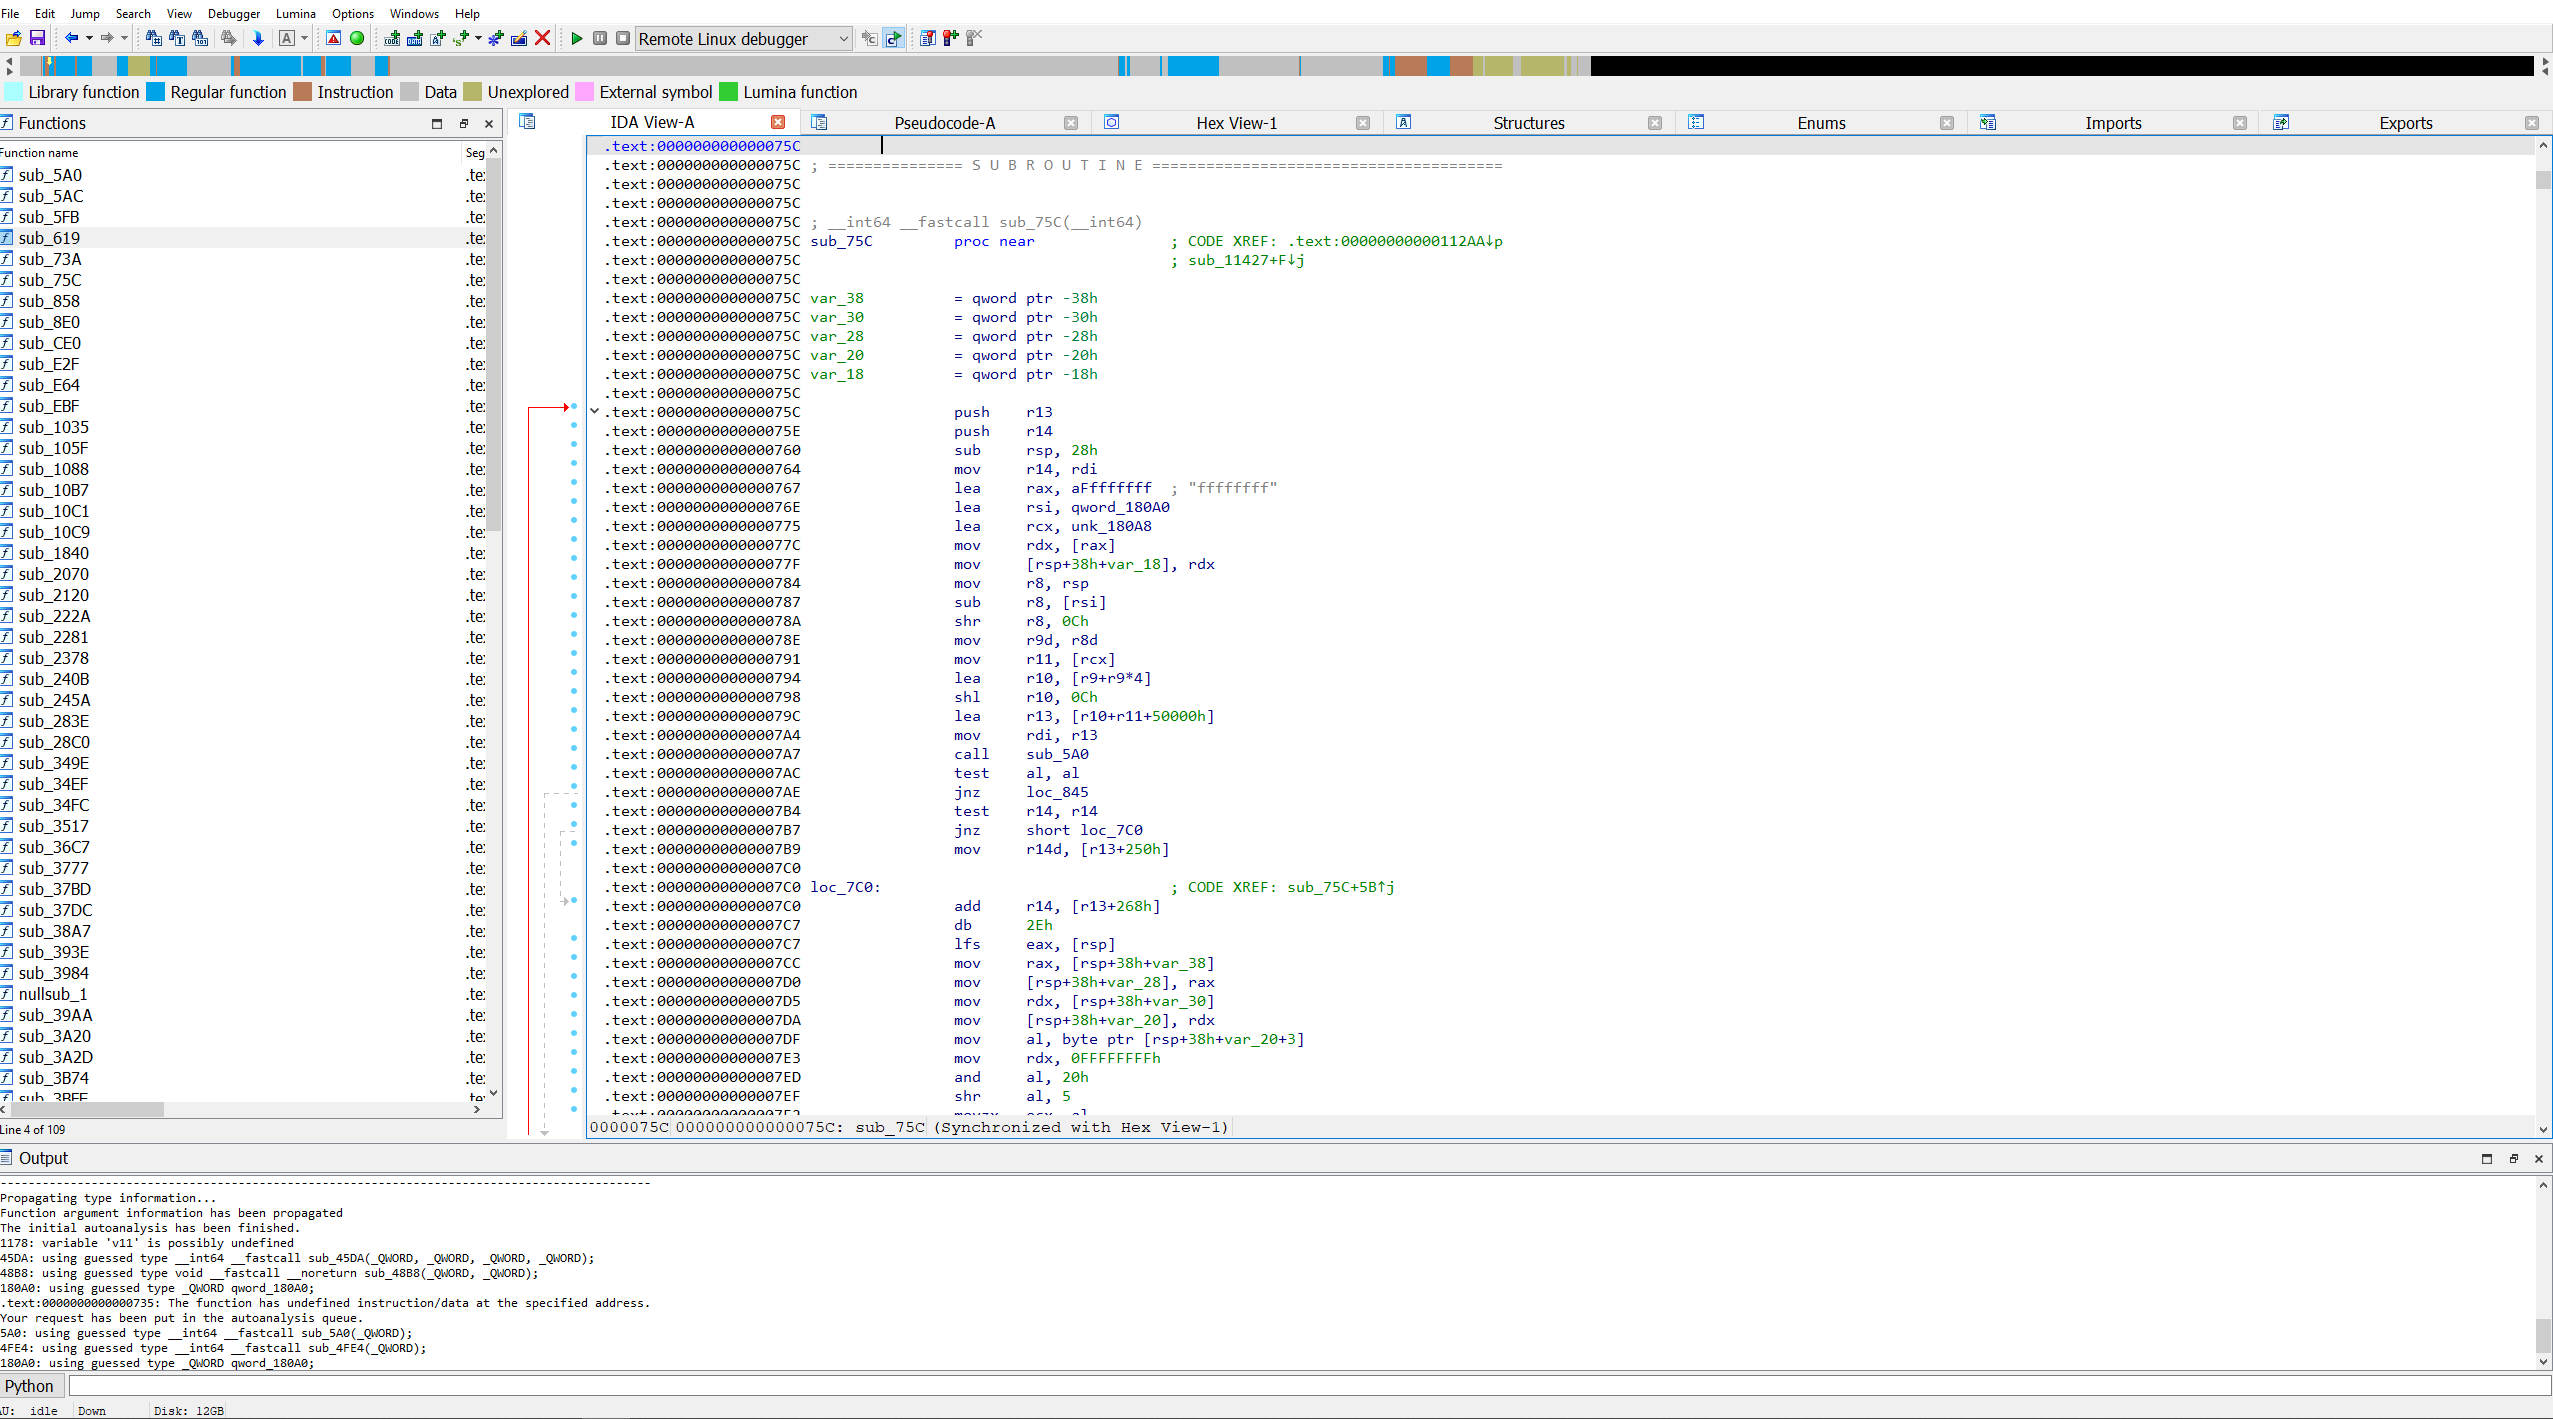 chip-red-pill/microcodedecryptor
Decrypts Intel Atom microcode updates and unpacks XuCode with recovered RC4 keys, revealing internal CPU microcode structures for hardware security…
 dump-guy/malware-analysis-and-reverse-engineering
Some of my publicly available Malware analysis and Reverse engineering.
 zodiacon/alltools
All reasonably stable tools
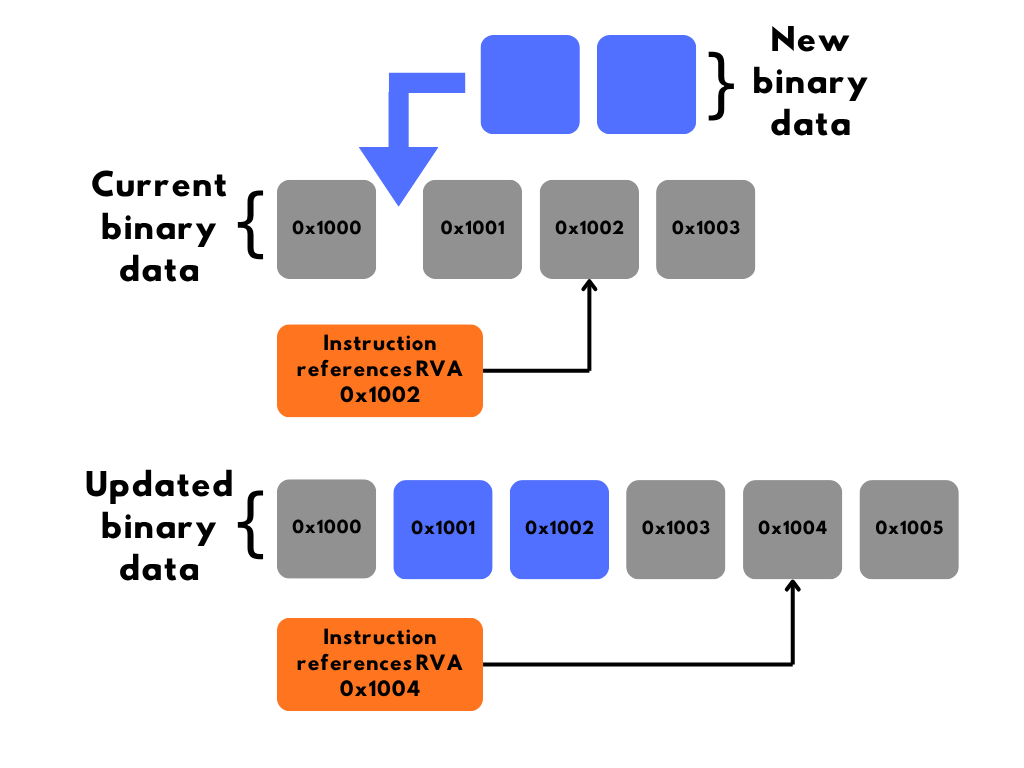 noahware/binprotect
x64 PE bin2bin obfuscator which doesn't add a section to the binary
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
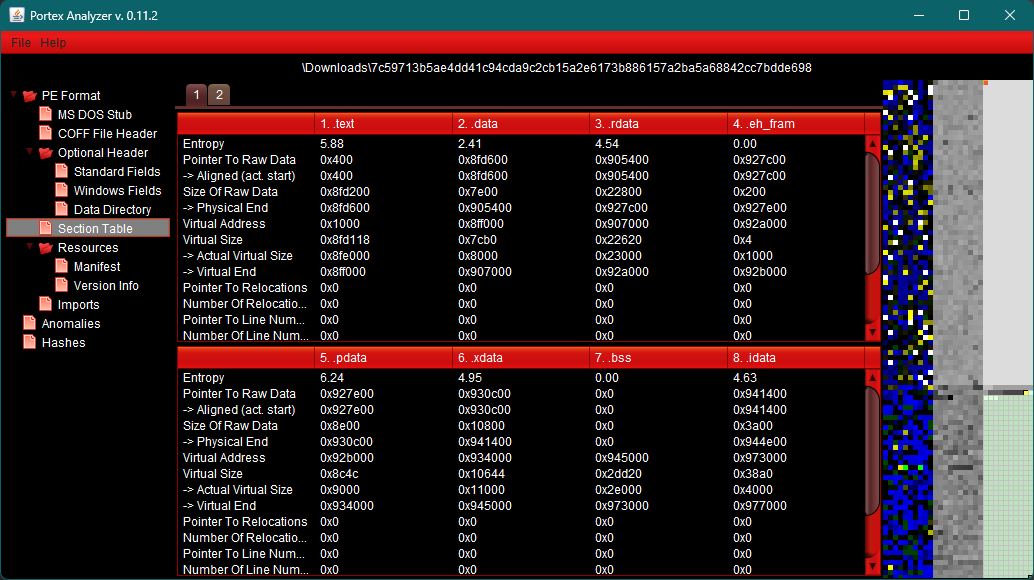 struppigel/portexanalyzergui
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library
 hari-prasaanth/thick-client-pentest-checklist
A OWASP Based Checklist With 80+ Test Cases
 bmaia/binwally
Binary and Directory tree comparison tool using Fuzzy Hashing
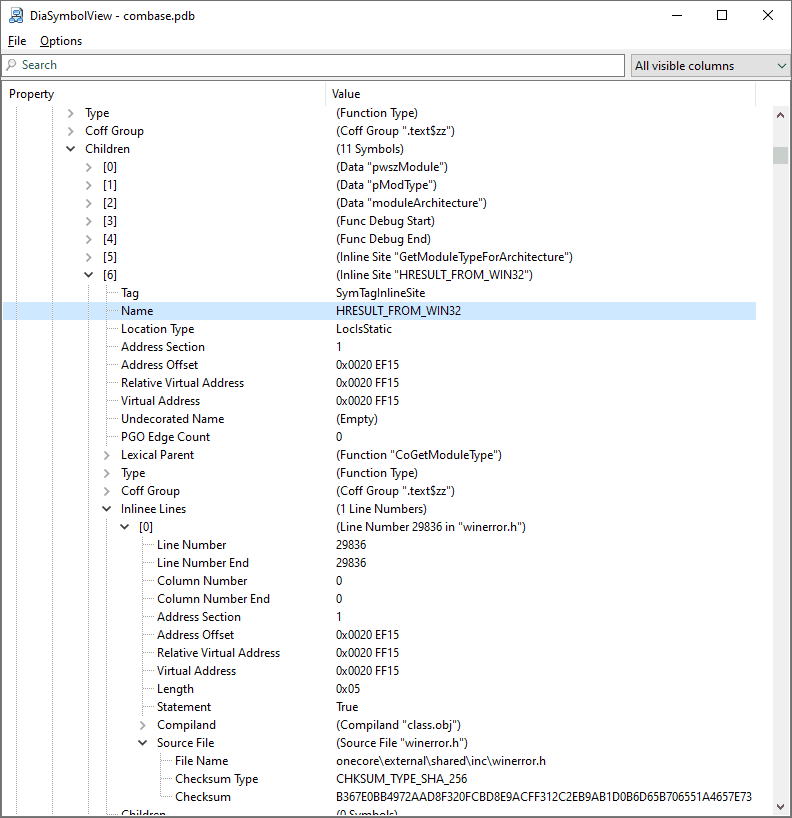 diversenok/diasymbolview
PDB file inspection tool
 whokilleddb/psi_bof
A BOF designed to inspect processes memory and addresses
 xoreaxeaxeax/hexcymatix
Visualizes repeated byte sequences in binary files to reveal hidden structure, supporting reverse engineering and pattern discovery without…