ThreatCheck
 rasta-mouse/threatcheck
Identifies the bytes that Microsoft Defender / AMSI Consumer flags on.
binary-analysisdefensive-toolsmalware-analysis+1
1.6k6 months ago
rasta-mouse/threatcheckIdentifies the bytes that Microsoft Defender / AMSI Consumer flags on.
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
 tekkenbugattii/linusware-source-code-internal
Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…
 cheat-engine/cheat-engine
Cheat Engine. A development environment focused on modding
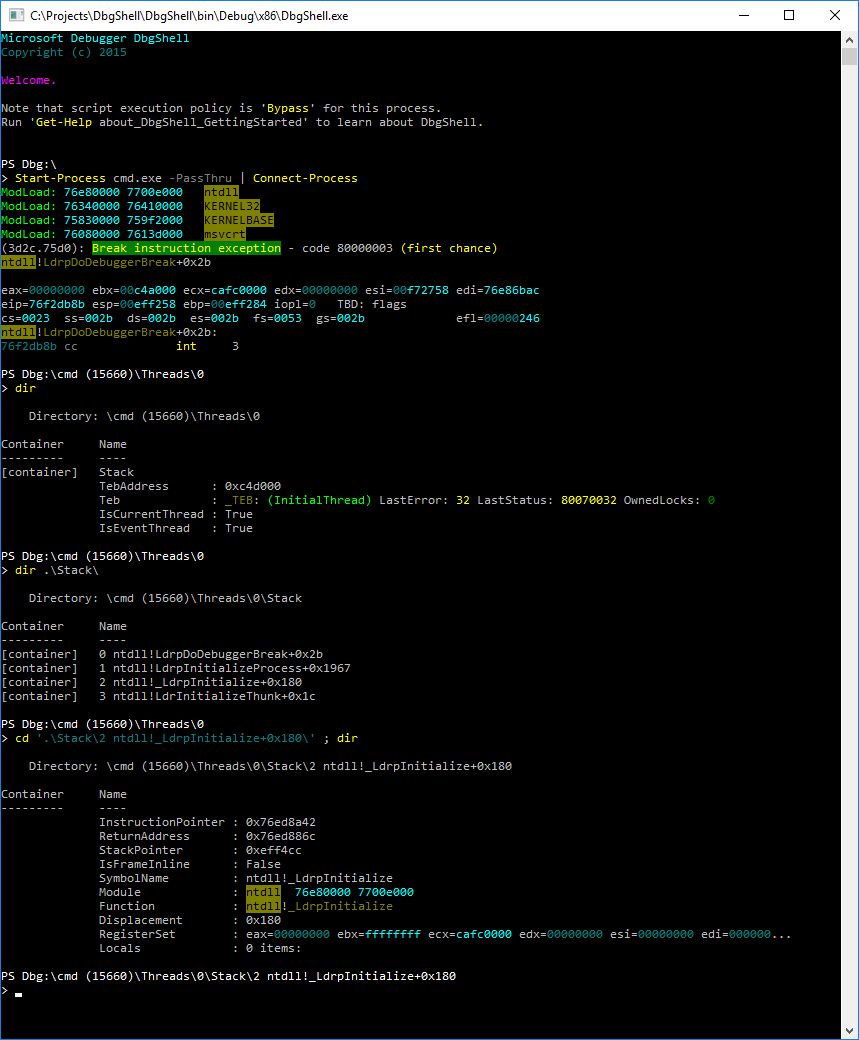 microsoft/dbgshell
A PowerShell front-end for the Windows debugger engine.
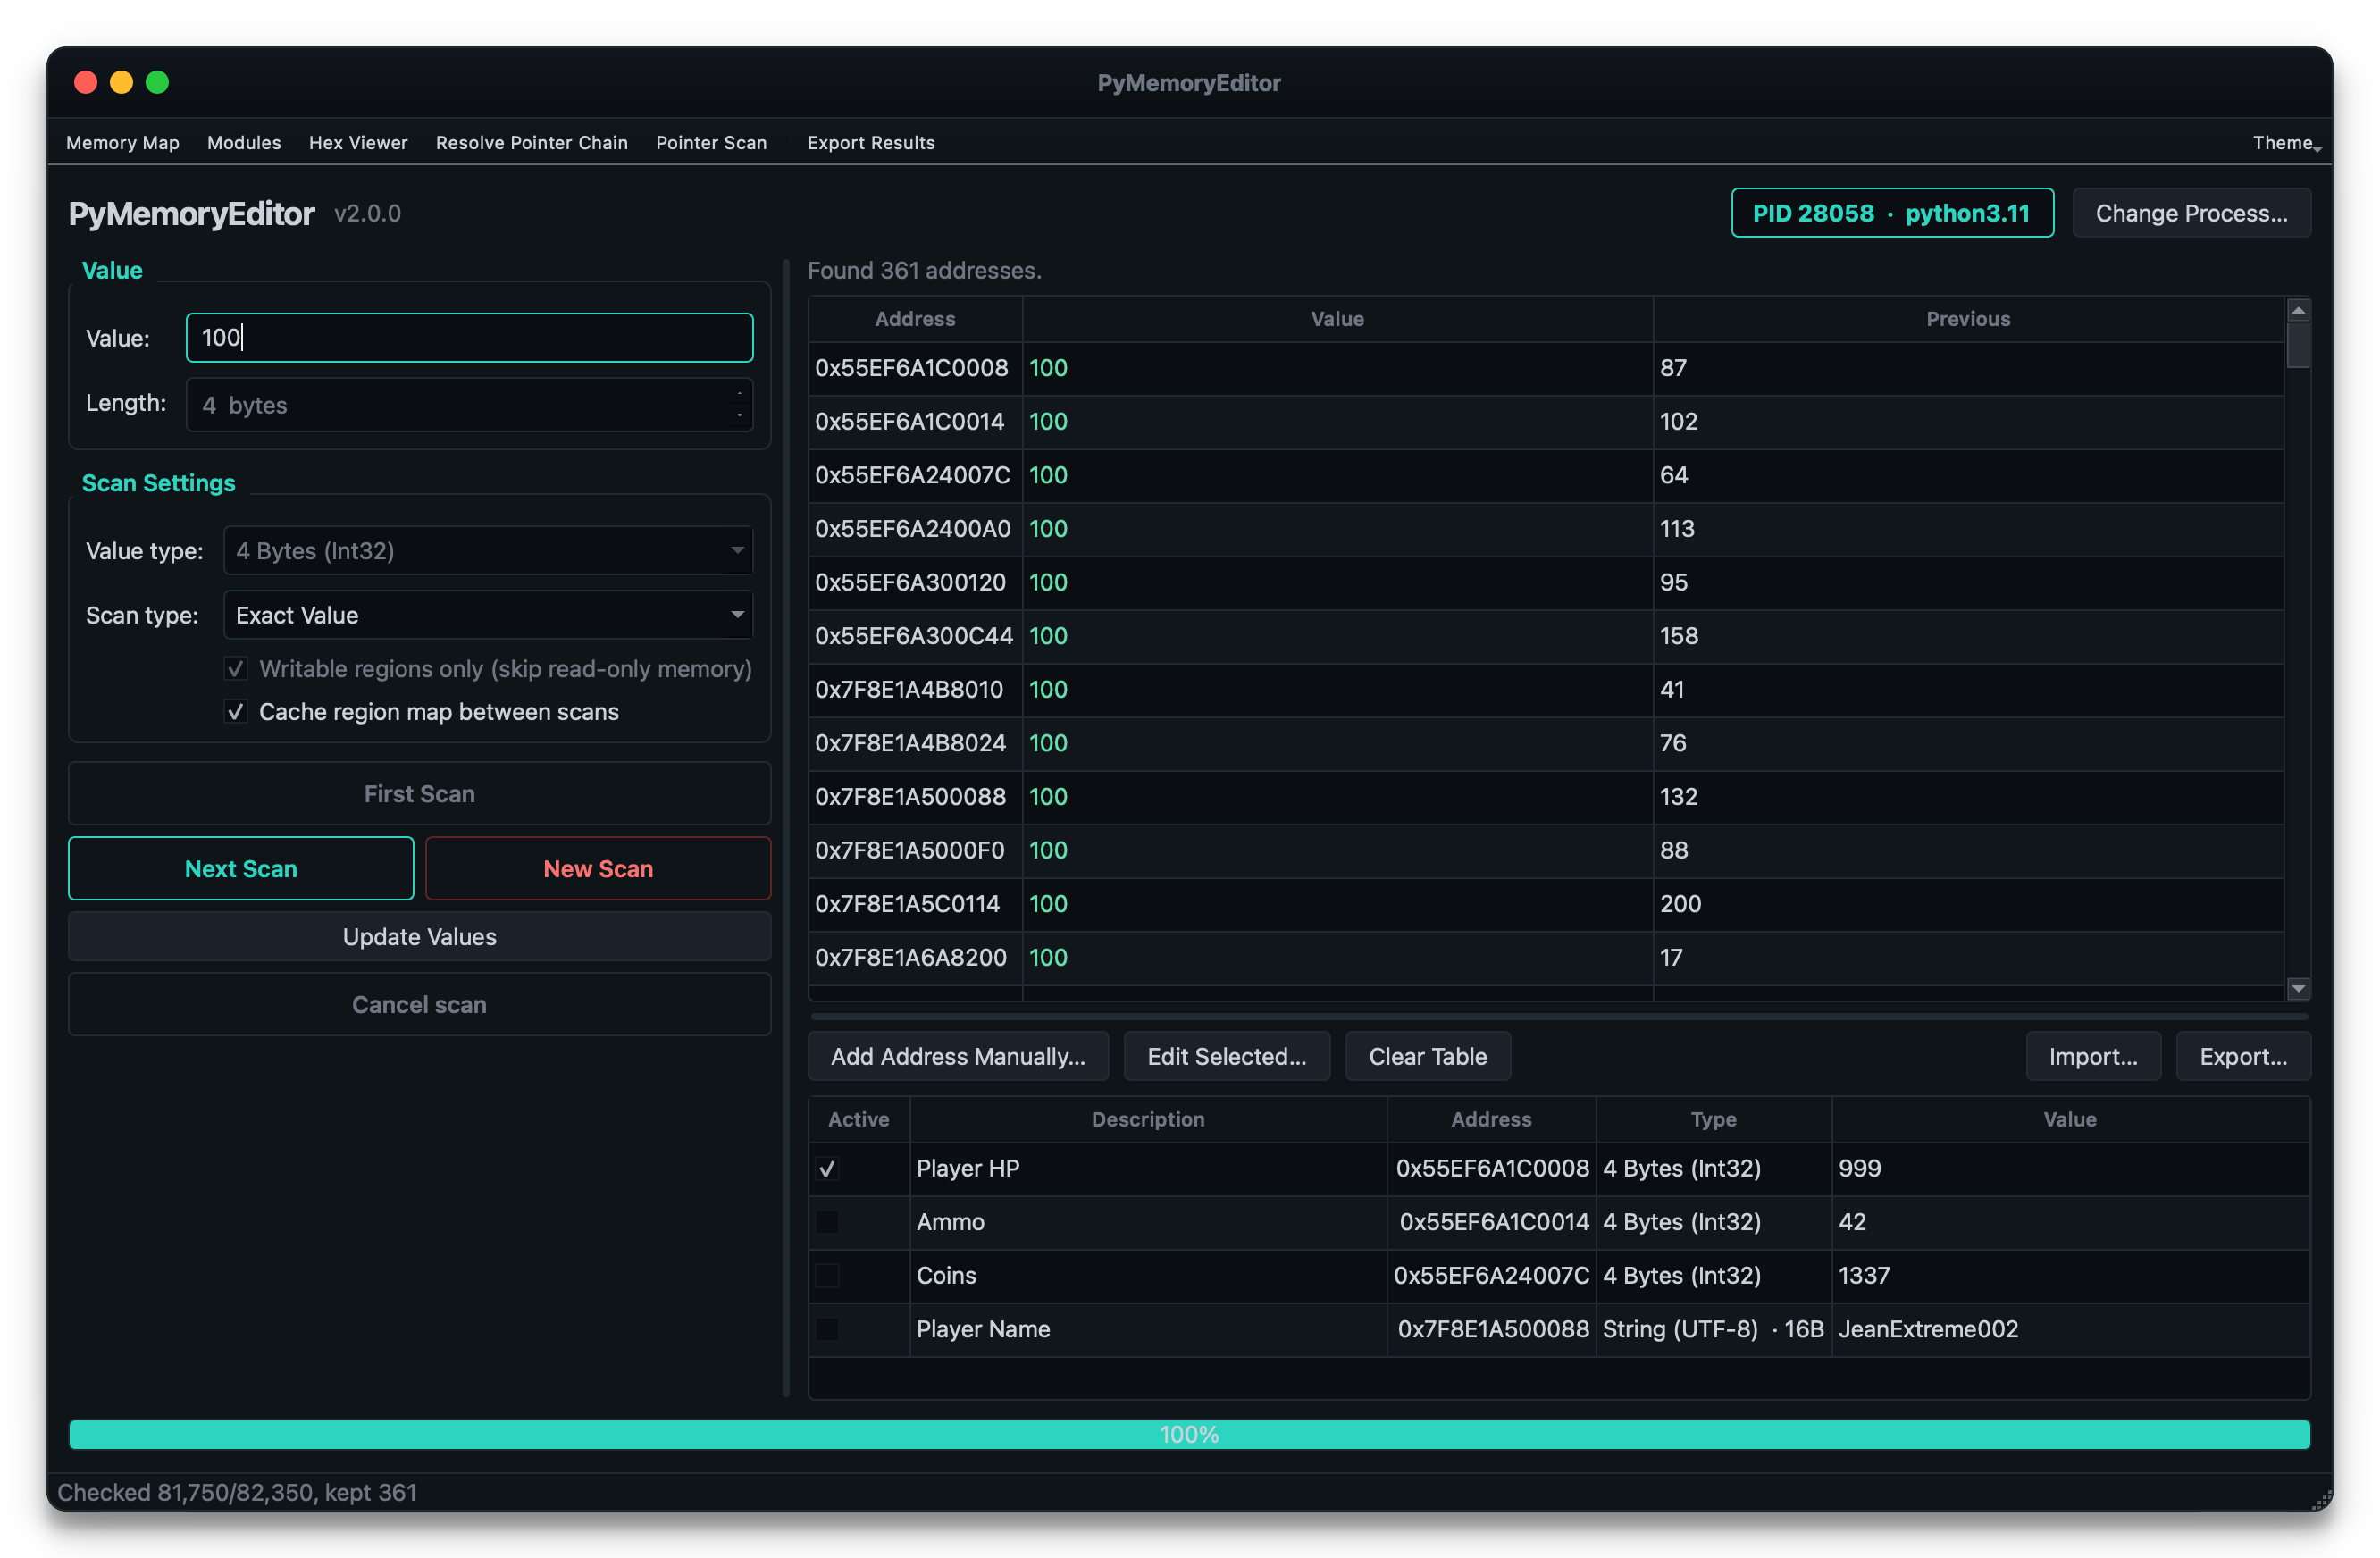 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 concollmic/concollmic
LLM-agent-powered concolic execution engine that instruments source code, summarizes path constraints in natural language, and generates test cases…
 elfmaster/maya
Highly advanced Linux anti-exploitation and anti-tamper binary protector for ELF.
 malwaretech/basichook
x86 Inline hooking engine (using trampolines)
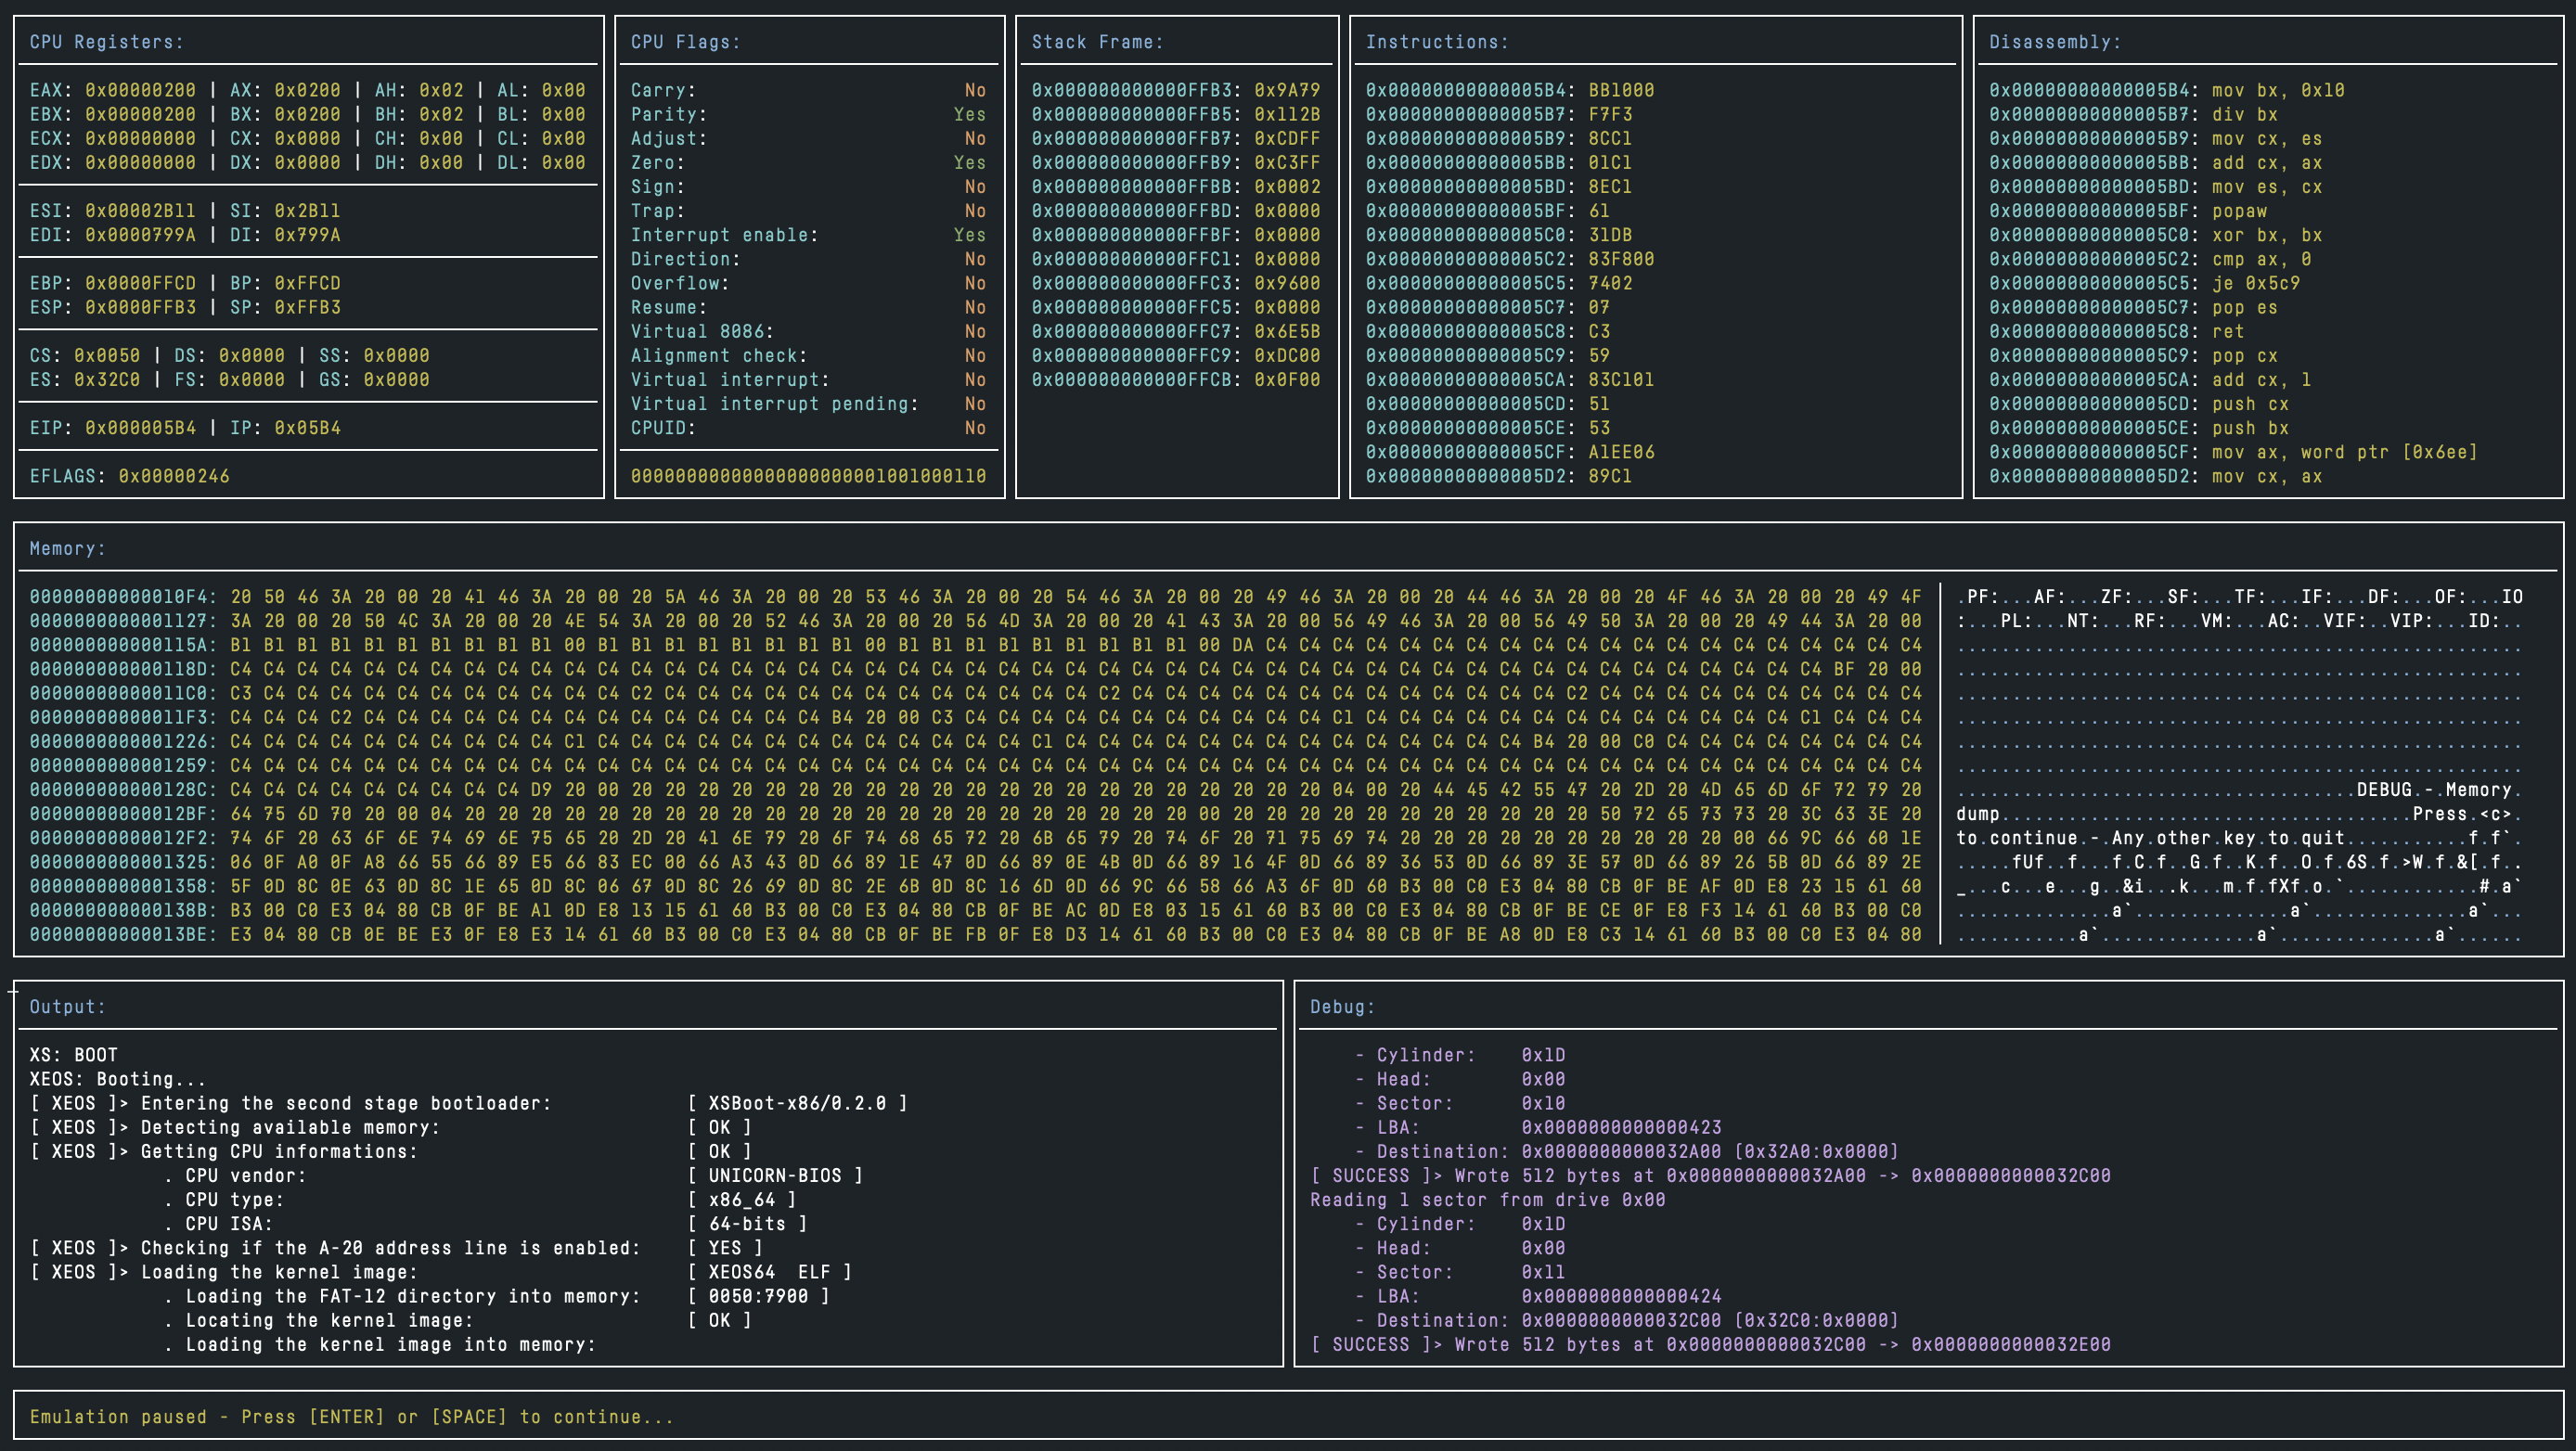 macmade/unicorn-bios
Basic BIOS emulator for Unicorn Engine.
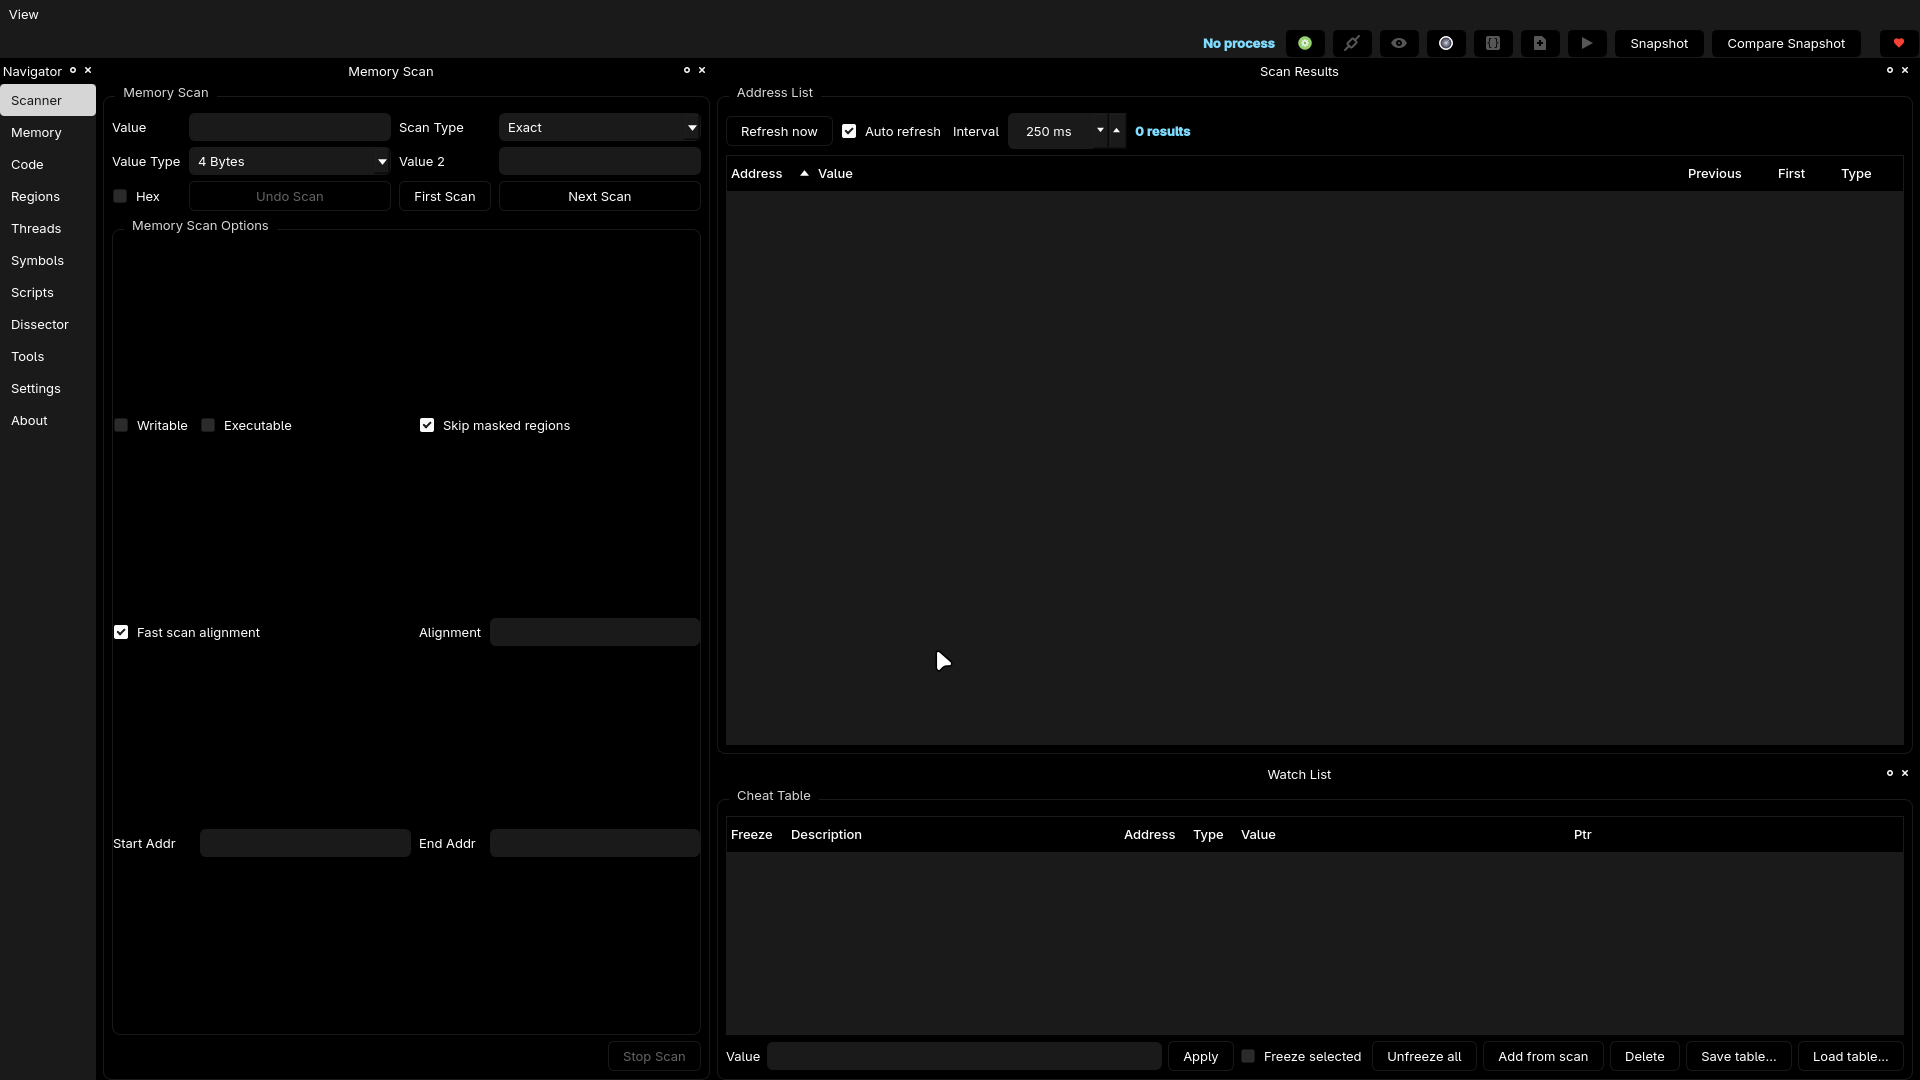 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 coldzer0/cmulator
Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…
 alexhude/uemu
Tiny cute emulator plugin for IDA based on unicorn.
 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…