
r0ak
 own2pwn/r0ak
r0ak ("roak") is the Ring 0 Army Knife -- A Command Line Utility To Read/Write/Execute Ring Zero on for Windows 10 Systems
binary-analysisexploitationpenetration-testing+3
278 years ago
own2pwn/r0akr0ak ("roak") is the Ring 0 Army Knife -- A Command Line Utility To Read/Write/Execute Ring Zero on for Windows 10 Systems
 moiz-2x/cve-2025-21420_poc
Proof of Concept CVE-2025-21420 (Windows Disk Cleanup Tool EoP)
 iss4cf0ng/dotnetpeloader
A C# PE loader for x64 and x86 PE files.
 xyl2k/black-eye-rsa-attacking-toolkit-v0.1f-compiled
The great RSA Attacking Toolkit compiled for Windows
 tarpeg007/cve-2026-19490
NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC
 ctn-qvo/auto_extract_offsets
Automated offset calculator for CVE-2026-43499, enabling precise memory offset computation for vulnerability exploitation and binary analysis.
 abraxas/mysql-mysqldump-show-tables-overflow
MySQL Community Server 26.7.0 - High - mysqldump SHOW TABLES stack overflow - crash dump UID
 jbaines-r7/theway
A tool for extracting, modifying, and crafting ASDM binary packages (CVE-2022-20829)
 nam3lum/msi-central_privesc
CVE-2022-38532 - Local Privilege Escalation vulnerability in MSI Center Application
 australeo/cve-2021-28476
Proof-of-concept for CVE-2021-28476, a Hyper-V vmswitch.sys arbitrary pointer dereference allowing guest-to-host denial-of-service and potential RCE.
 kemrec/cve-2025-0324-axis-vapix-privesc
Root-cause analysis and safety-gated verification tool for CVE-2025-0324, a privilege-escalation flaw in AXIS OS VAPIX allowing any authenticated…
 nektra/cve-2010-3971-hotpatch
Do you own security hotfix with Deviare hooking
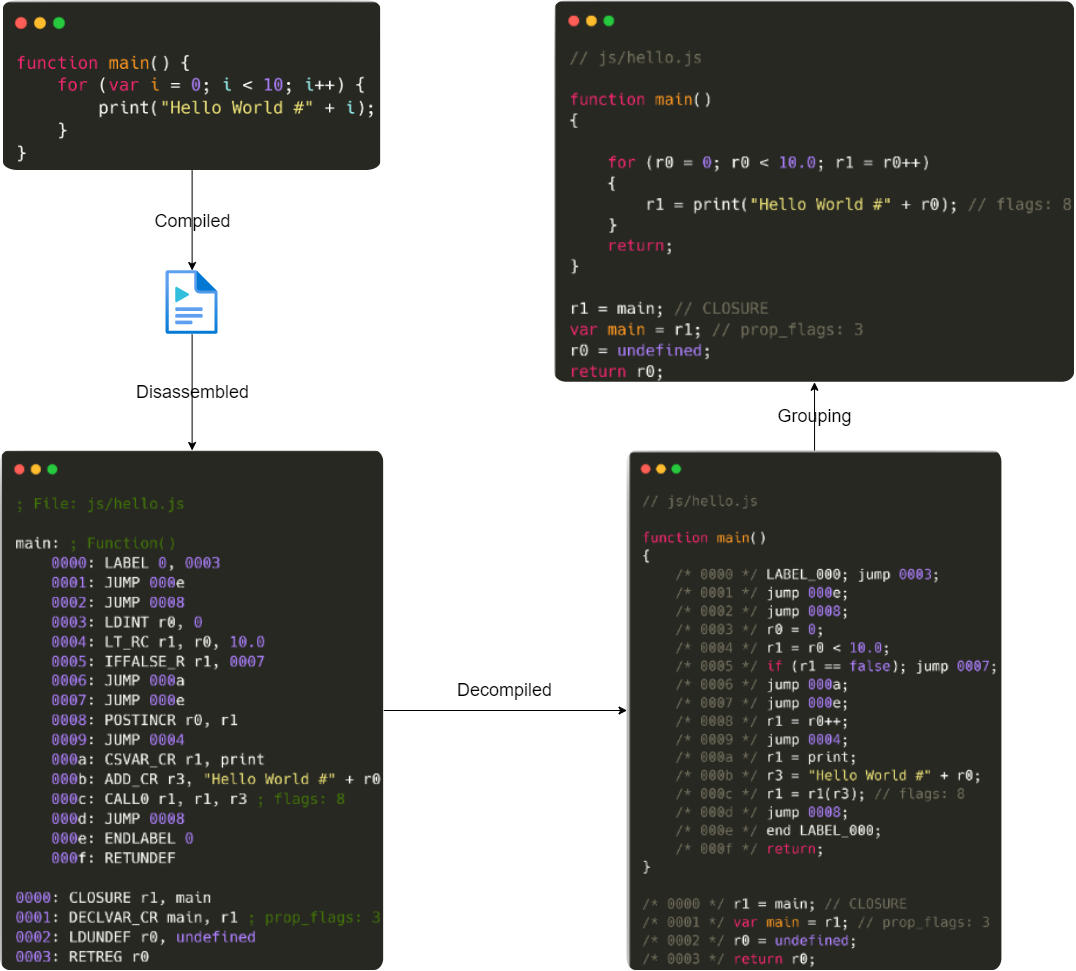 nccgroup/detaped
Detaped is a Python disassembler and decompiler for Duktape. The intended use is for source code review and analysis in situations where you only…
 snappyjack/pdfresurrect_cve-2019-14267
 gguaiker/trend_micro_poc
CVE-2018-3608 Trend_Micro_CVE
 ugvxb/cve-2026-9490
The ACCSvc service creates a Named Pipe with a weak Security Descriptor that allows any authenticated user to connect and send messages. When a…
 spiralbl0ck/cve-2024-24686
Crash File ( Poc for CVE-2024-24686)
 skrkcb2/cve-2025-0851
Proof-of-concept exploit for CVE-2025-0851, a file traversal vulnerability in Deep Java Library's tar/zip model extraction utility, enabling…