

xz-cve-2024-3094
 0xlane/xz-cve-2024-3094
XZ Backdoor Extract(Test on Ubuntu 23.10)
binary-analysisexploitationforensics+3
17
0xlane/xz-cve-2024-3094XZ Backdoor Extract(Test on Ubuntu 23.10)
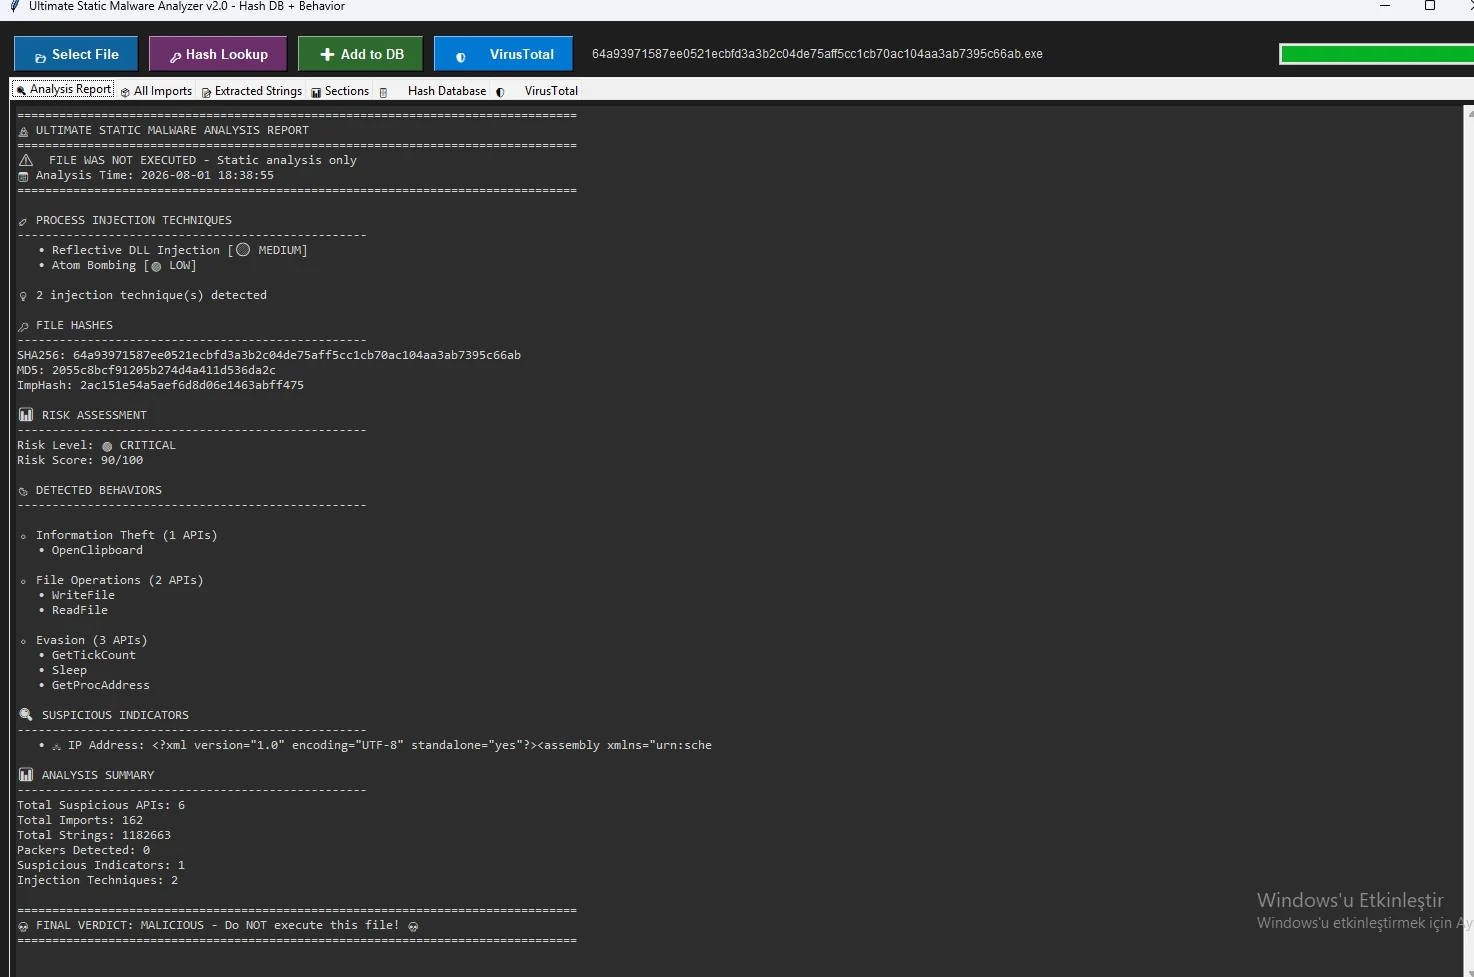 kaandemir993/malwareforge---advanced-static-malware-analyzer
Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 gmh5225/asm-obfuscator
Obfuscates x86-64 assembly with instruction injection, junk code, constant obfuscation, and runtime decryption to hinder reverse engineering and…
 dodo-sec/kpot-string-decrypter
IDA python scripts to decrypt strings from KPOT and set those as comments
 oitapps/find-vulnerableelectronversion
Scans an executable and determines if it was wrapped in an Electron version vulnerable to the Chromium vulnerability CVE-2023-4863/ CVE-2023-5129
 ret5et/watchguard_webui_unpacker
Watchguard Sysa-dl file format
 claesmnyberg/sdc
Self Decrypting Binary Generator
 mandiant/route-sixty-sink
Link sources to sinks in C# applications.
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
 mmozeiko/aes-finder
Utility to find AES keys in running processes
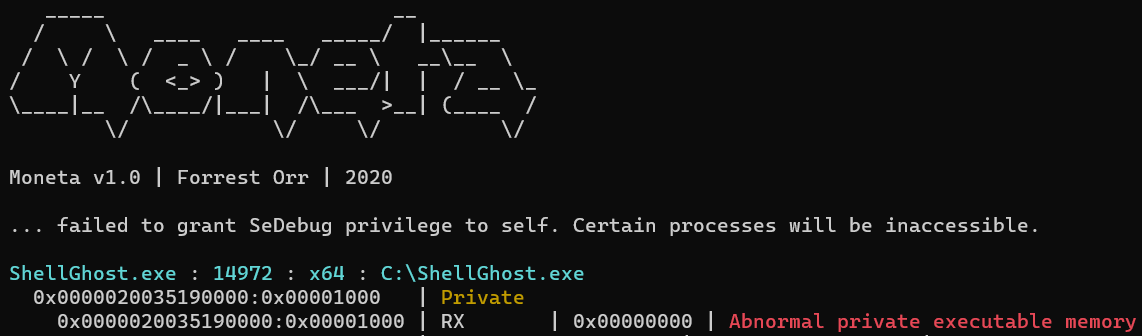 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
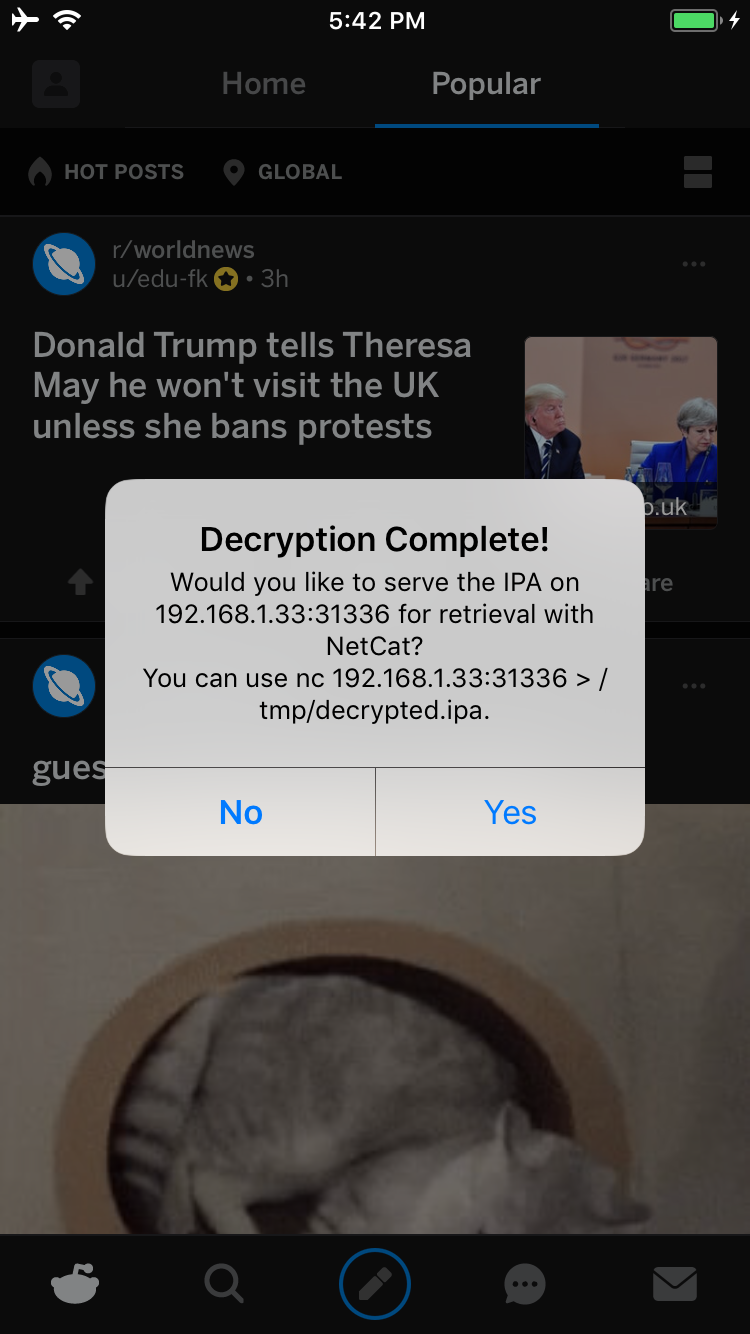 bishopfox/bfdecrypt
Utility to decrypt App Store apps on jailbroken iOS 11.x
 cerbersec/ares
Project Ares is a Proof of Concept (PoC) loader written in C/C++ based on the Transacted Hollowing technique
 hackerschoice/bincrypter
Pack/Encrypt/Obfuscate ELF + SHELL scripts
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
 nccgroup/pip3line
The Swiss army knife of byte manipulation