frameworks_base_AOSP10_r33_CVE-2020-0401

Android framework base repository for AOSP 10 r33, modified to address CVE-2020-0401, providing a patched or vulnerable version for security research…

Android framework base repository for AOSP 10 r33, modified to address CVE-2020-0401, providing a patched or vulnerable version for security research…

Android 6.0.1 framework base repository containing the CVE-2018-9338 vulnerability for analysis and exploitation research.

Android netd vulnerability analysis and exploitation research for CVE-2023-40084, focusing on the platform's network daemon.

Android framework base repository for Android 6.0.1 r22, modified to address CVE-2023-20921, providing a patched version for security analysis and…


Analyzes and patches Android AAC (Adaptive Audio Coding) library for CVE-2023-21282, focusing on vulnerability assessment and code-level fixes.

Android framework base repository for AOSP 4.2.2_r1, modified to address CVE-2023-21272, a vulnerability in the Android framework.

Frida-based proof-of-concept demonstrating authentication bypass in Telegram Android by hooking SharedConfig.checkPasscode to always return true,…

A native APK and DEX decompiler written in Rust

Agent skill for Android APK reverse engineering: dex patching, unpacking, repacking, ad and paywall removal, native .so analysis, and runtime…

Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…

Android and Java bytecode viewer

Flutter Reverse Engineering Framework

Translates Dalvik bytecode (DEX/APK) to equivalent Java bytecode, enabling Java analysis tools to process Android applications with high correctness…

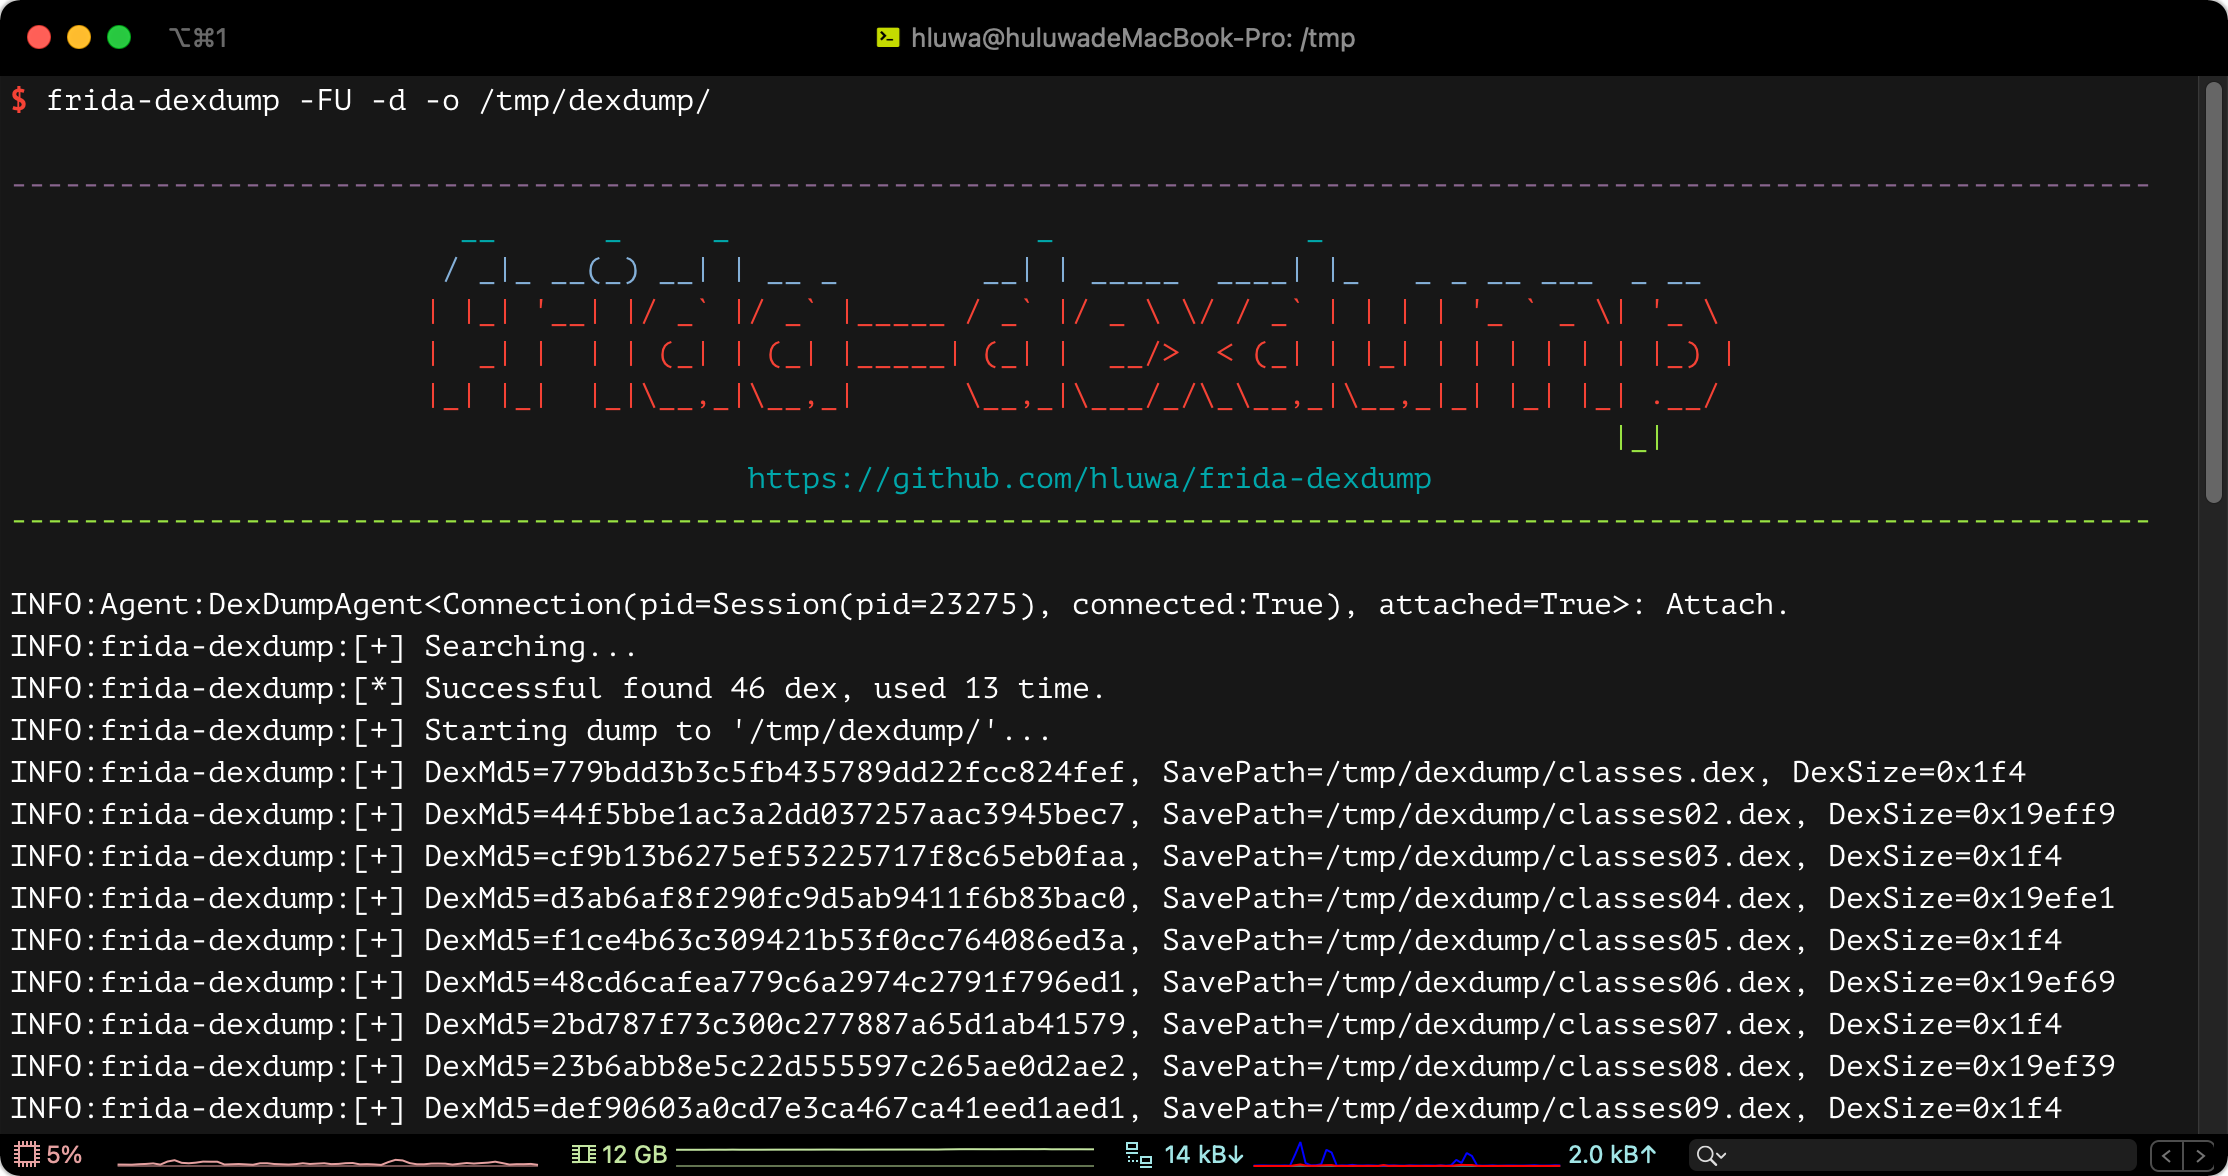
A frida tool to dump dex in memory to support security engineers analyzing malware.