

memory-forensic
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
binary-analysiscontainer-escapedata-recovery+7
12
securityronin/memory-forensicWalk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 fzrsllasher/cve-2026-12166_cve-2026-12167_cve-2026-12168
Technical advisory detailing three local privilege escalation vulnerabilities (CVE-2026-12166/7/8) in the Little Orbit GFAC kernel driver, including…
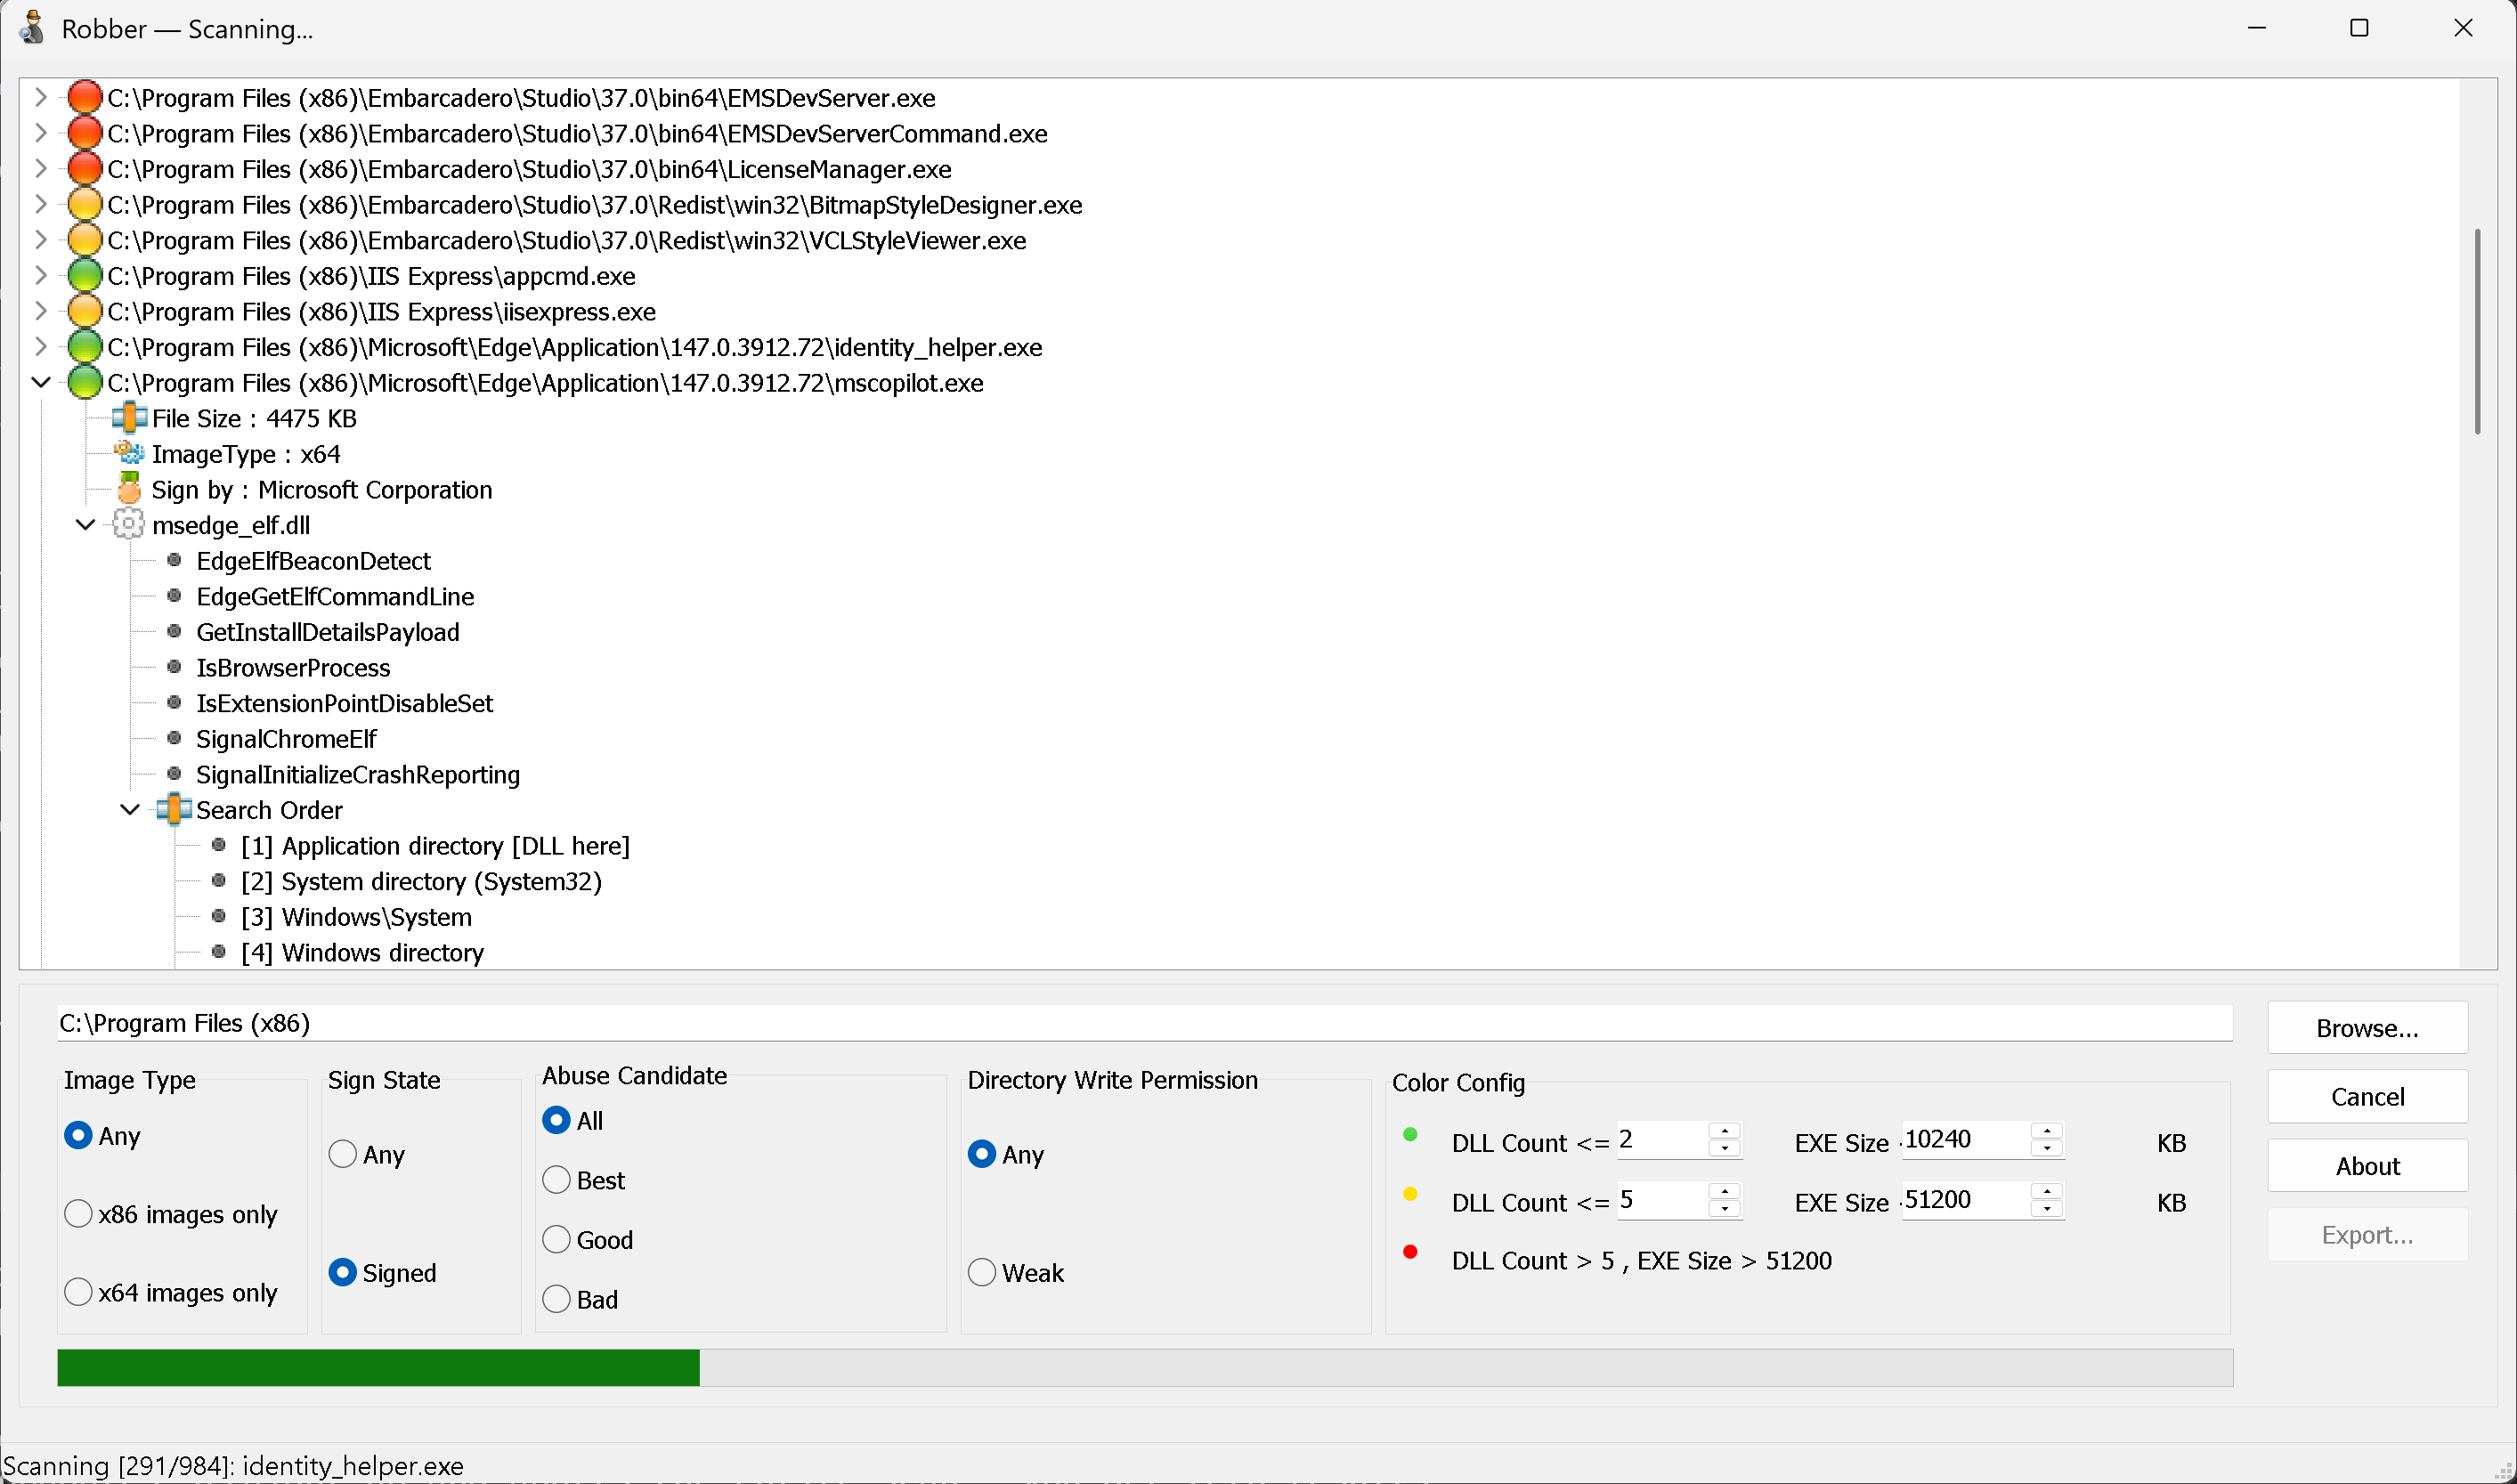 mojtabatajik/robber
Robber is open source tool for finding executables prone to DLL hijacking